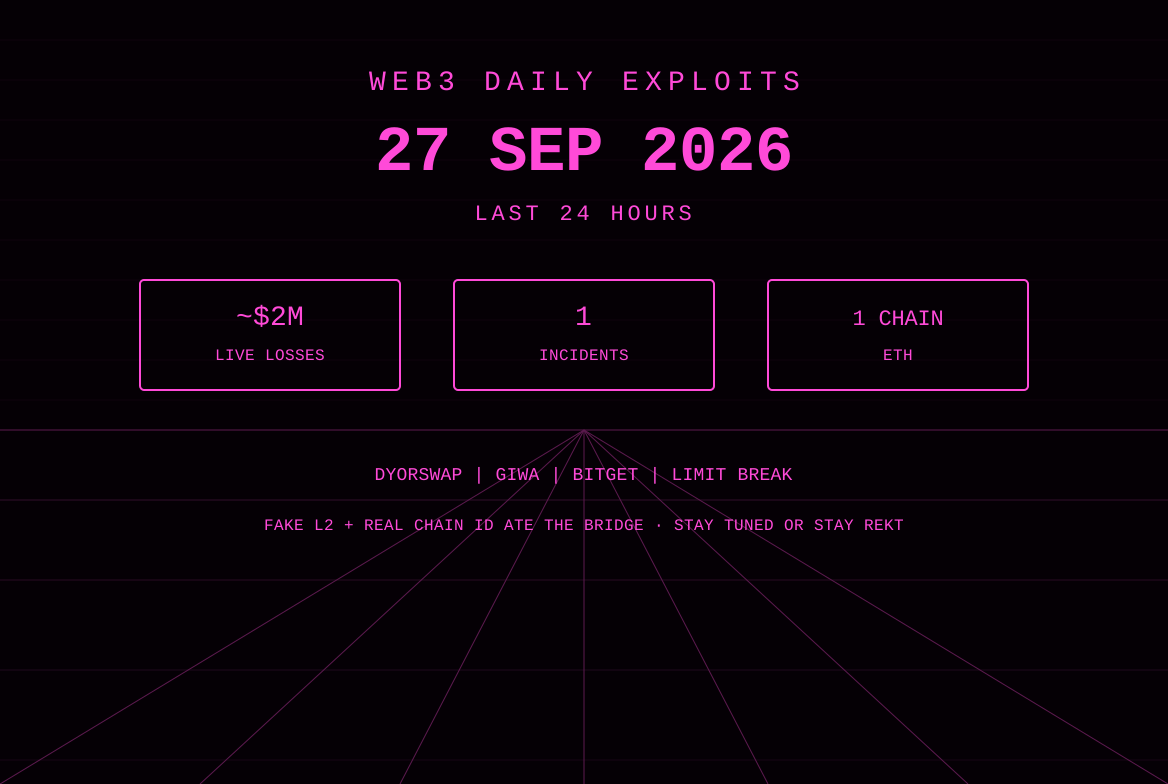
Web3 Daily Exploits — 27 Sep 2026: DYORSWAP Fake GIWA Bridge
First-report this window: DYORSWAP confirmed the GIWA mainnet it had listed was a scammer-built fake chain using chain ID 9134. Community and tracker estimates put ETH-bridge losses near $2M. GIWA (Upbit L2) said official mainnet is not live. Bitget and Limit Break remain UPDATEs. Duelbits still unverified.
Required monitors were checked through the 27 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. After that account check: one first-report incident sits in this window. It is not a bytecode drain of a production L2. GIWA by Upbit stated that official mainnet is not running and that rumored mainnet RPC posts are false. DYORSWAP then confirmed that the “GIWA Mainnet” it had previously identified was a scammer-built fake chain that reused chain ID 9134, and that significant losses had already moved through a fraudulent bridge. Community and secondary-tracker estimates cluster around $2 million. DYORSWAP itself has not published an official USD total; this card scores the ~$2M community figure as the live-loss estimate for the first-report item and labels it as unofficial.
CertiKAlert, PeckShieldAlert, Phalcon_xyz, BlockSecTeam, and CyversAlerts returned no in-window first-report protocol-drain posts. Immunefi and rekt.news had no fresh incident page located in this sweep. Material UPDATE traffic continues on Bitget (phased withdrawal reopen calendar, a THORChain refuse-service request, GoPlus laundering notes, a 28 Sep incident-report livestream) and on Limit Break / Magic Eden Payment Processor V2 (onchain victim outreach and a whitehat coordination message). Duelbits remains unverified. DPRK attribution on Bitget remains unlabeled as confirmed.
DYORSWAP / fake GIWA mainnet — Ethereum deposits into a fraudulent bridge — ~$2M (community estimate)
What happened: GIWA, the Upbit-linked OP Stack L2 project, posted on 27 Sep that official mainnet has not launched and that posts claiming GIWA mainnet RPC information are not true. A second GIWA post repeated that there is no mainnet RPC to leak. Those statements are the official-chain baseline for this window.
DYORSWAP, a multi-chain DEX that had listed a network as GIWA mainnet, published a security-incident notice the same morning. The team wrote that the so-called GIWA Mainnet it previously identified was in fact a fake chain set up by scammers; that the fake network used chain ID 9134, which made it appear legitimate during initial verification; that suspicious messages and individuals in a related community may be connected; and that significant losses had already occurred through a fraudulent bridge. DYORSWAP said it was contacting security teams for tracing, preserving chat logs, RPC data, bridge addresses and on-chain transactions, and preparing to use treasury funds to compensate affected users after verification. A later DYORSWAP post said loss verification would be reconstructed from Ethereum mainnet deposits into the fake GIWA bridge and listed internal counts: 1,731 transactions, 275 wallets, 744 DYOR trades, and more than 1,300 addresses bridged. The same account posted a Google Form for loss submissions, then said users would not need to calculate losses because the team would rebuild the victim list from chain data. A follow-up reply said the RPC was wrapped from the scam network and that DYORSWAP did not make a bridge frontend.
Independent posts in the same window (not required-monitor first reports) described users adding the fake network to wallets, connecting to a lookalike RPC, and sending ETH into contracts presented as a GIWA bridge. GIWA official language is that mainnet is not live, so there is no official destination L2 for those deposits. Owlto Finance posted that it did not enable an unverified GIWA route. PublicAML and DeTracker repeated a $2 million phishing-bridge figure; a widely circulated thread used the same notional. DYORSWAP’s own language remains “significant losses,” not a signed USD schedule.
Protocol / chain / asset: Ethereum mainnet as the source of user deposits. Destination presented as GIWA mainnet (chain ID 9134) is not the official GIWA network. Asset at risk in public estimates is ETH. This is a fake-chain / fake-bridge social and listing failure, not a confirmed exploit of GIWA production contracts.
Loss: Card scores ~$2M as the community and secondary-tracker estimate circulating with the 27 Sep confirmation. Operator has not published a matching official USD total. Wallet and transaction counts above are DYORSWAP’s own reconstruction figures, not a USD mark.
Attack type: Fake L2 / cloned chain ID plus a fraudulent bridge. Users approved and sent their own deposits. Required-monitor desks did not publish a contract-level RCA or a named attacker EOA in the posts used here. Exact bridge bytecode and receive addresses are not invented on this card.
Explorer URLs: No required-monitor post attached a primary drain hash or a canonical fake-bridge address. This desk does not invent hashes. Official GIWA and DYORSWAP statements are social-primary, not explorer-primary.
Status: Confirmed as a fake-chain listing incident by DYORSWAP. Official GIWA mainnet not live. Treasury compensation promised, eligibility unpublished. On-chain reconstruction in progress per the DEX. ZachXBT was publicly tagged by DYORSWAP and separately posted that he does not treat unaffiliated gamblers as a work obligation; that is not an investigative close on this item.
Sources: https://x.com/GIWA_by_Upbit/status/2104091017901433017, https://x.com/GIWA_by_Upbit/status/2104108336228843590, https://x.com/DYORSWAPDEX/status/2104120544178344112, https://x.com/DYORSWAPDEX/status/2104152247466872963, https://x.com/Owlto_Finance/status/2104169915850908133
UPDATE — Bitget Exchange — multi-chain CEX hot/warm wallets — recount ~$387.5M (already scored)
What happened (this window): No new unauthorized-transfer wave was confirmed. Bitget restated a phased withdrawal reopen: 28 Sep 08:00 UTC BTC; 29 Sep ETH rails (Ethereum, BSC, Arbitrum, Base, Optimism); 30 Sep USDT (Ethereum, BSC, Solana, Tron); 2 Oct other tokens / fiat / P2P. The operator said the original vulnerability was identified and remediated, Mandiant and SlowMist remain on the investigation, and the pause is a security measure rather than an asset-availability problem. On 27 Sep Bitget scheduled a 28 Sep 07:30 UTC livestream with Gracy Chen and Xie Jiayin for an incident report and withdrawal questions.
Gracy Chen formally asked THORChain to refuse service to published attacker addresses. GoPlusSecurity published a long 27 Sep essay arguing THORChain outbound signing is an active TSS event, not neutral base-layer inclusion, and wrote that in the Bitget case about 101.5 BTC (~$8.5M) had already gone out via THORChain with another ~27.63M XRP (~$43M) mid-swap into BTC. Those laundering-path figures are GoPlus analysis of movement after the 24 Sep drain, not a new CEX incident, and are not added to card live-loss. Lookonchain in-window prints (ENA CEX withdrawals, Pump.fun SOL sales) are market flow.
Loss: Not re-scored. Prior briefs carry $351.6M then the $387.5M recount of the same 24 Sep event.
Explorer URLs: Arkham cluster https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac. Bitget EVM first-hop https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee.
Status: Confirmed prior incident. Withdrawals still paused pending the published calendar. Full technical RCA unpublished.
Sources: https://x.com/bitget/status/2103695497458557342, https://x.com/bitget/status/2104164271248625776, https://x.com/GracyBitget/status/2103812967066439817, https://x.com/GoPlusSecurity/status/2104088981675925752
UPDATE — Limit Break payment processors / Magic Eden users — Ethereum and ApeChain
What happened (this window): No required-monitor post published a new official USD total. DefimonAlerts relayed several onchain messages dated into this slice: a 0.7724 WETH Payment Processor V2 sender-spoof claim with an 85/15 whitehat split offer; a MurMurCat #518 return offer after a Magic Eden-path theft; a request for return of 19 Persona Journey NFTs from 0x02dcd01d534477b5e76628a7284e7fa71c7a7ed7; a BrainDrops holder offering to return 152 tokens against a bounty and citing 0x5106115227b948e2a05138a3cd2451858f0cf5e2fc9f133ced106a9aea7fff00; and an earlier whitehat coordination note toward an address said to have front-run a copycat path for ~260 WETH. Those are victim and recovery correspondence, not a new protocol RCA. Processor addresses remain Ethereum V2 0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834 and ApeChain V3 0x9a1D00000000fC540e2000560054812452eB5366.
Loss: Not re-scored. Prior window ~660 WETH (~$1.7M) plus listed NFT inventory.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834. Cited BrainDrops-related transaction https://etherscan.io/tx/0x5106115227b948e2a05138a3cd2451858f0cf5e2fc9f133ced106a9aea7fff00. Prior cited theft https://etherscan.io/tx/0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf.
Status: Active user-side revoke. Redistribution of whitehat-rescued NFTs still described as in process in prior-window 0xQuit language.
Sources: https://x.com/DefimonAlerts/status/2104131353180516762, https://x.com/DefimonAlerts/status/2104057617911808002, https://x.com/DefimonAlerts/status/2104007039814955345, https://x.com/DefimonAlerts/status/2104049617344024744
Also noted
- Required-monitor silence on new protocol drains: CertiKAlert, PeckShieldAlert, Phalcon_xyz, BlockSecTeam, and CyversAlerts had no in-window first-report smart-contract drain posts in this sweep. SlowMist_Team’s visible in-window item was an OKX partnership note, not an incident hash.
- Duelbits ~$6M suspicious outflows (UNVERIFIED, prior window): Still no operator confirmation. Not scored. Source remains https://x.com/CertiKAlert/status/2103087558519624189.
- DPRK attribution on Bitget (unverified): Unchanged. GoPlus restated “highly likely” on-chain and IP-pattern layers; Bitget has not published a closed technical basis. ZachXBT’s prior “exploit by DPRK” wording is still not treated as confirmed RCA.
- Payy RollupV1 (~$1.83M): No new first-report hash this slice. Drain transaction remains https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814.
- Lookonchain non-exploit flow: ENA CEX withdrawals and Pump.fun SOL sales are market prints, not scored exploits.
- $2M DYORSWAP figure: Community / PublicAML / DeTracker estimate. Operator said “significant.” Flagged as unofficial on the card.
Sources & references
- https://x.com/GIWA_by_Upbit/status/2104091017901433017
- https://x.com/GIWA_by_Upbit/status/2104108336228843590
- https://x.com/DYORSWAPDEX/status/2104120544178344112
- https://x.com/DYORSWAPDEX/status/2104152247466872963
- https://x.com/DYORSWAPDEX/status/2104148047102103787
- https://x.com/Owlto_Finance/status/2104169915850908133
- https://x.com/bitget/status/2103695497458557342
- https://x.com/bitget/status/2104164271248625776
- https://x.com/GracyBitget/status/2103812967066439817
- https://x.com/GoPlusSecurity/status/2104088981675925752
- https://x.com/DefimonAlerts/status/2104131353180516762
- https://x.com/DefimonAlerts/status/2104057617911808002
- https://x.com/DefimonAlerts/status/2104007039814955345
- https://x.com/DefimonAlerts/status/2104049617344024744
- https://x.com/CertiKAlert/status/2103087558519624189
- https://x.com/zachxbt/status/2104159306736378111
- https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac
- https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee
- https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
- https://etherscan.io/tx/0x5106115227b948e2a05138a3cd2451858f0cf5e2fc9f133ced106a9aea7fff00
- https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
Editor’s note: First-report live-loss on this card is the unofficial ~$2M community estimate on the fake GIWA bridge path listed by DYORSWAP. Operator language is “significant,” not a signed total. Bitget and Limit Break are UPDATEs. Duelbits remains unverified. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
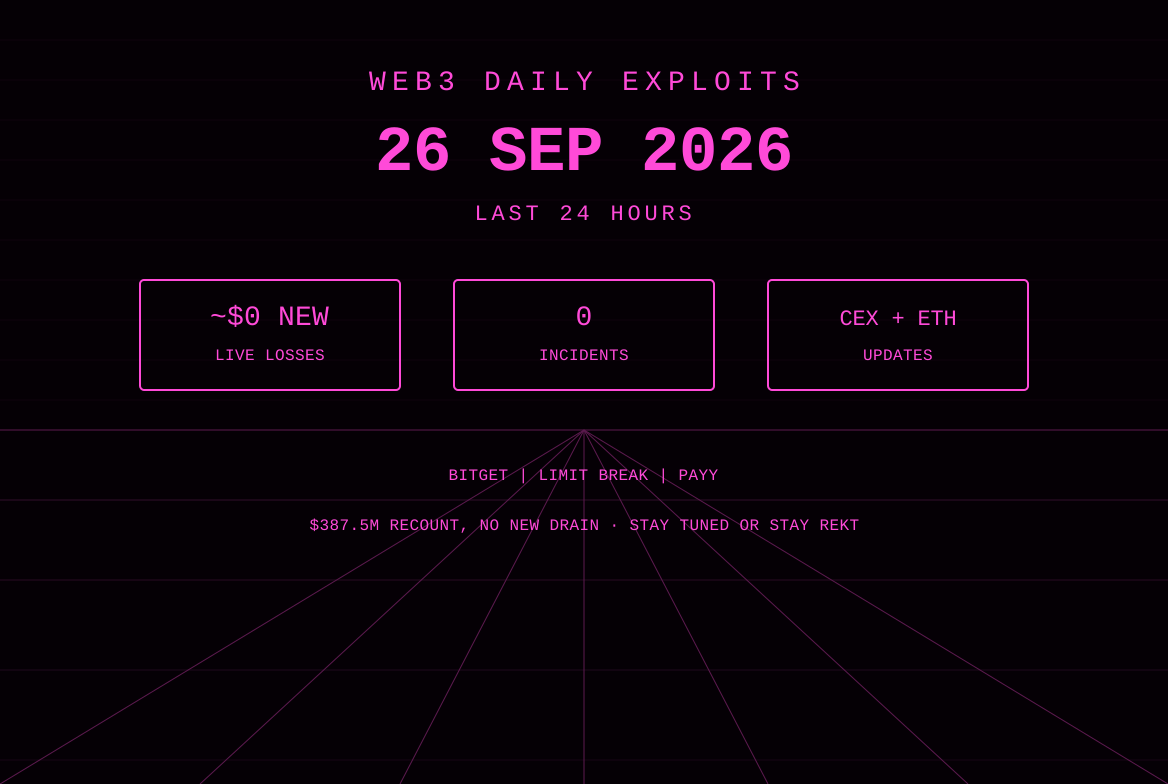
Web3 Daily Exploits — 26 Sep 2026: Bitget $387.5M Recount, No New Drain
No first-report protocol drain in this 26 Sep window after the required-monitor sweep. Bitget revised the 24 Sep hot/warm wallet incident from $351.6M to $387.5M (Zcash and TRON added; operator says not a second raid). GoPlus published a signing-pipeline analysis. Lookonchain flagged a $1.23M Binance withdrawal into the Bitget cluster. Limit Break / Magic Eden remains an UPDATE with victim outreach onchain. Payy and Duelbits stay prior-window.
Web3 Daily Exploits — 25 Sep 2026: Bitget $351.6M Hot Wallet Drain
First-report live-loss this window: Bitget confirmed unauthorized transfers from hot and warm wallets at 18:31 UTC on 24 Sep, estimated $351.6M. Lookonchain tracked multi-chain composition and ETH consolidation. Second scored item: Limit Break payment processors used by Magic Eden — GoPlus cites 660 WETH (~$1.7M) plus listed NFT collections. Duelbits ~$6M outflows remain unverified. Payy carried as UPDATE.
Web3 Daily Exploits — 24 Sep 2026: Payy $1.83M Rollup Verify Drain
First-report live-loss this window: Payy Network L1 rollup escrow drained ~$1.83M USDC in a single verifyRollup batch at 04:21 UTC on 24 Sep. Funds swapped to ~683 ETH and split. Required monitors also carried an UPDATE on Neutron/Astroport governance admin rewrite and an open RariGovernor proposal. Supply-chain TI: MemTensor MemoryOS PyPI/npm compromise.

Web3 Daily Exploits — 23 Sep 2026: Quiet Window + Rari & Astroport Updates
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live-loss scored ~$0. Material status items: RariGovernor malicious proposal remains open with ~2 days left; Astroport/Neutron admin-compromise incident continues with Cosmos Hub recovery of attacker ATOM holdings. Prior DoinGud ~$35K remains on the 22 Sep brief.