Web3 Daily Exploits — 23 Sep 2026: Quiet Window + Rari & Astroport Updates
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live-loss scored ~$0. Material status items: RariGovernor malicious proposal remains open with ~2 days left; Astroport/Neutron admin-compromise incident continues with Cosmos Hub recovery of attacker ATOM holdings. Prior DoinGud ~$35K remains on the 22 Sep brief.

Required monitors were checked through the 23 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. No new first-report smart-contract protocol drain with a fresh loss figure landed in this slice. Combined live-loss scored on this card is approximately $0. This is a quiet window for on-chain DeFi exploits after the 22 Sep cluster (DoinGud ~$35K offer-replay drain + RariGovernor attempted takeover).
Material status items first amplified or updated in the required-monitor and public on-chain discussion set during the window are the still-open RariGovernor proposal (vote remaining open) and continued recovery / containment activity around the Astroport–Neutron admin-privilege incident that triggered chain halts on Neutron and temporary measures on Cosmos Hub. Both are carried as status only; neither produced a new realized protocol live-loss figure scored on this card. Prior-day DoinGud, INT Base, and ASI key-cluster losses remain on their original briefs.
Rarible / RariGovernor — Ethereum — UPDATE (attempted, no funds moved)
What happened: First widely flagged by DefimonAlerts on 22 Sep (proposal submitted 20 Sep). Actor labeled “Falcon” (0x94223fcC…F04Ca, holding ~132.5K veRARI) submitted proposal 3648869205…835338 to RariGovernor. The single action calls the DAO’s delegatecall-executor with a minimal backdoor that performs a raw SSTORE into an AccessControl role slot, granting the proposer full control of the DAO if executed. Defimon follow-up on 22 Sep noted approximately three days remaining; as of the 23 Sep cutoff roughly two days remain and no execution has occurred.
Protocol / chain / asset: Ethereum. Rarible / RARI governance (RariGovernor). Proposal still open at time of report.
Loss: $0 realized. Execution would hand control of the DAO and any controlled treasury to the proposer. No transfer hashes located.
Attack type: Access-control / malicious governance proposal — DAO takeover via delegatecall + raw storage write. Not a classic smart-contract drain.
Status: Confirmed as an open malicious proposal by DefimonAlerts. Vote still open; no execution and no funds moved before cutoff. Community and token-holder response will determine whether the proposal can be defeated.
Sources: https://x.com/DefimonAlerts/status/2102348235650056597, https://x.com/DefimonAlerts/status/2102350161674478079
Astroport / Neutron — Cosmos ecosystem — UPDATE (admin compromise / chain halt)
What happened: On or about 22 Sep 2026 Astroport stated that an attack on the Neutron chain may have resulted in unauthorized access to its contract admin privileges. Neutron suspended on-chain activity for investigation; Astroport advised users to withdraw liquidity from all Astroport pools. Related discussion and on-chain analysis continued into 23 Sep, including Cosmos Hub measures to move attacker-held ATOM (~1.23M ATOM already on the address at halt, plus a pending THORChain refund of ~169k ATOM) into a recovery multisig and to block further signing from the attacker address. Final loss figures for Astroport pools and any recovered amounts remain under reconciliation and are not scored as a new live-loss total on this card.
Protocol / chain / asset: Neutron (Cosmos) and related IBC / Hub activity. Astroport DEX contracts; ATOM holdings tracked on Cosmos Hub.
Loss: No new confirmed realized protocol live-loss figure published by the required-monitor set in this 24h slice for scoring on this card. Earlier SlowMist-indexed references to Astroport and related Drop activity on 22 Sep are treated as status pending final on-chain reconciliation.
Attack type: Admin / privilege compromise leading to chain-level halt and governance-style recovery actions. Details of the precise privilege-acquisition path remain under investigation by the community and chain operators.
Status: Neutron halted for investigation; Cosmos Hub recovery steps (multisig sweep + ante-handler block) publicly discussed. Users advised to withdraw liquidity. Final loss and recovery still open.
Sources: Public Astroport / Neutron statements and on-chain recovery notes circulating 22–23 Sep; independent analyst threads summarizing Hub recovery of attacker ATOM.
Also noted
- DoinGud Polygon offer-replay (UPDATE, not re-scored): ~$35K primary remains on the 22 Sep brief. No return hash located in required monitors.
- INT Base arbitrary mint (UPDATE, not re-scored): ~$265K primary remains on the 21 Sep brief.
- Fetch / NuNet / ASI key cluster (UPDATE, not re-scored): ~$2.1M+ primary FET + NTX (and subsequent AGIX/WMTX activity) remain on the 20 Sep brief.
- Supply-chain / malware advisories: SlowMist continued TI on recruitment-themed GitHub/Bitbucket poisoning (RoyalCity-style) and published analysis of the joint international WaterPlum / Contagious Interview report (30k+ machines, wallet theft). FATF gaming/gambling risk report analysis also published. Client/CI supply-chain and social-engineering vectors, not protocol smart-contract drains; recorded as advisory only.
- Lookonchain / ZachXBT / CertiKAlert / CyversAlerts / Immunefi / rekt.news / PeckShieldAlert / BlockSecTeam: market-flow, investigative, or no additional first-report smart-contract drain with a fresh loss figure beyond the 22 Sep cutoff in the required-monitor set.
Sources & references
- https://x.com/DefimonAlerts/status/2102348235650056597
- https://x.com/DefimonAlerts/status/2102350161674478079
- https://x.com/SlowMist_Team/status/2102322041219322134
- https://x.com/SlowMist_Team/status/2102333435289194687
- https://x.com/SlowMist_Team/status/2102299453738951048
- https://x.com/SlowMist_Team/status/2102663214467371449
- https://www.tally.xyz/gov/rari-foundation/proposal/36488692052016914439745168161174461535879155122114390075942503328866246835338
Editor’s note: Card live-loss is this window’s confirmed realized protocol drains only (~$0). Rari remains an open attempted takeover with $0 moved. Astroport/Neutron is recorded as an ongoing admin-compromise / chain-halt status item pending final reconciliation. Prior-day DoinGud, INT and ASI items remain on their original briefs and are carried as status only. Malware and recruitment phishing advisories are recorded as confirmed TI, not protocol loss figures. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
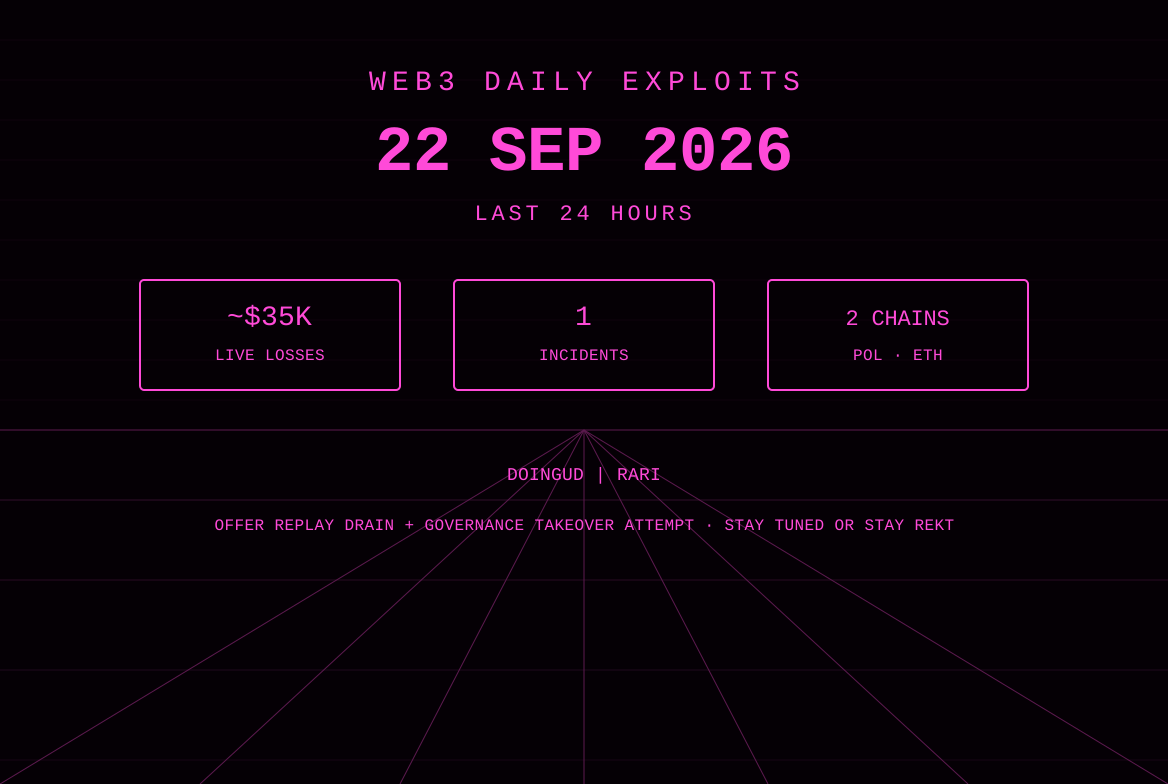
Web3 Daily Exploits — 22 Sep 2026: DoinGud ~$35K + Rari Gov Attempt
Required monitors flagged one confirmed smart-contract drain and one attempted governance takeover in the last 24 hours: DoinGud on Polygon lost ~$35K USDC via a missing offer-deletion replay bug in its Diamond acceptOffer path; Rarible’s RariGovernor carries an open malicious proposal that would grant full DAO control via a delegatecall backdoor if executed. Combined live-loss scored ~$35K.
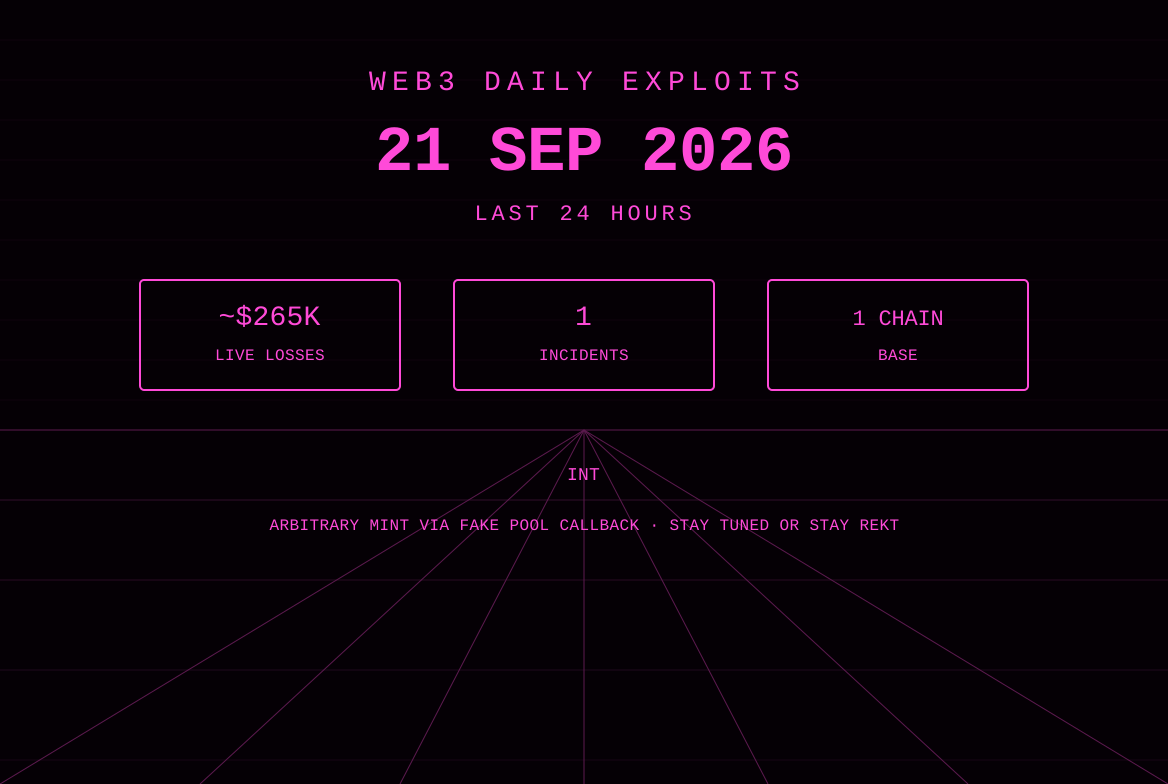
Web3 Daily Exploits — 21 Sep 2026: INT Base Arbitrary Mint ~$265K
Required monitors flagged one first-report smart-contract drain in the last 24 hours: Internet Token ($INT) on Base suffered an arbitrary-mint via an unvalidated Uniswap V3 pool callback in LiquidityUnifier, allowing a no-capital attacker to mint ~925M INT, dump for 5.85 WETH, and retain ~764M INT. Combined live-loss scored ~$265K at report-time pricing. ASI key-cluster updates remain on the 20 Sep brief.
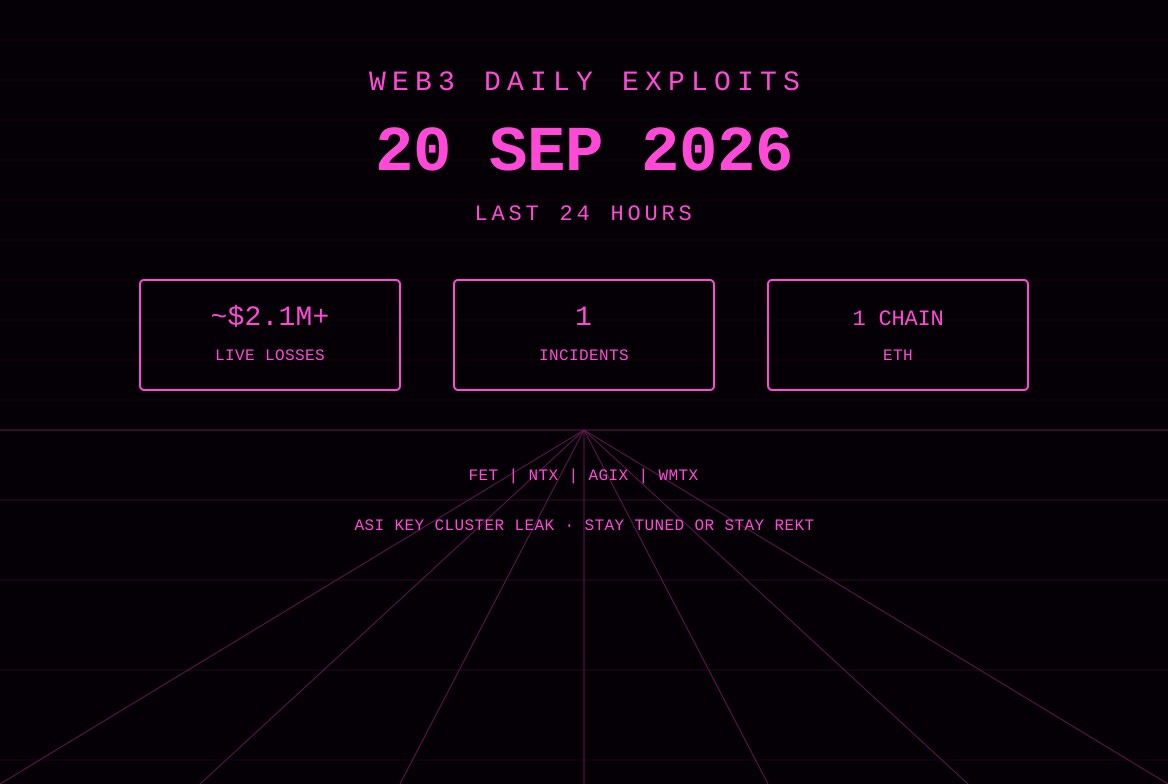
Web3 Daily Exploits — 20 Sep 2026: Fetch/NuNet/ASI Leaked Keys ~$2.1M+
Leaked privileged private keys enabled the same attacker cluster to drain ~8.72M FET (~$1.53–1.56M) from Fetch.ai’s TokenConversionManagerV3, mint ~408.5M NTX (~$450–463k) via NuNet’s deployer, and unauthorized-mint large AGIX + WMTX quantities on SingularityNET/World Mobile. Combined primary loss ~$2.1M+; attacker holdings later marked ~$16.8M by PeckShield.
Web3 Daily Exploits — 19 Sep 2026: Quiet Window + FomoPeek Malware
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live loss on this card is ~$0. SlowMist and OKX flagged FomoPeek App v1.1–1.2 as containing iOS kernel exploits capable of Keychain and private-key theft. Prior Nostra ~$3.5M, Nimiq ~$50k and Likwid remain on the 18 Sep brief.