Web3 Daily Exploits — 26 Sep 2026: Bitget $387.5M Recount, No New Drain
No first-report protocol drain in this 26 Sep window after the required-monitor sweep. Bitget revised the 24 Sep hot/warm wallet incident from $351.6M to $387.5M (Zcash and TRON added; operator says not a second raid). GoPlus published a signing-pipeline analysis. Lookonchain flagged a $1.23M Binance withdrawal into the Bitget cluster. Limit Break / Magic Eden remains an UPDATE with victim outreach onchain. Payy and Duelbits stay prior-window.
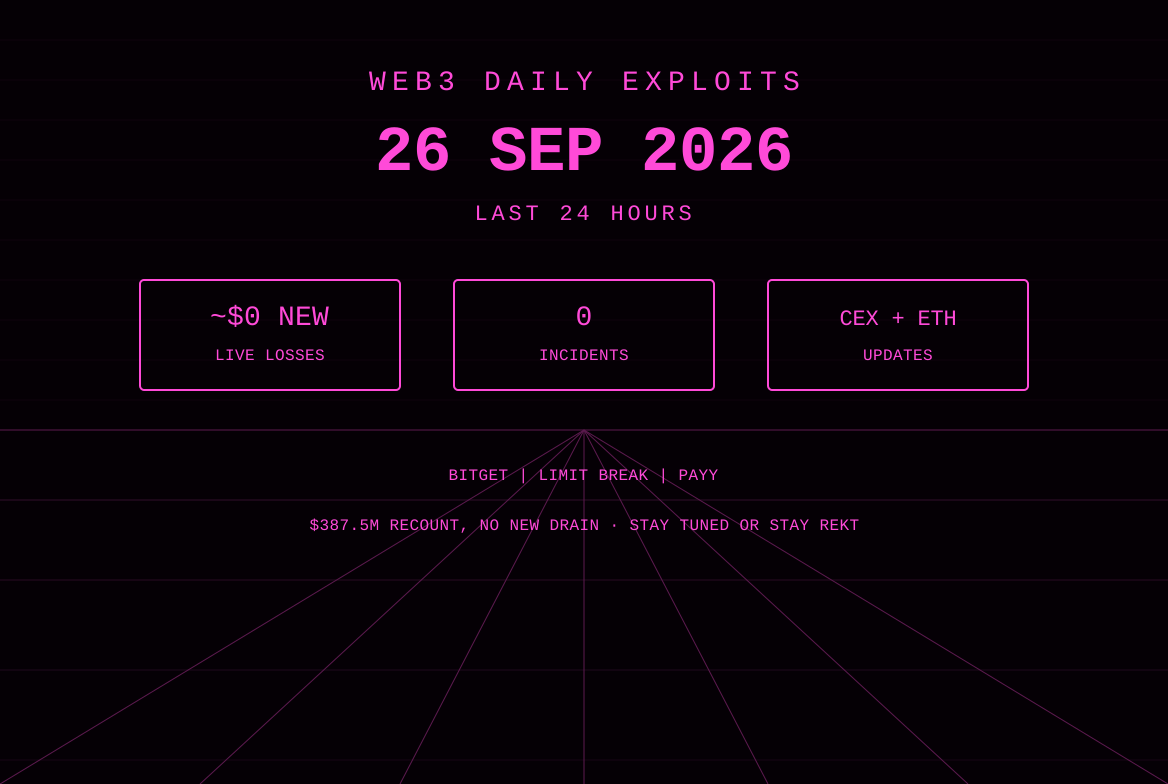
Required monitors were checked through the 26 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. After that account check: this is a quiet first-report window. No new smart-contract protocol drain with a fresh, independently confirmed live-loss figure was published in the required-monitor set. Card live-loss for new incidents is therefore $0 and incident count is 0. Material work in the last 24 hours is UPDATE traffic on the 24 Sep Bitget exchange incident and continued Limit Break / Magic Eden approval fallout.
Bitget’s official channel revised the affected-asset estimate from approximately $351.6 million to approximately $387.5 million. The operator stated that the increase adds Zcash and TRON legs that were missing from the first count and that it is not a second unauthorized-transfer wave. GoPlusSecurity published a long-form status and structural analysis on 26 Sep, arguing the break sat in the transaction-signing trust chain rather than a leaked private key, and listed additional first-hop addresses. Lookonchain separately reported that wallet 0x4885 withdrew about $1.23 million from Binance and sent the resulting ETH into a wallet already labeled as the Bitget cluster. Limit Break Payment Processor exposure remains active as a user-side revoke problem; DefimonAlerts relayed an onchain message from a victim seeking to repurchase NFTs sold through Blur after the 25 Sep drain path. Payy and Duelbits are carried only as prior-window items. DPRK attribution remains labeled unverified on this desk.
UPDATE — Bitget Exchange — multi-chain CEX hot/warm wallets — recount ~$387.5M
What happened (this window): First confirmation and the $351.6 million headline were scored on the 25 Sep brief. In this window Bitget posted an important-update thread stating that, based on later on-chain tracing and classification, assets equivalent to approximately $387.5 million were transferred to attacker-controlled addresses across multiple networks. The revised figure, Bitget wrote, reflects a more complete accounting of transfers that occurred during the original incident, adding affected assets on Zcash and TRON that were not in the initial estimate. The operator said the incident remains contained and that no further unauthorized transfers are possible. Withdrawals were still described as temporarily paused in that official update while additional checks and remediation continued. CEO Gracy Chen separately clarified that a withdrawal status/timing announcement was targeted by 26 Sep 04:00 UTC.
GoPlusSecurity on 26 Sep restated the $387.5 million figure and published a timeline that begins at 18:31 UTC on 24 Sep (attacker receive address funded with 0.84 ETH for gas from a Bitget hot wallet already under attacker control), first large out around 18:58 (~$34.75 million USDT), a largest wave around 19:16 (~$185 million in about a minute, including 13,966 ETH, ~91.4 million XRP, and 20.6 million TRX in that write-up), and a multi-chain drain window through about 21:23 UTC. GoPlus said Bitget later described root-cause work and system fixes as done and began reopening withdrawals on 26 Sep; that reopen claim is GoPlus’s status language, not a second Bitget primary source located in this sweep, and is recorded as such.
GoPlus argued this was not a private-key leak. The published thesis is that attackers caused Bitget’s own signing stack to produce valid signatures for transfers the exchange did not intend, a structural analogue (front-end versus back-end) to the 2025 Bybit Safe-signing UI case. Possible initial paths listed by GoPlus were explicitly labeled speculation pending an official technical report: withdrawal-database tampering, forged or replayed internal API calls, injection into a backend-to-signer queue, or a whitelist / address-map swap. This brief does not adopt any of those paths as confirmed RCA. Bitget’s earlier notices said the firm would not speculate on attack vector while the investigation with Mandiant and SlowMist remained open. SlowMist in this window posted a general note about working with OKX on ecosystem security; that is not a Bitget RCA.
Lookonchain on 26 Sep reported that wallet 0x4885 withdrew 257.6 ETH (~$692K) and 545K USDT from Binance, swapped the USDT for 200.2 ETH, then transferred 457.9 ETH (~$1.23M) to a wallet Lookonchain identified as the Bitget hacker. That print is post-incident movement, not a new CEX drain, and is not added to card live-loss.
Protocol / chain / asset: Centralized exchange custody. Bitget listed primary attacker-controlled receiving addresses in the recount post: EVM 0x770b10b273fc44fe9197d6bf20f145c2e98463ee, XRP rwNhefsz1UQEusxhCvHip3RANinWi4CTck, ZEC t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG, TRON TBWNguTTgezw9dVorX441C6nDrZpRxYwKD. Confirmed affected assets named by Bitget: XRP, ETH, USDT, ZEC, USDC, USDT0, XAUt, BNB, AVAX, and TRX. GoPlus additionally listed first-hop EVM addresses including 0xA6dD3F218B65E32Ccc37BE30f74884133c655545, 0xD2C2f029eFF5caCc686F24377CfdDcfc82d9F899, 0x600cfeDc6Bd65Fa79B604dC44964f419e45784b2, 0x94A43df7687A8494948Be937400e9d5D33135DA0, and 0x7c96279Ec1e888Aa56b9B836e0dB26ca48573E1C, and said related addresses were approaching 900 as splitting continued.
Loss: Operator recount ~$387.5 million for the original 24 Sep window. This card does not treat the +$35.9 million delta as a new live-loss incident. The 25 Sep brief scored $351.6 million. The delta is a classification update on the same event.
Attack type: Unauthorized hot/warm wallet transfers. Official RCA with a closed intrusion path is still unpublished. Signing-pipeline compromise is GoPlus analysis, not a Bitget-signed root-cause document. DPRK / Lazarus-style attribution circulated again (on-chain links cited by GoPlus to a July 2026 AFX case and to Bybit 2025 laundering addresses, plus an operator remark on VPN/IP patterns). Attribution is unverified on this card.
Explorer URLs: Arkham cluster from the prior brief https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac. EVM first-hop published by Bitget https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee. Individual drain hashes were not attached to Bitget’s recount post; this desk does not invent them. Lookonchain did not include a transaction hash in the $1.23M Binance-to-cluster post used here.
Status: Confirmed incident, revised notional. Investigation with Mandiant and SlowMist still described as ongoing in Bitget’s recount. Withdrawals paused in that official text. User Protection Fund coverage remains an operator statement. GoPlus said it blacklisted attacker-linked addresses and shared the set with partners.
Sources: https://x.com/bitget/status/2103485484165120005, https://x.com/GracyBitget/status/2103496589092491500, https://x.com/GoPlusSecurity/status/2103780874659791082, https://x.com/lookonchain/status/2103700414608892398, https://x.com/SlowMist_Team/status/2103389523850019137
UPDATE — Limit Break payment processors / Magic Eden users — Ethereum and ApeChain
What happened (this window): The revoke alert and GoPlus inventory (10 Meebits, 50 Otherdeeds, 10 World of Women, 235 Desperate ApeWives, 660 WETH / ~$1.7M) were first scored on 25 Sep. No required-monitor post in this slice published a new official USD total. DefimonAlerts relayed an onchain message dated into this window in which a victim stated that Sotheby’s Gen Art #78 and #153 were stolen on 25 Sep in the Limit Break Payment Processor exploit via transaction 0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf, then sold into Blur bids, and asked the current holder to sell them back at 1.15 ETH. That is victim-side correspondence, not a new protocol RCA. The two processor addresses remain: Ethereum V2 0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834 and ApeChain V3 0x9a1D00000000fC540e2000560054812452eB5366.
Loss: Not re-scored. Prior window ~660 WETH (~$1.7M) plus listed NFT inventory.
Attack type: Stale approvals against the payment-processor family. Exact vulnerability class still not specified in the required-monitor posts used here.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834. Cited theft transaction https://etherscan.io/tx/0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf.
Status: Active user-side containment (revoke). No Magic Eden reimbursement statement located in this sweep.
Sources: https://x.com/DefimonAlerts/status/2103805912007725503, https://x.com/GoPlusSecurity/status/2103433762847805524, https://x.com/0xQuit/status/2103396501779284239
UPDATE — Payy Network RollupV1 — Ethereum (~$1.83M already scored 24 Sep)
No new first-report hash or operator statement was located in PeckShieldAlert or Phalcon posts for this 26 Sep slice (those accounts returned no in-window hits in the keyword sweep). The 24 Sep drain transaction remains https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814. Not re-scored.
Also noted
- Quiet first-report day after the account check. CertiKAlert, Phalcon_xyz, PeckShieldAlert, BlockSecTeam, and CyversAlerts returned no in-window first-report protocol-drain posts in this sweep. Immunefi posts in the slice were bounty-payout marketing, not incident first reports. rekt.news had no fresh 26 Sep incident page located in search.
- Duelbits ~$6M suspicious outflows (UNVERIFIED, prior window): Still no operator confirmation. Not scored. Source remains https://x.com/CertiKAlert/status/2103087558519624189.
- DPRK attribution on Bitget (unverified): ZachXBT’s 25 Sep line still stands as the public remark that framed the incident as “the Bitget exploit by DPRK” while declining to monitor it. GoPlus called the link “highly likely” on three layers and noted Bitget has not published the technical basis. Recorded as unverified.
- DefimonAlerts other onchain mail: A separate message described an arbitrage bot that may have front-run an attack and offered to return funds against a possible 10% bounty; another was a user asking a presumed whitehat for help after a personal drain. Neither is a confirmed new protocol incident with a loss figure.
- Lookonchain non-exploit flow: AAVE whale sells, ENA perps, memecoin prints, and a $39.23M HYPE CEX-withdrawal cluster are market flow, not scored exploits.
Sources & references
- https://x.com/bitget/status/2103485484165120005
- https://x.com/GracyBitget/status/2103496589092491500
- https://x.com/GoPlusSecurity/status/2103780874659791082
- https://x.com/lookonchain/status/2103700414608892398
- https://x.com/DefimonAlerts/status/2103805912007725503
- https://x.com/GoPlusSecurity/status/2103433762847805524
- https://x.com/0xQuit/status/2103396501779284239
- https://x.com/SlowMist_Team/status/2103389523850019137
- https://x.com/zachxbt/status/2103364844368109792
- https://x.com/CertiKAlert/status/2103087558519624189
- https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac
- https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee
- https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
- https://etherscan.io/tx/0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf
- https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
Editor’s note: After the required account check this window has no new first-report live-loss. Card stats are $0 new / 0 incidents. Bitget’s $387.5 million figure is a recount of the 24 Sep CEX event already carried on yesterday’s brief. Limit Break and Payy are UPDATEs. Duelbits remains unverified. DPRK attribution is unlabeled as confirmed. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
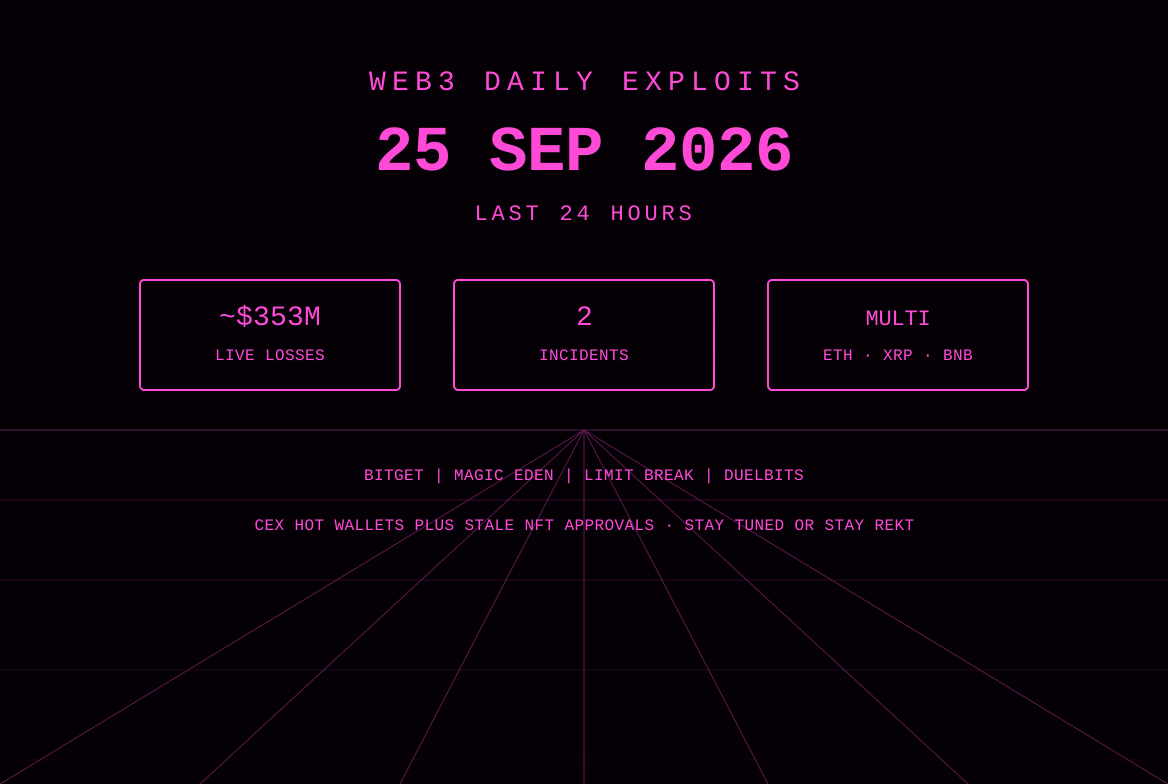
Web3 Daily Exploits — 25 Sep 2026: Bitget $351.6M Hot Wallet Drain
First-report live-loss this window: Bitget confirmed unauthorized transfers from hot and warm wallets at 18:31 UTC on 24 Sep, estimated $351.6M. Lookonchain tracked multi-chain composition and ETH consolidation. Second scored item: Limit Break payment processors used by Magic Eden — GoPlus cites 660 WETH (~$1.7M) plus listed NFT collections. Duelbits ~$6M outflows remain unverified. Payy carried as UPDATE.
Web3 Daily Exploits — 24 Sep 2026: Payy $1.83M Rollup Verify Drain
First-report live-loss this window: Payy Network L1 rollup escrow drained ~$1.83M USDC in a single verifyRollup batch at 04:21 UTC on 24 Sep. Funds swapped to ~683 ETH and split. Required monitors also carried an UPDATE on Neutron/Astroport governance admin rewrite and an open RariGovernor proposal. Supply-chain TI: MemTensor MemoryOS PyPI/npm compromise.

Web3 Daily Exploits — 23 Sep 2026: Quiet Window + Rari & Astroport Updates
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live-loss scored ~$0. Material status items: RariGovernor malicious proposal remains open with ~2 days left; Astroport/Neutron admin-compromise incident continues with Cosmos Hub recovery of attacker ATOM holdings. Prior DoinGud ~$35K remains on the 22 Sep brief.
Web3 Daily Exploits — 22 Sep 2026: DoinGud ~$35K + Rari Gov Attempt
Required monitors flagged one confirmed smart-contract drain and one attempted governance takeover in the last 24 hours: DoinGud on Polygon lost ~$35K USDC via a missing offer-deletion replay bug in its Diamond acceptOffer path; Rarible’s RariGovernor carries an open malicious proposal that would grant full DAO control via a delegatecall backdoor if executed. Combined live-loss scored ~$35K.