Web3 Daily Exploits — 25 Sep 2026: Bitget $351.6M Hot Wallet Drain
First-report live-loss this window: Bitget confirmed unauthorized transfers from hot and warm wallets at 18:31 UTC on 24 Sep, estimated $351.6M. Lookonchain tracked multi-chain composition and ETH consolidation. Second scored item: Limit Break payment processors used by Magic Eden — GoPlus cites 660 WETH (~$1.7M) plus listed NFT collections. Duelbits ~$6M outflows remain unverified. Payy carried as UPDATE.
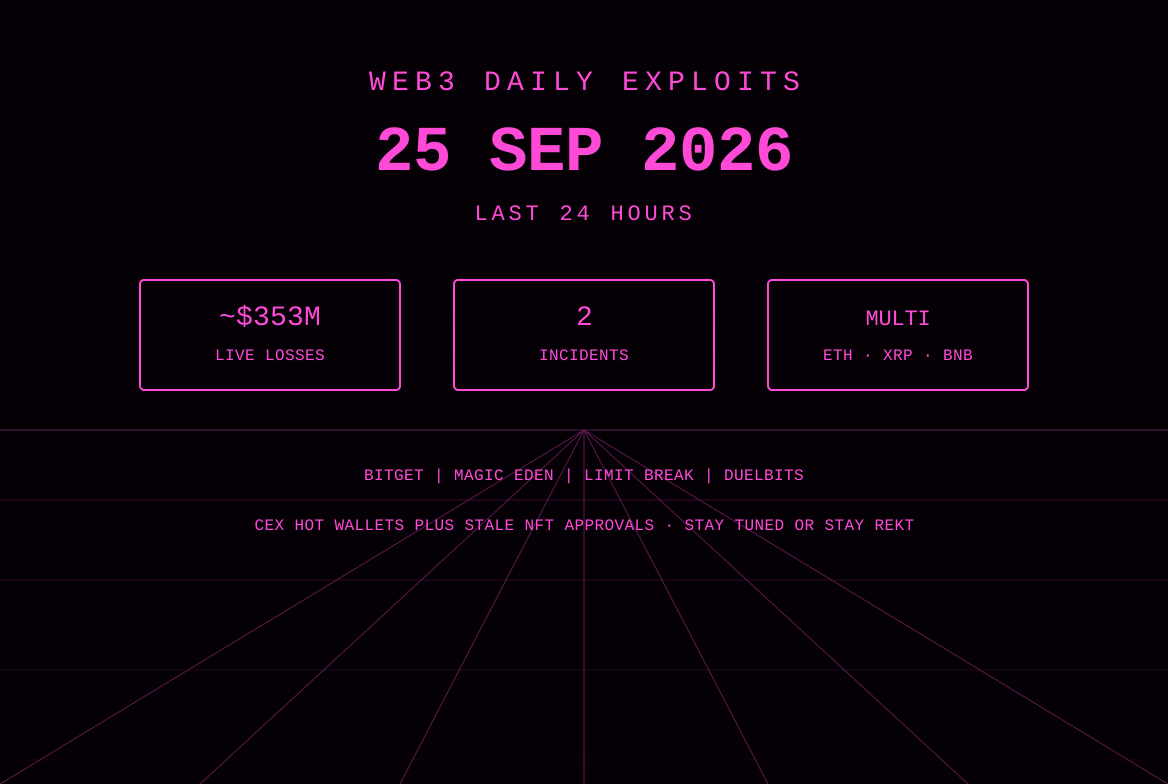
Required monitors were checked through the 25 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. This window is not quiet. Bitget publicly confirmed unauthorized transfers from a portion of its hot and warm wallet stack, detected at 18:31 UTC on 24 Sep, with an estimated $351.6 million affected. Lookonchain published a multi-asset breakdown and an Arkham entity for the cluster. Combined scored live-loss on this card is approximately $353 million: Bitget $351.6M plus Limit Break / Magic Eden 660 WETH (~$1.7M) as cited by GoPlusSecurity. Duelbits ~$6M of “suspicious outflows” is carried as unverified. Payy’s 24 Sep rollup drain remains on yesterday’s brief as UPDATE.
ZachXBT posted that he has no current plans to monitor the Bitget exploit and referenced a DPRK attribution in that remark; DPRK involvement is not treated as a confirmed root cause on this card. Bitget later named Mandiant and SlowMist as investigation partners and restated that user balances and the User Protection Fund cover the platform loss, while Bitget Wallet (self-custodial) was described as unaffected. Withdrawals on the exchange remained paused at cutoff.
Bitget Exchange — multi-chain CEX hot/warm wallets — ~$351.6M
What happened: Bitget CEO Gracy Chen published a security notice on 24 Sep 2026 stating that at 18:31 UTC the exchange’s security systems detected unauthorized transfers from some hot wallets. The notice estimated funds affected at approximately $351.6 million, said cold wallets remained fully secure, and described a three-tier architecture in which the breach was contained to a portion of the hot and warm layers. The exchange said the loss sits inside a User Protection Fund stated at more than $464 million, that account balances remain accurate, and that deposits and trading stayed open while withdrawals were paused pending review. A later official update named Mandiant and SlowMist as independent investigators and repeated that Bitget Wallet infrastructure is separate and was not affected.
Lookonchain independently labeled the event a hack of ~$351.6M and reported that the actor had already swapped most stolen funds on EVM chains for 67,982 ETH (~$183M at the time of that post). A follow-up Lookonchain inventory listed, among other line items: 102.93M XRP (~$157.48M), 31,890 ETH (~$85.75M), 34.75M USDT, 21.05M USDC, 19.67M USD₮0, 3,000 XAUt (~$12.82M), 12,719 BNB (~$9.88M), 821,012 AVAX (~$8.38M), and 20.59M TRX (~$7.07M). Those figures are on-chain tracker estimates at post time, not a Bitget-signed asset schedule. Lookonchain pointed at an Arkham entity page for the cluster.
GoPlusSecurity amplified the official confirmation the same evening. SlowMist publicly acknowledged working with Bitget. PeckShield’s in-window protocol alert set in the required monitors was still dominated by the prior Payy item rather than a separate Bitget first-hash thread located here.
Protocol / chain / asset: Centralized exchange custody, not a single smart-contract victim. Assets reported across EVM, XRP Ledger, BNB Chain, Avalanche, Tron, and stablecoin rails. Primary public figure is USD notional on mixed tokens, with a large ETH consolidation print from Lookonchain.
Loss: ~$351.6M estimated, matching Bitget’s official notice and Lookonchain’s headline. Card scores the official $351.6M as the realized CEX live-loss for this window. Individual token legs from Lookonchain are listed as tracker composition, not a second independent total.
Attack type: Unauthorized hot/warm wallet transfers. Official language does not publish a root-cause analysis in the notices cited here. Public commentary includes DPRK / Lazarus-style attribution; that attribution is unverified on this card. No exploit bytecode or spoofed-message proof is treated as confirmed vendor RCA.
Explorer URLs: Arkham cluster cited by Lookonchain https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac. Individual drain transaction hashes were not published in the Bitget CEO notice or the required-monitor first posts used for this brief; this desk does not invent hashes.
Status: Confirmed by the exchange. Withdrawals paused. Investigation with Mandiant and SlowMist underway. Full incident report was promised by Bitget within 24 hours of the first notice; a complete RCA with attack-vector detail was not located in the required-monitor set before this cutoff. User-fund coverage is an operator statement, not an on-chain recovery.
Sources: https://x.com/GracyBitget/status/2103235655879074084, https://x.com/bitget/status/2103381494056288658, https://x.com/lookonchain/status/2103268114603639155, https://x.com/lookonchain/status/2103290466116763936, https://x.com/GoPlusSecurity/status/2103264276492534234, https://x.com/SlowMist_Team/status/2103389523850019137, https://x.com/zachxbt/status/2103364844368109792
Limit Break payment processors / Magic Eden users — Ethereum and ApeChain — ~660 WETH (~$1.7M) plus NFTs
What happened: Researcher 0xQuit posted an urgent revoke notice for Limit Break Payment Processor V2 on Ethereum (0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834) and Payment Processor V3 on ApeChain (0x9a1D00000000fC540e2000560054812452eB5366). GoPlusSecurity amplified the same contracts and framed the issue for wallets that used Magic Eden on Ethereum when Limit Break was the settlement layer. GoPlus states that with an unrevoked approval an attacker can move NFTs and WETH without a new signature.
GoPlus listed confirmed stolen or unrecovered assets so far as: 10 Meebits, 50 Otherdeeds, 10 World of Women, 235 Desperate ApeWives, and 660 WETH (~$1.7M). That WETH figure is the only USD live-loss scored for this incident on the card. NFT collection counts are recorded as listed inventory, not separately marked-to-market here.
Protocol / chain / asset: Ethereum mainnet Payment Processor V2; ApeChain Payment Processor V3. Assets: WETH and multiple NFT collections. Exposure path is leftover token/NFT approvals, not a fresh Magic Eden frontend compromise confirmed in the required-monitor set.
Loss: 660 WETH (~$1.7M) plus the NFT set above, per GoPlus. Card scores ~$1.7M realized WETH. Collection-level USD marks from unofficial posts (some public replies cited multi-million NFT notions) are not adopted as a second official total.
Attack type: Stale unlimited / operator approvals against a payment-processor contract family after a vulnerability disclosure. Exact vulnerability class (arbitrary pull, signature bypass, or other) is not specified in the GoPlus or 0xQuit posts cited here and is not reconstructed.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834. ApeChain processor address as published: 0x9a1D00000000fC540e2000560054812452eB5366. Individual theft transaction hashes were not included in the GoPlus or 0xQuit alerts used for this brief.
Status: Active user-side containment (revoke). No official Magic Eden reimbursement statement located in the required-monitor set before cutoff. Ongoing risk for any wallet that still approves those two processors.
Sources: https://x.com/GoPlusSecurity/status/2103433762847805524, https://x.com/0xQuit/status/2103396501779284239
Duelbits wallets — multi-chain — ~$6M suspicious outflows (UNVERIFIED)
What happened: CertiKAlert reported that in the last few hours before that 24 Sep 11:42 UTC post there had been ~$6M of suspicious outflows from Duelbits wallets, and pointed at a February 2024 Duelbits incident (~$4.6M, possible private-key compromise) as precedent. Addresses published in the same thread: BSC/ETH 0xA77e24Fe29d16E051e487ef4Ea7b056cb05aef76, BTC bc1qhtu84kz3y94lvgl2t05zk84tqh57grvd82zvcl, SOL A3EBrhMBEGzcPgmbwywSPhW39G6PFGrorU8ib99T6yKw, Tron string as printed by CertiKAlert.
No Duelbits official confirmation was located in the required-monitor set. The item is not scored in the card live-loss total.
Loss: Not scored. CertiK figure ~$6M labeled suspicious.
Attack type: Unconfirmed. Historical analogue is private-key compromise; that is not a 2026 RCA.
Status: UNVERIFIED. Watch for operator confirmation or a second independent monitor with drain hashes.
Sources: https://x.com/CertiKAlert/status/2103087558519624189, https://x.com/CertiKAlert/status/2103087561963110552
Payy Network RollupV1 — Ethereum — UPDATE (~$1.83M already scored 24 Sep)
What happened: First reported on the 24 Sep brief. In this window Phalcon published an additional technical note: estimated losses around $1.93M in that post, and verifyRollup traces showing burn operations with all-zero burn_hash values. Phalcon said how those zero hashes passed verification remained unclear (circuit flaw versus privileged-infrastructure compromise) and that the team had not yet responded publicly at that time.
This brief does not re-score Payy as new live-loss. The 24 Sep card already carried ~$1.83M from PeckShield / Specter. Phalcon’s $1.93M is treated as the same incident cluster with a slightly different estimate, not a second drain.
Explorer URLs: Drain transaction from the 24 Sep brief https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814. Victim contract https://etherscan.io/address/0x367C1eAF14AA06b78ce76bd0243297de79d85270.
Sources: https://x.com/Phalcon_xyz/status/2103114775324733816, https://x.com/PeckShieldAlert/status/2103041942405960096
Also noted
- DPRK attribution on Bitget (unverified): ZachXBT’s 25 Sep post declined to monitor “the Bitget exploit by DPRK.” Secondary news posts repeated North Korea as a possible vector. Bitget’s own notices said they would not speculate on attack vector until the investigation finished. Recorded as unverified attribution.
- MemTensor MemoryOS supply-chain (UPDATE, advisory): SlowMist TI on 24 Sep remains valid: MemoryOS 2.0.34 (PyPI) and memtensor/memos-cloud-openclaw-plugin 0.1.21 / 0.1.23 / 0.1.25 (npm). Not a scored DeFi drain. Source: https://x.com/SlowMist_Team/status/2103060648800518552.
- Neutron / Astroport governance (UPDATE, not re-scored): Still the 22 Sep cluster. No new first-report live-loss hash in this window.
- RariGovernor proposal (UPDATE): No required-monitor post in this slice stated execution or treasury movement.
- DefimonAlerts / BlockSecTeam / CyversAlerts / Immunefi / rekt.news: no additional first-report smart-contract protocol drain with a fresh loss figure beyond the items above for this cutoff.
Sources & references
- https://x.com/GracyBitget/status/2103235655879074084
- https://x.com/bitget/status/2103381494056288658
- https://x.com/lookonchain/status/2103268114603639155
- https://x.com/lookonchain/status/2103290466116763936
- https://x.com/GoPlusSecurity/status/2103264276492534234
- https://x.com/GoPlusSecurity/status/2103433762847805524
- https://x.com/0xQuit/status/2103396501779284239
- https://x.com/SlowMist_Team/status/2103389523850019137
- https://x.com/zachxbt/status/2103364844368109792
- https://x.com/CertiKAlert/status/2103087558519624189
- https://x.com/Phalcon_xyz/status/2103114775324733816
- https://x.com/PeckShieldAlert/status/2103041942405960096
- https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac
- https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
- https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
Editor’s note: Card live-loss is this window’s confirmed realized figures only (~$351.6M Bitget official estimate plus ~$1.7M WETH on the Limit Break / Magic Eden approval path). Duelbits ~$6M is unverified and excluded from the card total. Payy remains on the 24 Sep brief. DPRK attribution is labeled unverified. Bitget user-fund coverage is an operator claim. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 24 Sep 2026: Payy $1.83M Rollup Verify Drain
First-report live-loss this window: Payy Network L1 rollup escrow drained ~$1.83M USDC in a single verifyRollup batch at 04:21 UTC on 24 Sep. Funds swapped to ~683 ETH and split. Required monitors also carried an UPDATE on Neutron/Astroport governance admin rewrite and an open RariGovernor proposal. Supply-chain TI: MemTensor MemoryOS PyPI/npm compromise.

Web3 Daily Exploits — 23 Sep 2026: Quiet Window + Rari & Astroport Updates
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live-loss scored ~$0. Material status items: RariGovernor malicious proposal remains open with ~2 days left; Astroport/Neutron admin-compromise incident continues with Cosmos Hub recovery of attacker ATOM holdings. Prior DoinGud ~$35K remains on the 22 Sep brief.
Web3 Daily Exploits — 22 Sep 2026: DoinGud ~$35K + Rari Gov Attempt
Required monitors flagged one confirmed smart-contract drain and one attempted governance takeover in the last 24 hours: DoinGud on Polygon lost ~$35K USDC via a missing offer-deletion replay bug in its Diamond acceptOffer path; Rarible’s RariGovernor carries an open malicious proposal that would grant full DAO control via a delegatecall backdoor if executed. Combined live-loss scored ~$35K.
Web3 Daily Exploits — 21 Sep 2026: INT Base Arbitrary Mint ~$265K
Required monitors flagged one first-report smart-contract drain in the last 24 hours: Internet Token ($INT) on Base suffered an arbitrary-mint via an unvalidated Uniswap V3 pool callback in LiquidityUnifier, allowing a no-capital attacker to mint ~925M INT, dump for 5.85 WETH, and retain ~764M INT. Combined live-loss scored ~$265K at report-time pricing. ASI key-cluster updates remain on the 20 Sep brief.