Web3 Daily Exploits — 24 Sep 2026: Payy $1.83M Rollup Verify Drain
First-report live-loss this window: Payy Network L1 rollup escrow drained ~$1.83M USDC in a single verifyRollup batch at 04:21 UTC on 24 Sep. Funds swapped to ~683 ETH and split. Required monitors also carried an UPDATE on Neutron/Astroport governance admin rewrite and an open RariGovernor proposal. Supply-chain TI: MemTensor MemoryOS PyPI/npm compromise.
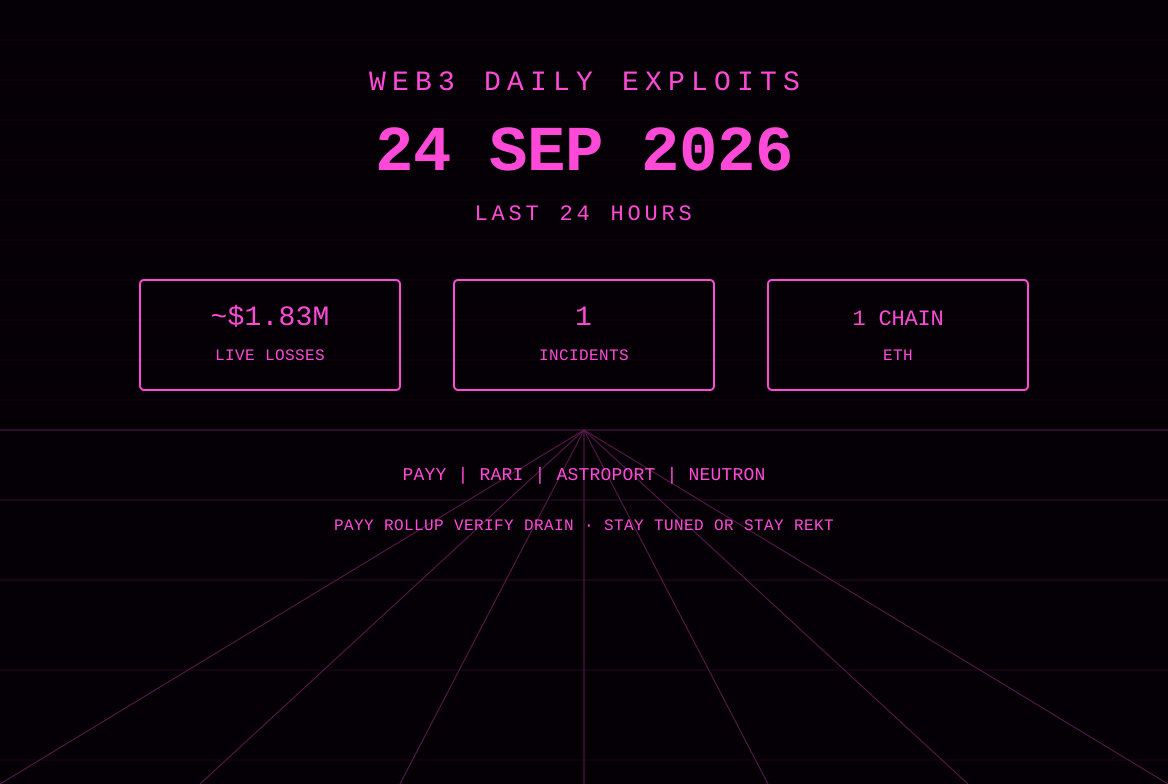
Required monitors were checked through the 24 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One new first-report protocol drain with a fresh realized loss figure landed in this slice: Payy Network's Ethereum L1 rollup contract released approximately 1.83 million USDC in a single verifyRollup call at 04:21 UTC on 24 Sep. Combined live-loss scored on this card is approximately $1.83M on Ethereum.
Material status items first amplified or updated in the required-monitor set during the window include a GoPlusSecurity breakdown of the 22 Sep Neutron governance / Astroport admin rewrite (notional ~$9.4M historically reported; not re-scored as a new first-report on this card) and the still-open RariGovernor malicious proposal from 22 Sep. SlowMist published a supply-chain TI alert on compromised MemTensor MemoryOS packages (PyPI and npm). Those items are carried as UPDATE or advisory only. Prior-day DoinGud ~$35K, INT Base, and ASI key-cluster losses remain on their original briefs.
Payy Network RollupV1 — Ethereum — ~$1.83M USDC
What happened: PeckShieldAlert, citing Specter, first flagged that Payy Network's rollup contract at 0x367C1eAF14AA06b78ce76bd0243297de79d85270 may have been drained of ~$1.83M in USDC. Independent on-chain write-ups in the same window (ExVul, public forensic threads quoting the PeckShield hash) describe a single L1 call to verifyRollup at block 26044909 (24 Sep 2026, 04:21:23 UTC) that released twelve USDC transfers. One transfer of 1,828,589 USDC went to 0xAa4985dBDaBfACa344237D40F7E06C4a0BB57E70. Total USDC leaving the contract in that transaction is reported around 1,832,149 USDC when including smaller companion transfers.
The transaction sender is reported as 0x5343b904bf837befb2f5a256b0cd5fbf30503d38, described by those write-ups as Payy's existing prover / operational key (high nonce, months of routine gas top-ups), not a fresh attacker EOA. Within about ninety-six seconds the bulk USDC is described as moving to an EIP-7702 delegated smart account, then swapped via a Uniswap X router into approximately 683.38 ETH, then split mainly as 200 ETH / 200 ETH / 280 ETH across three addresses. PeckShield's own alert used the same ETH-split figure.
ExVul's technical note, published after the PeckShield flag, argues that RollupV1 verifyRollup does not keep deposit accounting and has no withdrawal cap or pause: once a batch carries a valid proof and validator signature, it pays every burn message in the batch. Their reconstruction says the large withdrawal was the only one with an all-zero burn hash, that Payy's public circuits would not let a normal user produce a USDC withdrawal with a zero burn hash, and that the attacker only ever deposited 10 USDC on L1. They treat the root as either a compromised prover/validator setup or an aggregate proof that does not bind which inner circuit was verified. That mechanism read is an independent researcher reconstruction, not a Payy official post located in this window; it is recorded as analysis, not as a confirmed vendor RCA.
Protocol / chain / asset: Ethereum mainnet. Payy Network L1 rollup / escrow (RollupV1). Asset: USDC, then ETH after swap.
Loss: ~$1.83M realized USDC from the rollup escrow in the flagged transaction. PeckShield and follow-on monitors used ~$1.83M / 1,828,589 USDC as the primary figure. Remaining escrow was described by ExVul as about 96.8k USDC still in the rollup at time of their note — a residual balance, not additional confirmed theft in this slice.
Attack type: Rollup proof / operator-key path. Public analysis frames this as a validity-rollup batch that authorized a forged withdrawal rather than a classic AMM oracle or reentrancy drain. Whether the inner circuit was honest and the operator keys were taken, or the aggregate proof failed to bind the inner statement, is not settled by a project RCA in this window.
Explorer URLs: Drain transaction https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814. Victim contract https://etherscan.io/address/0x367C1eAF14AA06b78ce76bd0243297de79d85270. Recipient https://etherscan.io/address/0xAa4985dBDaBfACa344237D40F7E06C4a0BB57E70. Caller / reported prover key https://etherscan.io/address/0x5343b904bf837befb2f5a256b0cd5fbf30503d38.
Status: Confirmed as an on-chain outflow matching the PeckShield first-report. No official Payy incident post with a final RCA or user-reimbursement commitment was located in the required-monitor set before cutoff. Whether the smaller companion USDC transfers in the same batch were ordinary user withdrawals or attacker dust remains flagged unverified by public forensic threads. Operator-key rotation and any pause of further verifyRollup batches were recommended by independent analysts; execution of those steps is not confirmed here.
Sources: https://x.com/PeckShieldAlert/status/2103041942405960096, https://x.com/exvulsec/status/2103065252011397214, https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
Astroport / Neutron — Cosmos ecosystem — UPDATE (governance admin rewrite)
What happened: First widely acknowledged by Astroport on 22 Sep (Neutron halt; users told to withdraw liquidity). In this 24h window GoPlusSecurity published a structured breakdown: an attacker used Neutron governance proposal #9 (“AIATO: AI Agent Takeover”) to take admin on Astroport and Drop contracts via eleven MsgUpdateAdmin messages, then migrated contracts and called a malicious withdraw_all. GoPlus cites a notional ~$9.4M controlled at incident time, with ~$1.96M already bridged out in earlier reporting, and an economic-security mismatch (staked NTRN worth about $113K guarding those contract assets). Attacker paths listed in that thread include Neutron neutron1dd25c4sshelrpfs0433apg24c5phrhk8l6n605, Cosmos Hub cosmos1dd25c4sshelrpfs0433apg24c5phrhk8m96c4n, same-key derivatives on Noble / Axelar / dYdX / Osmosis, and Ethereum 0xe149310eB8b1b3D9C471CcD81819D393621fBA5c and 0xEF6c5A31df984c8569236a0AbC1f27580E2a5D54.
This brief does not re-score the historical notional as a new 24 Sep first-report live-loss. The 23 Sep card already carried the incident as status pending reconciliation. Today's addition is the GoPlus mechanism write-up and the public address set, not a new drain hash first seen today.
Protocol / chain / asset: Neutron (Cosmos) plus related IBC / Hub activity. Astroport DEX and Drop contracts. Mixed pool and bridged assets; ATOM recovery discussion continues on Cosmos Hub.
Loss: Not scored as new live-loss on this card. GoPlus notional ~$9.4M / ~$1.96M bridged remains an UPDATE figure from the 22 Sep incident cluster.
Attack type: Chain-level governance sitting above app-level admin (wasmd MsgUpdateAdmin), followed by malicious migrate and withdraw. Cheap voting power relative to controlled TVL is the economic note, not a separate exploit class.
Status: Ongoing containment / recovery. Neutron halt and Hub recovery steps were already public on 22–23 Sep. Final recovered versus realized totals still open.
Sources: https://x.com/GoPlusSecurity/status/2102737243760685263, https://x.com/astroport_fi/status/2102348511400403381
Rarible / RariGovernor — Ethereum — UPDATE (attempted, no funds moved)
What happened: First widely flagged by DefimonAlerts on 22 Sep. Actor labeled “Falcon” submitted a RariGovernor proposal whose single action would, if executed, write an AccessControl role slot via the DAO's delegatecall executor. As of the 23 Sep brief the vote was still open with roughly two days remaining and no execution. No DefimonAlerts, CertiKAlert, or PeckShield first-report in this 24h slice stated that the proposal executed or that treasury moved.
Loss: $0 realized on this card. Still an attempted governance takeover unless a later brief records execution.
Status: Carried as UPDATE. Holders and delegates should treat the Tally proposal as live until it is defeated, expired, or executed — that outcome is not confirmed here.
Sources: https://x.com/DefimonAlerts/status/2102348235650056597, https://www.tally.xyz/gov/rari-foundation/proposal/36488692052016914439745168161174461535879155122114390075942503328866246835338
Also noted
- MemTensor MemoryOS supply-chain (advisory, not protocol loss): SlowMist TI on 24 Sep reported that MemoryOS 2.0.34 on PyPI and memtensor/memos-cloud-openclaw-plugin 0.1.21 / 0.1.23 / 0.1.25 on npm ship cross-platform Go binaries that execute on import or gateway start. Potential collection of developer tokens, cloud keys, and prompt content, with exfil described toward infrastructure under skyleen[.]fr. Known-good pins cited: PyPI 2.0.33, npm 0.1.20. Recorded as confirmed TI, not a scored DeFi drain. Source: https://x.com/SlowMist_Team/status/2103060648800518552.
- FomoPeek / iOS kernel path (UPDATE, advisory): SlowMist continued public discussion of the earlier FomoPeek App Store poisoning and iOS kernel-exploitation investigation (Cointelegraph coverage of the joint work). Client malware, not a new protocol live-loss figure.
- Phalcon weekly roundup: BlockSec Phalcon published a Sep 14–20 weekly (~$11.3M that prior week, Nostra and related cases). Historical recap, not a 24 Sep first-report.
- DoinGud Polygon offer-replay (UPDATE, not re-scored): ~$35K primary remains on the 22 Sep brief.
- INT Base arbitrary mint (UPDATE, not re-scored): ~$265K primary remains on the 21 Sep brief.
- Fetch / NuNet / ASI key cluster (UPDATE, not re-scored): ~$2.1M+ primary remains on the 20 Sep brief.
- Lookonchain / ZachXBT / CertiKAlert / CyversAlerts / Immunefi / rekt.news / BlockSecTeam / DefimonAlerts: no additional first-report smart-contract protocol drain with a fresh loss figure beyond Payy in the required-monitor set for this cutoff. Immunefi activity in-window was competition / community, not an incident flag.
Sources & references
- https://x.com/PeckShieldAlert/status/2103041942405960096
- https://x.com/exvulsec/status/2103065252011397214
- https://x.com/GoPlusSecurity/status/2102737243760685263
- https://x.com/astroport_fi/status/2102348511400403381
- https://x.com/SlowMist_Team/status/2103060648800518552
- https://x.com/SlowMist_Team/status/2102967648636317839
- https://x.com/Phalcon_xyz/status/2102957387619680379
- https://x.com/DefimonAlerts/status/2102348235650056597
- https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
- https://etherscan.io/address/0x367C1eAF14AA06b78ce76bd0243297de79d85270
- https://www.tally.xyz/gov/rari-foundation/proposal/36488692052016914439745168161174461535879155122114390075942503328866246835338
Editor’s note: Card live-loss is this window’s confirmed realized protocol drain only (~$1.83M Payy USDC). Neutron/Astroport notional and bridged figures remain on the 22–23 Sep cluster and are not double-counted. Rari remains an open attempted takeover with $0 moved. MemTensor and FomoPeek items are supply-chain / client TI, not protocol loss figures. Payy mechanism details from ExVul and public forensic threads are labeled analysis until a project RCA lands. No official Payy reimbursement statement located before cutoff. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more

Web3 Daily Exploits — 23 Sep 2026: Quiet Window + Rari & Astroport Updates
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live-loss scored ~$0. Material status items: RariGovernor malicious proposal remains open with ~2 days left; Astroport/Neutron admin-compromise incident continues with Cosmos Hub recovery of attacker ATOM holdings. Prior DoinGud ~$35K remains on the 22 Sep brief.
Web3 Daily Exploits — 22 Sep 2026: DoinGud ~$35K + Rari Gov Attempt
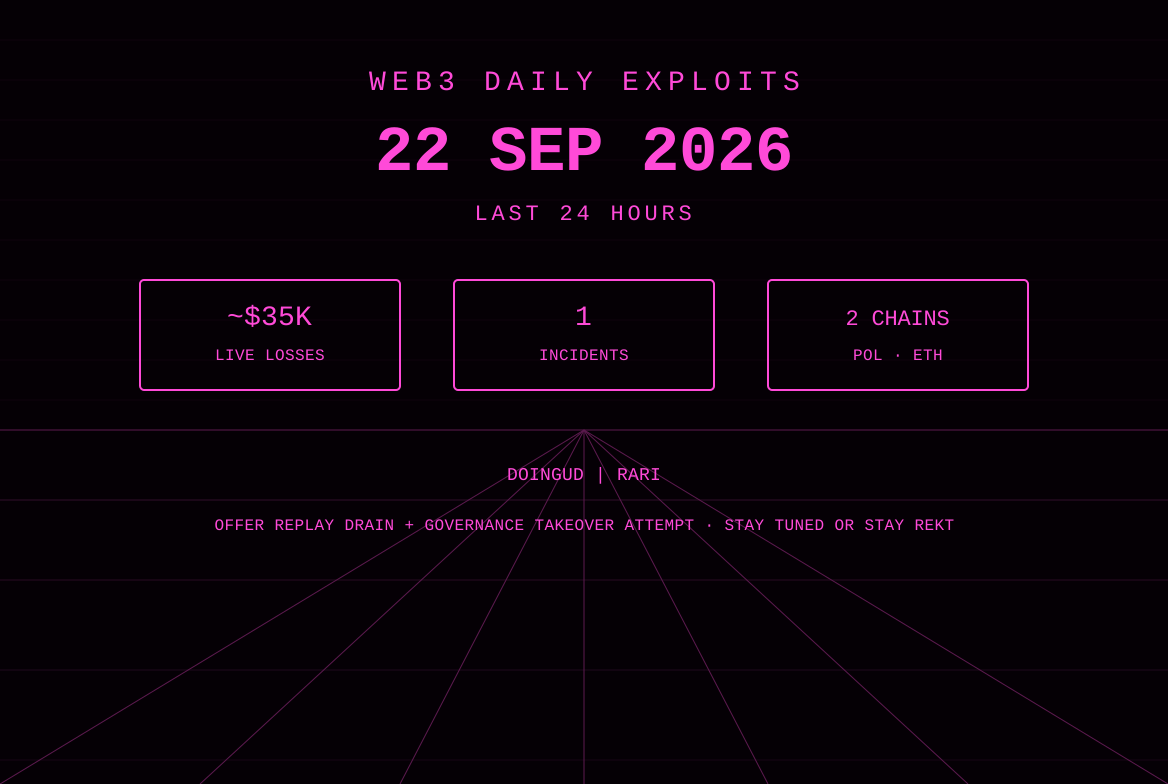
Required monitors flagged one confirmed smart-contract drain and one attempted governance takeover in the last 24 hours: DoinGud on Polygon lost ~$35K USDC via a missing offer-deletion replay bug in its Diamond acceptOffer path; Rarible’s RariGovernor carries an open malicious proposal that would grant full DAO control via a delegatecall backdoor if executed. Combined live-loss scored ~$35K.
Web3 Daily Exploits — 21 Sep 2026: INT Base Arbitrary Mint ~$265K
Required monitors flagged one first-report smart-contract drain in the last 24 hours: Internet Token ($INT) on Base suffered an arbitrary-mint via an unvalidated Uniswap V3 pool callback in LiquidityUnifier, allowing a no-capital attacker to mint ~925M INT, dump for 5.85 WETH, and retain ~764M INT. Combined live-loss scored ~$265K at report-time pricing. ASI key-cluster updates remain on the 20 Sep brief.
Web3 Daily Exploits — 20 Sep 2026: Fetch/NuNet/ASI Leaked Keys ~$2.1M+
Leaked privileged private keys enabled the same attacker cluster to drain ~8.72M FET (~$1.53–1.56M) from Fetch.ai’s TokenConversionManagerV3, mint ~408.5M NTX (~$450–463k) via NuNet’s deployer, and unauthorized-mint large AGIX + WMTX quantities on SingularityNET/World Mobile. Combined primary loss ~$2.1M+; attacker holdings later marked ~$16.8M by PeckShield.