Web3 Daily Exploits — 22 Sep 2026: DoinGud ~$35K + Rari Gov Attempt
Required monitors flagged one confirmed smart-contract drain and one attempted governance takeover in the last 24 hours: DoinGud on Polygon lost ~$35K USDC via a missing offer-deletion replay bug in its Diamond acceptOffer path; Rarible’s RariGovernor carries an open malicious proposal that would grant full DAO control via a delegatecall backdoor if executed. Combined live-loss scored ~$35K.
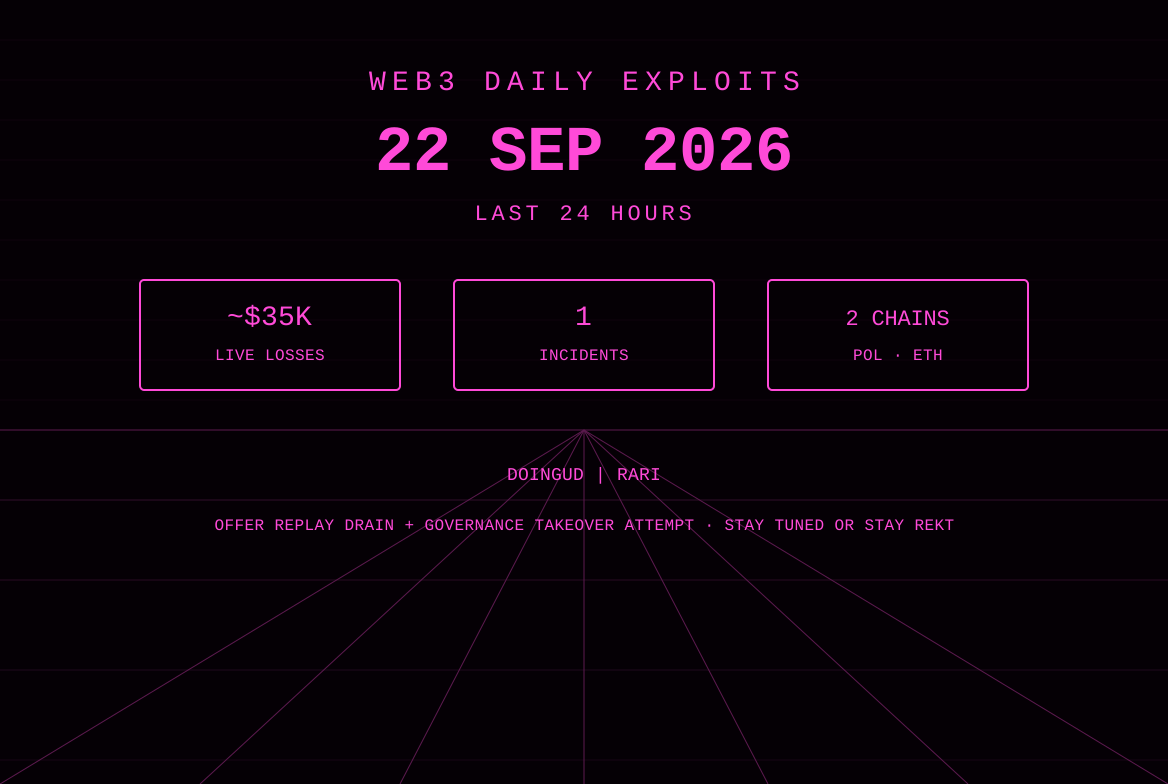
Required monitors were checked through the 22 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One material first-report smart-contract drain and one high-visibility attempted governance takeover landed in this slice. DoinGud (NFT platform) on Polygon suffered a replay of acceptOffer that drained the escrow of its remaining USDC balance; the attacker netted ~35,380 USDC after a flash-loan premium. Separately, Defimon surface of an open RariGovernor proposal that, if executed, would grant the proposer full control of the Rarible DAO via a raw SSTORE through a delegatecall executor. No funds moved on the Rari side before cutoff. Prior INT Base arbitrary mint (~$265K) and ASI key-cluster losses remain on the 21 and 20 Sep briefs and are not re-scored.
All dollar figures below are amounts still outside the affected parties’ control unless a return transaction is cited. Final reconciliation of any recovery remains open.
DoinGud — Polygon — Confirmed
What happened: On or about 21–22 Sep 2026 an attacker exploited the DoinGud Diamond implementation on Polygon. In acceptOffer (selector 0x5c924960) of Implementation 0x123aafc8d0a07ce1a146e53aa899e77f21a2dde1, after transferring offer.price USDC to msg.sender, the offer record is never deleted or zeroed — the swap-and-pop logic present in cancelOffer is missing. Additional missing guards (no offerer != msg.sender, no offerAmount > 0) and an amount=0 path that defeats _updateListingAfterTransfer cleanup allowed the same offer to be replayed with identical calldata, paying out the full price each time. Two replayed calls drained the contract’s entire escrow balance (70,973.871434 USDC outflow in one transaction); the attacker kept ~35,380 USDC after flash-loan costs, with zero NFT or principal transferred.
Protocol / chain / asset: Polygon. DoinGud NFT platform / Diamond bidding contracts. Vulnerable Implementation 0x123aafc8d0a07ce1a146e53aa899e77f21a2dde1. Attacker EOA 0xb8c717239bcace558c3a8dc471c16e07bf57a1eb / contract 0xe588834aa3161a0720e8f6bf223748d6098a4b76. Victim / escrow-related 0xe3a161edd679fc5ce2db2316a4b6f7ab33a8ed6a.
Loss: ~35,380 USDC realized by the attacker (~$35K). Full escrow outflow cited at ~70,974 USDC in the drain transaction; flash-loan premium and accounting closed the difference. No return hash located before cutoff.
Attack type: Logic error / missing state cleanup — offer replay via absent deletion after payout. Classic accounting bug compounded by missing access and amount checks.
Technical details: SlowMist TI described the exact flow: after the USDC transfer in acceptOffer the offer struct remains live; identical calldata can be re-submitted. An amount=0 input also skips the listing-update cleanup path. The sequence was funded by flash loan and executed in a single transaction path that emptied the escrow. Independent on-chain analysis (clarahacks / teddyctf notes) confirmed the accounting closes exactly and that a live offer record still claims residual USDC after the drain.
Explorer links:
- Attacker EOA: https://polygonscan.com/address/0xb8c717239bcace558c3a8dc471c16e07bf57a1eb
- Attacker contract: https://polygonscan.com/address/0xe588834aa3161a0720e8f6bf223748d6098a4b76
- Vulnerable Implementation: https://polygonscan.com/address/0x123aafc8d0a07ce1a146e53aa899e77f21a2dde1
- Victim / related: https://polygonscan.com/address/0xe3a161edd679fc5ce2db2316a4b6f7ab33a8ed6a
Status: Confirmed by SlowMist TI Alert. Independent on-chain notes corroborate the replay and residual offer state. No official DoinGudHQ statement or pause located in the required-monitor set before cutoff. Final loss and any recovery still open.
Sources: https://x.com/SlowMist_Team/status/2102322041219322134, https://x.com/clarahacks/status/2102342437947441278
Rarible / RariGovernor — Ethereum — Attempted (no funds moved)
What happened: On 20 Sep 2026 (first widely flagged by Defimon on 22 Sep) an actor labeled “Falcon” (0x94223fcC…F04Ca, holding ~132.5K veRARI votes, above the 5,000 proposalThreshold) submitted proposal 3648869205…835338 to RariGovernor (0x859e1c00…2edca). The single action calls the DAO’s delegatecall-executor 0xb23BCD4F…C5b5 with execute(0x36224b869…a722, write(slot,1)). Contract 0x36224 is a minimal backdoor whose only function performs a raw SSTORE; invoked via the executor’s DELEGATECALL it writes 1 into an AccessControl role slot of the executor, granting the proposer a privileged role and full control of the DAO. The proposal text explicitly states that a YES vote “grants full control of the DAO to the activist investor group Falcon.” Voting remains open; no funds have moved.
Protocol / chain / asset: Ethereum. Rarible / RARI governance (RariGovernor). Proposal still open at time of report (approximately three days remaining per Defimon follow-up).
Loss: $0 realized. Execution would hand control of the DAO and any controlled treasury to the proposer. No transfer hashes located.
Attack type: Access-control / malicious governance proposal — DAO takeover via delegatecall + raw storage write. Not a classic smart-contract drain; a governance path that, if executed, elevates the proposer to full control.
Technical details: Defimon described the payload as a four-line contract whose sole purpose is an SSTORE of 1 into a role slot when delegatecalled from the DAO executor. Because the proposal action is framed as an execute call on the existing executor, a successful vote would install the privilege without requiring a separate upgrade path. Tally link published by Defimon shows the proposal still live.
Explorer / governance links:
- Defimon alert: https://x.com/DefimonAlerts/status/2102348235650056597
- Tally proposal (per Defimon): https://www.tally.xyz/gov/rari-foundation/proposal/36488692052016914439745168161174461535879155122114390075942503328866246835338
Status: Confirmed as an open malicious proposal by DefimonAlerts. Vote still open; no execution and no funds moved before cutoff. Community and token-holder response will determine whether the proposal can be defeated.
Sources: https://x.com/DefimonAlerts/status/2102348235650056597, https://x.com/DefimonAlerts/status/2102350161674478079
Also noted
- INT Base arbitrary mint (UPDATE, not re-scored): ~$265K primary remains on the 21 Sep brief. Mint path status unchanged in required monitors.
- Fetch / NuNet / ASI key cluster (UPDATE, not re-scored): ~$2.1M+ primary FET + NTX (and subsequent AGIX/WMTX activity) remain on the 20 Sep brief.
- Supply-chain / malware advisories: SlowMist published additional TI on recruitment-themed GitHub/Bitbucket poisoning (RoyalCity-style tailwind.config.js payload) and a joint international report on North Korea-linked WaterPlum / Contagious Interview activity (30k+ machines, wallet theft). Client/CI supply-chain and social-engineering vectors, not protocol smart-contract drains; recorded as advisory only.
- TraderTraitor / Terraform provider malware (UPDATE): SlowMist / Sentinel Labs notes on weaponized .terraform.lock.hcl remain advisory.
- Lookonchain / ZachXBT / CertiKAlert / CyversAlerts / Immunefi / rekt.news / PeckShieldAlert / BlockSecTeam: market-flow, investigative, or no additional first-report smart-contract drain with a fresh loss figure beyond DoinGud in the required-monitor set after the 21 Sep cutoff.
Sources & references
- https://x.com/SlowMist_Team/status/2102322041219322134
- https://x.com/clarahacks/status/2102342437947441278
- https://x.com/DefimonAlerts/status/2102348235650056597
- https://x.com/DefimonAlerts/status/2102350161674478079
- https://x.com/SlowMist_Team/status/2102299453738951048
- https://x.com/SlowMist_Team/status/2102333435289194687
- https://polygonscan.com/address/0xb8c717239bcace558c3a8dc471c16e07bf57a1eb
- https://polygonscan.com/address/0x123aafc8d0a07ce1a146e53aa899e77f21a2dde1
- https://www.tally.xyz/gov/rari-foundation/proposal/36488692052016914439745168161174461535879155122114390075942503328866246835338
Editor’s note: Card live-loss is this window’s confirmed realized protocol drains only (~$35K DoinGud). The Rari governance proposal is recorded as an open attempted takeover with $0 moved. Prior-day INT and ASI items remain on their original briefs and are carried as status only. Malware and recruitment phishing advisories are recorded as confirmed TI, not protocol loss figures. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
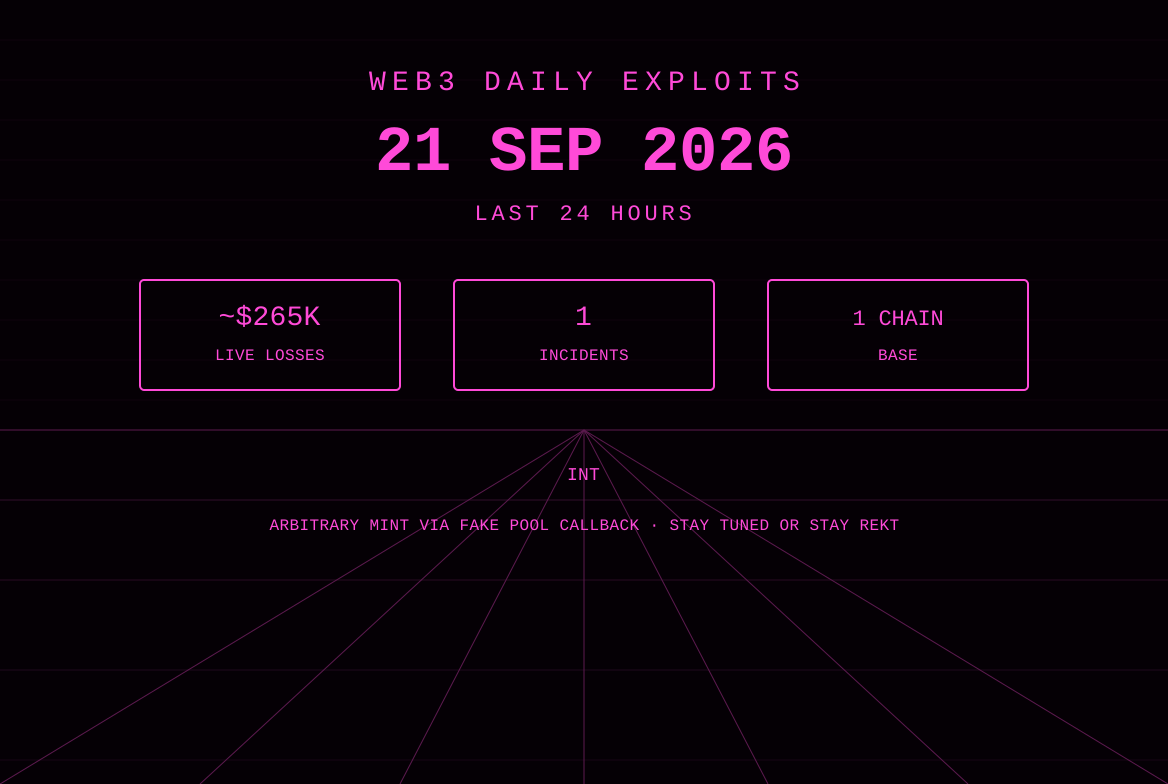
Web3 Daily Exploits — 21 Sep 2026: INT Base Arbitrary Mint ~$265K
Required monitors flagged one first-report smart-contract drain in the last 24 hours: Internet Token ($INT) on Base suffered an arbitrary-mint via an unvalidated Uniswap V3 pool callback in LiquidityUnifier, allowing a no-capital attacker to mint ~925M INT, dump for 5.85 WETH, and retain ~764M INT. Combined live-loss scored ~$265K at report-time pricing. ASI key-cluster updates remain on the 20 Sep brief.
Web3 Daily Exploits — 20 Sep 2026: Fetch/NuNet/ASI Leaked Keys ~$2.1M+
Leaked privileged private keys enabled the same attacker cluster to drain ~8.72M FET (~$1.53–1.56M) from Fetch.ai’s TokenConversionManagerV3, mint ~408.5M NTX (~$450–463k) via NuNet’s deployer, and unauthorized-mint large AGIX + WMTX quantities on SingularityNET/World Mobile. Combined primary loss ~$2.1M+; attacker holdings later marked ~$16.8M by PeckShield.
Web3 Daily Exploits — 19 Sep 2026: Quiet Window + FomoPeek Malware
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live loss on this card is ~$0. SlowMist and OKX flagged FomoPeek App v1.1–1.2 as containing iOS kernel exploits capable of Keychain and private-key theft. Prior Nostra ~$3.5M, Nimiq ~$50k and Likwid remain on the 18 Sep brief.
Web3 Daily Exploits — 18 Sep 2026: Nostra ~$3.5M + Nimiq ~$50k + Likwid
Nostra money market on Starknet lost ~$3.5M after NSTR oracle manipulation let one account over-borrow. Nimiq swap handlers on Polygon lost ~$50.4k via OpenGSN signature bypass. Likwid margin on BNB lost 74.31 BNB after a pair-reserve accounting bug. Combined live loss ~$3.6M.