Web3 Daily Exploits — 21 Sep 2026: INT Base Arbitrary Mint ~$265K
Required monitors flagged one first-report smart-contract drain in the last 24 hours: Internet Token ($INT) on Base suffered an arbitrary-mint via an unvalidated Uniswap V3 pool callback in LiquidityUnifier, allowing a no-capital attacker to mint ~925M INT, dump for 5.85 WETH, and retain ~764M INT. Combined live-loss scored ~$265K at report-time pricing. ASI key-cluster updates remain on the 20 Sep brief.
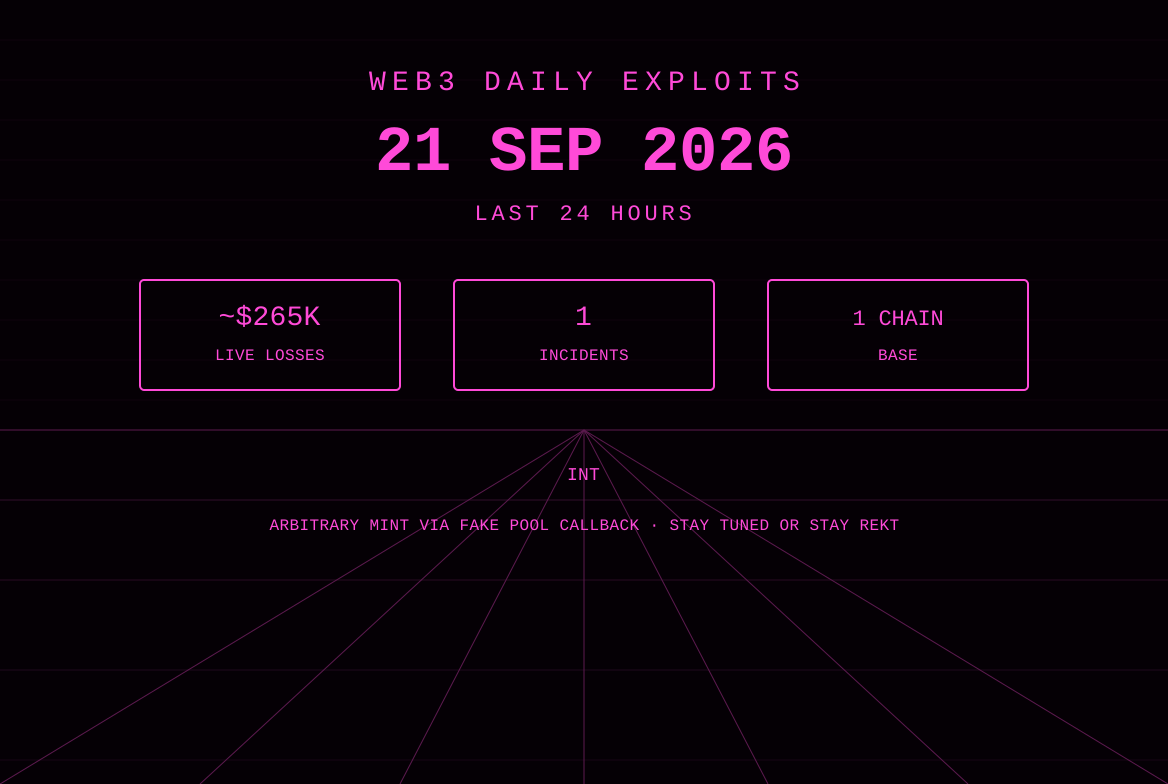
Required monitors were checked through the 21 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One material first-report smart-contract drain landed in this slice: Internet Token ($INT) on Base. LiquidityUnifier, which held the token’s MINTER_ROLE, exposed a permissionless swapV3 that accepted an attacker-supplied pool; a fake pool re-entered the uniswapV3SwapCallback to mint arbitrary amounts. The attacker minted ~925.4M INT, sold ~161M into the real INT/WETH Uniswap V3 pool for its entire 5.85 WETH, and retained ~764.1M INT. Defimon priced INT at ~$0.000328 at alert time, putting the retained bag plus extracted WETH near ~$265K. Mint rights remain open until revoked. Prior ASI ecosystem key-cluster losses (~$2.1M+ primary) stay on the 20 Sep brief and are not re-scored.
All dollar figures below are amounts still outside the affected parties’ control unless a return transaction is cited. Final reconciliation of minted supply and any recovery remains open.
Internet Token ($INT) — Base — Confirmed
What happened: On 21 Sep 2026 a no-capital attacker exploited LiquidityUnifier (0x837dbabc4f5fa78baf177597edbda09645822032), the contract holding MINTER_ROLE on the INT token. The function swapV3(token, pool) accepted a caller-supplied pool address. Validation only confirmed the pool had code, was not on an exclusion list, and that its token0()/token1() returned INT (and the supplied token). The attacker deployed a fake “pool” that returned INT for both sides, called swapV3, and on the re-entrant uniswapV3SwapCallback (checked only against the stored currentPoolV3) minted an attacker-chosen amount. A Convertor round-trip inside the same transaction defeated the validateSupply check that required supply not to increase across the call. Approximately 925.4M INT were minted; ~161.3M were dumped into the real INT/WETH Uniswap V3 pool, extracting its entire 5.85 WETH; the attacker retained ~764.1M INT.
Protocol / chain / asset: Base. Internet Token (INT, 0x968d6a288d7b024d5012c0b25d67a889e4e3ec19). Vulnerable LiquidityUnifier 0x837dbabc4f5fa78baf177597edbda09645822032. Attacker EOA 0x5f7ce6395818857ac20730dc990f614356d1ec68.
Loss: ~764M INT retained + 5.85 WETH extracted. At Defimon alert-time pricing of ~$0.000328 per INT the retained bag alone was ~$250K; 5.85 WETH at prevailing ETH (~$2,700) added ~$15–16K, for a combined primary mark of ~$265K. Subsequent price collapse of INT (to the low $0.00003 range on Basescan holdings) reduced the on-paper value of the remaining bag; card live-loss uses the report-time figure. No return hash located before cutoff.
Attack type: Access-control / logic error — arbitrary mint via unvalidated Uniswap V3-style pool callback. Not a classic reentrancy on a vault; the mint path itself was permissionless once a fake pool was supplied.
Technical details: ExVul and Defimon independently described the same flow. LiquidityUnifier’s swapV3 set currentPoolV3 = attacker pool and invoked pool.swap(). The fake pool’s callback satisfied the sole msg.sender == currentPoolV3 guard and called the mint function with an attacker-chosen amount. validateSupply (“supply cannot increase”) was bypassed by routing freshly minted INT through the project’s Convertor (reducing measured supply) and converting back after the check. The entire sequence ran inside a one-shot contract constructor. As of the monitor reports the mint role on LiquidityUnifier had not yet been revoked; both alerts warned against buying or providing liquidity to $INT until rights are removed.
Explorer links:
- Attacker: https://basescan.org/address/0x5f7ce6395818857ac20730dc990f614356d1ec68
- INT token: https://basescan.org/token/0x968d6a288d7b024d5012c0b25d67a889e4e3ec19
- LiquidityUnifier: https://basescan.org/address/0x837dbabc4f5fa78baf177597edbda09645822032
Status: Confirmed by DefimonAlerts and ExVul. Mint path still open at time of reports. No official project statement or pause located in the required-monitor set before cutoff. Final loss and any recovery still open.
Sources: https://x.com/DefimonAlerts/status/2101969009461567690, https://x.com/exvulsec/status/2101971282053263496
Also noted
- Fetch / NuNet / ASI key cluster (UPDATE, not re-scored): ~$2.1M+ primary FET + NTX (and subsequent AGIX/WMTX mint activity with attacker holdings tracked near $16.8M by PeckShield) remain on the 20 Sep brief. GoPlus published a follow-up noting the same attacker bag had grown and framing it as an ecosystem-wide ops-key compromise; no new primary drain figure scored here.
- PolinRider / Laravel Nova supply-chain malware: SlowMist published a TI alert on a PolinRider sample embedded in a development branch of the visanduma/nova-two-factor Laravel Nova extension (700k+ downloads). Malicious code in tailwind.config.js executes at frontend build time, resolves C2 via Ethereum transaction data, and delivers a cross-platform credential stealer (browsers, crypto wallets, password managers, Git/GitHub CLI). Client/CI supply-chain issue, not a protocol smart-contract drain; recorded as advisory only.
- FomoPeek iOS malware (UPDATE): remains on the 19 Sep brief.
- Nostra / Nimiq / Likwid (UPDATE): remain on the 18 Sep brief.
- Lookonchain / ZachXBT / CertiKAlert / CyversAlerts / Immunefi / rekt.news: market-flow, investigative, or no additional first-report smart-contract drain with a fresh loss figure beyond INT in the required-monitor set after the 20 Sep cutoff.
Sources & references
- https://x.com/DefimonAlerts/status/2101969009461567690
- https://x.com/exvulsec/status/2101971282053263496
- https://x.com/SlowMist_Team/status/2101969600422567945
- https://x.com/GoPlusSecurity/status/2101882746457215321
- https://basescan.org/address/0x5f7ce6395818857ac20730dc990f614356d1ec68
- https://basescan.org/token/0x968d6a288d7b024d5012c0b25d67a889e4e3ec19
- https://basescan.org/address/0x837dbabc4f5fa78baf177597edbda09645822032
Editor’s note: Card live-loss is this window’s confirmed realized protocol drains only (~$265K primary INT mint + WETH extraction at report-time pricing). Prior-day ASI and other items remain on their original briefs and are carried as status only. PolinRider is recorded as a confirmed supply-chain advisory, not a protocol loss figure. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 20 Sep 2026: Fetch/NuNet/ASI Leaked Keys ~$2.1M+
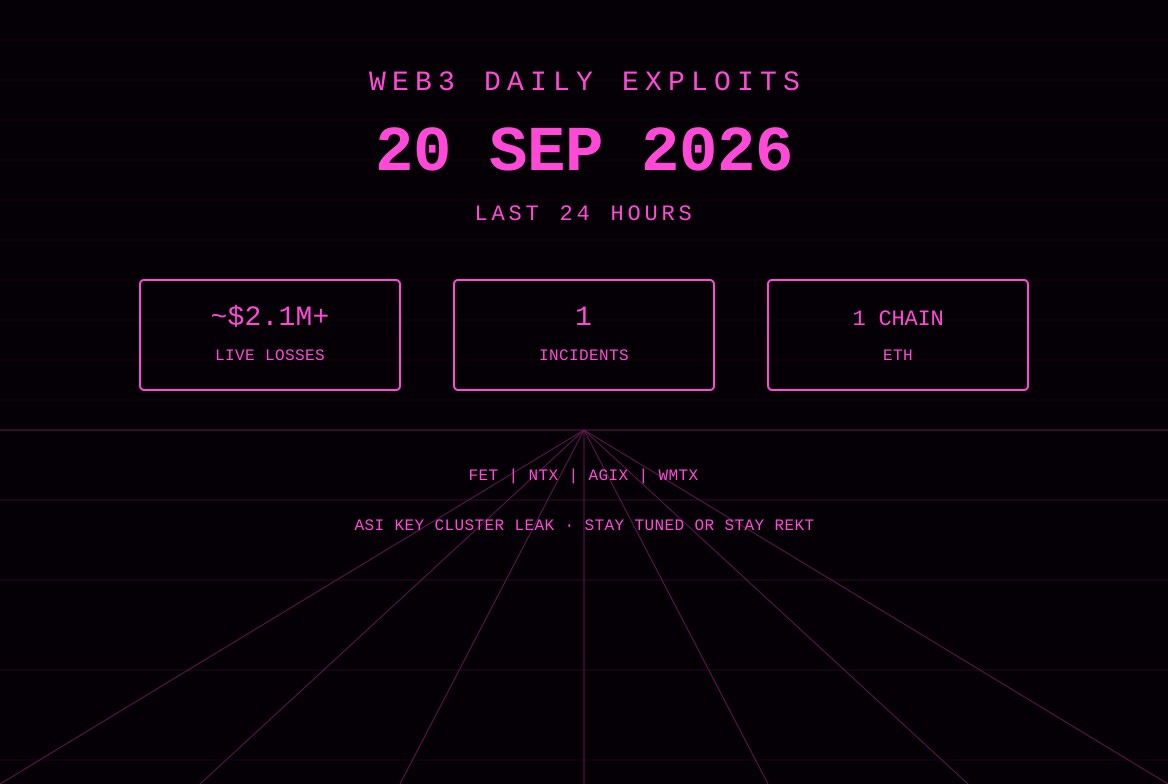
Leaked privileged private keys enabled the same attacker cluster to drain ~8.72M FET (~$1.53–1.56M) from Fetch.ai’s TokenConversionManagerV3, mint ~408.5M NTX (~$450–463k) via NuNet’s deployer, and unauthorized-mint large AGIX + WMTX quantities on SingularityNET/World Mobile. Combined primary loss ~$2.1M+; attacker holdings later marked ~$16.8M by PeckShield.
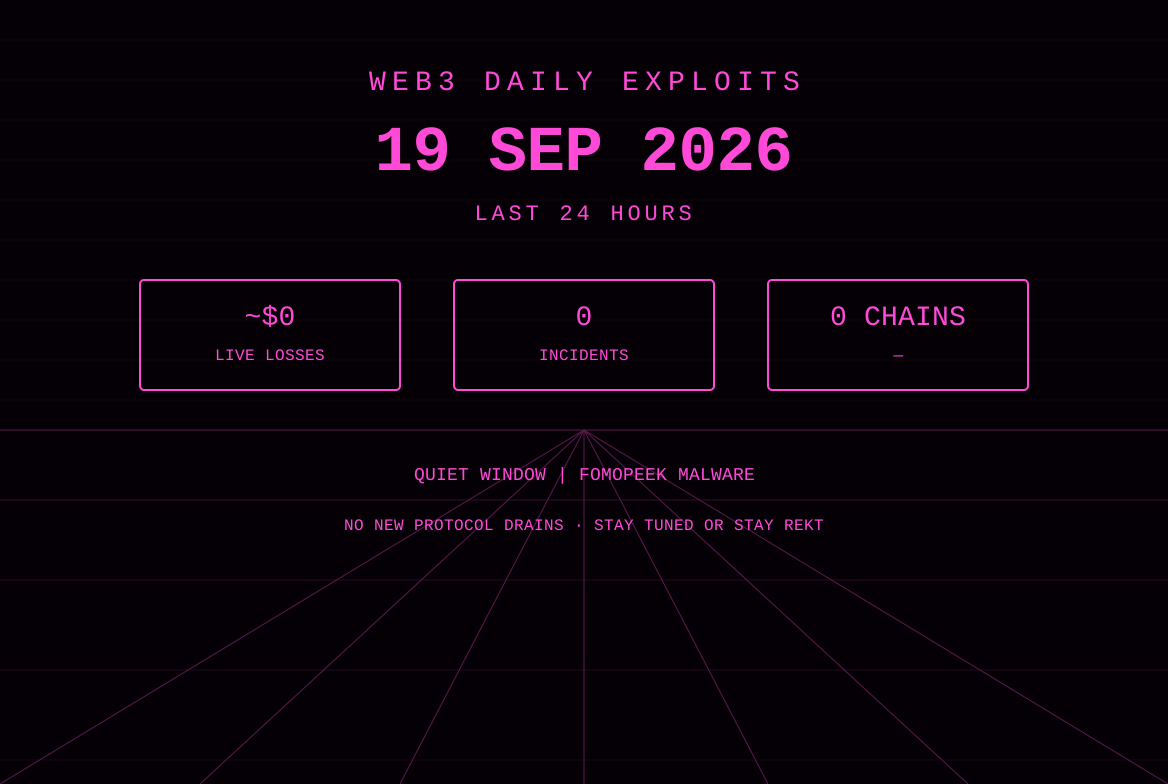
Web3 Daily Exploits — 19 Sep 2026: Quiet Window + FomoPeek Malware
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live loss on this card is ~$0. SlowMist and OKX flagged FomoPeek App v1.1–1.2 as containing iOS kernel exploits capable of Keychain and private-key theft. Prior Nostra ~$3.5M, Nimiq ~$50k and Likwid remain on the 18 Sep brief.
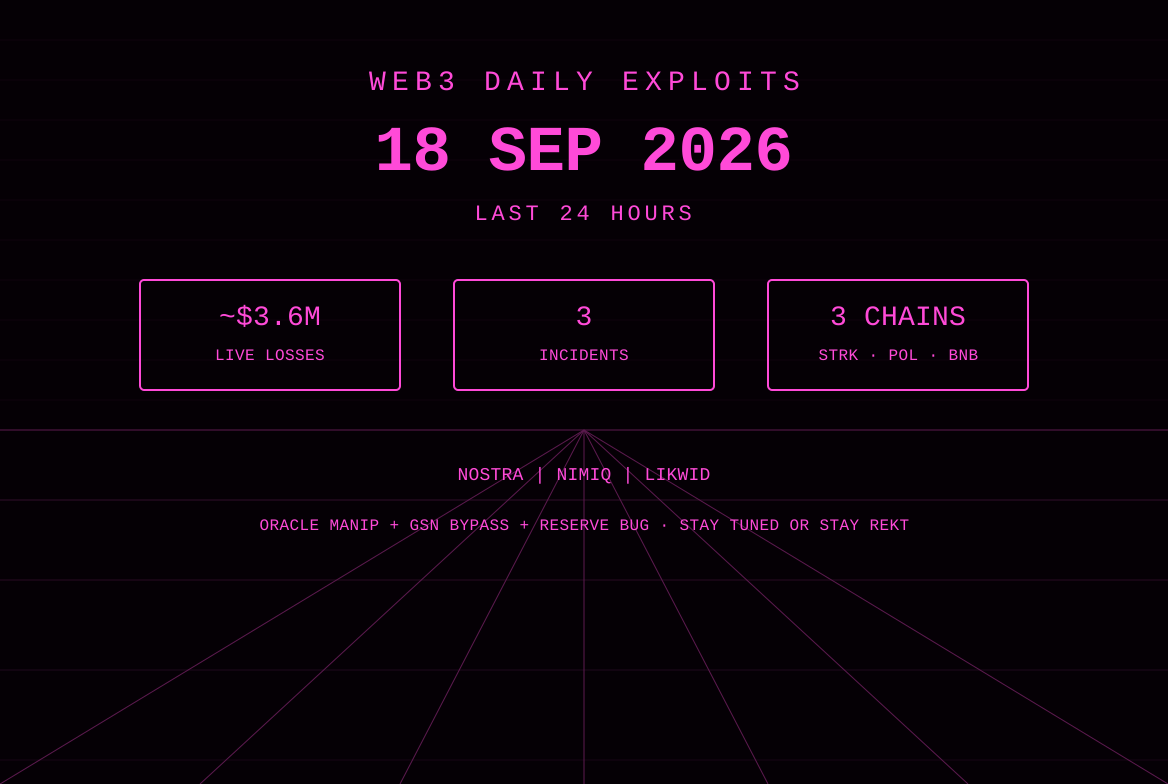
Web3 Daily Exploits — 18 Sep 2026: Nostra ~$3.5M + Nimiq ~$50k + Likwid
Nostra money market on Starknet lost ~$3.5M after NSTR oracle manipulation let one account over-borrow. Nimiq swap handlers on Polygon lost ~$50.4k via OpenGSN signature bypass. Likwid margin on BNB lost 74.31 BNB after a pair-reserve accounting bug. Combined live loss ~$3.6M.
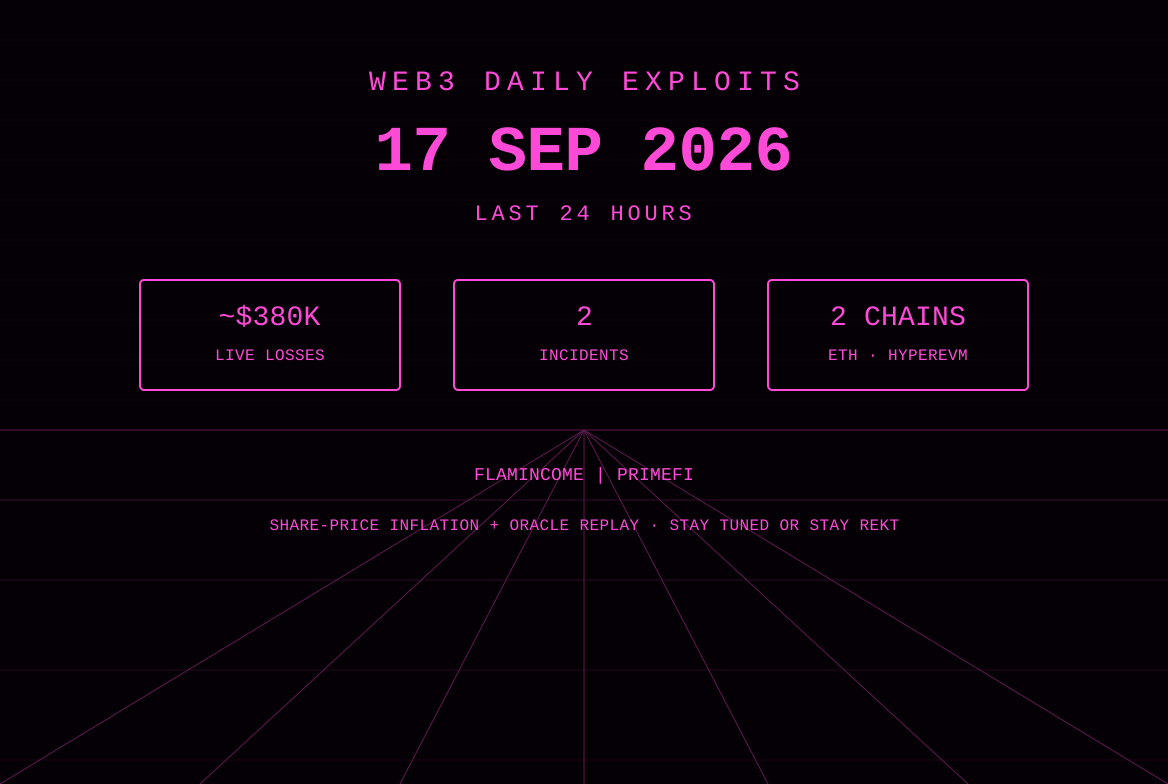
Web3 Daily Exploits — 17 Sep 2026: Flamincome ~$346k + PrimeFi ~$33k
Legacy Flamincome USDT Strategy on Ethereum lost ~$346k after share-price inflation via Convex stakeFor and Curve virtual-price. PrimeFi on HyperEVM lost ~$33k after permissionless oracle report replay inflated PRFI. Quiet otherwise.