Web3 Daily Exploits — 20 Sep 2026: Fetch/NuNet/ASI Leaked Keys ~$2.1M+
Leaked privileged private keys enabled the same attacker cluster to drain ~8.72M FET (~$1.53–1.56M) from Fetch.ai’s TokenConversionManagerV3, mint ~408.5M NTX (~$450–463k) via NuNet’s deployer, and unauthorized-mint large AGIX + WMTX quantities on SingularityNET/World Mobile. Combined primary loss ~$2.1M+; attacker holdings later marked ~$16.8M by PeckShield.
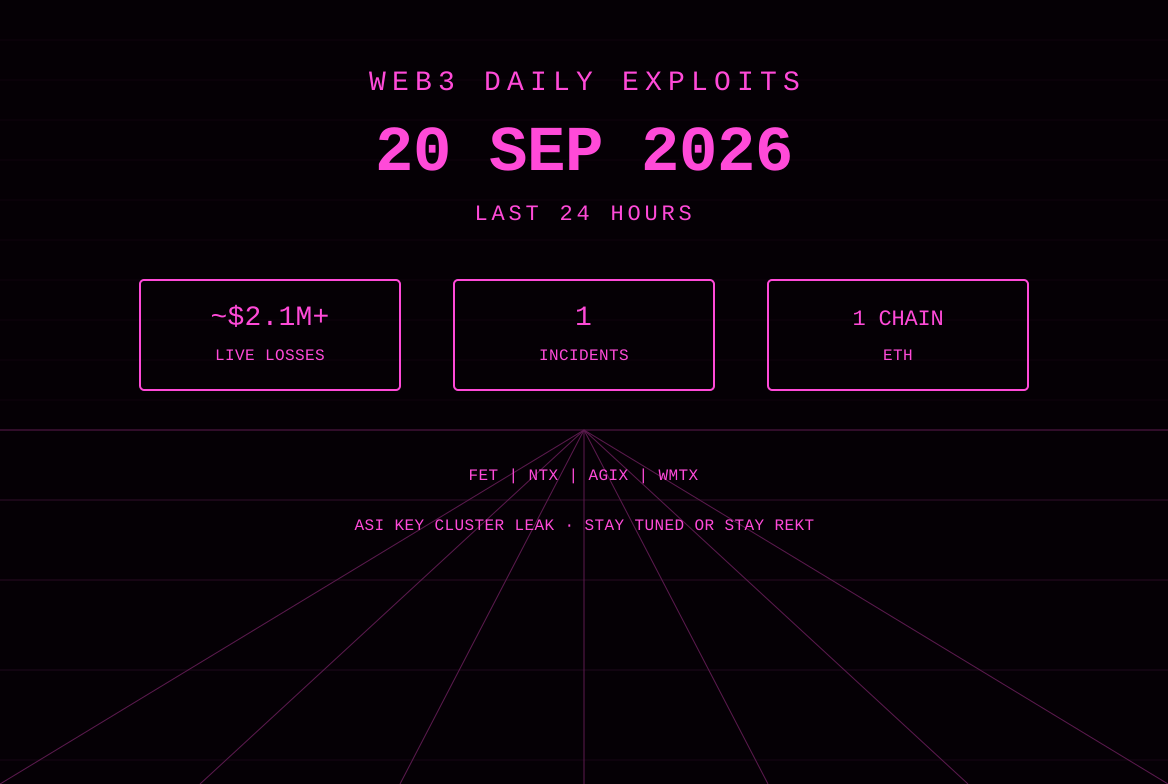
Required monitors were checked through the 20 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One material first-report cluster landed in this slice: leaked private keys belonging to privileged ASI-ecosystem accounts enabled a single attacker cluster to drain Fetch.ai’s Ethereum TokenConversionManagerV3 of ~8.72M FET, mint ~408.5M NTX from NuNet’s deployer, and execute unauthorized AGIX and WMTX mints linked to SingularityNET / World Mobile Chain. Phalcon marked total losses exceeding $2.1M; PeckShield initially printed ~$2M (FET + NTX) and later tracked attacker holdings near $16.77M after the AGIX/WMTX activity. Combined live-loss scored on this card is approximately $2.1M+ for the primary FET drain + NTX mint. Prior-day quiet window and FomoPeek malware advisory remain on the 19 Sep brief and are not re-scored.
All dollar figures below are amounts still outside the affected parties’ control unless a return transaction is cited. Final reconciliation of minted supply, exchange freezes, and any recovery remains open.
Fetch.ai / NuNet / SingularityNET (ASI cluster) — Ethereum — Confirmed
What happened: On 19–20 Sep 2026 the same attacker cluster, using leaked private keys of privileged accounts (Fetch.ai conversion-authorizer and NuNet deployer among them), executed authorized privileged operations. TokenConversionManagerV3 conversionIn() accepted a valid ECDSA signature from the compromised authorizer with no hard-cap enforcement and no on-chain burn/lock proof, draining the entire FET balance of the converter in one call. The same actor then minted large quantities of NTX via the compromised NuNet deployer and later performed unauthorized AGIX and WMTX minting activity tracked to SingularityNET / World Mobile Chain contracts.
Protocol / chain / asset: Ethereum. Fetch.ai TokenConversionManagerV3 (FET). NuNet deployer / mint path (NTX). SingularityNET-related AGIX and World Mobile Chain WMTX minting. Compromised accounts cited by monitors include conversion authorizer 0x69e5446b07b23de0a76730062c3252152216c85c and NuNet deployer 0x863F13e5B505f1Eb17803b94EC9d3DaF80092165. Attacker / primary recipient cluster includes 0x1572F2af7696b39c85E3221CDE8EFb640F86c362 and payout wallet 0x2dcc1085fDCf418B421E45e86e4e54637cc21dfE.
Loss: Card primary mark ~$2.1M+ (Phalcon >$2.1M; PeckShield / SlowMist / GoPlus / Blockaid ~$1.53–1.56M FET + ~$450–463k NTX). FET taken: 8,721,530 FET. NTX minted: ~408.5M (~42% of supply per some reports). Subsequent PeckShield tracking of the same exploiter after AGIX (260M minted, ~198.3M held) and WMTX (53.838M minted, ~33.5M held) activity placed total holdings near $16.77M (AGIX ~$14.42M + ETH ~$1.67M + WMTX ~$627k). NTX price collapsed 65–95% on the mint; FET declined mid-single digits. No return hash located before cutoff.
Attack type: Privileged-key compromise / leaked private key. Not a novel smart-contract logic bug in the classic sense; conversionIn() performed as designed once a valid authorizer signature was supplied. Mint paths similarly executed under control of the compromised deployer key.
Technical details: SlowMist: TokenConversionManagerV3 conversionIn() leaves single-EOA ECDSA signature as the sole authorization check; lacks the checkLimits(amount) modifier present on conversionOut(); does not verify on-chain burn/lock proof. Attacker signed a fresh message for their own address, passed the check, and drained the bridge’s entire FET balance. GoPlus and PeckShield independently linked the same wallet cluster to the subsequent NTX mint and later AGIX/WMTX activity. Fetch.ai published a preliminary on-chain analysis on ASI:One tracing the path from compromised signing key to cash-out wallets and, together with SingularityNET, deactivated affected wallets and contracts. World Mobile Chain issued a security notice on unauthorized WMTX minting via the SingularityNET bridge path and stated it was contacting exchanges and revoking mint authorities.
Explorer links:
- Attacker: https://etherscan.io/address/0x1572F2af7696b39c85E3221CDE8EFb640F86c362
- Payout / recipient: https://etherscan.io/address/0x2dcc1085fDCf418B421E45e86e4e54637cc21dfE
- Fetch TokenConversionManagerV3: https://etherscan.io/address/0xab424A430CC09864fA1277A38193111705ADF3A3
- NuNet-related contract (cited): https://etherscan.io/address/0xF0d33BeDa4d734C72684b5f9abBEbf715D0a7935
Status: Confirmed by SlowMist, Phalcon, GoPlus, PeckShield, Blockaid and official Fetch.ai statement. Affected wallets and contracts deactivated jointly by Fetch.ai and SingularityNET. World Mobile Chain responding on WMTX side. Final loss, recoveries and full mint reconciliation still open. Attacker has swapped a substantial portion of FET/NTX proceeds into ETH.
Sources: https://x.com/SlowMist_Team/status/2101503515877396639, https://x.com/Phalcon_xyz/status/2101520178047787148, https://x.com/GoPlusSecurity/status/2101587915230871570, https://x.com/PeckShieldAlert/status/2101457227379044822, https://x.com/PeckShieldAlert/status/2101602701251334368, https://x.com/Fetch_ai/status/2101564803533926694, https://x.com/Fetch_ai/status/2101595159054131393, https://x.com/wmchain/status/2101538765332431188
Also noted
- FomoPeek iOS malware (UPDATE, not re-scored): SlowMist / OKX advisory on FomoPeek App v1.1–1.2 remains on the 19 Sep brief; client-side key theft, not a protocol drain.
- Nostra / Nimiq / Likwid (UPDATE, not re-scored): ~$3.5M + ~$50.4k + 74.31 BNB remain on the 18 Sep brief.
- RISEx XLP white-hat offer: Defimon surface of an improved white-hat return offer on the 3 Aug 2026 unauthorized withdrawal already disclosed by the project; not a new first-report drain in this window.
- Lookonchain / ZachXBT: market-flow and investigative notes only; no new protocol-drain first-reports scored here.
- CertiKAlert, CyversAlerts, Immunefi, rekt.news: no additional first-report smart-contract drain with a fresh loss figure beyond the ASI cluster after the 19 Sep brief cutoff in the required-monitor set.
Sources & references
- https://x.com/SlowMist_Team/status/2101503515877396639
- https://x.com/Phalcon_xyz/status/2101520178047787148
- https://x.com/GoPlusSecurity/status/2101587915230871570
- https://x.com/PeckShieldAlert/status/2101457227379044822
- https://x.com/PeckShieldAlert/status/2101602701251334368
- https://x.com/Fetch_ai/status/2101564803533926694
- https://x.com/Fetch_ai/status/2101595159054131393
- https://x.com/wmchain/status/2101538765332431188
- https://etherscan.io/address/0x1572F2af7696b39c85E3221CDE8EFb640F86c362
- https://etherscan.io/address/0x2dcc1085fDCf418B421E45e86e4e54637cc21dfE
- https://etherscan.io/address/0xab424A430CC09864fA1277A38193111705ADF3A3
Editor’s note: Card live-loss is this window’s confirmed realized protocol drains / unauthorized mints only (~$2.1M+ primary FET + NTX; AGIX/WMTX mint activity tracked separately with attacker holdings ~$16.8M per PeckShield). Prior-day items remain on their original briefs and are carried as status only. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
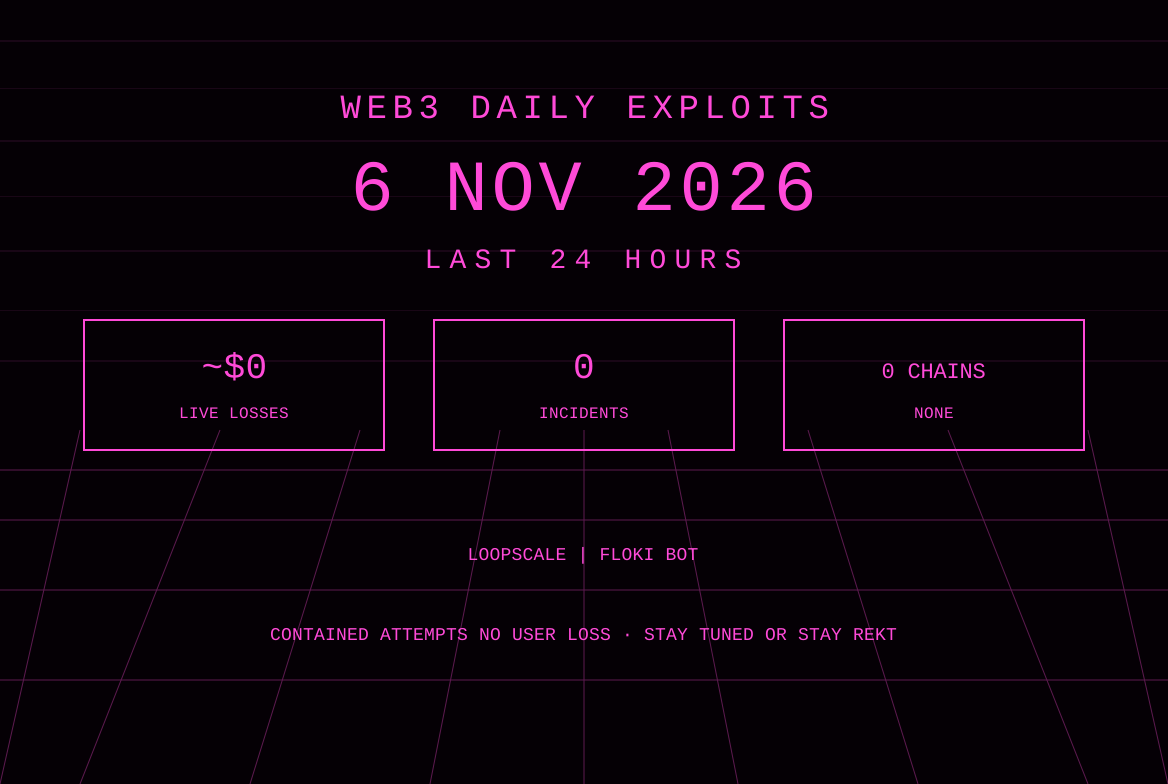
Web3 Daily Exploits — 6 Nov 2026: Loopscale Contained Attempts, FLOKI Bot Offline
Quiet scoring window: Loopscale paused Solana lending after week-long API campaign and two contained attack paths (~$412K undercollateralized loan, ~$521K NAV inflation halted). Vaults made whole, no user deposits lost. FLOKI Telegram trading bot taken offline after exploit; loss size undisclosed. TENDRIL remains prior brief. Live losses ~$0 across 0 scored incidents.
Web3 Daily Exploits — 5 Nov 2026: TENDRIL ~$555K Sell-Hook Drain on BNB
TENDRIL (Flap-style tax token) on BNB Chain suffered a sell-hook reserve desync that drained ~555K USDT (~$555K) from its PancakeSwap V2 pool. Attacker used flash loans and controlburn/sync ordering to empty the pair. CoreVault and Mercado Bitcoin remain UPDATEs. Live losses ~$555K across 1 scored incident.
Web3 Daily Exploits — 4 Nov 2026: CoreVault ~$112K Oracle Flash-Loan on BNB
CoreVault (BNIX/OSK) InsurancePool on BNB Chain drained of ~160 BNB (~$112K net) via flash-loan oracle manipulation inflating redemptions up to 33×. Mercado Bitcoin updated affected assets to ~$36.3M with ~$12.9M blocked and plans gradual reopening (UPDATE). Binance remains UPDATE. Live losses ~$112K across 1 scored incident.
Web3 Daily Exploits — 3 Nov 2026: Mercado Bitcoin ~$46M Multi-Chain Signing Drain
Mercado Bitcoin confirmed a security incident on 2 Nov with ~$40–48.5M drained across 10 chains via signing access to hot wallets and deposit addresses. Exchange later stated ~$38–40M involved, pledged full customer coverage, and reported ~$11M frozen with partners. BTCPay Server hot-wallet sweeps on older versions traced to ~$1.63M (UPDATE). ZachXBT flagged suspected ~$133M EU entity exchange-account theft (unconfirmed). Live losses ~$46M across 1 scored incident.