Web3 Daily Exploits — 19 Sep 2026: Quiet Window + FomoPeek Malware
Required monitors reported no new first-report smart-contract protocol drains in the last 24 hours. Combined live loss on this card is ~$0. SlowMist and OKX flagged FomoPeek App v1.1–1.2 as containing iOS kernel exploits capable of Keychain and private-key theft. Prior Nostra ~$3.5M, Nimiq ~$50k and Likwid remain on the 18 Sep brief.
Required monitors were checked through the 19 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. No new first-report smart-contract protocol drain with a fresh loss figure landed in this slice. Combined live loss scored on this card is approximately $0. This is a quiet window for on-chain DeFi exploits after the 18 Sep cluster (Nostra ~$3.5M, Nimiq ~$50.4k, Likwid 74.31 BNB).
The sole material security item first surfaced or amplified in the required-monitor set during the window is a joint SlowMist / OKX advisory on the FomoPeek iOS app (versions 1.1–1.2). That is client-side malware / private-key exposure, not a protocol smart-contract drain, and is therefore not scored as a live-loss incident on this card. All prior-day protocol losses remain on their original briefs and are carried as status only.
FomoPeek App v1.1–1.2 — iOS malware / private-key exposure — Confirmed advisory
What happened: On 19 Sep 2026 SlowMist published a TI alert, jointly investigated with OKX security teams, stating that multiple users who had installed FomoPeek App versions 1.1–1.2 reported asset theft. Analysis found the app contains malicious modules unrelated to its stated features, including an iOS kernel exploitation framework with eight different exploit methods that can auto-select based on device model and iOS version.
Protocol / chain / asset: Not a blockchain protocol. Client-side iOS application. Affected iOS versions cited: iOS 12.0–18.7 and iOS 26.0–26.1. Successful exploitation can escape the sandbox, access and decrypt Keychain data, and read files belonging to other apps, exposing private keys, seed phrases, credentials and related data. The app also connects to hidden servers and can receive remote commands; plaintext traffic analysis indicated attack functionality is currently enabled and runs automatically at intervals.
Loss: No aggregate dollar figure published by required monitors. Individual user reports of stolen assets; not scored as a protocol live-loss total on this card.
Attack type: Malicious mobile application / iOS kernel exploit chain leading to Keychain and private-key theft. Not a smart-contract vulnerability.
Technical details: SlowMist: two modules unrelated to stated business functions; one contains an iOS kernel exploitation framework. If the exploit succeeds the app may escape the sandbox and read Keychain and other-app files. Recommended actions from the advisory: check accounts for unusual activity; on a trusted device that never had FomoPeek installed, generate new keys/seed; move assets; update iOS; do not reinstall FomoPeek; preserve device and evidence if theft is observed.
Explorer links: Not applicable (client malware, not an on-chain drain).
Status: Confirmed by SlowMist TI and joint OKX investigation. Advisory live. No protocol pause or on-chain return path applies.
Sources: https://x.com/SlowMist_Team/status/2101211432541192615
Nostra money market — Starknet — UPDATE (not re-scored)
What happened: First report remains on the 18 Sep brief. ~$3.5M borrow via NSTR oracle manipulation. As of the prior window ~$1.92–1.93M had been bridged to Ethereum and ~$1.55M remained on Starknet at the named borrow account. No required monitor published a return transaction or a revised final-loss figure in this 24h slice. Carried as status only.
Status: Money market remains paused per last official note. Final loss still under reconciliation.
Sources: Prior 18 Sep brief; https://x.com/nostrafinance/status/2100577538053493076, https://x.com/PeckShieldAlert/status/2100747001516454390, https://x.com/CertiKAlert/status/2100774528494526812
Also noted
- Nostra / Nimiq / Likwid (UPDATE, not re-scored): ~$3.5M + ~$50.4k + 74.31 BNB remain on the 18 Sep brief.
- Flamincome / PrimeFi (UPDATE, not re-scored): ~$346k + ~$33k remain on the 17 Sep brief.
- rsETH / yoink (UPDATE, not re-scored): ~$7.8M stack remains under Kelp temporary pause; carried as status only across prior briefs.
- RISEx XLP / RWA strategy: Defimon surfaced an on-chain white-hat-style recovery message regarding a 3 Aug 2026 unauthorized withdrawal already disclosed and covered by the project; not a new first-report drain in this window.
- Lookonchain: Whale ETH/BTC deposits, Machi position sizing, ZEC short liquidations. Market-flow notes, not exploit first-reports.
- ZachXBT: NFT mint commentary and impersonation warning. Not a protocol-drain first-report.
- CertiKAlert, Phalcon, GoPlusSecurity, PeckShieldAlert, BlockSecTeam, CyversAlerts, Immunefi, rekt.news: no additional first-report smart-contract drain with a fresh loss figure after the 18 Sep brief cutoff in the required-monitor set.
Sources & references
- https://x.com/SlowMist_Team/status/2101211432541192615
- https://x.com/nostrafinance/status/2100577538053493076
- https://x.com/PeckShieldAlert/status/2100747001516454390
- https://x.com/CertiKAlert/status/2100774528494526812
- https://x.com/DefimonAlerts/status/2101200596015435847
- https://x.com/DefimonAlerts/status/2100868892742602793
- https://x.com/SlowMist_Team/status/2100896541859054006
- https://x.com/SlowMist_Team/status/2100785330849009937
Editor’s note: Card live-loss is this window’s confirmed realized protocol drains only (~$0). FomoPeek is recorded as a confirmed malware advisory, not a protocol loss figure. Prior-day items remain on their original briefs and are carried as status only. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 3 Nov 2026: Mercado Bitcoin ~$46M Multi-Chain Signing Drain
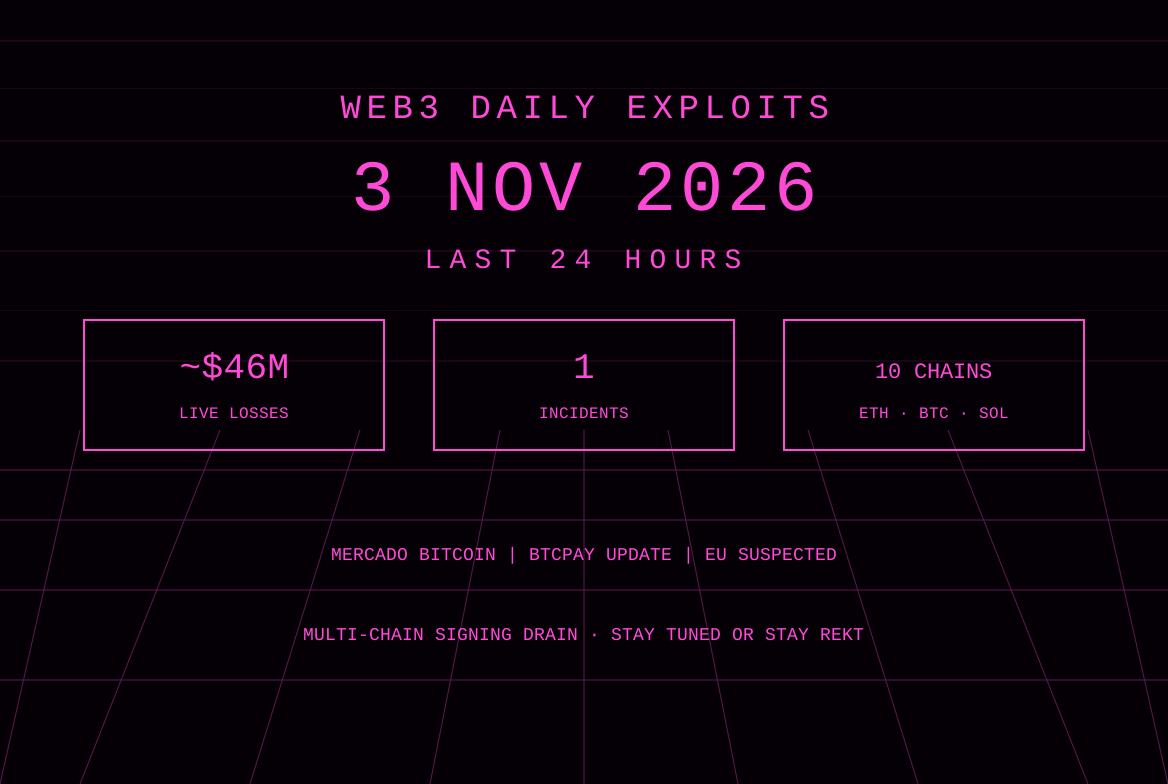
Mercado Bitcoin confirmed a security incident on 2 Nov with ~$40–48.5M drained across 10 chains via signing access to hot wallets and deposit addresses. Exchange later stated ~$38–40M involved, pledged full customer coverage, and reported ~$11M frozen with partners. BTCPay Server hot-wallet sweeps on older versions traced to ~$1.63M (UPDATE). ZachXBT flagged suspected ~$133M EU entity exchange-account theft (unconfirmed). Live losses ~$46M across 1 scored incident.
Web3 Daily Exploits — 2 Nov 2026: Quiet Window After Premia GoPlus Breakdown
Quiet day in the last 24 hours: no new first-reported protocol drains with scored live losses. GoPlus published a detailed breakdown of the prior PremiaLabs Arbitrum options vault incident (~$465K, already scored 1 Nov). Pando Rings 2022 exploiter moved additional funds to Tornado Cash. Binance remains an UPDATE. Live losses ~$0 for new items.

Web3 Daily Exploits — 1 Nov 2026: Premia $465K Arbitrum Options Drain, Troves 8.6 BTC Legacy Perm, b14g 97M CORE Zero-Withdraw
PremiaLabs vaults on Arbitrum drained ~$465K via empty option pools and flash-loan liquidity extraction. Troves xWBTC/WBTC vault on Starknet lost ~8.6 BTC through a legacy rebalancing contract that retained permissions. b14g dual-staking on Core lost ~97M CORE (~$1.47M) when zero-amount withdrawal requests were treated as full balances. Live losses ~$2.6M across 3 incidents. Binance remains an UPDATE.
Web3 Daily Exploits — 31 Oct 2026: Flap & Kintsu DNS Hijack Wave (StepDrainer), No New Scored Protocol Drains
Flap.sh and Kintsu.xyz (plus at least 10 other DeFi sites) suffered DNS hijacks on 31 October, redirecting users to StepDrainer wallet-drainer clones. No confirmed loss figure published. Live loss ~$0 for new scored items, 1 incident. Binance ~$6.3B remains an UPDATE with multi-breach notes, ~$3B frozen and $6.34B reserved.