Web3 Daily Exploits — 18 Sep 2026: Nostra ~$3.5M + Nimiq ~$50k + Likwid
Nostra money market on Starknet lost ~$3.5M after NSTR oracle manipulation let one account over-borrow. Nimiq swap handlers on Polygon lost ~$50.4k via OpenGSN signature bypass. Likwid margin on BNB lost 74.31 BNB after a pair-reserve accounting bug. Combined live loss ~$3.6M.
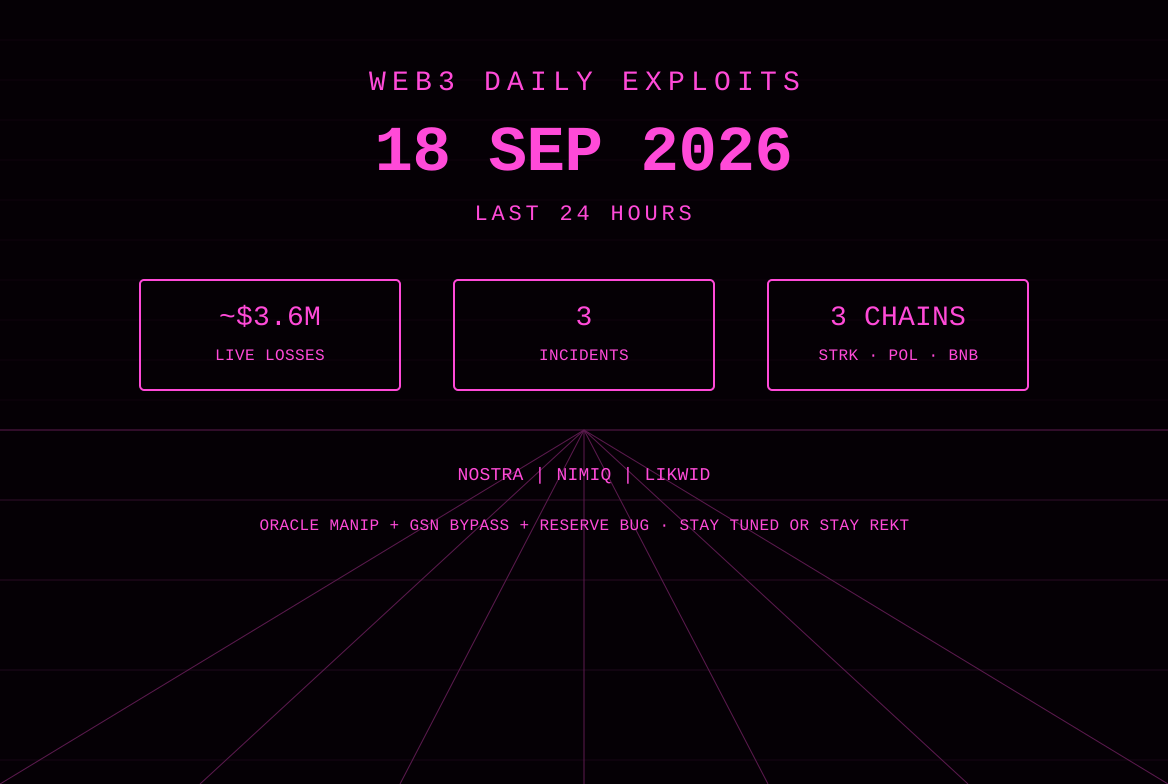
Required monitors were checked through the 18 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. Three confirmed first-report or materially updated money movements landed in this slice: Nostra’s Starknet money market was drained for ~$3.5M via NSTR oracle price manipulation, Nimiq’s Polygon swap/HTLC handlers lost ~$50.4k after an OpenGSN signature bypass, and Likwid’s BNB margin position lost 74.31 BNB after a pair-reserve accounting gap. Combined live loss scored on this card is approximately $3.6M. Yesterday’s Flamincome ~$346k and PrimeFi ~$33k remain on the 17 Sep brief and are not re-scored.
All dollar figures below are amounts still outside the affected party’s control unless a return transaction is cited. Final Nostra loss is still being reconciled by the protocol; the ~$3.5M borrow figure and ~$1.9M bridged print are the working card marks.
Nostra money market — Starknet — Confirmed
What happened: On 17 Sep 2026, a manipulated NSTR oracle price enabled one account to borrow approximately $3.5 million worth of ETH, STRK, USDC, USDT, WBTC and DAIv1 against NSTR collateral in the Nostra money market on Starknet. Nostra paused lending, borrowing, withdrawals and liquidations. PeckShield, CertiK, Phalcon and GoPlus published independent tracking through the 18 Sep window: roughly $1.92–1.93M bridged to Ethereum (234.57 ETH + ~1.3M DAI) while ~$1.55M remained on Starknet at the named borrow account.
Protocol / chain / asset: Nostra Finance money market on Starknet. Collateral token: NSTR. Assets taken: ETH, STRK, USDC, USDT, WBTC, DAIv1. Oracle path involved Pragma aggregation that could be influenced by a low-liquidity GeckoTerminal NSTR/SolvBTC pool the attacker seeded.
Loss: Card uses ~$3.5M (official Nostra statement). Desk marks: PeckShield / CertiK / GoPlus consistent with the $3.5M borrow; ~$1.92–1.93M confirmed bridged to Ethereum address 0xa059aaab82773caf622de9d9a0f2dbf9aa7f3c37; ~$1.55M still on Starknet at 0x06d48ef7ab62c26e3ef1987c322096cd508e9034c82048783a6b438fc1344bc3. Final loss and recoveries not yet known per protocol.
Attack type: Oracle / price-manipulation via low-liquidity pool seeding and GeckoTerminal selection. Attacker created an NSTR/SolvBTC pool with one-sided liquidity, wash-traded, then pushed a thin-range quote so the median of available sources averaged to ~$49.5 (vs normal ~$0.006).
Technical details: Phalcon and GoPlus reconstructed the flow: attacker pre-positioned NSTR months earlier, created the manipulated pool (tx cluster around 05:23–05:48 UTC 17 Sep), spiked the quote, then borrowed from the over-valued collateral account. Borrow account 0x06d48ef7ab62c26e3ef1987c322096cd508e9034c82048783a6b438fc1344bc3; manipulation account 0x2d9fb4edec9d5c015c43514ca5a309aab1b2638c3a45ad750d09ee971d0da23. STRK portions exited via NEAR Intents; ETH/DAI consolidated on Ethereum.
Explorer links:
- Borrow / remaining Starknet position: https://voyager.online/contract/0x06d48ef7ab62c26e3ef1987c322096cd508e9034c82048783a6b438fc1344bc3
- Ethereum consolidation: https://etherscan.io/address/0xa059aaab82773caf622de9d9a0f2dbf9aa7f3c37
Status: Confirmed by Nostra official statement, PeckShield, CertiK, Phalcon, GoPlus. Money market paused. Final loss still under reconciliation; no return hash located before cutoff.
Sources: https://x.com/nostrafinance/status/2100577538053493076, https://x.com/PeckShieldAlert/status/2100747001516454390, https://x.com/CertiKAlert/status/2100774528494526812, https://x.com/Phalcon_xyz/status/2100818035082952751, https://x.com/GoPlusSecurity/status/2100869014633468266
Nimiq swap / HTLC handlers — Polygon — Confirmed
What happened: On 16 Sep 2026 (first required-monitor report 18 Sep), Nimiq’s swap contracts that double as OpenGSN paymaster and forwarder were exploited for ~$50.4k. The attacker registered an EIP-7702 EOA as relay manager/worker/paymaster, set the forwarder to the HTLC handlers, forged open() requests from a liquidity wallet that had unlimited approvals, opened HTLCs for the full USDC/USDT0/USDC.e balance with hashlock sha256(0x01), then redeemed with secret 0x01.
Protocol / chain / asset: Nimiq ecosystem swap / Gas Abstraction contracts on Polygon. Assets taken: USDC, USDT0, USDC.e consolidated as USDC. Vulnerable handlers named by SlowMist: 0x0cFD862bE942846Cebad797d7c1BC6e47714959b, 0xf615bd7eA00C4Cc7F39fAAD0895Db5f40891359f.
Loss: Card uses ~$50.4k (Defimon) / ~$50,463 (SlowMist). No return identified.
Attack type: Access-control / signature-bypass via OpenGSN RelayHub. execute() discarded signature and nonce parameters and relied on preRelayedCall on an attacker-chosen paymaster, so signature checks were skipped.
Technical details: SlowMist: ERC20PermitHTLCHandler.execute() discards the five calldata parameters including signature & nonce; the only validation lived in preRelayedCall, which RelayHub invokes on the attacker-specified paymaster. Attacker staked 1 POL, registered as relay, forged request.from = victim, opened HTLCs, redeemed. Attacker: 0x2258491525C21f334c5a2dc22CE55e55023FC45D. Victim liquidity wallet: 0x24Cb173Ae221AeA93369f34bdcF0Ddb35b436773. Nimiq disabled stablecoin Gas Abstraction as containment.
Explorer links:
- Attacker: https://polygonscan.com/address/0x2258491525C21f334c5a2dc22CE55e55023FC45D
- Victim: https://polygonscan.com/address/0x24Cb173Ae221AeA93369f34bdcF0Ddb35b436773
- Vulnerable handlers: https://polygonscan.com/address/0x0cFD862bE942846Cebad797d7c1BC6e47714959b, https://polygonscan.com/address/0xf615bd7eA00C4Cc7F39fAAD0895Db5f40891359f
Status: Confirmed by Defimon and SlowMist. Nimiq investigating; Gas Abstraction for stablecoins disabled. Funds not reported returned.
Sources: https://x.com/DefimonAlerts/status/2100868892742602793, https://x.com/SlowMist_Team/status/2100896541859054006, https://x.com/nimiq/status/2100661471789412565
Likwid margin / LikwidVault — BNB Chain — Confirmed
What happened: SlowMist TI alerted on 18 Sep that Likwid lost 74.31 BNB. The root cause was in LikwidMarginPosition._executeAddCollateralAndBorrow (leverage=0 branch): delta.pairDelta was never assigned, so the borrow path left pairReserves untouched. getAmountOut(pairReserves, …) returned the same 4.7857 BNB quote on every call; the attacker repeated the margin/borrow cycle 14 times, settling 211.8M TOKEN at the first-trade marginal price with no AMM price impact.
Protocol / chain / asset: Likwid Finance margin position and vault on BNB Chain. Vulnerable contract: 0x6bec0c1dc4898484b7f094566ddf8bc82ed7abe8 (LikwidMarginPosition). Victim vault: 0x065d449ec9d139740343990b7e1cf05fa830e4ba. Asset taken: BNB.
Loss: Card uses 74.31 BNB (~$45–55k depending on spot). SlowMist figure is the sole required-monitor print in this window. No return identified.
Attack type: Accounting / reserve-state bug. Pair reserves were not updated on the zero-leverage borrow path, so repeated calls harvested the same marginal quote.
Technical details: Attacker EOA 0x90bde1e0bb16b3deeb9d638acf8d01f19fd2f31e → attack contract 0xc63fb27f52ed8d06673c60c3075b2d3bd26cf4aa. Fourteen repeated cycles extracted the full 74.31 BNB without moving the quoted reserve.
Explorer links:
- Vulnerable LikwidMarginPosition: https://bscscan.com/address/0x6bec0c1dc4898484b7f094566ddf8bc82ed7abe8
- Victim LikwidVault: https://bscscan.com/address/0x065d449ec9d139740343990b7e1cf05fa830e4ba
- Attacker EOA: https://bscscan.com/address/0x90bde1e0bb16b3deeb9d638acf8d01f19fd2f31e
- Attack contract: https://bscscan.com/address/0xc63fb27f52ed8d06673c60c3075b2d3bd26cf4aa
Status: Confirmed by SlowMist. No official @likwid_fi containment note or return hash located in the required-monitor set before cutoff.
Sources: https://x.com/SlowMist_Team/status/2100785330849009937
Also noted
- Flamincome / PrimeFi (UPDATE, not re-scored): ~$346k + ~$33k remain on the 17 Sep brief.
- rsETH / yoink (UPDATE, not re-scored): ~$7.8M stack remains parked under Kelp temporary pause; carried as status only across prior briefs.
- Bonfire (UPDATE, not re-scored): ~$47–50k approval drain remains on the 16 Sep brief.
- Lookonchain / ZachXBT: in-window posts were market-flow or unrelated investigative notes, not new protocol-drain first-reports scored here.
- Immunefi, CyversAlerts, rekt.news: no additional first-report smart-contract drain with a fresh loss figure beyond the three incidents above after the 17 Sep brief cutoff.
Sources & references
- https://x.com/nostrafinance/status/2100577538053493076
- https://x.com/PeckShieldAlert/status/2100747001516454390
- https://x.com/CertiKAlert/status/2100774528494526812
- https://x.com/Phalcon_xyz/status/2100818035082952751
- https://x.com/GoPlusSecurity/status/2100869014633468266
- https://x.com/DefimonAlerts/status/2100868892742602793
- https://x.com/SlowMist_Team/status/2100896541859054006
- https://x.com/SlowMist_Team/status/2100785330849009937
- https://x.com/nimiq/status/2100661471789412565
- https://voyager.online/contract/0x06d48ef7ab62c26e3ef1987c322096cd508e9034c82048783a6b438fc1344bc3
- https://etherscan.io/address/0xa059aaab82773caf622de9d9a0f2dbf9aa7f3c37
Editor’s note: Card live-loss is this window’s confirmed realized drains only (~$3.5M Nostra + ~$50k Nimiq + 74.31 BNB Likwid). Prior-day items remain on their original briefs and are carried as status only. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
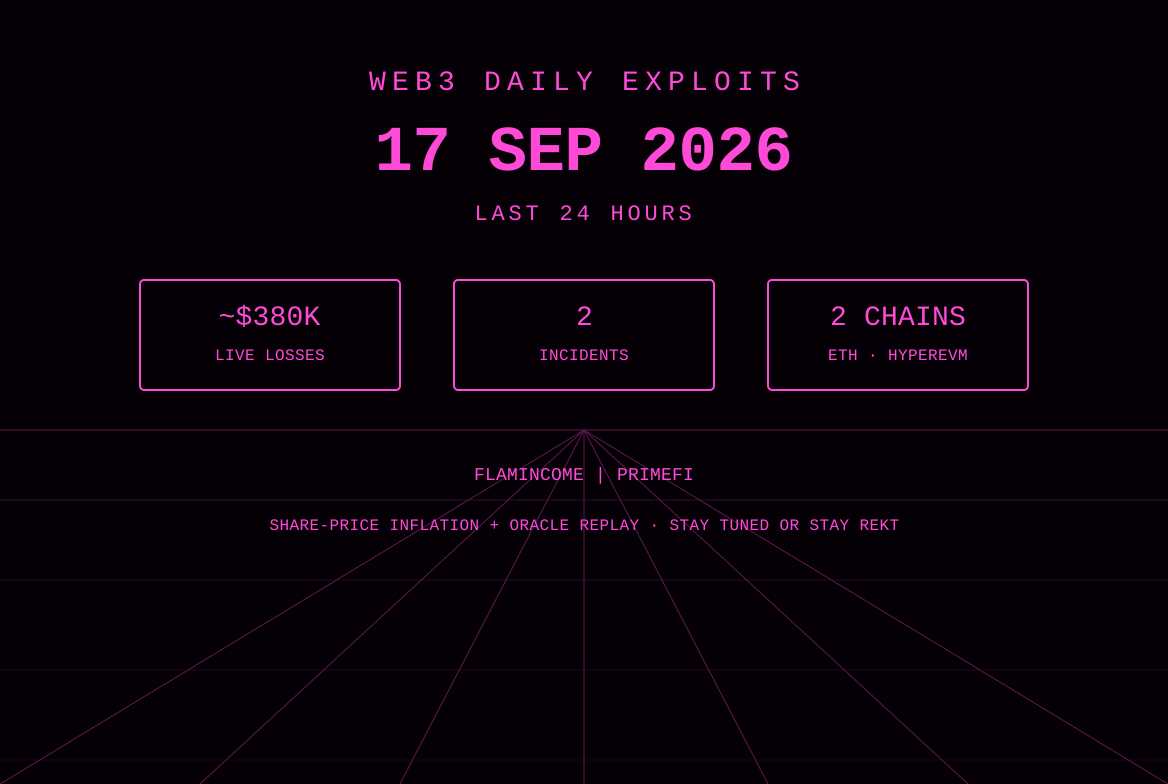
Web3 Daily Exploits — 17 Sep 2026: Flamincome ~$346k + PrimeFi ~$33k
Legacy Flamincome USDT Strategy on Ethereum lost ~$346k after share-price inflation via Convex stakeFor and Curve virtual-price. PrimeFi on HyperEVM lost ~$33k after permissionless oracle report replay inflated PRFI. Quiet otherwise.
Web3 Daily Exploits — 16 Sep 2026: Bonfire ~$50k Approval Drain
BonfireSwap router on BNB Chain lost ~$47–50k after an access-control gap in transfer let anyone spend holders’ standing approvals. rsETH / yoink stack remains parked under Kelp’s temporary pause. Quiet window otherwise.
Web3 Daily Exploits — 15 Sep 2026: rsETH Safe $7.8M + Yoink Frontrun
A Gnosis Safe holding leveraged aEthrsETH was drained for ~$7.8M on Ethereum. MEV bot yoink front-ran the public-mempool exploit and parked ~2,882 rsETH. Bridgeless posted a 48-hour Zano ETHX whitehat burn offer.
Web3 Daily Exploits — 14 Sep 2026: Yam $121k Gov Drain + Spiral 10.7 ETH
Yam proposal #45 finished as a realized ~$121k UMA-farm pull. SlowMist printed a same-block ~10.7 ETH (~$26.8k) spot-price borrow on SpiralHookV2. Ampleforth Governor Bravo #54 was cancelled on-chain.