Web3 Daily Exploits — 17 Sep 2026: Flamincome ~$346k + PrimeFi ~$33k
Legacy Flamincome USDT Strategy on Ethereum lost ~$346k after share-price inflation via Convex stakeFor and Curve virtual-price. PrimeFi on HyperEVM lost ~$33k after permissionless oracle report replay inflated PRFI. Quiet otherwise.
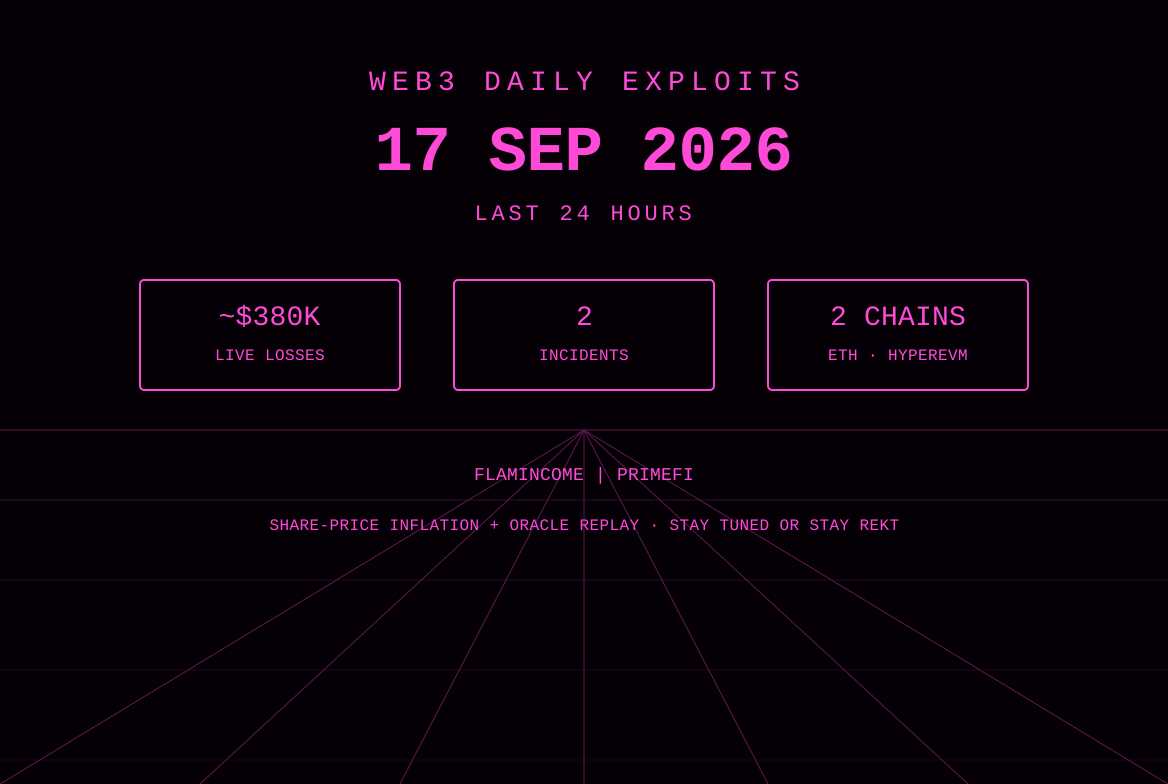
Required monitors were checked through the 17 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. Two confirmed first-report money movements landed in this slice: Flamincome’s legacy USDT Strategy on Ethereum was drained for ~$346k via share-price inflation, and PrimeFi’s HyperEVM market lost ~$33.4k after an oracle-report replay. Combined live loss scored on this card is approximately $380k. Yesterday’s Bonfire ~$50k approval drain stays on the 16 Sep brief and is not re-scored. The rsETH / yoink ~$7.8M stack remains under Kelp’s temporary pause and is carried as status only.
CertiKAlert, PeckShieldAlert, BlockSecTeam, CyversAlerts, and rekt.news published no new first-report smart-contract drain with a fresh loss figure after the 16 Sep brief cutoff. All dollar figures below are amounts still outside the affected party’s control unless a return transaction is cited.
Flamincome / VaultYUSDT Strategy — Ethereum — Confirmed
What happened: On 16 Sep 2026, Defimon, SlowMist, and Blockaid independently flagged a ~$346k extraction against the legacy Flamincome USDT Strategy. The attacker used a Morpho flash loan of ~$18M USDT, bought USDP cheaply, imbalance-minted a large amount of the Curve USDP metapool LP, deposited it into Convex, and staked it FOR the Strategy via stakeFor. This inflated the Strategy’s reported balanceOf and the per-share value derived from Curve get_virtual_price(). Redeeming YUSDT via VaultYUSDT.withdrawAll forced the Strategy to pull ~544k aUSDT from Aave and pay out at the inflated rate, netting the attacker ~$346k while the strategy lost ~$595k in aUSDT+USDT.
Protocol / chain / asset: Legacy Flamincome (associated with Flamingo Finance) USDT Strategy on Ethereum. Vulnerable strategy: 0xb8d6471cA573C92c7096Ab8600347F6a9Fe268a5. Flawed implementation named by SlowMist: 0xff20De3F3F4C7E9518035a968B4A3CEE500a2AFB. Asset taken: aUSDT / USDT. This is old 2020-era yield-aggregator code, not the live Flamingo protocol on Neo N3.
Loss: Card uses ~$346k. Desk marks: Defimon ~$346k; SlowMist ~$345.9k; Blockaid ~$345.9k. No return transaction identified. Do not invent a higher figure.
Attack type: Oracle / share-price inflation via permissionless Convex stakeFor and Curve virtual-price manipulation. Not a classic reentrancy or access-control bug on the vault itself; the economic accounting treated an injectable Convex balance and a manipulable virtual price as reliable NAV.
Technical details: The Strategy’s deposited() path valued its Convex/Curve position from BaseRewardPool.balanceOf(Strategy) × Curve USDP metapool get_virtual_price() plus aUSDT reserves. Because stakeFor is permissionless, the attacker could inflate the Strategy’s reported balance without owning the position. The depegged USDP pool made the virtual price overstate real economic value. Primary attacker named by SlowMist and Blockaid: 0x83381e7f7232775735169d72d237b858ffc36871. Victim strategy and related vault addresses match the required-monitor set.
Explorer links:
- Victim Strategy: https://etherscan.io/address/0xb8d6471cA573C92c7096Ab8600347F6a9Fe268a5
- Flawed Impl (SlowMist): https://etherscan.io/address/0xff20De3F3F4C7E9518035a968B4A3CEE500a2AFB
- Attacker: https://etherscan.io/address/0x83381e7f7232775735169d72d237b858ffc36871
Status: Confirmed by Defimon, SlowMist, and Blockaid. Funds not reported returned. Legacy contracts remain a residual exposure for any remaining depositors.
Sources: https://x.com/DefimonAlerts/status/2100235904543584600, https://x.com/SlowMist_Team/status/2100256590716907706, https://x.com/blockaid_/status/2100226158046461984
PrimeFi — HyperEVM — Confirmed
What happened: At 12:37 UTC on 16 Sep 2026, Defimon published the first required-monitor alert for a ~$33.4k loss against @primefinanceyz on HyperEVM. The attacker replayed a previously signed historical Chainlink Data Streams report through a permissionless DataStreamConsumer.verifyReport() that, after signature check, blindly overwrote the stored price for a feedId with no freshness/newer-than check. PRFI’s oracle price was inflated to ~$0.11 (vs ~$0.0021 real, ~52×). Using a Morpho flash loan the attacker bought PRFI cheaply from the thin WHYPE/PRFI pool, deposited it as over-valued collateral, and borrowed ~425.5 WHYPE (~$33.4k), draining the WHYPE reserve. Proceeds converted to ~398.7 HYPE.
Protocol / chain / asset: PrimeFi lending market on HyperEVM. Asset taken: WHYPE / HYPE. Oracle consumer failed to restrict report submission or enforce report freshness.
Loss: Card uses ~$33.4k (Defimon) / ~$31.1k (official PrimeFi post at time of disclosure). Official statement confirms ~398.7 HYPE extracted. No return identified at cutoff.
Attack type: Oracle manipulation / stale-report replay. Permissionless verifyReport allowed historical signed reports to overwrite current price without a freshness gate.
Technical details: DataStreamConsumer.verifyReport() checked the Chainlink Data Streams signature then overwrote the stored price for the feedId with no check that the report was newer than the one already stored. Attacker pushed a favorable signed PRFI report, inflated collateral value, borrowed against it. Primary incident tx named in the on-chain recovery request and Defimon: 0xff990876d863a61732779c341991215856c89420b84daaf31eece7ecd5ff4243. PrimeFi paused HyperEVM at 13:56 UTC, paused Base as precaution, confirmed XDC unaffected, deployed a hardened consumer that accepts reports only from approved keepers and rejects stale reports, set PRFI LTV to 0, and posted a white-hat recovery request offering 20% bounty for return of 80% of proceeds.
Explorer links:
- Incident tx (HyperEVM):
0xff990876d863a61732779c341991215856c89420b84daaf31eece7ecd5ff4243(full explorer path depends on HyperEVM scanner) - Recovery address named by protocol:
0xF2e2A49631927108086268c68C559c63c3C8f73d
Status: Confirmed by Defimon and official @primefinanceyz statement. Markets paused; hardened oracle deployed. White-hat recovery request live; no confirmed return hash before cutoff.
Sources: https://x.com/DefimonAlerts/status/2100306169231245535, https://x.com/primefinanceyz/status/2100497389991993446
Unidentified Gnosis Safe / leveraged aEthrsETH — Ethereum — UPDATE (not re-scored)
What happened: First report remains on the 15 Sep brief. The ~2,882 rsETH stack continues to sit at 0xC70f00CD7E461686b04B0E912E309becA8b80ea0. Kelp DAO’s temporary wallet-level pause is the last official containment note. No required monitor published a return transaction or a new dollar print. Carried as status only.
Status: Funds still outside the victim Safe’s control. Kelp stated contracts are safe and rsETH remains fully backed.
Sources: Prior 15–16 Sep briefs; https://x.com/KelpDAO/status/2099740756865159562
Also noted
- Bonfire / BonfireSwap (UPDATE, not re-scored): ~$47–50k approval drain remains on the 16 Sep brief.
- rsETH / yoink (UPDATE, not re-scored): ~$7.8M stack remains parked; see dedicated UPDATE section above.
- DCENT App Wallet: Official abnormal-transfer advisory and app-update guidance. Hardware wallets not confirmed impacted. Infrastructure / wallet note, not a protocol drain with loss figure scored here.
- Core Lightning experimental features: Official advisory to disable experimental dual-fund / splicing / peer-storage options. Infrastructure note.
- Lookonchain: Whale ETH accumulation, SYN long, ZEC liquidation, Unipcs portfolio rebound. Market-flow notes, not exploit first-reports.
- GoPlusSecurity: Wallet Theft Detective skill release and Arc copycat-rug warnings. Not a confirmed drain.
- Immunefi, CertiKAlert, Phalcon, PeckShieldAlert, BlockSecTeam, CyversAlerts, ZachXBT, rekt.news: no new first-report smart-contract drain with a fresh loss figure after the 16 Sep brief cutoff in the required-monitor set.
Sources & references
- https://x.com/DefimonAlerts/status/2100235904543584600
- https://x.com/DefimonAlerts/status/2100306169231245535
- https://x.com/SlowMist_Team/status/2100256590716907706
- https://x.com/blockaid_/status/2100226158046461984
- https://x.com/primefinanceyz/status/2100497389991993446
- https://x.com/KelpDAO/status/2099740756865159562
- https://etherscan.io/address/0xb8d6471cA573C92c7096Ab8600347F6a9Fe268a5
- https://etherscan.io/address/0x83381e7f7232775735169d72d237b858ffc36871
Editor’s note: Card live-loss is this window’s confirmed realized drains only (~$346k Flamincome + ~$33k PrimeFi). The rsETH / yoink extraction remains on the 15 Sep brief and is carried here as status only. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 16 Sep 2026: Bonfire ~$50k Approval Drain
BonfireSwap router on BNB Chain lost ~$47–50k after an access-control gap in transfer let anyone spend holders’ standing approvals. rsETH / yoink stack remains parked under Kelp’s temporary pause. Quiet window otherwise.
Web3 Daily Exploits — 15 Sep 2026: rsETH Safe $7.8M + Yoink Frontrun
A Gnosis Safe holding leveraged aEthrsETH was drained for ~$7.8M on Ethereum. MEV bot yoink front-ran the public-mempool exploit and parked ~2,882 rsETH. Bridgeless posted a 48-hour Zano ETHX whitehat burn offer.
Web3 Daily Exploits — 14 Sep 2026: Yam $121k Gov Drain + Spiral 10.7 ETH
Yam proposal #45 finished as a realized ~$121k UMA-farm pull. SlowMist printed a same-block ~10.7 ETH (~$26.8k) spot-price borrow on SpiralHookV2. Ampleforth Governor Bravo #54 was cancelled on-chain.
Web3 Daily Exploits — 13 Sep 2026: Ampleforth $2.5M Gov Alert + Orb3 Bridge Window
No confirmed new protocol drain in the last 24 hours. Defimon flagged Ampleforth Governor Bravo proposal #54 aiming 2.5M USDC at a fresh proposer, and an Orb3 Orbit L1-bridge assertion that can confirm after block 26,005,988.