Web3 Daily Exploits — 16 Sep 2026: Bonfire ~$50k Approval Drain
BonfireSwap router on BNB Chain lost ~$47–50k after an access-control gap in transfer let anyone spend holders’ standing approvals. rsETH / yoink stack remains parked under Kelp’s temporary pause. Quiet window otherwise.
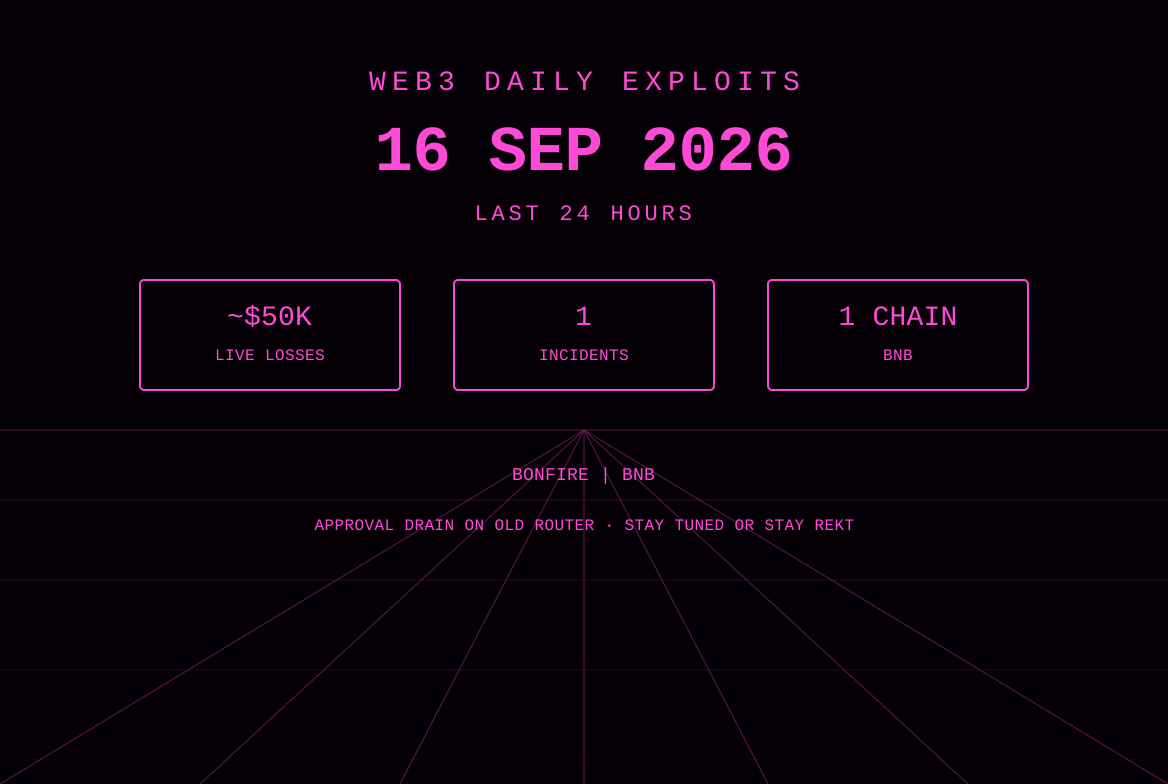
Required monitors were checked through the 16 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One confirmed first-report money movement landed in this slice: BonfireSwap’s router on BNB Chain was used to spend standing approvals of dozens of BONFIRE holders, extracting roughly $47–50k in WBNB. Combined live loss scored on this card is approximately $50k. Yesterday’s rsETH / yoink ~$7.8M extraction stays on the 15 Sep brief; the stack remains at the named receiver under Kelp’s temporary wallet pause and is not re-scored here.
CertiKAlert, Phalcon, PeckShieldAlert, BlockSecTeam, CyversAlerts, and rekt.news published no new first-report smart-contract drain with a fresh loss figure after the 15 Sep brief cutoff. All dollar figures below are amounts still outside the affected party’s control unless a return transaction is cited. Quiet day beyond the single BNB approval drain and the ongoing rsETH status notes.
Bonfire / BonfireSwap router — BNB Chain — Confirmed
What happened: At 03:29 UTC on 16 Sep 2026, SlowMist published the first required-monitor TI alert for a ~$50k loss against @bonfiretoken. Defimon followed at 04:23 UTC with a ~$47k print and the same root-cause framing. TenArmor independently flagged a ~$47.4k suspicious attack on the same old protocol on BSC with a matching transaction hash. The desks agree the BonfireSwap router allowed any caller to set an arbitrary holder as the token source and spend that holder’s existing approval to the router.
Protocol / chain / asset: BonfireSwap router on BNB Chain. Token: $BONFIRE. Vulnerable contract named by SlowMist and Defimon: 0x17e801e17cefc6334059189c178d4783830e03d3. Asset taken: BONFIRE from holders who had previously approved the router, force-sold into the Pancake pair, with WBNB proceeds skimmed to the attacker contract. SlowMist counts 41 affected TOKEN holders; Defimon notes a loop over ~65 holders who had approved BonfireSwap and extraction of ~66 BNB.
Loss: Card uses ~$50k. Desk marks in this window: SlowMist ~$50k; Defimon ~$47k / ~66 BNB; TenArmor ~$47.4k. No return transaction identified. Do not invent a higher figure or add unrelated BONFIRE market moves.
Attack type: Access control / arbitrary-source approval drain. The router’s transfer (and parallel loggedTransfer / simpleTransfer paths per Defimon) performed _safeTransferFrom from a caller-supplied source without checking that msg.sender owned or was authorized to spend that source’s tokens. Anyone could therefore spend any holder’s standing approval to the router.
Technical details: SlowMist: the function does not check msg.sender == from nor verify the caller’s allowance on from, letting anyone set a victim as from and themselves as to. The router drains the victim’s TOKEN using its pre-approved allowance (victim → router) and forwards funds via same-token pool swap. Defimon: transfer(address to, uint amountAIn, address beneficiary, uint deadline) calls _safeTransferFrom(tokenAddress, to, pancakePair, amountAIn) with no ownership or authorization check on the to argument used as source. Addresses named by required monitors: attacker EOA 0x2b5bf7d9d9dc1eec68f40c6b7a8f197e65f9731a → attack contract 0x28E976Ea7b83553d6D1D45CE81334156A2632127; largest named victim 0xefF2FC4E3145f58F534d68A36Bcd3085Be6a4096 (−5289.1 TOKEN per SlowMist). Primary attack transaction published by TenArmor and consistent with the named contracts: 0xb4c00e8f3ba815b6c70f45026f8794d2c1f079646a89919077688ce60692193f.
Explorer links:
- Vulnerable BonfireSwap router: https://bscscan.com/address/0x17e801e17cefc6334059189c178d4783830e03d3
- Attack transaction: https://bscscan.com/tx/0xb4c00e8f3ba815b6c70f45026f8794d2c1f079646a89919077688ce60692193f
- Attacker EOA: https://bscscan.com/address/0x2b5bf7d9d9dc1eec68f40c6b7a8f197e65f9731a
- Attack contract: https://bscscan.com/address/0x28E976Ea7b83553d6D1D45CE81334156A2632127
- Largest named victim: https://bscscan.com/address/0xefF2FC4E3145f58F534d68A36Bcd3085Be6a4096
Status: Confirmed by SlowMist, Defimon, and TenArmor. No official @bonfiretoken containment note or return hash located in the required-monitor set before cutoff. Funds not reported returned. Standing approvals to the old router remain a residual exposure until revoked by each holder.
Sources: https://x.com/SlowMist_Team/status/2100064586980528458, https://x.com/DefimonAlerts/status/2100077978528936392, https://x.com/TenArmorAlert/status/2100042823139721576
Unidentified Gnosis Safe / leveraged aEthrsETH — Ethereum — UPDATE (not re-scored)
What happened: First report remains on the 15 Sep brief. In this cutoff the ~2,882 rsETH stack continues to sit at 0xC70f00CD7E461686b04B0E912E309becA8b80ea0. Kelp DAO’s temporary 24-hour wallet-level pause (issued 15 Sep ~06:03 UTC) is the last official containment note located. No required monitor published a return transaction or a new dollar print. The item is carried as status only and is not added to today’s live-loss box.
Status: Funds still outside the victim Safe’s control. Kelp stated contracts are safe and rsETH remains fully backed. No public message from yoink’s operator on return. Secondary media reprints in this window do not change the on-chain picture.
Sources: Prior 15 Sep brief; https://x.com/KelpDAO/status/2099740756865159562
Also noted
- rsETH / yoink (UPDATE, not re-scored): ~$7.8M stack remains parked; see dedicated UPDATE section above.
- Bridgeless / Zano ETHX (UPDATE): 48-hour whitehat burn offer from the 14–15 Sep window had no new burn or official resolution hash in the required-monitor set before this cutoff.
- Yam Finance / GovernorAlpha #45 (UPDATE, not re-scored): Realized ~$121k remains on the 14 Sep brief.
- Spiral / SpiralHookV2 (UPDATE, not re-scored): ~10.7 ETH / $26,800 remains on the 14 Sep brief.
- Ampleforth Governor Bravo #54 (UPDATE): Cancelled; $0 live.
- Orb3 / Edgeless L1 bridges (UPDATE): Forged assertions still inside confirmation windows; no Outbox withdrawal hashes located.
- Lookonchain: New-wallet $HYPE buy, Cumberland $PONS rotation, Unipcs portfolio note, ARGUS 302x scalp, whale BTC→ETH rotation. Market-flow notes, not exploit first-reports.
- ZachXBT: in-window posts concerned LE email compromise and CEX response criticism, not a protocol-drain first-report.
- GoPlusSecurity: Arc Chain copycat-rug warning and Robinhood token-issuance risk research. Not a confirmed drain with loss figure.
- SlowMist: KREMLIN / REF9334 banking-malware TI (Ethereum contracts used as dead-drop resolvers). Infrastructure / malware note, not a DeFi drain.
- Immunefi, CertiKAlert, Phalcon, PeckShieldAlert, BlockSecTeam, CyversAlerts, rekt.news: no new first-report smart-contract drain with a fresh loss figure after the 15 Sep brief cutoff.
Sources & references
- https://x.com/SlowMist_Team/status/2100064586980528458
- https://x.com/DefimonAlerts/status/2100077978528936392
- https://x.com/TenArmorAlert/status/2100042823139721576
- https://x.com/KelpDAO/status/2099740756865159562
- https://bscscan.com/tx/0xb4c00e8f3ba815b6c70f45026f8794d2c1f079646a89919077688ce60692193f
- https://bscscan.com/address/0x17e801e17cefc6334059189c178d4783830e03d3
- https://bscscan.com/address/0x2b5bf7d9d9dc1eec68f40c6b7a8f197e65f9731a
- https://bscscan.com/address/0x28E976Ea7b83553d6D1D45CE81334156A2632127
- https://bscscan.com/address/0xefF2FC4E3145f58F534d68A36Bcd3085Be6a4096
Editor’s note: Card live-loss is this window’s confirmed realized drain only (~$50k Bonfire). The rsETH / yoink extraction remains on the 15 Sep brief and is carried here as status only. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
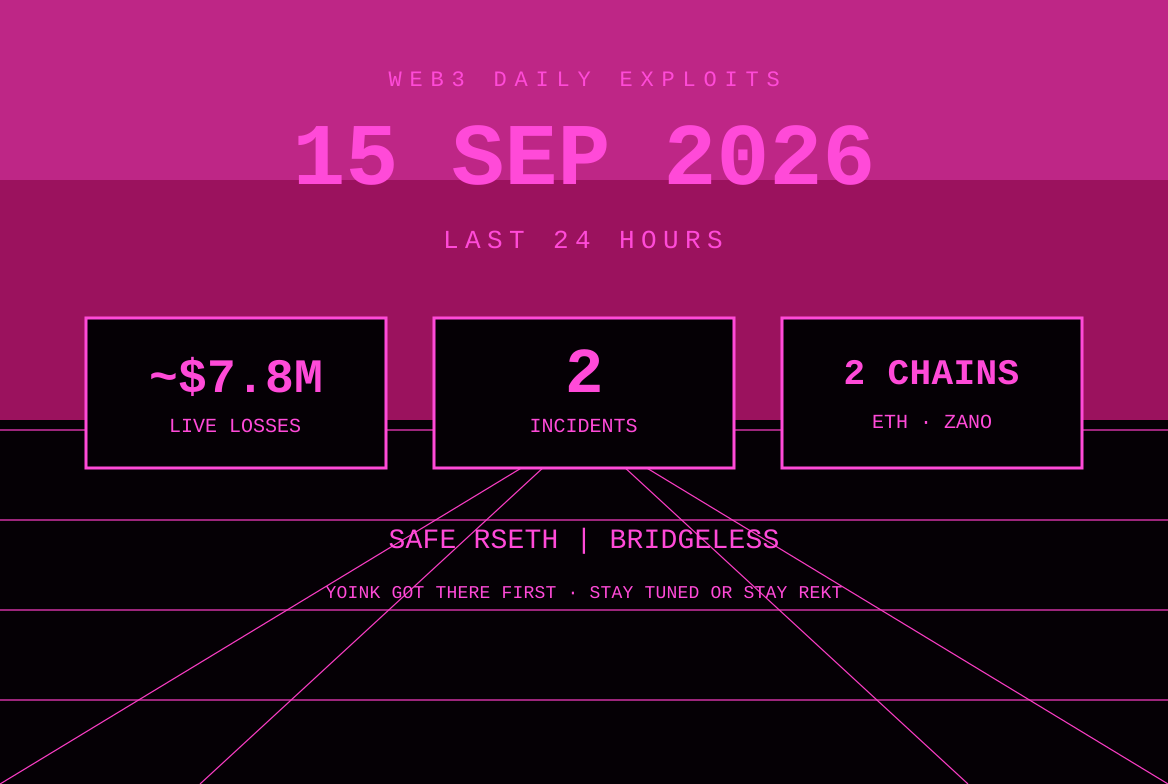
Web3 Daily Exploits — 15 Sep 2026: rsETH Safe $7.8M + Yoink Frontrun
A Gnosis Safe holding leveraged aEthrsETH was drained for ~$7.8M on Ethereum. MEV bot yoink front-ran the public-mempool exploit and parked ~2,882 rsETH. Bridgeless posted a 48-hour Zano ETHX whitehat burn offer.
Web3 Daily Exploits — 14 Sep 2026: Yam $121k Gov Drain + Spiral 10.7 ETH
Yam proposal #45 finished as a realized ~$121k UMA-farm pull. SlowMist printed a same-block ~10.7 ETH (~$26.8k) spot-price borrow on SpiralHookV2. Ampleforth Governor Bravo #54 was cancelled on-chain.
Web3 Daily Exploits — 13 Sep 2026: Ampleforth $2.5M Gov Alert + Orb3 Bridge Window
No confirmed new protocol drain in the last 24 hours. Defimon flagged Ampleforth Governor Bravo proposal #54 aiming 2.5M USDC at a fresh proposer, and an Orb3 Orbit L1-bridge assertion that can confirm after block 26,005,988.
Web3 Daily Exploits — 12 Sep 2026: Zentra ~$140k Citrea Drain + ORB Reentrancy
First public desk confirmation of Zentra’s 9 Sep ctUSD reserve drain on Citrea (~$140k official / ~$143k Defimon), a SlowMist-confirmed ~$32.6k ORB reentrancy on BNB Chain, and a pending fake rollup assertion against Edgeless’s dormant L1 bridge (~9.2 ewETH at risk).