Web3 Daily Exploits — 15 Sep 2026: rsETH Safe $7.8M + Yoink Frontrun
A Gnosis Safe holding leveraged aEthrsETH was drained for ~$7.8M on Ethereum. MEV bot yoink front-ran the public-mempool exploit and parked ~2,882 rsETH. Bridgeless posted a 48-hour Zano ETHX whitehat burn offer.
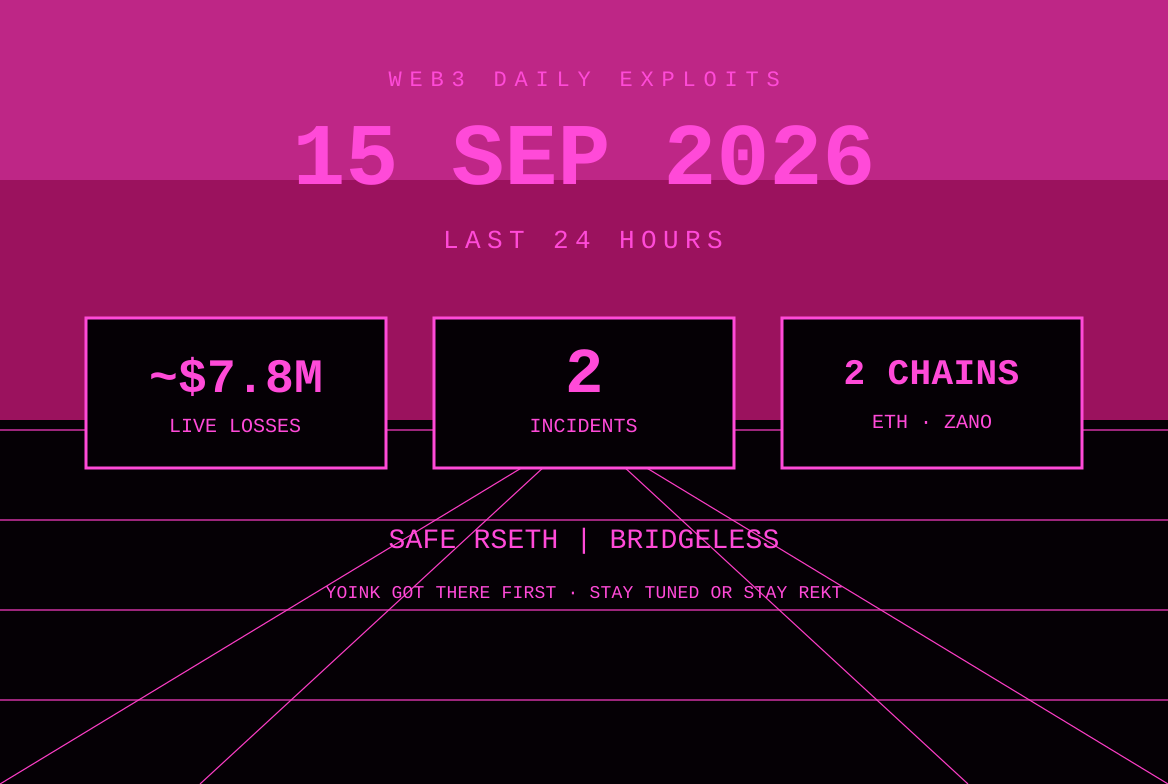
Required monitors were checked through the 15 Sep 2026 America/Panama cutoff: DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news. One confirmed large money movement landed in this slice: an unidentified user’s Gnosis Safe on Ethereum lost a leveraged rsETH stack after a public keeper / strategy-executor authorization check failed. Defimon, Phalcon, PeckShieldAlert, and SlowMist independently printed the same cluster. Combined live loss scored on this card is approximately $7.8M, using the Defimon / PeckShieldAlert ~$7.81M and Phalcon ~$7.8M / ~2,882 rsETH front-run print. SlowMist’s parallel desk mark is ~$7.73M against the same victim Safe. A second first-report item is a Bridgeless / Zano ETHX over-mint that the operators paused and tried to close as a whitehat burn; it is not added to the live-loss box.
Yesterday’s Yam (~$121k realized) and SpiralHookV2 (~10.7 ETH / $26,800) items stay on the 14 Sep brief. They are not re-scored. Ampleforth Governor Bravo #54 remains cancelled. Orb3 node 716 and Edgeless node 228 are still inside their L1 confirmation windows with no Outbox withdrawal hash located. CertiKAlert, BlockSecTeam’s main handle, CyversAlerts, Immunefi, and rekt.news published no new first-report smart-contract drain with a fresh loss figure after the 14 Sep brief cutoff. All dollar figures below are amounts still outside the affected party’s control unless a return transaction is cited. Yoink holding the extracted rsETH is not treated as a return to the victim.
Unidentified Gnosis Safe / leveraged aEthrsETH — Ethereum — Confirmed
What happened: At 05:18 UTC on 15 Sep 2026, Defimon published the first required-monitor write-up that MEV bot “yoink” had front-run a ~$7.81M rsETH exploit against whale 0x40E9’s Gnosis Safe. The original attacker deployed a token labeled “Permissionless Attacker Token,” sent the exploit into the public mempool, and lost the race. Phalcon (06:05 UTC), PeckShieldAlert (06:01 UTC), and SlowMist (08:35 UTC) reprinted the same victim, the same executor, and the same destination. Kelp DAO, issuer of rsETH, said at 06:03 UTC that core contracts were untouched and placed a 24-hour wallet-level pause on the address that received the tokens.
Protocol / chain / asset: User-controlled Gnosis Safe on Ethereum, Safe Singleton 1.3.0 per independent reconstructions that match the named victim. Asset taken: Aave V3 aEthrsETH unwrapped to Kelp rsETH (0xa1290d69c65a6fe4df752f95823fae25cb99e5a7). Phalcon: ~2,900 aEthrsETH moved into a Uniswap V4 pool paired with the worthless PAT token, leaving the Safe with a worthless LP NFT; yoink captured ~2,882 rsETH. This is not a Kelp core-contract drain and not a Safe core / owner-key bug in the required-monitor texts.
Loss: Card uses ~$7.8M. Desk marks in this window: Defimon ~$7.81M; PeckShieldAlert ~$7.81M; Phalcon ~$7.8M and ~2,882 rsETH; SlowMist ~$7.73M. A secondary reconstruction priced the main extraction leg at $7,848,604.81 and split the captured stack as 2,882.37 rsETH ($7,800,883.70) sent to the receiver plus 17.63 rsETH ($47,721.12) swapped. No return to the victim Safe was identified. Do not add April 2026’s separate Kelp / Lazarus rsETH-bridge event on top of this figure.
Attack type: Module-authorization / public-multicall bypass on a user-enabled Safe executor, then Uniswap V4 hooked-pool unwrap of aEthrsETH. Not an rsETH mint bug. Not a Safe singleton bug in the alerting desks’ wording.
Technical details: SlowMist and Phalcon locate the broken check in the executor / router at 0x4f0055926c839D1d960a82CBF84E2eE933958ebC. SlowMist: in multicall(address, bytes[]) the _contract argument could be set to address(this), so _isAuthorized returned true and the enabled Safe module executed attacker calldata via delegatecall. Defimon’s parallel wording: the whitelisted strategy executor exposed a recipe entrypoint that forwarded fully caller-supplied calldata into the Safe’s execTransactionFromModuleReturnData with operation=1 (DELEGATECALL) and no gate on the external caller. Because the module was already authorized, anyone who could reach that entrypoint executed in the Safe’s own context.
Addresses named by required monitors: victim Safe 0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8; SlowMist “attacker” 0x2f7e143e27f2fa26ef3b8ac72698f1d321422f67; yoink receiver 0xC70f00CD7E461686b04B0E912E309becA8b80ea0. Independent same-window reconstruction that matches those desks also names yoink EOA 0xFDe0d1575Ed8E06FBf36256bcdfA1F359281455A, yoink bot 0x80BF7Db69556D9521c03461978B8fC731DBBD4e4, and helper 0x10605eE48Ff962952C966277A5D2dac0A0705Cb1. Blockaid, not a required monitor but first to publish an example hash used below, listed exploiter-linked addresses 0x0dC2c5D6b05A317076CF501F7E7be36A5dfe9b66, the same helper, and the same receiver, plus truncated call-path hops 0xeA18B13d… and Uni V4 LP module 0xDcDc4ef8…. Those two truncated addresses are not expanded in this cutoff. A reply that the module “was MakinaFi’s” is unverified; @makinafi stated the issue is not related to a Makina module or Makina Machines and asked for a rectification.
Primary extraction window: 04:38:47 UTC on 15 Sep 2026, Ethereum block 25,980,525. Example exploit transaction published by Blockaid and consistent with the named victim: 0x0e7680b06cb8a6f86c149d9ba90d98e3d334e7b072dde03909d43fcfd98a8705. A later yoink transaction at 05:53:59 UTC in block 25,980,901, 0xe77f7513547d917e86e2ac8457b00e9f4336fee3908b9a674095603d467cde66, shows another aEthrsETH unwrap from the same Safe; that hash is an explorer match to the named yoink contracts, not a second required-monitor loss print. Blockaid also listed smaller follow-on transfers (~$134k / ~$24k / three ~$1.3k legs). Those extra legs are not added to the $7.8M card box. A second-Safe ~$129k claim circulating in secondary write-ups is flagged unverified against the required-monitor set.
Explorer links:
- Victim Safe: https://etherscan.io/address/0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8
- Vulnerable executor / router: https://etherscan.io/address/0x4f0055926c839D1d960a82CBF84E2eE933958ebC
- Example exploit tx: https://etherscan.io/tx/0x0e7680b06cb8a6f86c149d9ba90d98e3d334e7b072dde03909d43fcfd98a8705
- Later yoink tx (same Safe): https://etherscan.io/tx/0xe77f7513547d917e86e2ac8457b00e9f4336fee3908b9a674095603d467cde66
- Yoink bot: https://etherscan.io/address/0x80BF7Db69556D9521c03461978B8fC731DBBD4e4
- Yoink EOA: https://etherscan.io/address/0xFDe0d1575Ed8E06FBf36256bcdfA1F359281455A
- Receiver (Kelp-paused): https://etherscan.io/address/0xC70f00CD7E461686b04B0E912E309becA8b80ea0
- SlowMist-named attacker: https://etherscan.io/address/0x2f7e143e27f2fa26ef3b8ac72698f1d321422f67
- Helper named in-window: https://etherscan.io/address/0x10605eE48Ff962952C966277A5D2dac0A0705Cb1
- rsETH token: https://etherscan.io/token/0xa1290d69c65a6fe4df752f95823fae25cb99e5a7
Status: Confirmed drain by Defimon, Phalcon, PeckShieldAlert, and SlowMist. Funds sit at 0xC70f00CD…80ea0 per PeckShieldAlert. Kelp DAO applied a temporary 24-hour pause so rsETH cannot move in or out of that address, said Kelp contracts are safe and rsETH remains fully backed, and said minting, withdrawals, and integrations were running normally. No official statement from the unidentified Safe owner. No public message from yoink’s operator on whether the stack will be returned. @makinafi denied that a Makina module was involved.
Sources: https://x.com/DefimonAlerts/status/2099729577002053884, https://x.com/Phalcon_xyz/status/2099741447776096270, https://x.com/PeckShieldAlert/status/2099740493165068581, https://x.com/PeckShieldAlert/status/2099744390143217951, https://x.com/SlowMist_Team/status/2099779127662493875, https://x.com/KelpDAO/status/2099740756865159562, https://x.com/makinafi/status/2099761754100138097
Bridgeless / Zano ETHX over-mint — Ethereum + Zano — Paused / whitehat offer
What happened: At 21:05 UTC on 14 Sep 2026, Defimon relayed an on-chain message to a wallet holder. The operators said that on 14 September the address deposited 0.5015 ETH into the Bridgeless bridge and submitted the deposit 52 times under different spellings of the hash, minting 26 ETHX on Zano. The same actor then burned 11.6 ETHX toward withdrawals to that address. The bridge was paused. Those withdrawals will not be paid. 14.41 ETHX remains in the Zano wallet, per the message.
Protocol / chain / asset: Bridgeless bridge between Ethereum and Zano. Asset named: ETHX on Zano, minted against an ETH deposit. Deposit transaction cited only as 0x922878e8... in the Defimon relay; the full hash was not expanded in this cutoff and is not invented here.
Loss: $0 live on this card. The message describes an over-mint (26 ETHX from 0.5015 ETH) that was halted before the remaining 14.41 ETHX could be withdrawn as ETH. No required monitor published a dollar print. Do not convert ETHX or add a notional figure to the $7.8M box.
Attack type: Duplicate / variant-hash deposit replay against bridge mint accounting, per the operators’ own message. Not a smart-contract drain with an independent desk reconstruction in the required-monitor set.
Technical details: Defimon’s relay is the operators speaking on-chain, not a third-party post-mortem. Terms offered: within 48 hours, burn 9.409691 ETHX on Zano as a plain public burn with no bridge attachment; keep 5 ETHX as bounty; when the bridge resumes, a withdrawal of those 5 ETHX to the same address will be honoured. After the deadline the offer is withdrawn. The message also said the funding wallets behind the depositor had been identified. No burn hash and no official @Bridgeless_com or @zano_project statement were located in the required-monitor set before cutoff. Resolution is therefore pending the 48-hour clock that started with the 14 Sep 21:05 UTC relay.
Explorer links:
- Deposit tx (truncated as published): 0x922878e8… — full hash not published by the alerting desk
Status: First public desk relay by Defimon. Bridge paused per the operators. Whitehat burn not confirmed. Remaining ETHX not reported withdrawn as ETH.
Sources: https://x.com/DefimonAlerts/status/2099605487960444961
Also noted
- Kelp DAO wallet pause (same incident, not a second loss): Official pause on
0xc70f00cd7e461686b04b0e912e309beca8b80ea0for 24 hours. Source: https://x.com/KelpDAO/status/2099740756865159562. - Makina denial (unverified attribution retired): Independent replies tied the executor to MakinaFi. @makinafi: “The issue is not related to a Makina module or Makina Machines.” Source: https://x.com/makinafi/status/2099761754100138097.
- SlowMist GitLab CVE-2026-85706: Path-traversal advisory for self-managed GitLab CE/EE. Infrastructure note, not a Web3 drain.
- Yam Finance / GovernorAlpha #45 (UPDATE, not re-scored): Realized ~$121k UMA-farm pull remains on the 14 Sep brief. No new extract hash in this cutoff.
- Spiral / SpiralHookV2 (UPDATE, not re-scored): ~10.7 ETH / $26,800 SlowMist print remains on the 14 Sep brief.
- Ampleforth Governor Bravo #54 (UPDATE, not re-scored): Cancelled on 14 Sep. No revival in this window.
- Orb3 / chainId 788988 L1 bridge (UPDATE, not re-scored): Forged assertion node 716 still gated on L1 block 26,005,988 (~18 Sep). No Outbox withdrawal.
- Edgeless Network L1 bridge (UPDATE, not re-scored): Fake assertion node 228 still gated on L1 block 25,999,225 (~17–18 Sep). No Outbox withdrawal.
- Zentra Finance (UPDATE, not re-scored): First-report ctUSD drain remains on the 12 Sep brief. No new official post located after the 14 Sep bounty-reply deadline.
- Symbiosis Bitcoin Bridge (UPDATE, not re-scored): First-report mint-and-dump remains on the 11 Sep brief. No new return hash.
- Liquid Network (UPDATE, not re-scored): ~598.5 BTC remains with the 6 Sep actor. No new return hash.
- Lookonchain: Lazarus-labeled cluster sold 911 ETH (~$2.28M); Matrixport BTC/ETH exchange flow; Multicoin HYPE deposit; two dormant wallets sent 14,700 ETH to OKX; $STANDARD scalp. Market-flow and old-cluster notes, not exploit first-reports.
- ZachXBT: in-window posts were a CEX / Lazarus-laundering argument and the prior medical-fund thread, not a protocol-drain first-report.
- Immunefi: ENS audit-competition evaluation ongoing; researcher-pledge marketing. Not an incident.
- CertiKAlert, BlockSecTeam, CyversAlerts, GoPlusSecurity, rekt.news: no new first-report smart-contract drain with a fresh loss figure after the 14 Sep brief cutoff. GoPlus’s last required-monitor item in this window remains the 14 Sep Ampleforth reprint already scored as cancelled.
Sources & references
- https://x.com/DefimonAlerts/status/2099729577002053884
- https://x.com/DefimonAlerts/status/2099605487960444961
- https://x.com/Phalcon_xyz/status/2099741447776096270
- https://x.com/PeckShieldAlert/status/2099740493165068581
- https://x.com/PeckShieldAlert/status/2099744390143217951
- https://x.com/SlowMist_Team/status/2099779127662493875
- https://x.com/KelpDAO/status/2099740756865159562
- https://x.com/makinafi/status/2099761754100138097
- https://x.com/blockaid_/status/2099732957803999342
- https://x.com/blockaid_/status/2099738004776477083
- https://etherscan.io/address/0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8
- https://etherscan.io/address/0x4f0055926c839D1d960a82CBF84E2eE933958ebC
- https://etherscan.io/tx/0x0e7680b06cb8a6f86c149d9ba90d98e3d334e7b072dde03909d43fcfd98a8705
- https://etherscan.io/tx/0xe77f7513547d917e86e2ac8457b00e9f4336fee3908b9a674095603d467cde66
- https://etherscan.io/address/0xC70f00CD7E461686b04B0E912E309becA8b80ea0
- https://etherscan.io/address/0x80BF7Db69556D9521c03461978B8fC731DBBD4e4
- https://etherscan.io/address/0x2f7e143e27f2fa26ef3b8ac72698f1d321422f67
Editor’s note: Card live-loss is this window’s confirmed realized movement of the Safe’s rsETH stack (~$7.8M). Yoink capturing the tokens is not a victim-side recovery. Bridgeless ETHX is scored as a paused over-mint with $0 live loss and no dollar print from a required monitor. Blockaid follow-on legs and a circulating second-Safe ~$129k claim are not added to the box. Makina attribution is recorded as denied by the project. White-hat and bounty claims are recorded as claims. No how-to or exploit reproduction steps. Verify explorers and official channels before acting on any alert.
Read more
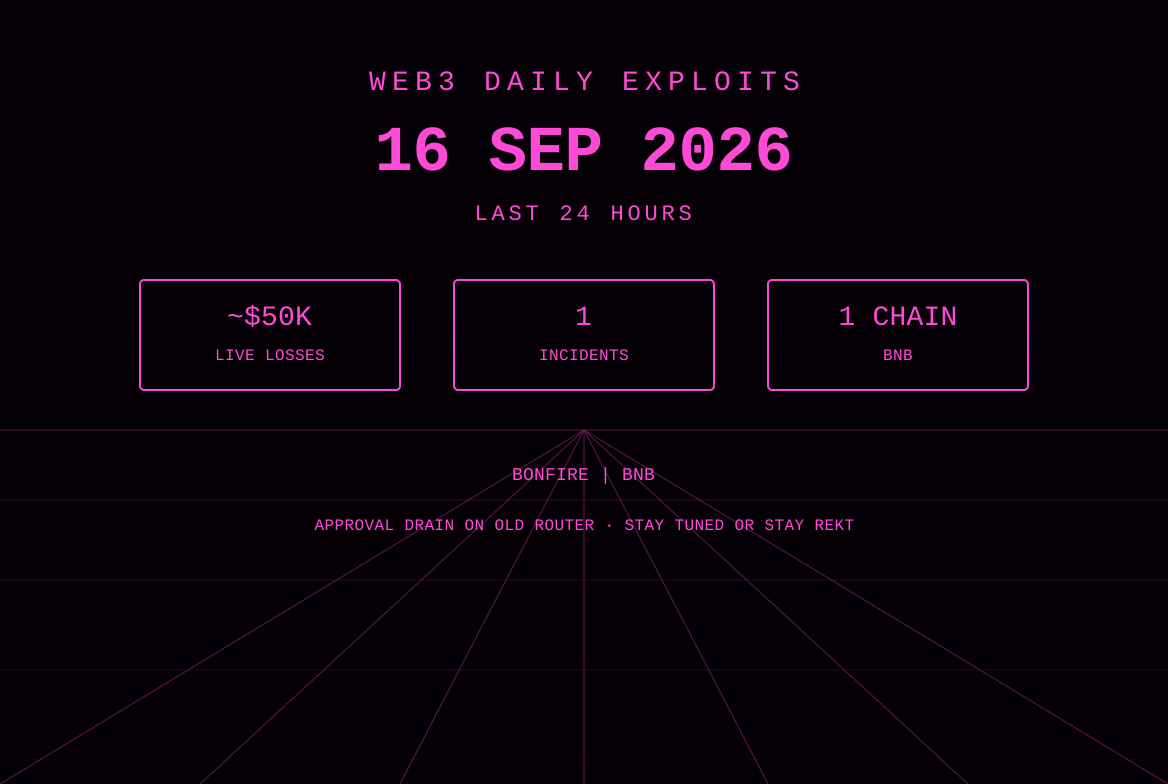
Web3 Daily Exploits — 16 Sep 2026: Bonfire ~$50k Approval Drain
BonfireSwap router on BNB Chain lost ~$47–50k after an access-control gap in transfer let anyone spend holders’ standing approvals. rsETH / yoink stack remains parked under Kelp’s temporary pause. Quiet window otherwise.
Web3 Daily Exploits — 14 Sep 2026: Yam $121k Gov Drain + Spiral 10.7 ETH
Yam proposal #45 finished as a realized ~$121k UMA-farm pull. SlowMist printed a same-block ~10.7 ETH (~$26.8k) spot-price borrow on SpiralHookV2. Ampleforth Governor Bravo #54 was cancelled on-chain.
Web3 Daily Exploits — 13 Sep 2026: Ampleforth $2.5M Gov Alert + Orb3 Bridge Window
No confirmed new protocol drain in the last 24 hours. Defimon flagged Ampleforth Governor Bravo proposal #54 aiming 2.5M USDC at a fresh proposer, and an Orb3 Orbit L1-bridge assertion that can confirm after block 26,005,988.
Web3 Daily Exploits — 12 Sep 2026: Zentra ~$140k Citrea Drain + ORB Reentrancy
First public desk confirmation of Zentra’s 9 Sep ctUSD reserve drain on Citrea (~$140k official / ~$143k Defimon), a SlowMist-confirmed ~$32.6k ORB reentrancy on BNB Chain, and a pending fake rollup assertion against Edgeless’s dormant L1 bridge (~9.2 ewETH at risk).