Web3 Daily Exploits — 13 Nov 2026: Pennysia ~$5K + Edel ~$300K
First-report incidents: Pennysia Settlement V1 on Ethereum exploited via arbitrary external call (~$5K observed in reported tx, residual approvals at risk); Edel Finance ~$300K EDEL tokens stolen and sold/blocked. Rujira, Across, Initia, Arcus remain UPDATEs.
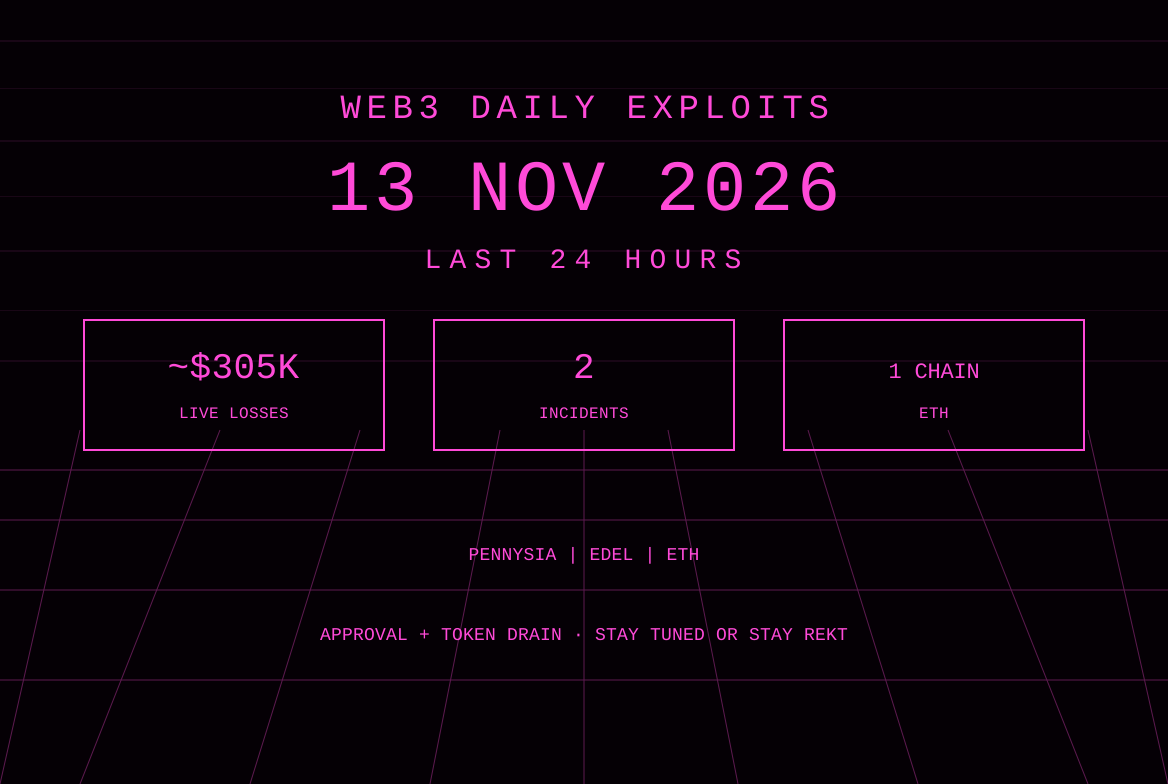
The 13 Nov America/Panama window records two first-reported protocol incidents with scored on-chain or project-reported movement. Pennysia Labs’ Settlement V1 contract on Ethereum was exploited through an arbitrary external call vulnerability, allowing an attacker to spend token approvals that users had previously granted to the contract but had not fully consumed. SlowMist issued a TI alert after user reports of stolen funds. On-chain data associated with the incident shows one related transaction that moved approximately 5,006.133489 USDC, 0.05 wstETH, and 101,000 YUNO. Exact total loss and number of affected users remain undisclosed at cutoff; further drains remain possible until remaining approvals are revoked. Separately, Edel Finance reported that approximately $300,000 worth of $EDEL tokens had been stolen and sold across the market. The team is working with authorities and exchanges to block remaining tokens; all stolen tokens have either been sold or blocked by exchanges including MEXC and BloFin. Method and source of the tokens remain undisclosed; a detailed post-mortem is expected. Live scored loss on this card is ~$305K across two incidents and one chain (Ethereum), based on the reported transaction amounts for Pennysia (USDC dominant) and the project-reported figure for Edel. The prior Rujira CCL skew flaw (~$200K, CosmWasm halted, reimbursement pledged), Across Protocol domain hijack (~$350K estimated, domain restored, reimbursement pledged), Initia L1 escrow halt (~$615K), and Arcus Perps accounting bug (~$2.23M withdrawn and treasury-covered) remain UPDATEs with no material new first-report scored figures in the last 24 hours.
Pennysia Settlement V1 — Ethereum — ~$5K — arbitrary external call / residual approval drain
What happened: After receiving user reports of stolen funds, SlowMist investigated @PennysiaLabs and confirmed that the Settlement contract on Ethereum (0x3aad97e5a91b8e43b7dc830aceb004307678795e, labeled Settlement V1) was exploited via an arbitrary external call. The vulnerability permitted the attacker to invoke token transferFrom (or equivalent) against approvals users had granted to the settlement contract for aggregator use. The design intended a single approval to the settlement contract to cover multiple downstream venues; residual unused allowances became spendable once the call target and calldata were under attacker control. SlowMist published the alert on 13 November, listing the attacker address 0x813a5ab666adeba907548235fbac087642878300 and urging immediate revocation of any approvals to the contract. Related on-chain activity reported at approximately 21:59 on 12 November moved the amounts noted above. White-hat on-chain messages referencing the same contract also appeared in the window, warning holders of residual unlimited or limited allowances. No official post-mortem or total-loss figure from the project had been published at cutoff. This is a new first-report incident.
Protocol / chain / asset: Pennysia Labs / Settlement V1 aggregator settlement contract on Ethereum. Assets moved in the reported transaction: USDC (dominant), wstETH, YUNO. Primary risk is any token previously approved to the contract and not yet revoked. Official sources: @SlowMist_Team alert; secondary coverage of the arbitrary external call.
Loss: No official total published. Reported related attack transaction moved ~5,006.13 USDC, 0.05 wstETH, and 101,000 YUNO. Live scored on this brief: ~$5K (USDC value dominant; other assets minor or unpriced). Exact final realized proceeds, full victim count, and any additional transactions remain under investigation. Residual approvals create ongoing exposure until revoked. Flag any subsequent quantified additional loss or official figure as material.
Attack type: Protocol logic / arbitrary external call. Attacker supplied call target and calldata that caused the settlement contract to spend existing user token approvals (transferFrom-style). Not a key compromise or private-key theft; classic residual-approval abuse once the contract could be made to call arbitrary targets.
Explorer URLs: Settlement contract: https://etherscan.io/address/0x3aad97e5a91b8e43b7dc830aceb004307678795e. Attacker: https://etherscan.io/address/0x813a5ab666adeba907548235fbac087642878300. Related transaction referenced in coverage: https://etherscan.io/tx/0x2716c50e450272240f68f2827bcb4a336c2ac520951e0e530154566c295b732d (interacts with the contract and shows USDC movement of the reported scale). Full set of drain transactions and exact calldata path remain under active investigation; no complete public post-mortem at cutoff.
Status: Confirmed by SlowMist TI alert after user reports. Contract remains live; risk continues for any unrevoked approvals. No project announcement of pause, patch, or reimbursement located at cutoff. Users who ever approved tokens to the Settlement contract are advised to revoke. Flag any official total, recovery details, or additional quantified drains as material. Exact technical root cause in the external-call path under investigation.
Sources: @SlowMist_Team official alert; secondary coverage (Lookonchain, BlockBeats, TokenPost, Odaily, TechFlow); on-chain references to the contract and reported amounts; DefimonAlerts on-chain messages referencing residual allowances on the same contract.
Edel Finance — Ethereum — ~$300K — token theft / source and method undisclosed
What happened: On 12 November 2026, Edel Finance (@edeldotfinance) announced that approximately $300,000 worth of $EDEL tokens had been stolen and sold across the market. The team stated they are working with authorities and cryptocurrency exchanges to block the hackers and investigate what happened. A follow-up noted that all tokens stolen have now either been sold or blocked by exchanges, specifically thanking MEXC and BloFin for acting quickly. A more detailed post-mortem is expected. No attacker address, transaction hashes, or technical root-cause details have been published at cutoff. This is a new first-report incident distinct from Edel’s earlier July 2026 oracle-manipulation event on its tokenized-stock lending markets.
Protocol / chain / asset: Edel Finance (margin layer for tokenized capital markets) / $EDEL token. Chain not explicitly stated in the announcement but consistent with prior Ethereum activity; scored as Ethereum pending confirmation. Primary impact is on the circulating supply of the native token via theft and market sale.
Loss: Project-reported: ~$300,000 worth of $EDEL tokens stolen and sold (or subsequently blocked). Live scored on this brief: ~$300K. Exact on-chain source, number of transactions, and final realized proceeds after any freezes remain under investigation. No official confirmation of user-fund impact beyond the token supply itself at cutoff.
Attack type: Undisclosed at cutoff. Classified by secondary sources as Protocol Logic / Unknown. Flag for update when post-mortem or explorer links appear.
Explorer URLs: No specific contract, attacker, or transaction hashes published by official sources at cutoff. Project announcement: https://x.com/edeldotfinance/status/2120902181104611616. Full details expected in the promised post-mortem.
Status: Confirmed by official project announcement. Tokens sold or blocked by exchanges. Investigation ongoing; post-mortem pending. No pause of core markets announced in the window. Flag any subsequent quantified additional loss, recovery figures, or technical details as material.
Sources: @edeldotfinance official announcements; DefiLlama classification (Protocol Logic / Unknown); secondary coverage noting the theft and exchange freezes.
Also noted
- Rujira AMM Strategies BTC/USDC CCL (UPDATE, not re-scored): First reported and covered in the 12 Nov brief. Skew calculation flaw allowed position imbalance; ~$200K losses ($175K Liquidy Finance, $25K users). CosmWasm halted; full reimbursement pledged; recovery estimated 1–2 days. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-12-nov-2026-rujira-200k-skew-ccl/. No material new scored loss in the last 24 hours.
- Across Protocol domain hijack (UPDATE, not re-scored): First reported 11 Nov. Domain across.to hijacked via Namecheap social engineering; phishing site collected approvals/permits. GoPlus ~$350K / Bitquery ~$348K estimates. Domain restored; Across pledged to make affected users whole. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-11-nov-2026-across-350k-domain-hijack/. No material new scored loss.
- Initia L1 escrow accounts (UPDATE, not re-scored): First reported 10 November. Compromised rollup infrastructure keys used to fabricate IBC transfers; ~$605K USDC + ~$10K other exited via Noble before halt. Most remaining assets on halted L1. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-10-nov-2026-initia-615k-ibc-escrow-halt/. No material new scored loss.
- Arcus Perps on Robinhood Chain (UPDATE, not re-scored): Accounting bug in subaccount transfers allowed ~$2.23M USDG withdrawal; shortfall fully covered from treasury. Whitehat offer extended. CertiK published analysis in the window (integer underflow framing). No new first-report user-loss figure.
- Other notes: DefimonAlerts carried on-chain messages including a white-hat recovery offer related to a Hyperliquid agent-key compromise (~48k USDC profit from 9–10 Nov activity) and additional residual-approval warnings. Scattered individual or non-protocol reports remain unverified and unattributed. No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts in the last 24 hours beyond the two scored items. Quiet window otherwise.
Sources and references
- SlowMist TI alert (Pennysia): https://x.com/SlowMist_Team/status/2121135351377047735
- Settlement contract: https://etherscan.io/address/0x3aad97e5a91b8e43b7dc830aceb004307678795e
- Attacker address: https://etherscan.io/address/0x813a5ab666adeba907548235fbac087642878300
- Related transaction: https://etherscan.io/tx/0x2716c50e450272240f68f2827bcb4a336c2ac520951e0e530154566c295b732d
- Edel Finance announcement: https://x.com/edeldotfinance/status/2120902181104611616
- Lookonchain coverage of Pennysia amounts: https://www.lookonchain.com/feeds/82046
- 12 Nov brief (Rujira): https://www.rektradar.xyz/web3-daily-exploits-12-nov-2026-rujira-200k-skew-ccl/
- 11 Nov brief (Across): https://www.rektradar.xyz/web3-daily-exploits-11-nov-2026-across-350k-domain-hijack/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh scored user-loss figures beyond the Pennysia and Edel items.
Editor’s note: the scored live loss on this card is ~$305K across two first-report incidents (Pennysia Settlement residual approval drain via arbitrary external call on Ethereum ~$5K; Edel Finance ~$300K EDEL token theft). Figures based on reported transaction amounts and project announcement; full totals and residual risk for Pennysia remain until revocations. Rujira, Across, Initia and Arcus remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
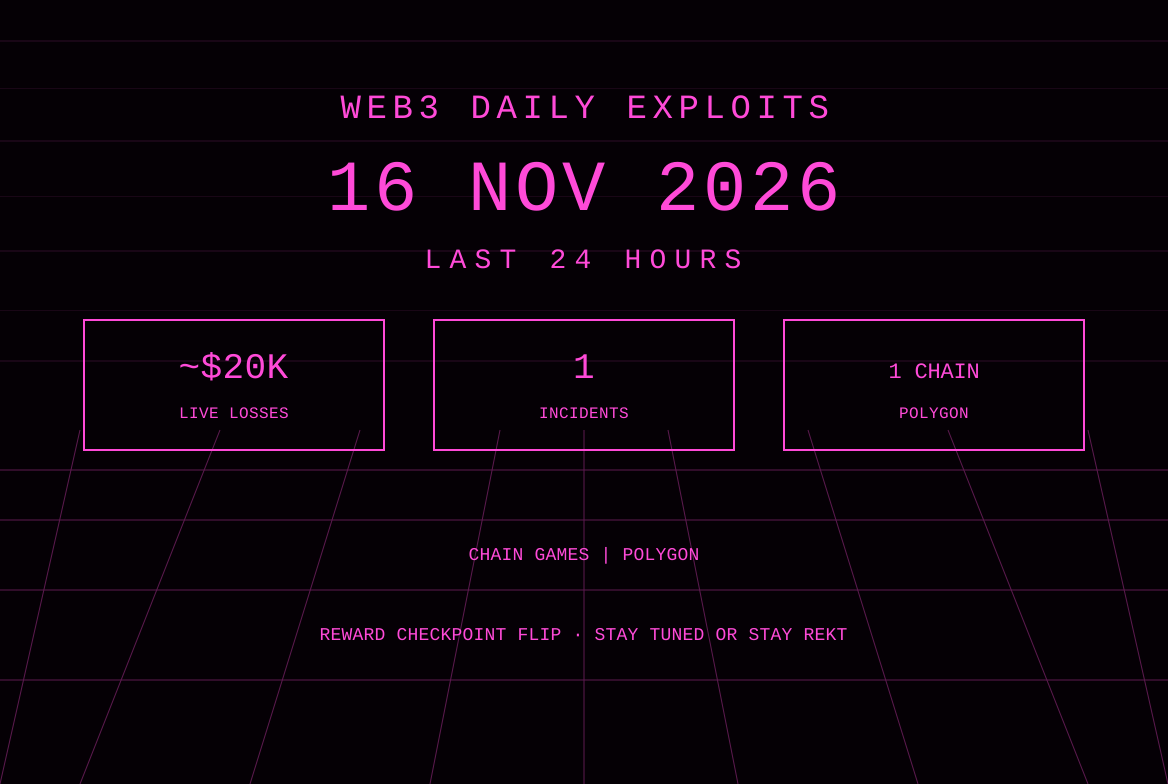
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.
Web3 Daily Exploits — 14 Nov 2026: Pool Party ~$215K Snapshot
First-report incident: Pool Party snapshot contracts on Arbitrum and Base exploited via recorded position manipulation (~$215K, 15 pools). Fix deployed; funds converted toward XMR. Independent tracing notes ~$212.7K USDC laundering leg. Pennysia, Edel, Rujira remain UPDATEs.
Web3 Daily Exploits — 12 Nov 2026: Rujira ~$200K Skew CCL
First-report incident: Rujira AMM Strategies BTC/USDC CCL on THORChain exploited via skew calculation flaw, ~$200K losses ($175K Liquidy Finance, $25K users). CosmWasm halted; full reimbursement pledged. Across domain, Initia, Arcus remain UPDATEs.