Web3 Daily Exploits — 14 Nov 2026: Pool Party ~$215K Snapshot
First-report incident: Pool Party snapshot contracts on Arbitrum and Base exploited via recorded position manipulation (~$215K, 15 pools). Fix deployed; funds converted toward XMR. Independent tracing notes ~$212.7K USDC laundering leg. Pennysia, Edel, Rujira remain UPDATEs.
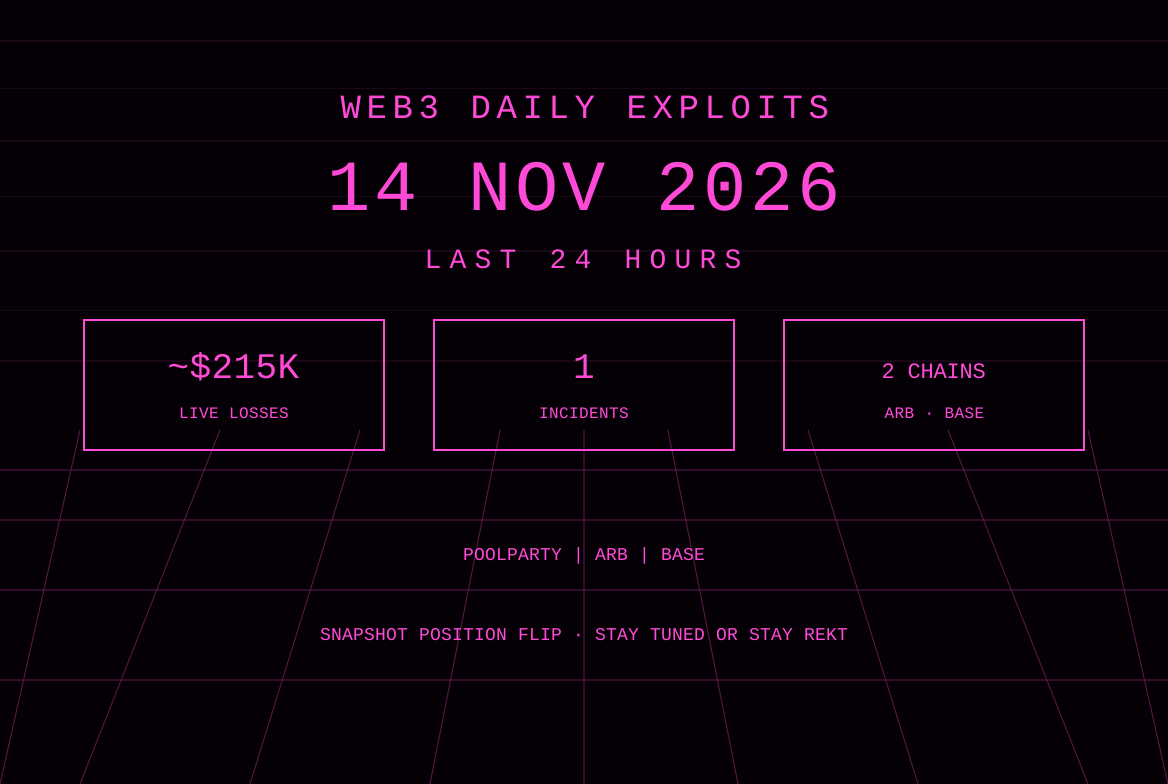
The 14 Nov America/Panama window records one first-reported protocol incident with a project-confirmed scored loss. Pool Party disclosed that an attacker drained 15 pools (12 on Arbitrum, 3 on Base) between 01:34 and 03:38 UTC on 13 November, for a total of approximately $215k. The team attributed the drain to a vulnerability in per-pool snapshot contracts that record user positions. An attacker altered a recorded position, deposited 10 USDC, and withdrew the pool’s funds. Pools on Polygon and Robinhood Chain were unaffected. The fix was deployed across all four chains the same day. The attacker address was published as 0x2075c17abbd077cf6406736bb7047ed446ab7f8f; the team stated the funds had already been converted toward XMR and that the incident was reported to law enforcement and involved exchanges. A white-hat bounty offer (10% keep, return the rest) was posted on-chain. Independent tracing published on 14 November mapped a subsequent USDC laundering leg of approximately $212,705 through a relay wallet and multiple one-time deposit addresses, with notes on residual XMR1 balances on public ledgers (later corrected regarding possible reserve mechanics). No additional first-report protocol drains with fresh confirmed user-loss figures appeared from monitored accounts in the same window. Prior items (Pennysia Settlement residual approvals, Edel token theft, Rujira CCL skew, Across domain, Initia escrow, Arcus accounting) remain UPDATEs with no material new scored losses.
Pool Party — Arbitrum / Base — ~$215K — snapshot position manipulation
What happened: On 13 November 2026, Pool Party (@PoolParty_xyz) published a security incident notice. Between 01:34 and 03:38 UTC an attacker drained 15 pools: 12 on Arbitrum and 3 on Base. Total loss reported by the project is approximately $215k. Each pool maintains a snapshot contract that records the position of each user. The attacker found a vulnerability in that recording logic, changed their recorded position, deposited 10 USDC, and withdrew the funds from the pool. The team confirmed the fix is live on all four chains (Arbitrum, Base, Polygon, Robinhood Chain). Secondary on-chain tracing referenced a loop involving Add Liquidity (10 USDC) → syncInvestor() → Withdraw and a subsequent relay wallet (0x4bf62A3dA5c8d8488bC7b5bB3856940c026a15Ac) used in laundering. The project stated the attacker had already converted the funds to XMR and that law enforcement plus involved exchanges were notified. Attacker address published: 0x2075c17abbd077cf6406736bb7047ed446ab7f8f. DefimonAlerts relayed the project’s on-chain bounty offer (keep 10%, return the remainder to 0x524d0A20EDFD36adD3a5eF5f5939958dF098B149) and a later message regarding a DAI receipt linked to the incident. Independent analysis on 14 November traced the USDC portion (~$212.7k) across 17 chunks; residual XMR1 (~38.53) was noted on public ledgers, with a subsequent correction that such balances may represent normal reserve inventory rather than stuck proceeds. This is a new first-report incident for the last-24h window, with material tracing updates in the current cutoff.
Protocol / chain / asset: Pool Party (on-chain fund / Uniswap-based pools) on Arbitrum and Base. Assets primarily USDC and related pool tokens. Official announcement from @PoolParty_xyz. Secondary tracing by independent analysts noted USDC laundering legs totaling ~$212.7k via a relay address, with residual XMR1 observations later qualified.
Loss: Project-reported: approximately $215k. Live scored on this brief: ~$215K. USDC laundering leg independently measured at $212,705. Exact composition of non-USDC assets and final realized proceeds after any freezes or failed swaps remain under investigation. No official breakdown of per-pool losses published at cutoff.
Attack type: Protocol logic / snapshot accounting flaw. Attacker manipulated the recorded investor position in the snapshot contract, then used a minimal deposit plus the inflated recorded balance to withdraw the pool’s funds. Not a key compromise. Fix deployed same day.
Explorer URLs: Attacker EOA: https://arbiscan.io/address/0x2075c17abbd077cf6406736bb7047ed446ab7f8f (Arbitrum) and corresponding Base activity. Project announcement thread: https://x.com/PoolParty_xyz/status/2121307902430359906. Relay wallet referenced in tracing: 0x4bf62A3dA5c8d8488bC7b5bB3856940c026a15Ac. Full set of individual pool drain transactions under active investigation; no complete public post-mortem with every hash at cutoff.
Status: Confirmed by official project announcement. Vulnerability fixed on all four chains. Funds largely converted toward privacy rails (XMR / XMR1). Bounty offer open. Independent tracing of USDC legs published 14 November with subsequent qualification on residual balances. Investigation and law-enforcement reporting ongoing. Flag any quantified recovery, residual visible funds, or detailed technical post-mortem as material.
Sources: @PoolParty_xyz official thread; DefimonAlerts relay of incident and on-chain messages; secondary on-chain tracing noting syncInvestor() loop, relay wallet, and laundering path (with correction on XMR1 interpretation).
Also noted
- Pennysia Settlement V1 (UPDATE, not re-scored): First reported and covered in the 13 Nov brief. Arbitrary external call allowed residual approval drain on Ethereum; reported related tx ~$5K (USDC dominant). SlowMist urged revocation. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-13-nov-2026-pennysia-5k-settlement-approval/. No material new scored loss in the last 24 hours.
- Edel Finance token theft (UPDATE, not re-scored): ~$300K $EDEL stolen and sold or blocked. Method undisclosed. Post-mortem pending. Prior coverage same 13 Nov brief. No new figures.
- Rujira AMM Strategies BTC/USDC CCL (UPDATE, not re-scored): Skew calculation flaw, ~$200K. CosmWasm halted; reimbursement pledged; upgraded contract in progress. Prior: https://www.rektradar.xyz/web3-daily-exploits-12-nov-2026-rujira-200k-skew-ccl/.
- Across Protocol domain hijack (UPDATE): ~$350K estimated phishing drain. Domain restored; reimbursement pledged. Prior 11 Nov brief.
- Initia L1 escrow (UPDATE): ~$615K via fabricated IBC. L1 halted. Prior 10 Nov brief.
- Arcus Perps (UPDATE): Accounting bug, ~$2.23M withdrawn and treasury-covered. CertiK analysis previously noted. No new user-loss figure.
- Other notes: Scattered on-chain messages and residual-approval warnings continued. No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts (DefimonAlerts, CertiKAlert, Phalcon, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news) in the last 24 hours beyond the Pool Party item and its tracing updates. Quiet window otherwise.
Sources and references
- Pool Party official announcement: https://x.com/PoolParty_xyz/status/2121307902430359906
- DefimonAlerts on-chain messages: https://x.com/DefimonAlerts/status/2121305457885053280, https://x.com/DefimonAlerts/status/2121482855398215788
- Attacker address (Arbitrum): https://arbiscan.io/address/0x2075c17abbd077cf6406736bb7047ed446ab7f8f
- 13 Nov brief (Pennysia / Edel): https://www.rektradar.xyz/web3-daily-exploits-13-nov-2026-pennysia-5k-settlement-approval/
- 12 Nov brief (Rujira): https://www.rektradar.xyz/web3-daily-exploits-12-nov-2026-rujira-200k-skew-ccl/
- Monitored accounts checked through the 14 Nov 2026 America/Panama cutoff. No additional first-report protocol exploits with fresh scored user-loss figures beyond Pool Party and its tracing updates.
Editor’s note: the scored live loss on this card is ~$215K across one first-report incident (Pool Party snapshot position manipulation on Arbitrum and Base). Figure is the project’s reported total. Fix is live. Independent tracing of the USDC laundering leg and residual observations added in this update. Prior items remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
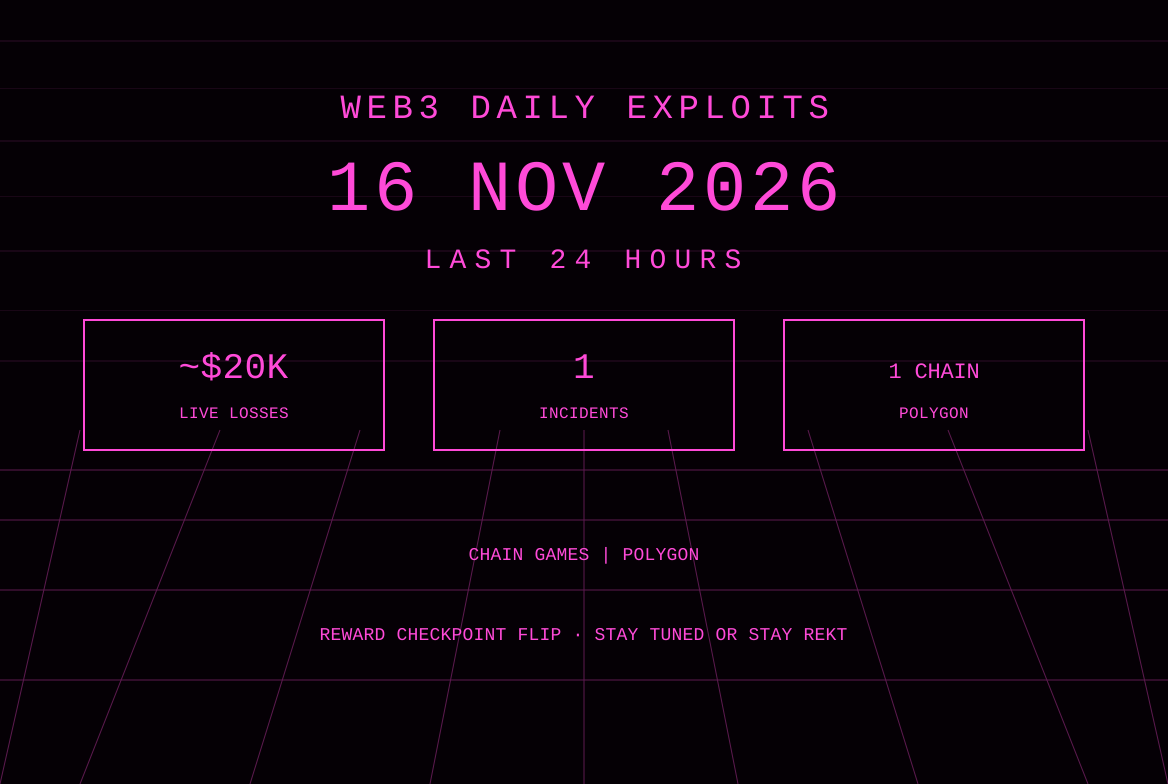
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.
Web3 Daily Exploits — 13 Nov 2026: Pennysia ~$5K + Edel ~$300K
First-report incidents: Pennysia Settlement V1 on Ethereum exploited via arbitrary external call (~$5K observed in reported tx, residual approvals at risk); Edel Finance ~$300K EDEL tokens stolen and sold/blocked. Rujira, Across, Initia, Arcus remain UPDATEs.
Web3 Daily Exploits — 12 Nov 2026: Rujira ~$200K Skew CCL
First-report incident: Rujira AMM Strategies BTC/USDC CCL on THORChain exploited via skew calculation flaw, ~$200K losses ($175K Liquidy Finance, $25K users). CosmWasm halted; full reimbursement pledged. Across domain, Initia, Arcus remain UPDATEs.