Web3 Daily Exploits — 11 Nov 2026: Across ~$350K Domain Hijack
First-report incident: Across Protocol domain across.to hijacked via Namecheap social engineering; phishing site served wallet-drainer approvals/permits. GoPlus estimates ~$350K user losses across ETH, ARB, BASE, BNB, Ink, Plasma. Official restored domain, pledged to make affected users whole. Initia and Arcus remain UPDATEs.
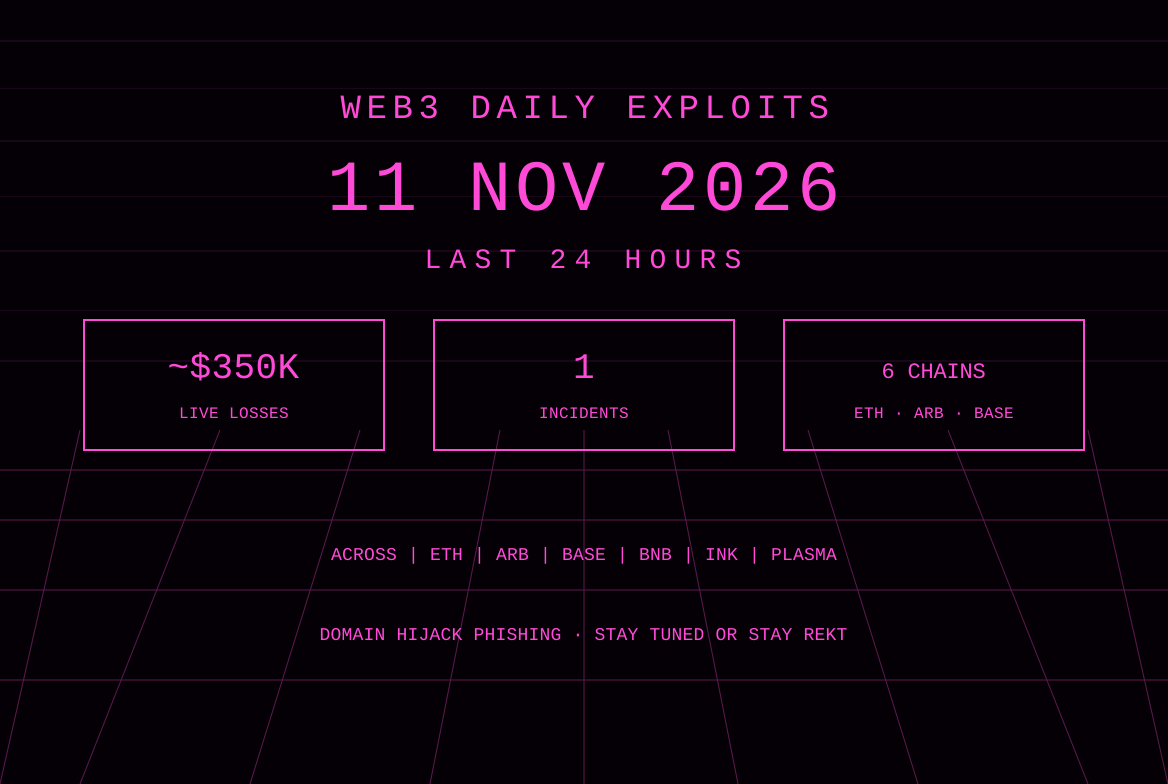
The 11 Nov America/Panama window records one first-reported incident with confirmed user-loss estimates. Across Protocol’s across.to domain was taken over at approximately 18:45 UTC on 10 November via a social engineering attack on registrar Namecheap. The attacker replaced the frontend with a phishing site that prompted users to sign token approvals, Permit2 authorizations, or EIP-2612 permits, enabling subsequent drains. GoPlusSecurity estimated total user losses at approximately $350,000 across Ethereum, Arbitrum, Base, BNB Chain, Ink, and Plasma. Bitquery traced roughly $348,000 from nine wallets on five chains between 19:02 and 21:53 UTC. Across confirmed the vector, took the site offline with SEAL911 and Cloudflare assistance, restored the domain early 11 November with help from Namecheap founder Richard Kirkendall, and stated all affected users will be made whole. No third-party integrations or API users were affected. Live scored loss on this card is ~$350K across one incident and six chains. The prior Initia L1 escrow halt (~$615K) and Arcus Perps accounting bug (~$2.23M withdrawn, treasury covered) remain UPDATEs with no material new first-report scored figures in the last 24 hours. Arcus has since published a whitehat offer.
Across Protocol domain hijack — multi-chain — ~$350K — registrar social engineering / phishing drainer
What happened: At ~18:45 UTC on 10 November 2026 an attacker gained control of the across.to domain through a social engineering attack on Namecheap. The legitimate frontend was replaced with a phishing page designed to collect wallet signatures. Across received an alert within 15 minutes, began takedown, and SEAL911 flagged the domain as phishing with major wallet providers. Cloudflare marked the domain at risk and later removed DNS records, rendering the malicious site inaccessible. Some users who visited during the brief window before full block connected wallets and signed approvals or permits. Across stated that earlier frontend users, API users, and third-party integrators were unaffected. On 11 November at ~01:16 UTC Across announced the domain was back under its control, all systems operational, and that all affected users will be made whole. A full post-mortem is promised. Users who interacted during the window were advised to revoke permissions.
Protocol / chain / asset: Across Protocol (cross-chain bridge/intents). Domain: across.to. Chains affected per GoPlus: Ethereum, Arbitrum, Base, BNB Chain, Ink, Plasma. Attack type was frontend phishing, not a smart-contract exploit of the bridge itself.
Loss: Official: undisclosed number of users or exact total; Across pledged full reimbursement. GoPlus: ~$350,000 across six chains. Bitquery on-chain investigation: ~$348,000 from nine wallets on five chains (one large Aave depositor ~$305K). Live scored on this brief: ~$350K (GoPlus estimate). Exact final realized proceeds and full victim list remain under investigation; reimbursement status pending post-mortem.
Attack type: Domain hijack via registrar social engineering followed by phishing site collecting token approvals, Permit2, and EIP-2612 permits for subsequent drains. Not a core protocol or bridge contract vulnerability.
Explorer URLs: Official incident posts: https://x.com/AcrossProtocol/status/2120231513459433747 (initial alert), https://x.com/AcrossProtocol/status/2120278803318489362 (details), https://x.com/AcrossProtocol/status/2120324818385912082 (restored). GoPlus and Bitquery reports contain address and transaction breakdowns as available. No single public attacker EOA published as primary by official sources at cutoff.
Status: Confirmed by official Across announcements. Domain restored, systems operational. Compensation pledged. Full scope, exact loss total, and post-mortem pending. Approvals signed on the malicious site may remain exploitable until revoked. Flag any subsequent quantified recovery or official loss figure as material.
Sources: @AcrossProtocol official; GoPlusSecurity estimates; Bitquery investigation; The Block; Cointelegraph; CryptoTimes; DefiPrime; SEAL911 / Cloudflare assistance noted by official.
Also noted
- Initia L1 escrow accounts (UPDATE, not re-scored): First reported 10 November. Compromised rollup infrastructure keys used to fabricate IBC transfers; ~$605K USDC + ~$10K other exited via Noble before halt at 06:18 UTC. Most remaining assets still on halted L1. Full scope ongoing. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-10-nov-2026-initia-615k-ibc-escrow-halt/. No material new scored loss in the last 24 hours.
- Arcus Perps on Robinhood Chain (UPDATE, not re-scored): Incident activity 9 November ET. Accounting bug in subaccount transfers allowed one newly created account to inflate balance and withdraw 2,234,391 USDG (~$2.23M). Additional ~$3M in requests blocked by bridge rate limit and reversed. Arcus patched within ~1 hour, covered full shortfall from company treasury, blocked exploiter addresses. User balances unaffected. Official report published. Exploiter address published: 0xeFbf442599310E5CeE1A4EDd5c66334c5f30b3Dd. On 11 November Arcus (via on-chain message relayed by DefimonAlerts) offered a whitehat resolution: return 90% (~$2.011M in ETH/WETH/DAI) to recovery address 0x1d4324C84e36D8104BDF327474755E5Aa0cFeBc9 by 13 November 01:00 UTC, keep 10% as bounty. No new first-report user-loss figure beyond the covered treasury shortfall.
- Ankr Ethereum cross-chain bridge (UPDATE, not re-scored): First reported 9 November. ~$304.5K via forged receipts with valid signatures reusing one already-redeemed Optimism deposit. No material new scored loss.
- Prior items (UPDATE, not re-scored): ACryptoS vaults, Keplr/Web3Auth, Loopscale, TENDRIL, Binance, Mercado Bitcoin, and earlier incidents. No material new first-report scored figures in the last 24 hours.
- Other notes: No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts. Scattered individual reports remain unverified and unattributed to any protocol. Supply-chain and malware notes from prior windows remain non-scored.
Sources and references
- Across official alert: https://x.com/AcrossProtocol/status/2120231513459433747
- Across details: https://x.com/AcrossProtocol/status/2120278803318489362
- Across restored: https://x.com/AcrossProtocol/status/2120324818385912082
- Bitquery investigation: https://bitquery.io/investigations/across-protocol-domain-hijack
- The Block coverage: https://www.theblock.co/news/defi/2026-11-11-crosschain-protocol-across-restores-systems-after-domain-hijack-437843
- 10 Nov brief (Initia): https://www.rektradar.xyz/web3-daily-exploits-10-nov-2026-initia-615k-ibc-escrow-halt/
- Arcus official incident report: https://arcus.xyz/blog/arcus-incident-report-november-9-2026
- Arcus whitehat offer (on-chain via DefimonAlerts): https://x.com/DefimonAlerts/status/2120322800921584119
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh scored user-loss figures beyond the Across item.
Editor’s note: the scored live loss on this card is ~$350K across one first-report incident (Across domain hijack phishing). Official figure not yet published; third-party estimates (GoPlus ~$350K, Bitquery ~$348K) used for scoring. Across pledged full reimbursement. Initia and Arcus remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
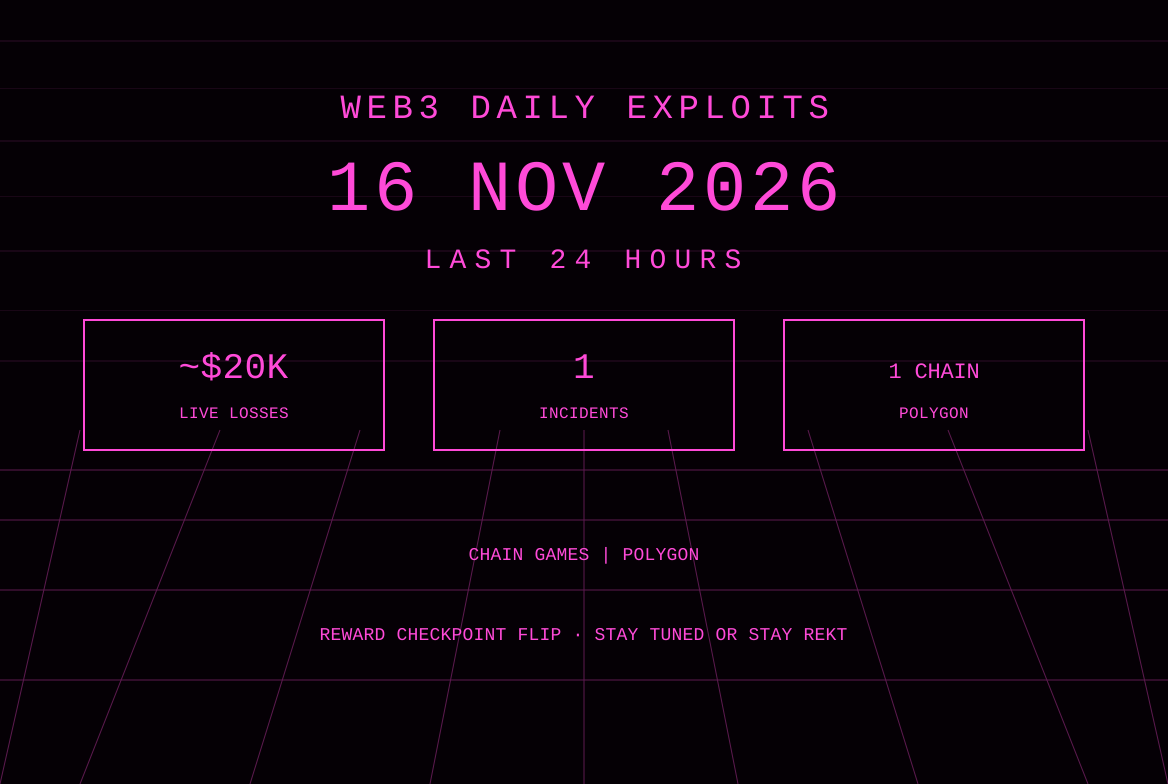
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.
Web3 Daily Exploits — 14 Nov 2026: Pool Party ~$215K Snapshot
First-report incident: Pool Party snapshot contracts on Arbitrum and Base exploited via recorded position manipulation (~$215K, 15 pools). Fix deployed; funds converted toward XMR. Independent tracing notes ~$212.7K USDC laundering leg. Pennysia, Edel, Rujira remain UPDATEs.
Web3 Daily Exploits — 13 Nov 2026: Pennysia ~$5K + Edel ~$300K
First-report incidents: Pennysia Settlement V1 on Ethereum exploited via arbitrary external call (~$5K observed in reported tx, residual approvals at risk); Edel Finance ~$300K EDEL tokens stolen and sold/blocked. Rujira, Across, Initia, Arcus remain UPDATEs.