Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
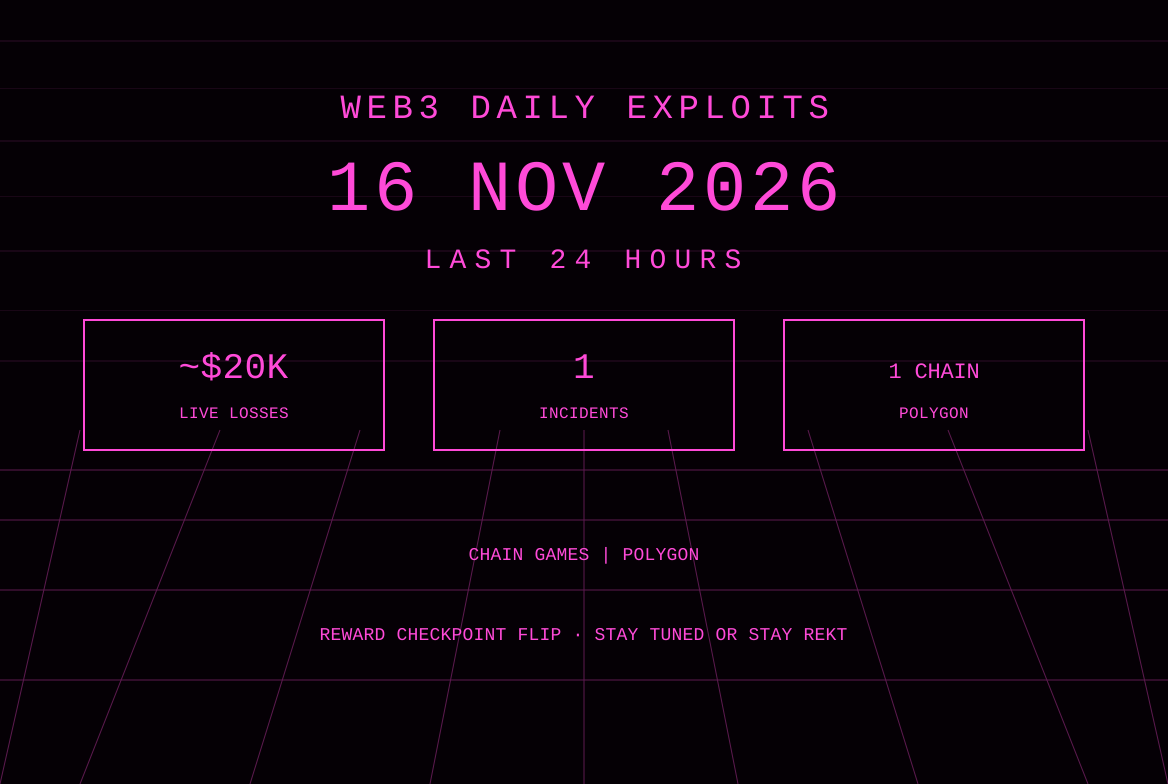
The 16 Nov America/Panama window records one first-reported protocol incident with a project- and on-chain-confirmed scored loss of approximately $20,000. Chain Games (RealChainGames) staking contracts on Polygon were exploited on 15 November through a failure to synchronize reward checkpoints during share transfers. Newly created recipient contracts could repeatedly claim historical rewards via restake(), allowing an attacker to inflate an initial 1,000 CHAIN position into more than 36 million shares across 360 cycles before redeeming through the normal withdrawal path. SlowMist and DefimonAlerts published analyses on 16 November; the project confirmed the drain of about 37.98 million CHAIN (~$20K), disabled delegation, and stated that stakers would be made whole. No bridge or token contract was affected. In parallel, Kava published its official HARD Lend incident report confirming the prior 53.9 million KAVA extraction, that the exploit is blocked, and that a governance proposal will permanently wind down the lending function. Luxor reported an AI-enabled compromise of its Commander fleet-management software that redirected hashrate from over a dozen client accounts; the company patched within two hours and pledged full compensation. No additional first-report protocol drains with fresh confirmed user-loss figures appeared from monitored accounts in the same window. Prior items remain UPDATEs.
Chain Games — Polygon — ~$20K — reward checkpoint desync / share inflation
What happened: On 15 November 2026, between approximately 03:23 and 04:38 UTC, an attacker exploited older CHAIN delegation staking contracts on Polygon. The contracts failed to synchronize reward checkpoints when shares were transferred. This allowed newly created recipient contracts to call restake() and claim historical rewards repeatedly. Across 360 cycles the attacker inflated an initial stake worth 1,000 CHAIN into more than 36 million shares, then redeemed them through the standard withdrawal process, draining roughly 36–38 million CHAIN (valued at ~$20K) from the shared staking escrow. SlowMist identified the vulnerable contract as 0x4b197ce70af7faece9544ef29b76c1cccd54d7ac, attacker 0x571d0ec17d84fdee89f5c9cf6b2fd930205e776f, and victim/escrow 0x1cb1f66bde215161d4b6598ddc2defbbc009c5a4. DefimonAlerts described a related unstakeClaimTokens / transferFunds path that paid out 36,007,148 CHAIN. The project confirmed the incident the same day, disabled delegation for all validators at 21:34 UTC, took a pre-attack snapshot of legitimate positions, and stated that all stakers, delegators, and validators will be made whole. The Polygon PoS bridge and the CHAIN token contracts themselves were not compromised; every CHAIN on Polygon remains fully backed on Ethereum.
Protocol / chain / asset: Chain Games (RealChainGames) older delegation staking contracts on Polygon. Primary asset: CHAIN token. Official confirmation from @RealChainGames; analyses by SlowMist and DefimonAlerts.
Loss: On-chain measured and project-reported: approximately 36–38 million CHAIN, valued at ~$20,000 at the time of the incident. Live scored on this brief: ~$20K. Exact residual holdings after any recovery steps remain under investigation. Project has committed to making all affected stakers whole via the pre-attack snapshot.
Attack type: Protocol logic / reward accounting error. Missing checkpoint synchronization on share transfer permitted repeated historical reward claims and share inflation, followed by normal withdrawal. Not a key compromise. Delegation has been disabled; snapshot taken for restitution.
Explorer URLs: Vulnerable contract: https://polygonscan.com/address/0x4b197ce70af7faece9544ef29b76c1cccd54d7ac. Attacker: https://polygonscan.com/address/0x571d0ec17d84fdee89f5c9cf6b2fd930205e776f. Victim/escrow: https://polygonscan.com/address/0x1cb1f66bde215161d4b6598ddc2defbbc009c5a4. Individual transaction hashes are referenced in the SlowMist and DefimonAlerts posts; readers are directed to those for the full set.
Status: Confirmed by on-chain data, SlowMist, DefimonAlerts, and the project. Delegation disabled; snapshot of legitimate balances taken at Polygon block 97338356. Restitution promised. Investigation and any residual fund movement continue. Flag any quantified recovery or detailed technical post-mortem as material.
Sources: SlowMist TI Alert (16 Nov); DefimonAlerts (16 Nov); @RealChainGames official statement (15 Nov); secondary coverage.
Also noted
- Kava Lend / HARD Lend (UPDATE): Official incident report published 16 November on Medium. Confirms approximately 53.9 million KAVA taken on 14 November via lending-accounting vulnerability that inflated BUSD collateral. Exploit blocked; no new KAVA minted; chain security unaffected; individual user deposits largely unaffected. ~49.2 million KAVA bridged to BNB Chain. Portion of funds frozen; recovery coordination underway. Governance proposal planned to permanently disable new lending/borrowing and wind down remaining positions. Prior scored coverage remains the 15 Nov brief. No new first-report loss figure.
- Luxor Commander (infrastructure note / not scored as protocol drain): On 14–15 November Luxor reported an AI-enabled attack on its Commander fleet-management software that redirected hashrate from over a dozen client accounts to another pool (reported as OCEAN). Company detected the activity, patched the vulnerability within two hours, and began restoring settings. No client funds or data were stolen; attackers received approximately 0.162 BTC (~$10.5K) in pool payouts. Luxor pledged full compensation to affected clients as if hashrate had mined normally. Isolated to Commander; other services unaffected. Not a smart-contract or on-chain protocol exploit.
- HyprEarn Perps (UPDATE / unquantified): Prior disclosure of unauthorized trading on a small number of Hyperliquid accounts that had authorized API agent wallets. Agents cannot withdraw. Cause, accounts, and any loss remain undisclosed. Not scored.
- Prior items (UPDATE): Pool Party, Pennysia, Edel, Rujira, Across, Initia, Arcus and earlier items remain without material new first-report scored losses in the last 24 hours.
- Other notes: No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts (DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news) in the last 24 hours beyond the Chain Games item. Quiet window otherwise for scored protocol losses.
Sources and references
- SlowMist TI Alert: https://x.com/SlowMist_Team/status/2122271777825128691
- DefimonAlerts: https://x.com/DefimonAlerts/status/2122239153056149613
- RealChainGames official statement: https://x.com/RealChainGames/status/2122112343970808002
- Kava official HARD Lend report: https://medium.com/@Kava_Chain/hard-lend-security-incident-579888f8dd73
- Kava announcement: https://x.com/KAVA_CHAIN/status/2122266605677580750
- Luxor Commander coverage: https://www.theblock.co/news/business/2026-11-15-luxor-attack-client-hashrate-440810
- 15 Nov brief (Kava Lend): https://www.rektradar.xyz/web3-daily-exploits-15-nov-2026-kava-lend-3-7m-arithmetic/
- Monitored accounts checked through the 16 Nov 2026 America/Panama cutoff. No additional first-report protocol exploits with fresh scored user-loss figures beyond Chain Games.
Editor’s note: the scored live loss on this card is ~$20K across one first-report incident (Chain Games reward checkpoint desync on Polygon staking). Figure based on on-chain measured CHAIN and project valuation. Kava Lend remains an UPDATE with official confirmation and wind-down plan. Luxor Commander is noted as an infrastructure hashrate redirect with compensation pledged, not scored as a protocol drain. Prior items remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
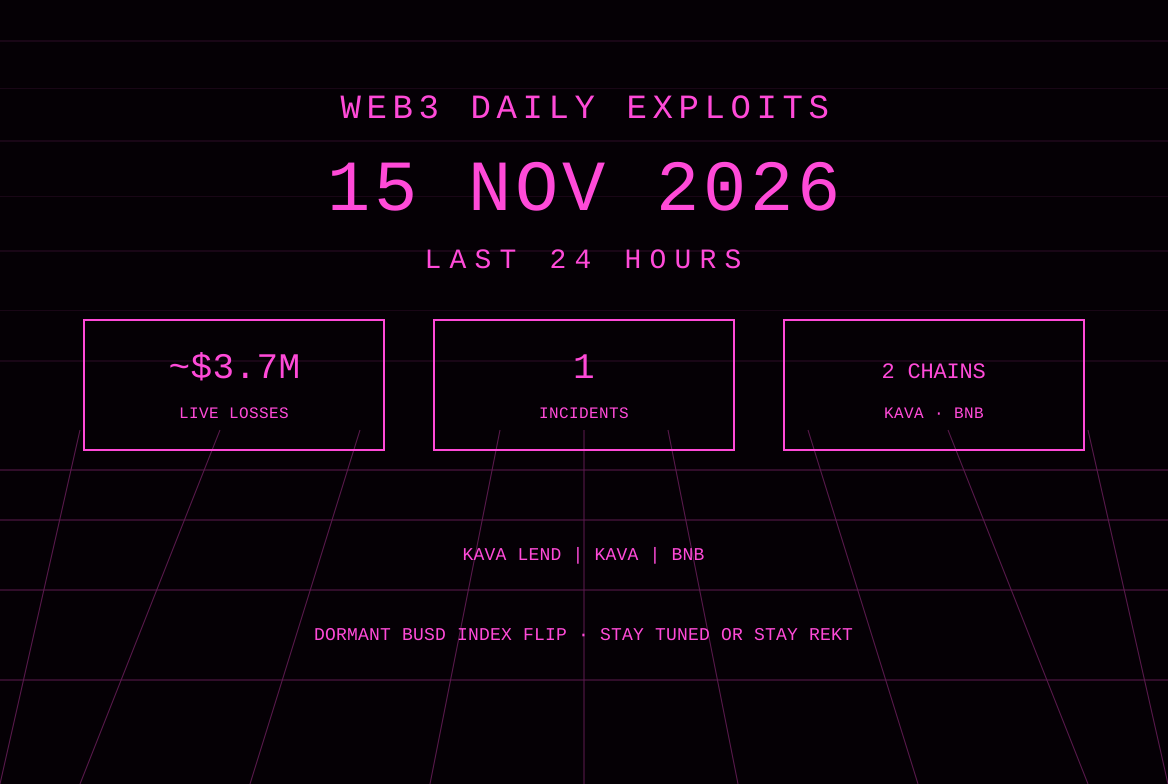
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.
Web3 Daily Exploits — 14 Nov 2026: Pool Party ~$215K Snapshot
First-report incident: Pool Party snapshot contracts on Arbitrum and Base exploited via recorded position manipulation (~$215K, 15 pools). Fix deployed; funds converted toward XMR. Independent tracing notes ~$212.7K USDC laundering leg. Pennysia, Edel, Rujira remain UPDATEs.
Web3 Daily Exploits — 13 Nov 2026: Pennysia ~$5K + Edel ~$300K
First-report incidents: Pennysia Settlement V1 on Ethereum exploited via arbitrary external call (~$5K observed in reported tx, residual approvals at risk); Edel Finance ~$300K EDEL tokens stolen and sold/blocked. Rujira, Across, Initia, Arcus remain UPDATEs.
Web3 Daily Exploits — 12 Nov 2026: Rujira ~$200K Skew CCL
First-report incident: Rujira AMM Strategies BTC/USDC CCL on THORChain exploited via skew calculation flaw, ~$200K losses ($175K Liquidy Finance, $25K users). CosmWasm halted; full reimbursement pledged. Across domain, Initia, Arcus remain UPDATEs.