Web3 Daily Exploits — 10 Nov 2026: Initia ~$615K IBC Escrow Halt
First-report incident: Initia L1 halted after unauthorized transfers from rollup escrow accounts using compromised infrastructure keys to fabricate IBC transfers; ~$605K USDC + ~$10K other tokens exited via Noble. Live scored ~$615K across Initia and Noble. Ankr bridge, ACryptoS, and NEAR AI remain UPDATEs.
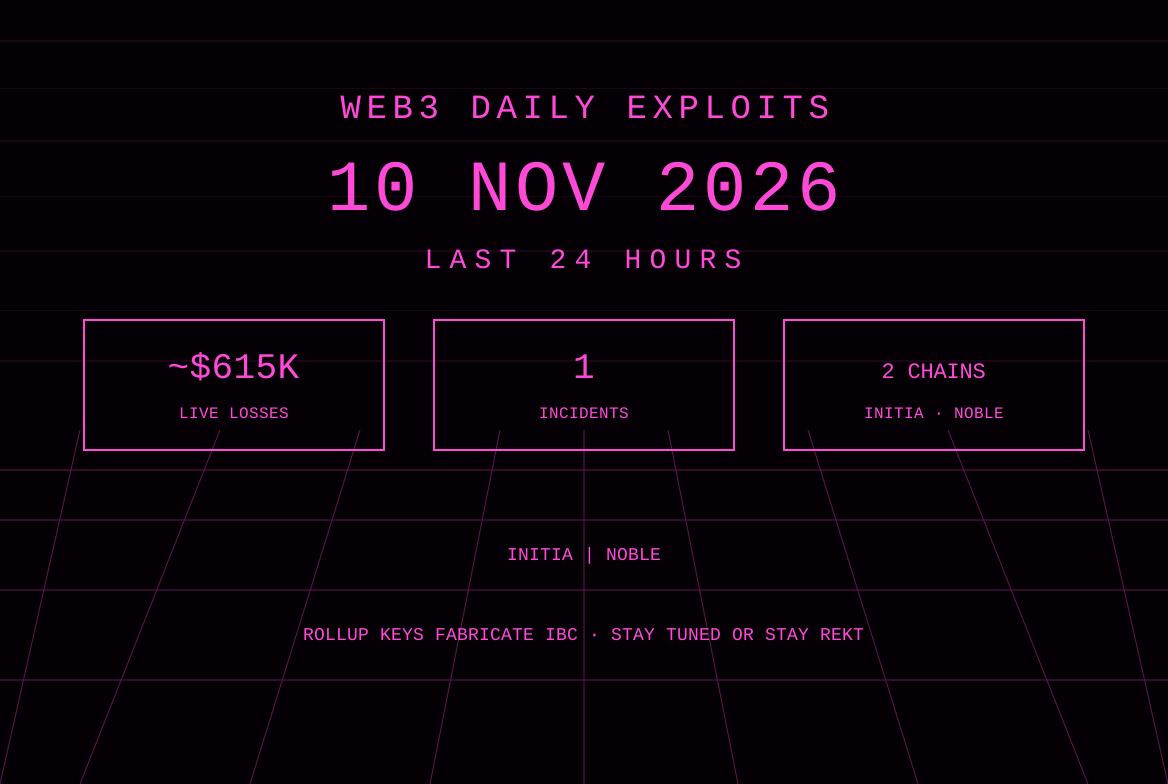
The 10 Nov America/Panama window records one first-reported protocol incident with a confirmed scored loss. Initia halted its L1 at 06:18 UTC after identifying unauthorized transfers from escrow accounts holding assets bridged to several rollups. Preliminary investigation attributes the transfers to compromised rollup infrastructure keys that allowed an attacker to fabricate IBC transfers. Approximately $605,000 USDC left via Noble along with roughly $10,000 in other tokens before the pause; most remaining assets moved out of escrow remain on the halted L1. Live scored loss on this card is ~$615K across one incident and two chains (Initia L1 and Noble). The prior Ankr bridge (~$304.5K), ACryptoS vault (~$665K), Zenji (~$4.9K), and Keplr/Web3Auth incidents remain UPDATEs with no material new scored figures in the last 24 hours. NEAR AI disclosed a contained infrastructure breach (SGLang RCE) with data exposure but no confirmed protocol fund loss.
Initia L1 escrow accounts — Initia / Noble — ~$615K — fabricated IBC transfers via compromised rollup keys
What happened: On 10 November 2026 at 06:18 UTC, Initia coordinated with validators to halt the L1 as a protective measure after detecting unauthorized transfers from escrow accounts on the Initia L1 that hold assets bridged to several rollups. Official preliminary review states the transfers used compromised rollup infrastructure keys, enabling the attacker to fabricate IBC transfers. Before the network was paused, approximately $605,000 USDC left Initia through Noble, plus about $10,000 in other tokens. Most of the remaining assets that had been moved out of the escrow accounts are still on the halted L1. Initia is working with security teams, validators, and exchanges to determine the full scope. Users were cautioned against unofficial links, messages, or claims. CertiKAlert observed suspicious outflow of ~$636K across 16 successful IBC transfers from a specific Initia address to Noble. This is a new first-report incident; a prior Initia mint-related event in late October is distinct and not re-scored here.
Protocol / chain / asset: Initia L1 (interwoven-1) escrow accounts holding bridged assets for rollups. Outflow path: IBC to Noble. Primary asset: USDC (~$605K) plus ~$10K other tokens. Official announcement from @initia; CertiKAlert monitoring of outflows.
Loss: Official: ~$605,000 USDC + ~$10K other tokens (~$615K total exited). CertiKAlert: ~$636K across 16 IBC transfers. Live scored on this brief: ~$615K (official preliminary figure). Full scope and any additional on-L1 impact remain under investigation; most remaining moved assets are still on the halted chain.
Attack type: Compromised infrastructure keys / IBC transfer fabrication. Unauthorized access to rollup infrastructure keys allowed fabrication of IBC transfers draining escrow holdings.
Explorer URLs: Official post: https://x.com/initia/status/2120050740626628972. CertiKAlert: https://x.com/CertiKAlert/status/2120101370909151548 (links to scan.initia.xyz account and transfers). Example account referenced: init1nyn989pkt2tx3rfz4rhzwldlh67vy4t30ccyz9 on Initia scan. Full transfer list and addresses in CertiK and official updates as investigation proceeds. No additional public attacker EOAs or final drain TXs published at cutoff.
Status: Confirmed by official Initia announcement and CertiKAlert. L1 remains halted. Full scope determination ongoing with security teams, validators, and exchanges. No reimbursement announcement or confirmed recovery figures at cutoff. Flag any subsequent quantified additional loss or official recovery as material. Exact key-compromise vector (how rollup infrastructure keys were obtained) unconfirmed.
Sources: @initia official; CertiKAlert; Phemex News; TokenPost; PANews; Odaily; TechFlow; The Block.
Also noted
- Ankr Ethereum cross-chain bridge (UPDATE, not re-scored): First reported 9 November. SlowMist ~$304.5K via five forged receipts reusing one already-redeemed Optimism deposit and carrying valid consensus signatures. GoPlus published detailed address and TX breakdown on 10 November (attacker 0x9A88Dd45AE846A979705c9cFdfD0f229e592D703, recipient 0x119D250b82C1cf5345dF5912EFb4B1a4107a1Aa6, contract 0xc437DF90B37C1dB6657339E31BfE54627f0e7181, notary 0x4069d8a3de3a72eca86ca5e0a4b94619085e7362). Pause flag status and signer-compromise origin remain under investigation. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-09-nov-2026-ankr-304k-bridge-zenji-5k-oracle/. No material new scored loss in the last 24 hours.
- ACryptoS concentrated-liquidity vaults (UPDATE, not re-scored): First reported 8 November. Official post-mortem confirms missing input validation in depositMulti() allowed short amounts arrays to undervalue holdings and mint excess shares; ~$665,429 extracted from 77 vaults across Arbitrum, BSC, Polygon, Base and Optimism by 135 addresses. Deposits disabled since ~16:40 UTC 8 Nov; withdrawals open; project deprecated. One Base DAI/USDbC vault partially restored via share burn on 9 Nov. No new first-report loss figure.
- NEAR AI infrastructure (UPDATE, not scored): Contained on 8–10 November. Attacker exploited RCE in open-source SGLang inference engine on one server, reached deprecated Private Chat internal system, downloaded account details (~100 users: emails, names, some plan/balance) and accessed chat history/settings/logs from 18 legacy agents (not in TEE). Two Cloud API keys exposed in logs and revoked. No confirmed protocol or on-chain fund loss; NEAR Protocol unaffected. Access closed, credentials rotated, Cloud restored. Official report and @near_ai update.
- Ethersphere / Swarm supply-chain malware (not scored): Compromised official releases of @ethersphere/bee-js@13.3.0 and Swarm Desktop v0.56.2 distributed wallet-key-stealing malware and a backdoor via the project’s own release pipeline. Malicious package withdrawn; clean versions available (bee-js 13.2.0, Swarm Desktop 0.56.3). No confirmed protocol or user fund losses attributed at cutoff. Flag as supply-chain malware distribution, not a scored smart-contract incident. SlowMist TI Alert.
- Zenji leveraged LlamaLend vaults (UPDATE, not re-scored): First reported 8–9 November. ~$4.9K flash-loan oracle/price manipulation of Curve StableNG pool used for valuation and unwind. Patch published. No larger follow-on drains reported.
- Prior items (UPDATE, not re-scored): Keplr/Web3Auth, Loopscale, TENDRIL, Binance hot-wallet, Mercado Bitcoin, and earlier Initia October mint event. No material new first-report scored figures in the last 24 hours.
- Other notes: No additional first-report protocol drains with fresh confirmed user-loss figures from monitored accounts. Scattered individual reports remain unverified and unattributed to any protocol. iOS worse_query sandbox-escape PoC noted by SlowMist (not scored; no protocol loss).
Sources and references
- Initia official: https://x.com/initia/status/2120050740626628972
- CertiKAlert Initia outflow: https://x.com/CertiKAlert/status/2120101370909151548
- SlowMist Swarm supply chain: https://x.com/SlowMist_Team/status/2119998212497125582
- NEAR AI incident report: https://near.ai/blog/security-incident-report-sglang-vulnerability
- NEAR AI X update: https://x.com/near_ai/status/2120043366444601458
- ACryptoS post-mortem: https://docs.acryptos.com/post-mortem-univ3-family-vault-exploit-2026-11-08
- GoPlus Ankr thread (10 Nov): https://x.com/GoPlusSecurity/status/2120078252194877649
- 9 Nov brief (Ankr/Zenji): https://www.rektradar.xyz/web3-daily-exploits-09-nov-2026-ankr-304k-bridge-zenji-5k-oracle/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh scored user-loss figures beyond the Initia item.
Editor’s note: the scored live loss on this card is ~$615K across one first-report incident (Initia escrow ~$615K via fabricated IBC). Official figure used for scoring; CertiK observed a slightly higher ~$636K outflow. Ankr, ACryptoS, Zenji and NEAR AI remain UPDATEs (no new scored fund loss for NEAR AI). No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 9 Nov 2026: Ankr ~$304K Bridge, Zenji ~$5K Oracle
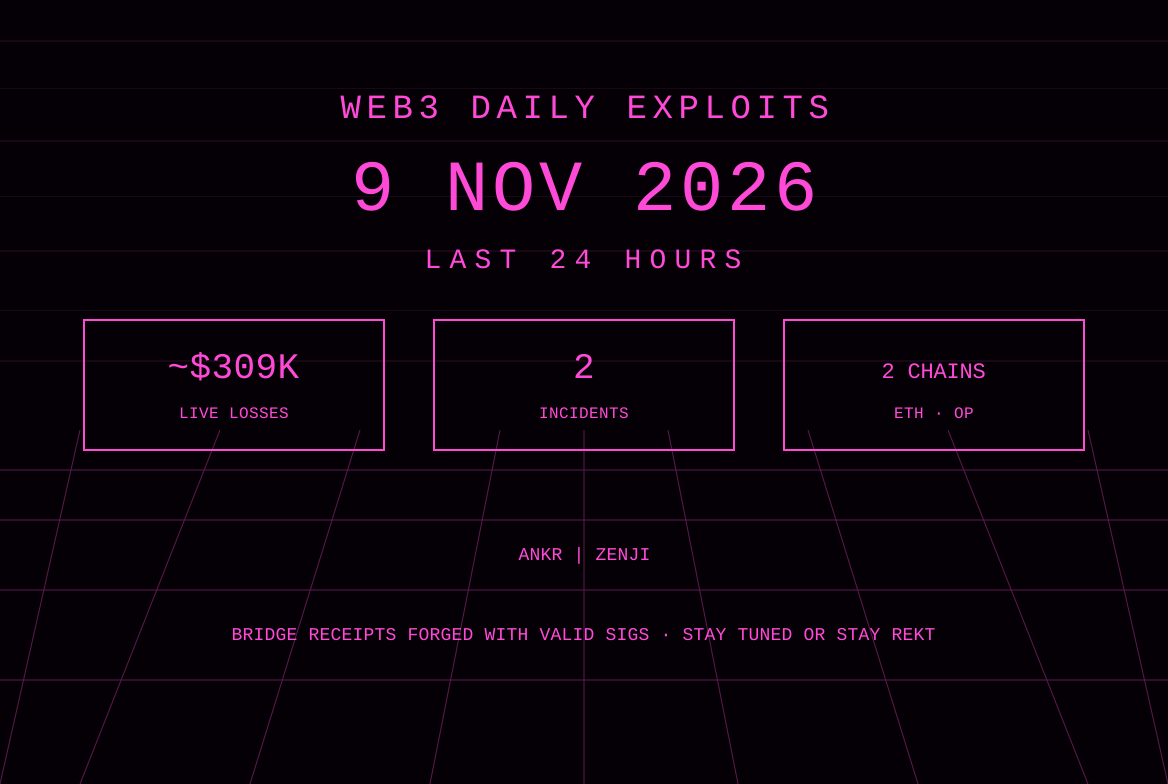
Two first-report incidents: Ankr Ethereum cross-chain bridge drained ~$304.5K via five forged receipts carrying valid consensus signatures that referenced one already-redeemed Optimism deposit; Zenji leveraged LlamaLend vaults lost ~$4.9K to flash-loan oracle/price manipulation of a Curve StableNG pool. Combined live scored ~$309K across ETH and OP. Keplr/Web3Auth remains UPDATE.
Web3 Daily Exploits — 8 Nov 2026: Quiet Window, Keplr Web3Auth ~$6M Update
Quiet scoring window: no first-reported protocol incidents with confirmed scored user losses in the last 24 hours. Keplr/Web3Auth social-login key exposure (first reported 6 Nov) has material update with Bitquery tracing ~$6.01M from 44k+ Cosmos wallets; recovery addresses published. Prior Loopscale, FLOKI bot, TENDRIL, Binance, Mercado Bitcoin remain UPDATEs. Live scored losses ~$0 across 0 incidents.
Web3 Daily Exploits — 7 Nov 2026: Quiet Window, No New Scored Losses
Quiet scoring window: no first-reported protocol incidents with confirmed scored user losses in the last 24 hours. Prior Loopscale contained attempts (vaults made whole, $0 user loss), FLOKI bot (loss undisclosed), TENDRIL sell-hook, Binance hot-wallet signing compromise, and Mercado Bitcoin remain UPDATEs. DarkSword iOS kit continues device-level wallet targeting on unpatched phones. Live scored losses ~$0 across 0 incidents.
Web3 Daily Exploits — 6 Nov 2026: Loopscale Contained Attempts, FLOKI Bot Offline
Quiet scoring window: Loopscale paused Solana lending after week-long API campaign and two contained attack paths (~$412K undercollateralized loan, ~$521K NAV inflation halted). Vaults made whole, no user deposits lost. FLOKI Telegram trading bot taken offline after exploit; loss size undisclosed. TENDRIL remains prior brief. Live losses ~$0 across 0 scored incidents.