Web3 Daily Exploits — 7 Oct 2026: Frogman Drain and HAI Vote
Trader Frogman says two wallets were drained for more than $4 million while he was asleep in Singapore. Lookonchain breaks out BP, MarsCoin, and Cash Cat. Defimon reports a letsgethai governance proposal on Optimism that would point 328,143 KITE at the proposer. No funds had moved on that proposal.
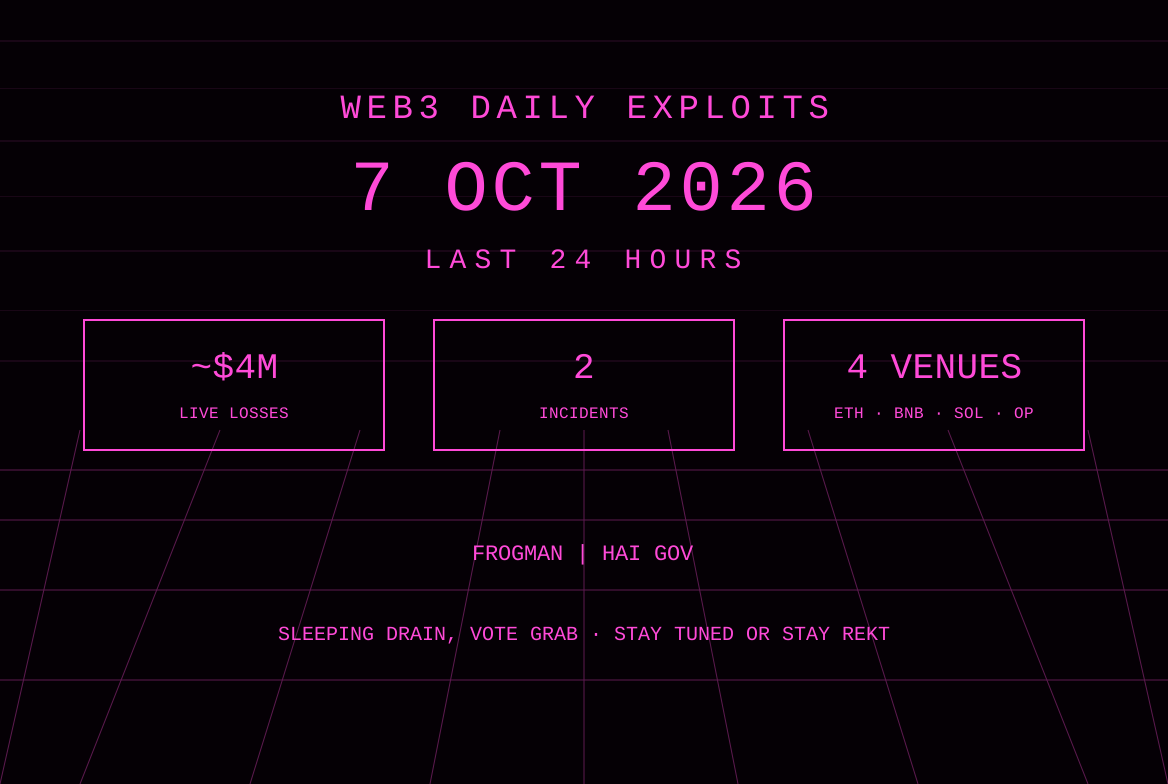
The 7 Oct America/Panama window is a personal-wallet day plus one governance attempt that had not moved money by the desk post. The scored live loss is the figure the trader himself printed. At 05:21 UTC on 7 Oct, Frogman wrote that he was drained for more than $4 million at 4:30am while he was asleep, that he is in Singapore, and that he does not yet know how it happened. Lookonchain, at 06:24 UTC, wrote that two of his wallets were hacked for about $4 million, named three token lines, and said the stolen assets had been swapped for ETH, BNB, and SOL and laundered. That is the card’s live-loss line. It is not a protocol exploit in either post.
The second scored item is earlier in the same 24-hour cut and is an attempt, not a drain. DefimonAlerts, at 22:39 UTC on 6 Oct, wrote that letsgethai had a governance takeover attempt with about $927,000 at risk. The network is Optimism. The token line is KITE at $2.83. The type line is a malicious governance proposal, voting-power capture. Defimon says no funds have moved yet. The about $927,000 is at-risk inventory in the alert, not a loss, and it is not added to the card. A later Defimon post, at 09:35 UTC on 7 Oct, is an on-chain recovery message asking for 77,558 DAI back as 90 percent of stolen funds. That message names no protocol, no transaction, and no desk loss figure. It stays off the card.
CertiKAlert, Phalcon, GoPlusSecurity, SlowMist, PeckShieldAlert, BlockSecTeam, and CyversAlerts did not post a separate first-report exploit in the posts read for this cutoff. ZachXBT’s visible lines in the window were replies on an older investigation, not a new drain. Immunefi’s visible lines were a researcher payout note, not an incident. rekt.news did not publish a new incident post used as a figure here. Lookonchain’s other 7 Oct line, a KuCoin and Gate withdrawal of a meme token, is a position note, not a hack.
Frogman wallets — multi-venue — about $4 million — unconfirmed key or session compromise
What happened: Frogman posted at 05:21 UTC on 7 Oct that he was drained for more than $4 million at 4:30am while he was asleep. He wrote that he is not sure how it happened, that he is in Singapore and met a lot of new people, and that teams are helping with the investigation. He said he will share more when he can. The clock he printed is 4:30am. He did not print a timezone. This brief does not convert that clock to UTC. The post time on X is 05:21 UTC. That is the confirmed timestamp.
Lookonchain posted at 06:24 UTC that two of Frogman’s wallets were hacked, losing about $4 million. The named lines are 1.43 million BP, about $1.77 million; 13.96 million MarsCoin, about $1.55 million; and 3.7 million Cash Cat, about $515,000; and more. The three named lines sum to about $3.835 million. The “and more” is what closes the gap to the about $4 million headline. This brief does not invent the other six token names. A later Lookonchain site note said the stolen assets cover nine tokens and printed Cash Cat at about $510,000. The X post’s $515,000 stays. The site note is a restatement, not a second loss.
Lookonchain wrote that the attacker swapped the stolen assets for ETH, BNB, and SOL and laundered the funds. The address attached to that sentence is 0x14AA2A71dbb5eF87b81F92205E2699AA4aa65794, linked on Arkham. A secondary Odaily note, citing on-chain analyst Yu Jin, used the prefix 0x14…5794 for a wallet it called the suspected victim, alongside a second truncated address 9wMS…ov8z. The role of the full address is therefore not settled in one sentence. This brief links it as the address Lookonchain attached to the laundering line and does not relabel it attacker or victim. The second wallet stays truncated. It is not expanded.
A reply under the Lookonchain post, not a Lookonchain post, said the loss spans three chains: BP on Solana, MarsCoin on BSC, and Cash Cat on Robinhood chain, and read the pattern as a seed or device compromise because one approval would not reach a Solana wallet and an EVM wallet at once. That chain split and that cause are unverified. Frogman did not name a vector. Lookonchain did not name a vector. A Lookonchain site write-up said the assets were dispersed via Privacy Cash and Chainflip. That dispersion path is not in the X post text read here. It is noted as a site line, not scored as a hop this desk re-opened.
Protocol / chain / asset: No protocol. Personal wallets of the trader @frogmanhaha. Exit assets named by Lookonchain are ETH, BNB, and SOL. Token lines named on the loss are BP, MarsCoin, and Cash Cat, plus unnamed remainder. Origin chains for those tokens are not in the Lookonchain X text. The reply’s Solana, BSC, and Robinhood split stays unverified.
Loss: More than $4 million, Frogman’s print. About $4 million, Lookonchain’s print. Named components about $1.77 million, about $1.55 million, and about $515,000. No recovery figure. No freeze posted by a desk. The card uses about $4 million. The “plus” in the trader’s post is not converted into a higher number.
Attack type: Wallet compromise, unconfirmed. Not a contract bug in either post. Seed, device, session, and approval theories appear only in replies and are not used as the type. Multi-wallet and multi-asset is the fact in the Lookonchain text. Two wallets, not one.
Explorer URLs: Address attached to the Lookonchain laundering sentence, Arkham: https://arkm.com/explorer/address/0x14AA2A71dbb5eF87b81F92205E2699AA4aa65794. No transaction hash was in the Lookonchain post or the trader post. This brief does not invent one. The second wallet prefix 9wMS…ov8z is from a secondary note and is not linked.
Status: Victim confirmed the drain at 05:21 UTC on 7 Oct. Cause open. No operator, because there is no protocol. No return posted. Secondary chain split, cause theories, and Privacy Cash or Chainflip hops stay unverified against the two primary posts.
Sources: https://x.com/frogmanhaha/status/2107702850679943584 and https://x.com/lookonchain/status/2107718754830549440
letsgethai — Optimism — about $927,000 at risk — malicious governance proposal
What happened: DefimonAlerts posted at 22:39 UTC on 6 Oct that letsgethai had a governance takeover attempt with about $927,000 at risk. The token is KITE, printed at $2.83. The network is Optimism. The type is a malicious governance proposal, voting-power capture. Defimon says a fresh six-transaction externally owned account, printed as 0xCc7B…2E0E, self-delegated KITE and then submitted a proposal printed as 9453…4266 on HaiGovernor. The proposal title in the alert is Quarterly Treasury Maintenance.
Five of the six batched Safe actions are described as harmless camouflage: approvals to the real StakingManager and RewardDistributor, and small KITE and OP transfers. The concealed sixth action is labeled Activate Governance: Delegate treasury KITE voting power. Defimon says that label does not match the calldata. The call is delegate, aimed at 0xCc7B…2E0E, pointing the DAO treasury Safe’s 328,143 KITE at the proposer rather than self-delegating. That balance is about 34 percent of the 973,967 total supply in the alert. Quorum is printed as 1 percent, 9,739 KITE. Defimon says execution would hand the proposer about 34 percent of voting power against that quorum, and unilateral control of HAI governance and the about $1.58 million protocol. Description-versus-calldata mismatch is the tell in the alert. No funds have moved yet.
The X post used short links. The same alert text, as expanded on the Defimon telegram mirror, resolves the transaction to 0x48f51df912052658ea256a3c2ea893a66dee79a79b82b24383fc4f23da706aeb, the proposer to 0xcc7b4a6429c967aa3bdcd812af7f25d728832e0e, the victim to 0xe807f3282f3391d237ba8b9becb0d8ea3ba23777, and the proposal to the Tally id that begins 9453071703385965548. Those expansions match the prefixes in the X post. This desk did not re-decode the Safe batch. The $2.83 KITE price is Defimon’s print. 328,143 KITE at $2.83 is about $929,000, which sits next to the about $927,000 at-risk line. The small gap is not treated as a second figure. The at-risk line stays $927,000. The about $1.58 million is the protocol figure in the alert, not a loss.
Protocol / chain / asset: letsgethai, named by Defimon, on Optimism. Governance token KITE. HAI is the stablecoin brand in public project text; the alert’s captured asset is KITE voting power on the treasury Safe, not a HAI mint. Victim address in the expanded alert is the address linked above. This brief does not further label that contract.
Loss: None posted. About $927,000 at risk. About $1.58 million named as protocol scale if control were taken. Neither is scored as a live loss. No recovery, because nothing is posted as taken.
Attack type: Malicious governance proposal. Voting-power capture via a description that does not match the delegate calldata, per Defimon. Not an oracle bug and not a key compromise in the alert text. The proposer is described as a fresh six-transaction account.
Explorer URLs: Proposal transaction https://optimistic.etherscan.io/tx/0x48f51df912052658ea256a3c2ea893a66dee79a79b82b24383fc4f23da706aeb. Proposer https://optimistic.etherscan.io/address/0xcc7b4a6429c967aa3bdcd812af7f25d728832e0e. Victim https://optimistic.etherscan.io/address/0xe807f3282f3391d237ba8b9becb0d8ea3ba23777. Proposal https://www.tally.xyz/gov/hai/proposal/945307170338596554802456536891275189748084619609113760500856562733210244266.
Status: First desk report in this window. Execution date in the alert is 6 Oct 2026. No funds moved, per Defimon. No letsgethai statement found in the posts read here. Not a live loss on the card.
Sources: https://x.com/DefimonAlerts/status/2107601752048435215
Also noted
- Defimon, DAI recovery message, incomplete: At 09:35 UTC on 7 Oct DefimonAlerts posted an on-chain message offering a 10 percent bounty if 77,558 DAI, described as 90 percent of the stolen funds, is returned to
0xBd28b1786060AdE61f0bFcEde736a80fC64ba13con Ethereum by 12:00 UTC on 14 Oct 2026. Taking the 90 percent line at face value implies about 86,176 DAI. That arithmetic is not a desk loss print. The X post names no protocol, no hash, and no victim. A telegram mirror of the same message prints the sender as that return address and the recipient as0xa566592cb94475baf5b46ce373a260dfc9d0df3fon Ethereum mainnet, without a transaction hash. Not scored. Not linked to the Frogman drain or the HAI proposal. - Lookonchain, KuCoin and Gate withdrawal: At 09:16 UTC on 7 Oct Lookonchain wrote that two wallets withdrew 114.9 million of a meme token, about $6.9 million, from KuCoin and Gate, about 11.49 percent of supply. Addresses named are
0x5a4284685De34b7c20dB03A8E26157B27fdEb320and0x594FcF750721300618679303b78AD4Ca8F0bd055. That is a withdrawal note, not a drain. Not scored. - Immunefi, researcher payout: At 09:00 UTC on 7 Oct Immunefi wrote that a researcher was paid $300,000 for a critical finding and sits first on a 90-day leaderboard. Not an incident. No protocol named in the text read here. Not scored.
- ZachXBT: Visible lines in this window were replies on an older investigation thread, not a new exploit report. Not scored.
- Chain split and laundering hops, unverified: A reply put BP on Solana, MarsCoin on BSC, and Cash Cat on Robinhood chain. A Lookonchain site note named Privacy Cash and Chainflip. Neither is in the Lookonchain X text. Not scored as extra loss.
- CertiKAlert, Phalcon, GoPlusSecurity, SlowMist, PeckShieldAlert, BlockSecTeam, CyversAlerts, rekt.news: No separate first-report exploit used as a figure in this cutoff.
Sources and references
- Frogman, drain confirmation, 05:21 UTC on 7 Oct: https://x.com/frogmanhaha/status/2107702850679943584
- Lookonchain, two-wallet breakdown, 06:24 UTC on 7 Oct: https://x.com/lookonchain/status/2107718754830549440
- Lookonchain address link: https://arkm.com/explorer/address/0x14AA2A71dbb5eF87b81F92205E2699AA4aa65794
- DefimonAlerts, letsgethai proposal, 22:39 UTC on 6 Oct: https://x.com/DefimonAlerts/status/2107601752048435215
- HAI proposal transaction: https://optimistic.etherscan.io/tx/0x48f51df912052658ea256a3c2ea893a66dee79a79b82b24383fc4f23da706aeb
- DefimonAlerts, DAI recovery message, 09:35 UTC on 7 Oct: https://x.com/DefimonAlerts/status/2107766858296267005
- Lookonchain, exchange withdrawal note, 09:16 UTC on 7 Oct: https://x.com/lookonchain/status/2107761856932921791
Editor’s note: the live loss is a trader’s wallets, not a named protocol. The cause is open. The HAI line is a proposal with a label that does not match the call, and Defimon says nothing has moved. The DAI message is a bounty text without a protocol or a hash. Figures follow the posts. Truncated addresses stay truncated. Reply theories stay unverified.
Read more
Web3 Daily Exploits — 6 Oct 2026: Maker Keeper and Set Rounding
Defimon reports a Tornado-funded caller pulled 200 WETH, about $538K, from a dormant 2020 MakerDAO ETH-A flip-keeper whose exit was not behind ds-auth. SlowMist reports Set Protocol lost about 5.08 ETH to an actualizeFee rounding step. Maker core is not scored as the bug.
Web3 Daily Exploits — 5 Oct 2026: LINK Permit2 and DAI Poison
GoPlus posts two Ethereum user drains first seen in this window: 12,041.3036 LINK, about $169.7K, pulled through a Permit2 path, and 305,560.46 DAI sent to a prefix-and-suffix lookalike. The Base vault gets a root-cause update and a $31.7M residual figure. That $6M is not re-scored.
Web3 Daily Exploits — 4 Oct 2026: Base Vault ~$6M wstETH
PeckShield and CertiK flag 1,783 wstETH, about $6M, leaving an unnamed Base vault via a newly deployed proxy. GoldPesa GPXHooks lost about $114.9K to a Uniswap v4 delta mix-up. SlowMist scores MALT at about $72K. Root cause on the vault is unconfirmed.
Web3 Daily Exploits — 3 Oct 2026: NEAR Intents $3.8M Returned
Quiet first-report window. NEAR Intents GM Alex Shevchenko said the $3.8M Omni exploit funds were sent back in full and the investigation is stopping. A labeled exploiter sent a return message on BNB Chain; the published Bitcoin address holds 34.589 BTC. FlashLoop’s 114.09 ETH bounty is still open. Card new live loss is ~$0.