Web3 Daily Exploits — 5 Oct 2026: LINK Permit2 and DAI Poison
GoPlus posts two Ethereum user drains first seen in this window: 12,041.3036 LINK, about $169.7K, pulled through a Permit2 path, and 305,560.46 DAI sent to a prefix-and-suffix lookalike. The Base vault gets a root-cause update and a $31.7M residual figure. That $6M is not re-scored.
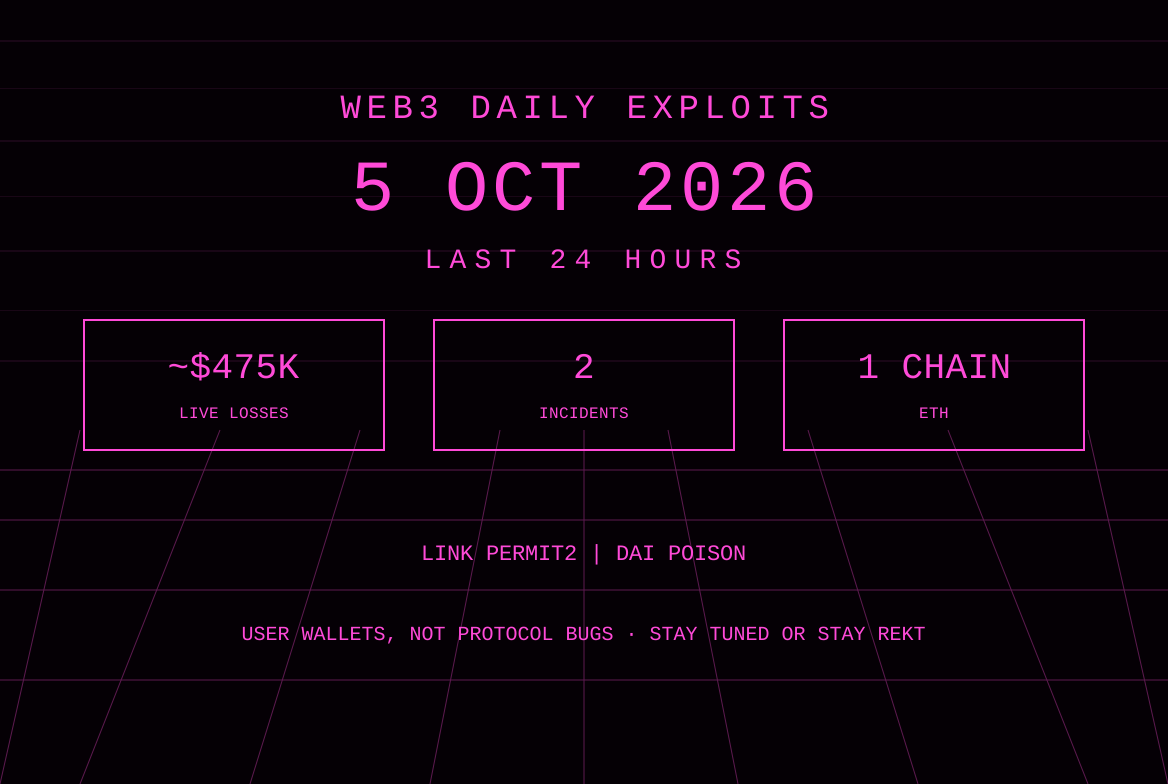
The 5 Oct America/Panama window is not a protocol-bug day. Two first desk reports land inside the slice, both user-wallet drains on Ethereum, both executed on 3 Oct and both posted by GoPlusSecurity on 4 Oct after the prior brief had already closed. Together they are about $475,000 of newly reported live loss. The larger dollar line in the conversation is older: the unnamed Base vault that lost about 1,783 wstETH. That figure was scored on 4 Oct and is not added again. What is new on that file is a root-cause note, a residual-balance claim, and an on-chain message aimed at the recipient.
GoPlusSecurity, at 11:59 UTC on 4 Oct, wrote that a user lost about $305,000 of DAI to an address-poisoning transfer. The screenshot attached to that post is an Ethereum transaction page: 0xaae85f2d7011454ce38a2024642daad54ea9ec81899782edc81dff7294e99739, block 26113833, timestamp 19:14:11 UTC on 3 Oct, status success. The caller is the victim address. The contract interacted with is the DAI token 0x6B175474E89094C44Da98b954EedeAC495271d0F. The token row moves 305,560.4567 DAI, printed at $305,560.46, from 0xb6bce73e112e566cf04742f003e1d82fd7f6b7bf to 0x085ccc21065c8c718fa0afcb4e842f247c18f1dd. GoPlus named the intended recipient as 0x085adc5a4a1227b1c8aab9a962c03676fa18f1dd. The two addresses share a prefix and a suffix and differ in the middle. That is the poisoning pattern the alert describes: dust from a lookalike, then a copy from transaction history.
Four hours later, at 14:55 UTC, GoPlus posted a second alert: about $170,000 of LINK after a malicious Permit2 signature. The attached page is also Ethereum. Transaction 0xa25807c87cc99a9c7195548c1438cde9ad937652cc3fb60fe609c01b339b04d0, block 26113853, timestamp 19:18:11 UTC on 3 Oct. From 0x0000db5c8B030ae20308ac975898E09741e70000, labeled Fake_Phishing187019 on that page, interacting with 0x0000cdCa01087D340e8fA4339b121B69a8aE0000, labeled Fake_Phishing1324813. The token row moves 12,041.3036 LINK, printed at $169,661.97, from victim 0x71619d71474F8D0AAa9C18a757be7617686B499b to 0xA6809aeDEbFA10A0C2dbcF3363cB0Ff37866f73D. Those three addresses are the phisher set in the alert text. The two drains sit four minutes apart on Ethereum. They are not the same attacker set in the posts this desk read, and they are not scored as one incident.
The Base update arrives later. GoPlus, at 23:40 UTC on 4 Oct, restated the 1,783.067 aBaswstETH outflow and the Aave V3 redemption into about 1,783 wstETH, loss roughly $6 million, and added a cause: the exploit contract was added to the vault’s borrow allowlist through a Safe multisig. The firm said the Safe had not executed a transaction for 25 days, then executed two. It left open whether that flow was phished, socially engineered, or insider. It also said about $31.7 million is still in the vault, that Aave’s core contracts and Base itself were not attacked, and that no project team has claimed the vault or posted a response. A secondary post on 5 Oct described the owner Safe as 3-of-7 and the whitelisted contract as deployed 85 minutes earlier. That signer count and the deploy gap are not in the GoPlus text and stay unverified. A separate secondary line, that about 1,001 of the stolen wstETH is in the Lido withdrawal queue, is also unverified and is not used as a status.
A late pass through the required monitors, ending just after 11:34 UTC on 5 Oct, did not add a third scored loss. DefimonAlerts relayed a carrotfunding return demand at 08:05 UTC and, at 11:34 UTC, an on-chain note about a removeLiquidity call that the sender says was not a swap. Neither post carries a desk loss figure. CertiKAlert, PeckShieldAlert, Phalcon, SlowMist, BlockSec, Cyvers, Lookonchain, and ZachXBT did not post a separate first-report exploit in this later slice. Lookonchain’s visible lines are trader position notes, not drains.
LINK Permit2 — Ethereum — 12,041.3036 LINK — malicious signature
What happened: GoPlusSecurity posted at 14:55 UTC on 4 Oct that a user was drained of about $170,000 in LINK after signing a malicious Permit2 transaction. The screenshot on that post is the transaction page for 0xa25807c87cc99a9c7195548c1438cde9ad937652cc3fb60fe609c01b339b04d0. It succeeded in block 26113853 at 19:18:11 UTC on 3 Oct. Value transferred in ETH is zero. The ERC-20 row is 12,041.3036 LINK, $169,661.97 on that page, from 0x71619d71474F8D0AAa9C18a757be7617686B499b to 0xA6809aeDEbFA10A0C2dbcF3363cB0Ff37866f73D. The transaction sender is 0x0000db5c8B030ae20308ac975898E09741e70000, shown with the label Fake_Phishing187019. The contract called is 0x0000cdCa01087D340e8fA4339b121B69a8aE0000, labeled Fake_Phishing1324813. GoPlus listed the same three addresses as the phisher set. Permit2 is the signature standard named in the alert. This brief does not have the permit payload, the spender field, or the nonce from a decoded input, because the page image stops at the token row.
A secondary print, carried by TechFlow and attributed to Scam Sniffer, puts the loss at $167,342 and says the authorization was signed on 18 Aug 2025. That date is not on the GoPlus post and was not re-opened on a permit log here, so the sleeper-approval age is unconfirmed. A reply under the post says a later 1inch swap turned the LINK into 62.31 ETH still on the recipient address, and that an earlier 0x swap failed. That reply is not a desk alert. The LINK amount matches the token row. The ETH conversion does not, and it is flagged unverified.
Protocol / chain / asset: No protocol. Ethereum. Asset is LINK, Chainlink’s token. Permit2 is the approval surface named by GoPlus. This is not scored as a Chainlink or Uniswap contract bug. The failure described is a signature the victim had already given, spent later by a phishing-labeled caller.
Loss: Token-row print 12,041.3036 LINK, $169,661.97. GoPlus desk line about $170,000. Scam Sniffer secondary print $167,342. Card uses the token-row dollar, rounded with the DAI line to about $475,000. No recovery figure.
Attack type: Phishing signature, Permit2. Not a key compromise in the alert text, and not an exploit of a lending or bridge contract.
Explorer URLs: Drain transaction https://etherscan.io/tx/0xa25807c87cc99a9c7195548c1438cde9ad937652cc3fb60fe609c01b339b04d0. Victim https://etherscan.io/address/0x71619d71474F8D0AAa9C18a757be7617686B499b. Caller https://etherscan.io/address/0x0000db5c8B030ae20308ac975898E09741e70000. Called contract https://etherscan.io/address/0x0000cdCa01087D340e8fA4339b121B69a8aE0000. LINK recipient https://etherscan.io/address/0xA6809aeDEbFA10A0C2dbcF3363cB0Ff37866f73D.
Status: First desk report in this window. Execution timestamp on the page is 3 Oct. No freeze posted by a desk. Cash-out beyond the LINK transfer is unconfirmed. No victim statement found.
Sources: https://x.com/GoPlusSecurity/status/2106759999745917293
DAI address poison — Ethereum — 305,560.46 DAI — lookalike recipient
What happened: GoPlusSecurity posted at 11:59 UTC on 4 Oct that a user lost about $305,000 of DAI to address poisoning. The alert’s flow is the standard one: the adversary dusts the victim from a lookalike that matches prefix and suffix, then waits for a copy from transaction history. Victim 0xb6bce73e112e566cf04742f003e1d82fd7f6b7bf. Intended recipient 0x085adc5a4a1227b1c8aab9a962c03676fa18f1dd. Poison address 0x085ccc21065c8c718fa0afcb4e842f247c18f1dd. The screenshot is the transaction page for 0xaae85f2d7011454ce38a2024642daad54ea9ec81899782edc81dff7294e99739, block 26113833, 19:14:11 UTC on 3 Oct, success. The caller is the victim. The contract is DAI at 0x6B175474E89094C44Da98b954EedeAC495271d0F. The token row is 305,560.4567 DAI, $305,560.46, from the victim to the poison address. ETH value on the transaction is zero. The short URL in the alert text was not expanded separately. The hash above is the one printed on the screenshot, not a reconstructed short link.
A reply under the alert says a dust transaction in block 26111585 hit both addresses, and that the poison address later approved DAI but still held the full 305,560.46 DAI. That reply is not a desk alert. The still-held claim is unverified. This brief does not treat the funds as frozen. The two addresses share a prefix and a suffix and differ in the middle. GoPlus described the campaign as automated. No mixer hop is on the transaction page this desk read, so laundering past the poison address is not scored.
Protocol / chain / asset: No protocol. Ethereum. Asset is DAI. The DAI contract is the token the victim called, not the bug. This is a destination error induced by a lookalike, not a DAI accounting flaw.
Loss: Token-row print 305,560.4567 DAI, $305,560.46. GoPlus about $305,000. Card uses the token-row print. No second desk figure in this window.
Attack type: Address poisoning. User-signed transfer to a lookalike. Not a contract exploit.
Explorer URLs: Transfer https://etherscan.io/tx/0xaae85f2d7011454ce38a2024642daad54ea9ec81899782edc81dff7294e99739. Victim https://etherscan.io/address/0xb6bce73e112e566cf04742f003e1d82fd7f6b7bf. Poison address https://etherscan.io/address/0x085ccc21065c8c718fa0afcb4e842f247c18f1dd. Intended recipient, from the alert, not re-opened: https://etherscan.io/address/0x085adc5a4a1227b1c8aab9a962c03676fa18f1dd. DAI token https://etherscan.io/address/0x6B175474E89094C44Da98b954EedeAC495271d0F.
Status: First desk report in this window. Execution on the page is 3 Oct, four minutes before the LINK pull. No project response, because there is no project. Residual balance on the poison address unconfirmed.
Sources: https://x.com/GoPlusSecurity/status/2106715903274684681
UPDATE — unnamed Base vault — allowlist note — about $31.7M still inside — $6M not re-scored
What happened: The 4 Oct brief scored the Base outflow at about 1,783 wstETH, about $6 million, with root cause open. PeckShieldAlert had named recipient 0x0B5126e1bc27C0de77e02e97945760A674EdB034. CertiKAlert had named vault 0xD1895f2019c2152FC2b9022D57f19198c4CFCABC and a newly deployed proxy borrowing aBaswstETH, redeemed through Aave. ExVul had named loot contract 0xcdFE91301356da873562EF513828a60dba1F569d and left the authorization failure unconfirmed. GoPlusSecurity, at 23:40 UTC on 4 Oct, is the material update. It restates 1,783.067 aBaswstETH taken out and redeemed on Aave V3 for about 1,783 wstETH, roughly $6 million. It says the vault holds an Aave V3 Base position sized in the tens of millions, and that Aave’s core lending contracts and Base itself were not attacked. The new cause line is a multisig governance and access-control failure: exploit contract 0xcdFE91301356da873562EF513828a60dba1F569d was added to the vault’s borrow allowlist through a Safe. GoPlus says the team had not executed a Safe transaction for 25 days, then these two were executed, and that the flow may have been socially engineered, phished, or insider collusion. That three-way split is the firm’s own open list, not a finding this desk closed.
GoPlus also named related address 0xC73448432a05deeA5Ea18a07D3b5d9ccf6297f8D. Role not stated in the text read here, so it is listed and not labeled. The firm said about $31.7 million remains in the vault and at risk, and that no project team has claimed the contract or posted an announcement. A secondary account on 5 Oct wrote that the owner Safe is 3-of-7 and that the whitelisted contract was deployed 85 minutes earlier. Signer threshold and deploy gap are unverified. Another secondary line, that about 1,001 wstETH of the stolen balance sits in a Lido withdrawal queue, is unverified and is not a status.
The on-chain message is real as a post, and the content is a solicitation. GoPlus said someone sent the attacker a message pushing a further withdrawal and asking for a tip. The image on that post is a BaseScan input-data view whose text urges a further withdraw of a quoted aBasETH amount and a donation to a named address. This brief does not repeat the calldata. It is not a desk instruction, and it is not evidence that a second drain happened. DefimonAlerts, at 11:58 UTC on 4 Oct, relayed a separate on-chain plea tied to Base transaction 0x16a3ad7651f499e142f479b4cd53622fc6033d97af67fb7fd33cd98dd025a956. That hash is from the Defimon post. It was not opened here, and it is not asserted to be the same message as the GoPlus screenshot.
Protocol / chain / asset: Still unnamed. Base. Path remains aBaswstETH borrowed from the vault, redeemed to wstETH through Aave. Aave core not scored as the bug, matching both the 4 Oct CertiK line and the GoPlus line.
Loss: Unchanged at about 1,783 wstETH, about $6 million. Not added to today’s card. Residual about $31.7 million is GoPlus’s at-risk figure, not a second loss. The earlier mid-attack $2.02 million Blockaid print stays a snapshot, as scored on 4 Oct.
Attack type: Updated working description: borrow allowlist extended by a Safe execution. Phish, social engineering, or insider still open. Not reclassified as an Aave core bug.
Explorer URLs: Vault https://basescan.org/address/0xD1895f2019c2152FC2b9022D57f19198c4CFCABC. Recipient https://basescan.org/address/0x0B5126e1bc27C0de77e02e97945760A674EdB034. Loot contract https://basescan.org/address/0xcdFE91301356da873562EF513828a60dba1F569d. Related address from the GoPlus post https://basescan.org/address/0xC73448432a05deeA5Ea18a07D3b5d9ccf6297f8D. Defimon-relayed message transaction, not opened: https://basescan.org/tx/0x16a3ad7651f499e142f479b4cd53622fc6033d97af67fb7fd33cd98dd025a956.
Status: Update, not a new incident. No team claim. No freeze or bounty from the operator, because no operator has posted. Residual balance is a desk estimate. Further-withdraw message is a solicitation, not a completed second drain.
Sources: https://x.com/GoPlusSecurity/status/2106892141716971780, first reports https://x.com/PeckShieldAlert/status/2106684818654482531, https://x.com/CertiKAlert/status/2106685511754735682
Also noted
- DefimonAlerts, carrotfunding message: At 08:05 UTC on 5 Oct the account relayed an on-chain message asking that 80 percent of stolen funds be returned to
0xd998C33b6D1Bb1F759f7D289586267aEA49a06D2by 12:00 UTC on 12 Oct, with 20 percent kept as a bounty, and an email at info@carrotfunding.io. No protocol, chain, hash, or loss figure is in the post. Not scored. Not linked to the Base vault or the two Ethereum drains. - DefimonAlerts, removeLiquidity note: At 11:34 UTC on 5 Oct the account relayed a message saying a transaction was an intentional removeLiquidity, not a swap, and that a private key may be compromised if the recipient did not send it. Linked address
0x81743b7262F52AbAe74E5E8b10866B0e0b72E05A. No loss figure, no transaction hash in the post text. Unconfirmed. Not scored. - DefimonAlerts, Base plea: At 11:58 UTC on 4 Oct, a relayed message asks a “WhiteHat” to return funds and links the Base transaction cited above. Unconfirmed as the vault case. Not a new loss.
- Immunefi: Visible posts in the late slice are product lines, not incident reports. An earlier $150,000 paid-report note was not re-opened as an exploit. Not scored.
- CertiKAlert, PeckShieldAlert: No new first-report after the Base vault alerts. The Base item above is the update path.
- Phalcon_xyz, SlowMist_Team, BlockSecTeam, CyversAlerts, Lookonchain, ZachXBT, rekt.news: No separate first-report exploit in this sweep. Lookonchain lines in the window are position and TVL notes. rekt.news had no new incident page in the window checked.
Sources & references
- https://x.com/GoPlusSecurity/status/2106759999745917293
- https://x.com/GoPlusSecurity/status/2106715903274684681
- https://x.com/GoPlusSecurity/status/2106892141716971780
- https://x.com/PeckShieldAlert/status/2106684818654482531
- https://x.com/CertiKAlert/status/2106685511754735682
- https://x.com/DefimonAlerts/status/2107019214292681094
- https://x.com/DefimonAlerts/status/2107071979920510997
- https://x.com/DefimonAlerts/status/2106715488638136594
- https://etherscan.io/tx/0xa25807c87cc99a9c7195548c1438cde9ad937652cc3fb60fe609c01b339b04d0
- https://etherscan.io/tx/0xaae85f2d7011454ce38a2024642daad54ea9ec81899782edc81dff7294e99739
- https://basescan.org/address/0xD1895f2019c2152FC2b9022D57f19198c4CFCABC
Editor note: scored loss is the two GoPlus Ethereum user drains only. The Base vault stays an update. Signer threshold, Lido queue, LINK-to-ETH cash-out, and the removeLiquidity key warning are unverified.
Read more
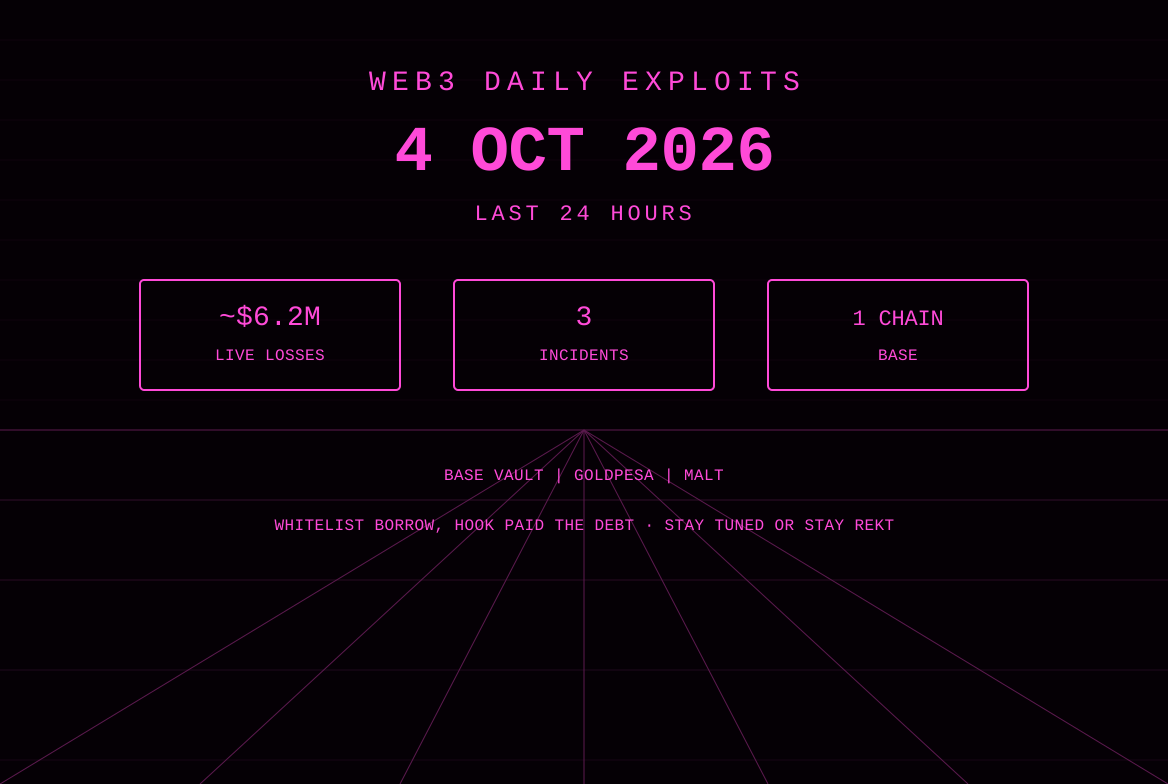
Web3 Daily Exploits — 4 Oct 2026: Base Vault ~$6M wstETH
PeckShield and CertiK flag 1,783 wstETH, about $6M, leaving an unnamed Base vault via a newly deployed proxy. GoldPesa GPXHooks lost about $114.9K to a Uniswap v4 delta mix-up. SlowMist scores MALT at about $72K. Root cause on the vault is unconfirmed.
Web3 Daily Exploits — 3 Oct 2026: NEAR Intents $3.8M Returned
Quiet first-report window. NEAR Intents GM Alex Shevchenko said the $3.8M Omni exploit funds were sent back in full and the investigation is stopping. A labeled exploiter sent a return message on BNB Chain; the published Bitcoin address holds 34.589 BTC. FlashLoop’s 114.09 ETH bounty is still open. Card new live loss is ~$0.
Web3 Daily Exploits — 2 Oct 2026: NEAR Intents $3.8M, FlashLoop $305K
NEAR Intents halted swaps after a bug in Omni deposit and withdrawal infrastructure drained about $3.8M from a BNB Chain hot wallet. A separate Ethereum incident spoofed FlashLoopAdapter Safe checks and left an attacker with about 114.09 ETH. Card live-loss is ~$4.1M across two incidents.
Web3 Daily Exploits — 1 Oct 2026: MetaMask Validator Exit
MetaMask disclosed an infrastructure incident and began exiting affected non-custodial staking validators. Lido said the last exits are expected by 7 Oct, with re-entry up to about 45 days. Researcher Kaden scored diverted block rewards at about 0.36 ETH to a Tornado-funded fee recipient. No wallet-principal loss confirmed.