Web3 Daily Exploits — 6 Oct 2026: Maker Keeper and Set Rounding
Defimon reports a Tornado-funded caller pulled 200 WETH, about $538K, from a dormant 2020 MakerDAO ETH-A flip-keeper whose exit was not behind ds-auth. SlowMist reports Set Protocol lost about 5.08 ETH to an actualizeFee rounding step. Maker core is not scored as the bug.
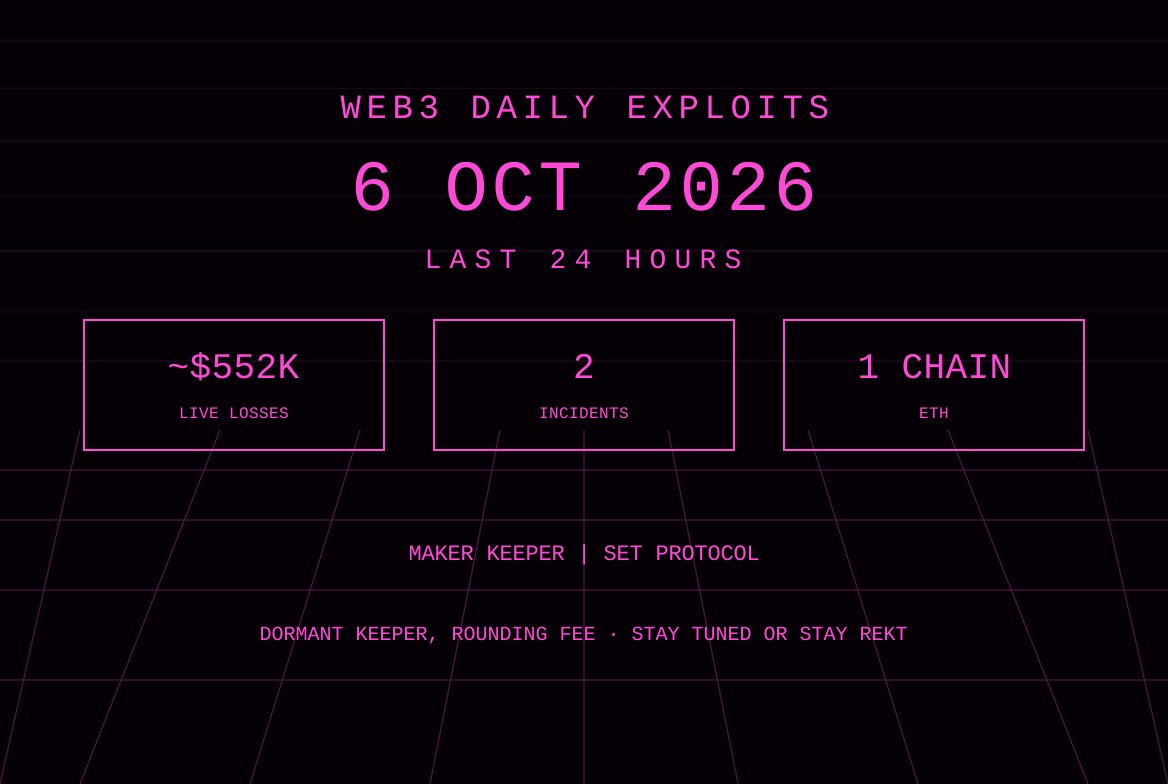
The 6 Oct America/Panama window is a two-incident Ethereum day, both first-desk reports landing after 08:00 UTC. Neither is a core-protocol compromise in the alerts this desk read. The larger line is old collateral sitting on a third-party keeper. DefimonAlerts, at 08:46 UTC, wrote that a Tornado-funded fresh externally owned account drained a dormant 2020 MakerDAO ETH-A liquidation flip-keeper for 200 WETH, about $538,000. The smaller line is share math. SlowMist, at 08:07 UTC, wrote that Set Protocol lost about 5.08 ETH because actualizeFee() raised unitShares from 4,927 to 4,928 even though no fee was minted. The attacker issued before that update and redeemed the same quantity after it. Uniswap v4 flash accounting supplied the temporary liquidity.
Taken together the scored live loss is about $552,000. That figure is Defimon’s $538,000 print plus a desk conversion of the 5.08 ETH at the price implied by 200 WETH for $538,000, about $2,690. SlowMist did not print a dollar. The conversion is on the card only. It is not a second desk figure. MakerDAO core contracts are not scored as the bug. Defimon says Vat, Flipper, and GemJoin behaved as designed. The flaw named in the alert is the keeper implementation’s unprotected exit. Set is scored as a rounding path on a named vault and a named vulnerable contract, not as a Uniswap v4 bug. The flash accounting is the liquidity source in the SlowMist text, not the failure.
A later slice of the same window did not add a third scored loss. Secondary on-chain notes, not desk alerts, put the keeper drain at 06:13 UTC and say the 200 ETH was sent back into Tornado in twenty 10 ETH deposits between about 06:19 and 06:28 UTC. That wash timing is parked under the keeper section as unverified relative to Defimon. ZachXBT’s 5 Oct thread on a Chinese laundering syndicate tied to Lazarus and the Bybit case remains an investigation disclosure, not a fresh drain. A reply under that thread saying about $170,000 of Bitget exploit funds were frozen at a service on Hyperliquid Core is an update on an older incident and is not re-scored. CertiKAlert, PeckShieldAlert, Phalcon, GoPlusSecurity, BlockSecTeam, and CyversAlerts did not post a separate first-report exploit in the posts read for this cutoff. Lookonchain’s 6 Oct lines were trader-position notes, not drains. Immunefi’s visible lines were not incident reports. rekt.news did not publish a new incident post in this window.
MakerDAO ETH-A flip-keeper — Ethereum — 200 WETH — missing auth on a dormant proxy
What happened: DefimonAlerts posted at 08:46 UTC on 6 Oct that a MakerDAO ETH-A liquidation keeper bot lost about $538,000. The token is WETH. The network is Ethereum. The type line is access control, missing auth on a keeper proxy. The account says a Tornado-funded fresh externally owned account drained a dormant 2020 flip-keeper. The keeper is an upgradeable proxy printed as 0x9c05…8273. The expanded victim link in that post resolves to 0x9c05a05893ada984fc20d0da0c046de5cc0e8273. The implementation is printed as 0x6839…5546. Defimon says that implementation is unverified. This brief does not expand the truncated implementation or the truncated owner beyond the prefixes in the alert.
The keeper had won four ETH-A liquidation auctions, numbers 1457 through 1460, 50 WETH each, in 2020, and never called deal(). That left 200 WETH of collateral locked in the ETH-A Flipper. The implementation’s drain routine, selector 0x8804d1de, was not protected by ds-auth. Defimon prints owner as 0xadc374e7 and authority as 0x0, so any caller could invoke the routine. The path in the alert is: call deal() on the keeper’s old auctions, Vat.flux the collateral to the keeper, GemJoin.exit() the 200 WETH to an attacker-supplied recipient, then unwrap to 200 ETH. The short link rendered as a function name in the post text resolves to flipper.deal, which matches the deal() step in the prose. MakerDAO core, Vat, Flipper, and GemJoin, behaved as designed. The flaw is the third-party keeper’s unprotected exit.
The transaction link in the Defimon post resolves to 0xbb6940f7c2a1e68cafbae7bb9b94d09af9af06ec3a114f6996f2cab993f3a88c. The attacker link resolves to 0x01eb957e5c7dcddd60f3c875956ccc6fb9bda5fa. Secondary write-ups restated the Defimon figures and the same path. They did not add a second loss number, a team statement, or a recovered balance. No Sky or MakerDAO post was found in this window claiming the keeper or disputing the core-contracts line.
After the desk alert, two non-desk accounts described a short wash cycle. One wrote that the attacker wallet was funded via Tornado at 05:57 UTC, that the exploit pulled 200 WETH out of the ETH-A GemJoin at 06:13 UTC, and that all 200 ETH went back into Tornado between 06:19 and 06:28 UTC as twenty deposits of 10 ETH. A second account used the same 06:13 UTC clock and the same missing-auth story. Those clocks are not in the Defimon text. This desk did not re-open the funding or exit hops. The wash is noted, not scored as a new fact beyond the 200 ETH exit already in the alert.
Protocol / chain / asset: Third-party MakerDAO ETH-A flip-keeper, not Maker core. Ethereum. Asset is WETH, unwrapped to ETH in the alert. Auctions 1457–1460 are the collateral source named by Defimon. The Flipper is where the collateral sat because deal() was never called. That is a settlement leftover from 2020, not a new auction. Sky, the current brand over the Maker system, is not named as the operator of this keeper in the alert.
Loss: 200 WETH, about $538,000, Defimon’s print. Four lots of 50 WETH match that total. No recovery figure. No bounty in the post. The $538,000 is the card’s main line. A secondary note printed about $543,000 for the same 200 ETH. That is not used. Defimon’s figure stays.
Attack type: Access control. Unprotected exit on a third-party keeper implementation. ds-auth not applied to selector 0x8804d1de. Authority printed as the zero address. Not a Vat, Flipper, or GemJoin bug in the alert text. Funding described as Tornado. This desk did not re-open the funding hop.
Explorer URLs: Drain transaction https://etherscan.io/tx/0xbb6940f7c2a1e68cafbae7bb9b94d09af9af06ec3a114f6996f2cab993f3a88c. Attacker https://etherscan.io/address/0x01eb957e5c7dcddd60f3c875956ccc6fb9bda5fa. Victim keeper proxy https://etherscan.io/address/0x9c05a05893ada984fc20d0da0c046de5cc0e8273. Implementation 0x6839…5546 and owner 0xadc374e7 are prefixes from the alert, not full addresses, and are not linked.
Status: First desk report in this window. Execution date in the alert is 6 Oct 2026. No freeze, no return, no operator statement. Core contracts not scored as affected. Implementation unverified, per Defimon. Secondary wash timing stays unverified against the desk post.
Sources: https://x.com/DefimonAlerts/status/2107391959853600812
Set Protocol — Ethereum — about 5.08 ETH — actualizeFee rounding
What happened: SlowMist posted a threat-intelligence alert at 08:07 UTC on 6 Oct. The loss line is about 5.08 ETH at Set Protocol. The root cause in the post is actualizeFee(). The function recalculated unitShares with upward rounding even though no fee was minted, raising unitShares from 4,927 to 4,928. The attacker issued before the update and redeemed the same quantity afterward, extracting collateral from the rounding-induced unit increase. Uniswap v4 flash accounting supplied temporary liquidity to scale the exploit. That is the full mechanism in the desk text. This brief does not add a decoded call trace.
SlowMist named four addresses. Attacker EOA 0x506440728d84eb22809dc9464bc8189618a1c5b6. Attack contract 0x016feaaa25ab8325e233bc8a2c25055bee0b2f6e. Victim, labeled Set Protocol Vault, 0x5b67871c3a857de81a1ca0f9f7945e5670d986dc. Vulnerable contract 0x54e8371c1ec43e58fb53d4ef4ed463c17ba8a6be. The post ends with a Tx label. In the text read here, no transaction hash follows that label. This brief does not invent one. The powered-by link on the post resolves to slowmist.ai, not to an explorer page.
A reply under the alert, not a SlowMist post, says gas came out of Tornado, 0.0979 ETH from the 0.1 pool at 07:17 UTC, 19 minutes before the exploit transaction. The same reply says the victim Set V1 vault still holds about 490 WETH, 2.2 WBTC, and 4,500 LINK of legacy collateral, roughly $1.6 million, and asks which other Sets sit behind the same fee logic. That residual and the Tornado hop are unverified. They are not a status and they are not a second loss. Later replies restated the 4,927 to 4,928 unitShares step. Those restatements match the SlowMist text and do not add a figure.
Protocol / chain / asset: Set Protocol, named by SlowMist. Ethereum. Loss asset printed as ETH, about 5.08. The victim is labeled a Set Protocol vault. The vulnerable contract is the address on the actualizeFee path in the alert, not identified further here. Uniswap v4 is the flash-accounting venue, not the scored bug. Set V1 is a label from a reply, not from SlowMist, and is not used as a version claim.
Loss: About 5.08 ETH. No dollar on the SlowMist post. At the about $2,690 implied by Defimon’s 200 WETH for $538,000, 5.08 ETH is about $13,700. That conversion is a card line only. No recovery. Residual collateral in the reply is unverified and is not subtracted or added.
Attack type: Rounding. Upward unitShares update inside actualizeFee() with no fee minted, then issue before and redeem after. Not an approval drain and not a key compromise in the alert text.
Explorer URLs: Attacker https://etherscan.io/address/0x506440728d84eb22809dc9464bc8189618a1c5b6. Attack contract https://etherscan.io/address/0x016feaaa25ab8325e233bc8a2c25055bee0b2f6e. Victim vault https://etherscan.io/address/0x5b67871c3a857de81a1ca0f9f7945e5670d986dc. Vulnerable contract https://etherscan.io/address/0x54e8371c1ec43e58fb53d4ef4ed463c17ba8a6be. No transaction URL, because the desk post’s Tx line did not include a hash in the text read here.
Status: First desk report in this window. No Set Protocol statement found. No freeze posted by a desk. Residual balance and Tornado funding are reply claims and stay unverified. The one-unit share increase is the SlowMist figure, not a reconstruction.
Sources: https://x.com/SlowMist_Team/status/2107382337654951943
Also noted
- ZachXBT, Lazarus laundering thread: At 12:13 UTC on 5 Oct ZachXBT posted a thread saying he posed as a client of a Chinese syndicate he ties to laundering for North Korea’s Lazarus Group, including Bybit exploit proceeds. He wrote that he fronted 349,700 USDC. Addresses named in the thread include
0xbaa551da0ae0c93025d9a983a68025a27dc15337, gas-funded by a wallet he says is on the Bybit exploit blacklist, and a Solana cluster he ties to more than $12 million of Bybit-linked funds. He wrote that Tether later froze 442,000 USDT at0x652d7f9edaaa8891be2de74ea568d70af823d89e. This is an investigation disclosure about an older hack. Not a new exploit. Not scored. - UPDATE — Bitget, Hyperliquid freeze: In a reply at 18:15 UTC on 5 Oct, ZachXBT wrote that he has seen DPRK actors use bridges to Hyperliquid when they launder, and that about $170,000 total was frozen for the Bitget exploit at a service on HL Core. That is an update on the September Bitget case. Not a new drain. Not added to today’s card.
- Set residual, unverified: A reply under the SlowMist alert claims the victim vault still holds about 490 WETH, 2.2 WBTC, and 4,500 LINK, roughly $1.6 million, and that 0.0979 ETH of gas came from Tornado at 07:17 UTC. Not a desk alert. Not scored.
- Keeper wash clocks, unverified: Non-desk notes put Tornado funding at 05:57 UTC, the GemJoin exit at 06:13 UTC, and a 20 by 10 ETH Tornado return between 06:19 and 06:28 UTC. Not a second loss.
- CertiKAlert, PeckShieldAlert, Phalcon, GoPlusSecurity, BlockSecTeam, CyversAlerts, Lookonchain: No separate first-report exploit in the posts read for this cutoff. Lookonchain’s recent visible lines were position notes, not drains.
- Immunefi, rekt.news: No new incident post used as a loss figure in this window.
Sources and references
- DefimonAlerts, MakerDAO ETH-A keeper, 08:46 UTC on 6 Oct: https://x.com/DefimonAlerts/status/2107391959853600812
- SlowMist, Set Protocol actualizeFee, 08:07 UTC on 6 Oct: https://x.com/SlowMist_Team/status/2107382337654951943
- ZachXBT thread start, 12:13 UTC on 5 Oct: https://x.com/zachxbt/status/2107081638073319437
- ZachXBT, Bitget freeze note, 18:15 UTC on 5 Oct: https://x.com/zachxbt/status/2107172895218954683
- Keeper drain transaction: https://etherscan.io/tx/0xbb6940f7c2a1e68cafbae7bb9b94d09af9af06ec3a114f6996f2cab993f3a88c
Editor’s note: both scored losses are third-party or legacy surfaces on Ethereum, not new core deployments. The keeper collateral had been sitting since 2020 because deal() was never called. The Set step is a one-unit share increase. Figures follow the desk posts. Truncated addresses stay truncated. Reply claims and wash clocks stay unverified.
Read more
Web3 Daily Exploits — 5 Oct 2026: LINK Permit2 and DAI Poison
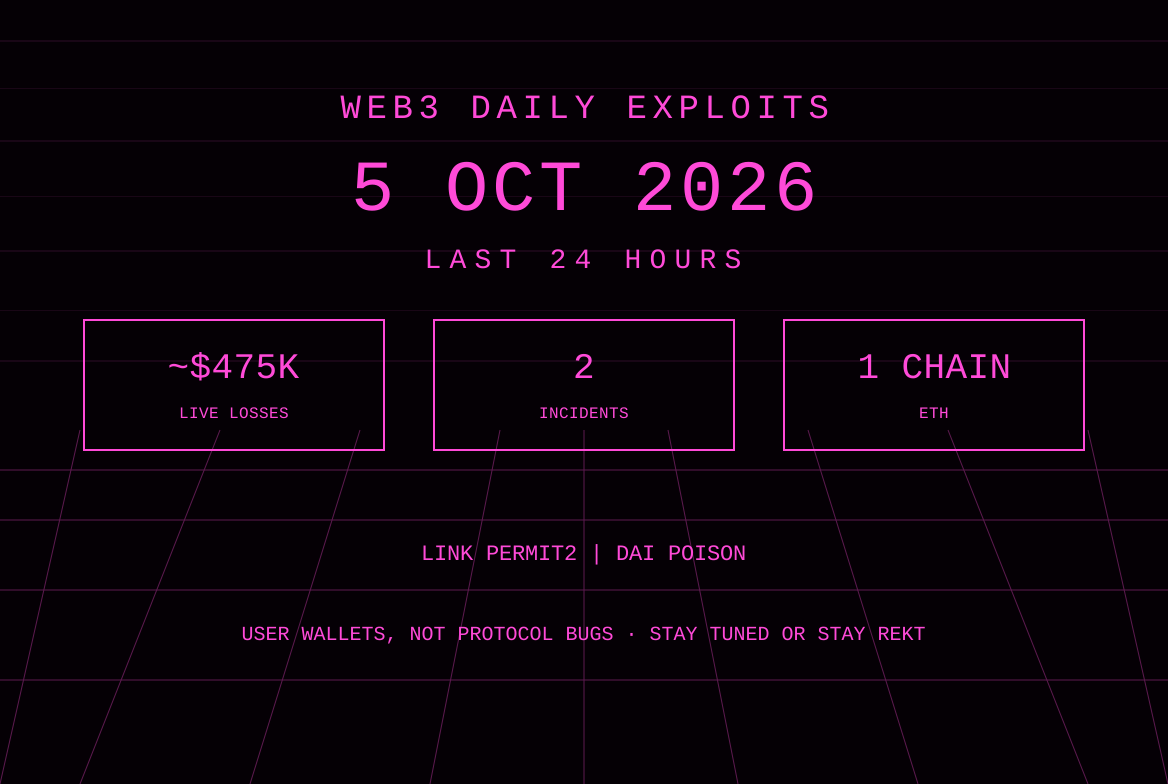
GoPlus posts two Ethereum user drains first seen in this window: 12,041.3036 LINK, about $169.7K, pulled through a Permit2 path, and 305,560.46 DAI sent to a prefix-and-suffix lookalike. The Base vault gets a root-cause update and a $31.7M residual figure. That $6M is not re-scored.
Web3 Daily Exploits — 4 Oct 2026: Base Vault ~$6M wstETH
PeckShield and CertiK flag 1,783 wstETH, about $6M, leaving an unnamed Base vault via a newly deployed proxy. GoldPesa GPXHooks lost about $114.9K to a Uniswap v4 delta mix-up. SlowMist scores MALT at about $72K. Root cause on the vault is unconfirmed.
Web3 Daily Exploits — 3 Oct 2026: NEAR Intents $3.8M Returned
Quiet first-report window. NEAR Intents GM Alex Shevchenko said the $3.8M Omni exploit funds were sent back in full and the investigation is stopping. A labeled exploiter sent a return message on BNB Chain; the published Bitcoin address holds 34.589 BTC. FlashLoop’s 114.09 ETH bounty is still open. Card new live loss is ~$0.
Web3 Daily Exploits — 2 Oct 2026: NEAR Intents $3.8M, FlashLoop $305K
NEAR Intents halted swaps after a bug in Omni deposit and withdrawal infrastructure drained about $3.8M from a BNB Chain hot wallet. A separate Ethereum incident spoofed FlashLoopAdapter Safe checks and left an attacker with about 114.09 ETH. Card live-loss is ~$4.1M across two incidents.