Web3 Daily Exploits — 3 Oct 2026: NEAR Intents $3.8M Returned
Quiet first-report window. NEAR Intents GM Alex Shevchenko said the $3.8M Omni exploit funds were sent back in full and the investigation is stopping. A labeled exploiter sent a return message on BNB Chain; the published Bitcoin address holds 34.589 BTC. FlashLoop’s 114.09 ETH bounty is still open. Card new live loss is ~$0.
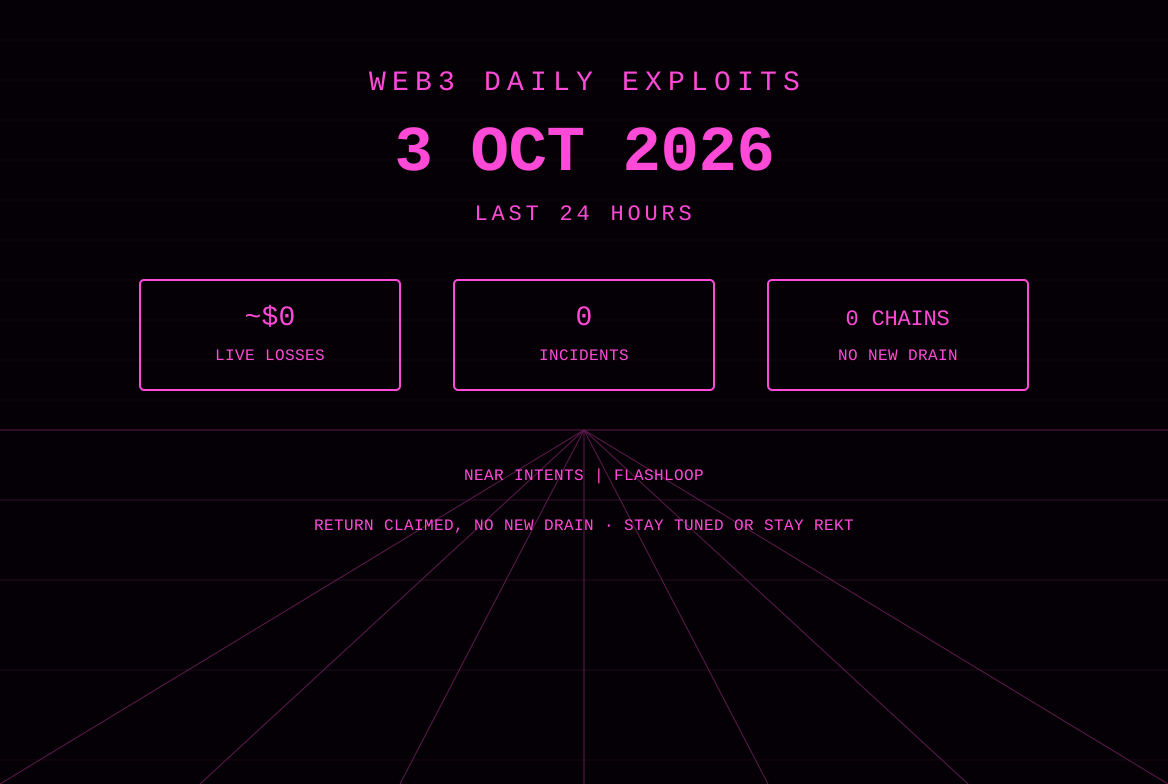
The 3 Oct America/Panama window is quiet on first reports. No new protocol drain, bridge mint, or hot-wallet outflow was posted by the desks checked for this slice. The material item is an UPDATE to yesterday’s NEAR Intents incident. At 15:52 UTC on 2 Oct, NEAR Intents general manager Alex Shevchenko wrote that the funds from the $3.8 million hack were sent back in full, that the team is stopping the investigation, and that researchers should use bug bounties instead of disrupting services. NEAR co-founder Illia Polosukhin quoted that post at 17:24 UTC and said the funds were back in full at 14:30 UTC the same day, after the Intents team identified the party in under 24 hours with SHIELD, the product’s AI security layer, plus what he called aggressive detective work. The official @near_intents account reposted the same claim at 18:53 UTC. This card does not score a new live loss. Yesterday’s preliminary $3.8 million comes off the new-loss line because the operator now says the principal is back and the probe is closed. The on-chain picture this brief could verify is narrower than that sentence, and the gap is flagged below.
The other carry-over is FlashLoopAdapter. SlowMist’s 114.09 ETH figure and DefimonAlerts’ $305,000 print were already scored on the 2 Oct brief. No return transaction was confirmed in this window. The owners’ 10 percent bounty, relayed through DefimonAlerts, still runs to 18:00 UTC on 3 Oct. That amount stays outstanding as an older item. It is not added again to today’s card. Today’s boxes are ~$0 new live losses, 0 new incidents, 0 new exploit chains.
UPDATE: NEAR Intents / Omni — return claimed, investigation stopping — prior loss ~$3.8M
What happened: Yesterday’s brief recorded the 1 Oct operator post: services stopped after a bug in the Omni deposit and withdrawal infrastructure where it interacts with the NEAR Intents smart contract, preliminary loss about $3.8 million, contract-side patch claimed, full user compensation promised, law enforcement notified, and no repayment receipt yet. PeckShieldAlert, citing ZachXBT, scored BNB Chain hot-wallet outflows at $3.865 million, with funds moved toward KuCoin and bridged toward Bitcoin. GoPlusSecurity scored about $3.87 million and described an early assessment of a withdrawal-authorization bypass, isolated from NEAR Protocol mainnet. Those figures are not restated as a new drain.
The new facts start just after midnight UTC on 2 Oct. At 00:18 UTC Shevchenko posted “We have identified you, sir,” and published three return addresses: Bitcoin bc1qjhv3hu8rfteh5e8exfmalvx2z3pzlmjlgnzxey, BNB / Ethereum 0xB18a1aEDfde8B70FD67012C9E9c7a088B4d0C0e7, and Solana AHTfKaeRcaK1sbSG8MFJS2uPxLBChfenigNtvbWEkhKD. He called it the last window for responsible disclosure and said that window would close after 48 hours, which lands near 00:18 UTC on 4 Oct. He did not name the party, did not publish the evidence used to identify them, and did not attach a transaction list.
At 15:52 UTC the same day he posted the close-out: the funds from the $3.8 million hack were sent back in full, the investigation is stopping, and bug bounties are the requested path. Polosukhin’s 17:24 UTC post adds a clock time the GM post does not: funds back in full at 14:30 UTC, identification in under 24 hours, SHIELD plus detective work, communication established, and hardening already underway. He also wrote that privacy is a right but not a way to facilitate crime, and that confidentiality cannot come at the expense of lawfulness. Neither post publishes a token table, a Bitcoin transaction id, or a split between the three published addresses. The @near_intents repost at 18:53 UTC does not add figures.
Protocol / chain / asset: Same incident as 2 Oct: NEAR Intents and the Omni / HOT Bridge deposit and withdrawal path, with the scored outflow on BNB Chain from the HOT Bridge treasury GoPlus named at 0x233c5370CCfb3cD7409d9A3fb98ab94dE94Cb4Cd. The return path the operator published spans Bitcoin, an EVM address used for both BNB Chain and Ethereum, and Solana. NEAR Protocol L1 is still not the reported failure point. This is a status change on an existing incident, not a second exploit.
Loss: Operator preliminary figure remains about $3.8 million, now described by the operator as returned in full. This brief does not re-score it as live loss. What this desk verified on explorers is not the whole $3.8 million. The published Bitcoin address shows total received and current balance of 34.58927254 BTC, all from inflows dated 2 Oct 2026. The visible credits are 5.79441418 BTC (58c6487fe95c5fa51317eaa7ba2d327e80262c23ebb11e6c579d0c05c13d5665), 8.67565137 BTC (45ad939aebb42044a3313eaa5eb363d65a9fd96ce20f4d546eea14089c033d8f), 11.44807246 BTC (1f24b67e0135f4d7be6cfe1d450e42d2b5e16f147170ad85881cc96148695e73), a 0.00002222 BTC dust credit (767ac8c26443c85d91bd5d58759d4742480ab4b8fe737cde33d9ef60e3d44613), and 8.67111231 BTC (1205e8a86dfe8375a7ee5989524bfae63769e76d9db026f6931c0ba208dea216). Secondary write-ups valued 34.59 BTC near $2.95 million at about $85,200 and timed the credits 14:31–15:05 UTC. The explorer summary used for this brief dated them 2 Oct but returned earlier clock times, so the minute window is not settled here. The dollar value of that Bitcoin is not independently marked to a desk print.
The BNB Chain transaction secondary outlets tied to the return is real, and it is not the principal. BscScan shows success at 16:15:28 UTC on 2 Oct, from 0x09Fd1f5d9F185067A92493E43AA259ea4AB3ad37 labeled Near Intents Exploiter 1, to 0xB18a1aEDfde8B70FD67012C9E9c7a088B4d0C0e7 labeled Near Intents: Recovery Wallet, value 0.038726950209346707 BNB, with no token transfers on the page. The input data decodes to: “We've returned all the funds, we were in the wrong. Thank you to the Near team for being respectful, constructive, and cordial during the return process. Remember to always use bug bounties!” That message matches the GM’s close-out in substance. It does not, by itself, move $3.8 million. Secondary reports that the published EVM address held about 1.04 BNB and 0.30 ETH, and that the Solana address was empty, were not re-checked on those explorers for this brief. The residual route that would close the gap between 34.589 BTC and the operator’s $3.8 million is therefore unconfirmed here. Wu Blockchain’s later note, 34.59 BTC worth about $2.95 million and roughly $850,000 by another route, is the same secondary split. The operator statement is the basis for taking the $3.8 million off the new-loss line. It is not a receipt this brief can add up from the two verified objects alone.
Attack type: Unchanged from yesterday. Operator description remains a bug in Omni deposit and withdrawal infrastructure interacting with the NEAR Intents smart contract. GoPlus’s early assessment remains a withdrawal-authorization bypass. The return does not add a root-cause function, and Polosukhin did not describe how SHIELD identified the party. Attribution of the original flow to a Lazarus-labeled address, already flagged unconfirmed by GoPlus, is not updated by the return posts.
Explorer URLs: Message transaction https://bscscan.com/tx/0x3b9b3cc9e53ae9ad97850c2b8f3e19259d97834210858f467bfc377f2aeeb3af. Labeled exploiter https://bscscan.com/address/0x09fd1f5d9f185067a92493e43aa259ea4ab3ad37. Published EVM recovery address https://bscscan.com/address/0xB18a1aEDfde8B70FD67012C9E9c7a088B4d0C0e7. Published Bitcoin address https://mempool.space/address/bc1qjhv3hu8rfteh5e8exfmalvx2z3pzlmjlgnzxey. Bitcoin credits https://mempool.space/tx/58c6487fe95c5fa51317eaa7ba2d327e80262c23ebb11e6c579d0c05c13d5665, https://mempool.space/tx/45ad939aebb42044a3313eaa5eb363d65a9fd96ce20f4d546eea14089c033d8f, https://mempool.space/tx/1f24b67e0135f4d7be6cfe1d450e42d2b5e16f147170ad85881cc96148695e73, https://mempool.space/tx/1205e8a86dfe8375a7ee5989524bfae63769e76d9db026f6931c0ba208dea216. Yesterday’s GoPlus victim and attacker addresses are unchanged and are not re-listed as new evidence.
Status: Operator says full return and investigation stopping. User compensation pledge from 1 Oct is separate from the exploiter return; this brief did not find a receipt that users have been paid. Identity of the sender is unconfirmed in public. The 34.589 BTC at the published Bitcoin address is confirmed as a balance. The message transaction is confirmed as a message plus dust BNB, not as the $3.8 million. The residual route is unconfirmed. No detailed public report has replaced the promised follow-up.
Sources: https://x.com/AlexAuroraDev/status/2105814573152661894, https://x.com/AlexAuroraDev/status/2106049685928677585, https://x.com/ilblackdragon/status/2106072953570181155, https://x.com/near_intents/status/2106095140586791407
UPDATE: FlashLoopAdapter — Ethereum — 114.09 ETH still out — bounty clock still running
What happened: No new FlashLoop transaction was posted by SlowMist, DefimonAlerts, or Aave in this window. The 1 Oct attack transaction 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4 remains the cited drain: fake Safe spoofing isModuleEnabled, attacker-controlled router and calldata becoming execTransactionFromModule on two Safes that had enabled the third-party adapter, Morpho used as the flash-loan source in the Defimon write-up, about 1,300 WETH of debt repaid, and 114.096 ETH retained by attacker EOA 0x42c2633438609881c8fBAb82414eb9A0c45F9353. Aave founder Stani Kulechov’s 2 Oct statement that this is not an Aave v3 contract, and SlowMist’s agreement, are unchanged. Aave v3 core is still not the reported bug.
The in-window movement is correspondence, not a settlement. DefimonAlerts relayed the owners’ offer to let the attacker keep 11.41 ETH and return 102.69 ETH to 0x329c54289Ff5D6B7b7daE13592C6B1EDA1543eD4 before 18:00 UTC on 3 Oct 2026. That deadline falls inside today’s calendar date and had not expired at this brief’s cutoff. No matching return to that address was confirmed here. A third-party trace posted on 3 Oct described the 1 Oct attacker as funded by a RAILGUN relay and the retained ETH as sent back toward RAILGUN through 0x951Ad21B…. That post is not a desk alert, does not match a SlowMist update, and is unconfirmed in this brief. It is not used to change the loss figure or the laundering status.
Protocol / chain / asset: Ethereum. Module 0x16bb8b912da187870c23ec6756bb3fad061283d8. Victim Safes 0xcfedf95a3653a128dfc2e4288758a1a1850d169f and 0xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520. Retained asset ETH. Not re-counted as a new incident.
Loss: Still about 114.09 ETH, Defimon’s $305,000 print. Not added to today’s card. Gross weETH withdrawal remains collateral movement after debt repayment, not attacker profit.
Attack type: Unchanged access-control spoof on a Safe module. Not a stolen owner key and not an Aave pool insolvency.
Explorer URLs: Attack transaction https://etherscan.io/tx/0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4. Attacker EOA https://etherscan.io/address/0x42c2633438609881c8fBAb82414eb9A0c45F9353. Vulnerable module https://etherscan.io/address/0x16bb8b912da187870c23ec6756bb3fad061283d8.
Status: Confirmed incident from 1–2 Oct. Return unconfirmed. Bounty open until 18:00 UTC on 3 Oct 2026. RAILGUN path unconfirmed.
Sources: https://x.com/DefimonAlerts/status/2105695635647144370, https://x.com/SlowMist_Team/status/2105855276536725599, https://x.com/StaniKulechov/status/2105892291638436078, https://x.com/DefimonAlerts/status/2105765575766990932
Also noted
- DefimonAlerts: In-window posts are on-chain message relays, not new protocol alerts. One, at 09:12 UTC on 3 Oct, demands 80 percent of remaining USDC back within 48 hours, offers a 20 percent bounty, and says the sender works at Circle and will start a freeze. That employment claim is unconfirmed. Another, at 06:05 UTC, is a YAYO NFT owner asking to buy back 36 tokens taken in the older PaymentProcessorV2 incident. A 2 Oct relay asks for 0.366 ETH to
0x2E1e6EE0D755afB85304F2a51aAc7D130B5b6DA4with a 4 Oct deadline. None of these are scored. - CertiKAlert: The 2 Oct thread on September losses of about $772.4 million, Q3 losses of about $1.27 billion, and year-to-date losses of about $2.69 billion was already noted yesterday. No new exploit hash in this slice.
- SlowMist_Team: No new TI alert after the FlashLoop note and the Punycode amplification already carried yesterday.
- PeckShieldAlert, Phalcon_xyz, GoPlusSecurity, BlockSecTeam, CyversAlerts, Lookonchain, ZachXBT, Immunefi, rekt.news: No separate first-report exploit in the keyword sweep for this window. ZachXBT’s visible 2 Oct post is a question about UPay and a sanctioned marketplace, not a new drain hash. Beldex BDX-BSC posts circulating on 2–3 Oct refer to the June 2026 bridge mint, not a new incident. Allbridge flash-loan write-ups in secondary pages did not match a desk alert inside this 24-hour slice and are not scored.
Sources & references
- https://x.com/AlexAuroraDev/status/2105814573152661894
- https://x.com/AlexAuroraDev/status/2106049685928677585
- https://x.com/ilblackdragon/status/2106072953570181155
- https://x.com/near_intents/status/2106095140586791407
- https://x.com/near_intents/status/2105642219357241796
- https://x.com/DefimonAlerts/status/2105695635647144370
- https://x.com/DefimonAlerts/status/2105765575766990932
- https://x.com/DefimonAlerts/status/2106311377203630118
- https://x.com/SlowMist_Team/status/2105855276536725599
- https://x.com/StaniKulechov/status/2105892291638436078
- https://x.com/CertiKAlert/status/2105976008201400320
- https://bscscan.com/tx/0x3b9b3cc9e53ae9ad97850c2b8f3e19259d97834210858f467bfc377f2aeeb3af
- https://mempool.space/address/bc1qjhv3hu8rfteh5e8exfmalvx2z3pzlmjlgnzxey
- https://etherscan.io/tx/0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4
Editor note
Quiet first-report day. The NEAR Intents line moves from pledged compensation to an operator return claim, with 34.589 BTC verified at the published Bitcoin address and a labeled message on BNB Chain that does not itself carry the principal. The gap to $3.8 million stays open until a token table lands. FlashLoop’s bounty clock is the only live older item, and it is not a new incident. No hashes were invented for routes this desk did not open.
Read more
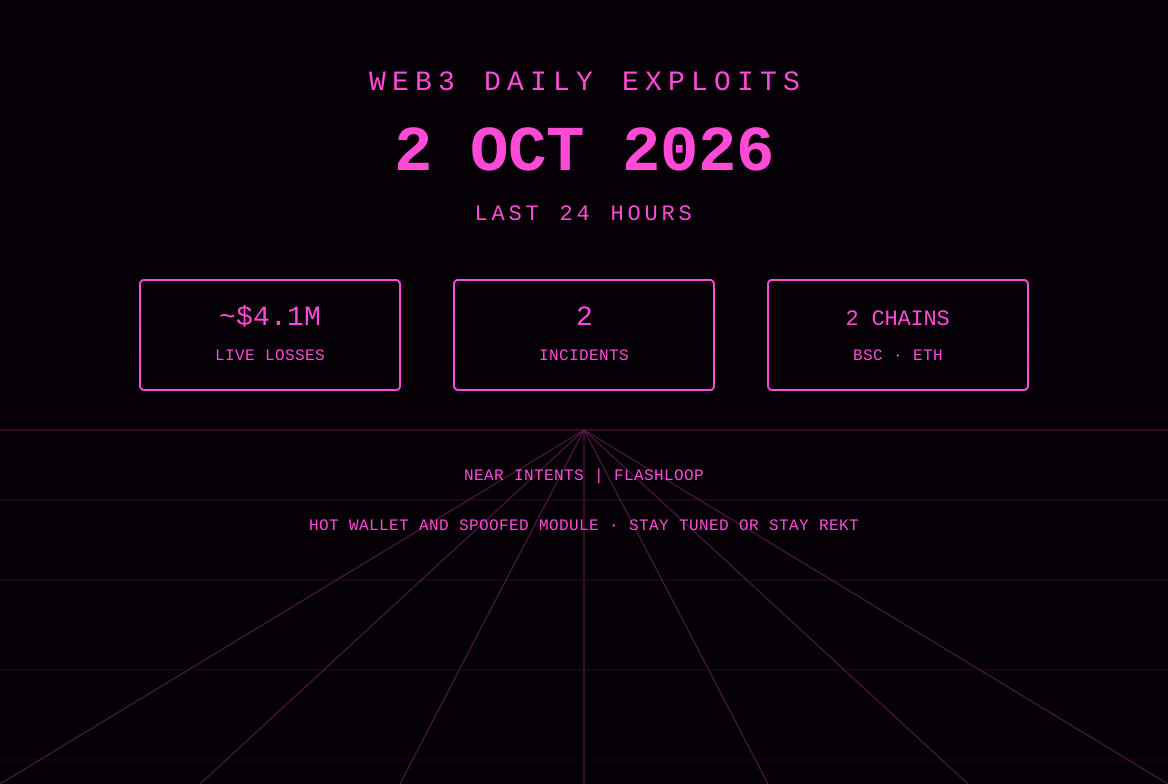
Web3 Daily Exploits — 2 Oct 2026: NEAR Intents $3.8M, FlashLoop $305K
NEAR Intents halted swaps after a bug in Omni deposit and withdrawal infrastructure drained about $3.8M from a BNB Chain hot wallet. A separate Ethereum incident spoofed FlashLoopAdapter Safe checks and left an attacker with about 114.09 ETH. Card live-loss is ~$4.1M across two incidents.
Web3 Daily Exploits — 1 Oct 2026: MetaMask Validator Exit
MetaMask disclosed an infrastructure incident and began exiting affected non-custodial staking validators. Lido said the last exits are expected by 7 Oct, with re-entry up to about 45 days. Researcher Kaden scored diverted block rewards at about 0.36 ETH to a Tornado-funded fee recipient. No wallet-principal loss confirmed.
Web3 Daily Exploits — 30 Sep 2026: MCN $93K, MUS $37K
First-report this window: SlowMist flagged MCN Labs LPBonus for ~$92.6k via inconsistent MSN reserve accounting, and MUSystem for ~$36.9k via a first-deposit bonus double-count. Bitget published SlowMist and Mandiant progress reports naming a third-party zero-day foothold from 31 Aug. Limit Break victim mail continued.
Web3 Daily Exploits — 29 Sep 2026: Reality.eth XSS, $0 Drain
First-report this window: DefimonAlerts flagged a stored XSS in the reality.eth question renderer; the project confirmed a 2022-era reality-eth-lib bug, shipped v3.4.32, and reported no confirmed drain. Bitget reopened ETH rails with a net inflow and thanked NEAR Intents SHIELD for a $503k mid-swap freeze. Limit Break whitehat mail continued.