Web3 Daily Exploits — 4 Oct 2026: Base Vault ~$6M wstETH
PeckShield and CertiK flag 1,783 wstETH, about $6M, leaving an unnamed Base vault via a newly deployed proxy. GoldPesa GPXHooks lost about $114.9K to a Uniswap v4 delta mix-up. SlowMist scores MALT at about $72K. Root cause on the vault is unconfirmed.
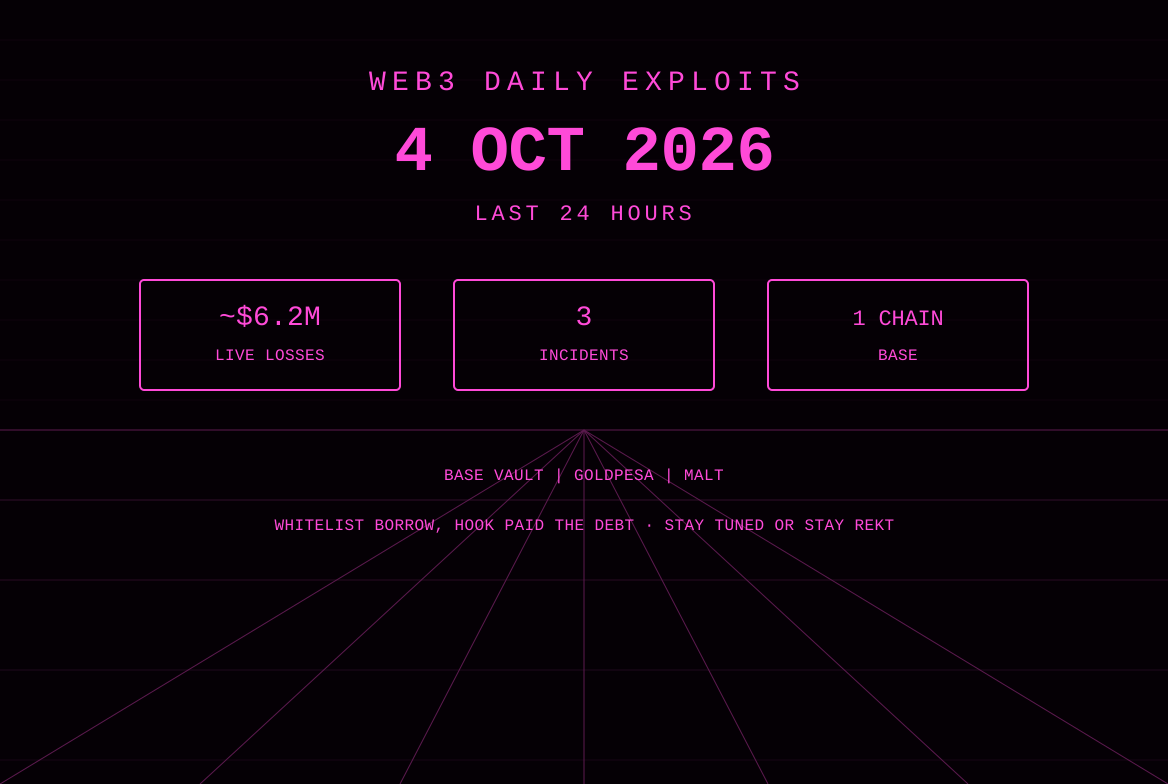
The 4 Oct America/Panama window is not quiet. Three first reports land inside the slice, and the dollar line is dominated by one Base outflow that desks are still naming differently. PeckShieldAlert, at 09:56 UTC, wrote that 0x0B5126e1bc27C0de77e02e97945760A674EdB034 had drained 1,783 wstETH, about $6 million, on Base. Three minutes later CertiKAlert described the same figure as a borrow of about 1,783 aBaswstETH from vault 0xD1895f2019c2152FC2b9022D57f19198c4CFCABC, redeemed through Aave into about 1,783 wstETH now sitting at that address. ExVul, at 10:09 UTC, called the target an unnamed vault and counted 1,783.067 aBaswstETH across six outflows. An earlier secondary print, attributed to Blockaid, had the same vault at about $2.02 million and still in progress. This brief scores the later desk figure, about $6 million, and treats the $2.02 million line as a mid-attack snapshot, not a second incident.
The other two first reports are smaller and better specified. DefimonAlerts posted GoldPesa at 14:25 UTC on 3 Oct: a logic error in the GPXHooks Uniswap v4 hook on Base, loss $114,000, incident date labeled 2026-10-02. SlowMist followed at 16:06 UTC with a tighter print, about $114,900, and a delta-isolation write-up. At 16:18 UTC SlowMist posted a separate MALT alert, about $72,000, on a swap function that counted treasury DAI as caller input. Added to the Base vault figure, the card is about $6.2 million of newly reported live loss, three incidents, one confirmed chain. The MALT chain is not in the alert text this desk read, and the cited contract page on Ethereum returned no matching transactions, so it is not drawn into the chain box.
Root cause on the $6 million line is open. CertiK and ExVul describe a newly deployed contract on a vault borrow path. A secondary Blockaid note says a new contract was added to a whitelist. A quote account said early signs point to a compromised wallet rather than a protocol bug. That last claim is not a desk finding and is flagged unverified. The address page this desk opened no longer lists a wstETH balance, and it shows a later Withdraw into the Aave pool proxy plus calls to the Base Lido wstETH token. The “still sitting” line is already stale relative to that page.
Unnamed Base vault — about 1,783 wstETH — borrow path — root cause open
What happened: Between about 09:54 and 10:09 UTC on 4 Oct, three monitors described the same Base outflow. PeckShieldAlert named the recipient and the token. CertiKAlert named the source vault and the path: a newly deployed proxy borrowed about 1,783 aBaswstETH from 0xD1895f2019c2152FC2b9022D57f19198c4CFCABC, then redeemed via Aave for about 1,783 wstETH at 0x0B5126e1bc27C0de77e02e97945760A674EdB034. ExVul counted 1,783.067 aBaswstETH across six vault outflows, said a newly whitelisted contract used the vault’s borrowing path, and said the precise authorization failure is unconfirmed. It named loot contract 0xcdFE91301356da873562EF513828a60dba1F569d and pointed at one transaction that moved 1 aBaswstETH, with five later outflows making up the total. That linked transaction hash was behind a short URL this desk did not expand, so it is not restated here as a hash.
What this desk opened on BaseScan matches the cast list, not the token table. The recipient address holds about 0.02 ETH and does not list wstETH among token holdings. Recent calls from that address include 0xf1c9448c615122423c5f21aad2f690e76dfe7b9e9bfc320b1d36ef79a7a9cd7e, 0xfc4bba1eb305270e6e137fb3e9e02706c088c025d80ade224fd72d37f9e0cfb2, 0x57a49136a5a5dbbb06ba03a3d76c85d59f6f6ae5547445e7d0ee4cbf3053d375, and 0x8e434d444bdeace44308717072026a7487ec7792befa0d1a9bbd01bcfe467db7, all to the loot contract ExVul named. A Withdraw, 0x557bfd0e8530fd3e089748ccaabaa7837877f7578b13a377008474f2e367ee8c, went to Aave’s Base pool proxy 0xA238Dd80C259a72e81d7e4664a9801593F98d1c5. Two later transfers, 0xe824b27ca120908d145fd071e27f43f05aff541296d76c7772c3829398cf85d2 and 0x20fb64ee4adceee8fb3c36b2441a32b830917afc56fe7064b46f82a58f6be145, went to the Base Lido wstETH token 0xc1CBa3fCea344f92D9239c08C0568f6F2F0ee452. The page did not print token amounts on those rows, so this brief does not invent a split between unwrap, transfer, and residual. The vault itself is a TransparentUpgradeableProxy. The recent Borrow rows the page returned are about 170 days old, from 0x3E68796A…2e7a7Ff36, and are not treated as today’s attack transactions.
Protocol / chain / asset: Unnamed vault on Base. CertiK and ExVul agree on the proxy address. Asset path is aBaswstETH borrowed, then redeemed for wstETH through Aave. Aave’s pool proxy appears as the withdraw target on the recipient page. This brief does not have an Aave statement that the pool itself was the bug. No protocol name has been published by PeckShield or CertiK.
Loss: Desk figure is about 1,783 wstETH, about $6 million. ExVul’s count is 1,783.067 aBaswstETH, about $6.0 million. The earlier Blockaid-attributed print of about $2.02 million across about four transactions is a mid-flow number, reported while the attack was still described as in progress. It is not added on top. No official loss post from a protocol team was found.
Attack type: Unconfirmed. Working descriptions are a newly deployed proxy on a vault borrow path, and a newly whitelisted contract. Authorization failure is explicitly unconfirmed by ExVul. A compromised-key theory circulating in quote posts is unverified. Not scored as an Aave core bug.
Explorer URLs: Recipient https://basescan.org/address/0x0B5126e1bc27C0de77e02e97945760A674EdB034. Vault proxy https://basescan.org/address/0xD1895f2019c2152FC2b9022D57f19198c4CFCABC. Loot contract https://basescan.org/address/0xcdFE91301356da873562EF513828a60dba1F569d. Loot calls https://basescan.org/tx/0xf1c9448c615122423c5f21aad2f690e76dfe7b9e9bfc320b1d36ef79a7a9cd7e, https://basescan.org/tx/0xfc4bba1eb305270e6e137fb3e9e02706c088c025d80ade224fd72d37f9e0cfb2, https://basescan.org/tx/0x57a49136a5a5dbbb06ba03a3d76c85d59f6f6ae5547445e7d0ee4cbf3053d375, https://basescan.org/tx/0x8e434d444bdeace44308717072026a7487ec7792befa0d1a9bbd01bcfe467db7. Aave withdraw https://basescan.org/tx/0x557bfd0e8530fd3e089748ccaabaa7837877f7578b13a377008474f2e367ee8c. Lido wstETH token calls https://basescan.org/tx/0xe824b27ca120908d145fd071e27f43f05aff541296d76c7772c3829398cf85d2, https://basescan.org/tx/0x20fb64ee4adceee8fb3c36b2441a32b830917afc56fe7064b46f82a58f6be145.
Status: First report today. Loss figure from desks, not from a protocol post. Root cause unconfirmed. Funds no longer visible as wstETH on the recipient page this desk opened. No freeze, bounty, or recovery post found.
Sources: https://x.com/PeckShieldAlert/status/2106684818654482531, https://x.com/CertiKAlert/status/2106685511754735682, https://x.com/exvulsec/status/2106688163452436763
GoldPesa GPXHooks — Base — about $114.9K — Uniswap v4 hook delta mix
What happened: DefimonAlerts posted at 14:25 UTC on 3 Oct, labeling the loss $114,000 and the incident date 2026-10-02. The type is a logic error in GoldPesa’s Uniswap v4 hook, GPXHooks. The hook rebalances protocol-owned GPX/USDC liquidity inside beforeSwap, and any swap can trigger that path once an hour has passed. reBalance() calls PositionManager.modifyLiquiditiesWithoutUnlock with BURN_POSITION and TAKE_PAIR. TAKE_PAIR collects the PositionManager’s full net credit, and that delta is shared by every caller inside the same PoolManager unlock. Defimon’s sequence: the attacker borrowed 175,000 USDC from Morpho, minted a WETH/USDC position through the PositionManager without paying, leaving about 115,000 USDC of debt on the PositionManager, then swapped on the GPX pool to trigger the rebalance. The hook burned its position for 148,900 USDC, but TAKE_PAIR netted that against the attacker’s debt, so the hook received 33,900 USDC. The attacker then burned its own position for 115,000 USDC, repaid the loan, swapped the profit to USDT, and bridged toward Solana and then BSC.
SlowMist’s 16:06 UTC alert is the same mechanism with ledger figures. reBalance() runs liquidity operations through the shared, flash-accounted PositionManager inside an attacker-controlled PoolManager unlock without checking that the PositionManager’s GPX/USDC deltas are zero. An unsettled MINT_POSITION left a −114,999.999187 USDC delta. The hook’s burn earned +148,868.602189 USDC, TAKE_PAIR could withdraw only the net, 33,868.603002 USDC, and burning the attacker position cleared the phantom debt and took 114,999.999186 USDC out of the PoolManager. SlowMist scores the loss at about $114,900. Attacker 0x4a5FD2e9357cC87DF4cD6A1808174DBc8646899F. Victim and vulnerable contract are both given as 0x4519e2b040ff1B64fa03aBe2AeF0BC99D7CcEaA8. BaseScan shows that address as verified GPXHooks, compiler 0.8.30, described in source as GoldPesa’s Uniswap v4 hook for the GPX-USDC pool. The attacker page shows activity about 45 to 46 hours before this brief’s cutoff, consistent with a 2 Oct execution and a 3 Oct first report. Visible rows include contract creation 0x5a3593d5d574d814b79ce7d44fc1592c1f69cba31c2cdd32f200316122bc37ef, follow-on calls 0x5c1febd5047c2a15c37988b6abd5c8b984236dddf6fd24eed96b0f43951ad2c9 and 0xa7910f17481af4352c62b77ab449a4bc35601b4960437ef7d58216f04b57f634 to 0x3d69591a…59Cce4e86, and a transfer 0x592113e005edcc28755a3219f0ebddfbb82a610f8b33d60b2c3e60c5729ebcd8 to bridged USDT 0xfde4C96c…. Token amounts were not printed on those rows. A reply under SlowMist timed an exploit transaction to 13:05 UTC on 2 Oct and a later Rango exit of about 96,388.99 USDT. That reply is not a desk alert and is not used as the loss figure. Defimon’s own transaction link was a short URL and is not expanded into a hash here.
Protocol / chain / asset: GoldPesa GPXHooks on Base. Asset extracted is USDC from protocol-owned liquidity, then swapped to USDT on the Defimon path. Uniswap v4 is the hook host. This is not scored as a Uniswap core bug. The flaw described is missing delta isolation on a shared PositionManager inside the hook’s rebalance.
Loss: SlowMist about $114,900, matching 114,999.999186 USDC. Defimon $114,000. Card uses the SlowMist print. Gross burn of 148,900 USDC is not attacker profit. The hook kept 33,868 USDC of its own burn credit in the SlowMist ledger.
Attack type: Logic error. Shared flash-accounting delta, unsettled mint, hook rebalance used as the payer. Not a key compromise in the desk write-ups.
Explorer URLs: GPXHooks https://basescan.org/address/0x4519e2b040ff1B64fa03aBe2AeF0BC99D7CcEaA8. Attacker https://basescan.org/address/0x4a5FD2e9357cC87DF4cD6A1808174DBc8646899F. Attacker rows https://basescan.org/tx/0x5a3593d5d574d814b79ce7d44fc1592c1f69cba31c2cdd32f200316122bc37ef, https://basescan.org/tx/0x592113e005edcc28755a3219f0ebddfbb82a610f8b33d60b2c3e60c5729ebcd8, https://basescan.org/tx/0xa7910f17481af4352c62b77ab449a4bc35601b4960437ef7d58216f04b57f634.
Status: First public desk report in this window, execution dated 2 Oct by Defimon. No GoldPesa response found. Laundering path to Solana and BSC is Defimon’s description. The Rango split in a reply is unconfirmed.
Sources: https://x.com/DefimonAlerts/status/2106390298469318702, https://x.com/SlowMist_Team/status/2106415554492059872
MALT — about $72K — swap counts treasury DAI as caller input — chain not confirmed here
What happened: SlowMist posted at 16:18 UTC on 3 Oct. Loss about $72,000. The cited function is swap(uint256,uint256,address). It records the caller’s input and pre-swap reserves, then calls an external rebalanceHook before transferring the requested output. The hook withdraws DAI from the Capital Source and deposits it into the same pool. The swap then checks its invariant against the pool’s final balances and treats that protocol-funded DAI as if the caller had supplied it. SlowMist’s conclusion is that the function does not isolate caller-funded input from hook-funded rebalancing capital, so a negligible input can trigger a treasury injection and a disproportionate MALT withdrawal. Attacker 0x8F103B6A0aD705bcE6357842A5fefEB49e8D83Ef. Victim 0xF0d314849A3Bc9270a79110F25dBA2c8325A2AAC. Vulnerable contract 0xfe6C096a2871337d4f6F7DD04Ebda733E94D7A13. The alert text includes a transaction link. This desk did not expand that short URL, and the hash is not restated.
Protocol / chain / asset: MALT. SlowMist did not name a chain in the alert text read for this brief. The vulnerable-contract page on Ethereum returned no matching transactions and no ETH balance. A token-holding note on that page pointed at DAI on Polygon, which is not enough to assign the incident. Chain stays unconfirmed. Asset path in the write-up is DAI from the Capital Source, extracted as excess MALT.
Loss: SlowMist about $72,000. No second desk print in this window. Not independently marked to a token table here.
Attack type: Accounting isolation failure on a swap that calls an external rebalance hook before the invariant check. Not described as a key compromise.
Explorer URLs: Vulnerable contract page opened, no matching Ethereum transactions: https://etherscan.io/address/0xfe6C096a2871337d4f6F7DD04Ebda733E94D7A13. Attacker and victim addresses are from the alert and were not re-opened on a confirmed chain.
Status: First report in this window. Chain unconfirmed. Transaction hash not verified. No project response found.
Sources: https://x.com/SlowMist_Team/status/2106418632041668784
Also noted
- UPDATE — FlashLoopAdapter: The owners’ 10 percent bounty, 11.41 ETH retained and 102.69 ETH due back before 18:00 UTC on 3 Oct, has now passed. No return transaction was posted by SlowMist, DefimonAlerts, or Aave in this slice. The 114.09 ETH from 1 Oct stays outstanding and is not added to today’s card.
- UPDATE — NEAR Intents: The 48-hour window Alex Shevchenko posted at 00:18 UTC on 2 Oct closed near 00:18 UTC on 4 Oct. No new operator post, no new receipt, and no change to yesterday’s return claim in this sweep. Not re-scored.
- DefimonAlerts: Other in-window posts are on-chain message relays, including a Circle-employment freeze claim at 09:12 UTC on 3 Oct and a YAYO buyback note. Employment claim unconfirmed. Not scored.
- GoPlusSecurity: Visible post is a Blast locked-LP advisory ahead of 26 Oct, not a new drain hash.
- Lookonchain, ZachXBT: Visible posts are token accumulation and a UPay reply thread. No new exploit hash.
- Phalcon_xyz, BlockSecTeam, CyversAlerts, Immunefi, rekt.news: No separate first-report exploit in the keyword sweep for this window.
Sources & references
- https://x.com/PeckShieldAlert/status/2106684818654482531
- https://x.com/CertiKAlert/status/2106685511754735682
- https://x.com/exvulsec/status/2106688163452436763
- https://x.com/DefimonAlerts/status/2106390298469318702
- https://x.com/SlowMist_Team/status/2106415554492059872
- https://x.com/SlowMist_Team/status/2106418632041668784
- https://x.com/DefimonAlerts/status/2106311377203630118
- https://basescan.org/address/0x0B5126e1bc27C0de77e02e97945760A674EdB034
- https://basescan.org/address/0xD1895f2019c2152FC2b9022D57f19198c4CFCABC
- https://basescan.org/address/0xcdFE91301356da873562EF513828a60dba1F569d
- https://basescan.org/address/0x4519e2b040ff1B64fa03aBe2AeF0BC99D7CcEaA8
- https://basescan.org/address/0x4a5FD2e9357cC87DF4cD6A1808174DBc8646899F
- https://basescan.org/tx/0x557bfd0e8530fd3e089748ccaabaa7837877f7578b13a377008474f2e367ee8c
- https://etherscan.io/address/0xfe6C096a2871337d4f6F7DD04Ebda733E94D7A13
Editor note
Three first reports, one of them still open on cause. The $6 million Base line is a desk consensus on size and a disagreement, or a silence, on whether the vault whitelist, a new proxy, or a key was the failure. GoldPesa is the cleanest write-up in the slice: shared PositionManager delta, hook paid the unsettled mint. MALT is scored on SlowMist’s number only, with chain and hash left blank rather than guessed. FlashLoop’s bounty clock expired without a confirmed return. No hashes were filled in for short links this desk did not open.
Read more
Web3 Daily Exploits — 3 Oct 2026: NEAR Intents $3.8M Returned
Quiet first-report window. NEAR Intents GM Alex Shevchenko said the $3.8M Omni exploit funds were sent back in full and the investigation is stopping. A labeled exploiter sent a return message on BNB Chain; the published Bitcoin address holds 34.589 BTC. FlashLoop’s 114.09 ETH bounty is still open. Card new live loss is ~$0.
Web3 Daily Exploits — 2 Oct 2026: NEAR Intents $3.8M, FlashLoop $305K
NEAR Intents halted swaps after a bug in Omni deposit and withdrawal infrastructure drained about $3.8M from a BNB Chain hot wallet. A separate Ethereum incident spoofed FlashLoopAdapter Safe checks and left an attacker with about 114.09 ETH. Card live-loss is ~$4.1M across two incidents.
Web3 Daily Exploits — 1 Oct 2026: MetaMask Validator Exit
MetaMask disclosed an infrastructure incident and began exiting affected non-custodial staking validators. Lido said the last exits are expected by 7 Oct, with re-entry up to about 45 days. Researcher Kaden scored diverted block rewards at about 0.36 ETH to a Tornado-funded fee recipient. No wallet-principal loss confirmed.
Web3 Daily Exploits — 30 Sep 2026: MCN $93K, MUS $37K
First-report this window: SlowMist flagged MCN Labs LPBonus for ~$92.6k via inconsistent MSN reserve accounting, and MUSystem for ~$36.9k via a first-deposit bonus double-count. Bitget published SlowMist and Mandiant progress reports naming a third-party zero-day foothold from 31 Aug. Limit Break victim mail continued.