Web3 Daily Exploits — 2 Oct 2026: NEAR Intents $3.8M, FlashLoop $305K
NEAR Intents halted swaps after a bug in Omni deposit and withdrawal infrastructure drained about $3.8M from a BNB Chain hot wallet. A separate Ethereum incident spoofed FlashLoopAdapter Safe checks and left an attacker with about 114.09 ETH. Card live-loss is ~$4.1M across two incidents.
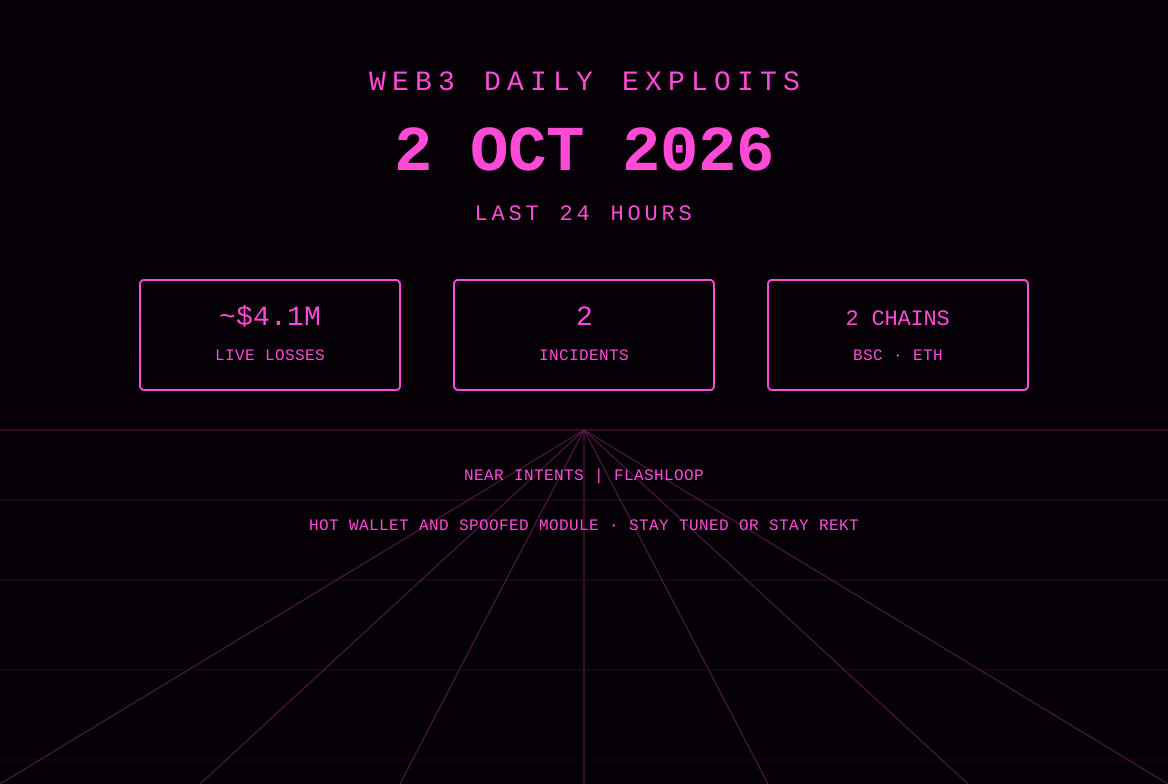
The 2 Oct America/Panama window has two first-report incidents, and they do not share a root cause. NEAR Intents posted at 12:53 UTC on 1 Oct that services had been stopped after a bug in the Omni deposit and withdrawal infrastructure and its interaction with the NEAR Intents smart contract. The team’s preliminary figure is about $3.8 million. It said those funds will be compensated in full, that the contract-side vulnerability has been patched, and that the case has been reported to law enforcement. PeckShieldAlert, citing ZachXBT, scored the BNB Chain hot-wallet outflows at $3.865 million and said the funds moved to KuCoin and were bridged toward Bitcoin. GoPlusSecurity scored about $3.87 million and described an early assessment of a withdrawal-authorization bypass. NEAR Protocol mainnet contracts are not the reported failure point.
The second incident is smaller and entirely on Ethereum. DefimonAlerts flagged FlashLoopAdapter, a third-party Safe module used to open and close leveraged Aave v3 loops, at 15:08:57 UTC on 1 Oct, with a $305,000 loss. SlowMist published the access-control write-up at 02:59 UTC on 2 Oct and scored the retained amount at about 114.09 ETH. Aave founder Stani Kulechov said the affected contract is a third-party adapter built on top of Aave and that Aave v3 itself had zero effect. SlowMist agreed. This card adds the official preliminary $3.8 million to Defimon’s $305,000 and rounds to ~$4.1 million, two incidents, two chains (BSC and ETH). The compensation pledge is not treated as a completed return. Bitcoin is a reported destination of laundering, not a second exploit chain, and is not counted in the chain box.
NEAR Intents / Omni — BNB Chain — hot-wallet drain — ~$3.8M preliminary
What happened: NEAR Intents, the intent-based swap product associated with HOT Bridge and near.com, said services were stopped after a security incident detected earlier on 1 Oct. The stated cause is a bug in the Omni deposit and withdrawal infrastructure where it interacts with the NEAR Intents smart contract. The post does not name the function, does not publish a transaction list, and does not publish a token table. It does say the contract-side vulnerability has been patched, that NEAR Intents and near.com were expected to resume within about one hour, and that deposits and withdrawals on eleven networks would stay unavailable for about twelve further hours while Omni-side fixes finished. Those networks were listed as BSC, Polygon, TON, Optimism, Avalanche, Stellar, Monad, LayerX, Adi, Scroll, and Plasma. Users holding assets from those chains inside NEAR Intents, including in HOT wallet or on near.com, were told they would be able to swap into other assets once the product was back. A detailed report was promised for the following days. This brief did not find a follow-up operator post with a final USD total or a completed repayment receipt.
Security desks filled in the on-chain side. PeckShieldAlert posted at 15:08 UTC on 1 Oct that ZachXBT had reported Near Intents exploited for $3.865 million after the BSC hot wallet saw multiple irregular outflows, that the exploiter transferred stolen funds to KuCoin and bridged them to BTC, and that the exploiter address had interacted with an address labeled North Korea / Lazarus Group, printed only as the prefix 0x098B7…E2f96. Phalcon_xyz quoted the operator post and described a drain from a BNB Chain hot wallet, routing through KuCoin, and a bridge to Bitcoin, plus the compensation plan. GoPlusSecurity, at 22:20 UTC on 1 Oct, scored the HOT Bridge treasury on BSC at about $3.87 million, named a victim address and an attacker address, and said the early assessment points to a withdrawal-authorization bypass. GoPlus also said the exploit was isolated to NEAR Intents and the Omni / HOT Bridge deposit and withdrawal stack, not NEAR Protocol mainnet contracts and not an L1 compromise. It repeated the Lazarus-labeled interaction as a ZachXBT follow-up and explicitly said NEAR Intents has not confirmed attribution and that DPRK ties remain unconfirmed.
Protocol / chain / asset: NEAR Intents and the Omni / HOT Bridge deposit and withdrawal path. The scored outflow is on BNB Chain, from a hot wallet GoPlus identified as the HOT Bridge treasury. Asset in the secondary reconstructions is BSC-USD / USDT. NEAR Protocol L1 is not the reported compromised system. The pause list covers additional networks; those pauses are operational containment, not separate confirmed drains.
Loss: Operator preliminary figure about $3.8 million, to be compensated in full. PeckShieldAlert / ZachXBT figure $3.865 million. GoPlusSecurity about $3.87 million. This card uses the operator preliminary $3.8 million. Compensation is a pledge in this window, not a confirmed on-chain return, so the amount stays in live loss. No operator token-by-token table was available.
Attack type: Operator description is a bug in Omni deposit and withdrawal infrastructure interacting with the NEAR Intents smart contract. GoPlus’s early assessment is a withdrawal-authorization bypass. Not described as an L1 key compromise. Laundering path reported by PeckShieldAlert, Phalcon, and GoPlus is a fast route through KuCoin and a bridge toward Bitcoin. That path is desk reporting, not an operator-published trace.
Explorer URLs: GoPlus victim / HOT Bridge treasury on BNB Chain https://bscscan.com/address/0x233c5370CCfb3cD7409d9A3fb98ab94dE94Cb4Cd. GoPlus attacker https://bscscan.com/address/0x09fd1f5d9f185067a92493e43aa259ea4ab3ad37. No operator-published transaction hash was in the 12:53 UTC post. A secondary write-up used a different attacker prefix (0x89fd…); this brief does not adopt that address because it was not in the GoPlus or PeckShield posts used here.
Status: Confirmed incident by the operator. Contract-side patch claimed. Omni-side fix described as still underway at the time of the post. Full compensation promised, not shown as settled. Law enforcement and analytics partners named without a case number. DPRK / Lazarus attribution unconfirmed by NEAR Intents. Detailed public report still outstanding.
Sources: https://x.com/near_intents/status/2105642219357241796, https://x.com/PeckShieldAlert/status/2105676117202067944, https://x.com/Phalcon_xyz/status/2105680009687957909, https://x.com/GoPlusSecurity/status/2105785045701267483
FlashLoopAdapter — Ethereum — spoofed Safe module — ~114.09 ETH
What happened: FlashLoopAdapter is a custom Safe module that opens and closes leveraged Aave v3 loops for Safes that enable it. DefimonAlerts, at 16:25 UTC on 1 Oct, said open() and close() trust any msg.sender that answers isModuleEnabled() = true, so a fake Safe passes. The callback checks also pass because the attacker contract is the flash-loan provider. _swap() then makes a raw call to a caller-supplied swapRouter with arbitrary swapCalldata. The attacker set the router to a victim Safe and the calldata to execTransactionFromModule. Because the call came from an enabled module, the Safe ran it. Using a Morpho WETH flash loan, the attacker repaid one Safe’s Aave debt and withdrew collateral to the attacker path, then pulled a smaller weETH balance from a second Safe. Both Safes share the same single owner. Defimon stated the adapter is a custom contract built on top of Aave and that Aave v3 itself is not affected. Detection time in that post is 15:08:57 UTC.
SlowMist’s 02:59 UTC alert on 2 Oct matches that path. It says access control on open() and close() only checks ISafe(msg.sender).isModuleEnabled(address(this)), which a fake Safe that always returns true can spoof. _swap() then executes with an attacker-controlled router and calldata. With the adapter enabled on the victim Safes, the attacker set router to the victim Safe and data to execTransactionFromModule, then drained weETH and Aave collateral. SlowMist scored about 114.09 ETH stolen and about 1,300 WETH of debt repaid to unlock collateral. At 05:27 UTC Stani Kulechov wrote that this is not an Aave v3 contract, that it is a third-party external adapter built on top of Aave, and that there was zero effect on Aave v3. SlowMist quoted that post at 06:33 UTC and restated that Aave V3 contracts are not affected.
The transaction the Safe owners cited in a DefimonAlerts on-chain relay, 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4, is a successful Ethereum transaction in block 26098264 at 15:08:47 UTC on 1 Oct. Etherscan shows it from SlowMist’s attacker EOA 0x42c2633438609881c8fBAb82414eb9A0c45F9353 to 0xF09168963ac7b31917A02Aa82fA9Cd667F4B67ff. The method line is a burn of 1,306.48 variableDebtEthWETH and a withdraw of 1,306.48 weETH. Token lines show 1,335.2558 WETH sent to Aave Ethereum WETH v3, 1,306.4823 weETH leaving Aave aEthweETH toward the attacker contract, and 6.426087 weETH moving from the second Safe 0xE3b23E47dF7cD85876aC6cB05BDb9d7cd5b28520. A later internal transfer moves 114.096151469674448809 ETH from Wrapped Ether through the attacker contract to the attacker EOA. Etherscan’s page-load valuation of that ETH was about $307,813. The gross weETH withdrawal is displayed near $3.90 million. That gross figure is collateral movement after debt repayment, not attacker profit. Defimon’s $305,000 and SlowMist’s 114.09 ETH are the net figures this brief scores. The owners’ relay offers a 10 percent whitehat bounty: keep 11.41 ETH and return 102.69 ETH to 0x329c54289Ff5D6B7b7daE13592C6B1EDA1543eD4 before 18:00 UTC on 3 Oct 2026. No return was confirmed in this window.
Protocol / chain / asset: Ethereum. Vulnerable module 0x16bb8b912da187870c23ec6756bb3fad061283d8. Victim Safes 0xcfedf95a3653a128dfc2e4288758a1a1850d169f and 0xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520. Assets are weETH collateral and WETH debt on Aave v3, with the retained balance in ETH after swaps through the attacker path. Aave v3 core and Safe core are not the reported bug. Morpho is the flash-loan source in the Defimon write-up, not the victim protocol.
Loss: About 114.09 ETH retained, per SlowMist and the transaction’s 114.096 ETH transfer to the attacker EOA. Defimon’s dollar print is $305,000. Etherscan displayed about $307,813 on the retained ETH at page load. Card uses ~$305K. The 1,306.48 weETH withdraw is gross collateral, not the loss.
Attack type: Access-control spoof on a Safe module. A fake Safe returns true for isModuleEnabled, then attacker-controlled router and calldata become execTransactionFromModule against the real Safes that had enabled the adapter. Not a stolen owner key, and not an Aave pool insolvency.
Explorer URLs: Attack transaction https://etherscan.io/tx/0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4. Attacker EOA https://etherscan.io/address/0x42c2633438609881c8fBAb82414eb9A0c45F9353. Vulnerable module https://etherscan.io/address/0x16bb8b912da187870c23ec6756bb3fad061283d8. Victim Safe 1 https://etherscan.io/address/0xcfedf95a3653a128dfc2e4288758a1a1850d169f. Victim Safe 2 https://etherscan.io/address/0xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520. Attacker contract called by the transaction https://etherscan.io/address/0xF09168963ac7b31917A02Aa82fA9Cd667F4B67ff.
Status: Confirmed by DefimonAlerts and SlowMist, and consistent with the cited transaction. Aave and SlowMist both say Aave v3 core is unaffected. Owner bounty open until 18:00 UTC on 3 Oct 2026. No confirmed return. No official adapter post-mortem beyond the two desk alerts.
Sources: https://x.com/DefimonAlerts/status/2105695635647144370, https://x.com/SlowMist_Team/status/2105855276536725599, https://x.com/StaniKulechov/status/2105892291638436078, https://x.com/SlowMist_Team/status/2105909100257423712, https://x.com/DefimonAlerts/status/2105765575766990932
Also noted
- CertiK September dashboard, not a new drain: CertiKAlert posted at 10:59 UTC on 2 Oct that September 2026 recorded about $772.4 million in losses, the second-highest month in its last three years after February 2025. The same thread put Q3 losses at about $1.27 billion, up 54.4 percent versus Q2, on 249 incidents, and year-to-date losses at about $2.69 billion. PeckShieldAlert’s 1 Oct leaderboard, already noted on yesterday’s brief, was $766.49 million across 55 major hacks. The desks do not share an incident set. Neither figure is added to this card.
- Owner and third-party recovery notes: Besides the FlashLoop bounty above, DefimonAlerts relayed an on-chain message asking for a return of 0.366 ETH to
0x2E1e6EE0D755afB85304F2a51aAc7D130B5b6DA4, with a 20 percent keep, deadline 4 Oct, and a trace to hub0xB7A57…a7D87. A separate Base message asks for a USDC refund and cites https://basescan.org/tx/0xfde15a9e7a2f935d919be63c128dc201b4934ac56002ed19760beb0a3b1f1665. These are correspondence, not new protocol RCAs, and they are not scored. - SlowMist_Team: The in-window TI alert is the FlashLoop note above. A second post amplified a ChangeNOW write-up on Punycode phishing. That is awareness, not a new loss hash.
- Phalcon_xyz, GoPlusSecurity, PeckShieldAlert: In-window exploit posts in this sweep were the NEAR Intents notes above. PeckShieldAlert’s other visible post was the September leaderboard already carried yesterday.
- CertiKAlert, BlockSecTeam, CyversAlerts, Lookonchain, ZachXBT, Immunefi, rekt.news: CertiKAlert’s in-window thread is the September dashboard, not a fresh exploit hash. Immunefi’s visible posts were short replies, not an incident page. No separate first-report from BlockSecTeam, CyversAlerts, Lookonchain, or rekt.news turned up in the keyword sweep used here. ZachXBT is cited by PeckShieldAlert on the NEAR Intents flow; this brief did not retrieve a standalone ZachXBT post in that sweep.
- MetaMask staking exits: No new operator loss print in this slice. Yesterday’s researcher estimate of about 0.36 ETH in diverted block rewards remains unconfirmed by MetaMask and is not re-scored.
Sources & references
- https://x.com/near_intents/status/2105642219357241796
- https://x.com/PeckShieldAlert/status/2105676117202067944
- https://x.com/Phalcon_xyz/status/2105680009687957909
- https://x.com/GoPlusSecurity/status/2105785045701267483
- https://x.com/DefimonAlerts/status/2105695635647144370
- https://x.com/SlowMist_Team/status/2105855276536725599
- https://x.com/StaniKulechov/status/2105892291638436078
- https://x.com/SlowMist_Team/status/2105909100257423712
- https://x.com/DefimonAlerts/status/2105765575766990932
- https://x.com/DefimonAlerts/status/2105980656744591408
- https://x.com/CertiKAlert/status/2105976008201400320
- https://etherscan.io/tx/0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4
- https://etherscan.io/address/0x42c2633438609881c8fBAb82414eb9A0c45F9353
- https://etherscan.io/address/0x16bb8b912da187870c23ec6756bb3fad061283d8
- https://etherscan.io/address/0xcfedf95a3653a128dfc2e4288758a1a1850d169f
- https://etherscan.io/address/0xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520
- https://bscscan.com/address/0x233c5370CCfb3cD7409d9A3fb98ab94dE94Cb4Cd
- https://bscscan.com/address/0x09fd1f5d9f185067a92493e43aa259ea4ab3ad37
Editor note: card live-loss is the operator preliminary $3.8 million plus Defimon’s $305,000, rounded to ~$4.1 million. Compensation on NEAR Intents is pledged, not booked as returned. Gross weETH movement on the FlashLoop transaction is not attacker profit. Lazarus labeling is unverified.
Read more
Web3 Daily Exploits — 1 Oct 2026: MetaMask Validator Exit
MetaMask disclosed an infrastructure incident and began exiting affected non-custodial staking validators. Lido said the last exits are expected by 7 Oct, with re-entry up to about 45 days. Researcher Kaden scored diverted block rewards at about 0.36 ETH to a Tornado-funded fee recipient. No wallet-principal loss confirmed.
Web3 Daily Exploits — 30 Sep 2026: MCN $93K, MUS $37K
First-report this window: SlowMist flagged MCN Labs LPBonus for ~$92.6k via inconsistent MSN reserve accounting, and MUSystem for ~$36.9k via a first-deposit bonus double-count. Bitget published SlowMist and Mandiant progress reports naming a third-party zero-day foothold from 31 Aug. Limit Break victim mail continued.
Web3 Daily Exploits — 29 Sep 2026: Reality.eth XSS, $0 Drain
First-report this window: DefimonAlerts flagged a stored XSS in the reality.eth question renderer; the project confirmed a 2022-era reality-eth-lib bug, shipped v3.4.32, and reported no confirmed drain. Bitget reopened ETH rails with a net inflow and thanked NEAR Intents SHIELD for a $503k mid-swap freeze. Limit Break whitehat mail continued.
Web3 Daily Exploits — 28 Sep 2026: Bitget Third-Party Creds RCA
Quiet first-report window. Bitget published its first operator RCA: a third-party security product yielded internal credentials, then fraudulent withdrawal commands bypassed risk controls. BTC withdrawals reopened. ZachXBT named five laundering aliases. DYORSWAP posted official 766.25 ETH / 1,335-address counts and a recovery address.