Web3 Daily Exploits — 1 Oct 2026: MetaMask Validator Exit
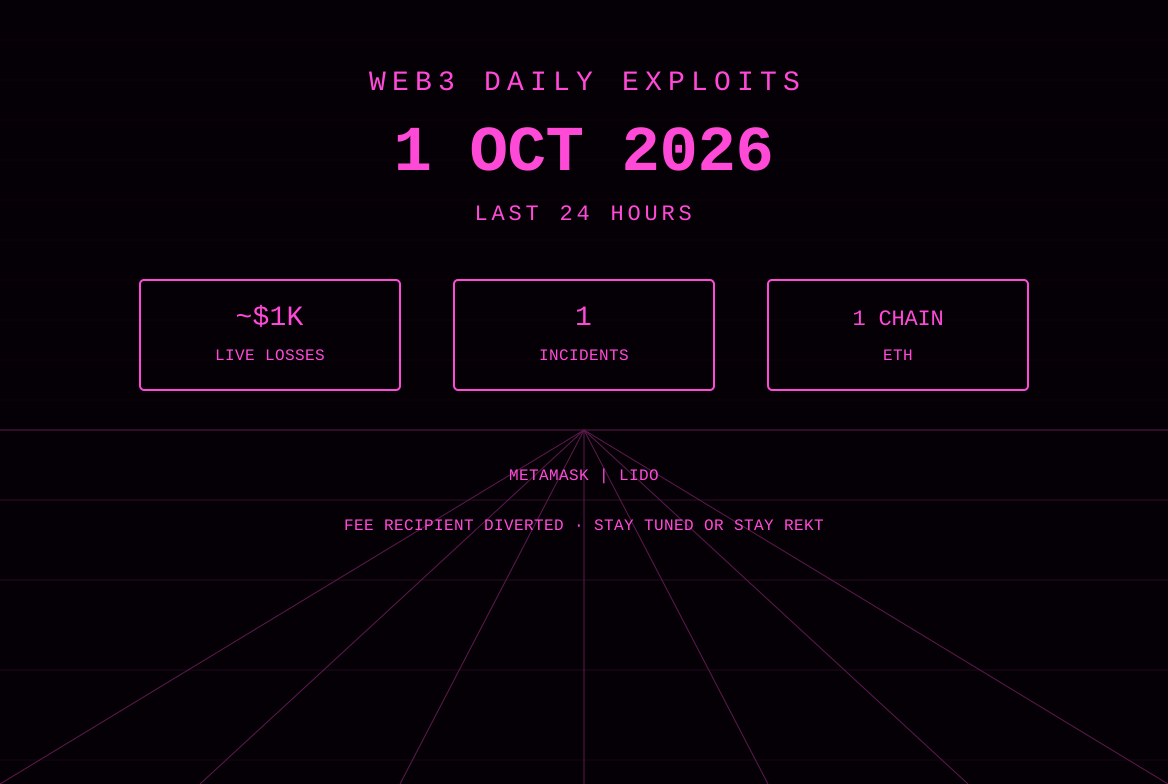
MetaMask disclosed an infrastructure incident and began exiting affected non-custodial staking validators. Lido said the last exits are expected by 7 Oct, with re-entry up to about 45 days. Researcher Kaden scored diverted block rewards at about 0.36 ETH to a Tornado-funded fee recipient. No wallet-principal loss confirmed.
The 1 Oct America/Panama window has one first-report incident, and it is an operator-infrastructure event rather than a new smart-contract drain. MetaMask posted at 23:38 UTC on 30 Sep that it was responding to a security incident affecting part of its infrastructure, that it had identified no immediate threat to MetaMask wallets, and that it was proactively exiting affected validators inside its non-custodial staking operations. A follow-up at 11:17 UTC on 1 Oct said the investigation was continuing, that partners had taken the precautionary exit step, and that there was still no indication MetaMask wallets or customer funds had been affected. Lido’s node-operator disclosure, posted by KimonSh, frames the same event as an infrastructure compromise under investigation and sets an operational clock: relevant validators have begun exiting, the last are expected to be exited but not fully withdrawn by the end of 7 Oct 2026, and the exit-withdrawal-re-entry cycle is estimated at up to about 45 days because of the entry queue.
The only dollar figure attached to stolen value in this window is not an operator total. Ethereum security researcher Kaden (@0xKaden) wrote that 19 MetaMask validators had won block rewards and that 18 of those rewards were paid to a Tornado-funded account, 0x98B9231de84334c1d48BA0b72CF13f92484924A3, instead of the correct fee recipient, for about 0.36 ETH. A reply on that thread reconstructed the same address as a fresh EOA that received 0.097787 ETH from the Tornado Cash 0.1 ETH pool at 10:27:23 UTC on 30 Sep, then 18 Titan Relay builder-fee payouts summing to about 0.36 ETH, starting in block 26090216 at 12:12:23 UTC. MetaMask has not confirmed the 0.36 ETH figure, the validator counts, or the fee-recipient address. This card scores the researcher estimate only, rounded to ~$1K, one incident, one chain (Ethereum). The ~17,000 validators and ~523,000 ETH Kaden described as already exiting are precautionary exposure, not a loss, and are not added to live-loss. CertiKAlert amplified the MetaMask post. Phalcon_xyz, PeckShieldAlert, BlockSecTeam, CyversAlerts, Immunefi, and rekt.news did not publish a separate first-report drain hash in the sweep used here.
MetaMask Staking — Ethereum — validator fee-recipient diversion — ~0.36 ETH researcher estimate
What happened: MetaMask, the Consensys wallet, disclosed an ongoing infrastructure incident and began exiting affected validators in its non-custodial staking business, previously Consensys Staking. The operator posts do not name the compromised system, do not publish a root-cause path, and do not publish a loss total. The stated user-facing claim, repeated on X and on the MetaMask news page dated 30 Sep, is that there is no immediate threat to MetaMask wallets and no indication that customer funds were affected. The news page adds that staking operations are non-custodial and that MetaMask does not manage withdrawal keys for stake on behalf of clients.
Lido, where MetaMask Staking operates validators, published the operational consequence. The governance-forum note says MetaMask Staking took precautionary steps after an investigation into an infrastructure compromise, including exiting its Ethereum validators in the Lido protocol. Those exits are expected to incur foregone rewards and possible downtime penalties if validators are taken offline to reduce the risk of network penalties. Final validators are expected to be exited, but not fully withdrawn, by the end of 7 Oct 2026. Exited ETH is expected to return to the protocol gradually; Lido estimates the full exit, withdrawal, and re-entry cycle at up to about 45 days because of the extended entry queue. stETH holders are told no action is required. Lido notes an ad hoc reserve fund of over 6,750 stETH as one of the protocol-side buffers. The note does not list validator indices, fee-recipient addresses, or a stolen-ETH figure.
The on-chain reconstruction that supplies the card’s live-loss number is Kaden’s, posted at 05:28 UTC on 1 Oct in reply to MetaMask’s first update. He wrote that 19 MetaMask validators had won block rewards, that 18 of those rewards were not paid to the correct fee recipient, and that the payments went to 0x98B9231de84334c1d48BA0b72CF13f92484924A3, which he described as Tornado-funded. He scored the stolen rewards at about 0.36 ETH and wrote that the attacker likely never had the ability to withdraw staked ETH. He also wrote that, depending on how signing access was obtained, intentional slashing remained a theoretical risk. On scale, he estimated about 17,000 validators already proactively exited, about 523,000 ETH in that set, 821 potentially impacted validators not yet exited, and 3 of the exploited validators not yet exited. He marked as unknown whether the attacker could change fee recipients on the whole set. MetaMask has not confirmed those counts.
A reply from @m4rio_eth on the same thread adds a transaction-level sketch that this brief treats as third-party reconstruction, not as an operator RCA. That reply says 0x98B9231de84334c1d48BA0b72CF13f92484924A3 is a new EOA that had not sent a transaction; that at 10:27:23 UTC on 30 Sep it received 0.097787 ETH from the Tornado Cash 0.1 ETH pool via relayer reltor.eth in transaction 0xbc403e6e3cdae7a17b1dfddb5432836a7d28302a40e9001f1a4a53e135f982bc; and that it then received exactly 18 incoming builder or MEV fee payouts through a Titan Relay forwarder whose address was given only as the prefix 0xFEEEEEE4. The first of those payouts is placed in block 26090216 at 12:12:23 UTC for 0.008168 ETH. The reply says the 18 transfers add up to about 0.36 ETH and that the wallet still held the ETH. This brief does not invent the remaining 17 payout hashes. Community replies on the same thread noted that a fee recipient lives in node configuration, so consensus would still treat the blocks as valid, and asked whether the redirected blocks implied valid builder registrations on Titan. Those are hypotheses, not findings.
A later MetaMask post at 11:17 UTC on 1 Oct said the team was still investigating, had worked with partners to exit affected validators, and still had no indication that wallets or customer funds were affected. It also warned users against unsolicited messages and against sharing a Secret Recovery Phrase. CertiKAlert quoted the first MetaMask post at 02:25 UTC on 1 Oct and did not add a loss figure. Independent coverage (CoinDesk, Decrypt) repeated Kaden’s 0.36 ETH and ~17,000-validator estimates and noted that MetaMask had not confirmed them. CoinDesk linked a Lookonchain feed id that, on fetch, resolved to an unrelated Joseph Lubin ETH transfer note; this brief does not treat that feed as a MetaMask source.
Protocol / chain / asset: Ethereum consensus and execution. Operator is MetaMask Staking (ex Consensys Staking), a node operator on Lido. Asset in the researcher score is ETH block-production payments (builder or MEV fee recipient), not staked principal and not stETH. Wallet key material for self-custodial MetaMask users is not reported compromised in the operator posts.
Loss: ~0.36 ETH in diverted block rewards, per Kaden, with a matching sum in the @m4rio_eth reply. At prices cited by secondary coverage that is under $1,000. Card rounds the researcher estimate to ~$1K and labels it unverified by the operator. The ~523,000 ETH attached to exiting validators is exposure under precautionary exit, not a booked theft. Foregone staking rewards and possible downtime penalties during the exit window are operational cost, not attacker profit, and are not scored.
Attack type: Infrastructure compromise at a node operator, as described by Lido and MetaMask, with a researcher claim that fee-recipient configuration on a subset of validators was pointed at an attacker address. Not described as a smart-contract bug in Lido, a withdrawal-key theft, or a MetaMask wallet-seed compromise. Intentional slashing is a stated residual risk if signing access was obtained, not a confirmed slash event.
Explorer URLs: Alleged fee-recipient EOA https://etherscan.io/address/0x98B9231de84334c1d48BA0b72CF13f92484924A3. Tornado-funding transaction cited in the thread reply https://etherscan.io/tx/0xbc403e6e3cdae7a17b1dfddb5432836a7d28302a40e9001f1a4a53e135f982bc. First cited payout block https://etherscan.io/block/26090216. No operator-published attacker transaction list was available for this brief.
Status: Confirmed incident by the operator and by Lido. Loss amount, fee-recipient change, and validator counts unconfirmed by MetaMask. Exits in progress; last exit expected by end of 7 Oct 2026, full re-entry cycle estimated up to about 45 days. Investigation described as ongoing. stETH holders directed to take no action.
Sources: https://x.com/MetaMask/status/2105442300335620460, https://x.com/MetaMask/status/2105618018676163063, https://metamask.io/news/user-update, https://research.lido.fi/t/security-disclosure-metamask-staking-precautionary-out-of-order-exits/11961, https://x.com/0xKaden/status/2105530184103563620, https://x.com/CertiKAlert/status/2105484301492203586
UPDATE — Limit Break payment processors / Magic Eden users — Ethereum
What happened (this window): No required-monitor post published a new official USD total. DefimonAlerts continued to relay onchain messages from people describing themselves as Magic Eden or Payment Processor V2 victims. One message cites a 1.34 WETH drain in https://etherscan.io/tx/0x6e132afc532f7ecabcf68e01c92e687f64a54a64a83a06114d598f21a1e27b3b and asks for a partial return. A separate DefimonAlerts relay asks for the return of about 0.4575 ETH to 0x9fA396721294E9E1A7acEC70f89FDF716052C38C; that message does not name a protocol and is not scored. These are recovery correspondence, not a new protocol RCA.
Loss: Not re-scored. Prior window remains the standing figure for the Payment Processor V2 cluster.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834. Victim-cited transaction https://etherscan.io/tx/0x6e132afc532f7ecabcf68e01c92e687f64a54a64a83a06114d598f21a1e27b3b.
Status: Active user-side correspondence. No new operator loss print in this slice.
Sources: https://x.com/DefimonAlerts/status/2105306055911543106, https://x.com/DefimonAlerts/status/2105588465211506922
Also noted
- September recap posts, not new drains: CertiKAlert posted that confirmed September losses were about $766.4 million, the highest month it has recorded for 2026. PeckShieldAlert posted 55 major hacks and $766.49 million for September, up about 462 percent from its August print of $136.3 million, with Bitget (~$387 million) and Liquid Network (~$320 million, of which $285 million returned) as the top two. GoPlusSecurity posted 39 major incidents and about $793,043,716 for September. The three desks do not use the same incident set. None of those posts is a first-report hash for 1 Oct, and none is added to this card.
- SlowMist_Team: In-window visible posts were a salute on Bitget coverage already scored on 30 Sep, and a TokenPocket Asset Inheritance audit announcement. No new TI drain alert after the MCN Labs LPBonus and MUSystem notes already booked on the 30 Sep brief.
- GoPlusSecurity: Besides the September rollup, in-window posts were DeepScan nomination traffic. No protocol-drain hash.
- PeckShieldAlert: The visible in-window post was the September leaderboard, not a fresh exploit transaction.
- BlockSecTeam: The latest visible post in the sweep was the 30 Sep Bitget laundering note already carried as an UPDATE on the prior brief. No new unauthorized-transfer wave was attached.
- Phalcon_xyz, CyversAlerts, ZachXBT, Immunefi, rekt.news: No in-window first-report incident page or exploit alert turned up in the keyword sweep used for this brief. rekt.news search hits for this date were older leaderboard pages, not a 1 Oct write-up.
- Lookonchain: No exploit RCA in the keyword sweep. A CoinDesk link to lookonchain.com/feeds/75017 resolved, on fetch, to a Joseph Lubin-linked transfer of 133,298 ETH to
0x1b3cB81E51011b549d78bf720b0d924ac763A7C2. That is a labeled wallet move, not an exploit, and it is not scored. - Bitget (~$387.5 million, already scored): No new drain hash this slice. SlowMist’s in-window activity on that cluster was amplification of coverage already in the 30 Sep brief.
Sources & references
- https://x.com/MetaMask/status/2105442300335620460
- https://x.com/MetaMask/status/2105618018676163063
- https://metamask.io/news/user-update
- https://research.lido.fi/t/security-disclosure-metamask-staking-precautionary-out-of-order-exits/11961
- https://x.com/0xKaden/status/2105530184103563620
- https://x.com/CertiKAlert/status/2105484301492203586
- https://x.com/CertiKAlert/status/2105266411358634360
- https://x.com/PeckShieldAlert/status/2105505048377848307
- https://x.com/GoPlusSecurity/status/2105455857488261340
- https://x.com/DefimonAlerts/status/2105306055911543106
- https://x.com/DefimonAlerts/status/2105588465211506922
- https://etherscan.io/address/0x98B9231de84334c1d48BA0b72CF13f92484924A3
- https://etherscan.io/tx/0xbc403e6e3cdae7a17b1dfddb5432836a7d28302a40e9001f1a4a53e135f982bc
- https://etherscan.io/block/26090216
Editor note: card live-loss is the rounded researcher estimate of diverted block rewards only. Validator ETH under precautionary exit is exposure, not theft. Operator post-mortem still outstanding.
Read more
Web3 Daily Exploits — 30 Sep 2026: MCN $93K, MUS $37K
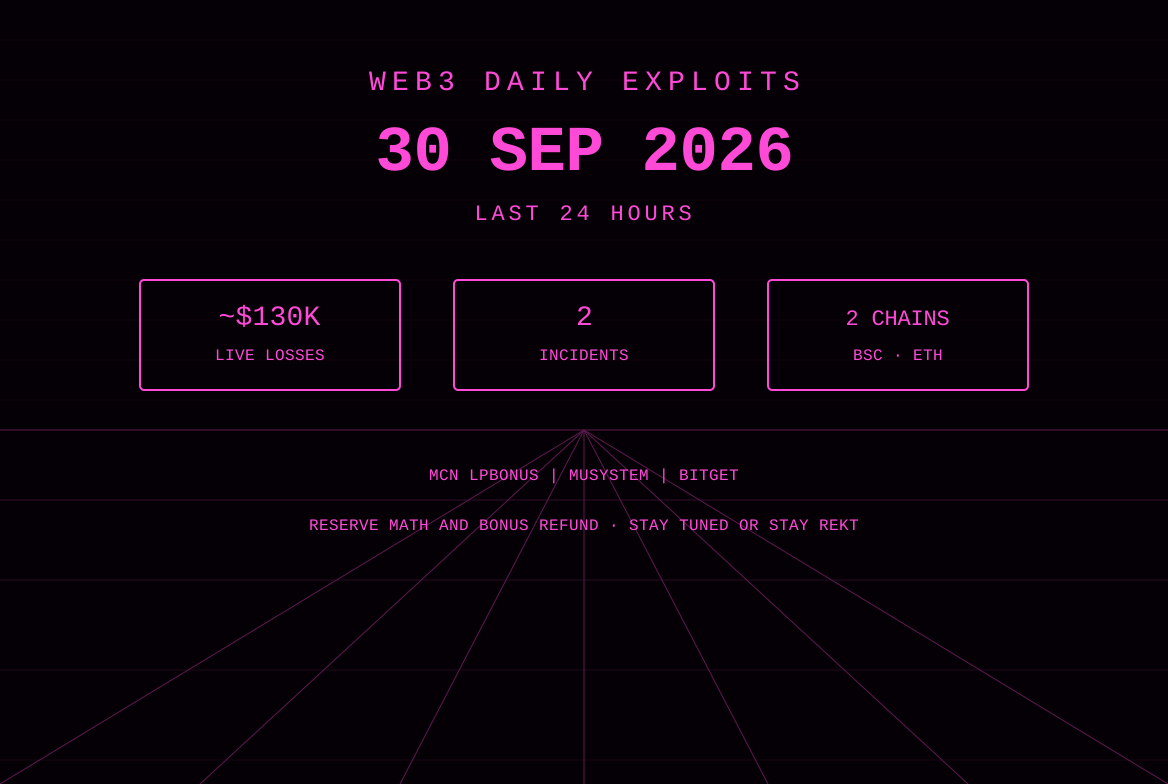
First-report this window: SlowMist flagged MCN Labs LPBonus for ~$92.6k via inconsistent MSN reserve accounting, and MUSystem for ~$36.9k via a first-deposit bonus double-count. Bitget published SlowMist and Mandiant progress reports naming a third-party zero-day foothold from 31 Aug. Limit Break victim mail continued.
Web3 Daily Exploits — 29 Sep 2026: Reality.eth XSS, $0 Drain
First-report this window: DefimonAlerts flagged a stored XSS in the reality.eth question renderer; the project confirmed a 2022-era reality-eth-lib bug, shipped v3.4.32, and reported no confirmed drain. Bitget reopened ETH rails with a net inflow and thanked NEAR Intents SHIELD for a $503k mid-swap freeze. Limit Break whitehat mail continued.
Web3 Daily Exploits — 28 Sep 2026: Bitget Third-Party Creds RCA
Quiet first-report window. Bitget published its first operator RCA: a third-party security product yielded internal credentials, then fraudulent withdrawal commands bypassed risk controls. BTC withdrawals reopened. ZachXBT named five laundering aliases. DYORSWAP posted official 766.25 ETH / 1,335-address counts and a recovery address.
Web3 Daily Exploits — 27 Sep 2026: DYORSWAP Fake GIWA Bridge
First-report this window: DYORSWAP confirmed the GIWA mainnet it had listed was a scammer-built fake chain using chain ID 9134. Community and tracker estimates put ETH-bridge losses near $2M. GIWA (Upbit L2) said official mainnet is not live. Bitget and Limit Break remain UPDATEs. Duelbits still unverified.