Web3 Daily Exploits — 30 Sep 2026: MCN $93K, MUS $37K
First-report this window: SlowMist flagged MCN Labs LPBonus for ~$92.6k via inconsistent MSN reserve accounting, and MUSystem for ~$36.9k via a first-deposit bonus double-count. Bitget published SlowMist and Mandiant progress reports naming a third-party zero-day foothold from 31 Aug. Limit Break victim mail continued.
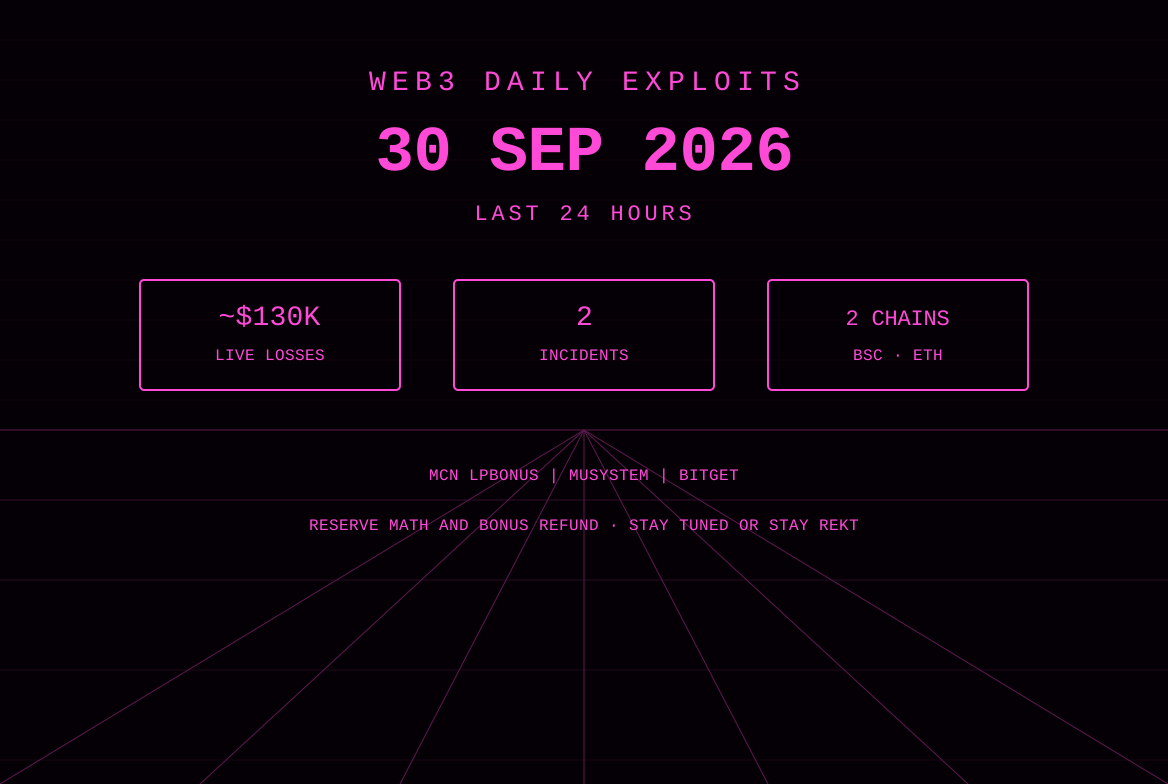
After the required-monitor sweep for this 30 Sep America/Panama window, first-report protocol-drain dollars are back on the card. SlowMist_Team published two TI alerts overnight: MCN Labs’ LPBonus contract, scored at about $92.6k after an attacker moved the MSN reserve between accrual and claim; and MUSystem, scored at about $36.9k after sixteen fresh addresses recycled a first-deposit bonus that was counted both as an immediate ETH refund and as MUS allocation. Combined first-report live-loss on this card is about $129.5k, rounded on the featured card to ~$130K across two incidents and two chains (BSC and Ethereum). CertiKAlert, Phalcon_xyz, PeckShieldAlert, and CyversAlerts published no in-window first-report smart-contract drain. PeckShieldAlert’s visible hit was a Solana meme-token price print. Lookonchain returned whale and CEX flow. Immunefi traffic was quiet on exploit keywords. rekt.news had no fresh 30 Sep incident page.
The rest of the window is UPDATE traffic on already-scored clusters. Bitget and its retained firms posted the first written forensic progress reports on the 24 Sep hot/warm-wallet theft: SlowMist described a zero-day on an unnamed third-party product as early as 31 Aug UTC+8, an employee-identity login to a second product’s management plane, a recovered custom withdrawal tool, and on-chain transfers spanning about 2 hours 52 minutes from 02:31 UTC+8 on 25 Sep. Mandiant, shared by Bitget, described unauthorized access to third-party security appliances, a web shell, lateral movement onto a production wallet job server, and access to warm and hot wallets. Neither firm named the vendors. BlockSec separately published a laundering-trace note: publicly visible freezes still under $1 million against the $387.5 million recount. Limit Break / Magic Eden Payment Processor V2 victim and whitehat mail continued through DefimonAlerts. Those UPDATE items are not added to card live-loss.
MCN Labs / LPBonus — BNB Chain — reward-accounting mismatch — ~$92.6k
What happened: SlowMist_Team posted a TI alert that the MCN Labs–related LPBonus contract used inconsistent MSN reserve values when it booked LP rewards. Accrual updated a per-share FIST index (oneshareFIST) by dividing newly acquired FIST by the MSN reserve at that moment (AddFistFee). Later, pending rewards (CalcPendingUser) multiplied that index by a user weight calculated from the reserve at withdrawal. The attacker first lowered the reserve to 89.327788899759978606 MSN during accrual, then raised it to 491.113095162589329323 MSN before calling UserRemoveLp. A newly registered LP holder then claimed 1,442,165.713011 FIST against an intervening reward increment funded by only 940,041.612768 FIST. SlowMist scored the gap at about $92,600.
FIST is the governance token of FstSwap on BNB Chain; MSN trades against FIST on PancakeSwap V2. The victim address and the vulnerable contract are the same contract in the SlowMist alert. No required-monitor desk published a primary transaction hash in plaintext; this brief does not invent one. The attacker EOA is on the record.
Protocol / chain / asset: BNB Chain. Reward token FIST, reserve token MSN, contract LPBonus associated by SlowMist with @MCNLabs. Community dashboards that printed a same-day “FastSwap ~$93k” line are treated here as a naming collision with FstSwap / FIST, not as a second incident, because no required-monitor desk attached a separate hash or a separate loss print.
Loss: ~$92,600 per SlowMist TI and the SlowMist Hacked ledger dated 2026-09-30. Card uses that figure.
Attack type: Smart-contract reward-accounting inconsistency. Reserve used at accrual is not the reserve used at claim. Not described as a reentrancy, an approval drain, or a private-key event.
Explorer URLs: Attacker https://bscscan.com/address/0xb6fff29dd2b5423a159e50877fc4af7a54e76f7a. Victim / vulnerable contract https://bscscan.com/address/0x52272524a22f941f5489c1233732797314bb054b. Same contract has no Ethereum mainnet history; FIST/MSN market structure is BNB Chain.
Status: First-reported by SlowMist on 30 Sep. No operator post from @MCNLabs was attached to the required-monitor alerts used here. Pause, patch, or recovery status unpublished in those posts.
Sources: https://x.com/SlowMist_Team/status/2105145534126358819, https://hacked.slowmist.io/
MUSystem — Ethereum — first-deposit bonus double-count — ~$36.9k
What happened: SlowMist_Team posted a second TI alert that MUSystem’s deposit() counted a first-deposit bonus in both the immediate ETH refund and the user’s MUS allocation, while withdraw() allowed same-transaction redemption without capping returned ETH to the amount deposited. Sixteen fresh addresses repeated that cycle and extracted ETH from the contract. SlowMist scored the drain at about $36,900.
The victim address and the vulnerable contract are the same Ethereum contract in the alert. Two SlowMist-linked transactions resolve on Etherscan as 0xfe28118e48c64b275b587c90da472fc13b8c3dbed9d3cded1e18c1e7a7fc0392 and 0xaa172fcaa4800b14826daed1a78c9d6dcd8f26ae45ce5f31786d55768b709ec6. The attacker EOA is on the record. No required-monitor desk published a per-address profit table; this brief does not invent one.
Protocol / chain / asset: Ethereum mainnet. Asset extracted is ETH from contract 0x9bdf81e6066d32764b7e75a1b5577237e06d9364 (labeled Mutual Uniting System / MUSystem on the explorer). Token ticker in the SlowMist post is MUS.
Loss: ~$36,900 per SlowMist TI and the SlowMist Hacked ledger dated 2026-09-30. Card uses that figure.
Attack type: Smart-contract accounting flaw in deposit bonus plus uncapped same-transaction withdraw. Not described as a flash-loan price oracle attack in the SlowMist text; a third-party reply that called it “flash loan math” is not treated as the RCA.
Explorer URLs: Attacker https://etherscan.io/address/0x1a083ADf234a8f67ad65A9B9B616853ACf5998E5. Victim / vulnerable contract https://etherscan.io/address/0x9bdf81e6066d32764b7e75a1b5577237e06d9364. Cited transactions https://etherscan.io/tx/0xfe28118e48c64b275b587c90da472fc13b8c3dbed9d3cded1e18c1e7a7fc0392, https://etherscan.io/tx/0xaa172fcaa4800b14826daed1a78c9d6dcd8f26ae45ce5f31786d55768b709ec6.
Status: First-reported by SlowMist on 30 Sep. No operator containment post was attached to the alerts used here.
Sources: https://x.com/SlowMist_Team/status/2105167166639407447, https://hacked.slowmist.io/
UPDATE — Bitget Exchange — multi-chain CEX hot/warm wallets — ~$387.5M already scored
What happened (this window): No new unauthorized-transfer wave was confirmed. The material change is written forensic progress from the two firms Bitget retained, plus a BlockSec laundering-trace note, plus operator deposit-flow language.
SlowMist posted that, as of 29 Sep, the investigation had identified malicious activity on certain third-party security products and a wallet application host, plus a highly customized withdrawal tool. Key findings in that thread, with all SlowMist dates in UTC+8: (1) malicious activity on a third-party product involving a zero-day; (2) unauthorized access to a third-party product’s management platform on 25 Sep using an internal employee identity; (3) recovery of a customized withdrawal tool built around the wallet system’s withdrawal logic; (4) on-chain activity beginning 02:31 on 25 Sep and running about 2 hours 52 minutes across multiple chains; (5) later attempts to manipulate withdrawal records and trigger additional BTC withdrawals. Independent coverage of the same progress report adds an earlier foothold: 31 Aug, a service on a node of “Product A” was hit by the zero-day, a hidden script ran under the service process, and a command read an environment variable that held a database password. Similar hidden-script activity was described on other nodes on 23 Sep and 25 Sep. Vendors remain unnamed; reports use “Product A” and “Product B.”
Bitget quoted that SlowMist thread and separately said Mandiant (Google Cloud) had shared findings on the 24 Sep incident: the attacker gained unauthorized access to certain third-party security appliances, then moved laterally into Bitget’s wallet environment and reached warm and hot wallets. Bitget wrote that those findings align with the attack path it had already published. Mandiant language circulating with that update adds a web shell on appliance B, a C2 channel, and malicious packages on a production wallet job server. Private keys were still described as not stolen. Cold wallets were still described as unaffected. Bitget posted later in the window that deposits over the prior 24 hours were about $231 million, near an August daily average of $245 million, and that 29 Sep futures volume was $9.2 billion with open interest $4.4 billion. Those are operator flow prints, not attacker outflows. A dedicated USDT-rail reopen confirmation was not in the Bitget keyword sweep used here; the prior calendar still pointed at 30 Sep 08:00 UTC for USDT on Ethereum, BSC, Solana, and Tron.
BlockSecTeam posted a fund-flow note the same morning: $387.5 million stolen, less than $1 million frozen; about $183 million swapped into ETH within hours; issuers froze about $339k–$340k; NEAR Intents blocked about $50 million in attempts but caught about $503k; THORChain “let it all through.” The accompanying BlockSec blog puts publicly visible freezes near $840k (0.2 percent of the recount), Tether and Circle combined near $340k, and a net of about $269 million routed into THORChain across 7,804 transactions. Those freeze and routing figures are not new drains and are not subtracted from the $387.5 million recount on this card.
Protocol / chain / asset: Centralized exchange custody. Prior briefs already carry the operator receiving addresses: EVM 0x770b10b273fc44fe9197d6bf20f145c2e98463ee, XRP rwNhefsz1UQEusxhCvHip3RANinWi4CTck, ZEC t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG, TRON TBWNguTTgezw9dVorX441C6nDrZpRxYwKD. Affected rails named in earlier operator posts include Ethereum, XRP Ledger, Arbitrum, Avalanche, Optimism, BSC, Base, and Tron. Third-party products remain unnamed.
Loss: Not re-scored. Operator recount remains ~$387.5 million for the original 24 Sep window. Deposit volume, issuer freezes, and the SHIELD / NEAR $503k mid-swap freeze are not new drains.
Attack type: Unchanged in outcome, more specific in path. Unauthorized hot/warm transfers through a custom withdrawal tool after a third-party appliance zero-day and lateral movement, per SlowMist and Mandiant as relayed by Bitget. Private keys not reported stolen. DPRK / TraderTraitor attribution remains unlabeled as confirmed by the operator RCA.
Explorer URLs: Arkham cluster https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac. Bitget EVM first-hop https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee.
Status: Confirmed prior incident. Written progress reports now public; vendors still unnamed. Lateral-movement reconstruction described as ongoing. User balances still described by the operator as covered by the Protection Fund.
Sources: https://x.com/SlowMist_Team/status/2105145931645743534, https://x.com/bitget/status/2105147238804537496, https://x.com/bitget/status/2105147900229783800, https://x.com/bitget/status/2105186400513540551, https://x.com/BlockSecTeam/status/2105224499352457296, https://blocksec.com/blog/bitget-hack-laundering-fund-tracing
UPDATE — Limit Break payment processors / Magic Eden users — Ethereum and ApeChain
What happened (this window): No required-monitor post published a new official USD total. DefimonAlerts continued to relay onchain messages from Payment Processor V2 victims and from parties holding front-run inventory, including a Magic Eden–linked WETH return request citing https://etherscan.io/tx/0x35e43f423b77e4f4c34ee5dd5e2dd475e46ece8f466346d561e4d0c04d964e46 and a PPV2 WETH return request citing https://etherscan.io/tx/0x49ca6c99cf555983ea1942196ed1194b2536ee723d4b0b716d1377aa71e43071. Those are recovery correspondence, not a new protocol RCA and not a new loss print.
Loss: Not re-scored. Prior window ~660 WETH (~$1.7M) plus listed NFT inventory.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834.
Status: Active user-side revoke. Redistribution of rescued inventory still in process via prior-window channels.
Sources: https://x.com/DefimonAlerts/status/2105259085050363970, https://x.com/DefimonAlerts/status/2105029373011140895
Also noted
- Required-monitor silence outside the two SlowMist TI alerts: CertiKAlert, Phalcon_xyz, PeckShieldAlert, and CyversAlerts had no in-window first-report smart-contract drain posts. PeckShieldAlert’s visible hit was
solana:98kfF7rmsg1QDUEoCqNE7g7M1FdrTt92TEp2CLzypumpdown 50 percent in 24 hours — a price print, not an exploit hash. Lookonchain returned Aster DEX trader PnL, ZEC and AAVE whale flow, Strive BTC accumulation, and a QNT founder-wallet move. - GoPlusSecurity: In-window posts were campaign and DeepScan nomination traffic with @termix_ai, not a protocol drain.
- ZachXBT: In-window posts were account-status discussion, not a new incident RCA.
- DPRK / TraderTraitor attribution on Bitget (unverified): Unchanged as a closed finding. SlowMist and Mandiant progress reports name a third-party appliance path and do not name a nation-state actor in the posts used here. Prior-window investigator language remains investigator language.
- Payy RollupV1 (~$1.83M) and DYORSWAP fake GIWA (766.25 ETH official): No new first-report hash this slice. Payy drain remains https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814. DYORSWAP recovery address remains https://etherscan.io/address/0xdf25f88aa6cde9937fdcfcf10fa349528c79dbf9.
- Apple CVE-2026-86950: SlowMist’s 29 Sep client-side advisory remains outside this card’s live-loss. No confirmed wallet theft total was attached in the posts used here.
Sources & references
- https://x.com/SlowMist_Team/status/2105145534126358819
- https://x.com/SlowMist_Team/status/2105167166639407447
- https://x.com/SlowMist_Team/status/2105145931645743534
- https://hacked.slowmist.io/
- https://x.com/bitget/status/2105147238804537496
- https://x.com/bitget/status/2105147900229783800
- https://x.com/bitget/status/2105186400513540551
- https://x.com/BlockSecTeam/status/2105224499352457296
- https://x.com/BlockSecTeam/status/2105222092644143576
- https://blocksec.com/blog/bitget-hack-laundering-fund-tracing
- https://x.com/DefimonAlerts/status/2105259085050363970
- https://x.com/DefimonAlerts/status/2105029373011140895
- https://x.com/PeckShieldAlert/status/2104774543638491356
- https://etherscan.io/tx/0xfe28118e48c64b275b587c90da472fc13b8c3dbed9d3cded1e18c1e7a7fc0392
- https://etherscan.io/tx/0xaa172fcaa4800b14826daed1a78c9d6dcd8f26ae45ce5f31786d55768b709ec6
- https://bscscan.com/address/0x52272524a22f941f5489c1233732797314bb054b
- https://etherscan.io/address/0x9bdf81e6066d32764b7e75a1b5577237e06d9364
Editor note: Card live-loss is first-report only (~$92.6k + ~$36.9k). Bitget remains an UPDATE on a prior-window $387.5 million recount. Third-party appliance names are still unpublished; this desk does not invent them. MCN Labs primary drain hash was not in the SlowMist plaintext used here.
Read more
Web3 Daily Exploits — 29 Sep 2026: Reality.eth XSS, $0 Drain
First-report this window: DefimonAlerts flagged a stored XSS in the reality.eth question renderer; the project confirmed a 2022-era reality-eth-lib bug, shipped v3.4.32, and reported no confirmed drain. Bitget reopened ETH rails with a net inflow and thanked NEAR Intents SHIELD for a $503k mid-swap freeze. Limit Break whitehat mail continued.
Web3 Daily Exploits — 28 Sep 2026: Bitget Third-Party Creds RCA
Quiet first-report window. Bitget published its first operator RCA: a third-party security product yielded internal credentials, then fraudulent withdrawal commands bypassed risk controls. BTC withdrawals reopened. ZachXBT named five laundering aliases. DYORSWAP posted official 766.25 ETH / 1,335-address counts and a recovery address.
Web3 Daily Exploits — 27 Sep 2026: DYORSWAP Fake GIWA Bridge
First-report this window: DYORSWAP confirmed the GIWA mainnet it had listed was a scammer-built fake chain using chain ID 9134. Community and tracker estimates put ETH-bridge losses near $2M. GIWA (Upbit L2) said official mainnet is not live. Bitget and Limit Break remain UPDATEs. Duelbits still unverified.
Web3 Daily Exploits — 26 Sep 2026: Bitget $387.5M Recount, No New Drain
No first-report protocol drain in this 26 Sep window after the required-monitor sweep. Bitget revised the 24 Sep hot/warm wallet incident from $351.6M to $387.5M (Zcash and TRON added; operator says not a second raid). GoPlus published a signing-pipeline analysis. Lookonchain flagged a $1.23M Binance withdrawal into the Bitget cluster. Limit Break / Magic Eden remains an UPDATE with victim outreach onchain. Payy and Duelbits stay prior-window.