Web3 Daily Exploits — 31 Oct 2026: Flap & Kintsu DNS Hijack Wave (StepDrainer), No New Scored Protocol Drains
Flap.sh and Kintsu.xyz (plus at least 10 other DeFi sites) suffered DNS hijacks on 31 October, redirecting users to StepDrainer wallet-drainer clones. No confirmed loss figure published. Live loss ~$0 for new scored items, 1 incident. Binance ~$6.3B remains an UPDATE with multi-breach notes, ~$3B frozen and $6.34B reserved.
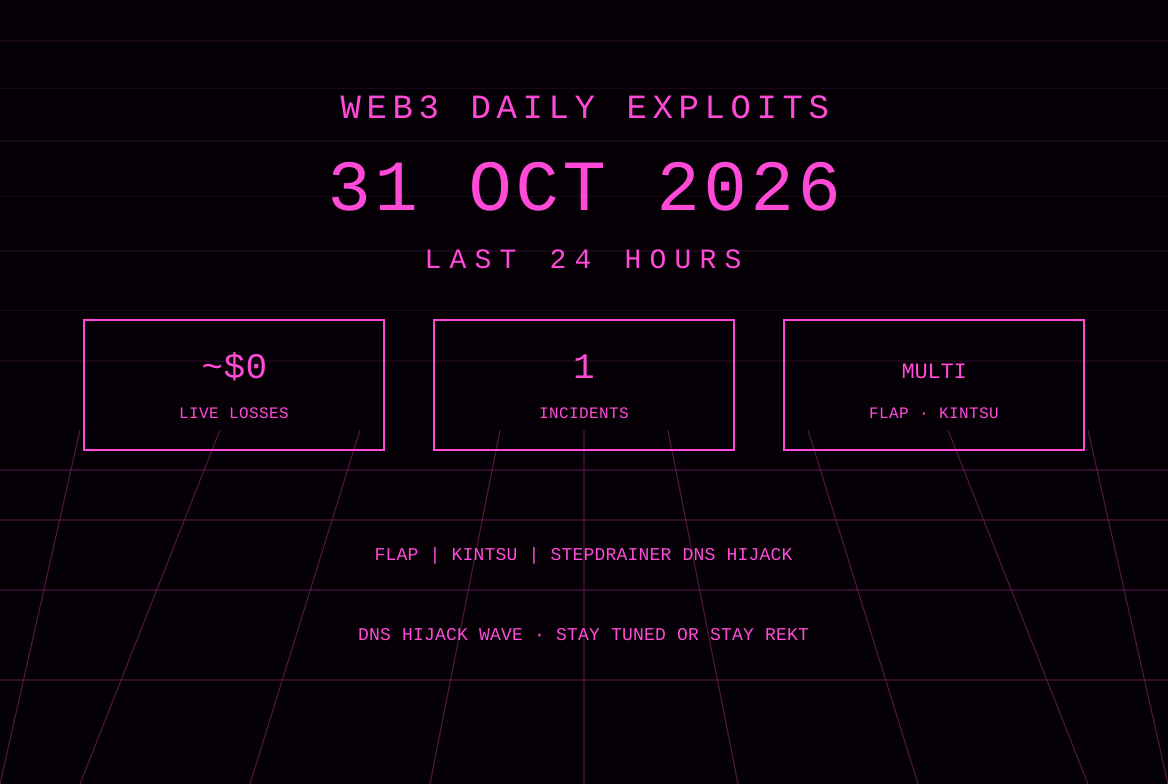
The 31 Oct America/Panama window records one first-reported incident used for scoring: a coordinated DNS-hijack wave that redirected Flap.sh, Kintsu.xyz and at least ten other DeFi and launchpad domains to malicious clones serving the StepDrainer wallet-drainer toolkit. No published loss amount, victim count or confirmed drained total has appeared in official project posts or primary security alerts at cutoff. Sites have been restored or redirected to alternate domains. Combined live loss on this card is $0 for newly scored items. The prior Binance hot-wallet signing-access compromise (~$6.3B) remains an UPDATE; ongoing on-chain movement, additional breach points, freezes and attribution notes are recorded but not re-scored. Recheck of monitored accounts confirmed no additional first-report protocol or smart-contract drains with fresh loss figures.
Flap / Kintsu (and additional domains) — multi-chain frontend — no published loss — DNS registrar hijack serving StepDrainer
What happened: Early on 31 October 2026 UTC, official domains for Flap (flap.sh, a BNB Chain token launchpad) and Kintsu (kintsu.xyz, a Monad liquid-staking protocol) began redirecting visitors to unauthorized clone sites. Security firm Blockaid and GoPlus identified the clones as serving the StepDrainer toolkit. Users who clicked “Connect Wallet” were presented with malicious signature requests for either direct native-token transfers (e.g., BNB to an attacker Safe) or unlimited ERC-20 approvals that the attacker later drained via transferFrom. GoPlus reported more than ten additional domains hijacked in the same wave (including stonkfun.xyz, pickle.finance, echelon.market, origami.finance, fluxbeam.xyz and others). Flap migrated service to flap.cool and warned users to avoid the original domain. Kintsu confirmed a registrar-level compromise and advised users who connected or signed after 00:00 UTC on 31 October to revoke approvals and move funds. Both projects restored or redirected traffic within hours. Primary alerts: https://x.com/GoPlusSecurity/status/2116443510412865653. Flap progress update: https://x.com/flapdotsh/status/2116400269445509360.
Protocol / chain / asset: Frontend / DNS infrastructure of Flap (BNB Chain) and Kintsu (Monad) plus additional DeFi sites. No smart-contract or protocol logic was exploited. Assets at risk were any tokens held by users who signed the malicious requests (native tokens or ERC-20s with unlimited approvals). Contracts themselves remained intact.
Loss: No confirmed loss figure, total drained amount or unique victim count has been published by the projects, Blockaid, GoPlus or other primary monitors as of cutoff. Flap has stated it will repay users whose funds were stolen. Individual anecdotal reports of small losses exist but are unverified and not used for scoring. The incident is recorded with a live loss of $0 pending any official quantification. Status remains under investigation for the registrar compromise path.
Attack type: DNS / registrar compromise (supply-chain at the domain level) that redirected traffic to a pixel-cloned frontend hosting the StepDrainer wallet-drainer kit. Classic frontend phishing that relies on user signatures rather than private-key theft or smart-contract bugs. Not a protocol vulnerability.
Explorer URLs: Attacker-controlled Safe recipient (reported by GoPlus): https://bscscan.com/address/0x24497068cA4166ca32a04ae530ce00Cf79755bD5. Safe sole owner / execution address: https://bscscan.com/address/0x33dfc810365193bff54326812d7df34b3e438da3. BSC explorer: https://bscscan.com/. Additional chains apply for other affected sites.
Status: Detected and contained on 31 October. Flap and Kintsu domains restored or redirected to alternate addresses. Root cause (domain registrar or provider compromise) under investigation. Users who interacted with the clones are advised to revoke approvals and move remaining funds to fresh wallets. No full post-mortem at cutoff. Treat unofficial recovery offers with caution.
Sources: https://x.com/GoPlusSecurity/status/2116443510412865653; https://x.com/flapdotsh/status/2116400269445509360; https://x.com/flapdotsh/status/2116352828734050339; Blockaid and project confirmations.
Also noted
- Binance hot-wallet signing-access compromise (UPDATE, not re-scored): The ~$6.3 billion multi-chain drain from 29 October remains on the 30 Oct brief. Binance has confirmed additional points of breach beyond the initial compromised DevOps laptop. Approximately $3 billion frozen by issuers and partners (Tether, Circle, Ripple and others). Binance has reserved over $6.34 billion in company funds (including SAFU and matching assets) to cover all user losses and states user funds are safe. Withdrawals remain paused with a target for phased resumption within ~34 hours (Sunday window) subject to security checks; deposits unaffected. Ongoing notes include further swaps by labeled hacker addresses (PeckShield), commingling of Binance and prior Bitget proceeds at a shared address (ZachXBT, indicating likely same actor / TraderTraitor overlap), and high-confidence attribution notes from TRM Labs, Chainalysis and Elliptic to North Korean TraderTraitor operators (Binance has not confirmed). No material new loss figures used for scoring today. https://www.rektradar.xyz/web3-daily-exploits-30-oct-2026-binance-63b-eip7702-polymarket-debugbear/. ZachXBT update: https://x.com/zachxbt/status/2116030284261179538.
- Polymarket DebugBear session abuse (UPDATE, not re-scored): The ~$2.5-2.71 million international-site drain via compromised DebugBear RUM script remains as previously covered. Polymarket status postmortem confirms third-party vendor compromise, full reimbursement of affected traders, and additional coverage for pause-related losses (total commitment around $3.9 million). Service restored; no new loss figures. https://www.rektradar.xyz/web3-daily-exploits-30-oct-2026-binance-63b-eip7702-polymarket-debugbear/.
- Prior items (not re-scored): zkLink Nova Arbitrator, Avalanche TranchePool, X100 and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the DNS-hijack wave.
Sources and references
- GoPlus Flap/Kintsu DNS alert: https://x.com/GoPlusSecurity/status/2116443510412865653
- Flap progress / migration update: https://x.com/flapdotsh/status/2116400269445509360
- Flap initial warning: https://x.com/flapdotsh/status/2116352828734050339
- ZachXBT Binance/Bitget commingling note: https://x.com/zachxbt/status/2116030284261179538
- Binance Security Incident Update #2: https://www.binance.com/en/support/announcement/detail/d3306d9dca5243548c813b605e1d1751
- 30 Oct brief for Binance/Polymarket coverage: https://www.rektradar.xyz/web3-daily-exploits-30-oct-2026-binance-63b-eip7702-polymarket-debugbear/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is $0. The only newly reported item is the Flap/Kintsu (and additional domains) DNS-hijack wave serving StepDrainer clones; no published loss figure exists at cutoff, so it is not assigned a non-zero amount. Binance remains an UPDATE and is not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 30 Oct 2026: Binance ~$6.3B Hot Wallet EIP-7702 Takeover & Polymarket DebugBear Drain
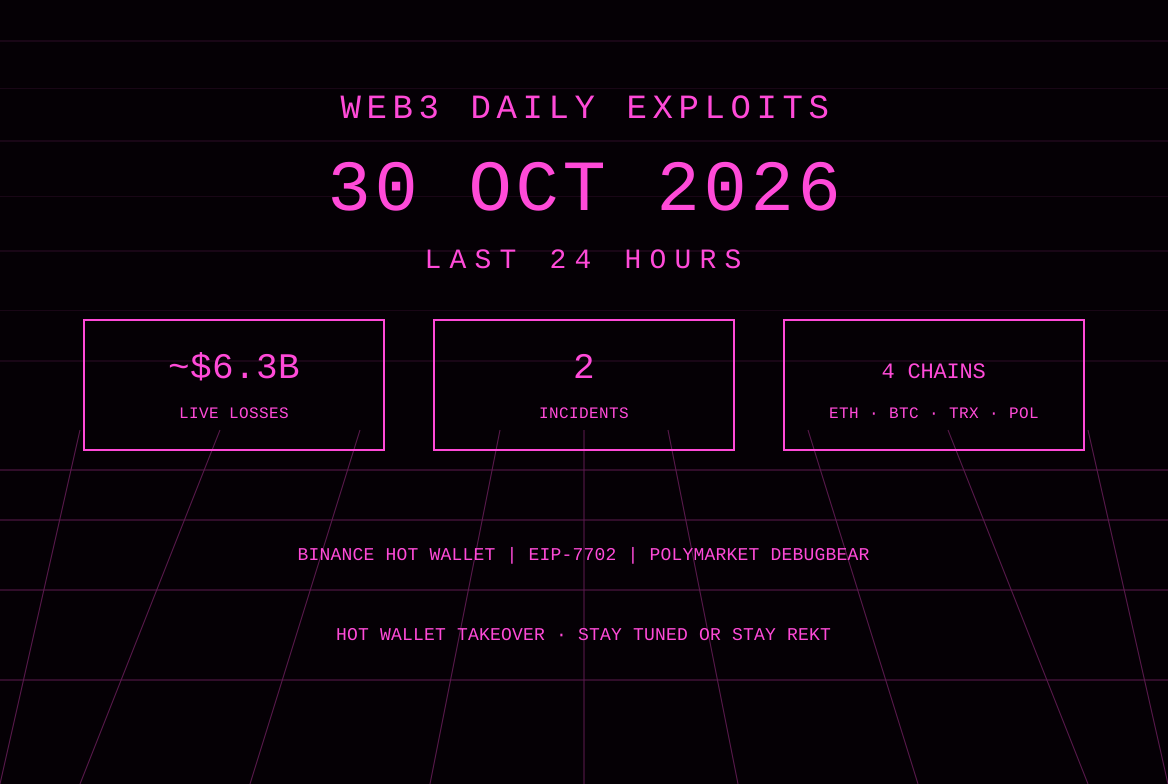
Binance hot wallets lost an estimated ~$6.3B across multiple chains after signing access was used to install an EIP-7702 delegation on Binance 14 and submit unauthorized withdrawals; ~$3B frozen. Polymarket international site lost ~$2.5-2.71M via a compromised DebugBear RUM script that abused logged-in sessions. Live loss ~$6.3B, 2 incidents, ETH · BTC · TRX · POL. zkLink Nova remains an UPDATE.
Web3 Daily Exploits — 29 Oct 2026: zkLink Nova ~$0.78M Arbitrator Forged Batch Root
zkLink Nova Arbitrator on Ethereum (and Optimism) lost ~$780-805K after the claim path failed to clear transient finalizeMessageHash, allowing a public relayer to install an attacker-chosen L2 logs root and finalize forged withdrawals. Live loss ~$0.78M, 1 incident, ETH · OP. Avalanche Tranche remains an UPDATE.
Web3 Daily Exploits — 28 Oct 2026: Avalanche Tranche Vault ~$1.01M Settlement Logic Double Draw
Avalanche TranchePool associated with Fence Finance, Valinor Digital and Oatfi lost ~$1.013M USDC after settlement logic treated a scheduled principal payment as received at UTC day rollover, restoring draw capacity for a second identical draw. Live loss ~$1.01M, 1 incident, AVAX. X100 remains an UPDATE.
Web3 Daily Exploits — 27 Oct 2026: Avalanche Safe ~$7.45M MEV Frontrun on Leftover Approvals
Avalanche 2-of-7 Safe lost ~$7.45M after unlimited approvals to an empty CreateCall-derived address were exploited; an MEV bot front-ran the sweeper and is negotiating a ~$371K WAVAX bounty. Live loss ~$7.45M, 1 incident, AVAX. X100 Tornado activity and an unverified CertiK ~$1.58M report noted.