Web3 Daily Exploits — 28 Oct 2026: Avalanche Tranche Vault ~$1.01M Settlement Logic Double Draw
Avalanche TranchePool associated with Fence Finance, Valinor Digital and Oatfi lost ~$1.013M USDC after settlement logic treated a scheduled principal payment as received at UTC day rollover, restoring draw capacity for a second identical draw. Live loss ~$1.01M, 1 incident, AVAX. X100 remains an UPDATE.
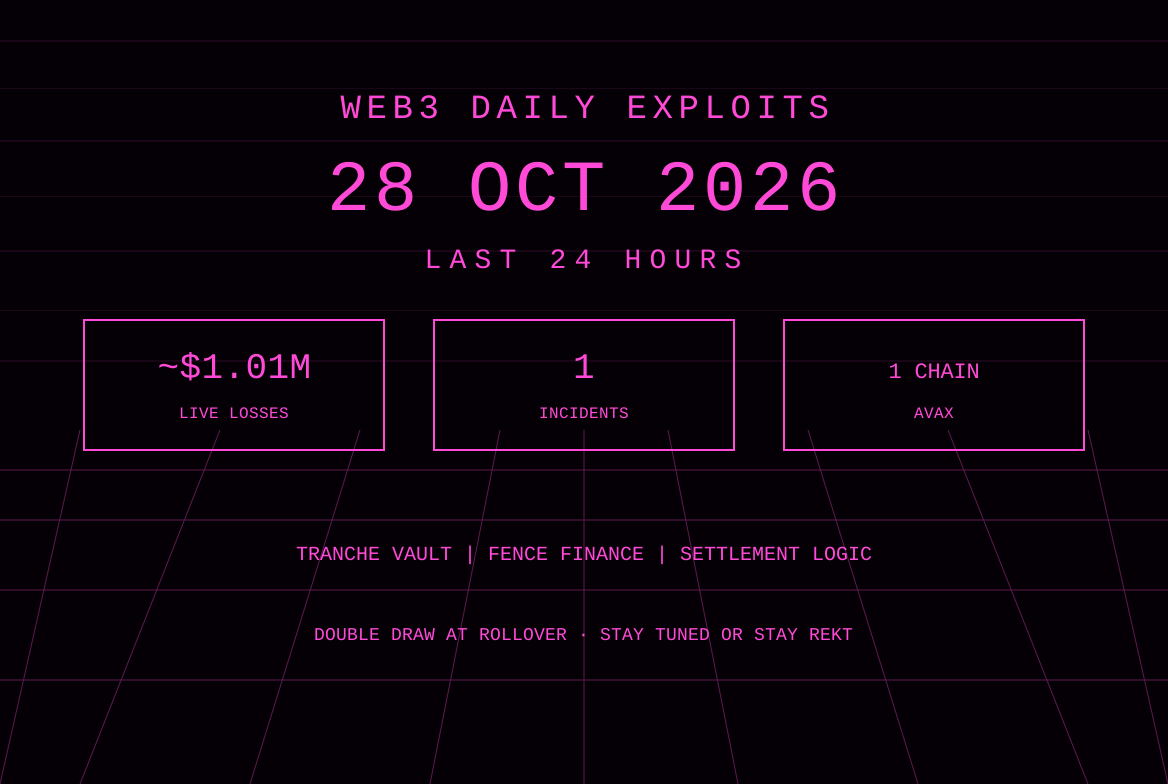
The 28 Oct America/Panama window records one first-report protocol incident used for scoring. A TranchePool / tranche vault on Avalanche C-Chain associated with Fence Finance, Valinor Digital and Oatfi lost approximately 1,013,353.61 USDC (about $1.01 million) after a settlement logic flaw at the UTC day rollover treated a scheduled principal payment as received, artificially restoring draw capacity. The attacker flash-loaned the amount, deposited as fund provider, drew as fund user, scheduled a repayment due at the rollover, then drew the same amount a second time against other users’ principal once the accounting error reopened the limit. Combined live loss on this card is approximately $1.01 million. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. The prior X100 flash-loan governance incident remains an UPDATE. Fence has offered a 10 percent recovery bounty via on-chain message. A small unverified EP project report involving a PHP session issue and ~$1k after swap is noted without scoring.
Tranche Vault / TranchePool — Avalanche — about $1.01M — Settlement logic double-draw at UTC rollover
What happened: Around 23:56 UTC on 27 October 2026 the attacker’s contract flash-loaned 1,013,353.61 USDC from Aave V3 on Avalanche, opened a tranche with itself as both fund provider and fund user (and as hook), deposited the borrowed USDC, scheduled a principal repayment of the same amount due at 00:00 UTC 28 October, then drew the full amount back and repaid the flash loan (paying roughly 507 USDC in fees). At 00:00:03 UTC the attacker called the draw/claim function again. Because the day had rolled over, the pool’s settlement logic booked the scheduled repayment as received and reduced recorded outstanding principal even though no USDC was repaid. The draw function checked against funded principal minus outstanding principal and therefore restored the full 1.013M USDC of draw capacity. The second draw was funded from the shared balance belonging to other lenders (tranche #0). The vault was left with zero USDC. Primary alerts from SlowMist, CertiK, DefimonAlerts, Phalcon and Blockaid appeared on 28 October. Primary alerts: https://x.com/SlowMist_Team/status/2115281126516490514, https://x.com/CertiKAlert/status/2115289650025923015, https://x.com/DefimonAlerts/status/2115328732181242351, https://x.com/Phalcon_xyz/status/2115371832593563761, https://x.com/blockaid_/status/2115249066787340562.
Protocol / chain / asset: TranchePool / tranche vault on Avalanche C-Chain, reportedly associated with Fence Finance, Valinor Digital and Oatfi. Vulnerable contract 0xe25cb545bdd47a8ec2d08001cb5661b00d47621a. Asset drained: USDC. The contract supports multiple lending tranches inside one pool; any caller can open a tranche by supplying a configuration whose admin matches the caller.
Loss: 1,013,353.61 USDC (approximately $1.01 million) according to SlowMist, CertiK, DefimonAlerts, Phalcon and Blockaid. The second draw emptied the remaining USDC belonging to other lenders. No independent loss figure contradicting the 1.013M USDC total was located at cutoff. The amount is scored as the live loss. Fence has offered a 10 percent recovery bounty.
Attack type: Smart-contract logic flaw in settlement / principal accounting. At UTC day rollover the logic treated a scheduled principal payment as received and subtracted it from outstanding principal despite no repayment. The draw/claim path then calculated available capacity as total deposits minus unmatured borrowed principal only, ignoring matured but unrepaid principal. Not a classic reentrancy, oracle manipulation, or private-key compromise. The attacker controlled both fund-provider and fund-user roles in the same tranche via flash loan and short maturity.
Explorer URLs: Example exploit / drain transaction: https://snowtrace.io/tx/0x3f6b23292a2e9c2956c7ac56d0b1f79b0271b49edec2156d2675ddf1de058c77. Setup / flash-loan transaction (reported): https://snowtrace.io/tx/0x19ab145e7f771549ca2f1da4b1768d7f728834015b2480ddb5be19c9769899fd. Attacker: https://snowtrace.io/address/0x6ff1c3ffa622e1062168f3497a275be9cc2b1246. Attack contract: https://snowtrace.io/address/0xF09DCf4EdE2a88bd316ff355dFC333A281a57805. Victim vault: https://snowtrace.io/address/0xe25cb545bdd47a8ec2d08001cb5661b00d47621a. Avalanche explorer: https://snowtrace.io/.
Status: Activity executed across the 27/28 October UTC boundary. Public alerts from Blockaid, SlowMist, CertiK, DefimonAlerts and Phalcon on 28 October. Vault left with zero USDC. Fence posted an on-chain message offering a 10 percent recovery bounty and requesting contact at recovery@fence.finance. No full official post-mortem located in monitored channels at cutoff. Users should treat any unofficial recovery claims with caution and verify addresses independently.
Sources: https://x.com/SlowMist_Team/status/2115281126516490514; https://x.com/CertiKAlert/status/2115289650025923015; https://x.com/DefimonAlerts/status/2115328732181242351; https://x.com/Phalcon_xyz/status/2115371832593563761; https://x.com/blockaid_/status/2115249066787340562.
Also noted
- EP project PHP session report (unverified, not scored): DefimonAlerts posted on-chain messages referencing an EP project theft involving a PHP session vulnerability, with an attacker withdrawing 612,506 EP tokens swapped via PancakeRouter for approximately 1,048 USDT and moved further. No independent confirmation from other required monitors, no protocol identification with scored loss, and the realized amount is small. Flagged only; not included in the scored total. Example TX: https://bscscan.com/tx/0x4663ccd38193c64d6df8d582911475a7523e6f66fe3d90f14c50497ea0bb0f8e.
- X100 flash-loan governance capture (UPDATE, not re-scored): The ~$4.85 million USDT drain via Senate majority capture on Ethereum remains on the 25 Oct brief. Further Tornado Cash activity by associated addresses was noted in prior windows. CertiK published a full analysis. No material new loss figures used for scoring today. https://www.rektradar.xyz/web3-daily-exploits-25-oct-2026-x100-4-85m-flash-gov-yape-22k/. CertiK analysis: https://x.com/CertiKAlert/status/2115379172109586588.
- Prior Avalanche Safe leftover-approvals / MEV front-run (UPDATE, not re-scored): The ~$7.45 million incident from 27 Oct remains as previously briefed. Bounty negotiation with the MEV bot continues. No material new loss figures used for scoring. https://www.rektradar.xyz/web3-daily-exploits-27-oct-2026-avax-safe-7-45m-mev-frontrun/.
- Prior items (not re-scored): Initia, Yapeswap, WAX bridge and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the Avalanche TranchePool detection.
Sources and references
- SlowMist TranchePool alert: https://x.com/SlowMist_Team/status/2115281126516490514
- CertiK Avalanche vault alert: https://x.com/CertiKAlert/status/2115289650025923015
- DefimonAlerts Fence alert: https://x.com/DefimonAlerts/status/2115328732181242351
- Phalcon_xyz analysis: https://x.com/Phalcon_xyz/status/2115371832593563761
- Blockaid alert: https://x.com/blockaid_/status/2115249066787340562
- Exploit TX: https://snowtrace.io/tx/0x3f6b23292a2e9c2956c7ac56d0b1f79b0271b49edec2156d2675ddf1de058c77
- Victim contract: https://snowtrace.io/address/0xe25cb545bdd47a8ec2d08001cb5661b00d47621a
- Attacker: https://snowtrace.io/address/0x6ff1c3ffa622e1062168f3497a275be9cc2b1246
- 25 Oct brief for X100 coverage: https://www.rektradar.xyz/web3-daily-exploits-25-oct-2026-x100-4-85m-flash-gov-yape-22k/
- 27 Oct brief for Avalanche Safe: https://www.rektradar.xyz/web3-daily-exploits-27-oct-2026-avax-safe-7-45m-mev-frontrun/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $1.01 million, driven by the Avalanche TranchePool settlement-logic double-draw that restored capacity at the UTC day rollover and emptied other lenders’ USDC. The incident was first publicly detailed by Blockaid, SlowMist, CertiK, DefimonAlerts and Phalcon in the last 24 hours. X100 and the prior Avalanche Safe remain UPDATEs and are not re-scored. A small EP PHP session report is flagged without scoring. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
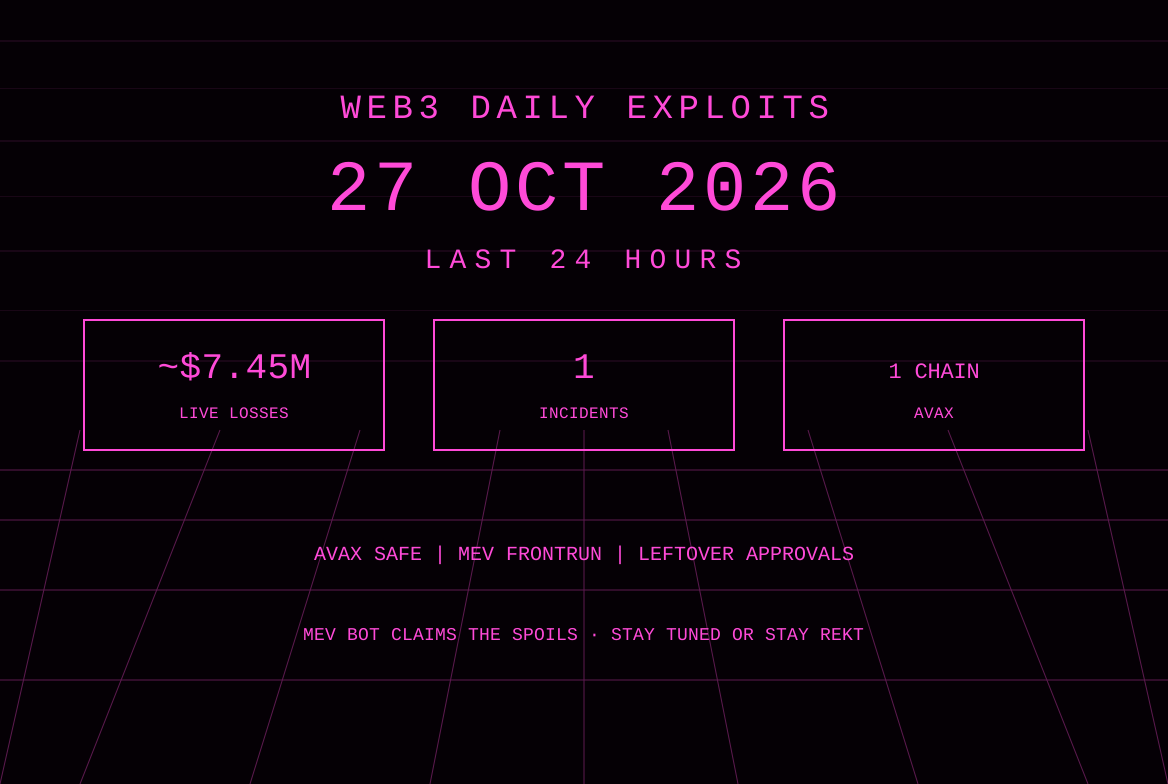
Web3 Daily Exploits — 27 Oct 2026: Avalanche Safe ~$7.45M MEV Frontrun on Leftover Approvals
Avalanche 2-of-7 Safe lost ~$7.45M after unlimited approvals to an empty CreateCall-derived address were exploited; an MEV bot front-ran the sweeper and is negotiating a ~$371K WAVAX bounty. Live loss ~$7.45M, 1 incident, AVAX. X100 Tornado activity and an unverified CertiK ~$1.58M report noted.
Web3 Daily Exploits — 26 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including X100, Yapeswap, Initia, and an unverified Optimism report.
Web3 Daily Exploits — 25 Oct 2026: X100 ~$4.85M Flash Governance Capture, Yapeswap $22K Zero-Quorum
X100 on Ethereum lost ~$4.85M after flash-loan governance capture of its three-seat Senate allowed same-block treasury swaps into attacker-controlled pools. Yapeswap lost ~$21.9K via zero-quorum WorkersUnion proposal that transferred feeToSetter and installed a fake Registry. Combined live loss ~$4.87M, 2 incidents, Ethereum. Initia remains an UPDATE.
Web3 Daily Exploits — 24 Oct 2026: Initia ~$2.7M MoveVM Script Cache Unbacked Mint
Initia L1 and rollups halted after a MoveVM script-caching bug let an attacker spoof VM state and credit unbacked WETH, iUSD and USDC without changing total supplies. ~$2.7M bridged out via LayerZero and CCTP before pause; swapped to 1,135.52 ETH on Ethereum. Official confirmation 24 Oct. Live loss ~$2.7M, 1 incident, 2 chains. Kimchi Solana KOL note and DarkSword iOS alert as UPDATE.