Web3 Daily Exploits — 29 Oct 2026: zkLink Nova ~$0.78M Arbitrator Forged Batch Root
zkLink Nova Arbitrator on Ethereum (and Optimism) lost ~$780-805K after the claim path failed to clear transient finalizeMessageHash, allowing a public relayer to install an attacker-chosen L2 logs root and finalize forged withdrawals. Live loss ~$0.78M, 1 incident, ETH · OP. Avalanche Tranche remains an UPDATE.
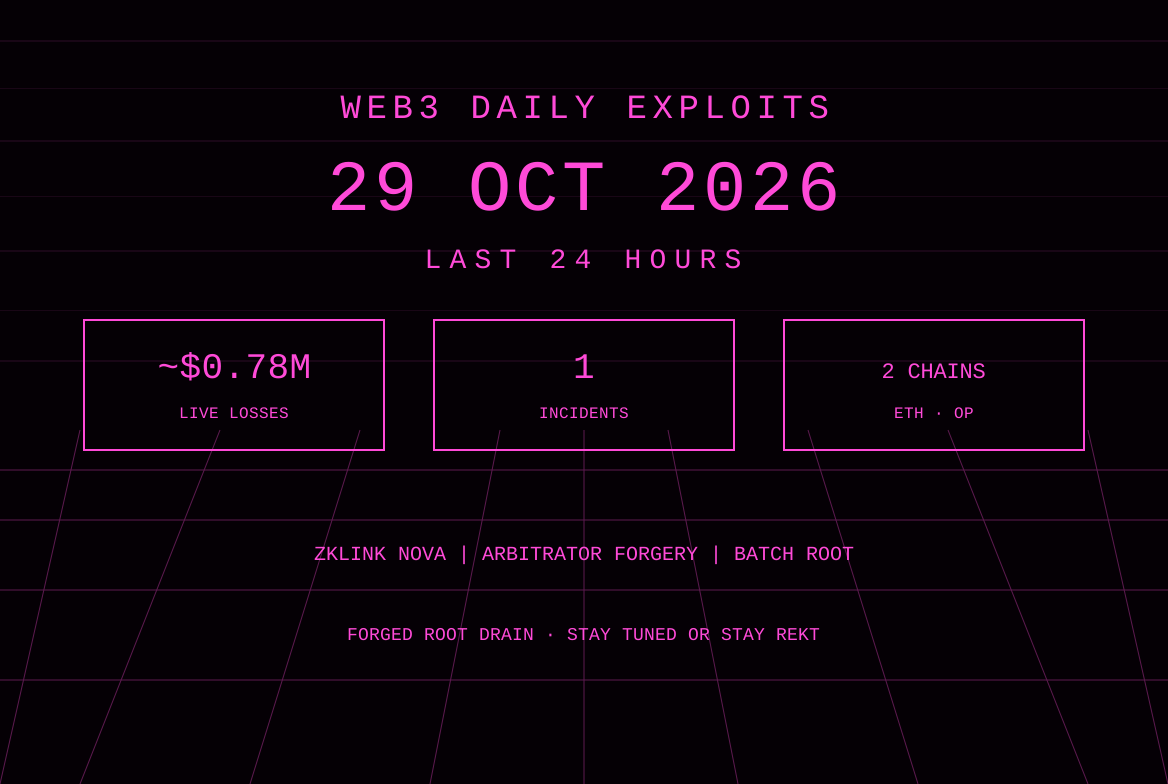
The 29 Oct America/Panama window records one first-report protocol incident used for scoring. zkLink Nova’s Arbitrator contract on Ethereum (with similar activity noted on Optimism and other L2s) lost approximately $780,000 to $805,000 after a flaw in the claim path failed to clear a transient authentication hash, allowing a publicly callable relayer to install an attacker-chosen L2 logs root and then finalize forged withdrawals from the L1 escrow and ERC20 bridge. Primary alerts from DefimonAlerts, Phalcon, SlowMist and Blockaid appeared on 29 October. Combined live loss on this card is approximately $0.78 million. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. The prior Avalanche TranchePool settlement-logic incident remains an UPDATE. zkLink has offered a 20 percent white-hat bounty. Small reports involving Humanode eHMND, mSamex and an ACP NodePurchase are noted without scoring. Recheck of monitored accounts through approximately 11:30 UTC on 29 October confirmed no additional scored incidents.
zkLink Nova — Ethereum / Optimism — about $0.78M — Arbitrator transient hash reuse / forged batch root
What happened: The attacker called the publicly accessible SyncL2TxHashRelayer to claim a valid message that populated finalizeMessageHash in the Arbitrator. Within the same transaction the attacker substituted the target for EthereumGateway.sendMessage, invoking syncBatchRoot with an attacker-chosen root. Because the Arbitrator did not clear the transient finalizeMessageHash between claims, the second call reused the prior authentication hash without a fresh authenticated callback. The gateway accepted the call from the trusted Arbitrator, the zkLink contract installed the forged root, and the attacker then submitted withdrawal proofs matching that root. Assets were released from the zkLink contract and L1ERC20Bridge with no corresponding L2 burn. Primary alerts: https://x.com/DefimonAlerts/status/2115672412486344960, https://x.com/Phalcon_xyz/status/2115671779717083260, https://x.com/SlowMist_Team/status/2115635114638250409. Official confirmation: https://x.com/zkLink_Official/status/2115731883313254565.
Protocol / chain / asset: zkLink Nova Arbitrator and associated gateway / bridge contracts on Ethereum, with similar attack transactions observed on Optimism and other L2s. Vulnerable Arbitrator 0x1ee09a2caa0813a5183f90f5a6d0e4871f4c6002 (implementation 0x7a0bb4805ecb7fd3c8dabbe4afa0e91cb1761e34). ZkLink contract 0x5fd9f73286b7e8683bab45019c94553b93e015cf. L1ERC20Bridge 0xad16edcf7deb7e90096a259c81269d811544b6b6. Assets drained included ~245.74 pufETH, ~22.43 ETH, ~12.57 ezETH, ~6.87 rsETH, ~6.30 STONE, smaller balances of mstETH, mswETH, wstETH, rswETH, ~18.1K USDC, ~3.36K USDT and ~0.174 WBTC.
Loss: Approximately $780,000 to $805,000 according to DefimonAlerts (~$805K), SlowMist (~$783.1K), Phalcon (~$780K) and Blockaid (~$786K). The bulk of the value came from pufETH (~$613-635K) plus ETH and other liquid-staking tokens. No independent figure contradicting the ~$780K range was located at cutoff. The amount is scored as the live loss. zkLink has offered a 20 percent white-hat bounty.
Attack type: Smart-contract logic flaw in authentication-state handling. The Arbitrator.claim path failed to clear the transient finalizeMessageHash and required a fresh authenticated callback for each invocation. Combined with a caller-controlled external call / target in the claim path, this allowed reuse of a valid hash to execute a privileged root update under the legitimate gateway identity, followed by forged Merkle proofs for withdrawals. Same output-root / withdrawal-forgery class as other rollup portal drains. Not a classic reentrancy or oracle manipulation.
Explorer URLs: Attacker: https://etherscan.io/address/0xaca0655a11200a80d33d0e48786317304cde5718. Additional attacker-related: https://etherscan.io/address/0xDAB137F390dF77caA97fd492540E973fd5e2F8c8. Victim ZkLink: https://etherscan.io/address/0x5fd9f73286b7e8683bab45019c94553b93e015cf. L1ERC20Bridge: https://etherscan.io/address/0xad16edcf7deb7e90096a259c81269d811544b6b6. Arbitrator: https://etherscan.io/address/0x1ee09a2caa0813a5183f90f5a6d0e4871f4c6002. Ethereum explorer: https://etherscan.io/.
Status: Activity reported on 28-29 October. Public alerts from DefimonAlerts, Phalcon, SlowMist and Blockaid on 29 October. zkLink official account confirmed an ongoing exploit targeting the Arbitrator on Ethereum and Optimism, stated the team is working to contain it, and offered a 20 percent white-hat bounty. No full post-mortem located in monitored channels at cutoff. Users should treat any unofficial recovery claims with caution and verify addresses independently. Pause flag on the main escrow was reported as false at the time of early alerts.
Sources: https://x.com/DefimonAlerts/status/2115672412486344960; https://x.com/Phalcon_xyz/status/2115671779717083260; https://x.com/SlowMist_Team/status/2115635114638250409; https://x.com/zkLink_Official/status/2115731883313254565.
Also noted
- Humanode eHMND precompile / approval drain (contained, not scored): Humanode confirmed an exploit on 28 October that used a bug in EVM precompiles (delegatecall acceptance) to take approximately 12.77M eHMND from 436 accounts, including a ChainPort vault. Native-side HMND was not reachable. The team shipped a fix within an hour, stated all identified issues are fixed, and promised full reimbursement to owners. Estimated realized value is low (~$30k range at contemporaneous prices). Not scored. Official update: https://x.com/humanode_io/status/2115542397413408974. Blog: https://blog.humanode.io/humanode-incident-response-and-recovery-update/.
- mSamex and ACP NodePurchase reports (unverified / small, not scored): DefimonAlerts posted on-chain messages referencing an mSamex vulnerability with a $1,000 bounty offer and an ACP incident that drained ~12.25M ACP from a NodePurchase contract. No independent confirmation from other required monitors with scored USD loss figures. Flagged only.
- Avalanche TranchePool settlement logic (UPDATE, not re-scored): The ~$1.01 million USDC double-draw on Avalanche from the 28 Oct brief remains as previously covered. Fence’s 10 percent recovery bounty offer continues. No material new loss figures used for scoring today. https://www.rektradar.xyz/web3-daily-exploits-28-oct-2026-avax-tranche-1-01m-settlement/.
- Prior items (not re-scored): X100, Avalanche Safe leftover-approvals / MEV, Initia, Yapeswap and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the zkLink Nova detection.
Sources and references
- DefimonAlerts zkLink alert: https://x.com/DefimonAlerts/status/2115672412486344960
- Phalcon_xyz analysis: https://x.com/Phalcon_xyz/status/2115671779717083260
- SlowMist TI Alert: https://x.com/SlowMist_Team/status/2115635114638250409
- zkLink official confirmation: https://x.com/zkLink_Official/status/2115731883313254565
- Humanode incident update: https://x.com/humanode_io/status/2115542397413408974
- 28 Oct brief for Avalanche Tranche coverage: https://www.rektradar.xyz/web3-daily-exploits-28-oct-2026-avax-tranche-1-01m-settlement/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $0.78 million, driven by the zkLink Nova Arbitrator transient-hash reuse that allowed a forged batch root to be installed and withdrawals finalized from the L1 escrow. The incident was first publicly detailed by DefimonAlerts, Phalcon, SlowMist and Blockaid in the last 24 hours, with official confirmation from zkLink. The Avalanche TranchePool remains an UPDATE and is not re-scored. Humanode, mSamex and ACP reports are flagged without scoring. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
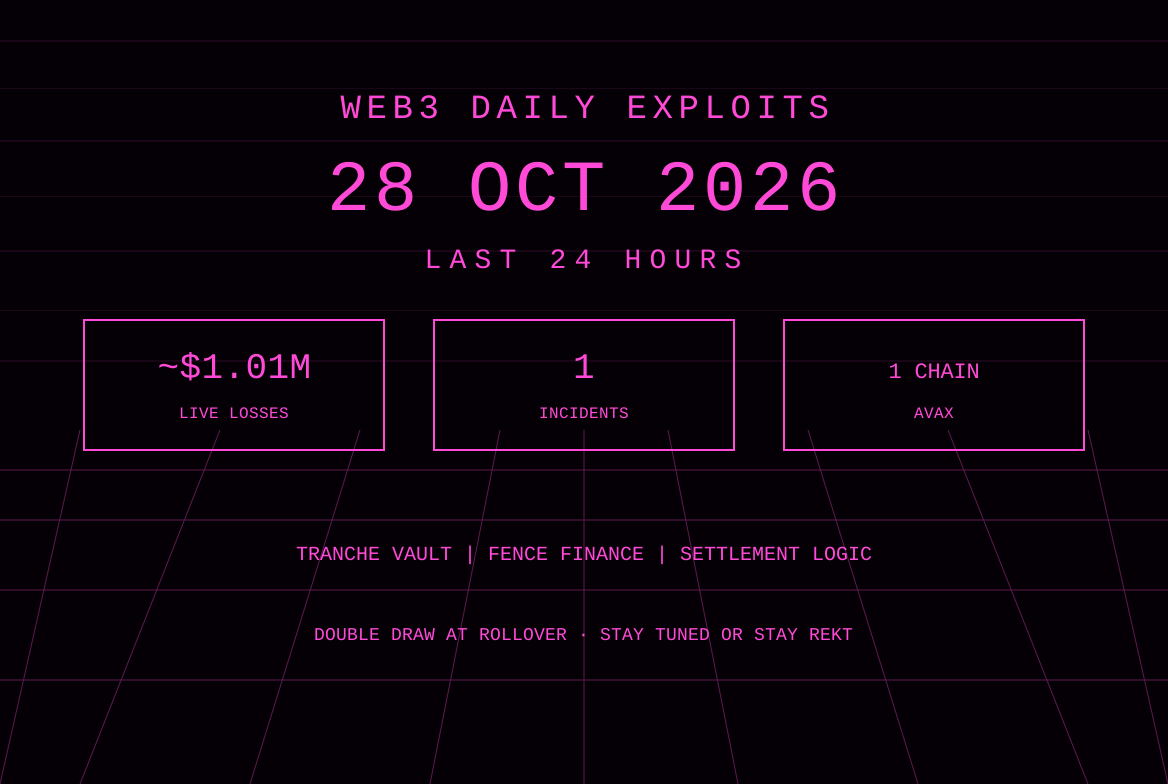
Web3 Daily Exploits — 28 Oct 2026: Avalanche Tranche Vault ~$1.01M Settlement Logic Double Draw
Avalanche TranchePool associated with Fence Finance, Valinor Digital and Oatfi lost ~$1.013M USDC after settlement logic treated a scheduled principal payment as received at UTC day rollover, restoring draw capacity for a second identical draw. Live loss ~$1.01M, 1 incident, AVAX. X100 remains an UPDATE.
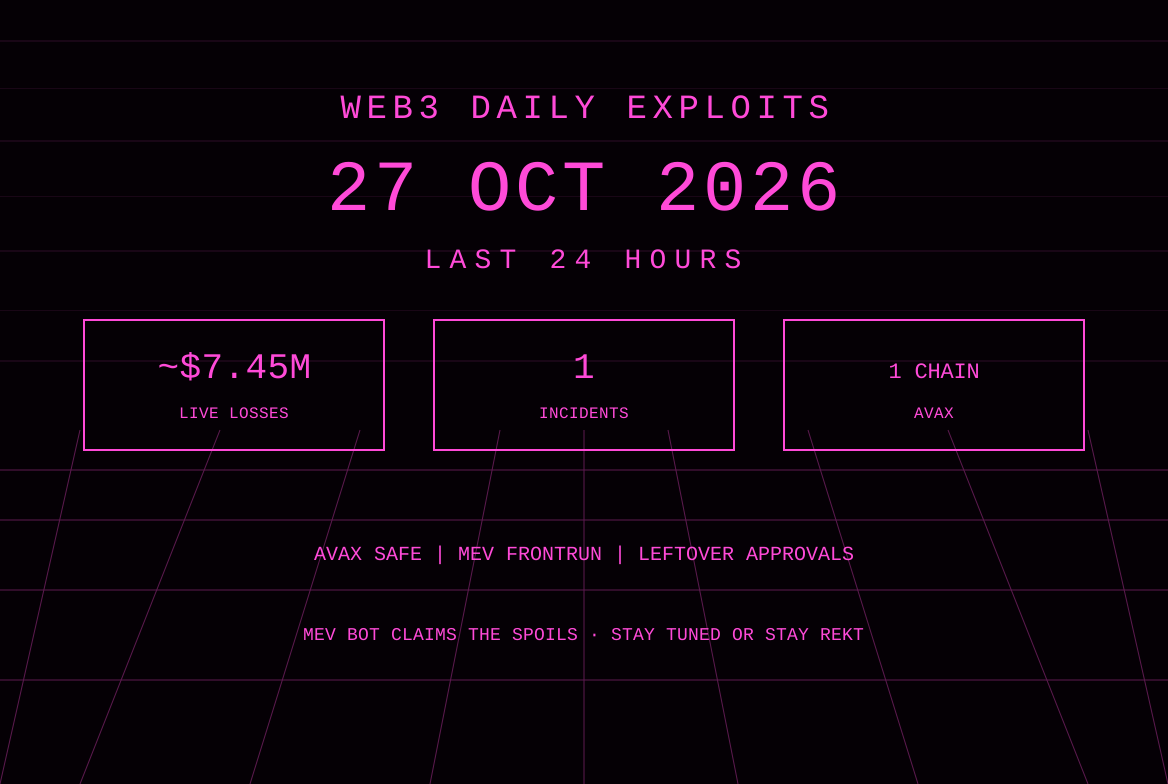
Web3 Daily Exploits — 27 Oct 2026: Avalanche Safe ~$7.45M MEV Frontrun on Leftover Approvals
Avalanche 2-of-7 Safe lost ~$7.45M after unlimited approvals to an empty CreateCall-derived address were exploited; an MEV bot front-ran the sweeper and is negotiating a ~$371K WAVAX bounty. Live loss ~$7.45M, 1 incident, AVAX. X100 Tornado activity and an unverified CertiK ~$1.58M report noted.
Web3 Daily Exploits — 26 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including X100, Yapeswap, Initia, and an unverified Optimism report.
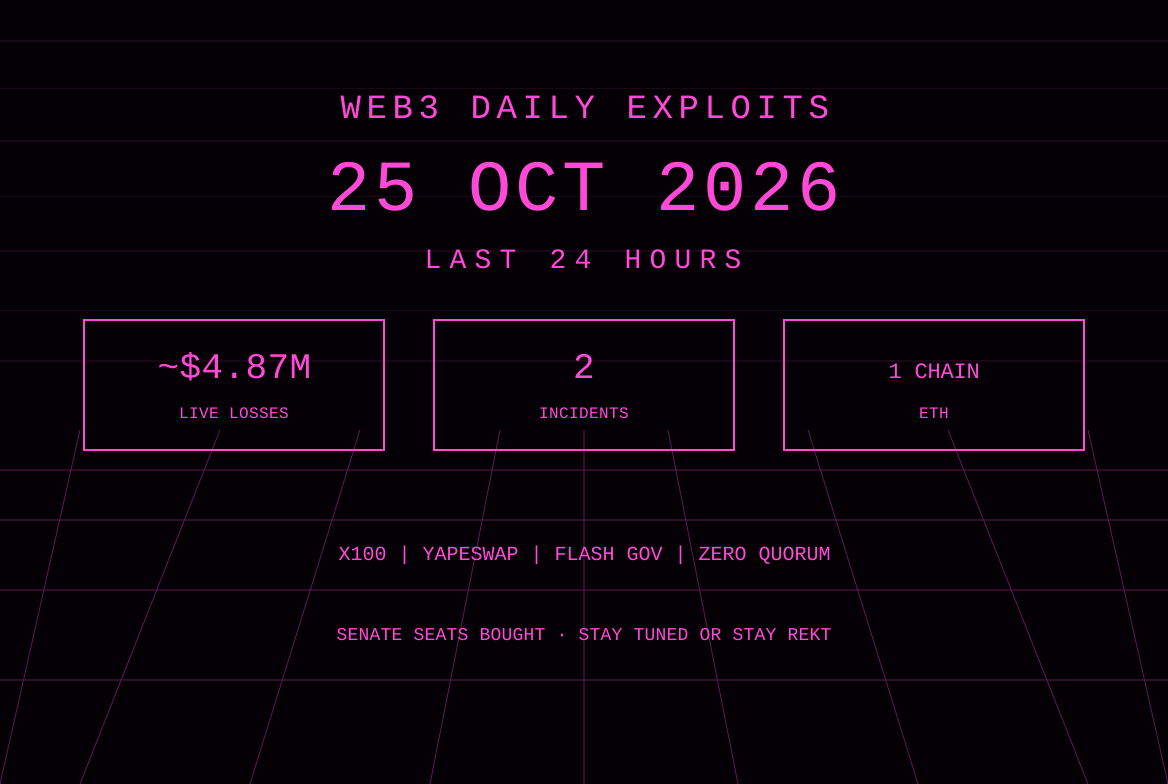
Web3 Daily Exploits — 25 Oct 2026: X100 ~$4.85M Flash Governance Capture, Yapeswap $22K Zero-Quorum
X100 on Ethereum lost ~$4.85M after flash-loan governance capture of its three-seat Senate allowed same-block treasury swaps into attacker-controlled pools. Yapeswap lost ~$21.9K via zero-quorum WorkersUnion proposal that transferred feeToSetter and installed a fake Registry. Combined live loss ~$4.87M, 2 incidents, Ethereum. Initia remains an UPDATE.