Web3 Daily Exploits — 30 Oct 2026: Binance ~$6.3B Hot Wallet EIP-7702 Takeover & Polymarket DebugBear Drain
Binance hot wallets lost an estimated ~$6.3B across multiple chains after signing access was used to install an EIP-7702 delegation on Binance 14 and submit unauthorized withdrawals; ~$3B frozen. Polymarket international site lost ~$2.5-2.71M via a compromised DebugBear RUM script that abused logged-in sessions. Live loss ~$6.3B, 2 incidents, ETH · BTC · TRX · POL. zkLink Nova remains an UPDATE.
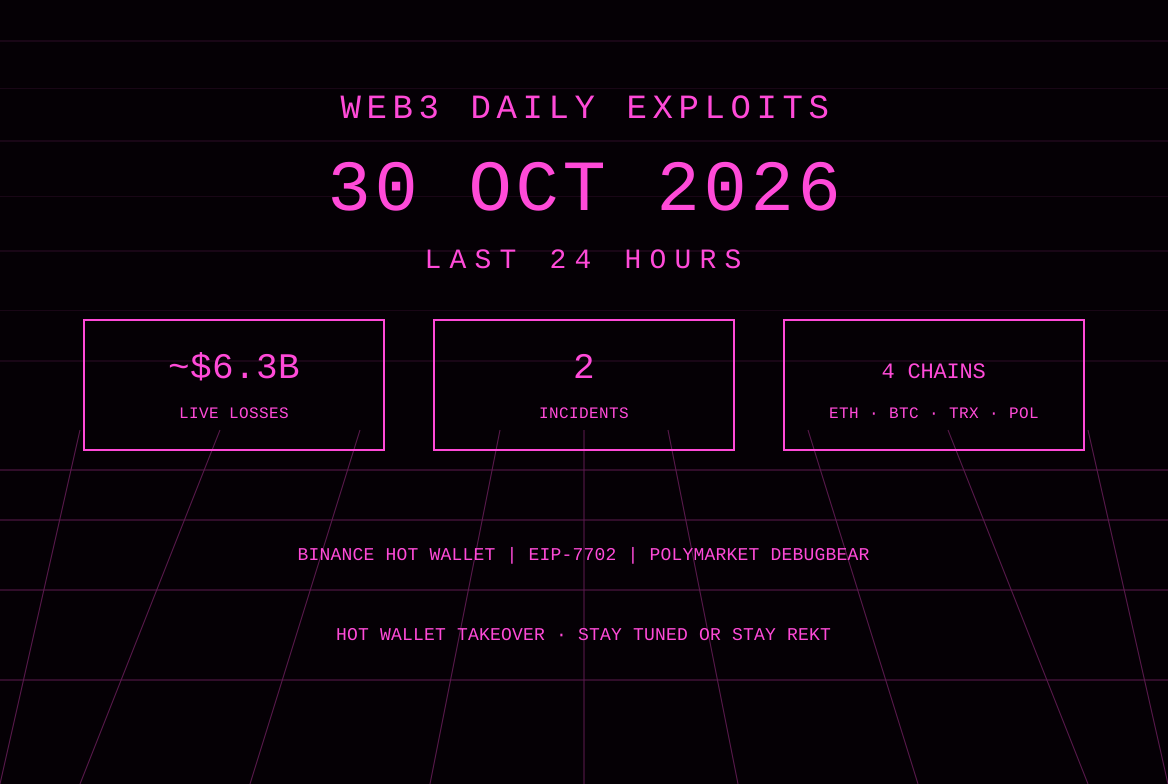
The 30 Oct America/Panama window records two first-report or materially updated incidents used for scoring. Binance hot wallets across Ethereum, Bitcoin, TRON and other chains lost an estimated approximately $6.3 billion after an attacker obtained signing access (initially linked to a compromised DevOps engineer’s laptop and a service container that submits withdrawals, with subsequent investigation uncovering additional points of breach) and used it to install an EIP-7702 delegation on the Binance 14 hot wallet, enabling a sweep of ETH and tokens, followed by additional signed withdrawals from other hot wallets. Approximately $3 billion has been frozen on-chain by issuers and partners. Binance states user funds are safe and will cover all losses from the SAFU fund and company funds, having reserved over $6.34 billion for the purpose. Separately, Polymarket’s international site lost approximately $2.5 million to $2.71 million after a compromised DebugBear real-user monitoring script delivered wallet-draining JavaScript that abused existing logged-in trading sessions to sell or transfer positions. Polymarket halted trading briefly, fixed the issue, and pledged full reimbursement. Combined live loss on this card is approximately $6.3 billion. The prior zkLink Nova Arbitrator incident remains an UPDATE. A Trezor CryptoBilis hardware-implant report is noted without scoring. Recheck of monitored accounts confirmed these as the primary scored items.
Binance Hot Wallets — Ethereum / Bitcoin / TRON / others — about $6.3B — EIP-7702 delegation + signing-access compromise
What happened: On 29 October 2026, around 20:20 UTC, an attacker-controlled address (funded via Tornado Cash) submitted an EIP-7702 type-4 transaction containing 50 authorizations signed by the Binance 14 hot wallet (0x28c6c06298d514db089934071355e5743bf21d60), delegating its code to an attacker-deployed sweeper contract. Minutes later the operator called the delegated wallet’s sweep function, moving approximately 167,464 ETH, 1.615 billion USDT and dozens of other tokens (LINK, UNI, ENA, COMP, AAVE and more) in a single transaction valued in the multi-billion range. Additional hot wallets on Ethereum, Bitcoin, TRON, Arbitrum, Avalanche and other chains executed further signed transfers to the same or related collection addresses. Circle froze approximately 823 million USDC in a main receiving wallet; Tether and others froze substantial USDT. Primary on-chain alerts and analysis appeared throughout 29-30 October. Official statement: https://x.com/binance/status/2115993361517891592. Investigation update: https://x.com/binance/status/2116089661408108712. DefimonAlerts alert: https://x.com/DefimonAlerts/status/2115923302069813348.
Protocol / chain / asset: Binance hot wallets (including labeled Binance 14 and others) on Ethereum (EIP-7702 delegation used), Bitcoin, TRON, and additional L2s/chains. Assets included ETH, BTC, USDT, USDC, BNB and 60+ other tokens. No user-deposit smart contracts were exploited; all movements were valid signatures from Binance-controlled keys.
Loss: Binance estimates total impact around $6.3 billion across all chains. Independent on-chain tallies range from approximately $3.3 billion (Blockaid, Ethereum/Arbitrum/Avalanche focus) to $5.5-5.8 billion (Decrypt, Conor Grogan, Chainalysis) and $6.36 billion (TRM Labs). Approximately $3 billion has been frozen on-chain. Binance has reserved over $6.34 billion in company funds (including $5 billion already held in matching assets) to cover the incident. The amount is scored at the official Binance estimate as the live loss figure. User funds are stated to be safe and fully covered.
Attack type: Signing-access / operational compromise enabling unauthorized withdrawal submissions, combined with EIP-7702 delegation on Ethereum. The delegation allowed the attacker’s contract code to run in the context of the hot wallet without further signatures from the key after the initial authorization. Binance reports no evidence of a direct private-key leak; the entry is linked to a compromised DevOps laptop that reached a service container used for withdrawals, with subsequent investigation uncovering additional points of breach. Not a smart-contract vulnerability in a protocol. Several blockchain intelligence firms (TRM Labs, Chainalysis, Elliptic) have attributed the activity with high confidence to North Korea’s TraderTraitor / Lazarus-linked operators; Binance has not confirmed attribution.
Explorer URLs: Binance 14 hot wallet: https://etherscan.io/address/0x28c6c06298d514db089934071355e5743bf21d60. Example collection / receiving address: https://etherscan.io/address/0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c. Operator / attacker EOA (reported): https://etherscan.io/address/0x7c8601d4645b93cea45F71e118A729332e6B5CA0. Sweeper contract: https://etherscan.io/address/0x63e842B054Bd624a465454D533C33F573e9c6fAe. Ethereum explorer: https://etherscan.io/. Additional chain explorers apply for BTC, TRON and L2 outflows.
Status: Activity concentrated on 29 October UTC evening. Public alerts and Binance statements on 29-30 October. Deposits unaffected; withdrawals paused while security checks complete (expected resumption within ~45-48 hours). Binance is working with law enforcement, issuers and intelligence firms; approximately $3 billion frozen. Full technical post-mortem pending. Users should rely only on official Binance channels and treat unofficial recovery claims with caution.
Sources: https://x.com/binance/status/2115993361517891592; https://x.com/binance/status/2116089661408108712; https://x.com/binance/status/2116121748555153621; https://x.com/DefimonAlerts/status/2115923302069813348; GoPlus Security alert.
Polymarket — Polygon — about $2.5-2.71M — DebugBear RUM script supply-chain session abuse
What happened: On 29 October 2026 a compromised real-user monitoring script served from DebugBear’s CDN (cdn.debugbear.com/C7xcKKrjUnXK.js) was loaded on Polymarket.com (international site). The malicious JavaScript read localStorage authentication context, proxy wallet and API key maps, located the live trading client/signer in the React app, and submitted orders or EIP-712 DepositWallet batch transfers that sold or moved user positions without additional prompts. Proceeds were swapped (USDC.e to POL via Relay) and consolidated to a hard-coded fallback address. Polymarket switched to cancel-only mode, removed the script, resumed trading within about an hour, and pledged full reimbursement. GoPlus analysis: https://x.com/GoPlusSecurity/status/2116030105713885218. DebugBear disclosed an ongoing incident and advised customers to remove the embed.
Protocol / chain / asset: Polymarket international prediction-market site on Polygon. Affected user DepositWallets and trading sessions. Assets moved included position tokens, USDC.e and POL. Polymarket US platform was not affected.
Loss: Estimates range from approximately $2.19 million (Hudson Rock screenshot of fallback address holdings) to $2.71 million (GoPlus on-chain analysis covering 710 DepositWallets and 731 addresses). Arkham data showed the primary consolidation address holding around $2.65 million in POL. Address counts do not equal unique users. The amount is scored in the $2.5-2.71 million range as the live loss. Polymarket has pledged full reimbursement to affected traders.
Attack type: Client-side supply-chain compromise of a third-party monitoring script. The payload reused existing authenticated session authority inside the page (no seed-phrase or private-key exfiltration). It constructed malicious orders or batch transfers that the existing signer would approve. Classic third-party script trust failure; not a smart-contract vulnerability on Polymarket or Polygon.
Explorer URLs: Primary consolidation / fallback address: https://polygonscan.com/address/0x3F99139F1C5854bb628c2e576Aaf638e99dFfc18. Polygon explorer: https://polygonscan.com/.
Status: Detected and contained on 29 October. Polymarket confirmed a third-party provider compromise, referred the matter to law enforcement, fixed the issue, and stated affected users will be made whole. DebugBear confirmed an incident and advised removal of the RUM embed. No full post-mortem on the vendor breach path at cutoff. Users should revoke unnecessary approvals and monitor official Polymarket channels.
Sources: https://x.com/GoPlusSecurity/status/2116030105713885218; Hudson Rock analysis and Polymarket status updates.
Also noted
- Trezor CryptoBilis hardware implant (precautionary, not scored): Trezor disclosed a single reported hardware implant in a Trezor Safe 5 purchased from the CryptoBilis reseller in August 2026. No losses have been reported. Users who bought from CryptoBilis since March 2026 are advised to move funds to a new seed and not enter existing seeds on the device. Trezor removed CryptoBilis as a reseller on 9 October after earlier Ledger reports. Official: https://x.com/Trezor/status/2116062963752747040. SlowMist alert: https://x.com/SlowMist_Team/status/2116086651684536385.
- zkLink Nova Arbitrator (UPDATE, not re-scored): The ~$0.78 million forged-batch-root incident from the 29 Oct brief remains as previously covered. zkLink suspended block production, patched contracts and disabled withdrawals. 20 percent white-hat bounty offered. No material new loss figures used for scoring today. https://www.rektradar.xyz/web3-daily-exploits-29-oct-2026-zklink-nova-780k-arbitrator/.
- Prior items (not re-scored): Avalanche TranchePool, X100, Avalanche Safe leftover-approvals / MEV and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the Binance and Polymarket detections.
Sources and references
- Binance official statement: https://x.com/binance/status/2115993361517891592
- Binance investigation update: https://x.com/binance/status/2116089661408108712
- Binance recovery update: https://x.com/binance/status/2116121748555153621
- DefimonAlerts Binance alert: https://x.com/DefimonAlerts/status/2115923302069813348
- GoPlus Polymarket breakdown: https://x.com/GoPlusSecurity/status/2116030105713885218
- Trezor CryptoBilis update: https://x.com/Trezor/status/2116062963752747040
- SlowMist Trezor alert: https://x.com/SlowMist_Team/status/2116086651684536385
- 29 Oct brief for zkLink coverage: https://www.rektradar.xyz/web3-daily-exploits-29-oct-2026-zklink-nova-780k-arbitrator/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $6.3 billion, driven by the Binance hot-wallet signing-access compromise that enabled an EIP-7702 delegation and multi-chain withdrawals, with Polymarket’s DebugBear supply-chain session abuse adding approximately $2.7 million. Both incidents were first publicly detailed or confirmed in the last 24 hours. zkLink Nova remains an UPDATE and is not re-scored. The Trezor implant report is flagged without scoring. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 29 Oct 2026: zkLink Nova ~$0.78M Arbitrator Forged Batch Root
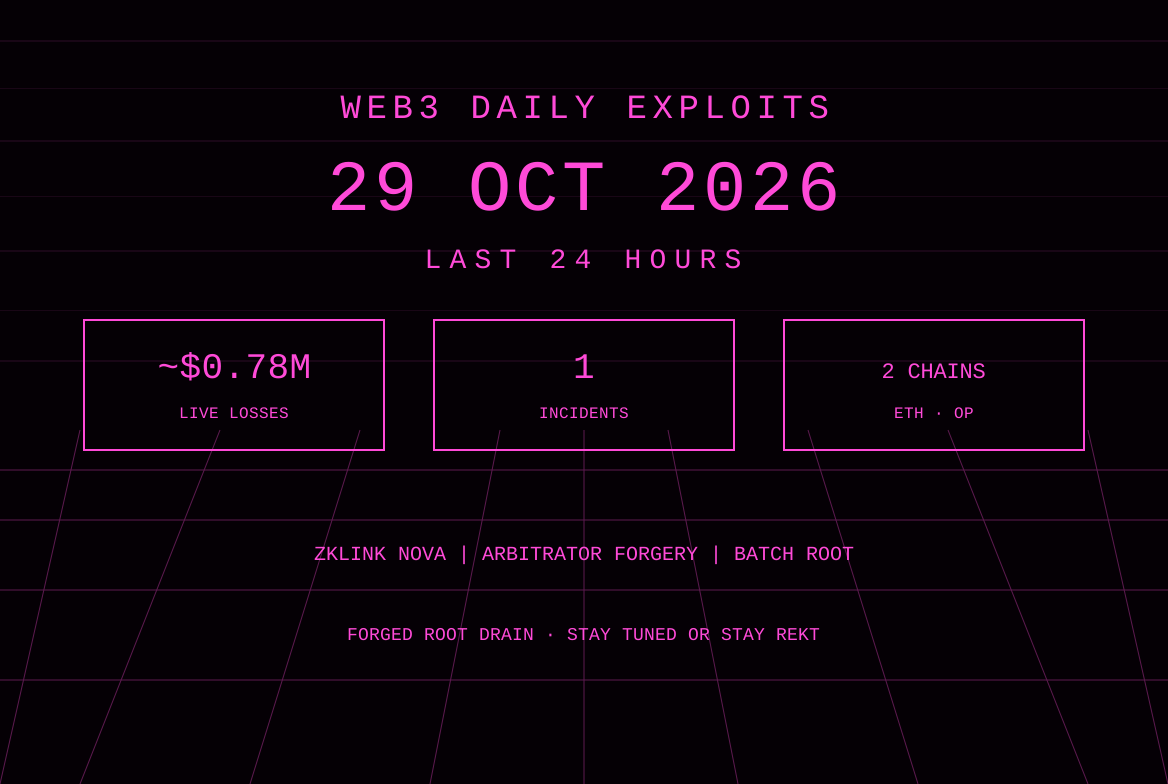
zkLink Nova Arbitrator on Ethereum (and Optimism) lost ~$780-805K after the claim path failed to clear transient finalizeMessageHash, allowing a public relayer to install an attacker-chosen L2 logs root and finalize forged withdrawals. Live loss ~$0.78M, 1 incident, ETH · OP. Avalanche Tranche remains an UPDATE.
Web3 Daily Exploits — 28 Oct 2026: Avalanche Tranche Vault ~$1.01M Settlement Logic Double Draw
Avalanche TranchePool associated with Fence Finance, Valinor Digital and Oatfi lost ~$1.013M USDC after settlement logic treated a scheduled principal payment as received at UTC day rollover, restoring draw capacity for a second identical draw. Live loss ~$1.01M, 1 incident, AVAX. X100 remains an UPDATE.
Web3 Daily Exploits — 27 Oct 2026: Avalanche Safe ~$7.45M MEV Frontrun on Leftover Approvals
Avalanche 2-of-7 Safe lost ~$7.45M after unlimited approvals to an empty CreateCall-derived address were exploited; an MEV bot front-ran the sweeper and is negotiating a ~$371K WAVAX bounty. Live loss ~$7.45M, 1 incident, AVAX. X100 Tornado activity and an unverified CertiK ~$1.58M report noted.
Web3 Daily Exploits — 26 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including X100, Yapeswap, Initia, and an unverified Optimism report.