Web3 Daily Exploits — 28 Sep 2026: Bitget Third-Party Creds RCA
Quiet first-report window. Bitget published its first operator RCA: a third-party security product yielded internal credentials, then fraudulent withdrawal commands bypassed risk controls. BTC withdrawals reopened. ZachXBT named five laundering aliases. DYORSWAP posted official 766.25 ETH / 1,335-address counts and a recovery address.
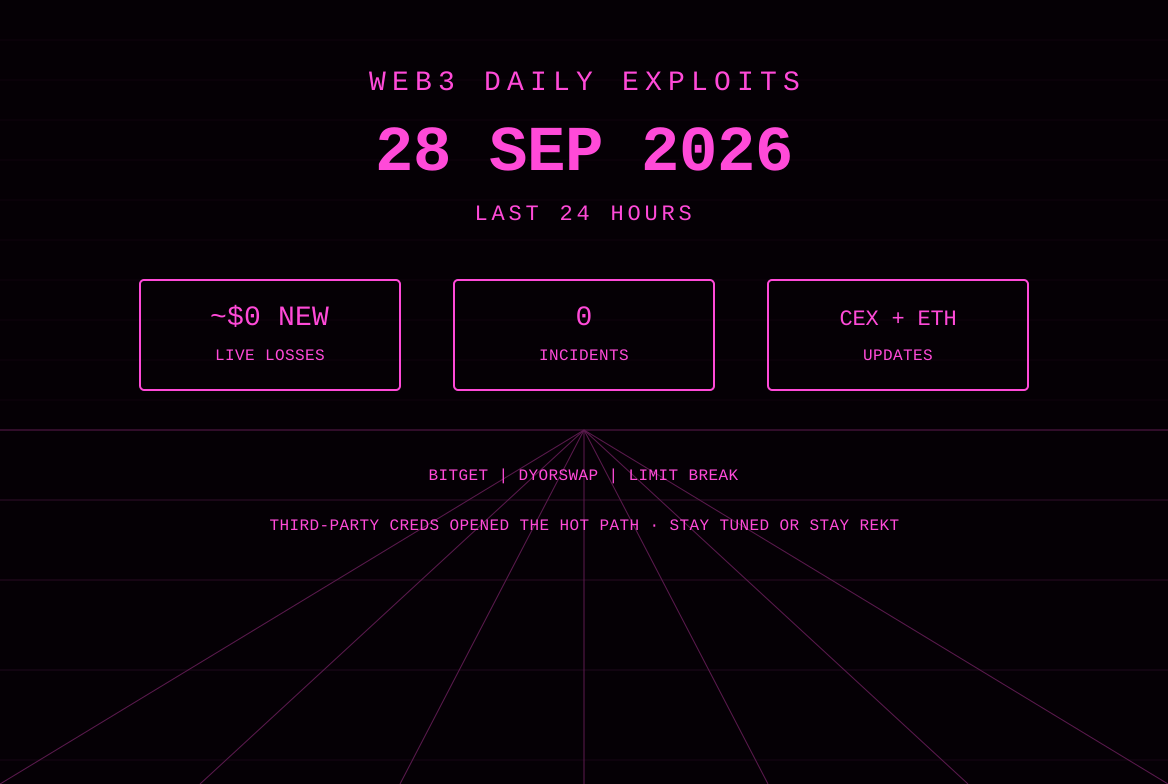
After the required-monitor sweep for this 28 Sep America/Panama window, this is a quiet first-report day. CertiKAlert, Phalcon_xyz, PeckShieldAlert, BlockSecTeam, and CyversAlerts published no in-window first-report smart-contract drain. Immunefi traffic was bounty marketing. rekt.news had no fresh 28 Sep incident page. Card live-loss for new incidents is therefore $0 and the first-report incident count is 0. The work in the last 24 hours is UPDATE traffic: Bitget’s first operator root-cause language and BTC withdrawal reopen; ZachXBT’s named laundering aliases on the same 24 Sep cluster; DYORSWAP’s official reconstruction of the fake GIWA 9134 bridge (766.25 ETH out, more than 200 ETH already repaid); and continued Limit Break / Magic Eden victim mail.
Bitget and CEO Gracy Chen used a 28 Sep livestream plus official threads to replace earlier “do not speculate” language with a closed-enough path: a vulnerability in a third-party security product used by the exchange produced high-level internal credentials; those credentials were used to send fraudulent withdrawal commands that bypassed risk controls; private keys were not compromised; cold wallets were not affected. BTC withdrawals on Bitcoin mainnet and BSC were live by the time of the recap (9,585 orders / 4,098.036 BTC processed as of 17:00 UTC+8). ZachXBT, in a separate post the same morning, said Chinese illicit actors were openly working Bitget proceeds in public Discord and Telegram channels and listed five aliases plus transaction hashes. DYORSWAP’s 27 Sep evening article, which landed after yesterday’s brief cutoff, replaced the unofficial “~$2M” community print with operator counts and an onchain recovery address later relayed by DefimonAlerts. Duelbits, carried as unverified on prior cards that waited on required-monitor confirmation, is now treated as a prior-window operator-confirmed ~$7M hot-wallet incident that has already relaunched; it is not re-scored here.
UPDATE — Bitget Exchange — multi-chain CEX hot/warm wallets — ~$387.5M already scored
What happened (this window): No new unauthorized-transfer wave was confirmed. The material change is operator RCA plus the first rails coming back online.
Bitget wrote that BTC withdrawals on the Bitcoin network started at 08:00 UTC on 28 Sep as scheduled, that BTC on BSC was also open, and that the published calendar remains: 29 Sep 08:00 UTC ETH (Ethereum, BSC, Arbitrum, Base, Optimism); 30 Sep 08:00 UTC USDT (Ethereum, BSC, Solana, Tron); 2 Oct 08:00 UTC other tokens / fiat / P2P. The operator said the vulnerability had been remediated, the incident remained contained, and no further unauthorized transfers had been identified after containment. User account balances were described as unaffected.
The same official thread, and a CEO recap of the livestream, stated the investigation finding in one paragraph: the attacker exploited a vulnerability in a third-party security product used by Bitget to obtain high-level internal credentials, then used those credentials to send fraudulent withdrawal commands to the wallet system, causing abnormal transfers that bypassed risk controls. Private keys were not compromised. Cold wallets were not affected. Affected systems and relevant servers were isolated. Internal credentials were revoked and reissued. Access to highly sensitive systems was restructured. The third-party vendor was notified, the vulnerability was shared with that vendor, and the affected functionality was disabled pending a fix. Mandiant and SlowMist remain on independent forensics and tracing. An internal security report is expected this week. Bitget called this its first security incident of this nature in eight years.
Gracy Chen’s livestream recap added operational numbers and the protection-fund line: 9,585 BTC withdrawal orders and 4,098.036 BTC processed as of 17:00 UTC+8; 100% coverage by the Bitget Protection Fund; the fund to be topped back up to more than $300 million with operator capital within the week; and a “Project Stand Together” fee-reward program for retail, VIP, and professional users. The livestream replay is the official broadcast https://x.com/i/broadcasts/1NGaroOnREXJj.
ZachXBT posted separately that Chinese illicit actors laundering funds from the $387 million Bitget exploit “on behalf of the alleged DPRK attackers” were asking for support with orders in public Discord servers and Telegram channels of services they use. He wrote that Alias 4 (lolo / Marin) had also been seen laundering funds from the Kelp DAO $292 million exploit earlier in the year, that the same pattern had followed multiple TraderTraitor-attributed exploits, and that funds were being chain-hopped via bridges and deposited into mixing services such as Wasabi. Five aliases and associated transaction hashes were published in that post. This desk records the aliases and hashes as ZachXBT’s attribution, not as a Bitget-signed identity list, and does not treat “alleged DPRK” as a closed RCA.
Protocol / chain / asset: Centralized exchange custody. Prior briefs already carry the operator receiving addresses: EVM 0x770b10b273fc44fe9197d6bf20f145c2e98463ee, XRP rwNhefsz1UQEusxhCvHip3RANinWi4CTck, ZEC t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG, TRON TBWNguTTgezw9dVorX441C6nDrZpRxYwKD. Confirmed affected assets named by Bitget in the recount window: XRP, ETH, USDT, ZEC, USDC, USDT0, XAUt, BNB, AVAX, and TRX. The third-party product was not named in the official posts used here. This brief does not invent a vendor.
Loss: Not re-scored. Operator recount remains ~$387.5 million for the original 24 Sep window. BTC reopen volume (4,098.036 BTC processed) is user withdrawal flow, not a new drain, and is not added to card live-loss.
Attack type: Unauthorized hot/warm wallet transfers initiated through stolen internal credentials obtained from a third-party security product, per Bitget. That is operator language, not a published vendor CVE and not a dumped signing-key event. GoPlus’s earlier signing-pipeline essay and THORChain outbound figures (~101.5 BTC already out; ~27.63M XRP mid-swap into BTC) remain analysis of post-drain movement from the prior window and are not added again. DPRK / TraderTraitor attribution remains unlabeled as confirmed.
Explorer URLs: Arkham cluster https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac. Bitget EVM first-hop https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee. Individual hashes in ZachXBT’s alias list were published without a chain prefix in the post used here; this desk does not invent explorer destinations for those strings.
Status: Confirmed prior incident. BTC rails open. ETH / USDT / remaining rails still on the published calendar. Full written technical report unpublished; promised this week. Vendor unnamed. Containment claimed by the operator.
Sources: https://x.com/bitget/status/2104489868722327700, https://x.com/bitget/status/2104498788564119612, https://x.com/bitget/status/2104498791034552328, https://x.com/bitget/status/2104494031036416485, https://x.com/GracyBitget/status/2104515761691939026, https://x.com/zachxbt/status/2104528688469647700
UPDATE — DYORSWAP / fake GIWA mainnet 9134 — Ethereum — 766.25 ETH official count (already scored ~$2M)
What happened (this window): The fake-chain listing was first-reported on the 27 Sep brief with a community ~$2 million print and no operator USD schedule. After that cutoff, DYORSWAP published a long reconstruction (X article, 27 Sep 18:00 UTC) and later an onchain recovery message.
Operator figures now on the record: the fraudulent network used chain ID 9134 and ran with a bridge and batcher similar to an OP Stack L2; deployment at 02:10:59 UTC+8 on 27 Sep in Ethereum block 26063331; about 8.5 hours earlier the deployer received roughly 0.045 ETH from an address DYORSWAP associated with ChangeHero; 39 blocks after deployment, three deposits totaling 0.4 ETH arrived in one block from wallets the DEX treated as internal-test-like; 1,335 addresses bridged about 767.65 ETH; about 766.25 ETH left the fraudulent bridge, with the drain associated with Ethereum block 26067309. DYORSWAP said its own contracts were not exploited. It said it had already paid more than 200 ETH from treasury to affected users and was still tracing the deployer, funding source, early test wallets, batcher infrastructure, and subsequent movement of the withdrawn ETH.
DefimonAlerts relayed an onchain message in this window that reconstructed the same path (“bridge deployment, early transactions, batcher activity, the drain transaction, and subsequent fund movements”), repeated the “more than 1,300 addresses” and treasury-compensation lines, and published an official recovery address 0xdf25f88aa6cde9937fdcfcf10fa349528c79dbf9 with an instruction not to send funds to any other address claiming to represent DYOR. GIWA by Upbit’s prior statement that official mainnet is not live still stands. No required-monitor desk published a named attacker EOA or a primary drain hash in the posts used here.
Protocol / chain / asset: Ethereum mainnet as the source of user deposits. Destination presented as GIWA mainnet (chain ID 9134) is not the official GIWA network. Asset is ETH. This remains a fake-chain / fake-bridge social and listing failure, not a confirmed exploit of GIWA production contracts or of DYORSWAP’s own AMM bytecode.
Loss: Not re-scored as a new incident. Official count is 766.25 ETH withdrawn from the fake bridge against 767.65 ETH deposited. The 27 Sep card already carried the unofficial ~$2M community estimate that matches that ether print at then-circulating prices. Compensation of more than 200 ETH is a treasury outflow from DYORSWAP, not recovered attacker funds, and is not subtracted from the prior card figure on this brief.
Attack type: Fake L2 using a live chain ID, a fraudulent bridge, and user-initiated deposits. Exact drain calldata and receive addresses were not attached to the required-monitor posts used here. This desk does not invent them.
Explorer URLs: Recovery address published in the Defimon-relayed message https://etherscan.io/address/0xdf25f88aa6cde9937fdcfcf10fa349528c79dbf9. Primary drain transaction hash was not published in that message or in the DYORSWAP article post used here.
Status: Confirmed fake-chain incident. Official counts now operator-signed. Compensation in progress. Tracing open. Official GIWA mainnet still not live.
Sources: https://x.com/DYORSWAPDEX/status/2104269975745945742, https://x.com/DefimonAlerts/status/2104507435155099804, https://x.com/GIWA_by_Upbit/status/2104091017901433017
UPDATE — Limit Break payment processors / Magic Eden users — Ethereum and ApeChain
What happened (this window): No required-monitor post published a new official USD total. DefimonAlerts relayed a fresh onchain message from a holder who said 4.4 WETH left via an ERC-20 transfer three days earlier and pointed other victims to OpenSea activity on collection 0x860bb7ce155d0a14574ce10033bec2c981739c8d, offering the current holder 4.3 WETH back and 0.1 WETH to keep. That is victim correspondence, not a new protocol RCA. Processor addresses remain Ethereum V2 0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834 and ApeChain V3 0x9a1D00000000fC540e2000560054812452eB5366.
Loss: Not re-scored. Prior window ~660 WETH (~$1.7M) plus listed NFT inventory.
Explorer URLs: Ethereum processor https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834. Cited collection https://etherscan.io/address/0x860bb7ce155d0a14574ce10033bec2c981739c8d. Prior cited theft https://etherscan.io/tx/0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf.
Status: Active user-side revoke. Redistribution of whitehat-rescued inventory still described as in process in prior-window language.
Sources: https://x.com/DefimonAlerts/status/2104506636219896209
Also noted
- Quiet first-report day after the account check. CertiKAlert, Phalcon_xyz, PeckShieldAlert, BlockSecTeam, and CyversAlerts had no in-window first-report protocol-drain posts. Lookonchain returned no in-window exploit-keyword hits in this sweep. Immunefi posts were a DAWN USD.infra vault bounty listing, not an incident first report.
- Duelbits ~$7M hot-wallet drain (prior window, now operator-confirmed): Co-founder confirmation and the site relaunch sat outside the first-report standard used on earlier cards that waited on required-monitor desks. The operator figure is about $7 million; independent traces clustered near $6–6.1 million on five chains. The casino is back online with an operator claim of about $8 million across hot and cold wallets. Not scored on this card. Original CertiK flag remains https://x.com/CertiKAlert/status/2103087558519624189.
- DPRK / TraderTraitor attribution on Bitget (unverified): Unchanged as a closed finding. ZachXBT’s 28 Sep post uses “alleged DPRK attackers” and ties Alias 4 to a prior Kelp DAO laundering pattern. Bitget’s RCA names a third-party credential path and does not name a nation-state actor.
- Payy RollupV1 (~$1.83M): No new first-report hash this slice. Drain transaction remains https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814.
- Nostra (17 Sep): DefimonAlerts relayed a Starknet Security Council onchain note asking the holder of a related account to write to securitycounciladmin@starknet.org, citing https://etherscan.io/tx/0xbfa0af1e2c7fe91c5cceba1c19b6d0b43c143b5e5143b718b8bfbca4c4ee0ccd. Outreach, not a new drain.
- SlowMist iOS Safari write-up: Cointelegraph coverage of a SlowMist investigation into an iOS Safari exploit chain (WYINCC / DarkSword-family techniques) states no confirmed crypto theft from that campaign in the published findings. Not scored. SlowMist’s own in-window post pointed at that article: https://x.com/SlowMist_Team/status/2104407459871785023.
Sources & references
- https://x.com/bitget/status/2104489868722327700
- https://x.com/bitget/status/2104494031036416485
- https://x.com/bitget/status/2104498788564119612
- https://x.com/bitget/status/2104498791034552328
- https://x.com/bitget/status/2104473674715959682
- https://x.com/GracyBitget/status/2104515761691939026
- https://x.com/i/broadcasts/1NGaroOnREXJj
- https://x.com/zachxbt/status/2104528688469647700
- https://x.com/DYORSWAPDEX/status/2104269975745945742
- https://x.com/DefimonAlerts/status/2104507435155099804
- https://x.com/DefimonAlerts/status/2104506636219896209
- https://x.com/DefimonAlerts/status/2104482018461409446
- https://x.com/GIWA_by_Upbit/status/2104091017901433017
- https://x.com/SlowMist_Team/status/2104407459871785023
- https://x.com/CertiKAlert/status/2103087558519624189
- https://arkm.com/explorer/entity/a4845a2d-0aca-4d28-b0fe-fb986c3370ac
- https://etherscan.io/address/0x770b10b273fC44Fe9197D6bF20F145c2e98463Ee
- https://etherscan.io/address/0xdf25f88aa6cde9937fdcfcf10fa349528c79dbf9
- https://etherscan.io/address/0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
- https://etherscan.io/address/0x860bb7ce155d0a14574ce10033bec2c981739c8d
- https://etherscan.io/tx/0x54bd37ca945aad1fb18aead696a3e65188a4a148070115ff0ac755ec4c464fcf
- https://etherscan.io/tx/0xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e1814
- https://etherscan.io/tx/0xbfa0af1e2c7fe91c5cceba1c19b6d0b43c143b5e5143b718b8bfbca4c4ee0ccd
Editor’s note: After the required account check this window has no new first-report live-loss. Card stats are $0 new / 0 incidents. Bitget’s third-party-credential RCA and BTC reopen are UPDATEs on the 24 Sep CEX event. DYORSWAP’s 766.25 ETH schedule is an UPDATE on yesterday’s fake-GIWA item. Limit Break is victim mail. Duelbits is prior-window and operator-confirmed, not a new score. DPRK attribution is unlabeled as confirmed. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 29 Sep 2026: Reality.eth XSS, $0 Drain
First-report this window: DefimonAlerts flagged a stored XSS in the reality.eth question renderer; the project confirmed a 2022-era reality-eth-lib bug, shipped v3.4.32, and reported no confirmed drain. Bitget reopened ETH rails with a net inflow and thanked NEAR Intents SHIELD for a $503k mid-swap freeze. Limit Break whitehat mail continued.
Web3 Daily Exploits — 27 Sep 2026: DYORSWAP Fake GIWA Bridge
First-report this window: DYORSWAP confirmed the GIWA mainnet it had listed was a scammer-built fake chain using chain ID 9134. Community and tracker estimates put ETH-bridge losses near $2M. GIWA (Upbit L2) said official mainnet is not live. Bitget and Limit Break remain UPDATEs. Duelbits still unverified.
Web3 Daily Exploits — 26 Sep 2026: Bitget $387.5M Recount, No New Drain
No first-report protocol drain in this 26 Sep window after the required-monitor sweep. Bitget revised the 24 Sep hot/warm wallet incident from $351.6M to $387.5M (Zcash and TRON added; operator says not a second raid). GoPlus published a signing-pipeline analysis. Lookonchain flagged a $1.23M Binance withdrawal into the Bitget cluster. Limit Break / Magic Eden remains an UPDATE with victim outreach onchain. Payy and Duelbits stay prior-window.
Web3 Daily Exploits — 25 Sep 2026: Bitget $351.6M Hot Wallet Drain
First-report live-loss this window: Bitget confirmed unauthorized transfers from hot and warm wallets at 18:31 UTC on 24 Sep, estimated $351.6M. Lookonchain tracked multi-chain composition and ETH consolidation. Second scored item: Limit Break payment processors used by Magic Eden — GoPlus cites 660 WETH (~$1.7M) plus listed NFT collections. Duelbits ~$6M outflows remain unverified. Payy carried as UPDATE.