Web3 Daily Exploits — 19 Nov 2026: K3 ~$3.4M sBOLD Share Accounting
First-report incidents: K3 Capital sBOLD vault on Ethereum drained ~$3.42M via share-accounting mismatch allowing flash-loaned assets to inflate redemption value. Gonka AI Ethereum bridge lost ~$1.05M after BLS key rotation (funds confirmed returned). RNT Lend on Polygon saw ~$955K stablecoins taken after admin upgrade of aToken proxies. LUKSO email recovery backend flaw affected ~300 profiles for ~1.4M LYX.
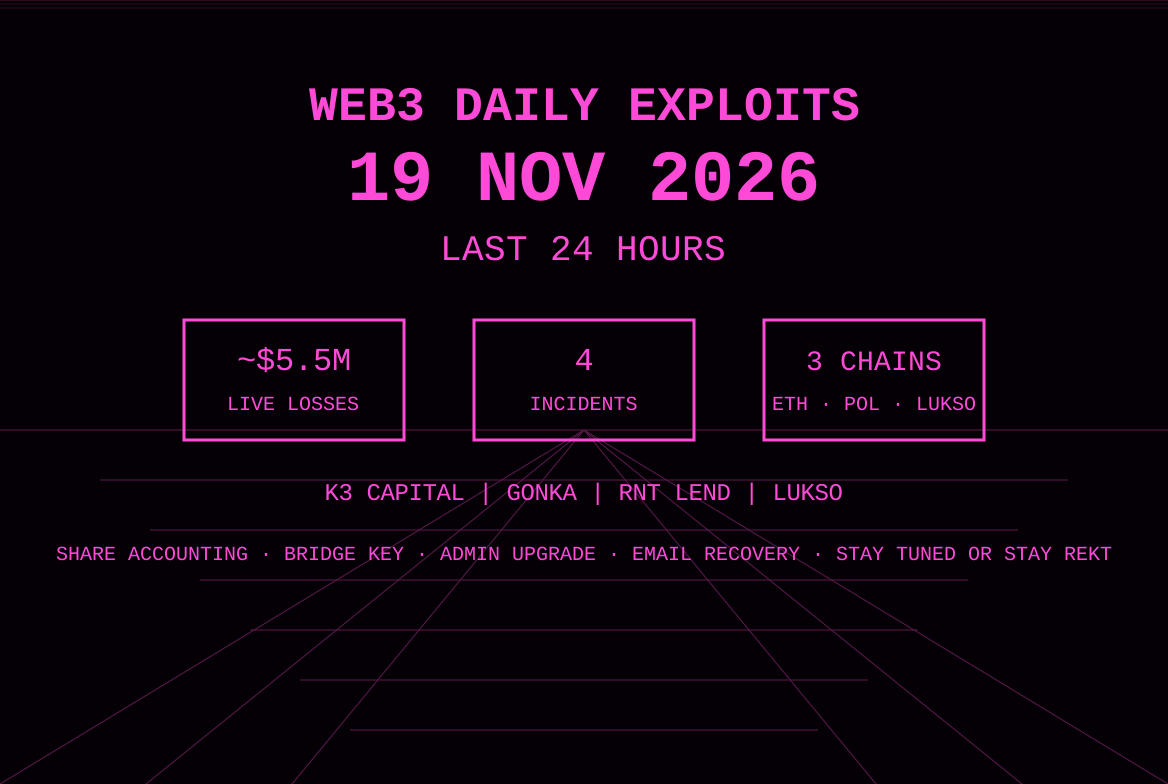
The 19 Nov America/Panama window records four first-reported incidents with scored losses totaling approximately $5.5 million across Ethereum, Polygon, and LUKSO. The largest is K3 Capital’s sBOLD vault on Ethereum, from which roughly $3.42 million was extracted in an eight-minute window through a share-accounting mismatch that let attackers introduce temporary assets excluded from valuation calculations and then redeem at inflated values. SlowMist and Blockaid independently flagged the activity; K3 Capital paused the affected contracts. Separately, Gonka AI’s Ethereum bridge lost approximately $1.05 million after an attacker rotated the epoch BLS group key, draining stablecoin reserves and minting unbacked WGNK; the project has confirmed the funds have been fully returned. On Polygon, RNT Lend (Reental) suffered an approximately $955,000 stablecoin drain after an admin key upgraded USDT and USDC aToken proxies to implementations permitting unrestricted withdrawals; MEV bots captured a portion and the project recovered associated property tokens. LUKSO disclosed that a backend flaw in its email-based recovery system allowed an attacker to add a controller key to roughly 300 Universal Profiles and extract approximately 1.4 million LYX, which was bridged and swapped for roughly 50 ETH. No additional first-report protocol drains with fresh confirmed user-loss figures appeared from monitored accounts beyond these items. Prior items remain UPDATEs.
K3 Capital — Ethereum — ~$3.42M — share accounting / flash-loan valuation mismatch
What happened: On 18 November 2026, attackers drained K3 Capital’s sBOLD vault on Ethereum. The vault compounds rewards from Liquity V2 stability pools. SlowMist identified the root cause as a check that verified the BOLD amount returned by a swap but failed to confirm that the router had actually spent the same token and amount used in the valuation calculation. Attackers exploited the mismatch by leaving WETH in the vault while redeeming shares at a valuation that included the temporary asset, then recovering the WETH through a second swap priced against a minimal amount of wstETH. An unused approval enabled the transfer. On-chain analysis by Bitquery documented 97 transactions across six wallets that emptied the vault between 12:25 and 12:33 UTC. One copycat bot extracted the largest share and paid substantial bribes to block builders; builders received approximately $1.78 million in aggregate. K3 Capital stated it was investigating malicious activity and paused the contracts. Initial Blockaid alerts described the activity as ongoing with roughly $3.43 million moved across about 34 transactions at the time of posting.
Protocol / chain / asset: K3 Capital sBOLD vault (Liquity V2-based yield product) on Ethereum. Primary asset: BOLD. Official response from @k3_capital. On-chain tracing by Bitquery, SlowMist, and Blockaid.
Loss: Approximately $3.42 million drained (Bitquery: $3.42M, the entire vault balance). Live scored on this brief: ~$3.42M. Final net loss after any recovery, builder payments, and residual holdings remains under investigation.
Attack type: Share-accounting / valuation mismatch combined with flash-loaned assets. Not a classic reentrancy. The protocol checked swap output quantity but not input identity or amount consistency.
Explorer URLs: Vulnerable contract referenced by SlowMist: https://etherscan.io/address/0x50Bd66D59911F5e086Ec87aE43C811e0D059DD11. Attacker address: https://etherscan.io/address/0xDC0e2FDEb89D2F363F2EA1B50E923d464C414dAA. Full transaction set documented in Bitquery investigation.
Status: Confirmed by on-chain data and multiple security firms. Contracts paused. Investigation ongoing. Flag any quantified recovery or detailed post-mortem as material.
Sources: SlowMist TI Alert (18 Nov); Blockaid alerts; Bitquery investigation; secondary coverage (Unchained, TokenPost, CryptoBriefing).
Gonka AI — Ethereum — ~$1.05M — BLS key rotation / bridge drain (UPDATE: funds fully returned)
What happened: On 18 November 2026, Blockaid reported an ongoing exploit of Gonka AI’s Ethereum bridge. An attacker rotated the epoch BLS group key used to authorize bridge operations, then drained remaining stablecoin reserves and minted unbacked Wrapped Gonka (WGNK). Blockaid estimated approximately $1.05 million realized across roughly five transactions. On-chain records showed withdrawals of approximately 884,151 USDT and 648 USDC. On 19 November the project confirmed that the funds have been fully returned. Network consensus and inference services were unaffected. Users were advised not to interact with WGNK or the bridge until further notice.
Protocol / chain / asset: Gonka AI Ethereum bridge. Assets: USDT, USDC, unbacked WGNK. Official statements from @gonka_ai. Detection by Blockaid.
Loss: Approximately $1.05 million reported realized value (stablecoin drain plus unbacked mint). Project confirmed funds fully returned. Live scored on this brief as ~$1.05M (initial reported); final net after confirmed return is zero for this incident.
Attack type: Compromise or rotation of the bridge epoch BLS group key enabling unauthorized reserve withdrawals and minting. Bridge logic / key management issue. Not a consensus failure.
Explorer URLs: Exploiter: https://etherscan.io/address/0x6650a1CB0c3B970a0e4CEd26984fe06DB7844D80. Example transaction: https://etherscan.io/tx/0xa6b23e579b004e47657fd8f963a1f5732c5063a7d6eb7f9d7b185cd05d487178. Victim bridge: https://etherscan.io/address/0x972a7A92D92796a98801A8818bcF91f1648f2F68.
Status: Confirmed by Blockaid and on-chain data. Project confirmed full return of funds on 19 November. Users advised to avoid WGNK and the bridge. Labeled with UPDATE for the confirmed return.
Sources: Blockaid alerts (18 Nov); @gonka_ai updates including return confirmation; The Defiant; TokenPost; CryptoTimes.
RNT Lend / Reental — Polygon — ~$955K — admin key compromise / malicious proxy upgrade
What happened: On 18 November 2026, an admin key associated with Reental’s RNT Lend on Polygon upgraded the USDT and USDC aToken proxy contracts to implementations containing an unprotected drain function. The upgrade allowed any address to withdraw underlying tokens. MEV bots front-ran and extracted approximately $455,000 from the aToken reserves. The keyholder subsequently extracted an additional approximately $500,000 from user wallets and Safes, bridging most proceeds off-chain within the hour. Approximately $49.3 million in property tokens was also moved; Reental recovered those tokens within roughly two hours using centralized manager controls. Initial alerts reported ~$454,000; later on-chain analysis placed the stablecoin total near $955,000. The protocol is an Aave V3 fork for real-estate-backed lending.
Protocol / chain / asset: RNT Lend (Reental) on Polygon. Assets: USDT, USDC (stablecoins); property tokens recovered. Detection by Blockaid and DefimonAlerts. On-chain analysis by Bitquery.
Loss: Approximately $955,000 in stablecoins. Property tokens recovered. Live scored on this brief: ~$955K. Final net loss after any further recovery remains under investigation.
Attack type: Private key compromise of admin / pool configurator leading to malicious aToken proxy upgrade with unrestricted drain function. Access control failure post-upgrade.
Explorer URLs: Referenced in DefimonAlerts and Blockaid posts; full transaction traces in Bitquery investigation of Reental RNT Lend drain.
Status: Confirmed by on-chain data and security firm alerts. Property tokens recovered. Stablecoin losses unrecovered at time of reporting. Investigation ongoing.
Sources: Blockaid alert (18 Nov); DefimonAlerts; Bitquery investigation; secondary coverage (TokenPost, Odaily).
LUKSO — LUKSO — ~$95K realized — email recovery backend flaw
What happened: Overnight 17–18 November 2026, an attacker exploited a backend security hole in LUKSO’s email-based recovery system. The attacker took control of the recovery service’s Universal Profiles and used them to add a controller key (0xa2f8Fd85366d1B4A3B13C33A48CD959F6D1Ba3a7) to approximately 300 user Universal Profiles, then moved assets. Approximately 1.4 million LYX was extracted, bridged to Ethereum, and swapped for roughly 50 ETH (~$95,000). The LUKSO blockchain and Universal Profile smart contracts were unaffected. The email recovery system was disabled. The project is working on a solution for affected users and published a post-mortem. Users who used email recovery were advised to remove the attacker key.
Protocol / chain / asset: LUKSO Universal Profiles email recovery backend. Asset: LYX. Official post-mortem from LUKSO / @LUKSO_io.
Loss: ~1.4 million LYX extracted; realized proceeds after swap approximately 50 ETH (~$95,000). Live scored on this brief as the realized ~$95K figure pending any reimbursement. Market value of stolen LYX was higher at the time of extraction.
Attack type: Backend vulnerability in centralized email recovery service allowing unauthorized controller key addition. Smart contracts and chain consensus unaffected.
Explorer URLs: Attacker controller referenced in post-mortem. Bridged LYX and ETH sink addresses documented in secondary on-chain reviews (The Defiant).
Status: Confirmed by official post-mortem. System disabled. Reimbursement plan under discussion. Affected users must remove attacker key.
Sources: LUKSO post-mortem (Medium, 18 Nov); @LUKSO_io announcement; The Defiant; CoinMarketCap Academy.
Also noted
- Peapods Finance (UPDATE / key compromise): Deployer key reportedly used to set minters on L2 PEAS contracts, mint tokens, bridge to mainnet, and sell. Team removed 98–99% of L2 liquidity, advised users to exit LP/LVF positions, and is pursuing recovery and a post-mortem. No quantified user-loss figure scored as first-report protocol drain in this window.
- Prior items (UPDATE): B18TimeBank Base voucher redemption (~$405K, 18 Nov brief), Lighter nonce reuse (~$10.4M, 17 Nov brief), Curve CowSwapBurner fee disclosure, and earlier items remain without material new first-report scored losses in the last 24 hours.
- Other notes: No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts in the last 24 hours beyond the four items above. Quiet window otherwise for new scored protocol losses.
Sources and references
- SlowMist on K3 Capital: https://x.com/SlowMist_Team/status/2123065339407991018
- Bitquery K3 Capital investigation: https://bitquery.io/investigations/k3-capital-sbold-hack
- Blockaid on Gonka: https://x.com/blockaid_/status/2123121262079664399
- Gonka AI funds returned: https://x.com/gonka_ai/status/2123344126276149308
- Blockaid on Reental/RNT Lend: https://x.com/blockaid_/status/2123033403553689899
- DefimonAlerts on Reental: https://x.com/DefimonAlerts/status/2123036062108836145
- Bitquery Reental investigation: https://bitquery.io/investigations/reental-rnt-lend-drain
- LUKSO post-mortem: https://medium.com/@lukso/post-mortem-security-incident-in-the-email-based-recovery-system-029f6f241e2b
- Peapods Finance statement: https://x.com/PeapodsFinance/status/2123088545573118150
- 18 Nov brief (B18TimeBank): https://www.rektradar.xyz/web3-daily-exploits-18-nov-2026-b18-405k-base-curve-38k/
Editor’s note: the scored live loss on this card is ~$5.5M across four first-report incidents (K3 Capital sBOLD share-accounting drain ~$3.42M on Ethereum; Gonka AI bridge ~$1.05M on Ethereum with confirmed full return; RNT Lend ~$955K on Polygon; LUKSO email recovery realized ~$95K). Figures based on on-chain measurements and contemporaneous security firm reports. Gonka return is confirmed by the project. Peapods remains an unquantified key-compromise note. Prior items remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 18 Nov 2026: B18 ~$405K Base Drain
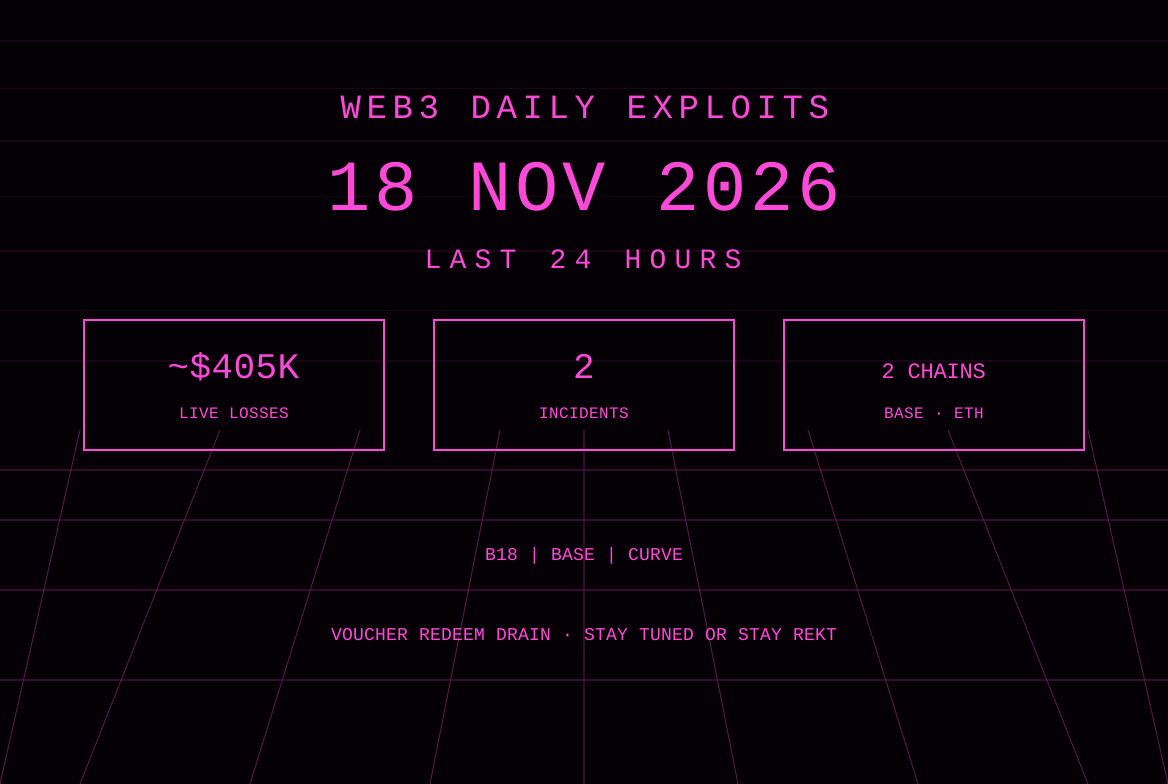
First-report incident: B18TimeBank on Base saw ~404,540 USDC withdrawn after redemption of signed level-reward vouchers. ~106,785 USDC remained in the settlement contract at a later check; containment unconfirmed. Curve disclosed ~$38.2K DAO fee revenue taken from CowSwapBurner on 10 Nov via order-check flaw.
Web3 Daily Exploits — 17 Nov 2026: Lighter ~$10.4M Nonce Reuse
First-report incident: Lighter (Ethereum L2 perp DEX) saw ~$10.4M USDC withdrawn after unofficial signing code reused nonces, allowing API private key recovery from public signatures. ~$5M returned by Security Council; protocol unaffected. Optimizely OPTIMJACK supply-chain clipper noted with small crypto losses.
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.