Web3 Daily Exploits — 18 Nov 2026: B18 ~$405K Base Drain
First-report incident: B18TimeBank on Base saw ~404,540 USDC withdrawn after redemption of signed level-reward vouchers. ~106,785 USDC remained in the settlement contract at a later check; containment unconfirmed. Curve disclosed ~$38.2K DAO fee revenue taken from CowSwapBurner on 10 Nov via order-check flaw.
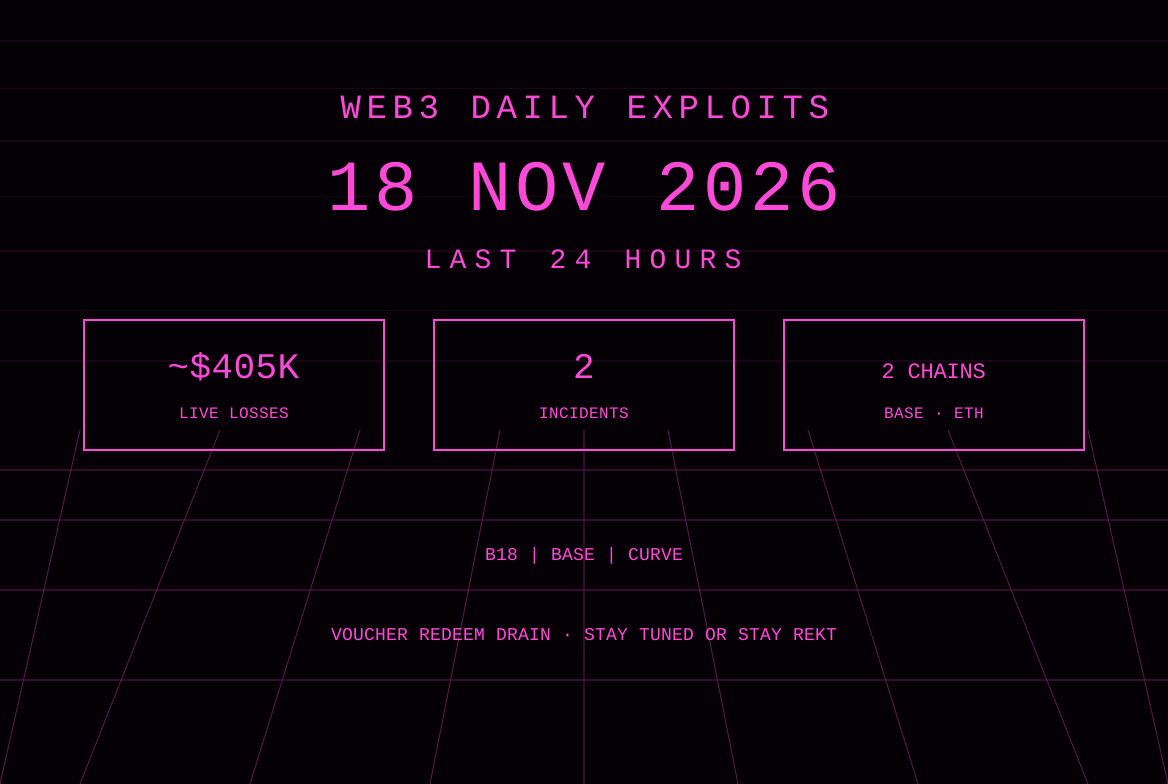
The 18 Nov America/Panama window records one first-reported protocol incident with an on-chain-confirmed scored loss of approximately $405,000 and one material disclosure of a prior fee-conversion incident. B18TimeBank, a time-based settlement protocol on Base, experienced a drain in which an address identified by Blockaid redeemed signed level-reward vouchers and withdrew 404,540.468304 USDC from the protocol’s settlement contract in a single transaction at approximately 13:50 ET on 17 November. A subsequent BaseScan check showed about 106,785 USDC still present in the settlement contract; whether those residual funds remained accessible through the same path, and the total depositor exposure across the protocol, were unconfirmed at the time of reporting. Separately, Curve Finance publicly disclosed on 17 November that an attacker had taken approximately $38,200 of DAO fee revenue from its Ethereum CowSwapBurner contract on 10 November by exploiting a missing order-hash check. Curve stated that no user funds, pools, lending markets, or crvUSD were affected. No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures appeared from monitored accounts in the same window. Prior items remain UPDATEs.
B18TimeBank — Base — ~$405K — signed voucher redemption / settlement drain
What happened: On 17 November 2026, Blockaid reported that an address it identified as an attacker redeemed digitally authorized level-reward vouchers at B18TimeBank on Base and withdrew corresponding USDC from the protocol’s settlement contract. On-chain records independently confirm a single transfer of 404,540.468304 USDC from the identified settlement contract to the flagged address at 1:50:59 p.m. ET. A later check of the same contract on BaseScan showed approximately 106,785 USDC remaining. The pool identified by Blockaid held zero USDC at a subsequent check but retained roughly 408,192 B18 tokens; the withdrawal transaction itself recorded 790,000 B18 tokens moving from that pool to the settlement contract before the USDC payout. Funds began moving onward, with one later transaction showing the flagged recipient sending about 104,533 USDC to another address. B18 documentation describes users depositing into time-based products that settle at maturity with principal and accrued value. The balances observed in the two identified contracts do not represent protocol-wide deposits; total depositor exposure has not been established. Containment of the remaining balance was unconfirmed at the time of the reports.
Protocol / chain / asset: B18TimeBank (time-based settlement protocol) on Base. Primary asset: USDC. Observations drawn from Blockaid reporting and independent BaseScan confirmation. No official project statement on the incident was located in the monitored window.
Loss: On-chain confirmed withdrawal: 404,540.468304 USDC (~$405,000) in a single transaction. Residual balance of ~106,785 USDC observed later in the settlement contract. Live scored on this brief: ~$405K (confirmed withdrawal). Final net loss, any further drains of residual funds, and total depositor exposure remain under investigation.
Attack type: Redemption of signed level-reward vouchers followed by USDC withdrawal from the settlement contract. The precise voucher-signing or authorization logic that permitted the redemptions was not detailed in public reports. Not characterized as a classic reentrancy or oracle manipulation in the available accounts.
Explorer URLs: BaseScan transaction confirming the 404,540.468304 USDC transfer (referenced in contemporaneous reporting; readers are directed to BaseScan for the full hash and contract addresses identified by Blockaid). Settlement contract balance checks and subsequent movements documented in The Defiant and TokenPost coverage.
Status: Confirmed by on-chain data and Blockaid. Containment of residual funds unconfirmed. Total depositor exposure not established. Flag any project response, residual drain, or quantified recovery as material.
Sources: Blockaid reporting as covered by The Defiant and TokenPost (17 Nov); Odaily and secondary Chinese-language flashes; BaseScan confirmation of the payout amount and timing.
Curve Finance — Ethereum — ~$38.2K — order-check flaw / fee burner (UPDATE / disclosure)
What happened: On 17 November 2026, Curve Finance disclosed that an attacker had taken about $38,200 of DAO fee revenue from the CowSwapBurner contract on Ethereum on 10 November. The burner is the contract that sells collected admin fees for crvUSD during a scheduled window. The contract checked the order it was shown on CoW Protocol rather than the order being executed. The attacker used this gap to submit forged orders that sold accumulated token balances (mostly below the burner’s normal minimum) to an attacker-controlled address. Curve reviewed 6,558 settled burner orders since deployment and found that only the disclosed forged orders paid somewhere other than the FeeCollector. The 138 forged orders produced 38,205.76 USDC; the regular weekly conversion still delivered 97,317.74 crvUSD to the FeeCollector. The Emergency DAO disabled the affected machinery at 13:59 UTC on the day of the incident and paused Ethereum fee conversion (fees continue to accrue). A DAO vote on a replacement burner closes 20 November. The attacker swapped the majority of proceeds to ETH, bridged to Arbitrum, and deposited into Hyperliquid within four hours. No user funds, pools, lending markets, or crvUSD were involved. A parallel investigation noted that Balancer’s fee burner had been drained by the same class of flaw on 24 October for a smaller amount; that earlier incident is outside this window.
Protocol / chain / asset: Curve Finance fee-conversion machinery (CowSwapBurner) on Ethereum. Asset: accumulated DAO fee tokens converted to USDC. Official disclosure from @CurveFinance. User deposits and core protocol contracts unaffected.
Loss: 38,205.76 USDC (~$38,200) of DAO fee revenue. No user funds affected. Live scored on this brief as a disclosed prior incident rather than a fresh first-report drain. Stolen proceeds unrecovered at the time of disclosure.
Attack type: Missing order-hash / order-identity check in the CoW Protocol integration of the fee burner. Forged orders were accepted because the contract validated the displayed order rather than the executed one. Not a user-fund or pool vulnerability.
Explorer URLs: Ethereum CowSwapBurner and related FeeCollector contracts referenced in Curve’s disclosure thread and secondary analyses (Bitquery, DefiPrime). Individual forged-order hashes and attacker exit paths documented in those publications; readers are directed there for full transaction lists.
Status: Confirmed by Curve official disclosure. User funds safe. Fee conversion on Ethereum paused pending governance vote on a replacement burner (closes 20 Nov). Funds unrecovered. Labeled UPDATE because the on-chain activity occurred on 10 November; the material public disclosure falls inside the last-24h window.
Sources: @CurveFinance thread (17 Nov); Curve incident disclosure; secondary coverage (DefiPrime, Altcoin Buzz, Phemex, Bitquery parallel analysis).
Also noted
- Lighter nonce-reuse / API key recovery (UPDATE): Withdrawals were restored after the Lighter Security Council returned approximately $5 million USDC to the affected trader. The on-chain confirmed withdrawal of ~10.4 million USDC on 16 November remains as previously scored. Protocol, smart contracts, and official SDKs were unaffected. See the 17 Nov brief for full detail.
- Optimizely OPTIMJACK supply-chain clipper (UPDATE): Malicious JavaScript injected into Optimizely Web Experimentation snippets serving 178 organizations (including Ledger) continued to be discussed. Payload performed cryptocurrency address swapping, card skimming, and other data theft. Victim crypto losses remain in the low thousands of dollars per on-chain tracing. Not a protocol drain.
- Binance prior hacker (UPDATE / laundering): Lookonchain reported continued movement of holdings from the earlier Binance-related attacker address, with additional ETH transferred and swapped toward BTC via THORChain. No new first-report loss figure.
- Prior items (UPDATE): Kava Lend arithmetic, Chain Games reward-checkpoint, Pool Party, and earlier items remain without material new first-report scored losses in the last 24 hours.
- Other notes: No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts in the last 24 hours beyond the B18TimeBank item. Curve is scored as a material disclosure of a prior incident. Quiet window otherwise for new scored protocol losses.
Sources and references
- The Defiant on B18TimeBank: https://thedefiant.io/news/hacks/blockaid-says-b18timebank-exploit-drained-404-540-usdc
- TokenPost on B18TimeBank: https://www.tokenpost.com/news/technology/59807
- Curve Finance disclosure: https://x.com/CurveFinance/status/2122732497419288904
- DefiPrime on Curve CowSwapBurner: https://defiprime.com/curve-cowswapburner-fee-theft-disclosure
- Bitquery on Balancer/Curve fee-burner pattern: https://bitquery.io/investigations/balancer-hack-cowswap-fee-burner
- 17 Nov brief (Lighter): https://www.rektradar.xyz/web3-daily-exploits-17-nov-2026-lighter-10-4m-nonce/
- SlowMist OPTIMJACK alert: https://x.com/SlowMist_Team/status/2122579014346776653
- Lookonchain Binance laundering updates: https://x.com/lookonchain/status/2122997562877821143
- Monitored accounts checked through the 18 Nov 2026 America/Panama cutoff. No additional first-report protocol exploits with fresh scored user-loss figures beyond B18TimeBank.
Editor’s note: the scored live loss on this card is ~$405K across one first-report incident (B18TimeBank signed-voucher redemption enabling a USDC withdrawal from the Base settlement contract). Figure based on on-chain measured USDC transfer. Residual balance and total depositor exposure remain unconfirmed. Curve’s ~$38.2K DAO fee disclosure is included as a material public update of a 10 November incident; user funds were unaffected. Lighter and Optimizely remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 19 Nov 2026: K3 ~$3.4M sBOLD Share Accounting
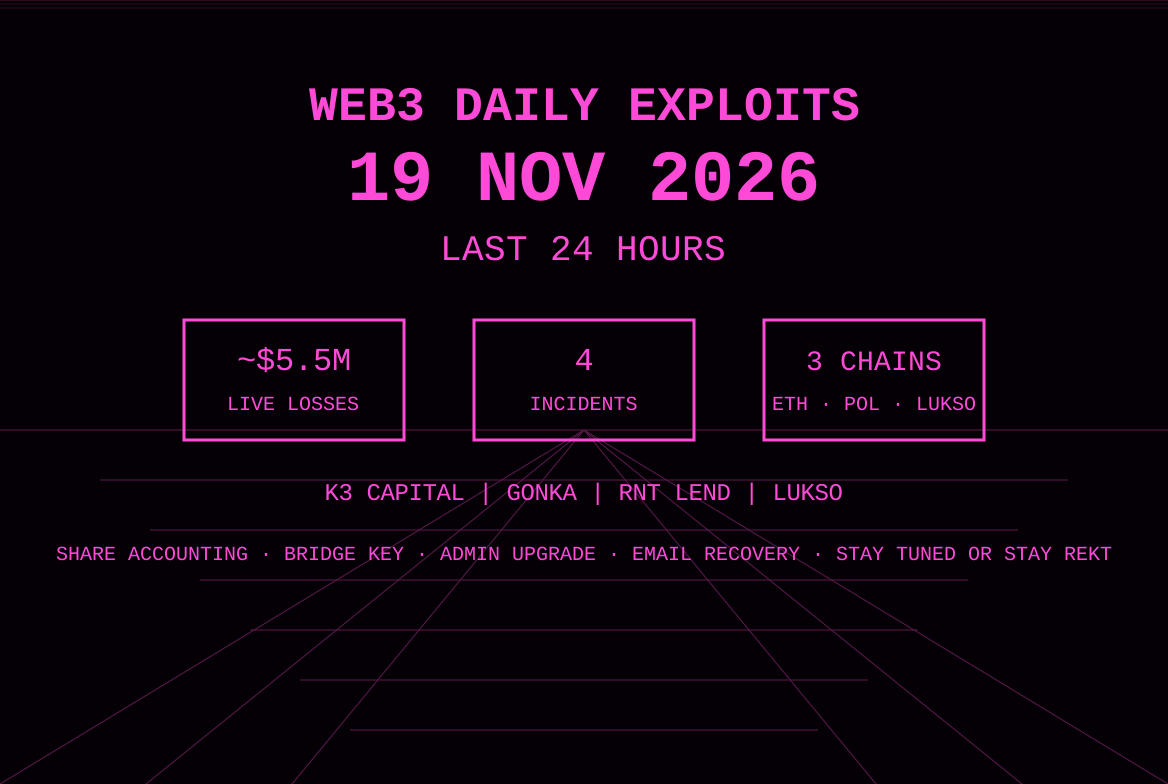
First-report incidents: K3 Capital sBOLD vault on Ethereum drained ~$3.42M via share-accounting mismatch allowing flash-loaned assets to inflate redemption value. Gonka AI Ethereum bridge lost ~$1.05M after BLS key rotation (funds confirmed returned). RNT Lend on Polygon saw ~$955K stablecoins taken after admin upgrade of aToken proxies. LUKSO email recovery backend flaw affected ~300 profiles for ~1.4M LYX.
Web3 Daily Exploits — 17 Nov 2026: Lighter ~$10.4M Nonce Reuse
First-report incident: Lighter (Ethereum L2 perp DEX) saw ~$10.4M USDC withdrawn after unofficial signing code reused nonces, allowing API private key recovery from public signatures. ~$5M returned by Security Council; protocol unaffected. Optimizely OPTIMJACK supply-chain clipper noted with small crypto losses.
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.