Web3 Daily Exploits — 17 Nov 2026: Lighter ~$10.4M Nonce Reuse
First-report incident: Lighter (Ethereum L2 perp DEX) saw ~$10.4M USDC withdrawn after unofficial signing code reused nonces, allowing API private key recovery from public signatures. ~$5M returned by Security Council; protocol unaffected. Optimizely OPTIMJACK supply-chain clipper noted with small crypto losses.
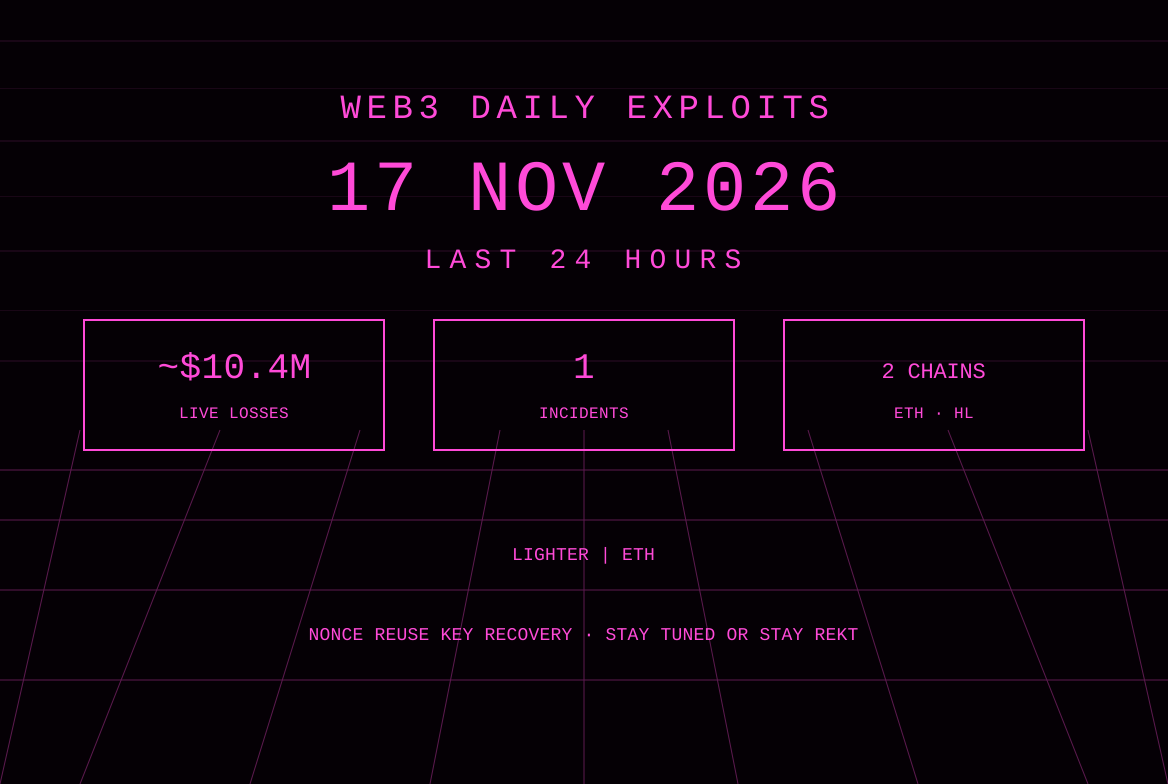
The 17 Nov America/Panama window records one first-reported trading-platform incident with on-chain-confirmed scored loss of approximately $10.4 million. Lighter, an Ethereum Layer-2 perpetual futures exchange, experienced an incident on 16 November in which an attacker recovered API private keys for affected trader accounts from publicly visible signatures. The accounts had used unofficial or custom signing code that reused cryptographic nonces. Reuse of a signing nonce with the same key across different messages allows anyone observing the signatures to compute the private key. Lighter stated that its protocol, smart contracts, infrastructure, and official SDKs were unaffected. On-chain data show a withdrawal of 10,393,057 USDC from Lighter’s Ethereum settlement contract at approximately 10:11 UTC on 16 November to an address later flagged by the project (0xb3fffca23d4444eE73349825ACD84f7b5020e387). The funds were rapidly swapped to ETH; a portion moved onward via routers toward Hyperliquid positions in XMR1. Researchers estimated potential exposure across two market-maker accounts at roughly $15.5 million; Lighter has not confirmed the higher figure. The platform’s Guardian mechanism paused withdrawals, enabling the Lighter Security Council to return approximately $5 million USDC to the affected trader. Withdrawals and deposits were restored later on 16 November after Guardian mode was disabled. In parallel, a large-scale JavaScript supply-chain attack (OPTIMJACK) injected malicious code into Optimizely Web Experimentation snippets serving 178 organizations, including Ledger. The payload performed cryptocurrency address swapping (clipper), card skimming, and other data theft; on-chain tracing places victim crypto losses in the low thousands of dollars. No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures appeared from monitored accounts in the same window. Prior items remain UPDATEs.
Lighter — Ethereum / Hyperliquid — ~$10.4M — nonce reuse / API key recovery
What happened: On 16 November 2026, an attacker recovered API private keys belonging to one or more trader accounts on Lighter by observing publicly available signatures. The affected accounts had employed unofficial or custom signing software that reused cryptographic nonces across different transactions. Because signatures are public, nonce reuse allows reconstruction of the private key from the signature pair. Lighter confirmed the root cause lay outside its official SDKs and that the protocol, smart contracts, and infrastructure were not compromised. With the recovered keys the attacker created a public pool from the compromised account, minted pool shares to an attacker-controlled account, transferred victim funds into the pool (increasing NAV without issuing corresponding shares to the victim), and redeemed the shares to withdraw. On-chain analysis (Bitquery and others) documented a single large withdrawal of 10,393,057 USDC from Lighter’s Ethereum contract at 10:11 UTC to 0xb3fffca23d4444eE73349825ACD84f7b5020e387. The USDC was swapped to approximately 5,764 ETH within minutes on CoW Swap; subsequent transfers of 160 ETH each moved funds via LI.FI toward Hyperliquid accounts that purchased XMR1. GoPlus and other researchers described two accounts (IDs 714710 and 714723) with combined reported exposure near $15.5 million. Lighter’s Guardian mode was triggered, pausing withdrawals and pool creation; the Security Council returned roughly $5 million USDC to the affected trader. Guardian mode was later disabled and normal deposit/withdrawal operations resumed. The project has required wallet signatures for transfers into public pools, made API signatures non-public, and announced plans for IP allowlisting, per-key permissions/limits, and nonce-reuse monitoring. Users of custom signing code were advised to rotate keys and switch to official SDKs.
Protocol / chain / asset: Lighter perpetual futures exchange (Ethereum L2 settlement). Primary asset: USDC. Exit path observed on Ethereum then toward Hyperliquid. Official statements from @Lighter_xyz; on-chain tracing by Bitquery, GoPlus, and community analysts.
Loss: On-chain confirmed withdrawal: 10,393,057 USDC (~$10.4 million) at 10:11 UTC on 16 November. Researchers estimate total affected balances across two accounts near $15.5 million; Lighter has not independently confirmed the higher figure. Approximately $5 million USDC returned by the Security Council. Live scored on this brief: ~$10.4M (confirmed withdrawal). Residual holdings, any further recovery, and final realized loss after the partial return remain under investigation.
Attack type: Cryptographic / key recovery via nonce reuse in unofficial signing code. Not a protocol or smart-contract vulnerability. Official SDKs generate nonces securely and were unaffected. Guardian mechanism limited further damage and enabled partial recovery.
Explorer URLs: Attacker-associated address: https://etherscan.io/address/0xb3fffca23d4444eE73349825ACD84f7b5020e387. Lighter Ethereum settlement contract referenced in on-chain analyses (Bitquery: https://bitquery.io/investigations/lighter-hack). Full transaction set and Hyperliquid XMR1 purchases documented in published investigations; readers are directed to those for individual hashes. Affected account identifiers: 714710 (on-chain address 0x0d1D09312665D31Ed68231b88079a245E0458F6F) and 714723 (0x66Cf2f85115CC20bF439720927C1f93De9672068).
Status: Confirmed by on-chain data and Lighter official statements. Protocol unaffected. Partial recovery completed (~$5M USDC). Withdrawals restored. Investigation and any residual fund movement continue. Flag any quantified additional recovery or detailed technical post-mortem as material.
Sources: @Lighter_xyz updates and postmortem (16 Nov); GoPlus Security breakdown (17 Nov); Bitquery investigation; secondary coverage (The Block, CoinDesk, Cointelegraph, Decrypt-adjacent reporting).
Also noted
- Optimizely OPTIMJACK (supply-chain / crypto clipper, small scored loss): On 16 November attackers injected malicious JavaScript into Optimizely Web Experimentation project snippets serving at least 178 organizations (including Ledger, CNN, BBC, Zoom, HSBC, and others). The payload swapped cryptocurrency wallet addresses in page content, form fields, and the clipboard (clipper behavior across BTC, ETH, TRON, SOL, TON, LTC and others), skimmed card data, stole cookies/screenshots, and attempted to deliver Coruna/DarkSword exploit kits to certain iOS versions. Optimizely stated the vulnerable path was blocked, injected code removed, and customers contacted. Report URI and Bitquery traced attacker wallets; initial tallies near $7K included the attacker’s own swaps, while victim-paid amounts are approximately $2,260 across 19 payments on five chains. Wallets were later emptied. Not a protocol drain; relevant as a Web3-impacting supply-chain attack. Flagged with small confirmed crypto loss.
- Binance prior hacker (UPDATE / laundering): Lookonchain reported on 17 Nov that the earlier Binance-related attacker address began moving holdings, transferring 74,880 ETH (~$136.8M) over three hours and swapping toward BTC via THORChain. No new first-report loss figure; prior incident remains an UPDATE. Residual holdings continue under monitoring.
- Prior items (UPDATE): Chain Games reward-checkpoint drain (~$20K, 16 Nov brief), Kava Lend arithmetic (~$3.7M, 15 Nov brief), Pool Party, Pennysia, and earlier items remain without material new first-report scored losses in the last 24 hours.
- Other notes: No additional first-report protocol or smart-contract drains with fresh confirmed user-loss figures from monitored accounts (DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news) in the last 24 hours beyond the Lighter item. Quiet window otherwise for scored protocol losses. Optimizely remains a supply-chain note with limited crypto impact.
Sources and references
- Lighter official updates: https://x.com/Lighter_xyz/status/2122394646164758654, https://x.com/Lighter_xyz/status/2122311006604984497, https://x.com/Lighter_xyz/status/2122284181422284986
- GoPlus Security Lighter breakdown: https://x.com/GoPlusSecurity/status/2122520900046319815
- Bitquery Lighter investigation: https://bitquery.io/investigations/lighter-hack
- SlowMist OPTIMJACK alert: https://x.com/SlowMist_Team/status/2122579014346776653
- GoPlus OPTIMJACK alert: https://x.com/GoPlusSecurity/status/2122542150080774563
- CertiK Optimizely insight: https://x.com/CertiKAlert/status/2122620774775419198
- Bitquery Optimizely investigation: https://bitquery.io/investigations/optimizely-hack
- Lookonchain Binance laundering update: https://x.com/lookonchain/status/2122633788127940768
- 16 Nov brief (Chain Games): https://www.rektradar.xyz/web3-daily-exploits-16-nov-2026-chaingames-20k-reward-checkpoint/
- Monitored accounts checked through the 17 Nov 2026 America/Panama cutoff. No additional first-report protocol exploits with fresh scored user-loss figures beyond Lighter.
Editor’s note: the scored live loss on this card is ~$10.4M across one first-report incident (Lighter nonce reuse enabling API key recovery on Ethereum settlement, with subsequent movement toward Hyperliquid). Figure based on on-chain measured USDC withdrawal. Researchers estimate higher exposure near $15.5M across two accounts; Lighter has not confirmed that total. Approximately $5M USDC was returned by the Security Council. Optimizely OPTIMJACK is noted as a supply-chain clipper with victim crypto losses in the low thousands. Prior items remain UPDATEs. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
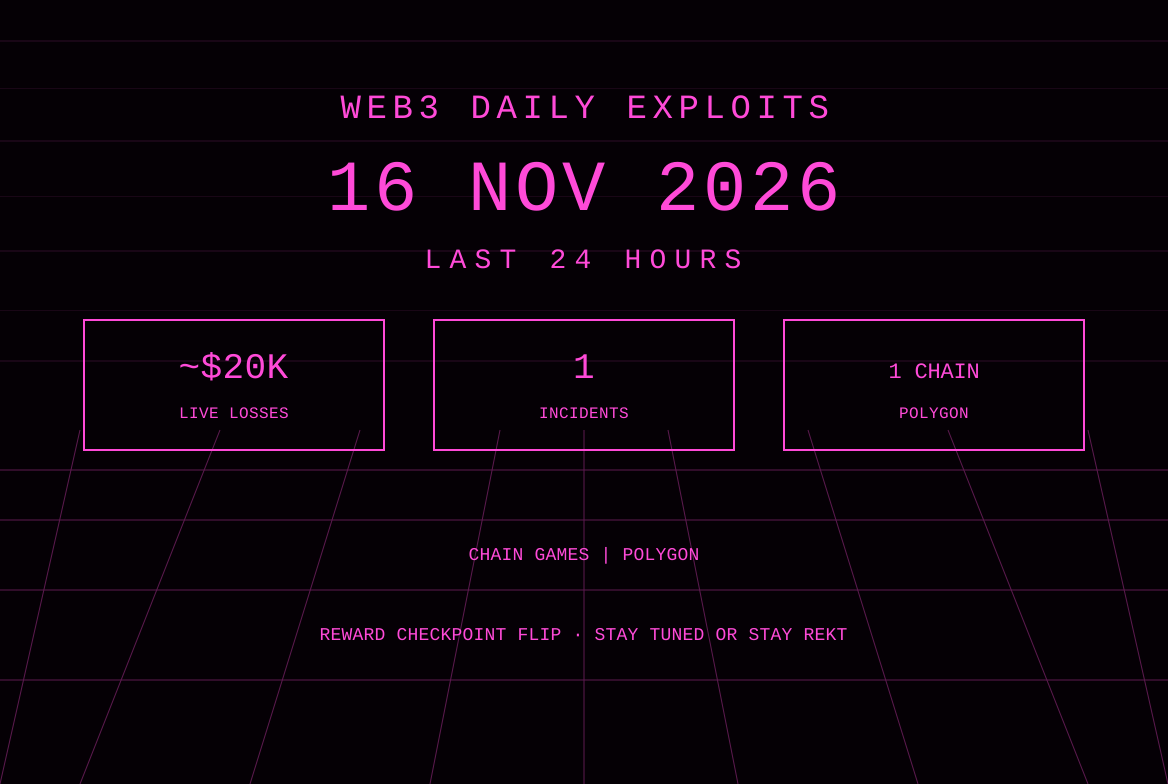
Web3 Daily Exploits — 16 Nov 2026: Chain Games ~$20K Reward Checkpoint
First-report incident: Chain Games (RealChainGames) staking contracts on Polygon drained ~$20K via reward checkpoint desync on share transfers. Attacker inflated 1,000 CHAIN shares to 36M+ across 360 cycles and withdrew. Kava Lend official report released confirming 53.9M KAVA and exploit blocked. Luxor Commander hashrate redirect noted.
Web3 Daily Exploits — 15 Nov 2026: Kava Lend ~$3.7M Arithmetic
First-report incident: Kava Lend on Kava chain drained ~$3.7M via arithmetic error in dormant BUSD market interest index (243,000x inflation). ~55.2M KAVA borrowed; most bridged to BNB and sold. HyprEarn unauthorized trading and CODA/OPUS vault note remain unquantified.
Web3 Daily Exploits — 14 Nov 2026: Pool Party ~$215K Snapshot
First-report incident: Pool Party snapshot contracts on Arbitrum and Base exploited via recorded position manipulation (~$215K, 15 pools). Fix deployed; funds converted toward XMR. Independent tracing notes ~$212.7K USDC laundering leg. Pennysia, Edel, Rujira remain UPDATEs.
Web3 Daily Exploits — 13 Nov 2026: Pennysia ~$5K + Edel ~$300K
First-report incidents: Pennysia Settlement V1 on Ethereum exploited via arbitrary external call (~$5K observed in reported tx, residual approvals at risk); Edel Finance ~$300K EDEL tokens stolen and sold/blocked. Rujira, Across, Initia, Arcus remain UPDATEs.