Web3 Daily Exploits — 2 Nov 2026: Quiet Window After Premia GoPlus Breakdown
Quiet day in the last 24 hours: no new first-reported protocol drains with scored live losses. GoPlus published a detailed breakdown of the prior PremiaLabs Arbitrum options vault incident (~$465K, already scored 1 Nov). Pando Rings 2022 exploiter moved additional funds to Tornado Cash. Binance remains an UPDATE. Live losses ~$0 for new items.
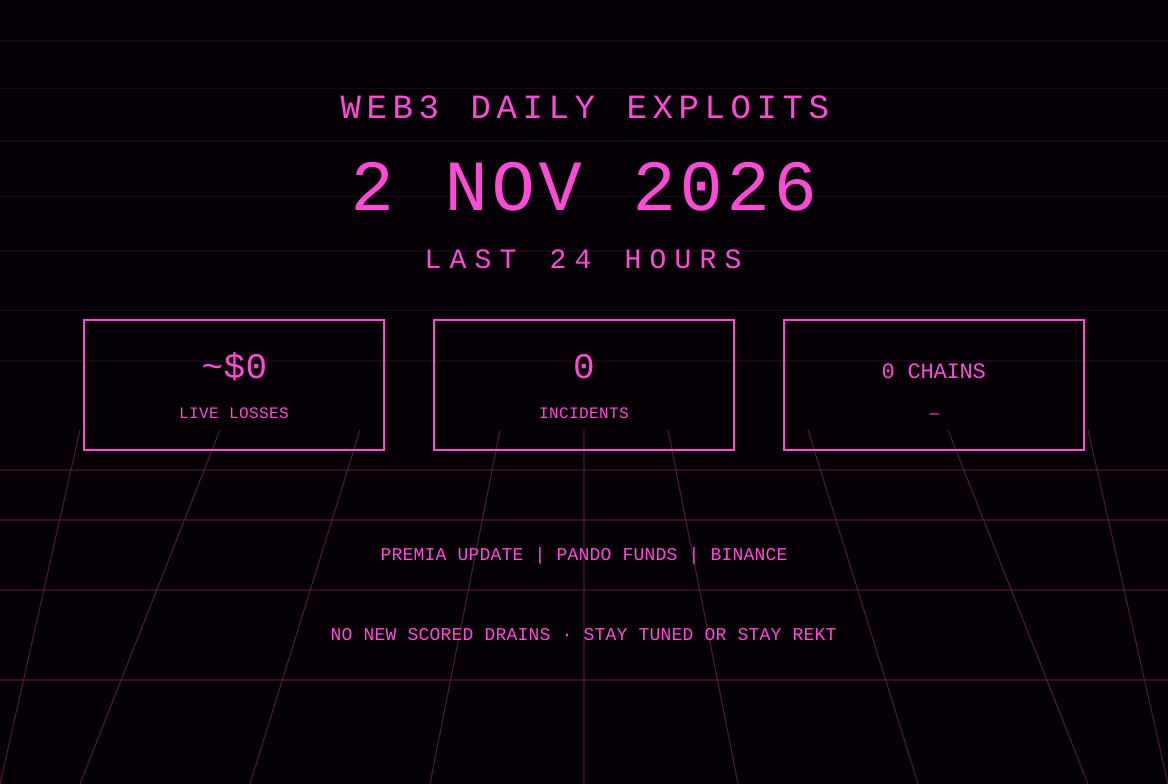
The 2 Nov America/Panama window records no first-reported or materially new protocol or smart-contract drains used for scoring. Recheck of monitored accounts confirmed a quiet period after the 1 Nov PremiaLabs, Troves and b14g items. GoPlus Security published a 13-part technical breakdown of the Premia options vault attack on Arbitrum (already scored at ~$465K on the prior brief). Separately, the labeled Pando Rings 2022 exploiter moved additional ETH toward Tornado Cash after Aave activity. The prior Binance hot-wallet signing-access compromise (~$6.3B) remains an UPDATE; ongoing laundering notes and regulatory responses are recorded but not re-scored. Combined live loss on this card is ~$0 for newly scored items.
PremiaLabs — Arbitrum — ~$465K (UPDATE, already scored) — empty option pools / flash-loan liquidity extraction
What happened: On 2 November 2026, GoPlus Security released a detailed multi-post analysis of the PremiaLabs options vault exploit that occurred early on 1 November UTC. The thread confirms the permissionless factory allowed deployment of empty option pools, which underwriter vaults then treated as legitimate markets without sufficient checks on liquidity or age. An attacker flash-loaned capital, purchased options to lock vault collateral into the empty pools, and extracted it via liquidity mechanisms. Example details match prior reporting: for the pSV-WBTC/USDCe-C vault (0x45dF5EA836A15B561937Ae8373ab9eE984aea531), a purchase locked 3.76125 WBTC collateral; the attacker then adjusted LP positions and withdrew approximately 4.4904 WBTC from the pool in the same transaction. Two main exploit transactions were executed roughly one second apart. Affected vaults included WBTC, WETH and ARB call and put series. This does not represent a new incident or additional loss; it is a post-incident forensic breakdown of the item already scored on the 1 Nov brief.
Protocol / chain / asset: PremiaLabs decentralized options protocol on Arbitrum. Assets previously extracted included WBTC, WETH, USDC.e and ARB. No new extraction reported in the GoPlus thread.
Loss: No new loss figure. Prior scored amount remains ~$465K (PeckShield); contemporaneous estimates ranged $400.5K–$464.6K. Not re-scored today.
Attack type: Options vault / pool mechanics abuse via empty pool creation and liquidity extraction. Confirmed as an accounting / validation gap on pool safety rather than a classic reentrancy or oracle issue.
Explorer URLs: Attacker EOA: https://arbiscan.io/address/0xbeBa8CEfD0D75d747C5AD966Dc17C0Bb60D84dBd. Attack contract: https://arbiscan.io/address/0x577168C8c6fA937495C3D6961f1d7D734b2d785f. Example tx: https://arbiscan.io/tx/0x64602cbbeba5d3c7a5e2cff4f98cc118886fc6051c56fa50458abec2c90441ac. Second tx: https://arbiscan.io/tx/0xd7e8086df0570c5389ca27eb9bcdff290e810c094155b410a42e5bad2b3244ff. Vault examples: https://arbiscan.io/address/0x45dF5EA836A15B561937Ae8373ab9eE984aea531. Arbiscan: https://arbiscan.io/.
Status: Prior incident already contained relative to the vaults; funds previously bridged and swapped. GoPlus analysis adds technical detail but no recovery announcement or new loss. Treat as confirmed prior drain.
Sources: GoPlus Security thread: https://x.com/GoPlusSecurity/status/2117191582361555366. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-01-nov-2026-premia-465k-troves-legacy-perm/.
Also noted
- Pando Rings 2022 exploiter funds movement (UPDATE, not re-scored): PeckShieldAlert and Lookonchain noted that the address linked to the November 2022 Pando Rings oracle exploit (~$20M at the time) supplied 16.8M USDT to Aave on or around 30 October, borrowed 5K ETH, repaid and withdrew collateral, then swapped ~16.7M DAI for 7,548 ETH and deposited 4,000 ETH into Tornado Cash. This is movement of previously stolen funds from a multi-year-old incident, not a new protocol drain. No new loss figure. Lookonchain: https://x.com/lookonchain/status/2117175914702553312. PeckShield: https://x.com/PeckShieldAlert/status/2117149190904270969.
- Binance hot-wallet signing-access compromise (UPDATE, not re-scored): The ~$6.3 billion multi-chain drain from 29 October remains on prior briefs. Ongoing notes include further fund movements, regulatory responses (including South Korean guidance on cold-wallet holdings), and continued attribution discussions to North Korean actors. Binance has covered losses and restored many withdrawals. No material new loss figures used for scoring today. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-30-oct-2026-binance-63b-eip7702-polymarket-debugbear/.
- DeFi frontend DNS / StepDrainer wave (UPDATE, not re-scored): Later reporting quantified approximate losses from the 31 October Name.com-linked DNS hijacks of Flap, Kintsu and additional sites at around $138K. The incident was first-reported and briefed on 31 Oct with no published figure at the time. Sites were restored; no new first-report today. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-31-oct-2026-flap-kintsu-dns-stepdrainer/.
- Prior items (not re-scored): Troves, b14g, zkLink Nova, Avalanche TranchePool and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures in the last 24 hours.
Sources and references
- GoPlus Premia breakdown thread: https://x.com/GoPlusSecurity/status/2117191582361555366
- 1 Nov brief for Premia/Troves/b14g: https://www.rektradar.xyz/web3-daily-exploits-01-nov-2026-premia-465k-troves-legacy-perm/
- Lookonchain Pando Rings funds: https://x.com/lookonchain/status/2117175914702553312
- PeckShieldAlert Pando Rings: https://x.com/PeckShieldAlert/status/2117149190904270969
- 30 Oct brief for Binance: https://www.rektradar.xyz/web3-daily-exploits-30-oct-2026-binance-63b-eip7702-polymarket-debugbear/
- 31 Oct brief for DNS/StepDrainer: https://www.rektradar.xyz/web3-daily-exploits-31-oct-2026-flap-kintsu-dns-stepdrainer/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is ~$0. No newly reported or materially updated items with fresh loss figures were identified. The GoPlus Premia breakdown, Pando Rings funds movement and Binance notes are UPDATES and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more

Web3 Daily Exploits — 1 Nov 2026: Premia $465K Arbitrum Options Drain, Troves 8.6 BTC Legacy Perm, b14g 97M CORE Zero-Withdraw
PremiaLabs vaults on Arbitrum drained ~$465K via empty option pools and flash-loan liquidity extraction. Troves xWBTC/WBTC vault on Starknet lost ~8.6 BTC through a legacy rebalancing contract that retained permissions. b14g dual-staking on Core lost ~97M CORE (~$1.47M) when zero-amount withdrawal requests were treated as full balances. Live losses ~$2.6M across 3 incidents. Binance remains an UPDATE.
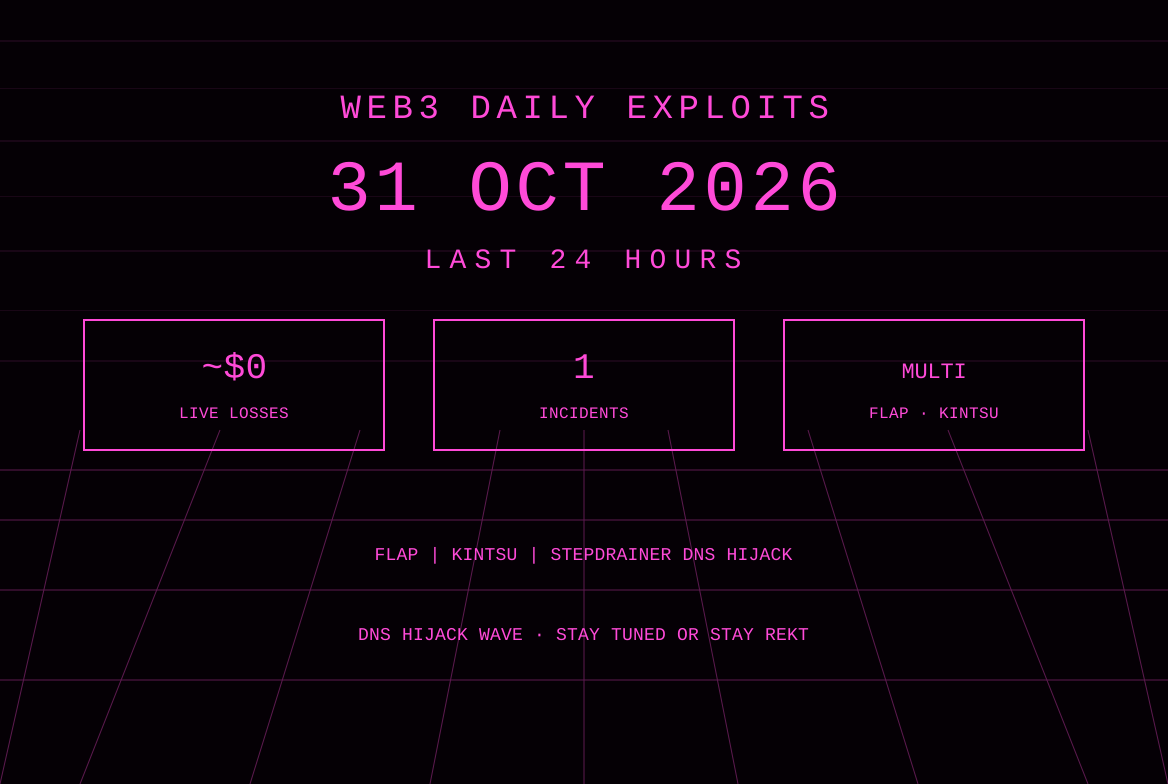
Web3 Daily Exploits — 31 Oct 2026: Flap & Kintsu DNS Hijack Wave (StepDrainer), No New Scored Protocol Drains
Flap.sh and Kintsu.xyz (plus at least 10 other DeFi sites) suffered DNS hijacks on 31 October, redirecting users to StepDrainer wallet-drainer clones. No confirmed loss figure published. Live loss ~$0 for new scored items, 1 incident. Binance ~$6.3B remains an UPDATE with multi-breach notes, ~$3B frozen and $6.34B reserved.
Web3 Daily Exploits — 30 Oct 2026: Binance ~$6.3B Hot Wallet EIP-7702 Takeover & Polymarket DebugBear Drain
Binance hot wallets lost an estimated ~$6.3B across multiple chains after signing access was used to install an EIP-7702 delegation on Binance 14 and submit unauthorized withdrawals; ~$3B frozen. Polymarket international site lost ~$2.5-2.71M via a compromised DebugBear RUM script that abused logged-in sessions. Live loss ~$6.3B, 2 incidents, ETH · BTC · TRX · POL. zkLink Nova remains an UPDATE.
Web3 Daily Exploits — 29 Oct 2026: zkLink Nova ~$0.78M Arbitrator Forged Batch Root
zkLink Nova Arbitrator on Ethereum (and Optimism) lost ~$780-805K after the claim path failed to clear transient finalizeMessageHash, allowing a public relayer to install an attacker-chosen L2 logs root and finalize forged withdrawals. Live loss ~$0.78M, 1 incident, ETH · OP. Avalanche Tranche remains an UPDATE.