Web3 Daily Exploits — 25 Oct 2026: X100 ~$4.85M Flash Governance Capture, Yapeswap $22K Zero-Quorum
X100 on Ethereum lost ~$4.85M after flash-loan governance capture of its three-seat Senate allowed same-block treasury swaps into attacker-controlled pools. Yapeswap lost ~$21.9K via zero-quorum WorkersUnion proposal that transferred feeToSetter and installed a fake Registry. Combined live loss ~$4.87M, 2 incidents, Ethereum. Initia remains an UPDATE.
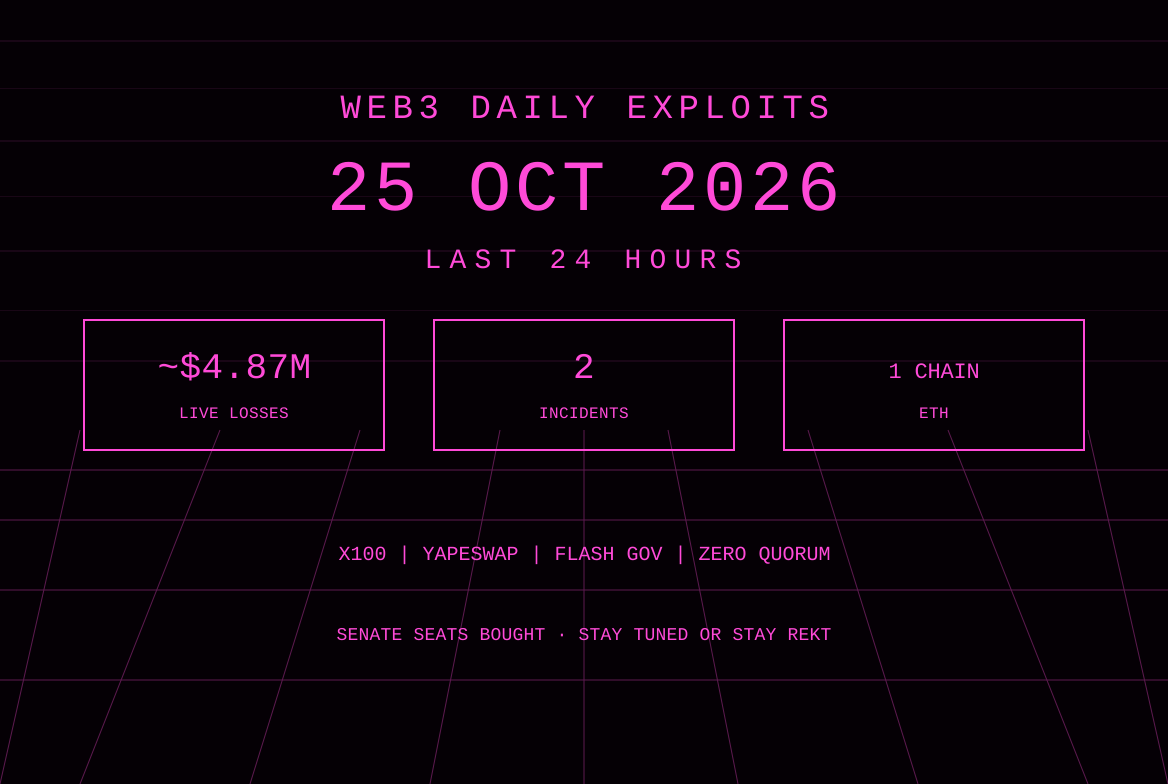
The 25 Oct America/Panama window records two first-report protocol incidents used for scoring. X100, an Ethereum-based project with a three-seat Senate governance model, lost approximately $4.85 million in USDT after attackers used flash loans to acquire a majority of Senate seats and execute malicious treasury proposals in the same transaction. A second, smaller incident hit Yapeswap for about $21.9 thousand via a zero-quorum governance proposal that transferred a critical role and installed a malicious registry. Combined live loss on this card is about $4.87 million. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors through the mid-day Panama cutoff. The prior Initia MoveVM script-caching incident remains an UPDATE and is not re-scored. DarkSword iOS malware coverage and other notes are retained without new loss figures.
X100 — Ethereum — about $4.85M — Flash-loan governance capture / same-block Senate majority and treasury swap
What happened: On 24 October 2026, beginning around 14:11 UTC, attackers exploited a governance design flaw in X100’s Senate (implemented via the Freezer / DexTreasury contract). Membership is determined by current frozen stake with no snapshot or timelock, and proposals can invoke the treasury’s own swap functions in the same transaction. The first attacker flash-borrowed approximately 1.94 million USDT from Aave, bought roughly 38,200 X tokens, split them across two helper contracts, and froze amounts that exceeded existing Senate members by a tiny margin (on the order of 0.000001 X). This secured two of the three Senate seats. The attacker then proposed and executed a swap that directed the treasury to sell 400,000 X into a freshly created, attacker-controlled PancakeSwap V3 X/USDT pool with a minimum output of zero, receiving only about 35.68 USDT. Liquidity was withdrawn, a portion of the recovered X was sold on the real Uniswap V3 pool, the flash loan was repaid, and the attacker retained approximately 4.75 million USDT. A second attacker followed a similar path minutes later for an additional roughly $96,000 USDT. A third transaction pulled approximately 550,000 X and a small USDT amount from a Uniswap V3 position held by the Freezer. Reports from DefimonAlerts, Phalcon_xyz, Bitquery, The Defiant and others converge on a combined realized loss near $4.85 million in USDT plus residual X. Official confirmation from the project was not located in the monitored channels at the time of writing; security firm alerts and on-chain reconstructions form the primary record. Primary first-report alerts: https://x.com/DefimonAlerts/status/2114007082055700836 and https://x.com/Phalcon_xyz/status/2114020331925258732.
Protocol / chain / asset: X100 on Ethereum mainnet. Freezer / Senate contract 0x79f35a33fe2813414851c4ae8daeacd14d822a46. X token 0x100a2c7f45fd48e217fdce72e658dc78fd43a100. Assets drained: USDT from treasury and liquidity positions, plus X tokens. Proceeds from the first attacker were later observed as ETH (approximately 2,022.86 ETH across several wallets that had not moved as of early 25 Oct reports).
Loss: Approximately $4.85 million in USDT across the primary transactions (first attack ~$4.75 million, second ~$96 thousand), plus residual X tokens (one report cites roughly 550,000 X in a third transaction and unsold balances). Figures are drawn from DefimonAlerts (~$4.75 million), Phalcon_xyz (~$4.75 million), Bitquery and The Defiant reconstructions (~$4.85 million combined). No additional external user-wallet drains outside the protocol treasury and liquidity are included in the scored total. Token price collapsed more than 96 percent according to contemporaneous reports.
Attack type: Governance design flaw enabling flash-loan funded acquisition of Senate majority followed by same-block proposal execution that called the treasury’s own swap. Not a classic reentrancy, not an oracle manipulation, and not a private-key compromise of operators. The absence of a snapshot, timelock, or quorum beyond current frozen stake made the capture practical. Multiple independent wallets reused the same open door within roughly half an hour.
Explorer URLs: First attack transaction: https://etherscan.io/tx/0x38c60844f1923d53fdce7d99e9bc2a2d8c73a08e793341dfbb479f8cc74d81d0. Second attack transaction: https://etherscan.io/tx/0x77c46e1aa9037ed4fbc9cc7e00d199dcd752acf576b4b5d3446e785dc45235c0. Third attack transaction: https://etherscan.io/tx/0x7c49bf28865defd5c1345f6527210360d635e510fa49279d0b62e6e02cfad99a. First attacker: https://etherscan.io/address/0x7ec2afdf3ec5964899894f8d58afa95cbb8ffd63. Freezer / Senate: https://etherscan.io/address/0x79f35a33fe2813414851c4ae8daeacd14d822a46. Ethereum explorer: https://etherscan.io/.
Status: Attacks executed 24 Oct 2026 between approximately 14:11 and 14:40 UTC. First public alerts from DefimonAlerts and Phalcon_xyz the same day. Multiple independent reconstructions published 24–25 Oct, including a detailed Bitquery on-chain investigation. No official post-mortem or recovery announcement from the X100 project located in the monitored channels at cutoff. Senate seats remained open to further capture according to some analyses. Users should treat any unofficial recovery claims or links with caution.
Sources: https://x.com/DefimonAlerts/status/2114007082055700836; https://x.com/Phalcon_xyz/status/2114020331925258732; https://bitquery.io/investigations/x100-hack; The Defiant coverage.
Yapeswap — Ethereum — about $21.9K — Zero-quorum governance / feeToSetter role transfer and fake Registry
What happened: On 25 October 2026 SlowMist reported that Yapeswap lost approximately $21.9 thousand after an attacker exploited a zero-quorum setting in the WorkersUnion governance mechanism. A proposal backed by roughly 0.000055 percent of voting power successfully transferred the feeToSetter role of the YapeFactory contract to the attacker. The attacker then installed a Registry contract that caused latestVault() to return forged vault addresses while vaults() continued to list the legitimate vaults. YapePair contracts counted the diverted deposits as farming assets without issuing redeemable shares, producing the loss. Attacker EOA 0x6e523866424220b3cb2cab88ba2195cfa5636b12 and contract 0x327bf6dfc38a79393f78866c705193c39b04be01 were listed. Vulnerable contracts include YapeFactory / YapePair / YapeWrapper at 0x46adc1c052fafd590f56c42e379d7d16622835a2. Primary alert: https://x.com/SlowMist_Team/status/2114290073546219799.
Protocol / chain / asset: Yapeswap (decentralized exchange / farming) on Ethereum. Affected contracts include multiple YapePair instances and the factory / wrapper. Assets: user deposits counted as farming assets without corresponding redeemable shares after the registry manipulation.
Loss: Approximately $21.9 thousand per SlowMist TI Alert. No additional independent loss figures were located at the time of writing. The amount is included in the scored total for this brief.
Attack type: Governance configuration flaw (zero quorum) allowing a proposal with negligible voting power to transfer a privileged role, followed by installation of a malicious Registry that broke consistency between latestVault() and vaults() views. Not a classic reentrancy or oracle manipulation. The zero-quorum setting converted governance into an execution path available to any holder of a tiny stake.
Explorer URLs: Attacker EOA: https://etherscan.io/address/0x6e523866424220b3cb2cab88ba2195cfa5636b12. Attacker contract: https://etherscan.io/address/0x327bf6dfc38a79393f78866c705193c39b04be01. Vulnerable contract example: https://etherscan.io/address/0x46adc1c052fafd590f56c42e379d7d16622835a2. Full transaction hash was linked in the SlowMist post (shortened URL); refer to the original alert for the primary transaction. Ethereum explorer: https://etherscan.io/.
Status: Alert posted by SlowMist on 25 Oct 2026. First public report in the monitored set. No official project response located at cutoff. Users should review any active positions and await further confirmation from the protocol or additional security firms.
Sources: https://x.com/SlowMist_Team/status/2114290073546219799.
Also noted
- Initia MoveVM script-caching incident (UPDATE, not re-scored): Official confirmation and details were posted on 24 Oct. Approximately $2.7 million was bridged out after unbacked credit of WETH, iUSD and USDC. L1 and rollups remain halted. See the 24 Oct brief for full coverage. No material new loss figures used for scoring today. https://www.rektradar.xyz/web3-daily-exploits-24-oct-2026-initia-2-7m-movevm-cache-mint/.
- DarkSword iOS malware (prior note, not scored): SlowMist TI alert on 24 Oct regarding iOS vulnerabilities used to escape the sandbox and steal Keychain credentials, wallet keys and Notes data. Over 1,500 related phishing sites identified. No specific on-chain loss figure attached. https://x.com/SlowMist_Team/status/2113861390335373779.
- Prior items (not re-scored): WAX Multi-Chain Bridge negative max_fee, NEM LP burn, Slice FundsModule, institutional MORPHO EIP-7702 and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the X100 detections and the Yapeswap alert.
Sources and references
- DefimonAlerts X100 alert: https://x.com/DefimonAlerts/status/2114007082055700836
- Phalcon_xyz X100 alert: https://x.com/Phalcon_xyz/status/2114020331925258732
- Bitquery X100 investigation: https://bitquery.io/investigations/x100-hack
- SlowMist Yapeswap alert: https://x.com/SlowMist_Team/status/2114290073546219799
- X100 first attack TX: https://etherscan.io/tx/0x38c60844f1923d53fdce7d99e9bc2a2d8c73a08e793341dfbb479f8cc74d81d0
- X100 Freezer / Senate: https://etherscan.io/address/0x79f35a33fe2813414851c4ae8daeacd14d822a46
- Yapeswap attacker EOA: https://etherscan.io/address/0x6e523866424220b3cb2cab88ba2195cfa5636b12
- SlowMist DarkSword (prior): https://x.com/SlowMist_Team/status/2113861390335373779
- 24 Oct brief for Initia coverage: https://www.rektradar.xyz/web3-daily-exploits-24-oct-2026-initia-2-7m-movevm-cache-mint/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $4.87 million, driven primarily by the X100 flash-loan Senate capture that converted treasury X and liquidity into roughly $4.85 million USDT, plus the smaller Yapeswap zero-quorum governance incident at about $21.9 thousand. Both were first reported or confirmed in the last 24 hours by the monitored accounts. The Initia incident remains an UPDATE from the prior window and is not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 24 Oct 2026: Initia ~$2.7M MoveVM Script Cache Unbacked Mint
Initia L1 and rollups halted after a MoveVM script-caching bug let an attacker spoof VM state and credit unbacked WETH, iUSD and USDC without changing total supplies. ~$2.7M bridged out via LayerZero and CCTP before pause; swapped to 1,135.52 ETH on Ethereum. Official confirmation 24 Oct. Live loss ~$2.7M, 1 incident, 2 chains. Kimchi Solana KOL note and DarkSword iOS alert as UPDATE.
Web3 Daily Exploits — 23 Oct 2026: WAX ~$90.5K Bridge Negative Fee Zero Debit
WAX Multi-Chain Bridge drained ~$90.5K after eth.token::withdraw allowed negative max_fee that zeroed the debit while still logging full withdrawals and releasing mapped USDC/USDT/DAI/WETH/WBTC on Solana and Ethereum. SlowMist and Blockaid first reports. Live loss ~$0.09M, 1 incident, 3 chains. Kimchi Solana KOL pump-dump and CoinDCX wallet movements noted as UPDATE.
Web3 Daily Exploits — 22 Oct 2026: NEM ~$820K LP Burn Reserve Manip
NEM (Newmont) token on BNB Chain drained ~$820K from its PancakeSwap USDT/NEM LP after a tax-settlement flaw let the attacker inflate pendingLpSellRecycle without real sells, then burn existing reserves via flushLpSellRecycle + sync. Defimon, CertiK, SlowMist, Phalcon first reports. Live loss ~$0.82M, 1 incident, 1 chain. Cysic bounty and Fearless Wallet key-leak noted as UPDATE.
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.