Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
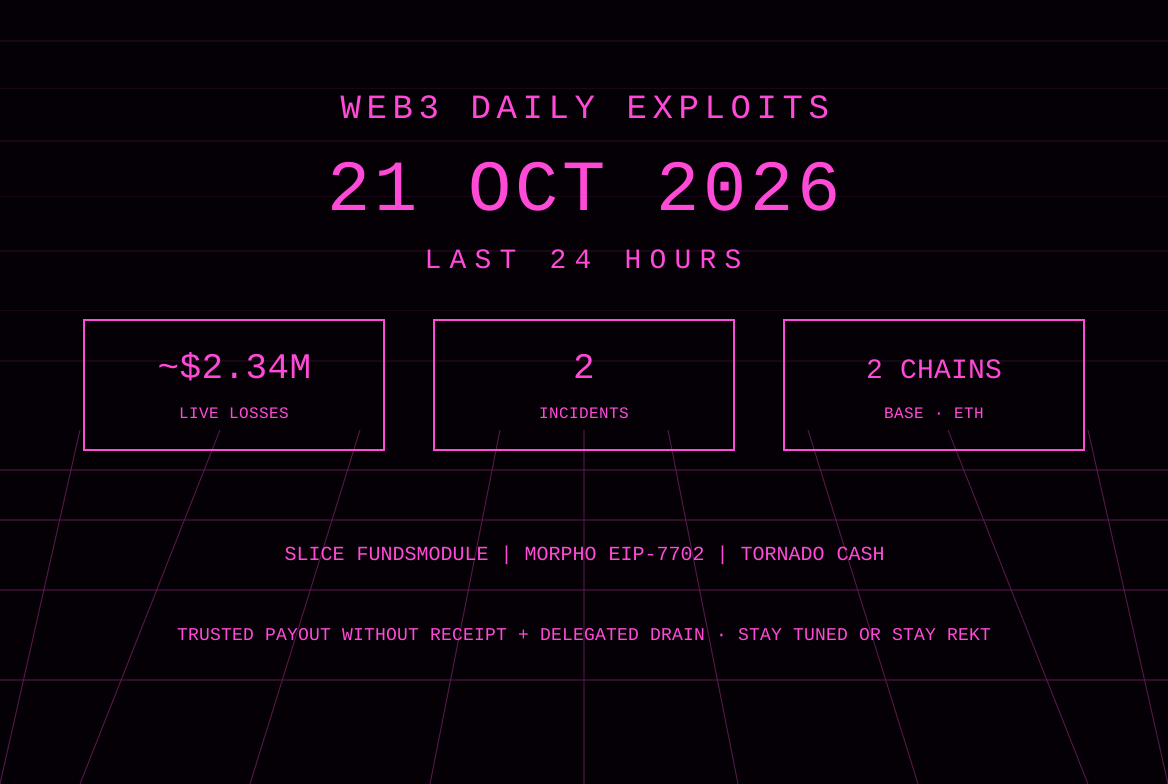
The 21 Oct America/Panama window records two first-report incidents used for scoring. Slice’s FundsModule on Base was drained for approximately $41K–$42K after the release function (0x9d2edfac) trusted amounts returned by caller-selected source contracts without verifying that corresponding ETH or USDC had actually been received. The attacker force-released unclaimed sales revenue from real stores into the module, then used fake sources that reported the full balance as payout and withdrew it. Separately, an institutional entity lost approximately 973,000 MORPHO tokens (~$2.3M) from two addresses hours earlier; both involved EIP-7702 account delegation transactions, and the funds were deposited into Tornado Cash. Combined live loss on this card is about $2.34M. SlowMist and DefimonAlerts posted the Slice detection on 21 Oct; ZachXBT reported the MORPHO theft. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. Continued Tornado Cash deposits by the Drift Protocol exploiter remain an UPDATE and are not re-scored.
Slice FundsModule — Base — about $41K — unbacked release / trusted source amounts
What happened: On 20 Oct 2026 (transaction timestamp ~18:39 UTC) an attacker exploited Slice’s FundsModule on Base. The 0x9d2edfac release function called any address the caller passed in as a “slicer” and credited whatever amount that address said it had paid out. It never checked that the address was a real Slicer contract or that any funds had actually arrived. The attacker first force-released the unclaimed sales revenue of about 70 real Slice stores into the FundsModule (credited to store owners but left sitting in the contract). Then they passed in their own fake slicer contracts, which reported the module’s entire balance as its payout, and withdrew it in the same call: approximately 8.72 ETH and 19.8K USDC that belonged to the store owners. The FundsModule implementation was unverified at the time. SlowMist identified the root cause as the function trusting release amounts returned by caller-selected source contracts without verifying receipt. DefimonAlerts provided matching details. Slice upgraded and paused the module roughly 1.5 hours later and sent an on-chain bounty offer: return 90% (15.11 ETH equivalent) by Friday 23 Oct 17:00 UTC and keep 10% as white-hat bounty. Official statement confirmed ~$41k in store earnings, fewer than 10 user stores affected, contracts paused and fixed within an hour of alert, protocol temporarily paused. Representative tx: 0x02b039a6345348d984e4a0b70dd233127772206e61ce82c390c4709c0b8d790a. Attacker: 0xc34572ebb26b9a4c54854aae8d2347108e8c892f. Victim proxy: 0x61bcd1ed11fc03c958a847a6687b1875f5eacaaf. Vulnerable impl: 0x8db3b6f51b594dc87b87a3a3b844de9c0d8d60b5. Attacker-deployed helper: 0x8ebc7878287415f1fadcf4ace8817094e4c86f90.
Protocol / chain / asset: Slice (onchain commerce / store settlement protocol). Chain: Base. Assets: ETH and USDC from pooled store earnings in the FundsModule. The loss stems from missing verification that reported release amounts matched actual token transfers into the contract.
Loss: Approximately $41K per SlowMist; ~$42K per DefimonAlerts. Official Slice statement cited about $41k. Figures reflect the ETH and USDC withdrawn from the module. No additional external user-wallet drains outside the module are included in the scored total.
Attack type: Logic error / missing asset-receipt verification in a release/payout function that trusted external contract return values. Not a classic reentrancy, not an oracle manipulation, and not a private-key compromise. The unverified implementation and the ability to force-release real stores before calling with fakes made the vector practical.
Explorer URLs: Attacker: https://basescan.org/address/0xc34572ebb26b9a4c54854aae8d2347108e8c892f. Victim proxy: https://basescan.org/address/0x61bcd1ed11fc03c958a847a6687b1875f5eacaaf. Vulnerable implementation: https://basescan.org/address/0x8db3b6f51b594dc87b87a3a3b844de9c0d8d60b5. Helper contract: https://basescan.org/address/0x8ebc7878287415f1fadcf4ace8817094e4c86f90. Representative tx: https://basescan.org/tx/0x02b039a6345348d984e4a0b70dd233127772206e61ce82c390c4709c0b8d790a. Base explorer: https://basescan.org/.
Status: First reported 21 Oct by SlowMist and DefimonAlerts. Attack executed on 20 Oct. Protocol paused contracts, upgraded, offered 10% white-hat bounty with deadline 23 Oct 17:00 UTC, and stated most funds were internal or partner-related with fewer than 10 user stores affected. Users should check Slice dashboard for notices.
Sources: https://x.com/SlowMist_Team/status/2112746806585274454; https://x.com/DefimonAlerts/status/2112804669865042308; https://x.com/slice__so/status/2112843976545796498.
Institutional MORPHO theft — Ethereum — about $2.3M — EIP-7702 delegation drain to Tornado Cash
What happened: On 21 Oct 2026 ZachXBT reported that an institutional entity lost approximately 973,000 MORPHO tokens (~$2.3M) from two addresses a few hours earlier. The stolen tokens were deposited into Tornado Cash. Both victim addresses were involved in EIP-7702 account delegation transactions. One of the addresses (affiliated with the same entity) had previously lost approximately $3.5M on 9 Oct from claims on an old cross-chain bridge; those funds were bridged from Ethereum to Zcash via NEAR Intents and entered the Ironwood privacy pool. The 0x4943 address shows on-chain overlap with a wallet suspected to belong to Nima Capital, which reportedly lost eight figures to a private-key compromise in September 2023. Victim addresses: 0x4943b0c9959dcf58871a799dfb71bece0d97c9f4 and 0x10bf1dcb5ab7860bab1c3320163c6dddf8dcc0e4. Prior related address: 0x24a9e00be5f169142c4f0797b41dacdf807d3e63. No detailed root-cause write-up beyond the EIP-7702 involvement was posted in the monitored feeds at cutoff; the exact access vector (compromised key, malicious delegation, or other) remains as reported by ZachXBT.
Protocol / chain / asset: MORPHO token holdings of an institutional entity. Chain: Ethereum (Tornado Cash deposits). Assets: MORPHO. The loss stems from unauthorized transfers involving EIP-7702 delegations on the victim addresses.
Loss: Approximately $2.3M (973,000 MORPHO). The figure reflects the value of the tokens moved to Tornado Cash. Combined with the prior 9 Oct incident the same entity has lost roughly $5.8M in under two weeks, but only the fresh 21 Oct amount is scored here.
Attack type: Unauthorized transfer involving EIP-7702 account delegation. Specific mechanism (key compromise enabling delegation, malicious delegate contract, or related) not fully detailed in public alerts at this cutoff. Not a protocol-level smart-contract bug in Morpho itself.
Explorer URLs: Victim 1: https://etherscan.io/address/0x4943b0c9959dcf58871a799dfb71bece0d97c9f4. Victim 2: https://etherscan.io/address/0x10bf1dcb5ab7860bab1c3320163c6dddf8dcc0e4. Prior related: https://etherscan.io/address/0x24a9e00be5f169142c4f0797b41dacdf807d3e63. Ethereum explorer base: https://etherscan.io/.
Status: First reported 21 Oct by ZachXBT. Funds deposited to Tornado Cash. No official recovery announcement observed in monitored feeds. Users of similar institutional or high-value addresses should review EIP-7702 delegation history and revoke unwanted delegations.
Sources: Reports citing ZachXBT: https://www.odaily.news/en/newsflash/526242; https://www.theblockbeats.info/flash/372942.
Also noted
- Drift Protocol exploiter (UPDATE, not re-scored): The address labeled as the Drift exploiter continued depositing stolen ETH into Tornado Cash after earlier movements on 20 Oct. Additional batches of roughly 18.8K–24.9K ETH were reported on 21 Oct, with remaining holdings still substantial (tens of thousands of ETH). PeckShieldAlert and Lookonchain reported the updates. Original theft remains prior; no new scored loss. https://x.com/PeckShieldAlert/status/2112821306282688960; https://x.com/lookonchain/status/2112845846471745822.
- Prior items (not re-scored): Argent-style wallet recovery wrap (~$60K), AlpsCon Hardhat + EIP-7702 (~$152K), Qubic weak-seed, BiFi, UNCX Vesting and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the Slice and MORPHO detections.
Sources and references
- SlowMist Slice alert: https://x.com/SlowMist_Team/status/2112746806585274454
- DefimonAlerts Slice detection: https://x.com/DefimonAlerts/status/2112804669865042308
- Slice official statement: https://x.com/slice__so/status/2112843976545796498
- Representative Slice tx: https://basescan.org/tx/0x02b039a6345348d984e4a0b70dd233127772206e61ce82c390c4709c0b8d790a
- ZachXBT MORPHO report (via coverage): https://www.odaily.news/en/newsflash/526242
- PeckShield Drift update: https://x.com/PeckShieldAlert/status/2112821306282688960
- Lookonchain Drift update: https://x.com/lookonchain/status/2112845846471745822
- 20 Oct brief for Argent-style coverage: https://www.rektradar.xyz/web3-daily-exploits-20-oct-2026-argent-style-wallet-60k-recovery-wrap/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $2.34M from the Slice FundsModule unbacked release on Base (~$41K) and the institutional MORPHO EIP-7702 drain to Tornado Cash (~$2.3M). The Slice attack was first reported by SlowMist and DefimonAlerts on 21 Oct; the MORPHO theft by ZachXBT. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. Fund movements by the prior Drift exploiter remain updates and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
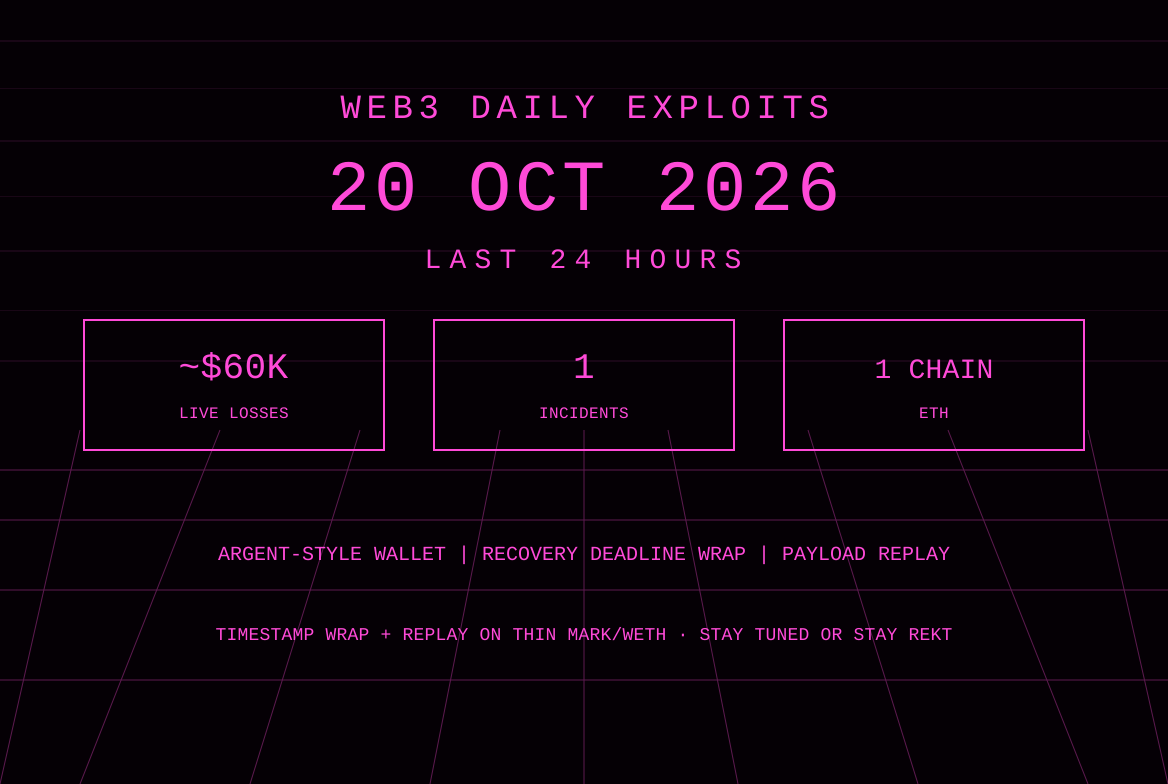
Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.
Web3 Daily Exploits — 19 Oct 2026: AlpsCon ~$152K Hardhat Default Account + EIP-7702 Reward Bug
AlpsCon AI Trade Hub on BNB Chain drained for ~$152K after a Hardhat default account was left on the KYC whitelist and used via EIP-7702 to claim historical rewards on a fresh stake. DefimonAlerts first report. Live loss ~$152K, 1 incident, 1 chain. Qubic weak-seed drain and BiFi noted as UPDATE.
Web3 Daily Exploits — 18 Oct 2026: BiFi Lending ~$165K Idle-Market Interest Inflation
BiFi Lending USDT market on Ethereum drained for ~$165.4K via interest-calculation inflation after a 36-day idle period. DefimonAlerts first report. Live loss ~$165K, 1 incident, 1 chain. UNCX official verified ~$807.6K with white-hat returns noted as UPDATE.
Web3 Daily Exploits — 17 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including Kolan, UNCX, Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery.