Web3 Daily Exploits — 22 Oct 2026: NEM ~$820K LP Burn Reserve Manip
NEM (Newmont) token on BNB Chain drained ~$820K from its PancakeSwap USDT/NEM LP after a tax-settlement flaw let the attacker inflate pendingLpSellRecycle without real sells, then burn existing reserves via flushLpSellRecycle + sync. Defimon, CertiK, SlowMist, Phalcon first reports. Live loss ~$0.82M, 1 incident, 1 chain. Cysic bounty and Fearless Wallet key-leak noted as UPDATE.
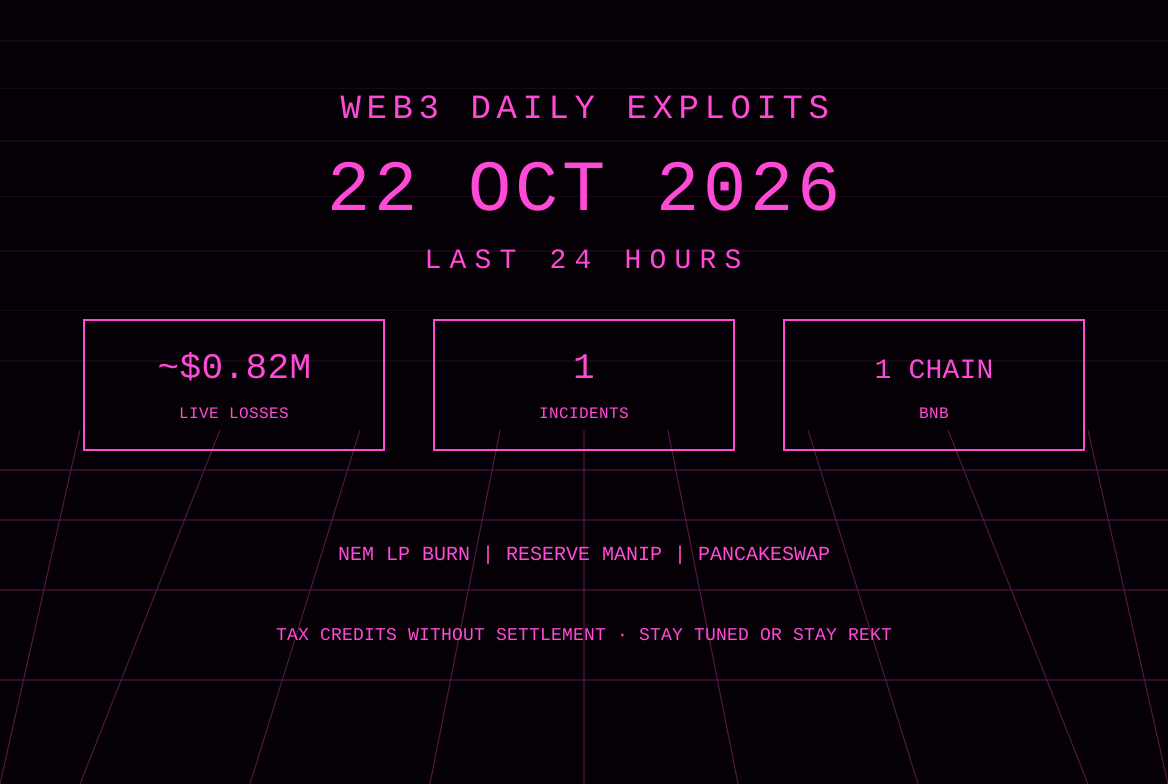
The 22 Oct America/Panama window records one first-report protocol incident used for scoring. The NEM (Newmont) token on BNB Chain lost approximately $820K from its PancakeSwap USDT/NEM liquidity pool after a logic flaw in the tax-settlement mechanism allowed an attacker to credit phantom sell volume, burn pre-existing LP reserves, and extract USDT at a manipulated price. DefimonAlerts, CertiKAlert, SlowMist_Team and Phalcon_xyz posted detections on 22 Oct. Combined live loss on this card is about $0.82M. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. The Cysic bridge bounty offer and the Fearless Wallet browser-extension key-leak disclosure remain UPDATEs and are not re-scored.
NEM / NemTokenV2 — BNB Chain — about $820K — tax credit without settlement / LP burn reserve manipulation
What happened: On 22 Oct 2026 an attacker exploited NemTokenV2 on BNB Chain. The contract credited any transfer of NEM into the PancakeSwap pair as sell volume via pendingLpSellRecycle without verifying that a real swap had settled. These credits remained valid after the attacker used skim() to recover most of the transferred tokens. The permissionless flushLpSellRecycle / _flushLpSellRecycle then burned up to a percentage of the pair’s existing NEM balance (reported as 70% of pending in one analysis, or up to 20% in another) and called pair.sync(), collapsing the recorded NEM reserve while the USDT reserve stayed intact. The attacker repeated the transfer → skim → flush sequence 42 times, reducing the pair’s NEM balance to near zero, then swapped remaining NEM for USDT at the inflated price, extracting approximately $820K–$821,920 USDT from the pool. Flash loans from Moolah, Venus and Pancake V3/V4 were used in some reconstructions. Attacker is a fresh Tornado-funded EOA. Representative tx cited by CertiK: 0xfb093c96c0094cbcca10801f97ed2e5ed3d96550ce64b544df5a349545723f91. Attacker: 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6. Attack contract: 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Vulnerable contract: 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777 (NemTokenV2). Victim pair: 0x840e19dcca541ee0b55a3c67e900a39d523b12b8 (PancakePair USDT/NEM).
Protocol / chain / asset: NEM (Newmont) token / NemTokenV2. Chain: BNB Chain (BSC). Assets: USDT extracted from the PancakeSwap USDT/NEM liquidity pool. The loss stems from the token’s own tax/sell-tracking logic that burned LP reserves without corresponding real sells.
Loss: Approximately $820K per CertiK and Phalcon; ~$821,920 per SlowMist; ~$726K net after loan repayment per DefimonAlerts. Figures reflect USDT drained from the LP. No additional external user-wallet drains outside the pool are included in the scored total.
Attack type: Logic error / missing verification that pendingLpSellRecycle credits matched actual settled sells, combined with permissionless burn of LP balance + sync that enabled constant-product price manipulation. Not a classic reentrancy, not an oracle manipulation on an external feed, and not a private-key compromise of the protocol. The self-sabotaging LP-sell-destroy mechanism made the vector practical once the accounting gap was identified.
Explorer URLs: Attacker: https://bscscan.com/address/0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6. Attack contract: https://bscscan.com/address/0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Vulnerable NemTokenV2: https://bscscan.com/address/0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777. Victim pair: https://bscscan.com/address/0x840e19dcca541ee0b55a3c67e900a39d523b12b8. Representative tx: https://bscscan.com/tx/0xfb093c96c0094cbcca10801f97ed2e5ed3d96550ce64b544df5a349545723f91. BNB Chain explorer: https://bscscan.com/.
Status: First reported 22 Oct by DefimonAlerts, CertiKAlert, SlowMist_Team and Phalcon_xyz. Attack executed a few hours prior. Funds reported bridged to Ethereum in one earlier detection. No official recovery announcement or bounty observed in monitored feeds at cutoff. Users of the NEM/USDT pool should treat remaining liquidity as at risk until the team posts a statement and any remaining positions are reviewed.
Sources: https://x.com/DefimonAlerts/status/2113212012171870663; https://x.com/CertiKAlert/status/2113211110879117323; https://x.com/SlowMist_Team/status/2113206749524316486; https://x.com/Phalcon_xyz/status/2113223739978707083.
Also noted
- Fearless Wallet browser extension key leak (UPDATE, not re-scored): Polkadot Community Foundation and SlowMist disclosed that versions 3.0.1 and 3.0.3–3.0.5 of the third-party Fearless Wallet browser extension contained malicious code that exfiltrated private keys / recovery phrases when the wallet was unlocked. The code was introduced around February 2025 and active intermittently through October 2026. Eight users reported unauthorized transactions totaling 17,286 DOT. Users of the affected extension since February 2025 are advised to treat accounts as compromised and migrate to new keypairs. Android/iOS apps checked clean, but imported keys remain at risk. https://x.com/SlowMist_Team/status/2113187562336706815; https://forum.polkadot.network/t/security-notice-fearless-wallet-browser-extension-leaked-private-keys/19058.
- Cysic bridge exploit bounty (UPDATE, not re-scored): Cysic posted an on-chain message offering approximately 10% recovery bounty for return of ~90% of identified ETH proceeds from the prior unauthorized mint of 10M CYS. Return 275.872 ETH to a foundation address within 72 hours; retain ~30.652 ETH. Original incident remains prior; no new scored loss. https://x.com/DefimonAlerts/status/2113203181681250611.
- Prior items (not re-scored): Slice FundsModule (~$41K), institutional MORPHO EIP-7702 (~$2.3M), Argent-style wallet, AlpsCon, Qubic, BiFi, UNCX Vesting and earlier incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the NEM detection.
Sources and references
- DefimonAlerts NEM detection: https://x.com/DefimonAlerts/status/2113212012171870663
- CertiK Alert NEM exploit: https://x.com/CertiKAlert/status/2113211110879117323
- SlowMist NEM TI Alert: https://x.com/SlowMist_Team/status/2113206749524316486
- Phalcon NEM analysis: https://x.com/Phalcon_xyz/status/2113223739978707083
- Representative tx: https://bscscan.com/tx/0xfb093c96c0094cbcca10801f97ed2e5ed3d96550ce64b544df5a349545723f91
- SlowMist Fearless Wallet alert: https://x.com/SlowMist_Team/status/2113187562336706815
- Polkadot Forum security notice: https://forum.polkadot.network/t/security-notice-fearless-wallet-browser-extension-leaked-private-keys/19058
- Cysic bounty message: https://x.com/DefimonAlerts/status/2113203181681250611
- 21 Oct brief for Slice and MORPHO coverage: https://www.rektradar.xyz/web3-daily-exploits-21-oct-2026-slice-41k-fundsmodule-morpho-2-3m-eip7702/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $0.82M from the NEM / NemTokenV2 tax-settlement flaw that enabled LP reserve burn and price manipulation on the PancakeSwap USDT/NEM pair on BNB Chain. The attack was first reported by DefimonAlerts, CertiKAlert, SlowMist_Team and Phalcon_xyz on 22 Oct. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. The Cysic bounty offer and Fearless Wallet key-leak disclosure remain updates and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
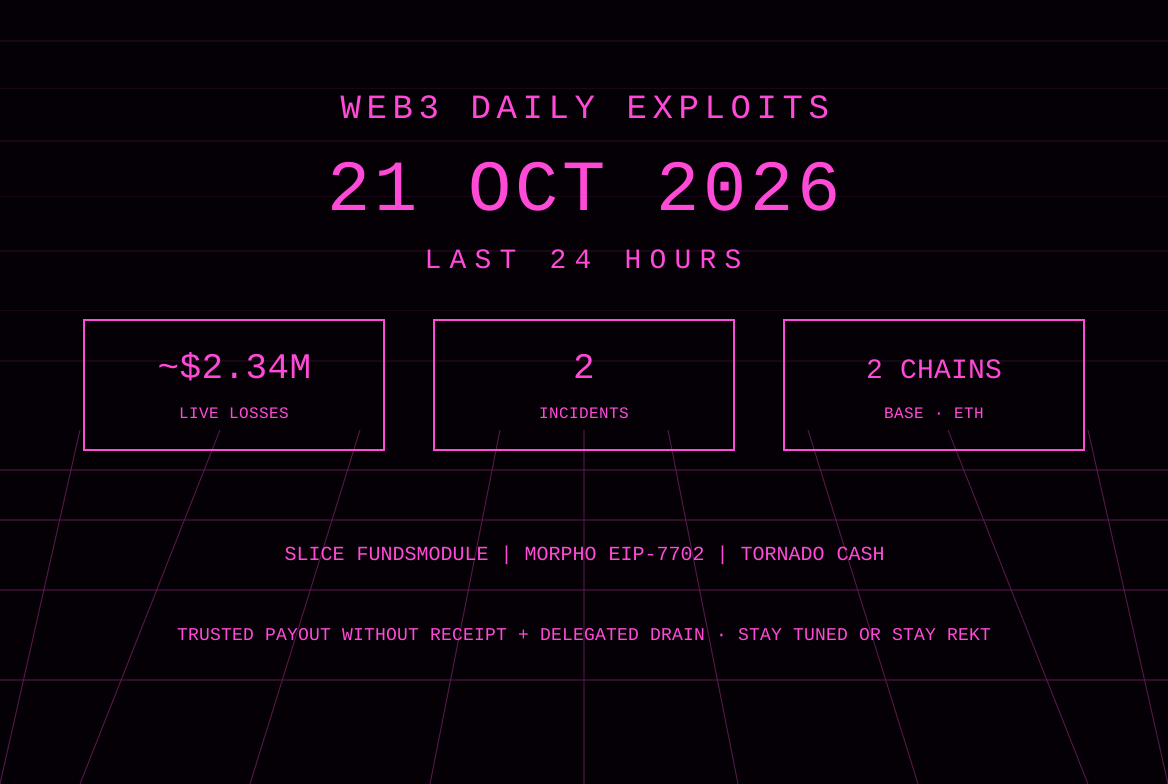
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.
Web3 Daily Exploits — 19 Oct 2026: AlpsCon ~$152K Hardhat Default Account + EIP-7702 Reward Bug
AlpsCon AI Trade Hub on BNB Chain drained for ~$152K after a Hardhat default account was left on the KYC whitelist and used via EIP-7702 to claim historical rewards on a fresh stake. DefimonAlerts first report. Live loss ~$152K, 1 incident, 1 chain. Qubic weak-seed drain and BiFi noted as UPDATE.
Web3 Daily Exploits — 18 Oct 2026: BiFi Lending ~$165K Idle-Market Interest Inflation
BiFi Lending USDT market on Ethereum drained for ~$165.4K via interest-calculation inflation after a 36-day idle period. DefimonAlerts first report. Live loss ~$165K, 1 incident, 1 chain. UNCX official verified ~$807.6K with white-hat returns noted as UPDATE.