Web3 Daily Exploits — 18 Oct 2026: BiFi Lending ~$165K Idle-Market Interest Inflation
BiFi Lending USDT market on Ethereum drained for ~$165.4K via interest-calculation inflation after a 36-day idle period. DefimonAlerts first report. Live loss ~$165K, 1 incident, 1 chain. UNCX official verified ~$807.6K with white-hat returns noted as UPDATE.
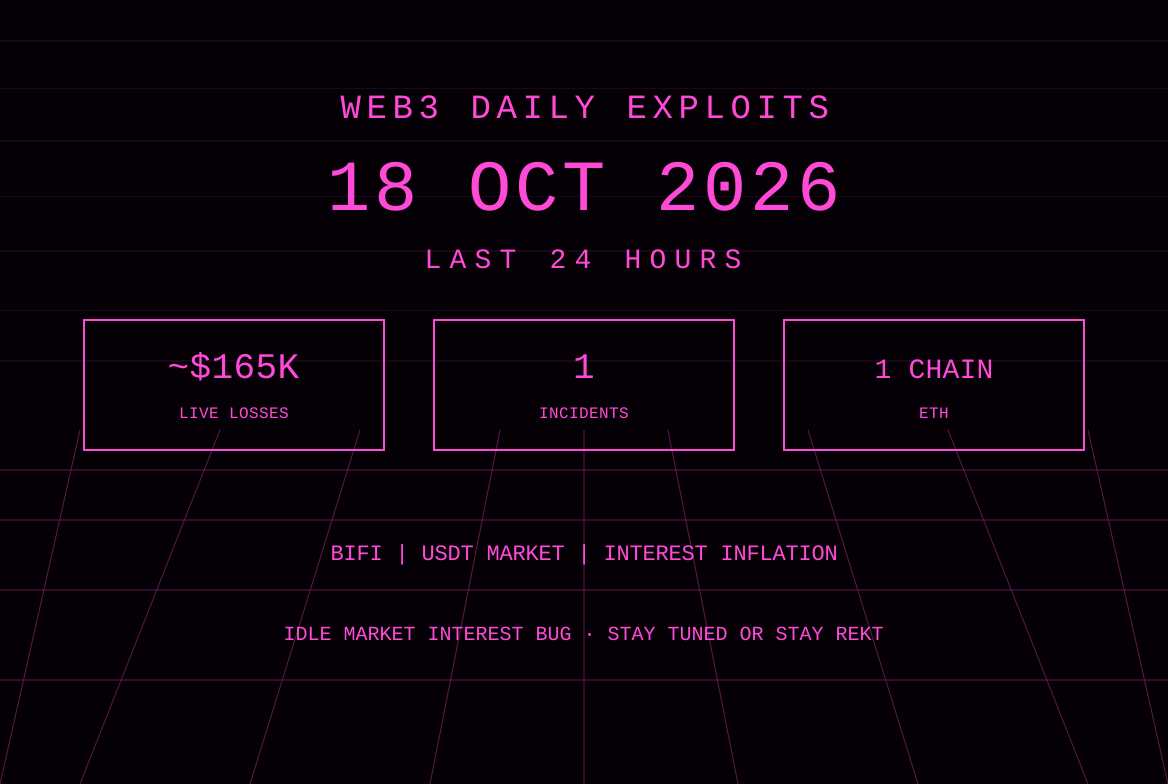
The 18 Oct America/Panama window records one first-report protocol incident used for scoring: BiFi Lending’s USDT market on Ethereum was drained for approximately $165.4K through an interest-calculation inflation that accumulated after the market had sat idle for about 264,000 blocks (~36 days). Combined live loss on this card is about $165K. DefimonAlerts posted the detection on 18 Oct. The original attacker deployed an exploit contract; one block later c0ffeebabe.eth front-ran it, flash-loaned roughly 40.5M USDT from Morpho, deposited in growing tranches, borrowed to raise utilization, then used a repay/withdraw loop to extract inflated deposit interest twice, draining 165.6K USDT which was swapped to WETH. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. UNCX Network published an official incident report confirming verified realized economic value of approximately $807,609 for the earlier Vesting V2 event, together with confirmed white-hat returns; that remains an UPDATE and is not re-scored.
BiFi Lending — Ethereum — about $165.4K — interest-calculation inflation / idle-market logic error
What happened: On 18 Oct 2026 DefimonAlerts detected an exploit against BiFi Lending’s USDT market on Ethereum. The market had been idle for approximately 264,000 blocks, or about 36 days. TokenHandler._checkFirstAction stores that gap as inactiveActionDelta and freezes actionEXR once per block. Subsequent actions inside the same block re-run interestModel.getInterestAmount, which computes globalEXR = actionEXR × (1 + rate × 264K). Because the rate is taken from live deposit and borrow totals, an attacker who first sets utilization can cause the entire accumulated idle-period interest to be charged at the manipulated rate on every call. The original attacker deployed an exploit contract in block 26210255. One block later c0ffeebabe.eth front-ran the attack from its own contract, flash-loaning 40.5M USDT from Morpho, depositing in successive growing tranches, borrowing 30M to push utilization higher, then looping repay and withdraw operations to cash out the inflated deposit interest. The cycle was run twice, draining 165.6K USDT that was swapped to WETH. Proceeds remain under the control of the front-running MEV operator as of the detection post.
Protocol / chain / asset: BiFi Lending (cross-chain lending protocol). Chain: Ethereum. Market: USDT. Attacker (initial deployment) and front-running MEV (c0ffeebabe.eth) as listed in the DefimonAlerts post. Victim: BiFi USDT market contracts. No private-key compromise of the protocol itself; the loss stems from the interest-accounting interaction with a long inactiveActionDelta.
Loss: Approximately $165.4K (165.6K USDT) per DefimonAlerts detection. Figures reflect the USDT extracted from the market and swapped to WETH. No additional user-wallet drains outside the market are included. Residual balances in other BiFi markets are not scored.
Attack type: Logic error / interest-calculation inflation after prolonged market inactivity. The combination of a frozen actionEXR, an accumulated inactiveActionDelta, and re-computation of interest against live utilization inside the same block allows an attacker to apply an extreme rate to the stored idle interest. Not an oracle manipulation, not a classic reentrancy, and not a key compromise. Shared-market design and flash-loan capital made the extraction practical.
Explorer URLs: DefimonAlerts provided shortened links in its post for the initial attacker, the exploit deployment transaction (block 26210255), the front-run transaction (block 26210256), the MEV bot, and the victim contract. Full transaction hashes are not restated here beyond those cited by the source. Ethereum explorer base: https://etherscan.io/.
Status: First reported 18 Oct by DefimonAlerts. Attack executed and front-run in consecutive blocks. No official protocol statement or recovery announcement observed in the monitored feeds as of this cutoff. Users of the USDT market should treat positions as at risk until the team posts guidance.
Sources: https://x.com/DefimonAlerts/status/2111725425554571750.
Also noted
- UNCX Network Vesting V2 (UPDATE, not re-scored): Official incident report published (dated 15 Oct, widely covered 17 Oct) confirms verified realized economic value of approximately $807,609 across Ethereum, BNB Smart Chain, Base and Robinhood Chain. Chain breakdown per the report: BNB Chain ≈$567,501, Ethereum ≈$77,167, Robinhood ≈$124,588, Base ≈$38,353. White-hat returns include 82,143,476 X tokens and roughly 23.87 ETH. Inventory status: no material tokens awaiting disposition. Earlier third-party estimates of ~$1.49M are superseded by the project’s verified figure. Remains on the 15 Oct brief; not added to this card’s live-loss total. Full report: https://uncx.network/vesting-incident. Official X recap: https://x.com/UNCX_token/status/2111424972694368464.
- Kolan Protocol Uniswap V4 Hook (UPDATE, not re-scored): The ~$3,000 flash-loan price manipulation remains on the 16 Oct brief. No material new loss figures in this window.
- Pirate Chain (ARRR) unbacked mint (UPDATE, not re-scored): Official updates confirmed an October 14 transaction-validation vulnerability allowing unauthorized creation of approximately 39.8 million ARRR. No USD loss figure used for scoring. Remains prior.
- XPR Network / LOAN Protocol webauthn (UPDATE, not re-scored): On 17 Oct ~02:35 UTC an attacker used a webauthn contract vulnerability to control 67 accounts and borrow ~$1.32M from LOAN Protocol, then attempted to bridge ~1.14M USDC to Ethereum. The bridge did not release funds; amounts returned to LOAN. Markets paused and contract patched. Reported by block producer MadBlocks; not posted by required monitors. No confirmed net protocol loss used for scoring. Remains outside this card.
- Gamdom hot-wallet breach (UPDATE, not re-scored): October 13 incident remains prior. No new scored loss.
- Prior items (not re-scored): THEO / Hyperlane, 79Vault, Ledger / CryptoBilis implant, BitBay, EtherVista, NEAR Intents and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the BiFi detection.
Sources and references
- DefimonAlerts BiFi detection: https://x.com/DefimonAlerts/status/2111725425554571750
- UNCX official incident report: https://uncx.network/vesting-incident
- UNCX X recap and update: https://x.com/UNCX_token/status/2111424972694368464
- MadBlocks XPR/LOAN timeline: https://x.com/madblocksbp/status/2111344089950048767
- 15 Oct brief for original UNCX coverage: https://www.rektradar.xyz/web3-daily-exploits-15-oct-2026-uncx-vesting-1-49m-share-accounting/
- 16 Oct brief for Kolan coverage: https://www.rektradar.xyz/web3-daily-exploits-16-oct-2026-kolan-3k-uniswap-v4-hook/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $165K from the BiFi Lending USDT-market interest-inflation logic error on Ethereum. The attack was first reported by DefimonAlerts on 18 Oct and was front-run by an MEV operator. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. Prior-day items including UNCX and the XPR/LOAN webauthn attempt remain on prior coverage or as updates and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 17 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including Kolan, UNCX, Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery.
Web3 Daily Exploits — 16 Oct 2026: Kolan Uniswap V4 Hook ~$3K Price Manipulation
Small scored incident: Kolan Uniswap V4 hook drained ~$3K via flash-loan price manipulation on permissionless accept() with no slippage guard on buyback. Live loss ~$3K, 1 incident, 1 chain (ETH). Prior items including UNCX and Bofur Capital noted as updates.
Web3 Daily Exploits — 15 Oct 2026: UNCX Vesting V2 ~$1.49M Multi-Chain Share Accounting Drain
UNCX Network Vesting V2 shared pools exploited via share-accounting flaw in cancel() and release(). Blockaid reports ~$1.49M drained across Ethereum, BSC, Base and Robinhood Chain involving 10 tokens and copycats. Containment via high fees. One incident, four chains.
Web3 Daily Exploits — 14 Oct 2026: Quiet Window, No New Protocol Drains
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits or user-wallet drains with fresh loss figures in the last 24 hours. Combined live loss on this card is ~$0. THEO Hyperlane mint remains on the 13 Oct brief. iOS Safari advisory noted with no confirmed crypto theft.