Web3 Daily Exploits — 16 Oct 2026: Kolan Uniswap V4 Hook ~$3K Price Manipulation
Small scored incident: Kolan Uniswap V4 hook drained ~$3K via flash-loan price manipulation on permissionless accept() with no slippage guard on buyback. Live loss ~$3K, 1 incident, 1 chain (ETH). Prior items including UNCX and Bofur Capital noted as updates.
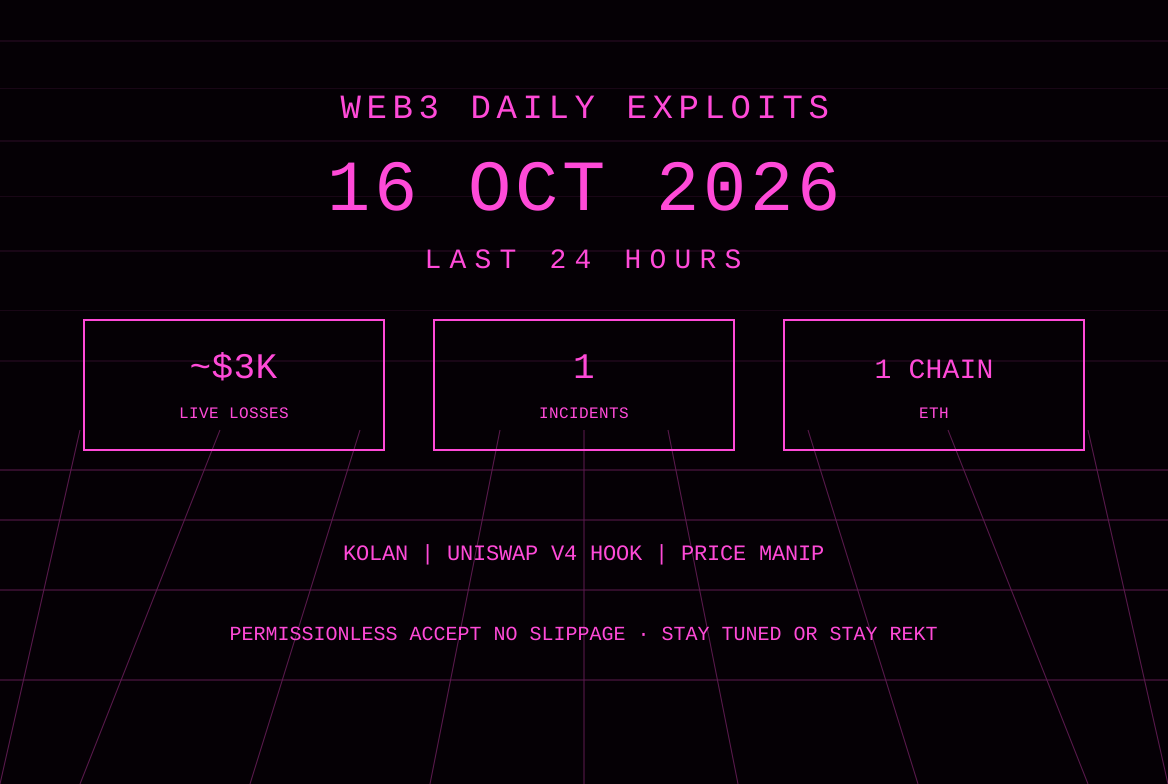
The 16 Oct America/Panama window records one first-report protocol incident used for scoring: a small flash-loan price manipulation against the Kolan Uniswap V4 hook on Ethereum that extracted approximately $3,000 in net attacker profit. Combined live loss on this card is about $3,000. The root cause is a permissionless accept(id) after window expiry that triggers an unbounded buyback of the hook’s own ETH reserves using the instantaneous pool price with no slippage protection. Monitored accounts including DefimonAlerts and ExVul posted details in the last 24 hours. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. Prior items including the UNCX Vesting V2 multi-chain drain remain on earlier briefs and are not re-scored.
Kolan Protocol Uniswap V4 Hook — Ethereum — about $3,000 — flash loan / price manipulation / logic error
What happened: On 15 Oct 2026 ExVul and DefimonAlerts reported an exploit against Kolan’s Uniswap V4 hook (KolanHook). Kolan is a “window” protocol that lets buyers purchase tokens with a timed undo option; the hook holds ETH/token reserves and allows anyone to close an expired window via the permissionless accept(id) function. accept calls _closeWindow which calls _buyBack, swapping the hook’s own ETH reserves back into the pool with no slippage guard (sqrtPriceLimit set near MIN_SQRT_PRICE). The attacker flash-loaned approximately 6.7 WETH from Balancer, bought KLN to inflate the pool price, then triggered accept on two expired windows (ids 10 and 42). This forced the hook to spend about 2.31 ETH of its reserves buying and burning tokens at the manipulated price. The attacker then sold the pre-bought KLN into the ETH-enriched pool, repaid the loan, and netted approximately 1.28 ETH profit. Victim hook drained roughly 2.31 ETH (about $5.4K at the time); attacker profit about 1.28 ETH (about $3.0K). The exploit transaction is recorded at 0x7b131926e6f06491ae1aead3e419b208c8aa70ed7898e8c5a33d9f52e40915a9. Attacker address: 0x8df735014eab81905e76b87ef0c069bd8e0ae382. Victim hook: 0x0136fecf49e0217bfd2d9551e8e7b05f174ba8ec. No official protocol response or recovery steps were noted in the monitored posts as of cutoff.
Protocol / chain / asset: Kolan Protocol (Uniswap V4 hook for timed-window token purchases). Chain: Ethereum. Asset: native ETH held by the hook and KLN token. Vulnerable contract (KolanHook): 0x0136fecf49e0217bfd2d9551e8e7b05f174ba8ec. Attacker: 0x8df735014eab81905e76b87ef0c069bd8e0ae382. Proceeds remain under attacker control.
Loss: Approximately $3,000 per DefimonAlerts (attacker net profit ~1.28 ETH). Hook reserves reduced by ~2.31 ETH. Figures reflect ETH extracted from the hook’s own reserves via the manipulated buyback; not additive external user-wallet drains. Token price impact on KLN is separate and not scored.
Attack type: Flash loan / price manipulation / logic error. Permissionless accept() after expiry trusts the instantaneous pool sqrtPrice for the buyback and uses no slippage limit, allowing an attacker to manipulate the price, force the hook to buy high, then reverse the trade. Not a classic reentrancy, not an oracle issue in the traditional sense, not a private-key compromise. Shared-pool / hook design with permissionless close amplified the opportunity.
Explorer URLs: Exploit transaction: https://etherscan.io/tx/0x7b131926e6f06491ae1aead3e419b208c8aa70ed7898e8c5a33d9f52e40915a9. Attacker: https://etherscan.io/address/0x8df735014eab81905e76b87ef0c069bd8e0ae382. Victim hook: https://etherscan.io/address/0x0136fecf49e0217bfd2d9551e8e7b05f174ba8ec. This brief does not invent additional transaction hashes beyond those cited by sources.
Status: First reported 15 Oct by ExVul and DefimonAlerts. No confirmed recovery, bounty, or protocol statement in the posts read for this cutoff. Funds remain with the attacker.
Sources: https://x.com/DefimonAlerts/status/2110776621087047818, https://x.com/exvulsec/status/2110708025753481600, and secondary technical notes.
Also noted
- Bofur Capital related address (UPDATE, not re-scored): PeckShieldAlert posted on 16 Oct that the phisher who drained approximately $2 million in DAI from a Bofur Capital-related address has swapped the stolen funds for 825.5 ETH. The original drain occurred in August via address-poisoning after a Compound withdrawal. First reported outside the strict last-24h window for new scoring; the swap is a material movement of prior proceeds and is noted here but not added to the live-loss total.
- UNCX Network Vesting V2 (UPDATE, not re-scored): Multi-chain share-accounting drain of approximately $1.49 million remains on the 15 Oct brief. Containment measures (high fees, disabled bypasses) in place. No material new loss figures or confirmed recoveries in this window. 10% white-hat bounty offer outstanding.
- Fake Ledger firmware update phishing (no scored loss): SlowMist posted a TI Alert on 16 Oct warning of a fake “Ledger firmware update” campaign exploiting the recent Ledger / CryptoBilis supply-chain incident. Pages mimic Genuine Check and device selection with an “Update Now” button. Users advised never to click website links for updates and never to enter recovery phrases. No confirmed theft figures tied to this specific campaign in the monitored posts.
- Defimon recovery to known exploit address (unverified impact): On-chain messages circulating 16 Oct note that automated Defimon claims of stale Sui Bridge withdrawals sent approximately $392K to an address publicly associated with the Cetus exploit. Defimon acknowledged the screening gap and stated the funds remain unmoved. Not a new protocol exploit; noted as an operational incident pending further confirmation. Not scored.
- CL8Y Asset Recovery Notice (unverified, no scored loss): DefimonAlerts continued posting on-chain recovery coordination messages for a 15 October 2026 incident. No independent confirmation of protocol type or loss figure used for scoring.
- Prior items (not re-scored): THEO / Hyperlane, 79Vault, Ledger / CryptoBilis implant, BitBay, EtherVista and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the Kolan item.
Sources and references
- DefimonAlerts Kolan alert: https://x.com/DefimonAlerts/status/2110776621087047818
- ExVul technical alert: https://x.com/exvulsec/status/2110708025753481600
- PeckShieldAlert Bofur Capital swap: https://x.com/PeckShieldAlert/status/2110899366429102307
- SlowMist fake Ledger firmware TI Alert: https://x.com/SlowMist_Team/status/2110988183039332417
- 15 Oct brief for full UNCX coverage: https://www.rektradar.xyz/web3-daily-exploits-15-oct-2026-uncx-vesting-1-49m-share-accounting/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $3,000 from the Kolan Uniswap V4 hook flash-loan price manipulation. No other new first-report protocol drains with fresh figures were posted by the monitored accounts as of the latest cutoff. Prior-day items including UNCX remain on their original briefs and are not re-scored. The Bofur Capital swap and Ledger phishing campaign are noted as updates or advisories without new scored losses. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
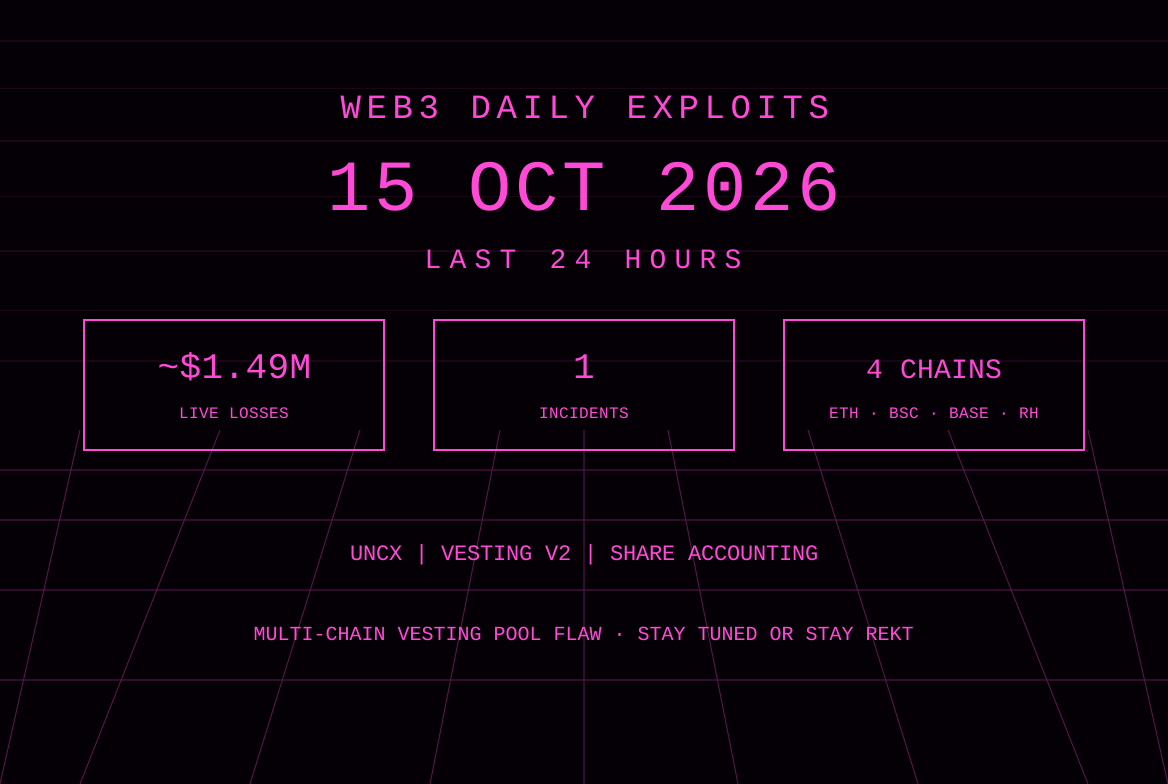
Web3 Daily Exploits — 15 Oct 2026: UNCX Vesting V2 ~$1.49M Multi-Chain Share Accounting Drain
UNCX Network Vesting V2 shared pools exploited via share-accounting flaw in cancel() and release(). Blockaid reports ~$1.49M drained across Ethereum, BSC, Base and Robinhood Chain involving 10 tokens and copycats. Containment via high fees. One incident, four chains.
Web3 Daily Exploits — 14 Oct 2026: Quiet Window, No New Protocol Drains
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits or user-wallet drains with fresh loss figures in the last 24 hours. Combined live loss on this card is ~$0. THEO Hyperlane mint remains on the 13 Oct brief. iOS Safari advisory noted with no confirmed crypto theft.
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.