Web3 Daily Exploits — 15 Oct 2026: UNCX Vesting V2 ~$1.49M Multi-Chain Share Accounting Drain
UNCX Network Vesting V2 shared pools exploited via share-accounting flaw in cancel() and release(). Blockaid reports ~$1.49M drained across Ethereum, BSC, Base and Robinhood Chain involving 10 tokens and copycats. Containment via high fees. One incident, four chains.
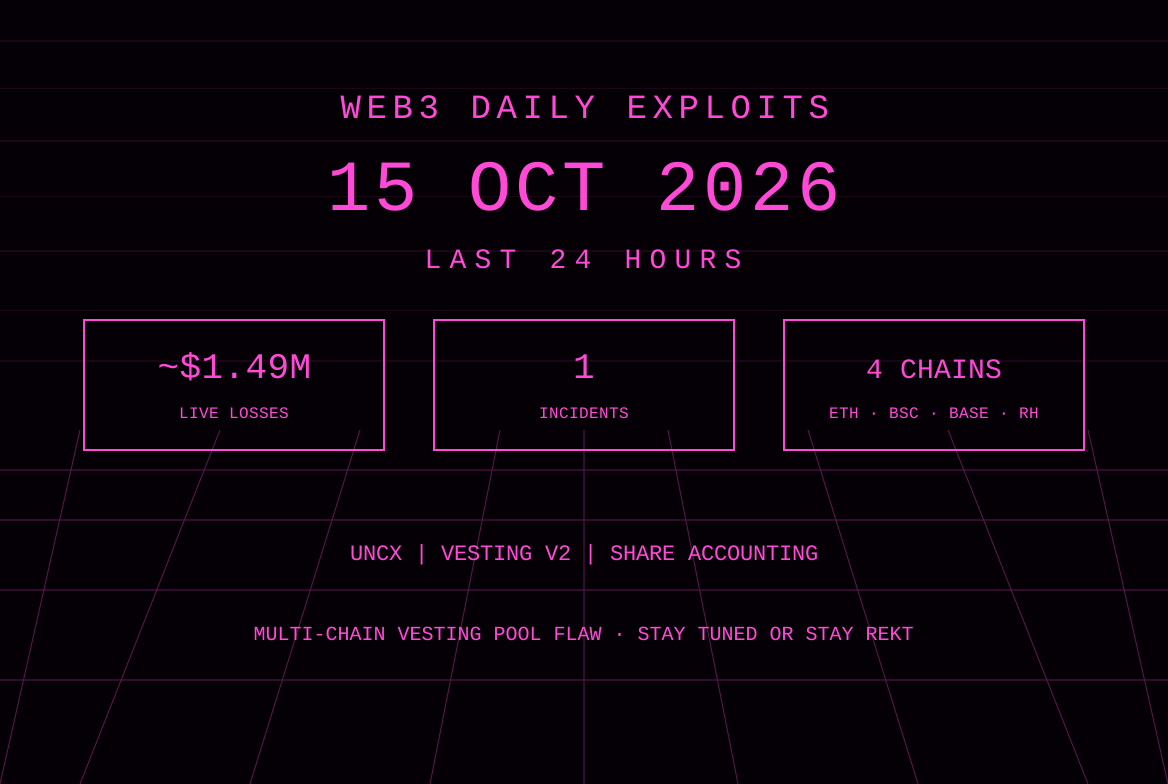
The 15 Oct America/Panama window records one first-report protocol incident used for scoring, with a material update on a prior-day item that escalated substantially overnight: UNCX Network’s Vesting V2 shared token-vesting pools were drained via a share-accounting logic error. Blockaid reported the total at approximately $1.49 million across four chains as of 15 Oct, up from the initial ~$86,000 Ethereum drain flagged on 14 Oct. Combined live loss on this card is about $1.49 million. The root cause is inconsistent tracking of _totalTokenShares between release() and cancel() in the VestingManager, allowing donation-plus-top-up sequences to over-deduct shares and inflate payouts from the shared pool. Monitored accounts including Blockaid, DefimonAlerts, SlowMist_Team and Phalcon_xyz posted details and updates in the last 24 hours. UNCX has raised fees above 1,000 ETH equivalent, disabled fee-bypass paths, and is coordinating recovery with a 10% white-hat bounty offer. LP lockers remain unaffected. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors.
UNCX Network Vesting V2 — Ethereum / BSC / Base / Robinhood Chain — about $1.49 million — logic error / share-accounting manipulation
What happened: On 14 Oct 2026 Blockaid detected an ongoing exploit against UNCX’s shared Vesting V2 contracts on Ethereum. The initial drain extracted approximately $86,000 across five ERC-20 tokens (EDGEN, ZC, pepeCoin, LO0P, PAAL AI) in one transaction. The attacker created self-owned vesting schedules, released portions, donated tokens directly to the contract to alter the shares-per-token rate, topped up other schedules, and canceled them in a way that over-reduced the global _totalTokenShares denominator. This allowed a retained attacker schedule to claim excess tokens belonging to other users in the shared pool. By 15 Oct the attack had spread. Blockaid updated that total stolen reached ~$1.49 million across 11 drain transactions on four chains, involving the original attacker, copycat wallets and MEV bots. Breakdown: BSC ~$969k, Ethereum ~$242k, Robinhood Chain ~$169k, Base ~$114k. Affected tokens total 10: Ethereum (pepecoin, EDGEN, ZC, X, LO0P, PAAL), Base (IMO), BNB Chain (BTCLE), Robinhood Chain (CASHCAT, RKST). Phalcon_xyz detailed the accounting inconsistency using an example exploit transaction: the attacker created schedules 5058, 5059 and 5060; fully released 5059 and 5060 while retaining 5058; donated tokens to inflate asset-per-share without minting new shares; topped up the fully released schedules (increasing totalAmount while minting few new shares, pushing vestedShare below released); then canceled them so that cancel() deducted previously released shares a second time from _totalTokenShares. The reduced denominator inflated the payout when 5058 was released. SlowMist confirmed the cancel() failure to ensure retained shares covered already-released amounts. UNCX responded by introducing flat fees exceeding 1,000 ETH per lock, removing bypass interactions, raising token fees to the 5% contract maximum, and contacting holders of proceeds on-chain (via DefimonAlerts messages) with a 10% white-hat bounty offer to return 90% to multisig 0x32f0eB068fD804195629A2CBEE30A7e9CE58c4cb within 48 hours. No funds returned as of the latest posts. LP lockers and legacy vesting contracts are unaffected.
Protocol / chain / asset: UNCX Network Vesting V2 (shared token vesting pools). Chains: Ethereum, BNB Smart Chain, Base, Robinhood Chain. Tokens: EDGEN, ZC, pepecoin, LO0P, PAAL, X (ETH); IMO (Base); BTCLE (BSC); CASHCAT, RKST (Robinhood). Vulnerable contract on Ethereum: 0xa98f06312b7614523d0f5e725e15fd20fb1b99f5. Attacker (initial): 0x78c9b11853e4f183a34c63ffd1924d2319a2f5b3. Proceeds remain under attacker control or with copycats pending recovery.
Loss: Approximately $1.49 million per Blockaid 15 Oct update (BSC ~$969k + ETH ~$242k + Robinhood ~$169k + Base ~$114k). Initial Ethereum figure ~$86k–$89k. Figures reflect tokens extracted from the shared vesting balances at the time of drains; not additive user-wallet drains outside the pools. Token price impact on affected assets is separate and not scored. Still-at-risk balances in unaffected schedules exist but are not included in the live-loss total.
Attack type: Logic error / incorrect share accounting. VestingManager.release() and cancel() inconsistently update _totalTokenShares. Donation lowers the conversion rate; top-up after full release followed by cancel over-reduces the denominator, inflating the payout of a retained schedule. Not an oracle manipulation, not a reentrancy in the classic sense, not a private-key compromise of the vesting contracts themselves. Shared-pool design amplified the blast radius across multiple project tokens.
Explorer URLs: Ethereum vulnerable contract: https://etherscan.io/address/0xa98f06312b7614523d0f5e725e15fd20fb1b99f5. Attacker: https://etherscan.io/address/0x78c9b11853e4f183a34c63ffd1924d2319a2f5b3. Blockaid and Phalcon listed sample transactions including the Ethereum main drain and the multi-schedule example (full hashes in the original posts). This brief does not invent additional transaction hashes beyond those cited by sources.
Status: First reported 14 Oct by Blockaid; material multi-chain escalation confirmed 15 Oct. UNCX has applied containment measures (high fees, disabled bypasses). Coordinating with law enforcement and SEAL_911. 10% bounty offered for return of 90% to designated multisig. No recoveries confirmed in the posts read for this cutoff. Comprehensive incident report expected this week. Users advised against trading affected pools until token-team guidance.
Sources: https://x.com/blockaid_/status/2110616419939566029, https://x.com/DefimonAlerts/status/2110417910048956515, https://x.com/SlowMist_Team/status/2110565552083325032, https://x.com/Phalcon_xyz/status/2110684882443870452, https://x.com/UNCX_token/status/2110506196339941423, and secondary coverage from CryptoTimes, CryptoBriefing and others.
Also noted
- CL8Y Asset Recovery Notice (unverified, no scored loss): DefimonAlerts posted on-chain messages on 15 Oct referencing a 15 October 2026 incident and coordinating recovery for addresses funded from an exchange withdrawal. Contact details provided. No independent confirmation of protocol type, loss figure, or attacker details in the monitored feeds used for scoring. Flagged as unverified pending further reports. Not added to the live-loss total.
- Gamdom hot-wallet breach (UPDATE, not re-scored): Outflows from hot wallets began 13 Oct across multiple chains. Founder Felix Romer confirmed on 14 Oct a loss of just over $3 million and that remaining hot-wallet funds were moved to cold storage. Independent on-chain estimates (vxdb and others) place the figure near $4.2 million. First reported outside the strict last-24h window for new scoring; no material new loss figure used for this card. Platform taken offline then prepared for restart.
- THEO / Hyperlane (UPDATE, not re-scored): Unbacked mint on Base (~$1.76M) remains on the 13 Oct brief. No material new figures in this window.
- Prior items (not re-scored): 79Vault, Ledger/CryptoBilis, BitBay, EtherVista, Papertrade and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the UNCX escalation.
Sources and references
- Blockaid multi-chain update: https://x.com/blockaid_/status/2110616419939566029
- DefimonAlerts initial alert: https://x.com/DefimonAlerts/status/2110417910048956515
- SlowMist TI Alert: https://x.com/SlowMist_Team/status/2110565552083325032
- Phalcon_xyz technical breakdown: https://x.com/Phalcon_xyz/status/2110684882443870452
- UNCX official update: https://x.com/UNCX_token/status/2110506196339941423
- UNCX recovery message: https://x.com/UNCX_token/status/2110683296115966234
- CryptoTimes escalation coverage: https://www.cryptotimes.io/2026/10/15/uncx-exploit-escalates-vesting-v2-bug-drains-1-5m-across-4-chains-as-copycats-join-in/
Editor’s note: the scored live loss on this card is approximately $1.49 million from the UNCX Vesting V2 share-accounting logic error across four chains. The initial Ethereum drain was first flagged 14 Oct; the multi-chain total and copycat activity constitute the material update scored for this window. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. Prior-day items remain on their original briefs and are not re-scored. CL8Y recovery notice is noted as unverified. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
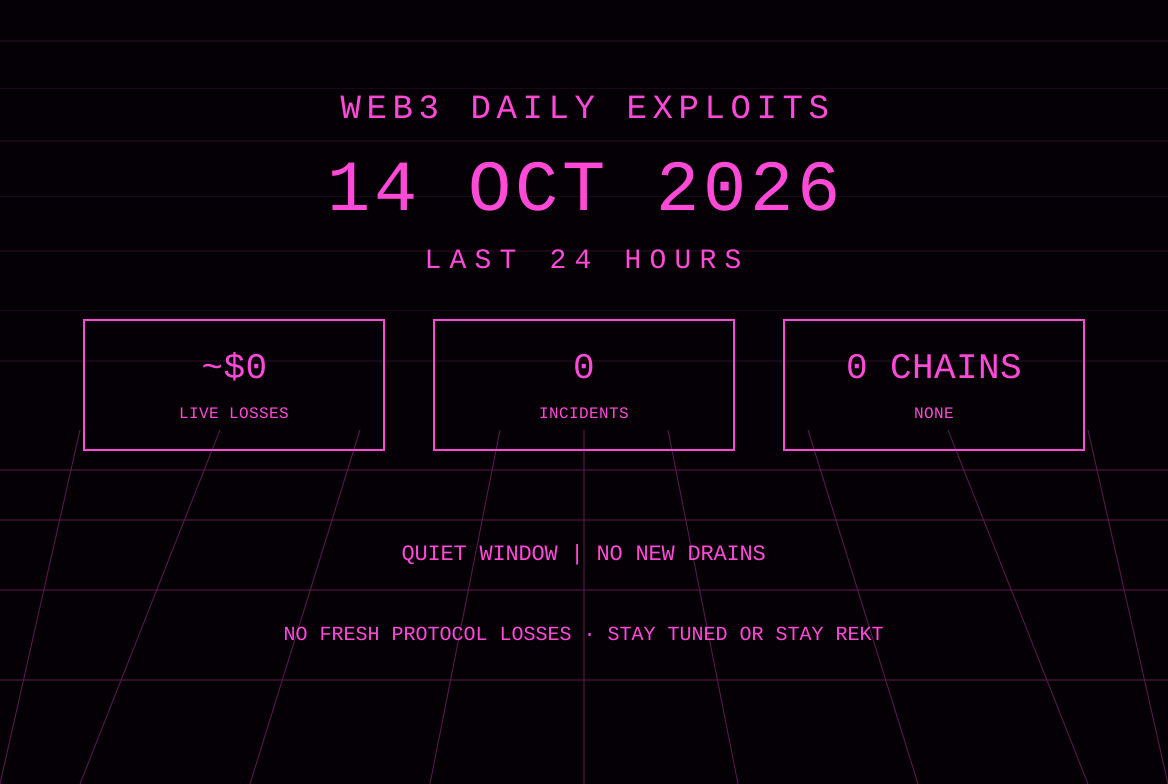
Web3 Daily Exploits — 14 Oct 2026: Quiet Window, No New Protocol Drains
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits or user-wallet drains with fresh loss figures in the last 24 hours. Combined live loss on this card is ~$0. THEO Hyperlane mint remains on the 13 Oct brief. iOS Safari advisory noted with no confirmed crypto theft.
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.
Web3 Daily Exploits — 11 Oct 2026: Ledger Implant Confirmed, 2,990 ETH to Tornado
UPDATE on the CryptoBilis Ledger supply-chain incident. Ledger confirms an unauthorized hardware implant in one affected user device. On-chain researchers report the attacker deposited 2,990 ETH worth about $7.45 million into Tornado Cash between 9 and 10 Oct, with further deposits continuing on 11 Oct. No new protocol drains in the window.