Web3 Daily Exploits — 17 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including Kolan, UNCX, Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery.
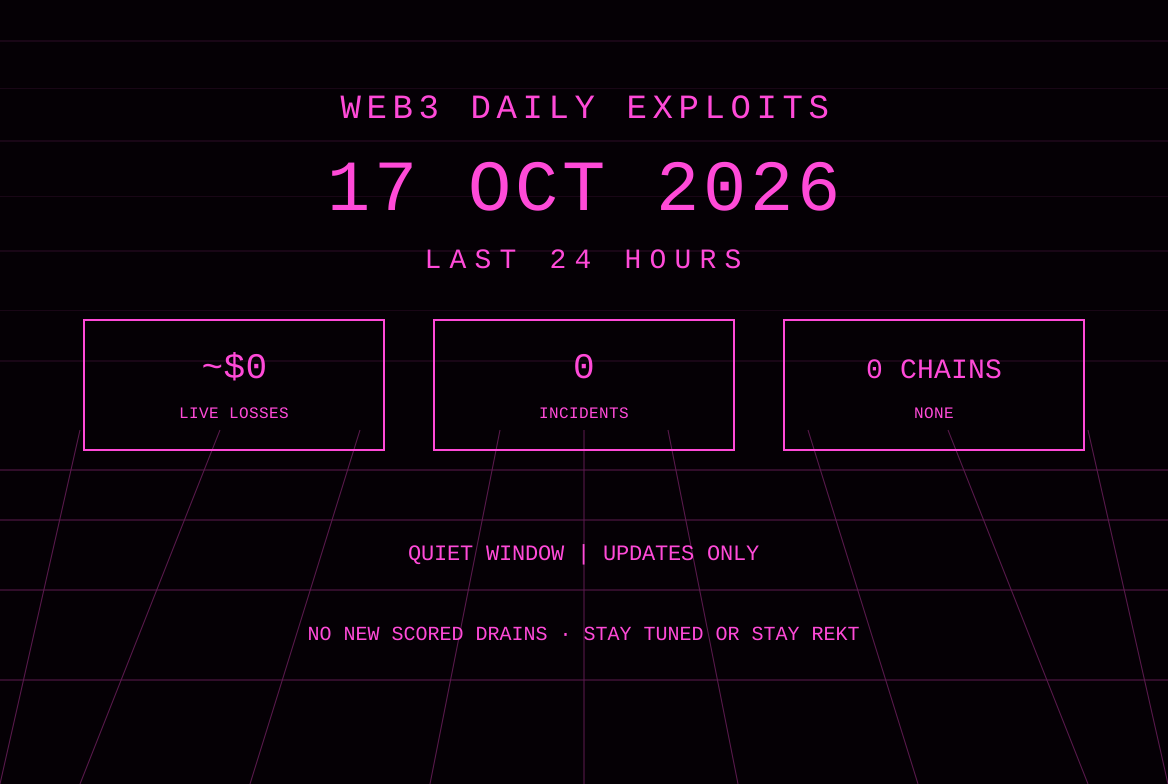
The 17 Oct America/Panama window records no first-report protocol incidents used for scoring. Combined live loss on this card is $0. Required monitors including DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news posted no new smart-contract exploits with fresh loss figures in the last 24 hours. Prior items remain on their original briefs and are noted only as updates. No new hashes, loss amounts, or recovery figures are invented.
Also noted
- Kolan Protocol Uniswap V4 Hook (UPDATE, not re-scored): The ~$3,000 flash-loan price manipulation via permissionless accept() and no-slippage buyback remains on the 16 Oct brief. No material new loss figures or confirmed recoveries in this window. Attacker proceeds remain under control of 0x8df735014eab81905e76b87ef0c069bd8e0ae382.
- UNCX Network Vesting V2 (UPDATE, not re-scored): Multi-chain share-accounting drain of approximately $1.49 million remains on the 15 Oct brief. Containment measures (high fees, disabled bypasses) in place. No material new loss figures or confirmed recoveries in this window. 10% white-hat bounty offer outstanding.
- Pirate Chain (ARRR) unbacked mint (UPDATE, not re-scored): Official project updates confirmed an October 14 transaction-validation vulnerability that allowed unauthorized creation of approximately 39.8 million ARRR, increasing supply by about 20%. Newly minted funds moved into the Sapling shielded pool. The project stated a unilateral rollback is not possible due to decentralization; dPoW notarizations paused and exchanges/mining pools asked to voluntarily pause. First reported outside the strict last-24h window for new scoring; no USD loss figure used for this card. Post-mortem pending.
- Bofur Capital related address (UPDATE, not re-scored): PeckShieldAlert noted on 16 Oct that the phisher who drained approximately $2 million in DAI has swapped the stolen funds for 825.5 ETH. Original drain outside the scoring window; the swap is a material movement of prior proceeds but not added to live-loss total.
- Fake Ledger firmware update phishing (no scored loss): SlowMist posted a TI Alert on 16 Oct warning of a fake “Ledger firmware update” campaign exploiting the recent Ledger / CryptoBilis supply-chain incident. Pages mimic Genuine Check and device selection with an “Update Now” button. Users advised never to click website links for updates and never to enter recovery phrases. No confirmed theft figures tied to this specific campaign in the monitored posts.
- Defimon recovery to known exploit address (unverified impact): On-chain messages on 16 Oct note that automated Defimon claims of stale Sui Bridge withdrawals sent approximately $392K to an address publicly associated with the Cetus exploit (0x89012a55cd6b88e407c9d4ae9b3425f55924919b). Defimon acknowledged the screening gap and stated the funds remain unmoved. Not a new protocol exploit; noted as an operational incident. Not scored.
- Gamdom hot-wallet breach (UPDATE, not re-scored): The October 13 incident (founder reported just over $3M, on-chain trackers nearer $4.2M across multiple chains) remains prior to this window. Site reported back online on 16 Oct with compensation packages. No new scored loss or material recovery confirmation used for this card.
- CL8Y Asset Recovery Notice (unverified, no scored loss): DefimonAlerts continued posting on-chain recovery coordination messages. No independent confirmation of protocol type or loss figure used for scoring.
- Prior items (not re-scored): THEO / Hyperlane, 79Vault, Ledger / CryptoBilis implant, BitBay, EtherVista, NEAR Intents, and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures.
Sources and references
- PeckShieldAlert Bofur Capital swap: https://x.com/PeckShieldAlert/status/2110899366429102307
- SlowMist fake Ledger firmware TI Alert: https://x.com/SlowMist_Team/status/2110988183039332417
- DefimonAlerts on-chain Cetus-related claim messages: https://x.com/DefimonAlerts/status/2110968667676537104
- Pirate Chain official update: https://x.com/PirateChain/status/2110774266123767871
- 16 Oct brief for Kolan coverage: https://www.rektradar.xyz/web3-daily-exploits-16-oct-2026-kolan-3k-uniswap-v4-hook/
- 15 Oct brief for full UNCX coverage: https://www.rektradar.xyz/web3-daily-exploits-15-oct-2026-uncx-vesting-1-49m-share-accounting/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is $0. No new first-report protocol drains with fresh figures were posted by the monitored accounts as of the latest cutoff. Prior-day items including Kolan and UNCX remain on their original briefs and are not re-scored. Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery are noted as updates or advisories without new scored losses. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
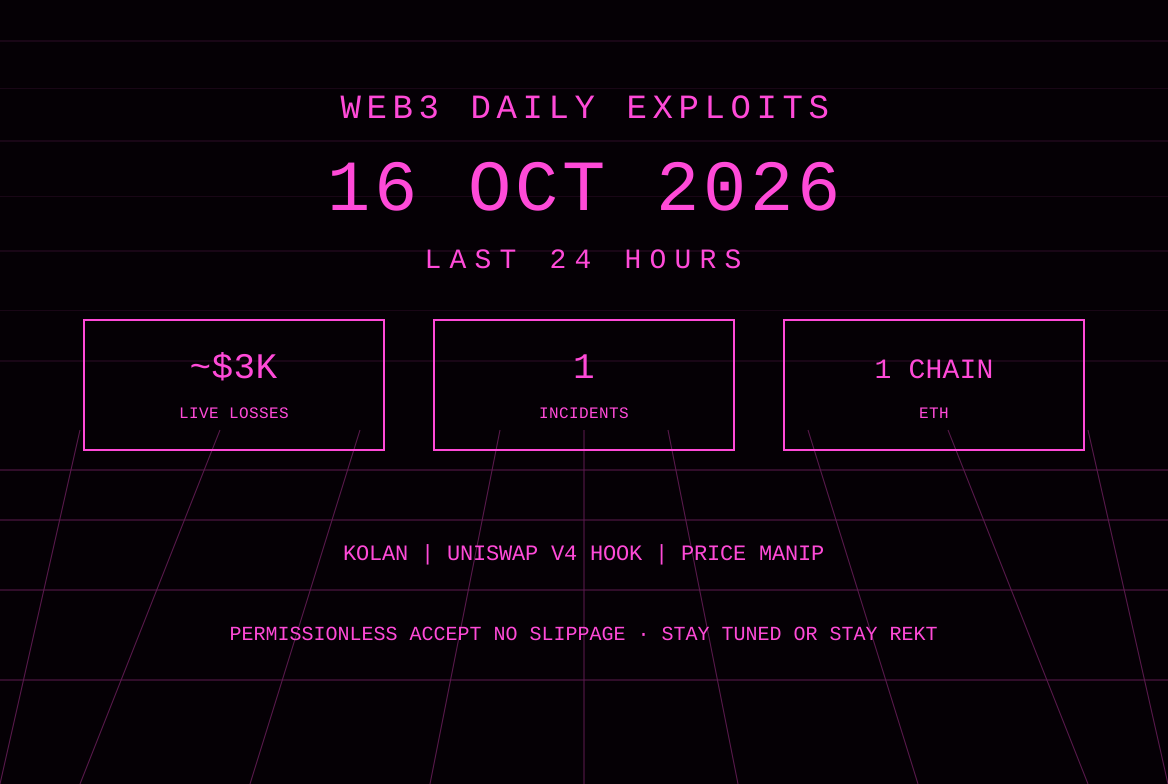
Web3 Daily Exploits — 16 Oct 2026: Kolan Uniswap V4 Hook ~$3K Price Manipulation
Small scored incident: Kolan Uniswap V4 hook drained ~$3K via flash-loan price manipulation on permissionless accept() with no slippage guard on buyback. Live loss ~$3K, 1 incident, 1 chain (ETH). Prior items including UNCX and Bofur Capital noted as updates.
Web3 Daily Exploits — 15 Oct 2026: UNCX Vesting V2 ~$1.49M Multi-Chain Share Accounting Drain
UNCX Network Vesting V2 shared pools exploited via share-accounting flaw in cancel() and release(). Blockaid reports ~$1.49M drained across Ethereum, BSC, Base and Robinhood Chain involving 10 tokens and copycats. Containment via high fees. One incident, four chains.
Web3 Daily Exploits — 14 Oct 2026: Quiet Window, No New Protocol Drains
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits or user-wallet drains with fresh loss figures in the last 24 hours. Combined live loss on this card is ~$0. THEO Hyperlane mint remains on the 13 Oct brief. iOS Safari advisory noted with no confirmed crypto theft.
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.