Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.
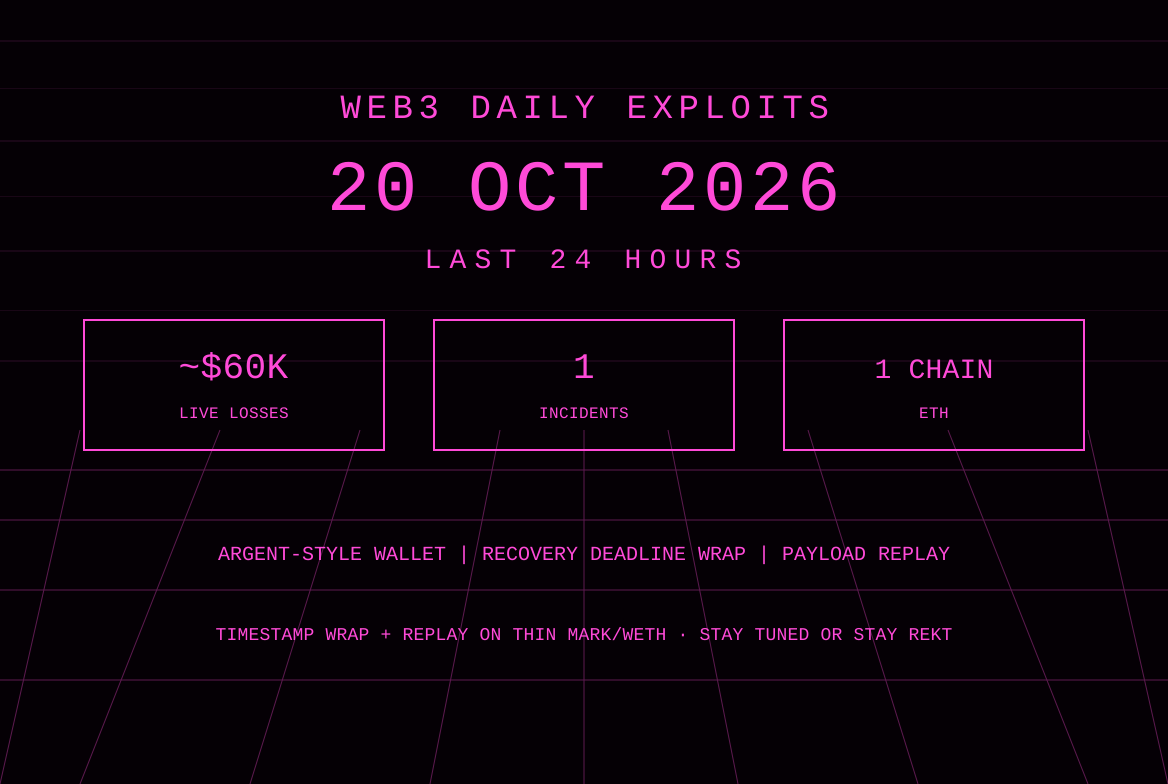
The 20 Oct America/Panama window records one first-report protocol incident used for scoring: an Argent-style smart wallet system on Ethereum was drained for approximately $59.8K after the recovery module’s unrestricted setter allowed a crafted recovery period that made the calculated deadline wrap to a timestamp in the past, enabling same-transaction finalization of a guardian-signed recovery and owner change, while the execution module failed to reject reuse of an identical signed payload that was executed repeatedly against a low-liquidity MARK/WETH pool. Combined live loss on this card is about $60K. SlowMist posted the detection on 19 Oct. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. Movements of previously stolen funds by the Drift Protocol and Aztec exploiters into Tornado Cash, plus further analysis of the Qubic weak-seed incident, remain UPDATES and are not re-scored.
Argent-style smart wallet system — Ethereum — about $59.8K — recovery deadline wrap + signed payload replay
What happened: On 19 Oct 2026 SlowMist issued a threat-intelligence alert for an Argent-style smart wallet system on Ethereum. The recovery module contained an unrestricted 0x254a2e49 setter that allowed a crafted recovery period to cause the calculated deadline to wrap to a timestamp in the past. This permitted a recovery backed by a valid guardian signature to be finalized in the same transaction, changing the wallet owner. Separately, the execution module failed to reject reuse of an identical signed 0xaacaaf88 payload; the same payload succeeded 19 times in one transaction and nine times in the other. The attacker used the repeated executions to trade around a low-liquidity MARK/WETH Uniswap V2 pool. Attacker address: 0xc10609ce5c032db92e562e463b1234aab0872b02. Victim wallets: 0xe545b9a69bff1bf0ed2e922551dda4afc8ee8f66 and 0x5a79e5772493cf4329682d202aa2d28f85a85440. Vulnerable contracts: 0xf490557d67d934440677a4f16793d5ef319b8ef5 and 0x4e50adfc953551286bbd7fee2b2b846d1d227394. A representative transaction (0xbfed8d33561ed5f9cbd0f4e62a5bbd20187a64f3e22180148dcb58ed6ebaa795, block 26225798, ~09:42 UTC 19 Oct) shows the attacker interacting with the module, ownership changes on the victim wallet, repeated MARK/WETH swaps, a Balancer flash loan, and final conversion toward USDC.
Protocol / chain / asset: Argent-style smart wallet system (recovery and execution modules; not confirmed as the official Argent product). Chain: Ethereum. Assets affected via the victim wallets and the MARK/WETH pool. The loss stems from the combination of the unrestricted recovery-period setter (timestamp wrap) and the missing replay protection on signed execution payloads, which together allowed control of the wallets and repeated trading against thin liquidity.
Loss: Approximately $59.8K per SlowMist. Figures reflect the value extracted through the wallet takeovers and subsequent trading activity. No additional external user-wallet drains beyond the two listed victims are included in the scored total.
Attack type: Logic error / integer wrap in recovery-deadline calculation combined with missing replay protection on signed execution payloads. Not a classic reentrancy, not an oracle manipulation, and not a private-key compromise of an end-user seed. The unrestricted setter and the repeated execution of the same signed payload made the vector practical once a valid guardian signature was available.
Explorer URLs: Attacker: https://etherscan.io/address/0xc10609ce5c032db92e562e463b1234aab0872b02. Victim 1: https://etherscan.io/address/0xe545b9a69bff1bf0ed2e922551dda4afc8ee8f66. Victim 2: https://etherscan.io/address/0x5a79e5772493cf4329682d202aa2d28f85a85440. Vulnerable contract 1: https://etherscan.io/address/0xf490557d67d934440677a4f16793d5ef319b8ef5. Vulnerable contract 2: https://etherscan.io/address/0x4e50adfc953551286bbd7fee2b2b846d1d227394. Representative tx: https://etherscan.io/tx/0xbfed8d33561ed5f9cbd0f4e62a5bbd20187a64f3e22180148dcb58ed6ebaa795. Ethereum explorer base: https://etherscan.io/.
Status: First reported 19 Oct by SlowMist. Attack executed. No official protocol recovery announcement or user guidance observed in the monitored feeds as of this cutoff. Users of similar Argent-style recovery and execution modules should review recovery-period setters and payload-replay protections.
Sources: https://x.com/SlowMist_Team/status/2112157232624476254.
Also noted
- Drift Protocol exploiter (UPDATE, not re-scored): The address labeled as the Drift exploiter (original theft reported over $270M) deposited approximately 21.3K–25.7K ETH (~$50M–$61M) into Tornado Cash after roughly two months of inactivity. Remaining holdings still substantial. PeckShieldAlert and Lookonchain reported the movements on 20 Oct. No new scored loss. https://x.com/PeckShieldAlert/status/2112467387769557111; https://x.com/lookonchain/status/2112475259907846217.
- Aztec exploiter (UPDATE, not re-scored): A labeled Aztec rollup exploiter address (June incident) deposited 1,255.8 ETH (~$3M) into Tornado Cash. CertiKAlert and PeckShieldAlert noted the deposit on 20 Oct. No new scored loss. https://x.com/CertiKAlert/status/2112359201507049692; https://x.com/PeckShieldAlert/status/2112373195294831076.
- Qubic weak-seed wallet drain (UPDATE, not re-scored): Further analysis from SlowMist and GoPlus on the Math.random() seed issue and potential private-key recovery via network observations. Original drain of ~2.94 trillion QU remains on prior briefs. No fresh USD figure added. https://x.com/SlowMist_Team/status/2112471727209161180.
- AlpsCon AI Trade Hub (UPDATE, not re-scored): The ~$152K Hardhat-default + EIP-7702 historical-reward incident remains on the 19 Oct brief. No material new loss figures in this window.
- Prior items (not re-scored): BiFi Lending, UNCX Vesting, Kolan, and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the Argent-style wallet detection.
Sources and references
- SlowMist Argent-style wallet alert: https://x.com/SlowMist_Team/status/2112157232624476254
- Representative transaction: https://etherscan.io/tx/0xbfed8d33561ed5f9cbd0f4e62a5bbd20187a64f3e22180148dcb58ed6ebaa795
- PeckShield Drift deposit: https://x.com/PeckShieldAlert/status/2112467387769557111
- Lookonchain Drift deposit: https://x.com/lookonchain/status/2112475259907846217
- CertiK Aztec deposit: https://x.com/CertiKAlert/status/2112359201507049692
- SlowMist Qubic analysis: https://x.com/SlowMist_Team/status/2112471727209161180
- 19 Oct brief for AlpsCon coverage: https://www.rektradar.xyz/web3-daily-exploits-19-oct-2026-alpscon-152k-hardhat-eip7702/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $60K from the Argent-style smart wallet recovery-deadline wrap and signed-payload replay on Ethereum. The attack was first reported by SlowMist on 19 Oct. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. Fund movements by prior exploiters (Drift, Aztec) and additional Qubic analysis remain on prior coverage or as updates and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
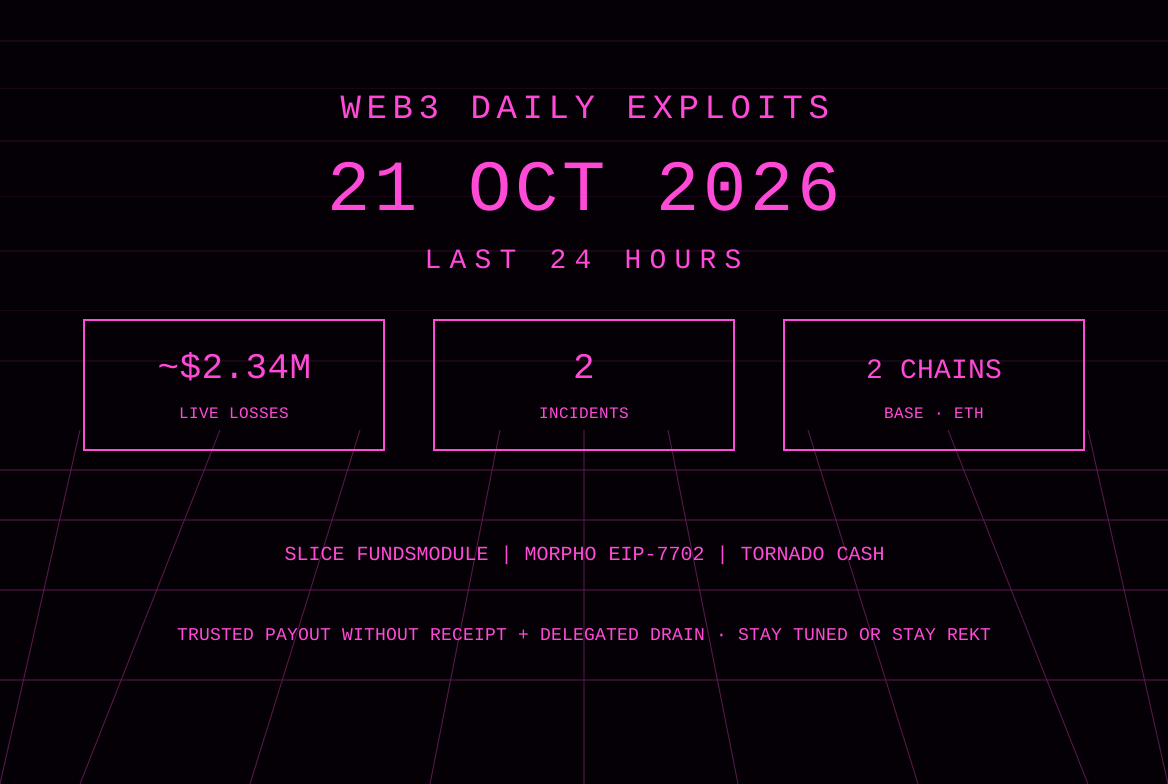
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
Web3 Daily Exploits — 19 Oct 2026: AlpsCon ~$152K Hardhat Default Account + EIP-7702 Reward Bug
AlpsCon AI Trade Hub on BNB Chain drained for ~$152K after a Hardhat default account was left on the KYC whitelist and used via EIP-7702 to claim historical rewards on a fresh stake. DefimonAlerts first report. Live loss ~$152K, 1 incident, 1 chain. Qubic weak-seed drain and BiFi noted as UPDATE.
Web3 Daily Exploits — 18 Oct 2026: BiFi Lending ~$165K Idle-Market Interest Inflation
BiFi Lending USDT market on Ethereum drained for ~$165.4K via interest-calculation inflation after a 36-day idle period. DefimonAlerts first report. Live loss ~$165K, 1 incident, 1 chain. UNCX official verified ~$807.6K with white-hat returns noted as UPDATE.
Web3 Daily Exploits — 17 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including Kolan, UNCX, Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery.