Web3 Daily Exploits — 19 Oct 2026: AlpsCon ~$152K Hardhat Default Account + EIP-7702 Reward Bug
AlpsCon AI Trade Hub on BNB Chain drained for ~$152K after a Hardhat default account was left on the KYC whitelist and used via EIP-7702 to claim historical rewards on a fresh stake. DefimonAlerts first report. Live loss ~$152K, 1 incident, 1 chain. Qubic weak-seed drain and BiFi noted as UPDATE.
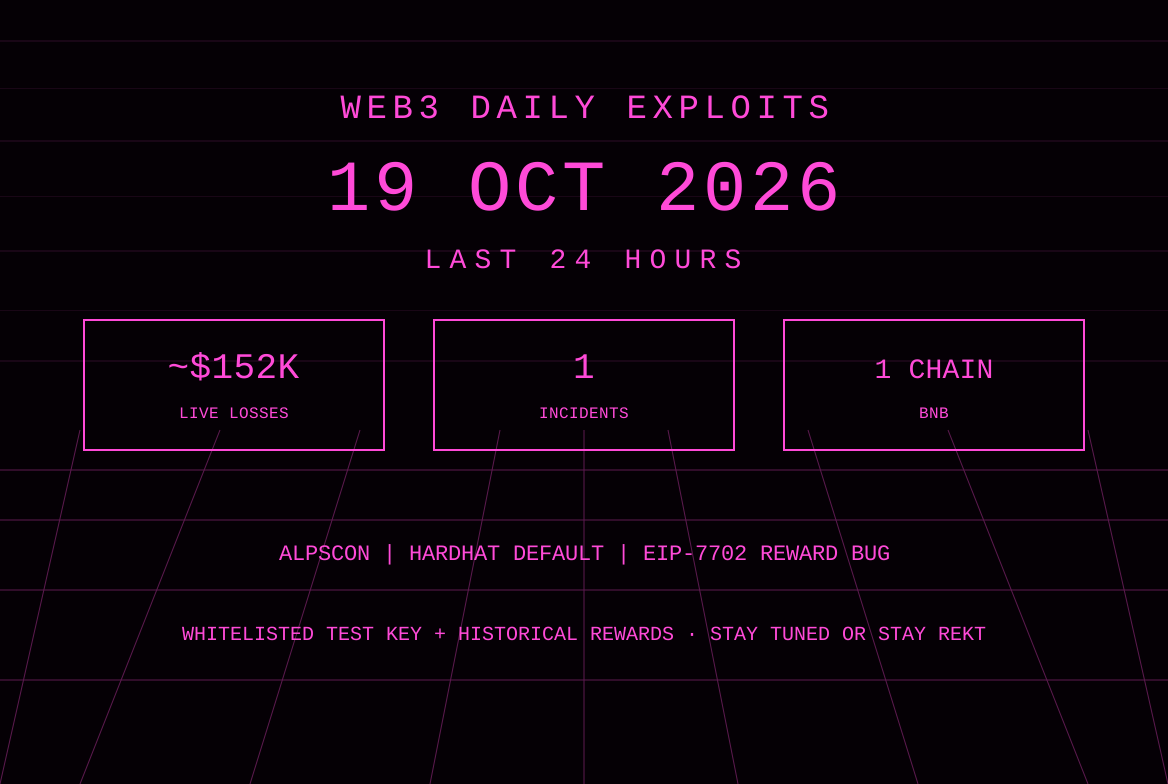
The 19 Oct America/Panama window records one first-report protocol incident used for scoring: AlpsCon’s AI Trade Hub on BNB Chain was drained for approximately $152K after the Hardhat/Anvil default account #0 remained on the KYC whitelist for roughly 14 months and was used via EIP-7702 to execute code that claimed historical rewards against a fresh stake. Combined live loss on this card is about $152K. DefimonAlerts posted the detection on 19 Oct. The attacker flash-loaned roughly 1.03M USDC, acquired and staked ALPS in an older hub that still accepted deposits, then had newer reward contracts treat the stake as if it had existed from the start, paying out accumulated rewards of about $355K USDC before unstaking, selling, and repaying the loan for a net of ~$152K. No other first-report smart-contract exploits with fresh scored loss figures were posted by the required monitors. Qubic’s weak-seed wallet drain of ~2.94 trillion QU and the prior BiFi Lending interest-inflation event remain UPDATES and are not re-scored.
AlpsCon AI Trade Hub — BNB Chain — about $152K — Hardhat default whitelist + EIP-7702 + historical reward accounting
What happened: On 19 Oct 2026 DefimonAlerts detected an exploit against AlpsCon.ai, an AI trading service in which users stake ALPS tokens to earn USDC rewards. Staking and claiming are restricted to KYC-whitelisted wallets. The whitelist included the Hardhat/Anvil default account #0 (0xf39fd6e51aad88f6f4ce6ab8827279cfffb92266), whose private key is publicly known. The deployer added the address in a bulk import on 2025-08-24; it remained whitelisted for approximately 14 months. The attacker used the public key to sign an EIP-7702 delegation and executed exploit code in the context of the whitelisted account. They flash-loaned about 1.03M USDC, bought ALPS, and staked it in an older hub contract that still accepted deposits. Newer reward contracts (V7–V9) recursively imported balances from the preceding version and applied each version’s already-accumulated profitPerShare while the new account’s entryProfitPerShare remained zero. This allowed a fresh deposit to claim distributions that had been made before the stake existed, yielding roughly $355K USDC that emptied the main reward pool. The attacker then unstaked, sold the ALPS, and repaid the loan, netting approximately $152K (ExVul reported 152,809.3575 USDC lost by the hub and 152,295.3625 USDC received by the attacker before gas). The deployer removed the address from the whitelist on 2026-10-18 at 11:40 UTC, roughly five hours after the attack.
Protocol / chain / asset: AlpsCon (AI trading / staking rewards service). Chain: BNB Smart Chain. Asset: USDC rewards drawn from the AI Trade Hub. Attacker: 0x3d9df7d20d8296286383ffe475aa7b9e548946b2. Delegated/whitelisted account: 0xf39fd6e51aad88f6f4ce6ab8827279cfffb92266. Victim contract (AI Trade Hub V9): 0x9b210da482217afc24074e57f6f8337fe07f0124. The loss stems from the combination of a long-lived public test key on the whitelist and reward-accounting logic that credited historical profit to a newly visible stake.
Loss: Approximately $152K (152,809.3575 USDC per ExVul; ~$152K per DefimonAlerts). The figure reflects the net USDC extracted after the flash-loan repayment. No additional user-wallet drains outside the reward pool are included in the scored total.
Attack type: Access-control failure (public Hardhat default account left on KYC whitelist) combined with EIP-7702 code execution in that account’s context and a reward-accounting logic error (historical profitPerShare applied to a fresh stake whose entryProfitPerShare was zero). Not a classic reentrancy, not an oracle manipulation, and not a private-key compromise of the protocol deployer itself. The public nature of the Hardhat key and the persistence of the whitelist entry made the vector practical.
Explorer URLs: Attacker: https://bscscan.com/address/0x3d9df7d20d8296286383ffe475aa7b9e548946b2. Whitelisted Hardhat account: https://bscscan.com/address/0xf39fd6e51aad88f6f4ce6ab8827279cfffb92266. Victim (AI Trade Hub V9): https://bscscan.com/address/0x9b210da482217afc24074e57f6f8337fe07f0124. DefimonAlerts and ExVul provided shortened transaction links in their posts; full hashes are not restated beyond the addresses cited by the sources. BNB Chain explorer base: https://bscscan.com/.
Status: First reported 19 Oct by DefimonAlerts. Attack executed; whitelist entry removed by the deployer approximately five hours later. No official protocol recovery announcement or user guidance observed in the monitored feeds as of this cutoff. Users of the AlpsCon reward contracts should treat positions as at risk until the team posts a statement.
Sources: https://x.com/DefimonAlerts/status/2112102178026308045; https://x.com/exvulsec/status/2112118384464892127.
Also noted
- Qubic weak-seed wallet drain (UPDATE, not re-scored): Between 23:42 UTC on 17 Oct and 01:26 UTC on 18 Oct an attacker drained 1,404 Qubic wallets totaling around 2.94 trillion QU (reported ~$1.3M–$1.4M at the time). Root cause was insufficient randomness in seed generation (Math.random() on certain Apple/Safari/iOS environments), not the Qubic protocol. Validators halted the network at tick 85,371,949; 87.1% of drained funds remained frozen on-chain and 12.9% was frozen at MEXC. Seed generation fixed in wallet version 4.26.4. Official update and subsequent coverage fall partly outside the strict last-24h first-report window for new scoring; no fresh USD figure is added to this card. Phalcon noted the February report and the matching fix. Full official thread: https://x.com/_Qubic_/status/2111796725677715474.
- BiFi Lending USDT market (UPDATE, not re-scored): The ~$165.4K interest-calculation inflation after a 36-day idle period remains on the 18 Oct brief. No material new loss figures in this window.
- UNCX Network Vesting V2 (UPDATE, not re-scored): Official verified realized economic value of approximately $807,609 remains prior. No new scored loss.
- Prior items (not re-scored): Kolan Protocol, Pirate Chain, XPR/LOAN, THEO / Hyperlane, 79Vault, Ledger / CryptoBilis, BitBay, EtherVista, NEAR Intents and earlier September incidents remain as previously briefed. No material new loss figures used for scoring.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news. No additional first-report protocol exploits with fresh scored loss figures beyond the AlpsCon detection.
Sources and references
- DefimonAlerts AlpsCon detection: https://x.com/DefimonAlerts/status/2112102178026308045
- ExVul technical breakdown: https://x.com/exvulsec/status/2112118384464892127
- Qubic official security update: https://x.com/_Qubic_/status/2111796725677715474
- Phalcon on Qubic seed issue: https://x.com/Phalcon_xyz/status/2112059239829242142
- 18 Oct brief for BiFi coverage: https://www.rektradar.xyz/web3-daily-exploits-18-oct-2026-bifi-165k-interest-calc/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh loss figures in the last 24 hours.
Editor’s note: the scored live loss on this card is approximately $152K from the AlpsCon AI Trade Hub reward-pool drain on BNB Chain. The attack was first reported by DefimonAlerts on 19 Oct and combined a long-lived Hardhat default account on the KYC whitelist with EIP-7702 execution and historical reward accounting. No other new first-report protocol drains with fresh figures were posted by the monitored accounts. Prior items including Qubic and BiFi remain on prior coverage or as updates and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
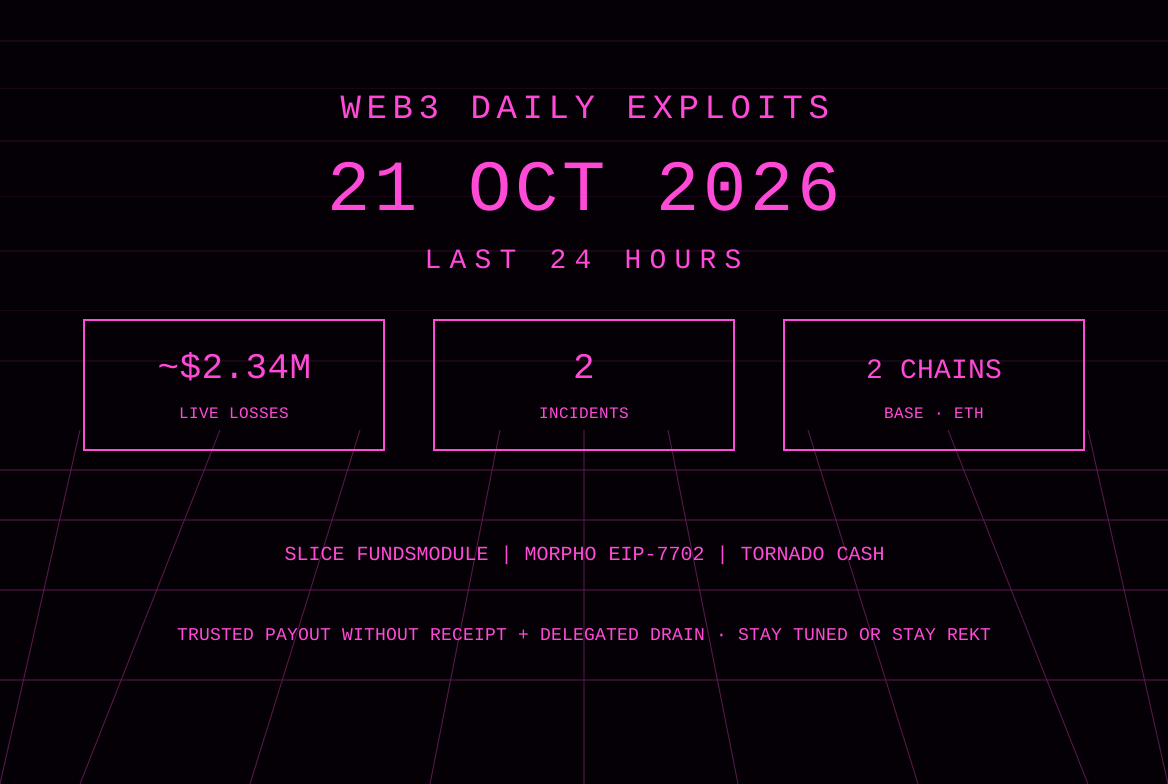
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.
Web3 Daily Exploits — 18 Oct 2026: BiFi Lending ~$165K Idle-Market Interest Inflation
BiFi Lending USDT market on Ethereum drained for ~$165.4K via interest-calculation inflation after a 36-day idle period. DefimonAlerts first report. Live loss ~$165K, 1 incident, 1 chain. UNCX official verified ~$807.6K with white-hat returns noted as UPDATE.
Web3 Daily Exploits — 17 Oct 2026: Quiet Window, No New Scored Drains
Quiet America/Panama window: no first-report protocol exploits with fresh scored loss figures from required monitors. Live loss $0, 0 incidents, 0 chains. Updates on prior items including Kolan, UNCX, Pirate Chain, Bofur Capital, Ledger phishing, Defimon Sui Bridge claim, and Gamdom recovery.