Web3 Daily Exploits — 9 Nov 2026: Ankr ~$304K Bridge, Zenji ~$5K Oracle
Two first-report incidents: Ankr Ethereum cross-chain bridge drained ~$304.5K via five forged receipts carrying valid consensus signatures that referenced one already-redeemed Optimism deposit; Zenji leveraged LlamaLend vaults lost ~$4.9K to flash-loan oracle/price manipulation of a Curve StableNG pool. Combined live scored ~$309K across ETH and OP. Keplr/Web3Auth remains UPDATE.
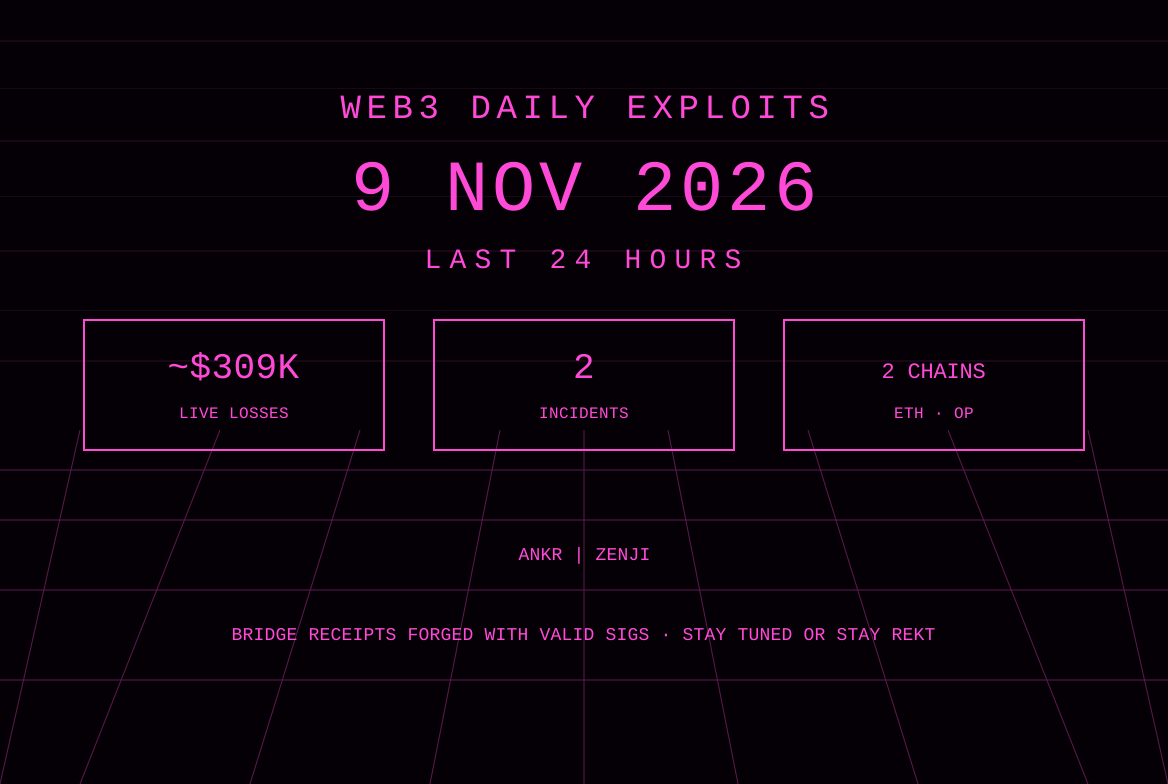
The 9 Nov America/Panama window records two first-reported protocol incidents with confirmed scored losses. Ankr’s Ethereum cross-chain bridge was drained for approximately $304.5K (SlowMist; other monitors range ~$286K–$303.6K) after an attacker submitted five forged withdrawal receipts that reused a single legitimate, already-redeemed Optimism deposit and carried valid signatures from the bridge’s trusted consensus signer. The withdraw function released assets without independently verifying the source-chain events. Separately, Zenji’s leveraged LlamaLend vaults on Ethereum lost roughly $4.9K to a flash-loan oracle/price-manipulation attack against a Curve StableNG pool used both for valuation and for unwinding. Combined live scored loss on this card is ~$309K across two incidents and two chains (Ethereum and Optimism). The Keplr/Web3Auth social-login key-exposure case remains an UPDATE with no material new scored loss in the last 24 hours.
Ankr Ethereum cross-chain bridge — Ethereum / Optimism — ~$304.5K — forged receipts with valid signatures
What happened: Beginning early 9 November 2026, an attacker submitted five withdraw calls against Ankr’s Ethereum bridge contract. Each call referenced the same legitimate Optimism deposit transaction (a small 0.0044 ankrETH transfer dated 3 November that had already been redeemed on Ethereum). The attacker altered the recipient address, the token type, and the withdrawal amounts on the forged receipts. All five receipts carried valid signatures from the bridge’s designated consensus signer, allowing the withdraw function to release the requested assets without an independent check against the actual source-chain event logs. Blockaid first flagged the activity as an ongoing exploit; SlowMist, PeckShield and The Defiant subsequently confirmed the drain. Most stolen funds were swapped for ETH. At the time of early reporting the contract’s pause flag remained false. The origin of the unauthorized signatures is under investigation; signer-key compromise has not been confirmed.
Protocol / chain / asset: Ankr cross-chain bridge (Ethereum side). Source chain: Optimism. Assets drained included ankrETH, ankrPOL, ANKR, aMATICb and aETHb. Recipient wallet received the tokens; a large portion was later swapped to ~103 ETH.
Loss: SlowMist: ~$304.5K. PeckShield: ~$286K (5,372 aMATICb, 515.2K ankrPOL, ~8M of token 0x8290333cef9e6d528dd5618fb97a76f268f3edd4, 83 ankrETH, later swapped to 103 ETH). Blockaid: ~$292K. The Defiant / PrimeXBT: ~$303.6K (priced components ~$216K ankrETH + ~$56K ankrPOL + ~$31K ANKR). Live scored on this brief: ~$304.5K (highest consistent monitor figure). Exact net realized proceeds after swaps remain subject to price movement.
Attack type: Cross-chain bridge receipt forgery / authorization bypass. Valid signatures on altered receipts that reused an already-redeemed source deposit; missing independent source-chain event verification.
Explorer URLs: Vulnerable contract: https://etherscan.io/address/0xc437DF90B37C1dB6657339E31BfE54627f0e7181. Attacker (tx sender): https://etherscan.io/address/0x9A88Dd45AE846A979705c9cFdfD0f229e592D703. Recipient: https://etherscan.io/address/0x119D250b82C1cf5345dF5912EFb4B1a4107a1Aa6. Example attack tx (TraceFast): https://tracefast.xyz/tx/0x7310af5d53e08259915bc3547daf343d188b9c36db8dd6b3ff3b5e70565e88df. Full attack tx list in SlowMist alert.
Status: Confirmed by SlowMist, PeckShield, Blockaid and The Defiant. Pause flag was still false in early reports; containment status unconfirmed at cutoff. Signer-compromise not established. No official Ankr reimbursement announcement located. Flag unverified exact final USD totals pending post-swap pricing.
Sources: SlowMist TI Alert; PeckShieldAlert; Blockaid; The Defiant; PrimeXBT; Onchain Lens / Odaily.
Zenji (ZenSats) leveraged LlamaLend vaults — Ethereum — ~$4.9K — flash-loan oracle / price manipulation
What happened: On 8–9 November 2026 an attacker flash-borrowed 7.24M USDT from Morpho and swapped into the crvUSD/USDT StableNG pool to skew its internal metrics. The attacker then called the permissionless rebalance() on Zenji’s leveraged LlamaLend vaults (ZenjiWstEthLlamaUsdtStakeDao and related). The vault valued its StakeDAO Curve-LP strategy and LTV/strategy-debt ratio using the same pool’s get_virtual_price and calc_withdraw_one_coin, treating the manipulated state as out-of-band. The vault deleveraged by withdrawing LP and trading crvUSD through the skewed pool at a disadvantageous price. The attacker reversed the swap and captured the spread. The swap’s minOut floor reused the same manipulable pool quote and therefore offered no protection. DefimonAlerts reported net ~$4.95K USDT to the attacker and ~$8.36K drained from the Curve pool. A patch commit was published shortly after the alert.
Protocol / chain / asset: Zenji / ZenSats (zensats.app) leveraged LlamaLend vaults on Ethereum. Assets: USDT / crvUSD. Vault examples: 0x23f1…dd2c, 0x18e2…3f74. Pool: 0x390f…7bf4.
Loss: DefimonAlerts: ~$4.9K–$4.95K net to attacker. Live scored on this brief: ~$4.9K.
Attack type: Flash-loan oracle / price-manipulation (permissionless rebalance using manipulable pool metrics for both valuation and unwind).
Explorer URLs: DefimonAlerts alert contains the primary TX, attacker and victim links (shortened at source). Patch: https://github.com/NateBrune/ZenSats-contracts/commit/df541b7aeb21180bff5e3377cabff616430e0d40. Full addresses and TX in the original DefimonAlerts post: https://x.com/DefimonAlerts/status/2119693714272497877.
Status: Confirmed by DefimonAlerts with on-chain details. Patch published. No larger follow-on drains reported at cutoff. Flag any subsequent quantified recovery or additional vault impact as material.
Sources: DefimonAlerts; ZenSats contracts GitHub.
Also noted
- Keplr Wallet / Web3Auth social-login key exposure (UPDATE, not re-scored): First reported 6 November. Bitquery prior trace ~$6.01M from 44k+ wallets; recovery addresses published 8 November. GoPlus re-flagged the issue on 9 November with lower “at least ~$1M stolen / ~$6M moved to recovery” language. No material new first-report loss figure. Prior coverage: https://www.rektradar.xyz/web3-daily-exploits-08-nov-2026-quiet-window-keplr-6m-update/.
- SlowMist infostealer warning (not scored): “Cracked TradingView Premium” campaign distributing an infostealer that harvests browser, wallet and Telegram data. No protocol loss attributed. Flag as malware distribution, not a smart-contract incident.
- Prior items (UPDATE, not re-scored): Loopscale (vaults made whole), FLOKI bot (loss undisclosed), TENDRIL (~$555K prior), Binance hot-wallet signing compromise, Mercado Bitcoin. No material new scored figures in the last 24 hours.
- Other notes: No additional first-report protocol drains with fresh confirmed user-loss figures from monitored accounts. Scattered individual seed or device reports remain unverified and unattributed to any protocol.
Sources and references
- SlowMist Ankr alert: https://x.com/SlowMist_Team/status/2119720284093890615
- PeckShieldAlert Ankr: https://x.com/PeckShieldAlert/status/2119730625695662322
- Blockaid Ankr: https://x.com/blockaid_/status/2119712260184527262
- DefimonAlerts Zenji: https://x.com/DefimonAlerts/status/2119693714272497877
- The Defiant Ankr coverage: https://thedefiant.io/news/hacks/ankr-ethereum-bridge-loses-more-than-303-000-in-five-transaction-exploit
- ZenSats patch: https://github.com/NateBrune/ZenSats-contracts/commit/df541b7aeb21180bff5e3377cabff616430e0d40
- 8 Nov brief (Keplr UPDATE): https://www.rektradar.xyz/web3-daily-exploits-08-nov-2026-quiet-window-keplr-6m-update/
- Monitored accounts checked: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news. No additional first-report protocol exploits with fresh scored user-loss figures beyond the two items above.
Editor’s note: the scored live loss on this card is ~$309K across two first-report incidents (Ankr bridge ~$304.5K, Zenji ~$4.9K). Loss figures for Ankr vary slightly across monitors; the SlowMist figure is used for scoring. Keplr/Web3Auth remains an UPDATE. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 10 Nov 2026: Initia ~$615K IBC Escrow Halt
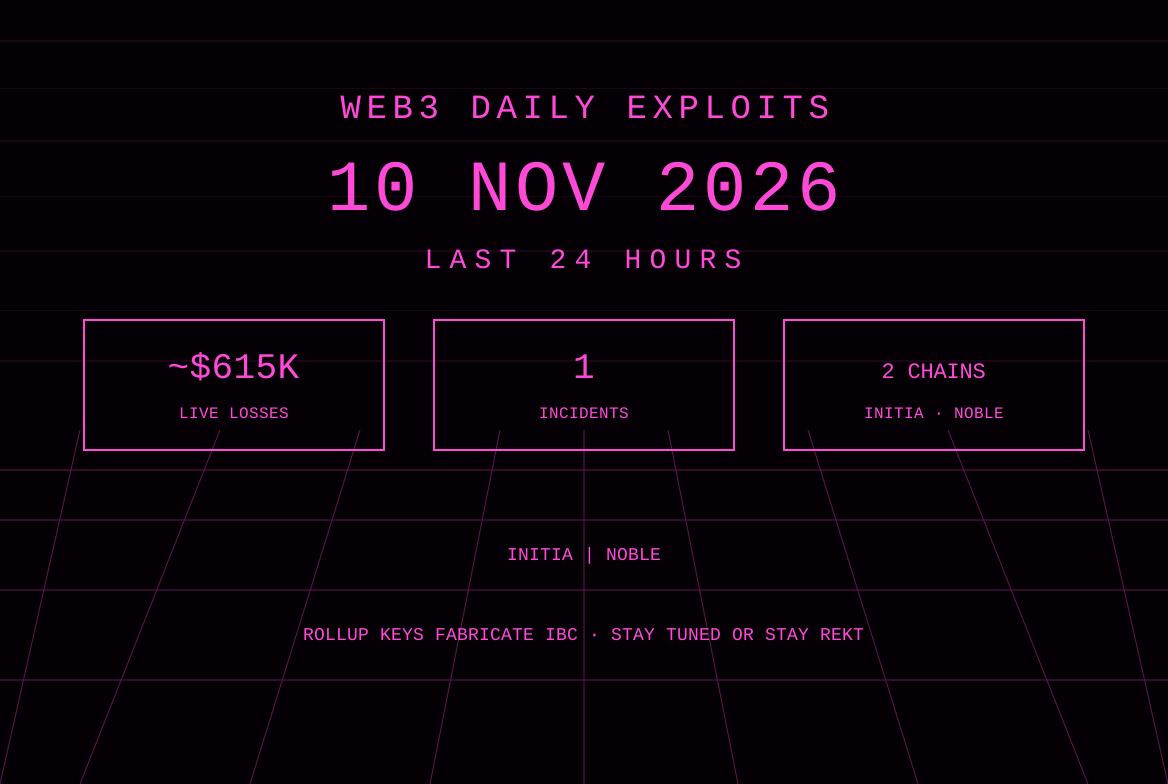
First-report incident: Initia L1 halted after unauthorized transfers from rollup escrow accounts using compromised infrastructure keys to fabricate IBC transfers; ~$605K USDC + ~$10K other tokens exited via Noble. Live scored ~$615K across Initia and Noble. Ankr bridge, ACryptoS, and NEAR AI remain UPDATEs.
Web3 Daily Exploits — 8 Nov 2026: Quiet Window, Keplr Web3Auth ~$6M Update
Quiet scoring window: no first-reported protocol incidents with confirmed scored user losses in the last 24 hours. Keplr/Web3Auth social-login key exposure (first reported 6 Nov) has material update with Bitquery tracing ~$6.01M from 44k+ Cosmos wallets; recovery addresses published. Prior Loopscale, FLOKI bot, TENDRIL, Binance, Mercado Bitcoin remain UPDATEs. Live scored losses ~$0 across 0 incidents.
Web3 Daily Exploits — 7 Nov 2026: Quiet Window, No New Scored Losses
Quiet scoring window: no first-reported protocol incidents with confirmed scored user losses in the last 24 hours. Prior Loopscale contained attempts (vaults made whole, $0 user loss), FLOKI bot (loss undisclosed), TENDRIL sell-hook, Binance hot-wallet signing compromise, and Mercado Bitcoin remain UPDATEs. DarkSword iOS kit continues device-level wallet targeting on unpatched phones. Live scored losses ~$0 across 0 incidents.
Web3 Daily Exploits — 6 Nov 2026: Loopscale Contained Attempts, FLOKI Bot Offline
Quiet scoring window: Loopscale paused Solana lending after week-long API campaign and two contained attack paths (~$412K undercollateralized loan, ~$521K NAV inflation halted). Vaults made whole, no user deposits lost. FLOKI Telegram trading bot taken offline after exploit; loss size undisclosed. TENDRIL remains prior brief. Live losses ~$0 across 0 scored incidents.