Web3 Daily Exploits — 25 Aug 2026: Comet AMM $750K Drain on Stellar & Enjin $142K ERC-1155 Bypass
Comet AMM $750K Stellar drain via same-asset swap accounting bug; Enjin $142K via malicious ERC-1155 transfer adapter; warp.green $93K bridge hit. White-hat offers active.
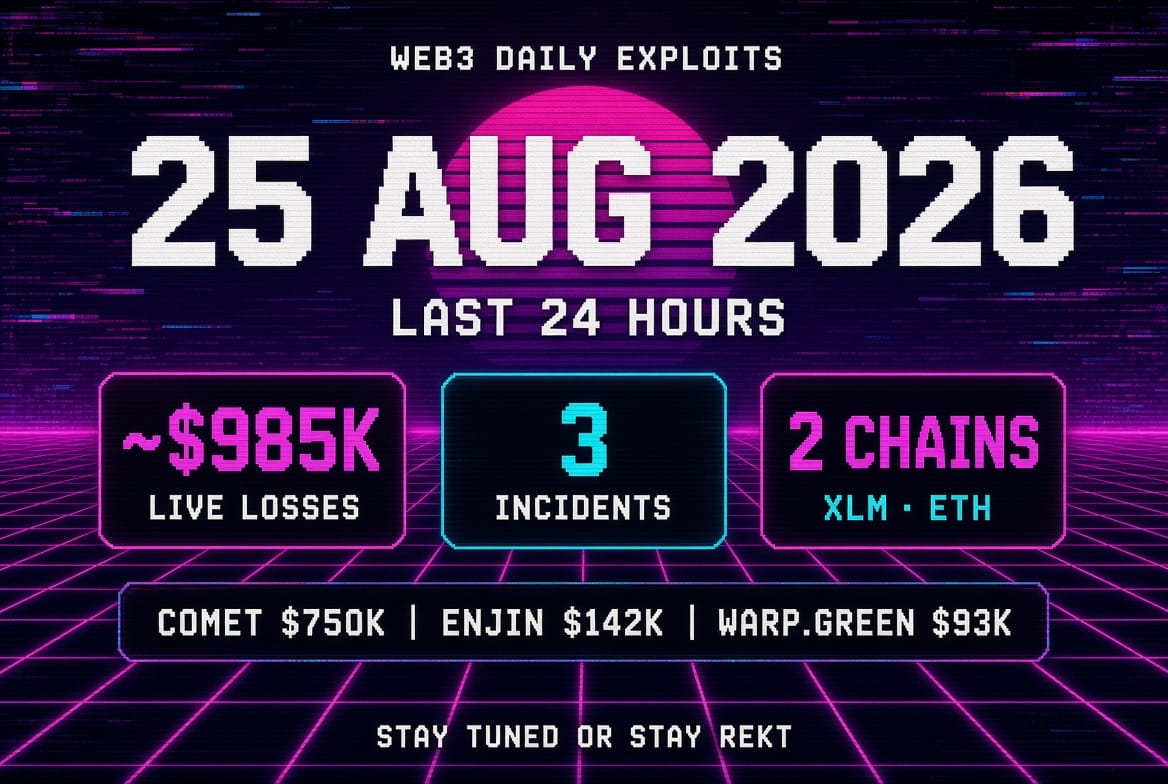
Summary: In the past 24 hours, the Comet AMM BLND-USDC liquidity pool on Stellar was exploited for approximately $750K via an accounting flaw allowing same-asset swaps that corrupted reserves, while Enjin's ERC-1155 Crypto Items platform lost ~$142K after a malicious transfer adapter bypassed owner approvals and redeemed ENJ backing. White-hat recovery offers are active on the Stellar incident.
Additional recent activity includes the warp.green bridge $93K drain and ongoing fallout from the Term Finance $8.5M governance takeover.
Comet AMM / Blend Protocol BLND-USDC Pool Exploited for ~$750K on Stellar
On August 25, 2026, the BLND-USDC liquidity pool on Comet AMM (Stellar network) was drained of roughly $717K–$750K. The root cause was an accounting bug in the pool that accepted "swap a token for itself" (USDC→USDC). This corrupted reserve math, allowing the attacker to withdraw more than deposited.
The attacker executed the attack ~36 times via four throwaway contracts, funded by a wallet created shortly before. Pattern per run: flash-loan ~530,000 USDC from a Blend pool, trigger same-asset swap on the CometDEX pool, withdraw excess, repay loan atomically. Profits decayed from ~$46K to $6K per run as liquidity bled out.
Proceeds (~747,801 USDC) were quickly moved via Allbridge. The pool contract remains unpatched and still holds residual liquidity.
Key addresses:
- Attacker (ETH side / related): 0x0ff9ebafc1ef4a0aa479533dff8ecb10492df7da
- Pool (Stellar): CAS3FL6TLZKDGGSISDBWGGPXT3NRR4DYTZD7YOD3HMYO6LTJUVGRVEAM
YieldBlox Security Council (related to the protocol) has sent an on-chain message offering a 15% white-hat bounty for return of 85% of funds within 72 hours, with contact details provided. Validation TX on Stellar: 8e5e682eed6e478e9814be485332e5369c75fa861f78b9e519034eaf414eba09.
Reference: @DefimonAlerts alert | On-chain message post
Enjin ERC-1155 "Crypto Items" Platform Drained of ~$142K
Defimon detected an exploit on Enjin that drained approximately $142K (~5.24M ENJ) on Ethereum. Enjin's ERC-1155 Crypto Items allow each item to route transfers through a per-item adapter. The attacker registered or used a malicious transfer adapter that skipped the owner-approval check.
This enabled the exploit contract to call transferFrom(holder, attacker, 1) and pull ENJ-backed items from ~52 unrelated holders' wallets without any approval (emitting real TransferSingle events, no setApprovalForAll). The attacker then called melt() on each stolen item, redeeming the 500-ENJ backing per item from the platform reserve at 0x4e643a25a64952895f553f20252861258727174e. Net proceeds forwarded to the attacker EOA.
Key links:
- Exploit TX: 0xd4a382da03c99ce3084661b913b50b525a4b283f66f510bcf1040152830b2a7e
- Attacker: 0x5ec1ba7892d11059c39557b762a97dd695778ca5
- Reserve/Victim: 0x4e643a25a64952895f553f20252861258727174e
Reference: @DefimonAlerts detailed alert
warp.green ERC-20 Bridge Exploited for $93K
The warp.green cross-chain messaging protocol's ERC-20 bridge suffered a ~$93K drain. The vulnerability was in the Chia-side Chialisp puzzle. The attacker minted worthless tokens, obtained validator signatures, and drained USDC from the bridge contracts. The team identified the issue, confirmed no further malicious transactions, and offered a 10% white-hat bounty for return of 90% of funds to their Ethereum multisig 0x1D495d48c54A3C668D69bd08cb0786afFf669646 within 48 hours.
References: @DefimonAlerts | @warpdotgreen confirmation
Broader Context & Other Notes
@Phalcon_xyz highlighted ongoing concerns around Cosmos EVM v0.7.2 critical vulnerability fixes that were quietly included while some chains (including prior TAC ~$7.5M incident) may not have been promptly notified. Multiple chains were affected before public acknowledgment by Cosmos Labs.
The larger Term Finance ~$8.5M governance exploit (Aug 23) remains relevant: attacker cheaply acquired majority of sparsely-held DAO governance tokens in vaults with zero prior voters, passed malicious proposals, zeroed delays, and drained ~2,843 ETH + 1.68M USDC. Deep dive available via Defimon.
No major alerts from @CertiKAlert in the immediate window. Monitoring continues via on-chain messages and security accounts.
This report aggregates public on-chain data and X alerts as of August 25, 2026. Always verify independently. Not financial advice.
Read more
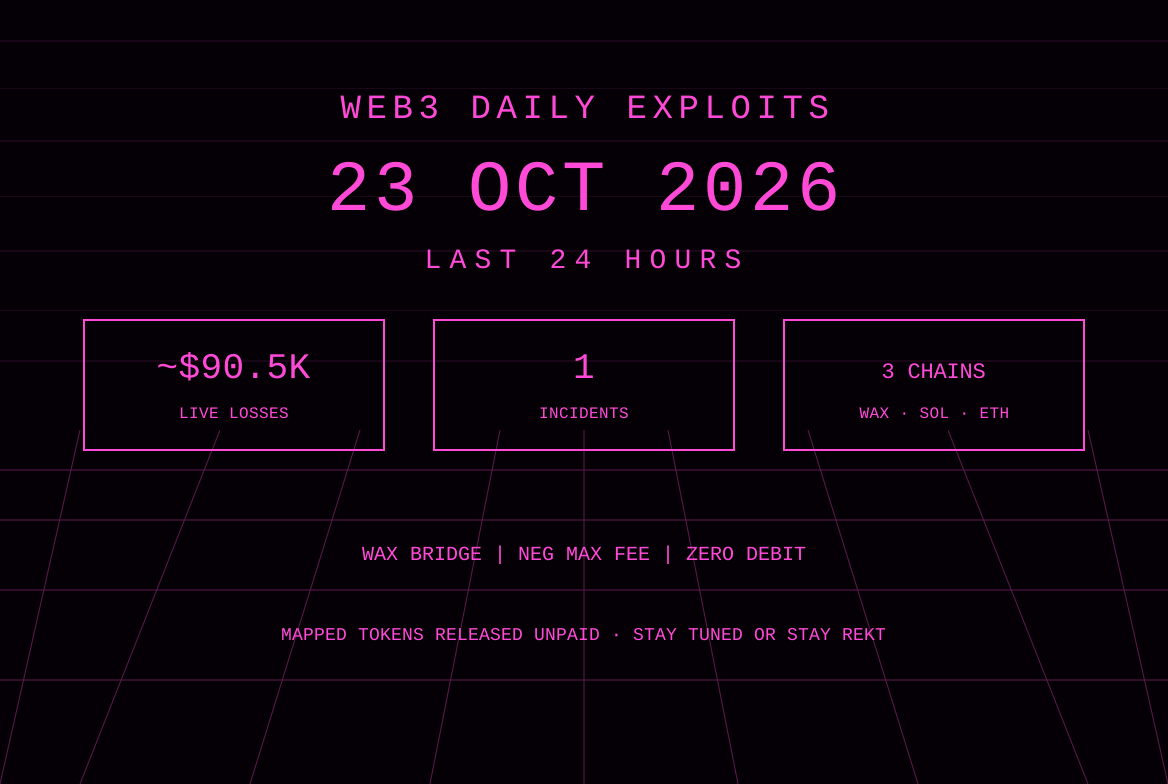
Web3 Daily Exploits — 23 Oct 2026: WAX ~$90.5K Bridge Negative Fee Zero Debit
WAX Multi-Chain Bridge drained ~$90.5K after eth.token::withdraw allowed negative max_fee that zeroed the debit while still logging full withdrawals and releasing mapped USDC/USDT/DAI/WETH/WBTC on Solana and Ethereum. SlowMist and Blockaid first reports. Live loss ~$0.09M, 1 incident, 3 chains. Kimchi Solana KOL pump-dump and CoinDCX wallet movements noted as UPDATE.
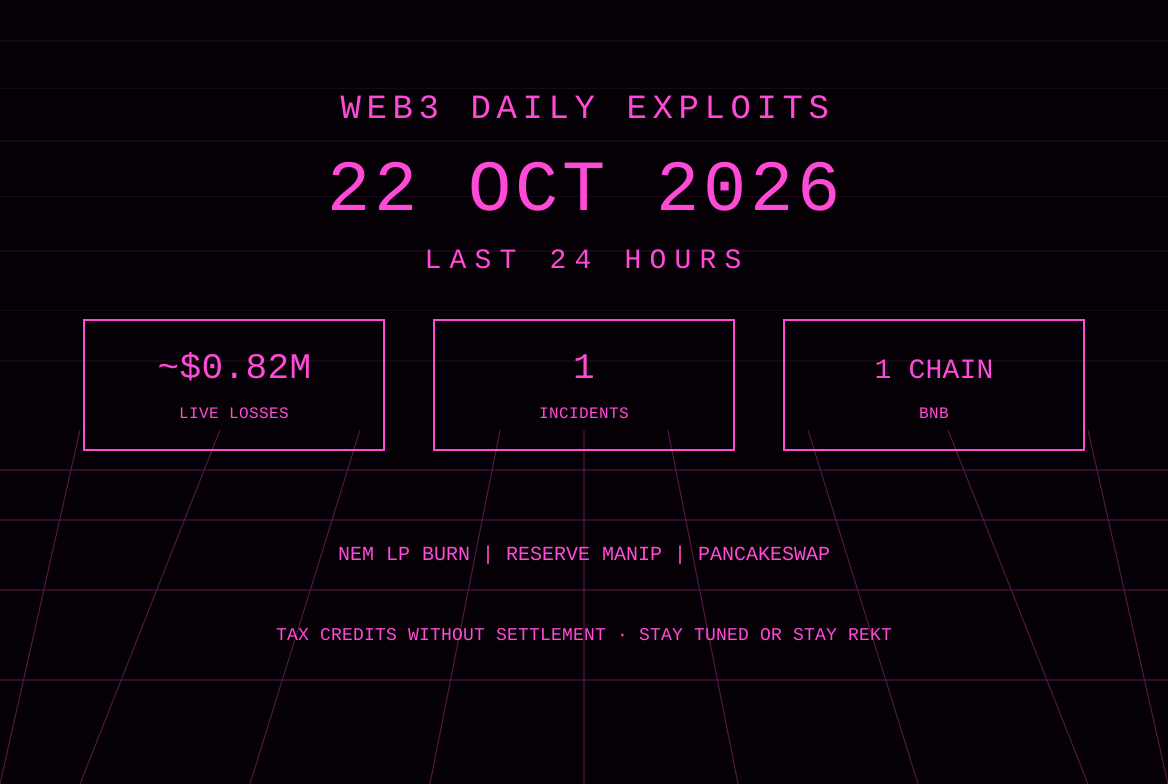
Web3 Daily Exploits — 22 Oct 2026: NEM ~$820K LP Burn Reserve Manip
NEM (Newmont) token on BNB Chain drained ~$820K from its PancakeSwap USDT/NEM LP after a tax-settlement flaw let the attacker inflate pendingLpSellRecycle without real sells, then burn existing reserves via flushLpSellRecycle + sync. Defimon, CertiK, SlowMist, Phalcon first reports. Live loss ~$0.82M, 1 incident, 1 chain. Cysic bounty and Fearless Wallet key-leak noted as UPDATE.
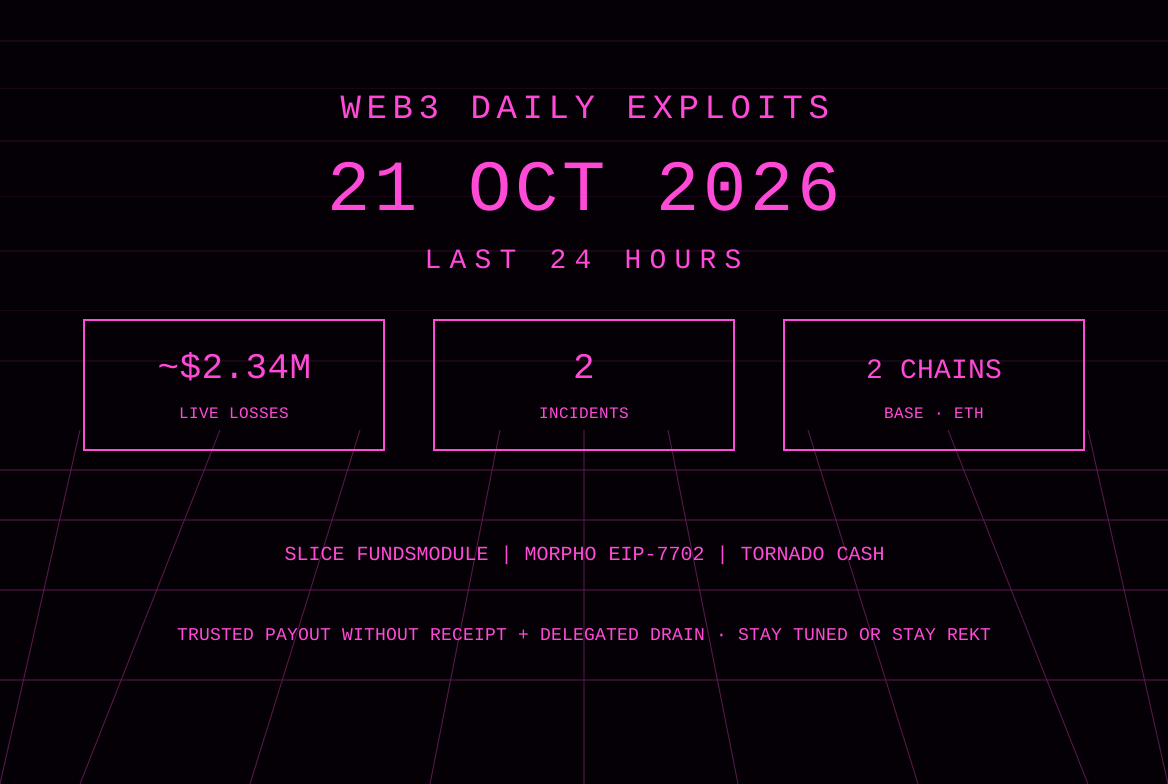
Web3 Daily Exploits — 21 Oct 2026: Slice ~$41K FundsModule Unbacked Release + MORPHO ~$2.3M EIP-7702 Drain
Slice FundsModule on Base drained for ~$41K after release function trusted caller-selected source contracts without verifying actual ETH or USDC receipt. Institutional addresses lost ~973K MORPHO (~$2.3M) via EIP-7702 delegations, funds to Tornado Cash. SlowMist and Defimon first reports on Slice; ZachXBT on MORPHO. Live loss ~$2.34M, 2 incidents, 2 chains. Drift fund movements noted as UPDATE.
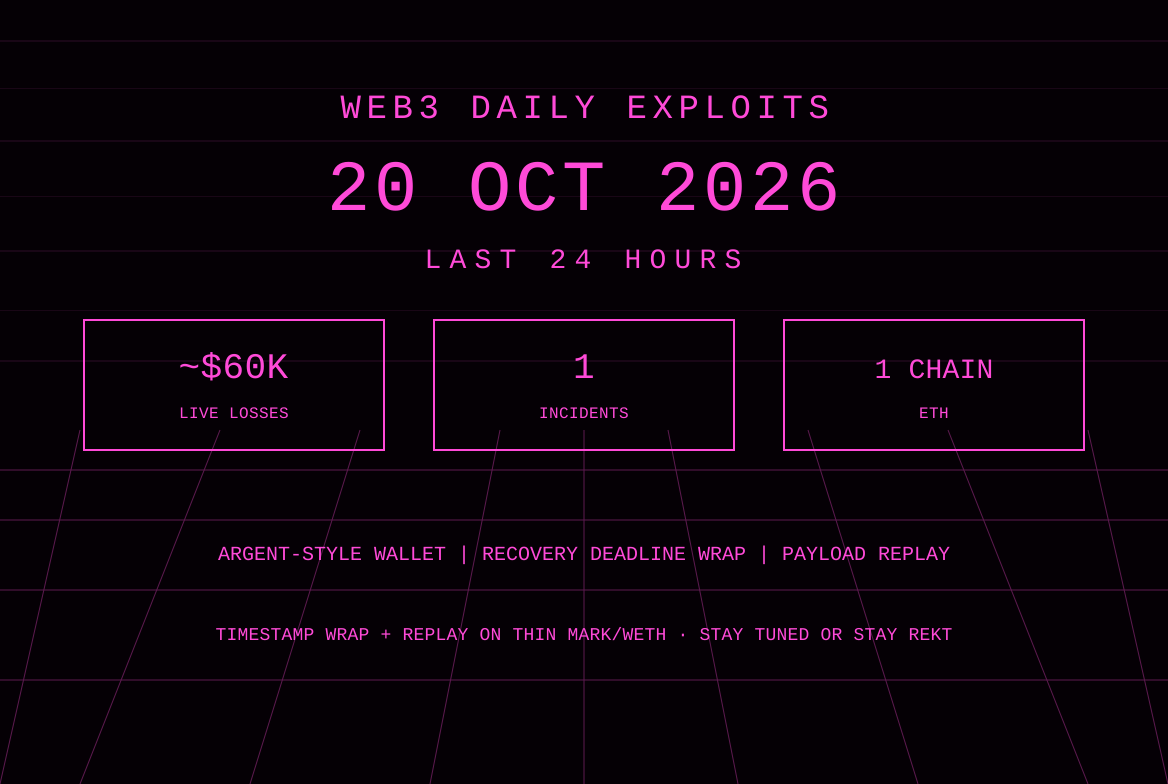
Web3 Daily Exploits — 20 Oct 2026: Argent-Style Wallet ~$60K Recovery Deadline Wrap + Payload Replay
Argent-style smart wallet system on Ethereum drained for ~$59.8K after unrestricted recovery-period setter caused deadline wrap to past timestamp and execution module allowed signed payload reuse, used against thin MARK/WETH pool. SlowMist first report. Live loss ~$60K, 1 incident, 1 chain. Drift and Aztec fund movements noted as UPDATE.