Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
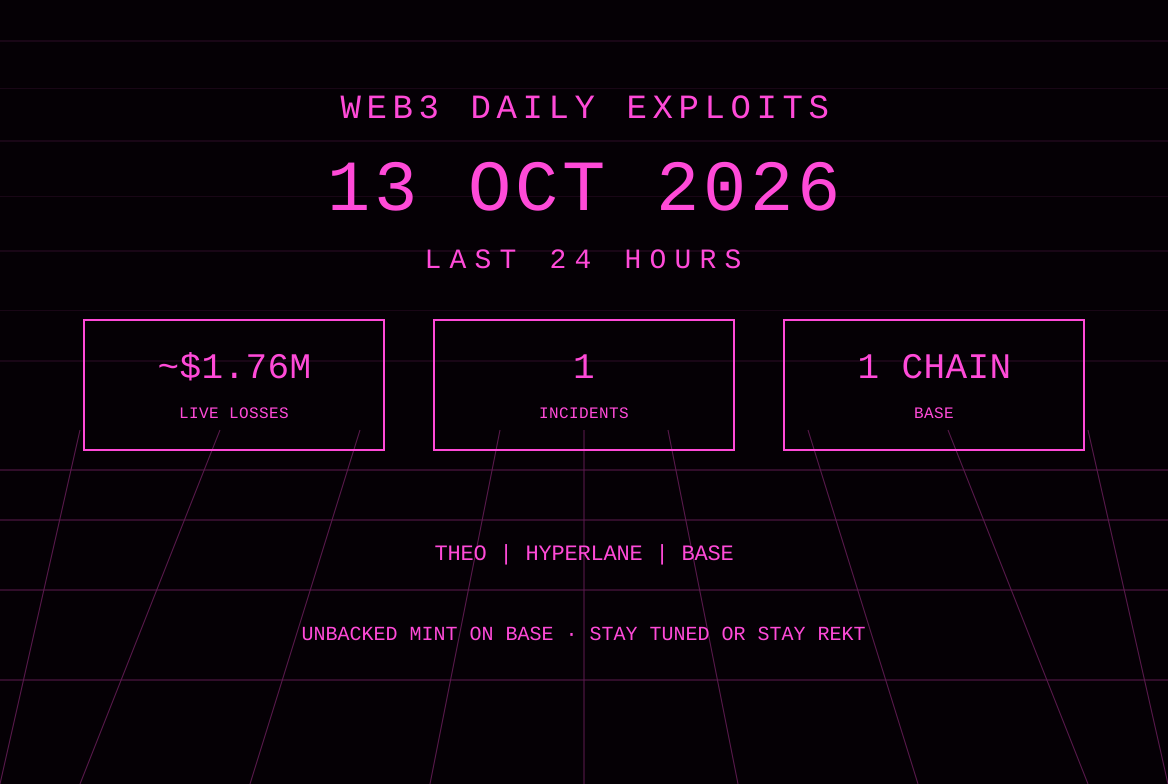
The 13 Oct America/Panama window records one first-report protocol incident used for scoring: an unbacked mint of Autheo’s THEO token on Base that allowed an attacker to extract approximately $1.76 million in ETH and other assets. Combined live loss on this card is about $1.76 million. The root cause is a logic error in a Hyperlane HypERC20 warp-route configuration that used a TrustedRelayerIsm security module; a single relayer key could authorize any inbound interchain message, permitting a mint from address 0x0 with no corresponding lock or burn on the origin chain. Monitored accounts including PeckShieldAlert and DefimonAlerts posted the alert on 13 Oct. Autheo advised users not to buy, sell, or bridge THEO while investigating. No other first-report smart-contract exploits with fresh loss figures were posted by the required monitors in the last 24 hours. Prior items (Ledger / CryptoBilis, Papertrade, BitBay, EtherVista, 79Vault and others) remain on earlier briefs and are not re-scored.
Autheo THEO — Base — about $1.76 million — logic error / unbacked cross-chain mint
What happened: On or around 12–13 Oct 2026 an attacker exploited the THEO token (a Hyperlane HypERC20 warp-route token) on Base. DefimonAlerts reported that the security module is a TrustedRelayerIsm, so a single relayer key can authorize any inbound interchain message. In a prior transaction the attacker delivered a Hyperlane message from origin domain 2127 that minted 19,000,000 THEO out of thin air (handle() resulting in a Transfer from 0x0) with no backing lock on the origin chain. In a subsequent transaction the attacker’s orchestrator pulled 9.5 million of the unbacked THEO and ran it through a multi-swap extraction path, dumping across the THEO/USDC pair and Uniswap v4 / Hydrex THEO pools to extract real WETH, USDC and cbBTC. PeckShieldAlert reported that 19 million THEO were minted on Base, swapped for 700.8 ETH (approximately $1.76 million), and the ETH was bridged to Ethereum. THEO price dropped approximately 92% in 24 hours. Autheo issued a notice advising users to stop buying, selling or bridging THEO while the team investigates.
Protocol / chain / asset: Autheo THEO token (HypERC20 warp route) on Base. Token contract 0xebe516a20238f79dc20b07ead6768e08891ed309. Assets extracted include ETH / WETH, USDC and cbBTC. Bridged proceeds moved to Ethereum.
Loss: Approximately $1.76 million per PeckShieldAlert (700.8 ETH). DefimonAlerts listed ~$1.7M. Figures reflect the value extracted from liquidity pools into attacker-controlled assets; the unbacked mint itself inflated supply. Token price impact is separate and not added to the scored loss. Not a user-wallet drain of existing balances beyond the liquidity extracted.
Attack type: Logic error in cross-chain warp-route configuration. TrustedRelayerIsm allowed an unauthorized mint of unbacked tokens. Not an oracle manipulation, not a reentrancy, not a private-key compromise of the token contract itself. The single-relayer trust model permitted the inbound message that minted from the zero address.
Explorer URLs: Token: https://basescan.org/address/0xebe516a20238f79dc20b07ead6768e08891ed309. DefimonAlerts linked the extraction transaction and attacker addresses (shortened in the alert); full hashes appear in the original posts. PeckShieldAlert images show the mint and swap activity. This brief does not invent additional transaction hashes.
Status: Incident first reported 13 Oct by monitored accounts. Autheo investigating and has advised users to pause trading and bridging of THEO. Proceeds bridged to Ethereum. No recovery or bounty announcement in the posts read for this cutoff. Price impact ongoing.
Sources: https://x.com/PeckShieldAlert/status/2109933198096711890, https://x.com/DefimonAlerts/status/2109918883037454782, and secondary coverage from The Defiant, CryptoBriefing and Lookonchain.
Also noted
- Papertrade (UPDATE, not re-scored): Oracle / BBO manipulation on HyperEVM reported earlier (approx. $1.28M, Oct 10). GoPlusSecurity published a detailed breakdown on 12 Oct. Not a new incident in this window.
- Ledger / CryptoBilis (UPDATE, not re-scored): Ongoing supply-chain / hardware-implant investigation. No material new loss figure in the last 24 hours used for scoring. Prior researcher estimate remains on earlier briefs.
- BitBay StableVault (~$14k) and EtherVista (~$18.6k): Reported 9 Oct. No new material updates in this cutoff.
- 79Vault (~$12.5M): Earlier item; partial return noted previously. Not re-scored.
- Monitored accounts: DefimonAlerts, CertiKAlert, Phalcon_xyz, GoPlusSecurity, SlowMist_Team, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi and rekt.news posted no additional first-report protocol exploits with fresh loss figures in the last 24 hours beyond the THEO item.
Sources and references
- PeckShieldAlert THEO mint alert: https://x.com/PeckShieldAlert/status/2109933198096711890
- DefimonAlerts Autheo THEO logic-error alert: https://x.com/DefimonAlerts/status/2109918883037454782
- The Defiant coverage: https://thedefiant.io/news/hacks/autheo-s-theo-plunges-92-after-suspected-bridge-exploit-on-base
- CryptoBriefing: https://cryptobriefing.com/autheo-theo-plunges-suspected-bridge-exploit/
- Lookonchain feed: https://lookonchain.com/feeds/76635
Editor’s note: the scored live loss on this card is approximately $1.76 million from the single Autheo THEO unbacked mint on Base. No other new first-report protocol drains were posted by the monitored accounts in the last 24 hours. Prior-day items remain on their original briefs and are not re-scored. No how-to or exploit reproduction steps. Stay tuned or stay rekt.
Read more
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
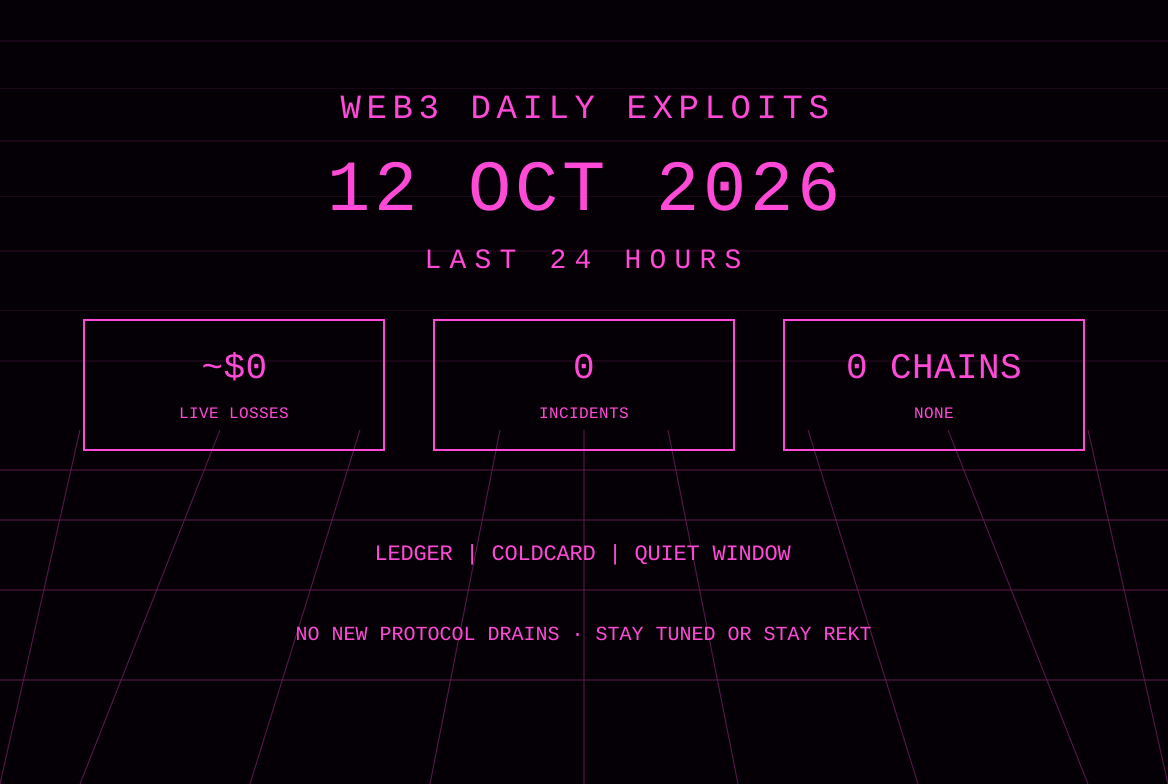
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.
Web3 Daily Exploits — 11 Oct 2026: Ledger Implant Confirmed, 2,990 ETH to Tornado
UPDATE on the CryptoBilis Ledger supply-chain incident. Ledger confirms an unauthorized hardware implant in one affected user device. On-chain researchers report the attacker deposited 2,990 ETH worth about $7.45 million into Tornado Cash between 9 and 10 Oct, with further deposits continuing on 11 Oct. No new protocol drains in the window.
Web3 Daily Exploits — 10 Oct 2026: Ledger Reseller Drains and Bridge EIP-7702 Claim
Ledger investigates reports of fund losses among Southeast Asia buyers of devices from reseller CryptoBilis. Researchers estimate about $93 million drained across Bitcoin, Ethereum, Tron, BNB Chain and Polygon. Phalcon flags $3.55 million in unclaimed bridge funds claimed via EIP-7702 by a Tornado-funded address; ownership intent is open.
Web3 Daily Exploits — 9 Oct 2026: BitBay Vault and EtherVista Overflow
SlowMist flags two small smart-contract drains on 9 Oct: BitBay’s Polygon DAI/USDC vault lost about 14,838 DAI after a zero-liquidity withdrawal, and EtherVista lost about $18,600 to a uint112 overflow in the pair K-check. CertiK says the 79Vault attacker returned 15,000 BNB.