Web3 Daily Exploits — 11 Oct 2026: Ledger Implant Confirmed, 2,990 ETH to Tornado
UPDATE on the CryptoBilis Ledger supply-chain incident. Ledger confirms an unauthorized hardware implant in one affected user device. On-chain researchers report the attacker deposited 2,990 ETH worth about $7.45 million into Tornado Cash between 9 and 10 Oct, with further deposits continuing on 11 Oct. No new protocol drains in the window.
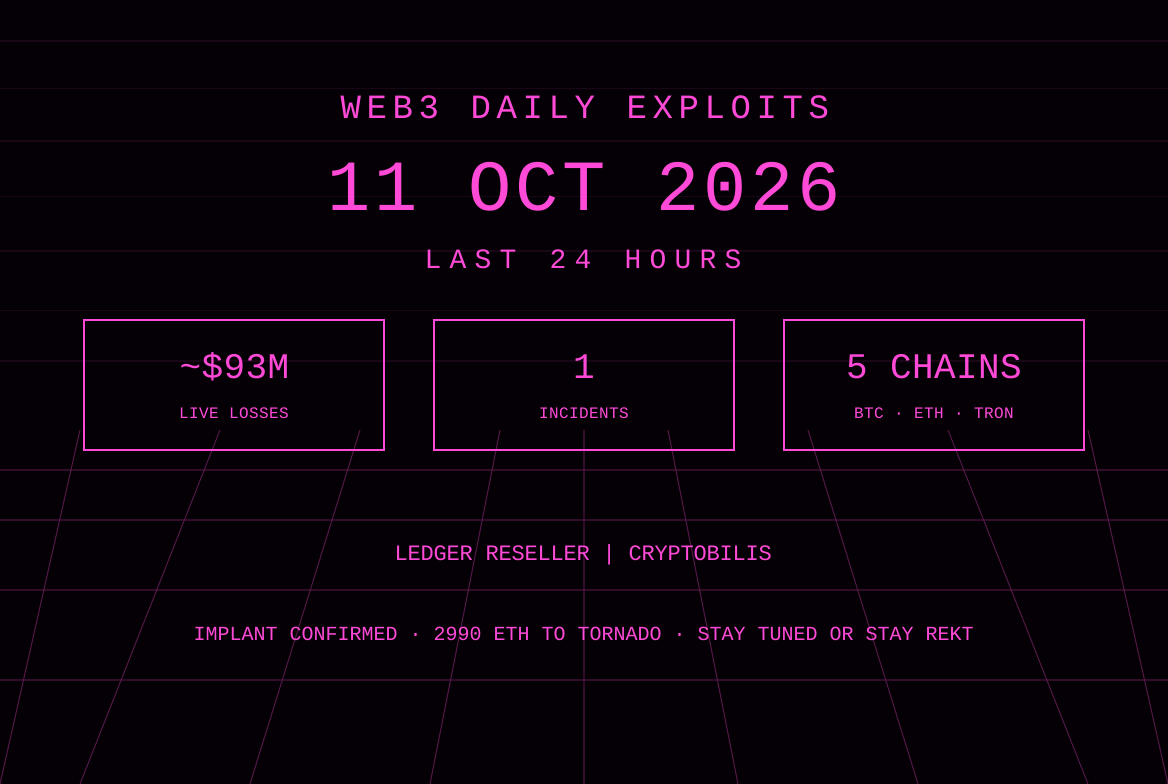
The 11 Oct America/Panama window contains no new first-report protocol drains from the monitored accounts. The dominant item remains a material update to the CryptoBilis Ledger hardware-wallet supply-chain incident that opened on 9 Oct. Ledger Support posted a situation update on 10 Oct confirming that one of the impacted users’ devices contained an unauthorized hardware implant. CryptoBilis has ceased sales of all hardware wallet inventory pending the investigation. Separately, on-chain researcher Specter reported that addresses linked to the incident deposited 2,990.3 ETH, valued at about $7.45 million, into Tornado Cash between 9 and 10 Oct. Secondary coverage on 11 Oct noted additional Tornado Cash deposits, including a fourth run of roughly 596.5 ETH beginning at 09:43 UTC straight from collector addresses, bringing the cumulative ether through the mixer higher while portions continue toward NEAR Intents and ZEC. The original researcher loss estimates of roughly $93 million remain the card line; Ledger has not published its own total. The Tornado deposits are a laundering step, not an additional loss.
DefimonAlerts posted an on-chain message on 10 Oct from a user requesting a partial refund of a $3 million loss. SlowMist, CertiKAlert, Phalcon, GoPlusSecurity, PeckShieldAlert, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, and rekt.news did not post a separate new protocol exploit used as a figure in this cutoff. Lookonchain activity in the window was limited to trading and deposit notes unrelated to drains. The prior BitBay, EtherVista, and 79Vault items remain closed for scoring purposes. BeraFarm on Berachain paused contracts after an attempted exploit involving hub reward-vault balance accounting was flagged by Hypernative and KodiakFi; the team stated no user funds were lost and deposits and withdrawals later reopened after a fix. Papertrade on HyperEVM faced unverified allegations of price-manipulation activity around Hyperliquid BBO references; the risk was previously disclosed in protocol documentation and no independently confirmed loss figure was posted by the monitored accounts.
UPDATE: CryptoBilis Ledger devices — multi-chain — about $93 million estimated — supply-chain / hardware implant
What happened: On 10 Oct at 17:09 UTC Ledger Support posted a situation update stating that the company can confirm one of the impacted users’ devices contained an unauthorized hardware implant. Ledger is reaching out to impacted users as part of the ongoing investigation and directed anyone with information to its bounty program at bounty@ledger.fr. As a precaution CryptoBilis confirmed it has ceased sales of all hardware wallet inventory until the investigation is concluded. Ledger is in active communication with the reseller on next steps, is working with appropriate authorities, and thanked SEAL_911 for collaborative support. The post states there is no indication that Ledger’s security infrastructure, systems or services have been compromised. Users who purchased a Ledger device from this reseller are advised not to initiate setup if they have not yet done so. Users who have already set up the device are advised to consider moving assets to a new Ledger signer with a new seed. The company noted it is continuously adding security mitigations and working on further enhanced anti-tampering solutions. This confirmation follows the 9 Oct initial investigation post and reports from researchers including Mark Karpelès who documented a suspected cellular implant in a device obtained from a Malaysian channel.
Separately, on 11 Oct coverage of Specter’s monitoring stated that between 9 and 10 Oct attacker addresses associated with the CryptoBilis Ledger incident deposited 2,990.3 ETH, worth approximately $7.45 million, into Tornado Cash. The attacker had previously withdrawn funds to 14 addresses, then bridged portions cross-chain via NEAR Intents into ZEC for additional privacy processing. Specter noted operational-security lapses: some withdrawal transactions reused prior deposit addresses, and some were initiated by wallets linked to addresses that paid gas fees during the original thefts, allowing partial linking of the flows. Funds continue to move. YFarmX coverage updated on 11 Oct at 11:00 UTC described a fourth Tornado Cash run of 596.5 ETH beginning at 09:43 UTC directly from three Ethereum collectors into fresh splitters and then into the mixer pools, alongside additional USDD-to-USDT conversions and flows toward Binance. The $7.45 million figure is a subset of the earlier researcher estimates and is not additive to the card total. Further movement on 11 Oct remains part of the same estimated loss.
Protocol / chain / asset: Not a protocol. Hardware wallets sold through reseller CryptoBilis. Chains named in the researcher traces remain Bitcoin, Ethereum, Tron, BNB Chain, and Polygon. Assets include BTC, ETH, USDT, and other tokens. The confirmed implant is a physical hardware modification in at least one affected device. The Tornado Cash deposits occurred on Ethereum.
Loss: About $92.9 million per the Bitquery reconstruction of 311 wallets cited in the prior brief (later prints near $93.2 million). Other prints in the same window have ranged from roughly $72 million to $93.4 million. Ledger has not confirmed a dollar total. The new Tornado Cash deposits of 2,990.3 ETH (~$7.45 million) plus the additional 596.5 ETH run on 11 Oct are laundering steps drawn from the existing estimated loss and are not scored as incremental. No freeze total is in the posts read here. Counted on the card at about $93 million.
Attack type: Supply-chain compromise of hardware devices sold by an authorized reseller, resulting in possession of private keys or seeds. Ledger has now confirmed an unauthorized hardware implant in one impacted user device. The precise mechanism that allowed the keys to be obtained remains under investigation. Not a smart-contract vulnerability. Not an oracle bug. Not a remote exploit of Ledger’s core systems according to the company’s statement.
Explorer URLs: Researcher-published collector addresses from earlier coverage remain in the GoPlusSecurity post and Specter / Bitquery notes. Full transaction lists for the Tornado Cash deposits are not expanded in the secondary coverage read here. This brief does not invent hashes. Example prior links: https://arkm.com/explorer/address/0x6eb486CB5Afb1FBf2ccC84fAE649D55272FEEB62 and Bitcoin example https://arkm.com/explorer/address/bc1q9r0jxknrtlc96dankvgkwa0347569rc6dn53fs.
Status: Implant confirmed by Ledger on 10 Oct. Reseller sales paused. Investigation ongoing with law-enforcement coordination. Users advised to use a fresh seed if the device was purchased from the reseller and already set up. Attacker continues to move funds, including the 2,990 ETH Tornado Cash deposits reported on 11 Oct and a further run of approximately 596.5 ETH later the same day. No recovery figure published by Ledger.
Sources: https://x.com/Ledger_Support/status/2108968264055345381, Specter monitoring as reported in Odaily and TokenPost on 11 Oct, YFarmX update on additional Tornado activity, prior Bitquery investigation https://bitquery.io/investigations/ledger-cryptobilis-hack, and the 9 Oct Ledger Support post https://x.com/Ledger_Support/status/2108551100613714002.
Also noted
- UPDATE, prior protocol items: BitBay StableVault (~$14k), EtherVista (~$18.6k), and 79Vault (~$12.5M with partial BNB return) remain as previously briefed. No material new figures in this window.
- BeraFarm attempted exploit (zero loss): On 10 Oct the Berachain protocol paused contracts after detecting an attack targeting hub reward-vault balance accounting that could inflate reported balances via third-party delegated stake. HypernativeLabs and KodiakFi assisted. The team stated no user funds were lost. A fix was deployed and deposits/withdrawals reopened. Not scored as a loss.
- Papertrade pricing allegations (unverified): Community posts on 10–11 Oct alleged that wallets used large Hyperliquid trades to move the ETH BBO midpoint used by Papertrade for synthetic positions. Protocol documentation had previously flagged BBO manipulation risk. No monitored account posted a confirmed loss figure. Not scored.
- DefimonAlerts on-chain message: A user posted a request for a partial refund of a reported $3 million loss. Not scored as a new incident.
- Lookonchain: Trading and deposit notes only. No new drains.
- Monitored accounts: SlowMist_Team, CertiKAlert, Phalcon_xyz, GoPlusSecurity, PeckShieldAlert, BlockSecTeam, ZachXBT, CyversAlerts, Immunefi, and rekt.news did not post a first-report protocol exploit used as a new figure in this cutoff.
Sources and references
- Ledger Support situation update, implant confirmation, 10 Oct: https://x.com/Ledger_Support/status/2108968264055345381
- Ledger Support initial investigation post, 9 Oct: https://x.com/Ledger_Support/status/2108551100613714002
- Bitquery investigation: https://bitquery.io/investigations/ledger-cryptobilis-hack
- Specter monitoring of 2,990 ETH Tornado Cash deposits, reported 11 Oct via Odaily and TokenPost
- YFarmX coverage of additional Tornado Cash activity on 11 Oct: https://yfarmx.com/ledger-reseller-cryptobilis-drain/
- GoPlusSecurity on Ledger / CryptoBilis, 10 Oct: https://x.com/GoPlusSecurity/status/2108763510041960525
- DefimonAlerts on-chain message, 10 Oct: https://x.com/DefimonAlerts/status/2108963194882453768
- BeraFarm post-mortem, 11 Oct: https://x.com/realBeraFarm/status/2109228713065791495
Editor’s note: the scored live loss remains the researcher estimate on the CryptoBilis-linked Ledger device drains. Ledger has confirmed an unauthorized hardware implant in one device but has not published a confirmed total or a final root-cause statement. The Tornado Cash deposits, including the additional run reported on 11 Oct, are a laundering update drawn from the existing estimated loss. No new protocol drains were reported by the monitored accounts in the last 24 hours. The BeraFarm pause resulted in zero scored loss. Papertrade allegations remain unverified.
Read more
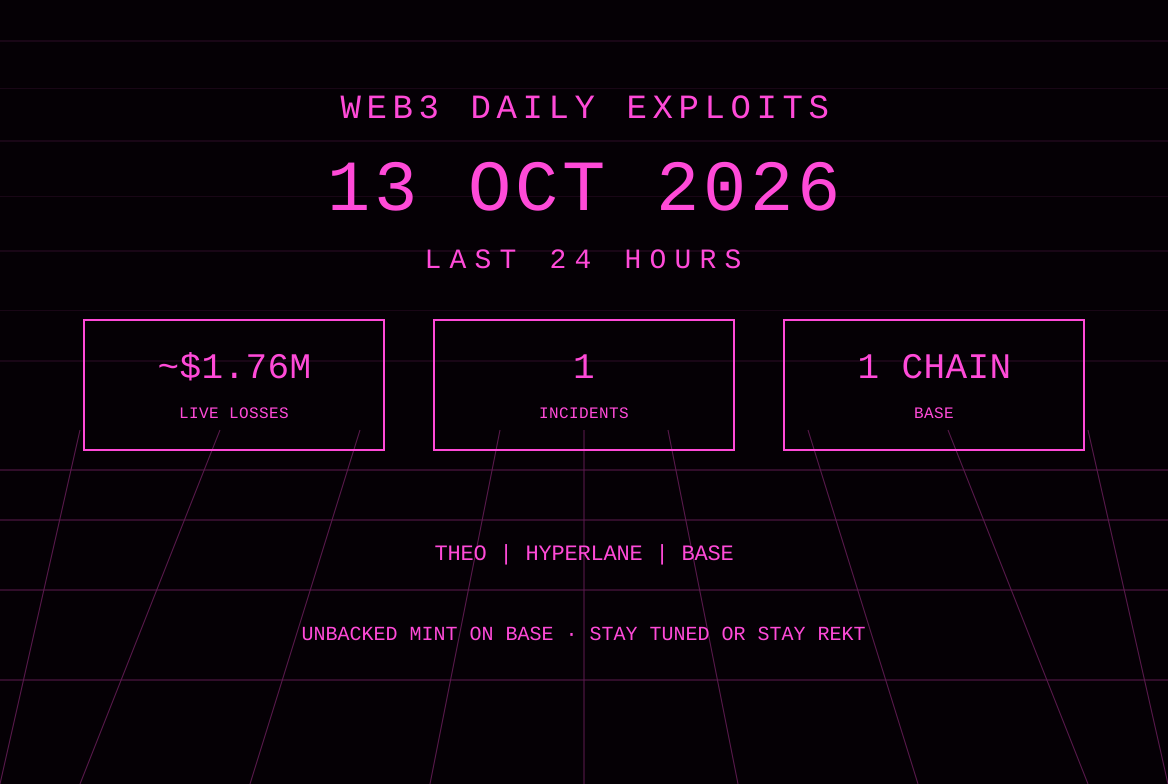
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
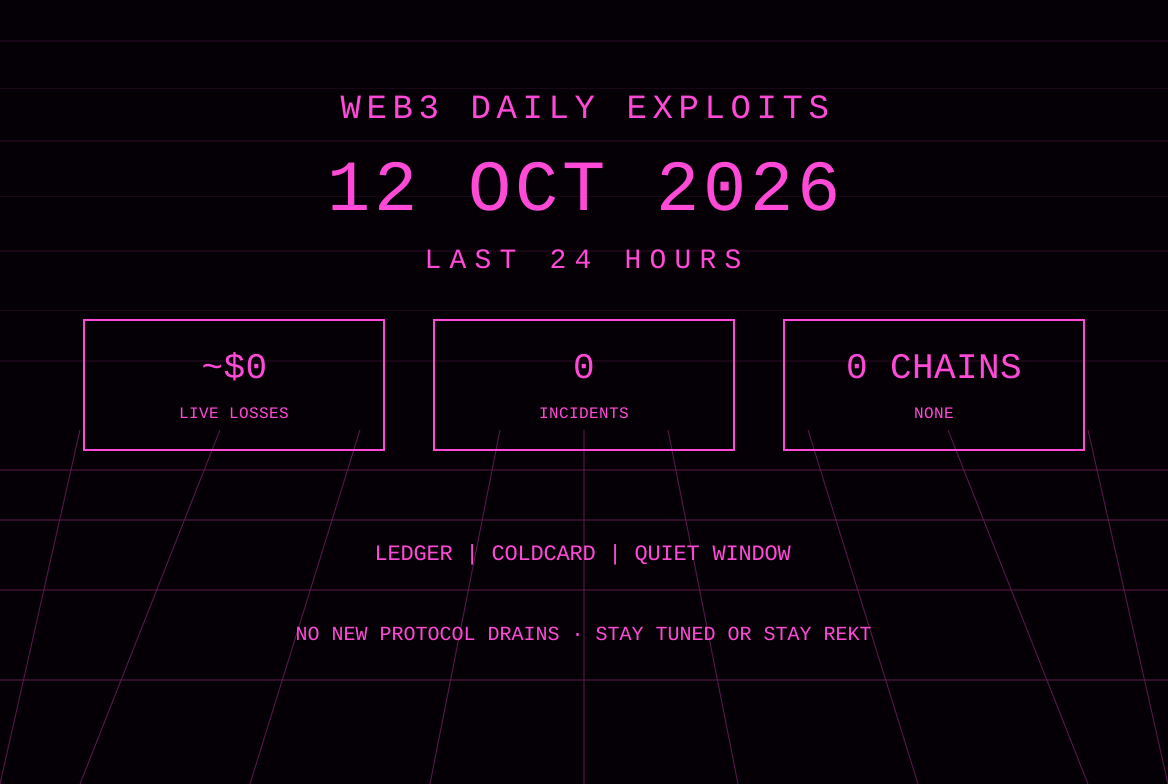
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.
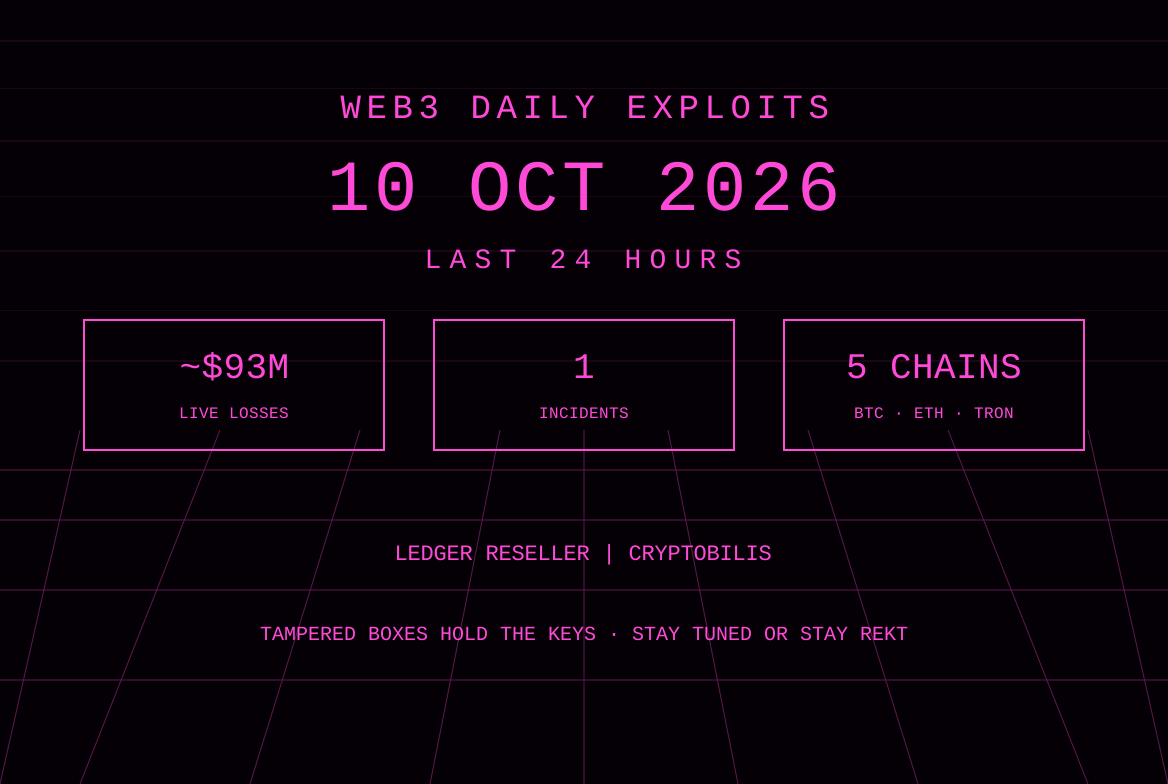
Web3 Daily Exploits — 10 Oct 2026: Ledger Reseller Drains and Bridge EIP-7702 Claim
Ledger investigates reports of fund losses among Southeast Asia buyers of devices from reseller CryptoBilis. Researchers estimate about $93 million drained across Bitcoin, Ethereum, Tron, BNB Chain and Polygon. Phalcon flags $3.55 million in unclaimed bridge funds claimed via EIP-7702 by a Tornado-funded address; ownership intent is open.
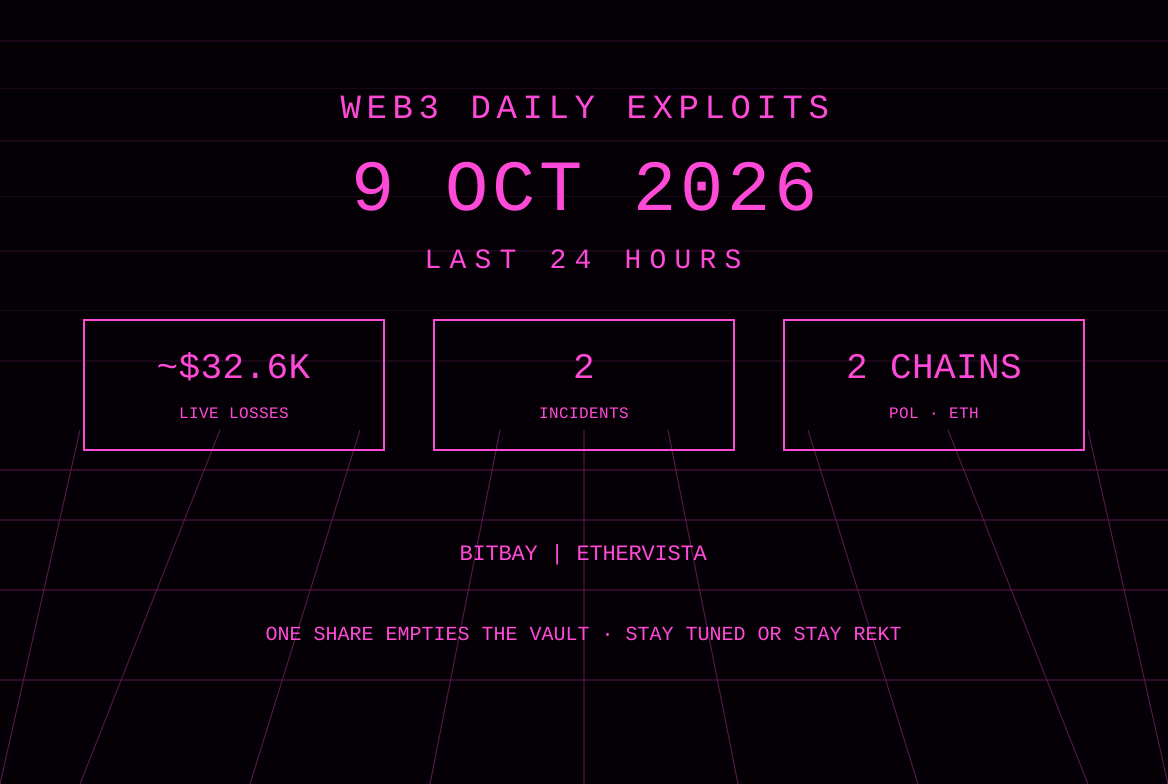
Web3 Daily Exploits — 9 Oct 2026: BitBay Vault and EtherVista Overflow
SlowMist flags two small smart-contract drains on 9 Oct: BitBay’s Polygon DAI/USDC vault lost about 14,838 DAI after a zero-liquidity withdrawal, and EtherVista lost about $18,600 to a uint112 overflow in the pair K-check. CertiK says the 79Vault attacker returned 15,000 BNB.