Web3 Daily Exploits — 9 Oct 2026: BitBay Vault and EtherVista Overflow
SlowMist flags two small smart-contract drains on 9 Oct: BitBay’s Polygon DAI/USDC vault lost about 14,838 DAI after a zero-liquidity withdrawal, and EtherVista lost about $18,600 to a uint112 overflow in the pair K-check. CertiK says the 79Vault attacker returned 15,000 BNB.
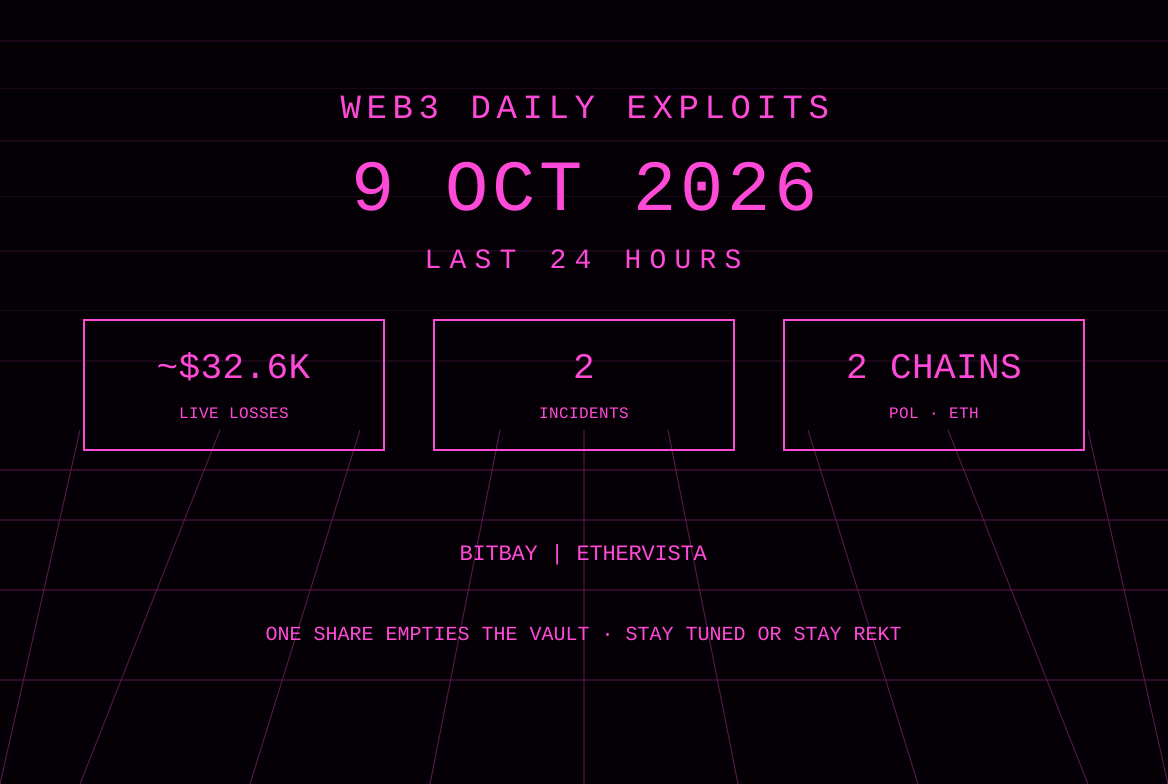
The 9 Oct America/Panama window is two small smart-contract drains, not a key day. SlowMist posted the first alert at 03:28 UTC and the second at 05:20 UTC. The first names BitBay and about $14,000. The second names EtherVista and about $18,600. SlowMist Hacked lists the same pair: BitBay StableVault at $14,000 and EtherVista at $18,600, both typed as smart-contract vulnerability, both dated 9 Oct 2026. The card adds those two desk figures and stops there. About $32,600 is the live-loss line. It is not a new eight-figure incident, and it is not a quiet day.
The material update on an older case is CertiKAlert at 09:57 UTC on 9 Oct. In the thread that opened yesterday on 79thVault, CertiK wrote that the attacker has returned 15,000 BNB, about $11 million, and linked a BscScan transaction. DefimonAlerts had already relayed on-chain settlement text this morning asking for that same 15,000 BNB. That return is not a new loss and is not on the card. Phalcon had no exploit post in the window read here. BlockSecTeam, ZachXBT, and CyversAlerts did not post a first-report drain used as a figure. PeckShieldAlert’s last exploit print in the posts read here is yesterday’s 79Vault note, not a new incident. Lookonchain posted trader and flow notes, not a protocol drain. Immunefi posted bounty payouts, not an incident. rekt.news did not publish a new incident post used as a figure.
BitBay StableVault — Polygon — about $14,000 — zero-liquidity withdrawal
What happened: SlowMist posted at 03:28 UTC on 9 Oct a threat-intel alert on BitBay. The loss line is about $14,000. The root-cause sentence says the vault’s _withdraw function transfers its entire token balance when liquidity equals zero, without limiting the payout to the user’s proportional share. The attacker, in that account, triggered a zero-liquidity state via reposition, then redeemed one minimal share unit and drained approximately 14,838.47 DAI. That is the alert. This brief does not re-decode the vault and does not add a call trace beyond that sentence.
The attacker in the alert is 0x59Ae3c8dd50063429D86BdaEBbC350fB64e9884B. The victim and the vulnerable contract are the same address, 0x048E88311ca84876aeA086125825492e2AF2e5A0. The post ends with “Tx:” and does not print a hash in the text read here. This brief does not invent one. SlowMist Hacked, dated 9 Oct 2026, names the target BitBay StableVault and describes BitBay’s Polygon DAI/USDC vault, UsdcDaiV4Vault. It repeats the same sequence: reposition to force liquidity to zero, then one minimal share, because _withdraw sends the contract’s entire token balance when liquidity equals zero. The database loss is $14,000. The method line is smart-contract vulnerability. The reference on that entry is the same SlowMist post. PublicAML’s 9 Oct note uses the same Polygon, DAI, and $14,000 lines and points at the same post. CryptoTimes, published on 9 Oct, uses the same 03:28 UTC timestamp, the same 14,838.47 DAI figure, and the same two addresses in truncated form.
The SlowMist post itself does not print the word Polygon. The chain reading in this brief is the SlowMist Hacked entry and the secondary notes that cite that alert, not a chain word in the tweet. A later post that names another chain would supersede that reading. No freeze, no bounty, and no project statement appeared in the posts read here. BitBay is named with the handle in the alert. This desk did not find a matching reply from that handle in the window.
Protocol / chain / asset: BitBay, vault described by SlowMist Hacked as the Polygon DAI/USDC vault UsdcDaiV4Vault. Asset out is DAI, about 14,838.47 units. Chain is Polygon on the database and secondary notes, not on the tweet text.
Loss: About $14,000, SlowMist alert and SlowMist Hacked. Token amount in the alert: approximately 14,838.47 DAI. No recovery figure. No freeze posted. Counted on the card.
Attack type: Withdrawal accounting. A zero-liquidity path paid the contract balance instead of a share, after reposition set liquidity to zero, per SlowMist. Not a key compromise in the text. Not an oracle bug in the text.
Explorer URLs: Attacker https://polygonscan.com/address/0x59Ae3c8dd50063429D86BdaEBbC350fB64e9884B. Victim and vulnerable contract https://polygonscan.com/address/0x048E88311ca84876aeA086125825492e2AF2e5A0. No transaction hash in the alert text. Polygonscan is used because SlowMist Hacked places the vault on Polygon. If that chain reading is wrong, the same addresses on another EVM explorer are the check.
Status: First report in this window is the SlowMist alert at 03:28 UTC on 9 Oct. Database entry the same day. No project statement found in the posts read here. Transaction hash missing from the alert text. Funds not shown as returned.
Sources: https://x.com/SlowMist_Team/status/2108399198035202138, https://hacked.slowmist.io/, and https://publicaml.org/news/2026-10-09-bitbay-stablevault/
EtherVista — Ethereum — about $18,600 — uint112 K-check overflow
What happened: SlowMist posted at 05:20 UTC on 9 Oct a threat-intel alert on EtherVista. The loss line is about $18,600. The root-cause sentence says EtherVistaPair.swap suffers from an integer overflow in its K-invariant check. Both reserves are uint112, so their multiplication overflows and wraps, and the invariant check can pass even when the actual reserve product decreases. The attacker, in that account, used an attacker-controlled contract registered as the authorized router and ran two crafted swaps to drain WETH and VISTA from the pool. That is the alert. This brief does not re-decode the pair and does not print a swap formula.
The attacker in the alert is 0xbbf8f3fe8e4fdf6b594e6107144d78293d2018fa. The attack contract, labeled router, is 0x469424b628a9d2036e41496e814db500d683b120. The vulnerable contract is 0xfdd05552f1377aa488afed744c8024358af02041. The post ends with “Tx:” and does not print a hash in the text read here. This brief does not invent one. SlowMist Hacked, dated 9 Oct 2026, names EtherVista and repeats the same overflow, the same router registration, and the same two swaps, with a loss of about $18,600. The method line is smart-contract vulnerability. The reference on that entry is the same SlowMist post. PublicAML’s 9 Oct note says the pool is on Ethereum and uses the same $18,600 figure. TokenPost, published 9 Oct, says two transactions withdrew WETH and VISTA and does not print hashes. A secondary post this morning priced the same incident at $18,590.72 and timed a drain at 03:47 UTC on 9 Oct. That dollar print and that timestamp are not in the SlowMist alert. They stay secondary and are not adopted as the card figure.
The SlowMist post does not print the word Ethereum. The chain reading here is PublicAML’s Ethereum line plus the WETH unit in the alert. A later post that names another chain would supersede that reading. No freeze, no bounty, and no project statement appeared in the posts read here. One reply under the alert restated the uint112 wrap in general terms. It is not a second incident report and it is not used as a loss figure.
Protocol / chain / asset: EtherVista, contract EtherVistaPair, as named by SlowMist. Assets named in the alert are WETH and VISTA. Chain reading is Ethereum from PublicAML and the WETH unit, not from an explicit chain word in the alert.
Loss: About $18,600, SlowMist alert and SlowMist Hacked. The alert also prints ~18.6K. No split between WETH and VISTA is in the alert. No recovery figure. No freeze posted. Counted on the card. The $18,590.72 secondary print is not added and not substituted.
Attack type: Arithmetic in the pair invariant. uint112 reserves multiplied in a width that wraps, so the K-check can pass on a falling product, per SlowMist. The path in the alert also uses an attacker-controlled contract registered as the authorized router. Not a key compromise in the text.
Explorer URLs: Attacker https://etherscan.io/address/0xbbf8f3fe8e4fdf6b594e6107144d78293d2018fa. Attack contract https://etherscan.io/address/0x469424b628a9d2036e41496e814db500d683b120. Vulnerable contract https://etherscan.io/address/0xfdd05552f1377aa488afed744c8024358af02041. No transaction hash in the alert text. Etherscan is used because the secondary note places the pool on Ethereum. If that chain reading is wrong, the same addresses on another EVM explorer are the check.
Status: First report in this window is the SlowMist alert at 05:20 UTC on 9 Oct. Database entry the same day. No project statement found in the posts read here. Transaction hashes missing from the alert text. Funds not shown as returned. A secondary timestamp of 03:47 UTC is unverified by this desk.
Sources: https://x.com/SlowMist_Team/status/2108427455572918626, https://hacked.slowmist.io/, and https://publicaml.org/news/2026-10-09-ethervista/
Also noted
- UPDATE, 79Vault return of 15,000 BNB: CertiKAlert at 09:57 UTC on 9 Oct, in the thread opened at 08:36 UTC on 8 Oct, wrote that the attacker has returned 15,000 BNB, about $11 million, and linked https://bscscan.com/tx/0xf345a03f15b62758cd2ab30ef1d5eabd844f4bc6b2c33322975f476502b19f15. This desk did not re-open that page. The dollar line is CertiK’s. DefimonAlerts at 08:15 UTC on 9 Oct relayed an on-chain settlement text asking for 15,000 BNB to
0x2BFcF0475e7B40cd68E91A7178Cf5E43262EB7b2, with the remainder kept as bounty, and saying risk flags would be lifted and legal action dropped on receipt. An earlier Defimon relay at 13:05 UTC on 8 Oct, still inside this cutoff, asked for at least 50 percent first to the same address. The 7 Oct drain and the about $12.5 million cash-out were already in the 8 Oct brief. The return is not a new loss and is not on today’s card. Whether 15,000 BNB is the full remainder, a partial return, or a bounty settlement is not settled by the posts read here. The 79thVault announcement at 17:15 UTC on 8 Oct called the incident a malicious attack from account-permission weaknesses, said an operator private key was obtained, and said a white-hat discussion was ongoing. That post did not print the 15,000 BNB return. The return line is CertiK’s later note. - UPDATE, X7Pioneer dollar listing: The 8 Oct brief scored SlowMist’s 10:28 UTC alert at about 6.78 ETH and did not convert it, because the alert had no dollar figure. SlowMist Hacked now lists that same X7 Finance event at $16,514, dated 8 Oct, with the same claimRewards account. No new SlowMist alert on X7 landed in this window. The $16,514 line is a database valuation of yesterday’s incident. It is not a new drain and is not on today’s card.
- SlowMist, FOMO bookmark analysis: At 12:15 UTC on 8 Oct SlowMist followed its earlier warning with an analysis of a bookmark phishing page aimed at the FOMO web interface. The post says a fake verification page led users to drag an icon to the bookmarks bar and click it, and that the bookmarklet collected session material from a logged-in page. It says stolen funds were traced through USDC and SOL swaps, splits, and deposits to Privacy Cash and gambling platforms. No loss figure. Not scored. The click path is not repeated here.
- UPDATE, Duelbits bounty text: DefimonAlerts at 11:07 UTC on 8 Oct relayed an on-chain message naming Duelbits, offering a bounty if the remainder is returned, and asking the recipient to contact DuelbitsRecovery on Telegram. The message claims an individual has been identified. That claim is the sender’s. It is not confirmed here. No new dollar figure. Not on the card.
- On-chain message, Hyperliquid XMR1, unverified: DefimonAlerts at 22:40 UTC on 8 Oct relayed a message saying 16.28 XMR1 on Hyperliquid was stolen on 2 Oct from
0xc70765ce72945f22E2D08a6Fd5D31d5533612915, and offering a 90 percent return to0x7bC84a12DB499ebB67d990192ff903a87CbC4a16. The date in the message is outside this window. No desk alert in the posts read here confirms the theft or the amount. Not scored. - GoPlus service note: At 13:00 UTC on 8 Oct GoPlus said Token Security API support for Abstract and Blast ends on 19 Oct 2026. Not an exploit.
- Phalcon, BlockSecTeam, ZachXBT, CyversAlerts, PeckShieldAlert, Lookonchain, Immunefi, rekt.news: No separate first-report exploit used as a figure in this cutoff. Lookonchain’s posts in the window are trader and flow notes. Immunefi’s posts are researcher payouts.
Sources and references
- SlowMist, BitBay, 03:28 UTC on 9 Oct: https://x.com/SlowMist_Team/status/2108399198035202138
- SlowMist, EtherVista, 05:20 UTC on 9 Oct: https://x.com/SlowMist_Team/status/2108427455572918626
- SlowMist Hacked index: https://hacked.slowmist.io/
- PublicAML, BitBay note: https://publicaml.org/news/2026-10-09-bitbay-stablevault/
- PublicAML, EtherVista note: https://publicaml.org/news/2026-10-09-ethervista/
- CertiKAlert, 79Vault return, 09:57 UTC on 9 Oct: https://x.com/CertiKAlert/status/2108497100665487361
- CertiKAlert, 79Vault first note, 08:36 UTC on 8 Oct: https://x.com/CertiKAlert/status/2108114270559096916
- BscScan transaction linked by CertiK: https://bscscan.com/tx/0xf345a03f15b62758cd2ab30ef1d5eabd844f4bc6b2c33322975f476502b19f15
- DefimonAlerts, 15,000 BNB settlement text, 08:15 UTC on 9 Oct: https://x.com/DefimonAlerts/status/2108471295197266303
- DefimonAlerts, 50 percent return text, 13:05 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108181921737932985
- 79thVault announcement, 17:15 UTC on 8 Oct: https://x.com/79thVault/status/2108244949963833685
- SlowMist, X7Pioneer, 10:28 UTC on 8 Oct: https://x.com/SlowMist_Team/status/2108142452888776907
- SlowMist, FOMO bookmark analysis, 12:15 UTC on 8 Oct: https://x.com/SlowMist_Team/status/2108169316025893169
- DefimonAlerts, Duelbits bounty text, 11:07 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108152352305742137
- DefimonAlerts, XMR1 message, 22:40 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108326704355647669
- GoPlusSecurity, Abstract and Blast API note, 13:00 UTC on 8 Oct: https://x.com/GoPlusSecurity/status/2108180614684049492
Editor’s note: the live dollar loss is the BitBay DAI figure plus the EtherVista pool figure, about $32,600, and both are contract bugs rather than keys. Transaction hashes were not in the SlowMist alert text, so the explorer links are address pages. The 15,000 BNB return is an update on yesterday’s 79Vault case. It is not rescored as a new loss, and this desk did not re-open the linked transaction.
Read more
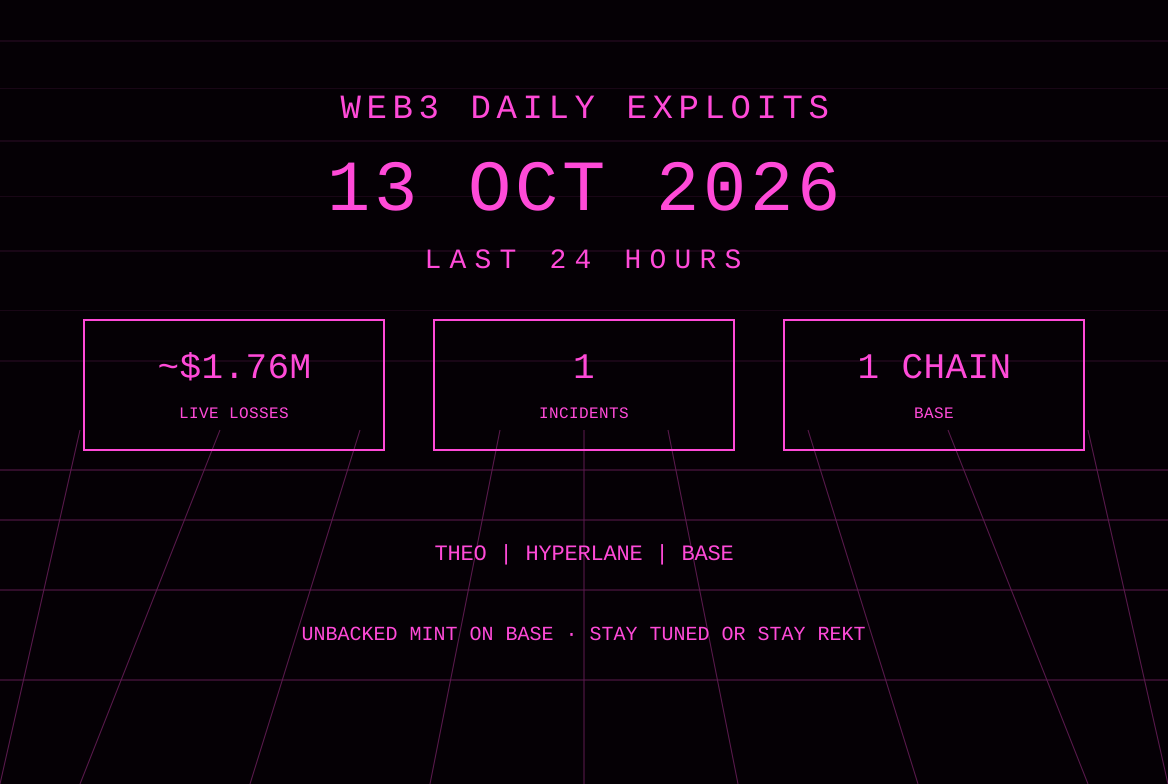
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.
Web3 Daily Exploits — 11 Oct 2026: Ledger Implant Confirmed, 2,990 ETH to Tornado
UPDATE on the CryptoBilis Ledger supply-chain incident. Ledger confirms an unauthorized hardware implant in one affected user device. On-chain researchers report the attacker deposited 2,990 ETH worth about $7.45 million into Tornado Cash between 9 and 10 Oct, with further deposits continuing on 11 Oct. No new protocol drains in the window.
Web3 Daily Exploits — 10 Oct 2026: Ledger Reseller Drains and Bridge EIP-7702 Claim
Ledger investigates reports of fund losses among Southeast Asia buyers of devices from reseller CryptoBilis. Researchers estimate about $93 million drained across Bitcoin, Ethereum, Tron, BNB Chain and Polygon. Phalcon flags $3.55 million in unclaimed bridge funds claimed via EIP-7702 by a Tornado-funded address; ownership intent is open.