Web3 Daily Exploits — 8 Oct 2026: 79Vault Operator Drain
CertiK, Defimon, GoPlus, and PeckShield flag a 79Vault drain on BNB Chain: 2.01 million 79AU moved by an operator key and sold for 16,249 BNB, about $12.5 million. SlowMist reports an X7Pioneer reward-counter bug for about 6.78 ETH. Duelbits posted fresh on-chain bounty messages on an older hot-wallet case.
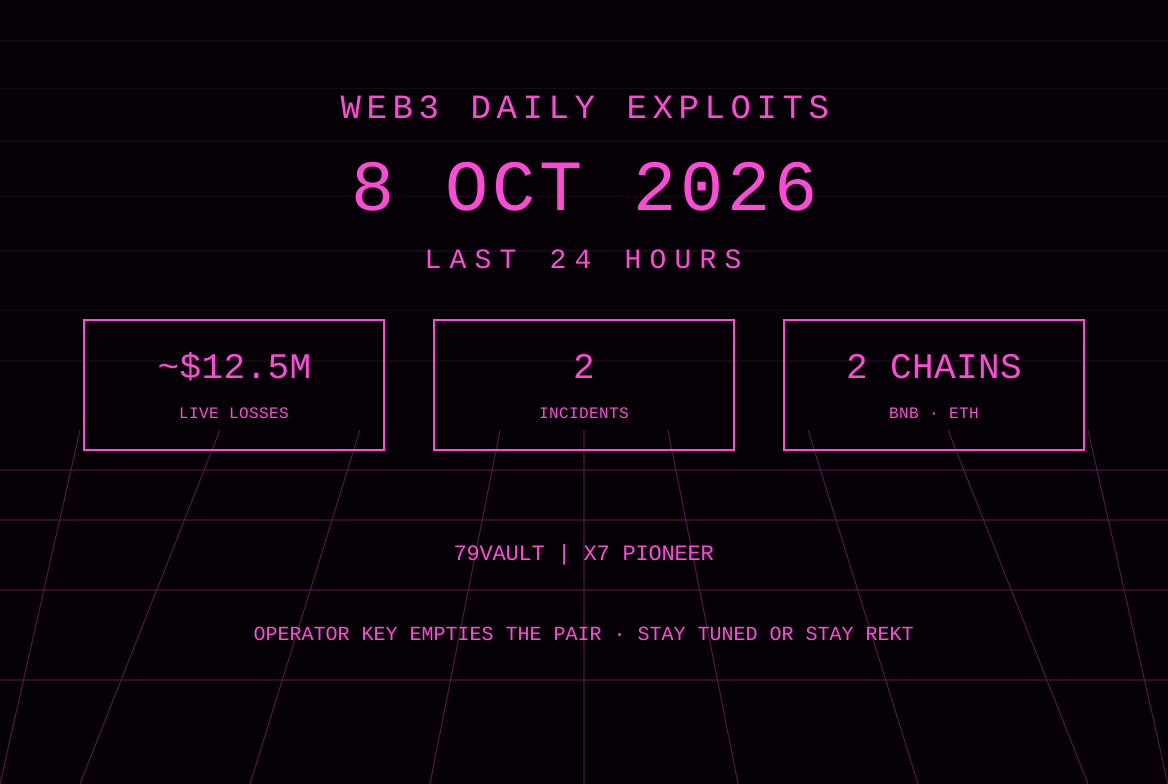
The 8 Oct America/Panama window is an operator-key day on BNB Chain, plus a small Ethereum reward-accounting drain that SlowMist priced in ETH only. The scored live loss is the 79Vault figure the desks printed this morning. CertiKAlert, at 08:36 UTC on 8 Oct, wrote that suspicious movement from 79thVault sold 2.01 million 79AU via a privileged function and moved 16.2k BNB, about $12.5 million, to an attacker. DefimonAlerts, at 07:41 UTC, used the same dollar line and typed the incident as a private-key compromise of the operator wallet. GoPlusSecurity, at 10:49 UTC, called it a $12.5 million loss after a privileged admin address was used without authorization, and left key leak and insider both open. PeckShieldAlert, at 09:53 UTC, printed 16.249k BNB, about $12.51 million. That cluster is the card’s live-loss line. The on-chain move itself is earlier: the BNB consolidation transaction on BscScan is timestamped 10:10:47 UTC on 7 Oct. The first desk reports used here landed on 8 Oct.
The second scored item is SlowMist at 10:28 UTC on 8 Oct. The alert names X7 Finance, contract X7Pioneer, and a loss of about 6.78 ETH. No dollar conversion is in that post. This brief does not invent one. The 6.78 ETH is not folded into the about $12.5 million card line. Phalcon had no post in the window read here. BlockSecTeam, Lookonchain, ZachXBT, and CyversAlerts did not post a separate first-report exploit used as a figure. Immunefi and rekt.news did not publish a new incident post used as a figure. A Defimon on-chain message pair this morning is a Duelbits bounty text on an older case. It is an update, not a new loss.
79Vault — BNB Chain — about $12.5 million — operator key and privileged pair drain
What happened: DefimonAlerts posted at 07:41 UTC on 8 Oct that 79thVault lost $12.5 million, dated 2026-10-07 in the alert. The token is 79AU. The network is BNB Chain. The type line is private key compromise. Defimon says the 79AU token has an OPERATOR_ROLE-only function that moves any amount of 79AU straight out of the PancakeSwap 79AU/USDT pair to any address, then calls sync. The team’s operator hot wallet, printed as 0x019bd8ed, normally uses that function for small pair-to-reward-pool transfers. Between 07:27 and 08:19 UTC it sent seven transfers totalling 2.01 million 79AU from the pair to the attacker externally owned account. The slices in the alert are 10,000, 100,000, 100,000, 300,000, 500,000, 500,000, and 500,000.
Defimon says the attacker sold that inventory back into the same pair through about 95 swaps. The pair’s USDT reserve fell from $15.2 million to $3.9 million in that account. The attacker cashed out 16,249 BNB, about $12.5 million, to 0x629b368c. Forty-one seconds later the operator key sent its own 3.79 BNB to that same address. Defimon reads that hop as evidence the attacker controls the key, or that the operator is an insider. Another 500,000 79AU went to a truncated address printed as 0xf219d073. Defimon says OPERATOR_ROLE has since been revoked. This desk did not re-check the role bitmap after that sentence.
GoPlusSecurity, at 10:49 UTC, expanded the same path and left the cause open. The function selector in that post is 0x2a2c5923. GoPlus says the source is unverified on BscScan, that on-chain calls show the function can move 79AU from a chosen address — this time the 79AU/USDT pair — to any recipient, then call sync, and that the effect is backdoor-like. The operator address in full in that post is 0x019bD8ED017D11AF0eB24d28DCdd0f9930c85cA3. GoPlus says there was no multisig and no timelock. In the window 07:25 to 08:19 UTC that address executed seven privileged calls and moved 2.01 million 79AU to 0xc3E90f78A918594a605d584887b2775F4b80A099. The same slices appear. GoPlus says the role was revoked after the incident. The receiving address sold the 79AU into the pool, drained the USDT, converted the proceeds to 16,249 BNB, and consolidated them to 0x629B368c6BF1a9f190e38f21235033FEcE8A6231. Aside from several smaller transfers of 10 to 15 BNB each, purpose still unclear in that post, most of the funds now sit at 0xa9537B40b02Af7Af8f1543aea3691992B2174F89 — 14,394.92 BNB, about $11.03 million. No further movement yet, per GoPlus. GoPlus also wrote that close to 10,000 holders are affected. That holder count is their print. It is not re-counted here.
CertiKAlert, at 08:36 UTC, linked the 16.2k BNB move to 0xee0e44167518ff0071ede02a03b3710a1a8438d52616aad4bf1d5e417b37b0df and said about 90 percent is held at the same 0xa9537 address, to which a 10 percent bounty was offered. An earlier Defimon post, at 05:15 UTC, is the on-chain message that offer sits on. The message says it is from the AU project team, names nearly 60,000 retail users, asks the recipient to keep 10 percent and return 90 percent to 0x2BFcF0475e7B40cd68E91A7178Cf5E43262EB7b2, and says the team will treat a return as a white-hat case. Defimon’s later alert says that bounty message was sent from the same operator key. GoPlus flags the authenticity: using the privileged address to talk to an attacker would be unusual, and the message’s authenticity is still in question. The 60,000-user line is in the message. It is not a desk census.
The project’s own X post, at 02:36 UTC on 8 Oct, did not describe a drain. It called the event a system upgrade, said some front-end features and asset-related operations may be temporarily affected, and said services will resume after the upgrade. GoPlus noted that limited disclosure. PeckShieldAlert, at 09:53 UTC, wrote that 79thVault was exploited, with 10k 79AU drained and swapped for 16.249k BNB, about $12.51 million, and that the exploiter has since deposited 30 BNB to KuCoin. The 10k figure matches only the first slice in the Defimon and GoPlus lists. This brief does not replace the 2.01 million token total with 10k. The 30 BNB KuCoin deposit is PeckShield’s print. This desk did not re-open that hop. A secondary post claimed about $12.0 million of the BNB was still unspent and that OPERATOR_ROLE was still granted. That conflicts with Defimon’s revocation line and with GoPlus’s revocation line. It stays unverified.
BscScan shows the consolidation transaction as success, 07 Oct 2026 10:10:47 UTC, from 0xc3E90f78A918594a605d584887b2775F4b80A099 to 0x629B368c6BF1a9f190e38f21235033FEcE8A6231, value 16,249.117811157533821075 BNB. The page displayed that value at about $12,392,389. The desk prints stay at about $12.5 million and about $12.51 million. The page dollar figure is a display value, not a second loss and not a revision this brief adopts. The seven privileged calls are not given individual hashes in the posts read here. This brief does not invent them.
Protocol / chain / asset: 79thVault, also written 79Vault in the CertiK post, on BNB Chain. Asset out of the pair is 79AU. Asset cashed out is BNB. Pair named by Defimon and GoPlus is the PancakeSwap 79AU/USDT pair. The pair contract address was behind a short link in the Defimon post and is not expanded here. The project bio on X prints a contract address. That bio line is not used as the pair address.
Loss: About $12.5 million, CertiK, Defimon, and GoPlus. About $12.51 million, PeckShield, on 16.249k BNB. Token amount moved from the pair: 2.01 million 79AU, Defimon and GoPlus. USDT reserve drop in the Defimon alert: $15.2 million to $3.9 million. Residual at the 0xa9537 address: 14,394.92 BNB, about $11.03 million, GoPlus. Bounty offered: 10 percent, not accepted in any post read here. No freeze posted by a desk. The card uses about $12.5 million. The BscScan page dollar figure is not added and not subtracted.
Attack type: Privileged function plus operator key. Defimon types it private key compromise and leaves insider open because the operator key later sent 3.79 BNB to the cash-out address and also sent the bounty message. GoPlus types it privileged function plus operator key compromise, or an insider, and says both are still open. Not an oracle bug in any of these posts. The function is role-gated. The open question is who held the key at 07:27 UTC on 7 Oct.
Explorer URLs: Consolidation transaction https://bscscan.com/tx/0xee0e44167518ff0071ede02a03b3710a1a8438d52616aad4bf1d5e417b37b0df. Operator https://bscscan.com/address/0x019bD8ED017D11AF0eB24d28DCdd0f9930c85cA3. 79AU recipient and BNB sender https://bscscan.com/address/0xc3E90f78A918594a605d584887b2775F4b80A099. First BNB consolidation address https://bscscan.com/address/0x629B368c6BF1a9f190e38f21235033FEcE8A6231. Later holding address in the CertiK and GoPlus posts https://bscscan.com/address/0xa9537B40b02Af7Af8f1543aea3691992B2174F89. Bounty return address named in the on-chain message https://bscscan.com/address/0x2BFcF0475e7B40cd68E91A7178Cf5E43262EB7b2. The 0xf219d073 prefix is not expanded.
Status: First desk reports in this window, on a drain timestamped 7 Oct. Project post called it a system upgrade and did not print a loss. Operator role revocation is in the Defimon and GoPlus text and is contradicted by one secondary post. Bounty offered, not shown as paid. About 14,394.92 BNB still at the holding address in the GoPlus post. KuCoin 30 BNB deposit unverified by this desk. Insider versus external key remains open.
Sources: https://x.com/DefimonAlerts/status/2108100434942431441, https://x.com/CertiKAlert/status/2108114270559096916, https://x.com/GoPlusSecurity/status/2108147742233284637, and https://x.com/PeckShieldAlert/status/2108133701448327326
X7Pioneer — Ethereum — about 6.78 ETH — reward-counter accounting
What happened: SlowMist posted at 10:28 UTC on 8 Oct a threat-intel alert on X7 Finance. The loss line is about 6.78 ETH. The root-cause sentence says that in claimRewards, totalRewards is incremented by the contract balance minus lastETHBalance on every call, but lastETHBalance is updated only when claimable is greater than zero. Calling with an empty array leaves claimable at zero, so the same unaccounted balance is repeatedly added to totalRewards, inflating the per-token reward. SlowMist also says the attacker donated ETH to amplify the delta before draining funds. That is the alert’s account. This brief does not re-decode the function and does not add a call sequence.
The attacker in the alert is 0xc79352119a7cf6efbfabbd7e6b013b79687bacf2. The victim and the vulnerable contract are the same address, 0x70000299ee8910ccacd97b1bb560e34f49c9e4f7, labeled X7Pioneer. The post ends with “Tx:” and does not print a hash in the text read here. This brief does not invent one. The alert prices the loss in ETH and prints Ethereum-style addresses. The chain is treated as Ethereum on that basis. A later post that names another chain would supersede that reading. No dollar figure is in the alert. About 6.78 ETH stays in ETH on the card’s incident count and off the dollar line.
Protocol / chain / asset: X7 Finance, contract X7Pioneer, as named by SlowMist. Asset is ETH. Chain reading is Ethereum from the unit and the address format, not from an explicit chain word in the alert.
Loss: About 6.78 ETH. No USD print. No recovery figure. No freeze posted in the alert. Not added to the about $12.5 million line.
Attack type: Reward accounting. Balance snapshot updated only on a positive claimable path, so an empty claim input reused the same unaccounted balance, per SlowMist. Donation of ETH widened the delta, per the same alert. Not a key compromise in the text.
Explorer URLs: Attacker https://etherscan.io/address/0xc79352119a7cf6efbfabbd7e6b013b79687bacf2. Victim and vulnerable contract https://etherscan.io/address/0x70000299ee8910ccacd97b1bb560e34f49c9e4f7. No transaction hash in the post.
Status: First report in this window is the SlowMist alert. No project statement found in the posts read here. Transaction hash missing from the alert text. Dollar value not scored.
Sources: https://x.com/SlowMist_Team/status/2108142452888776907
Also noted
- UPDATE, Duelbits on-chain bounty messages: DefimonAlerts posted on-chain messages at 10:43 UTC and 11:07 UTC on 8 Oct. The text says stolen funds were traced, names Duelbits, offers a bounty if the remainder is returned in full, and asks the recipient to contact DuelbitsRecovery on Telegram. The messages do not restate a dollar figure, a hash, or a chain. The September Duelbits hot-wallet case was previously reported near $7 million. That older figure is not a new loss and is not on today’s card. The identification claim in the message is the sender’s claim. It is not confirmed here.
- UPDATE, MakerDAO keeper analysis: CertiKAlert at 12:40 UTC on 7 Oct pointed at its write-up of the 6 Oct MakerDAO liquidation keeper incident, 200 ETH, about $542,000. That drain was already in the 6 Oct brief. No new loss figure in the 8 Oct window. Not rescored.
- SlowMist, FOMO bookmark phishing: At 03:40 UTC on 8 Oct SlowMist warned of a bookmark-based phishing page aimed at the FOMO web interface. The alert describes a fake check that leads a logged-in user to a malicious bookmark. No loss figure. Not scored. The click path is not repeated here.
- 79Vault token-count mismatch: PeckShield printed 10k 79AU. Defimon and GoPlus printed 2.01 million 79AU across seven transfers, the first of which is 10,000. The BNB cash-out figure matches across the four desks. The 10k line is not used as the token total.
- Role-revocation conflict, unverified: Defimon and GoPlus say OPERATOR_ROLE was revoked. A secondary post said the role was still granted and that about $12.0 million remained unspent. Not resolved here.
- KuCoin 30 BNB, unverified: PeckShield said the exploiter deposited 30 BNB to KuCoin. Not re-opened. Not added to the loss.
- Phalcon, BlockSecTeam, Lookonchain, ZachXBT, CyversAlerts, Immunefi, rekt.news: No separate first-report exploit used as a figure in this cutoff.
Sources and references
- DefimonAlerts, 79Vault alert, 07:41 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108100434942431441
- DefimonAlerts, on-chain bounty message, 05:15 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108063706122711452
- CertiKAlert, 79Vault, 08:36 UTC on 8 Oct: https://x.com/CertiKAlert/status/2108114270559096916
- GoPlusSecurity, 79Vault analysis, 10:49 UTC on 8 Oct: https://x.com/GoPlusSecurity/status/2108147742233284637
- PeckShieldAlert, 79Vault, 09:53 UTC on 8 Oct: https://x.com/PeckShieldAlert/status/2108133701448327326
- 79thVault, system-upgrade post, 02:36 UTC on 8 Oct: https://x.com/79thVault/status/2108023747240411244
- BNB consolidation transaction: https://bscscan.com/tx/0xee0e44167518ff0071ede02a03b3710a1a8438d52616aad4bf1d5e417b37b0df
- SlowMist, X7Pioneer, 10:28 UTC on 8 Oct: https://x.com/SlowMist_Team/status/2108142452888776907
- SlowMist, FOMO phishing warning, 03:40 UTC on 8 Oct: https://x.com/SlowMist_Team/status/2108039792219013578
- DefimonAlerts, Duelbits bounty messages, 10:43 and 11:07 UTC on 8 Oct: https://x.com/DefimonAlerts/status/2108146283827400733 and https://x.com/DefimonAlerts/status/2108152352305742137
- CertiKAlert, MakerDAO keeper analysis pointer, 12:40 UTC on 7 Oct: https://x.com/CertiKAlert/status/2107813422817579518
Editor’s note: the live dollar loss is the 79Vault BNB cash-out, and the open question is key versus insider. The project post did not print a loss. X7Pioneer is a separate ETH figure with no hash in the alert and no dollar conversion. Duelbits and the Maker keeper note are updates. Truncated addresses stay truncated. Secondary role and KuCoin claims stay unverified.
Read more
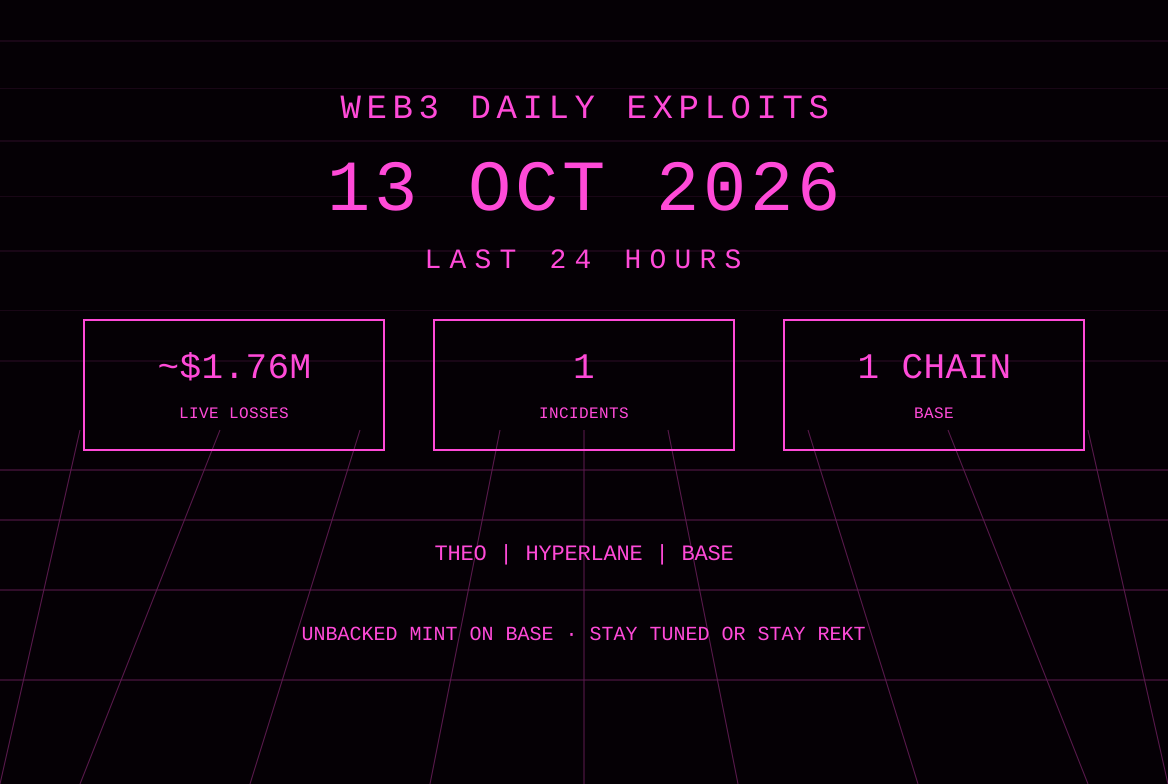
Web3 Daily Exploits — 13 Oct 2026: THEO $1.76M Unbacked Hyperlane Mint on Base
Autheo THEO token on Base suffered an unbacked mint of 19 million tokens via a Hyperlane warp-route TrustedRelayerIsm logic error. Attacker swapped for approximately 700.8 ETH (~$1.76M) and bridged to Ethereum. Token dropped ~92%. One incident, one chain.
Web3 Daily Exploits — 12 Oct 2026: Quiet Window, Ledger Update, COLDCARD X Phish
Quiet day for new protocol drains. Monitored accounts posted no first-report smart-contract exploits with fresh loss figures in the last 24 hours. Ledger issued a follow-up limiting confirmed CryptoBilis implant cases to the Southeast Asian reseller. COLDCARD reported a phishing post on its official X account with no confirmed user losses. Card live loss is ~$0.
Web3 Daily Exploits — 11 Oct 2026: Ledger Implant Confirmed, 2,990 ETH to Tornado
UPDATE on the CryptoBilis Ledger supply-chain incident. Ledger confirms an unauthorized hardware implant in one affected user device. On-chain researchers report the attacker deposited 2,990 ETH worth about $7.45 million into Tornado Cash between 9 and 10 Oct, with further deposits continuing on 11 Oct. No new protocol drains in the window.
Web3 Daily Exploits — 10 Oct 2026: Ledger Reseller Drains and Bridge EIP-7702 Claim
Ledger investigates reports of fund losses among Southeast Asia buyers of devices from reseller CryptoBilis. Researchers estimate about $93 million drained across Bitcoin, Ethereum, Tron, BNB Chain and Polygon. Phalcon flags $3.55 million in unclaimed bridge funds claimed via EIP-7702 by a Tornado-funded address; ownership intent is open.